November 19, 2026

5
min read
Data Retention Requirements for compliance
See 2026 data retention requirements by framework: how long to keep records, when to delete them, and how Strac enforces retention across SaaS, cloud and AI.
Data retention requirements are legal and contractual rules that govern the life of a record from creation to deletion. They come in two forms that pull in opposite directions.
Keep rules say a record must exist for a set time. SOX, SEC and FINRA rules, and HIPAA documentation rules are mostly keep rules. Delete a trade confirmation or an audit workpaper early and the penalty can be severe.
Delete rules say a record must not exist longer than it is needed. GDPR, the CCPA and CPRA, the GLBA Safeguards Rule and PCI DSS are mostly delete rules. Keep a card verification code or a former customer's passport scan and you hold a liability with no business value.
A retention program is the policy, the schedule and the controls that satisfy both at once. The schedule says how long. The controls make it happen on every system where the data actually lives, which is where most programs stop short.
Retention used to be a records management problem. You kept files in a few systems of record, set a schedule, and ran a purge job once a year. That model assumed sensitive data stayed where it was created.
It no longer does. A single customer record now travels through five or six tools in an afternoon. It starts in Salesforce, gets exported to a spreadsheet in Google Drive, pasted into Slack to ask a question, attached to a Jira ticket to reproduce a bug, and summarized in ChatGPT. Your retention schedule covers the first system. The other five keep the data forever by default.
Three shifts make this sharper this year.
AI tools became record stores. Prompts, uploads and chat histories in ChatGPT, Claude, Gemini and Copilot now hold customer data, and the vendor's retention policy decides how long it lives, not yours. In 2025, a US court ordered one major AI vendor to preserve consumer chat logs that users had already deleted. Once regulated data is pasted into a tool you do not control, your deletion promise depends on someone else. See does ChatGPT save data for how that works in practice.
AI agents read on a user's behalf. An agent connected through the Model Context Protocol (MCP) can pull a CRM record or a support ticket into its working memory and write it into a new document or log. Every agent action can create a new copy that no retention schedule lists. MCP DLP is the control that inspects those reads before the copy is made.
Regulators started asking for proof, not policy. Auditors for SOC 2, PCI DSS and HIPAA now expect evidence that deletion happened on the system in scope, not a PDF that says it should. A schedule tells the auditor what you intend. A deletion log tells them what you did.
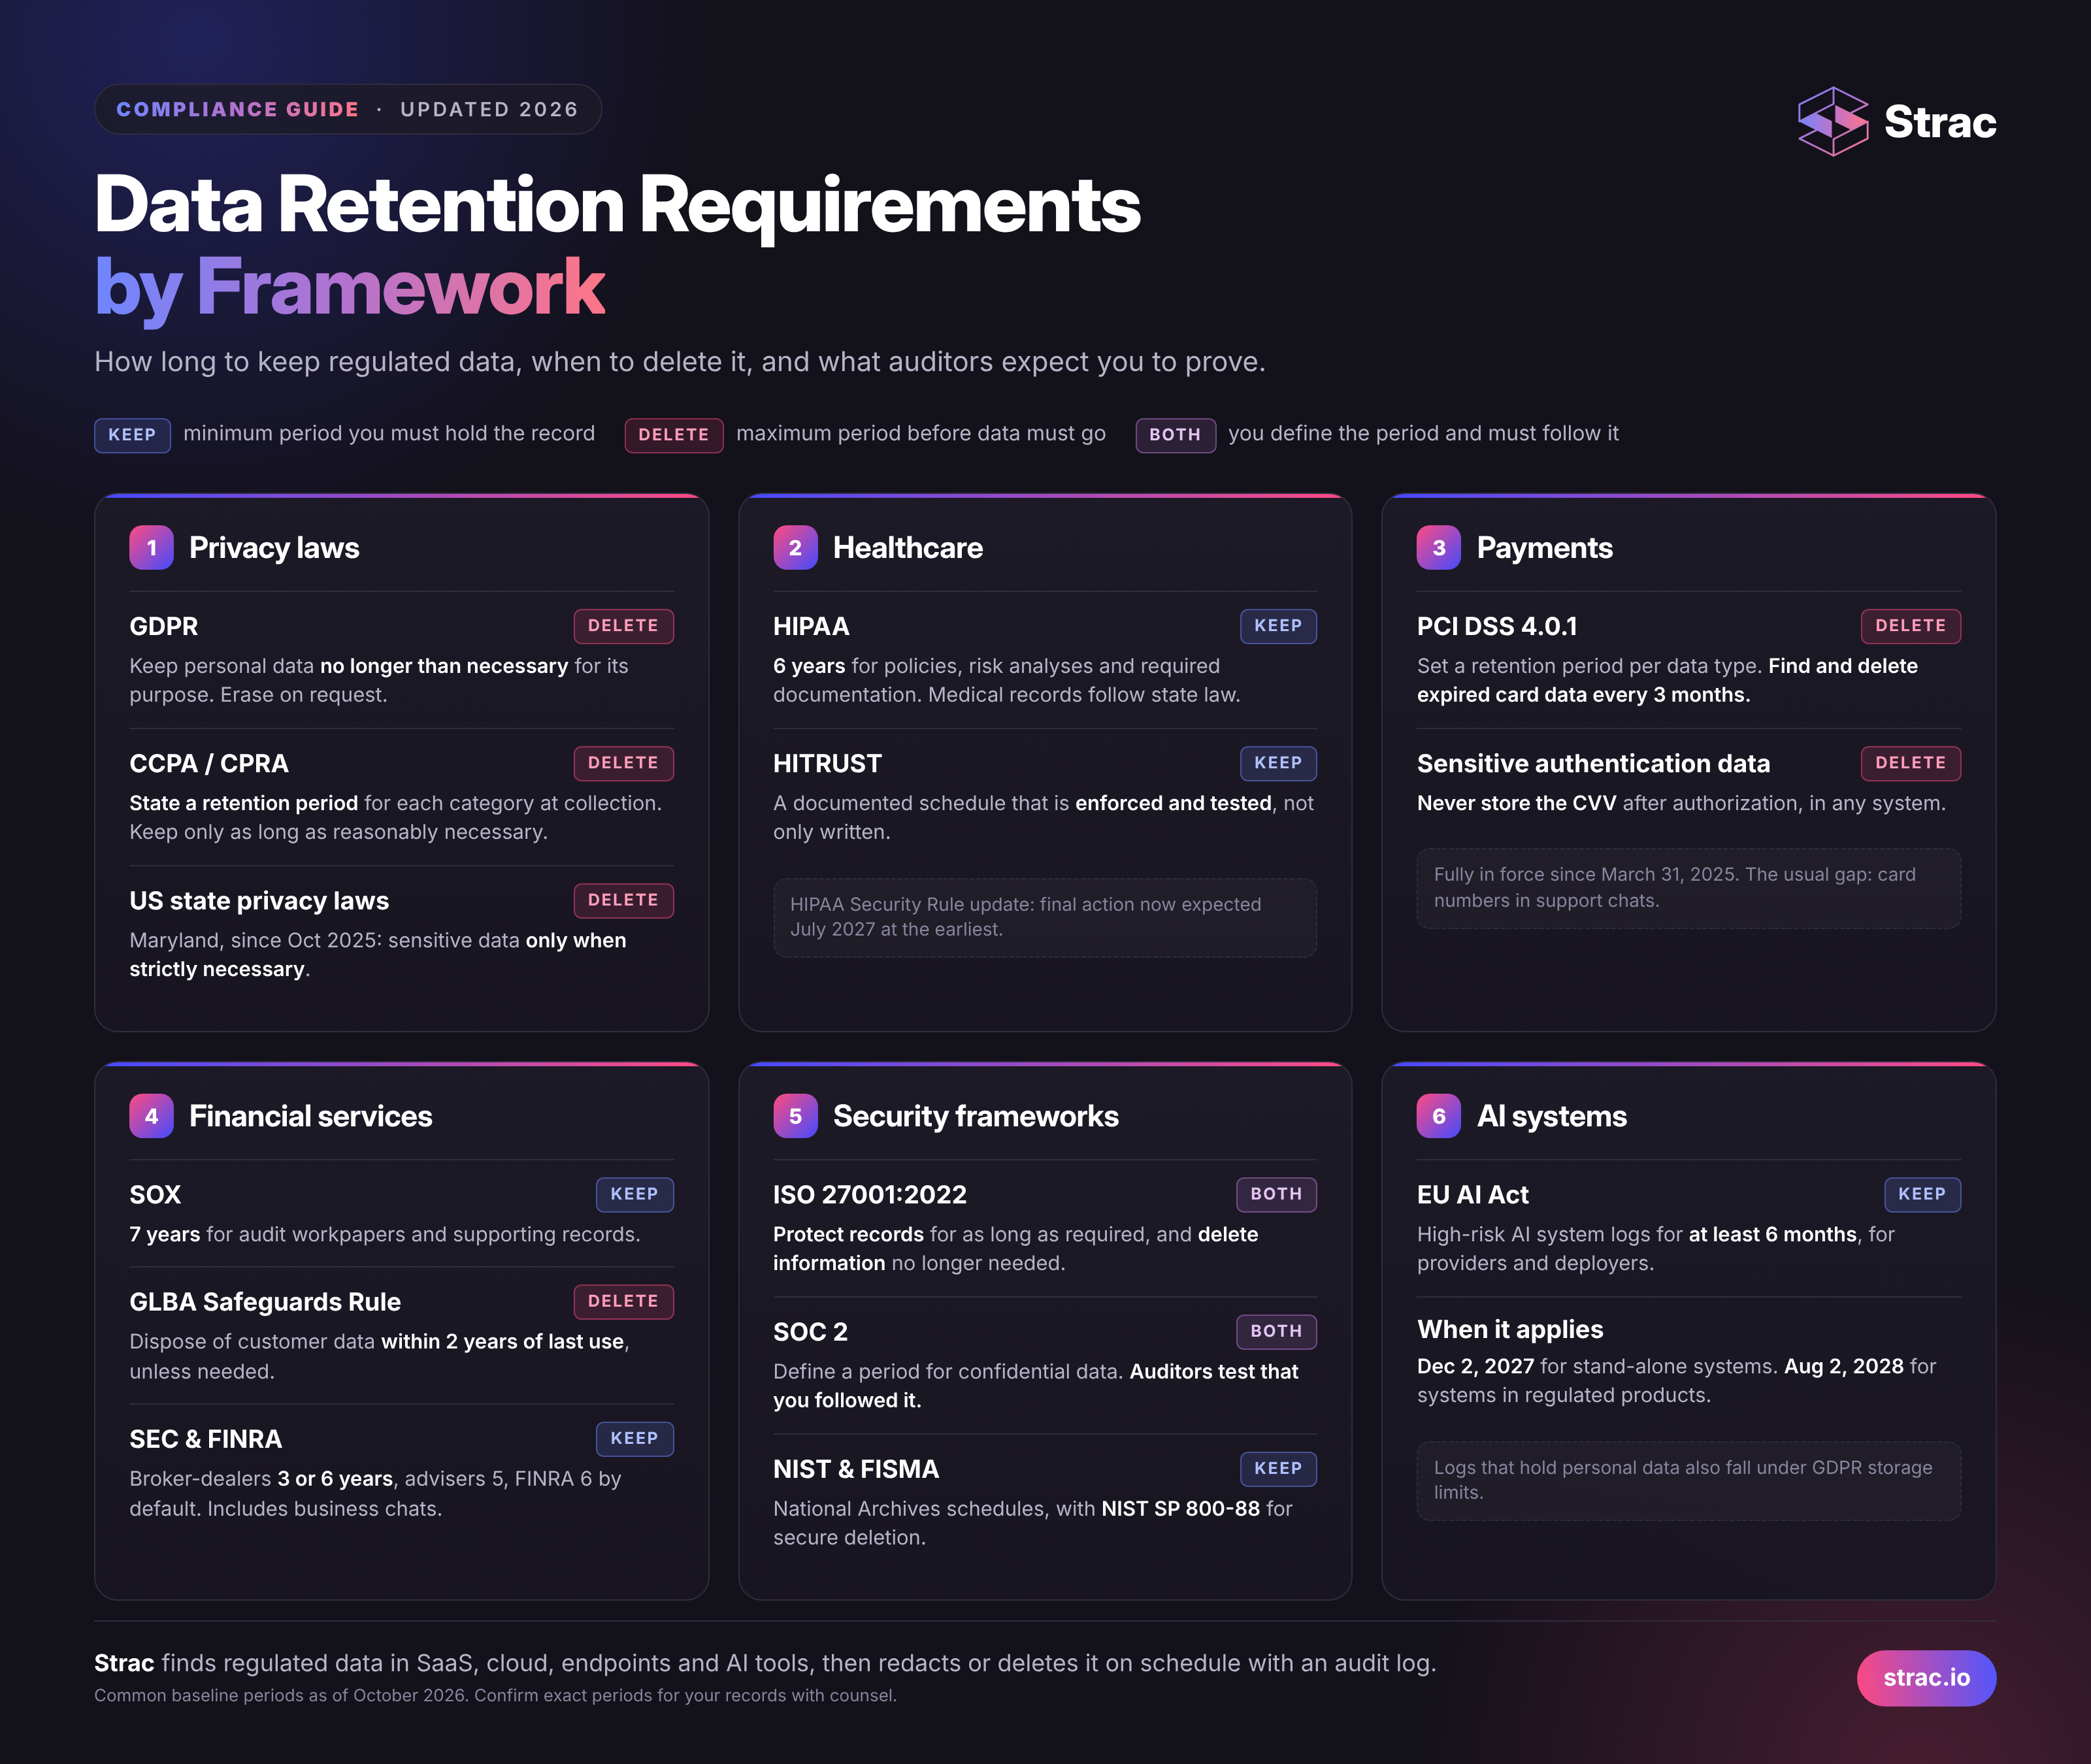
The periods below are the common baseline. Many depend on record type, state law or your own contracts, so treat them as the floor your legal team builds on.
GDPR does not set a number. Its storage limitation principle requires that personal data be kept in an identifiable form no longer than necessary for the purpose it was collected for. You set the period, document why, and delete or anonymize when it ends. Data subjects can also ask for erasure. Fines reach €20 million or 4% of global annual turnover, whichever is higher. The deeper walkthrough is in GDPR data minimization.
The CCPA, as amended by the CPRA, requires your notice at collection to state how long you keep each category of personal information, or the criteria you use to decide. You may not keep it longer than is reasonably necessary for the disclosed purpose. Penalties are assessed per violation and have been adjusted upward for inflation since 2025. See CPRA data minimization and the CCPA compliance page.
Other US state privacy laws now cover most of the country, and several go further than California. Maryland's law, in force since October 2025, limits collection of sensitive data to what is strictly necessary for the service the consumer asked for. For a company selling nationally, the strictest state sets the practical rule.
HIPAA requires covered entities and business associates to keep required policies, procedures, risk analyses and related documentation for six years from the date created or last in effect. Medical record retention itself is set by state law, often six to ten years for adults and longer for minors. The proposed overhaul of the HIPAA Security Rule has been pushed back, with final action now expected no earlier than July 2027, but the Office for Civil Rights enforces the current rule today. Every copy of protected health information (PHI) in a chat tool or ticket is PHI you now maintain. See HIPAA DLP and Slack HIPAA compliance.
HITRUST folds HIPAA, state law and NIST controls into one framework and expects a documented retention schedule that is enforced and tested, not only written.
PCI DSS 4.0.1 requires you to keep stored account data to a minimum through a retention and disposal policy, with a defined retention period for each data type and a process, run at least every three months, to find and securely delete stored cardholder data that has passed its retention date. Sensitive authentication data, including the card verification code, must not be stored after authorization at all. These requirements have been fully in force since March 31, 2025. The usual failure is not the payment system but the card number a customer typed into a support chat. See PCI DLP and PCI DSS PAN masking.
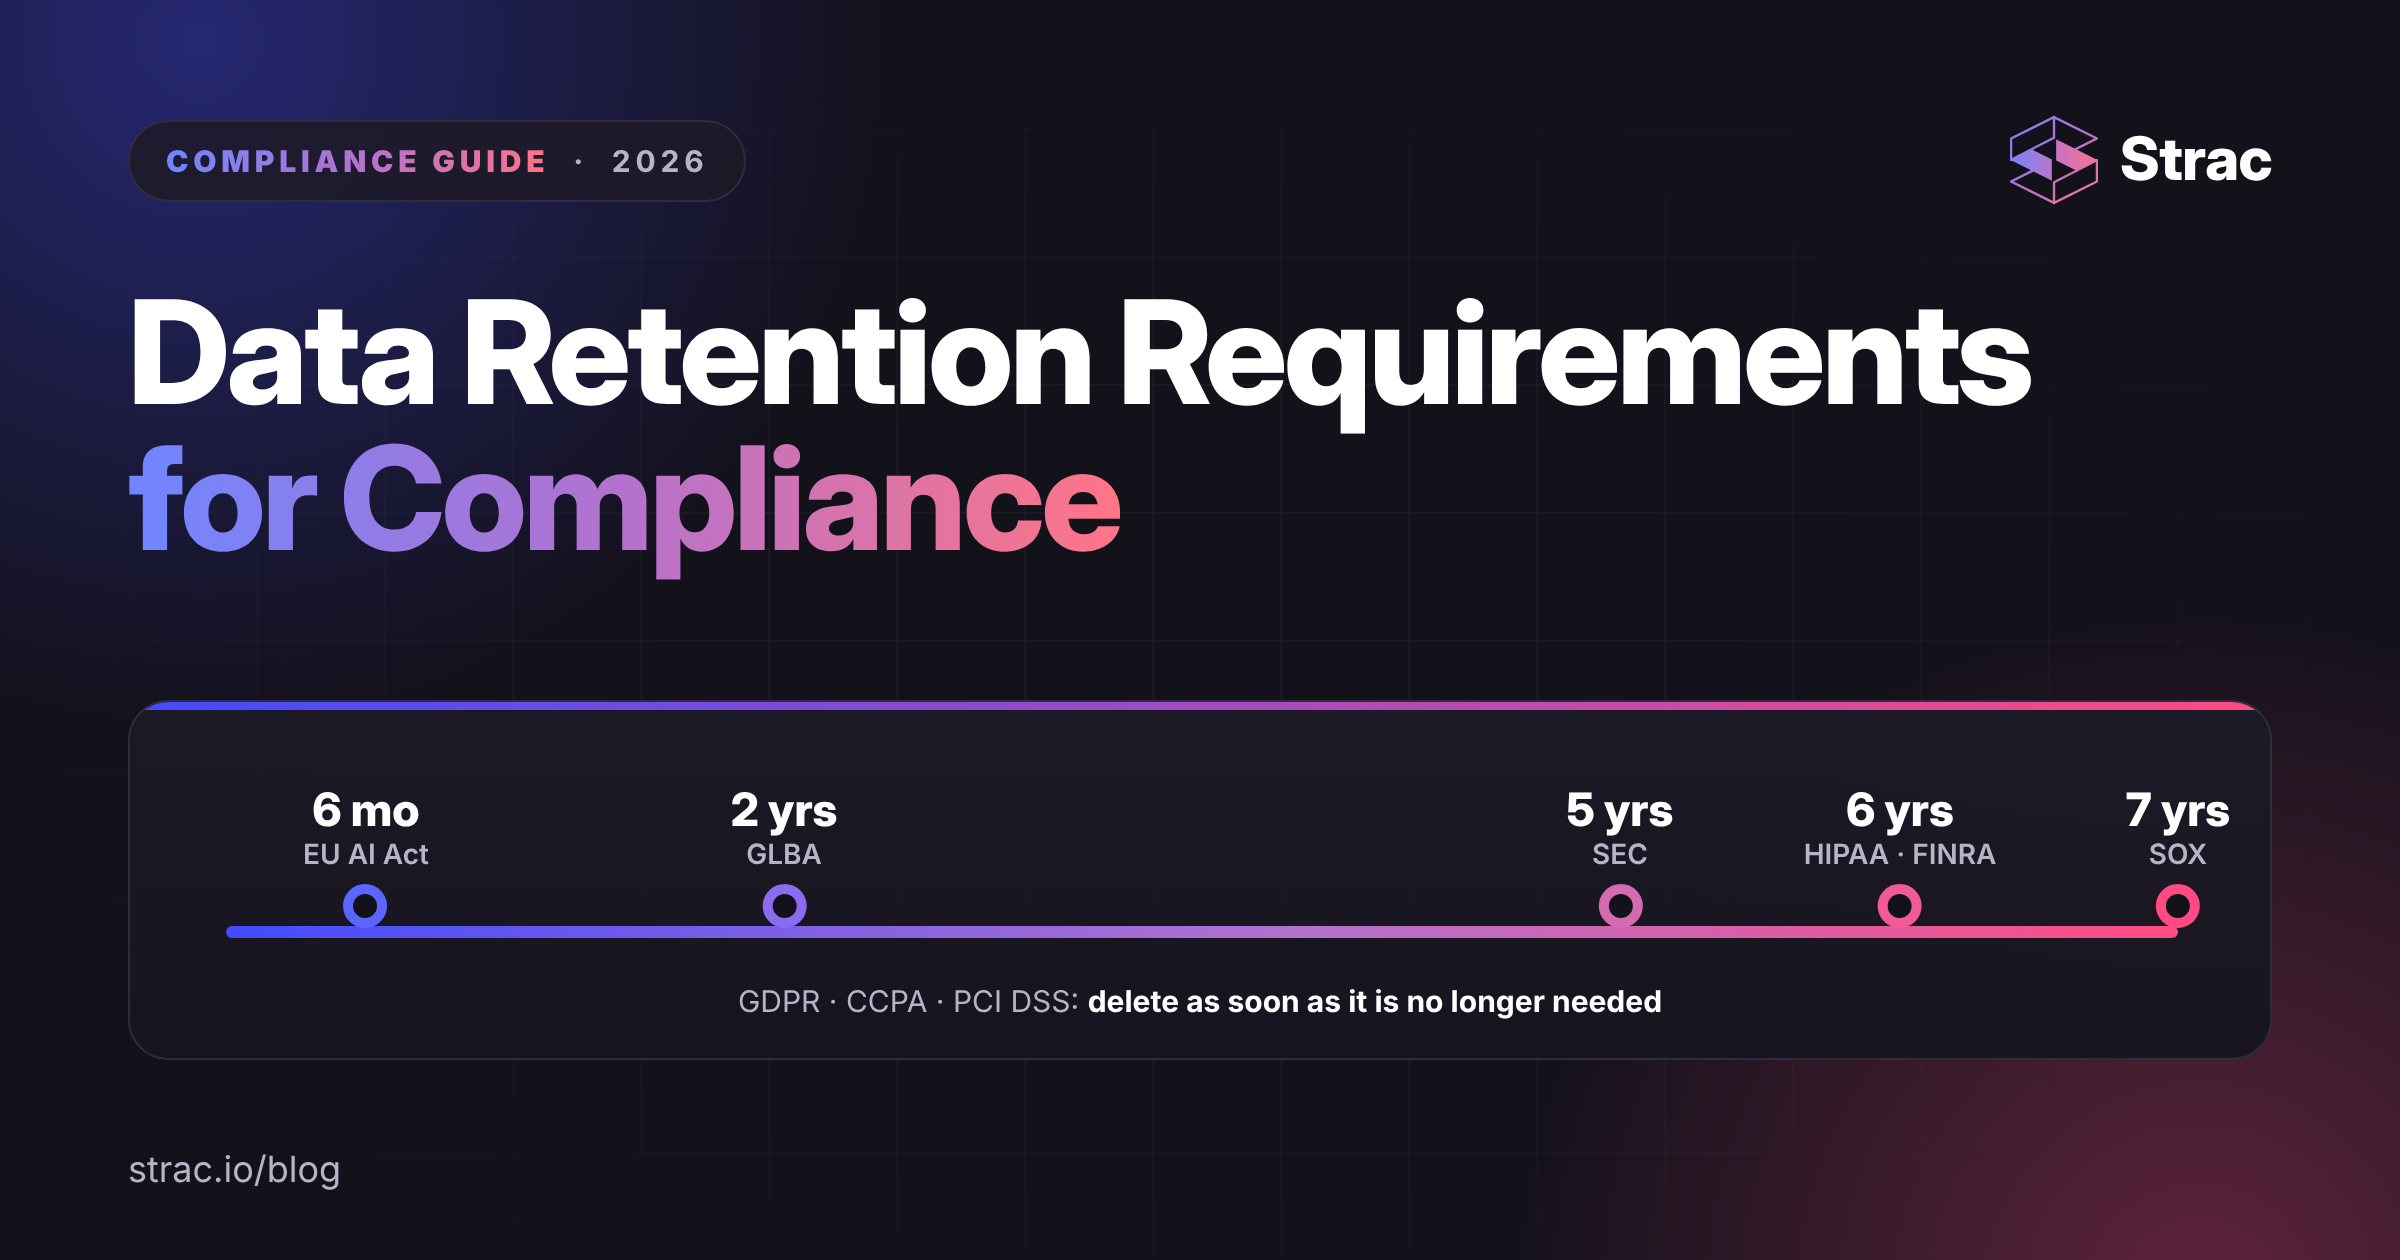
SOX requires public company auditors to keep audit workpapers and related records for seven years, and makes destroying records to obstruct an investigation a federal crime. In practice, finance teams apply a seven-year floor to the financial records that support those audits.
The GLBA Safeguards Rule is a delete rule. Financial institutions must dispose of customer information no later than two years after it was last used to serve the customer, unless it is needed for a legitimate business or legal reason, and must review their retention policy periodically.
SEC and FINRA rules are keep rules. Broker-dealers keep most records for three or six years, with the first two years easily accessible. Investment advisers generally keep books and records for five years. FINRA requires six years where no other period applies. The SEC wound down its sweep of off-channel communications in 2025, but the rule did not change and FINRA still brings cases from routine exams. A business conversation in an unapproved app is a record you were required to keep.
ISO 27001:2022 has two controls that matter here: protection of records, which covers keeping records intact for as long as required, and information deletion, which requires deleting information that is no longer needed. Neither sets a period; both expect you to define one and follow it. See ISO 27001 DLP.
SOC 2 also sets no period. The confidentiality criteria require you to identify confidential information, keep it for the defined period, and dispose of it when that period ends. Auditors test whether you followed your own policy across the observation window. See SOC 2.
NIST and FISMA guide federal agencies and their contractors. Agencies follow National Archives records schedules, and NIST's media sanitization guidance, revised in 2025, sets the standard for how deletion must happen so data cannot be recovered.
The EU AI Act adds a new kind of record: the logs a high-risk AI system generates. Providers and deployers must keep those logs for at least six months, unless other law requires longer. Under the Digital Omnibus agreement reached in 2026, the high-risk obligations now apply from December 2, 2027 for stand-alone systems and August 2, 2028 for systems built into regulated products. The logs will hold personal data, so they sit under GDPR's storage limitation at the same time. A log you must keep is still a log you must protect. The wider picture is in AI data governance.
Every retention failure falls into one of two buckets.
Over-retention is keeping data longer than the law allows or the business needs. It is the more common failure and the more expensive one. Old exports, closed tickets, and years of Slack history do not help anyone, but every one of them is in scope for a breach notice, an access request, or a discovery order. Data you no longer hold cannot leak.
Under-retention is deleting a record you were required to keep. It usually comes from blunt tools: a workspace-wide setting that deletes all messages after 90 days removes the regulated trade conversation along with the joke in the random channel.
Both failures have the same root cause. The rule is applied by age and location, not by content. A retention rule that cannot read the record will either keep too much or delete the wrong thing. The fix is to classify first, then let the data type decide the clock.
Strac connects to each app through its API, with no proxy and no change to how people work. It scans historical data and new activity with detectors for PII, PHI, card data, credentials and source code, including OCR for images and full inspection of PDF, DOCX, XLSX and ZIP files.
When data matches a retention policy, Strac acts on the data itself:
Every action is written to an audit log and can be forwarded to your SIEM, with alerts in Slack or Microsoft Teams.
A retention schedule enforced in one system is a schedule with gaps. Strac applies the same detectors and the same rules everywhere regulated data lands.
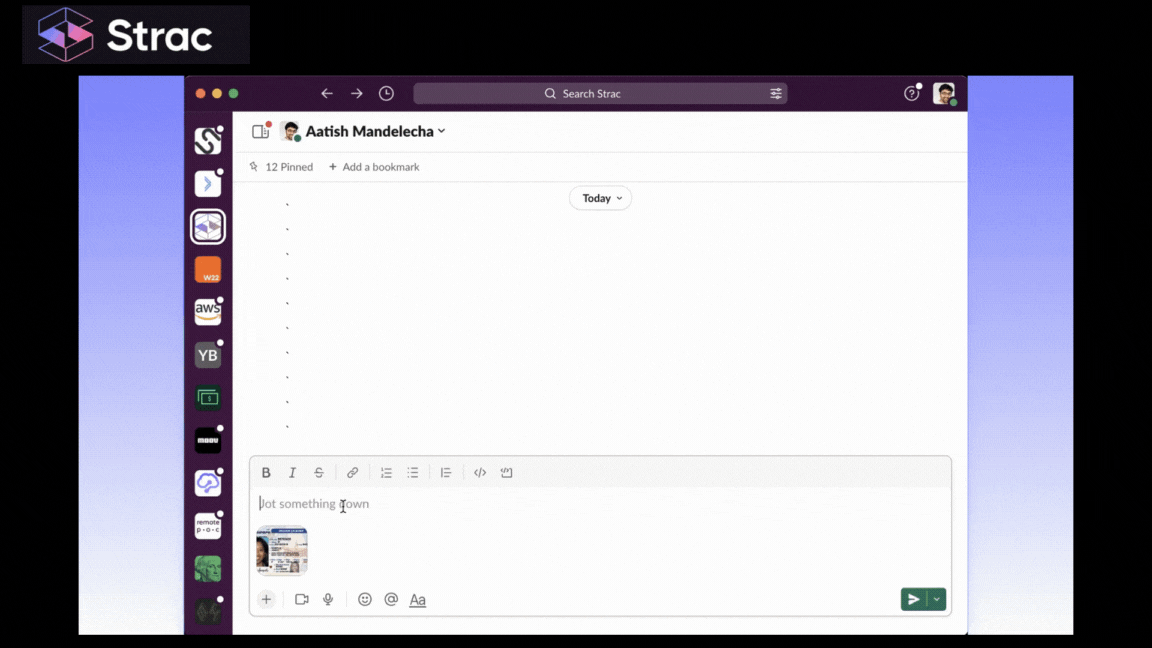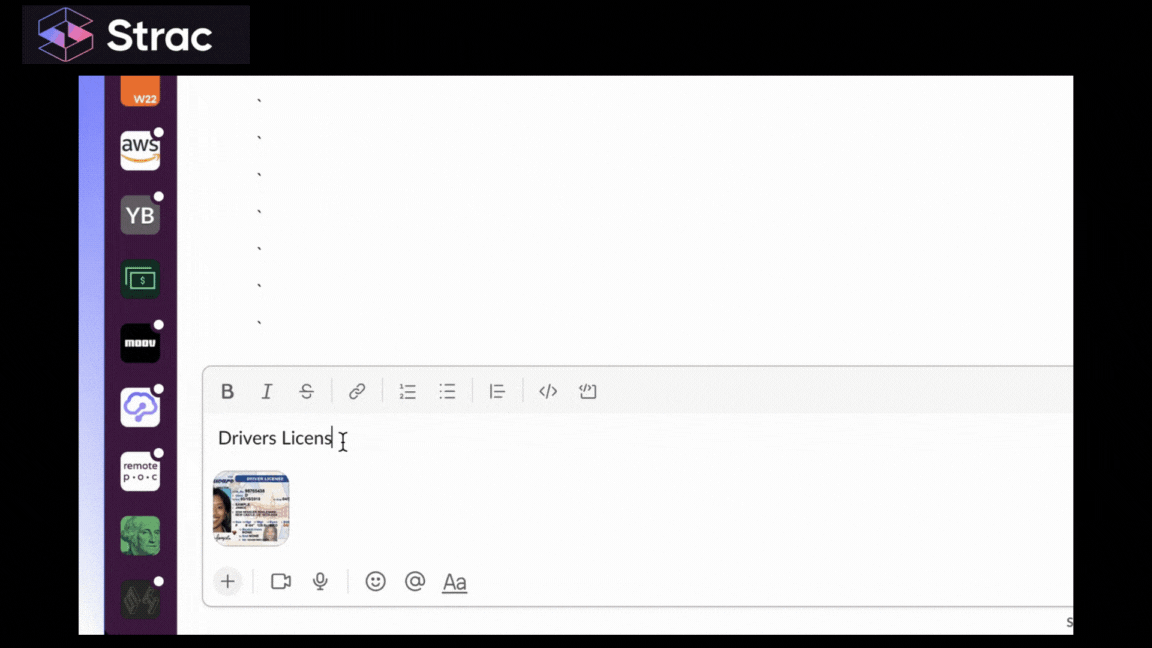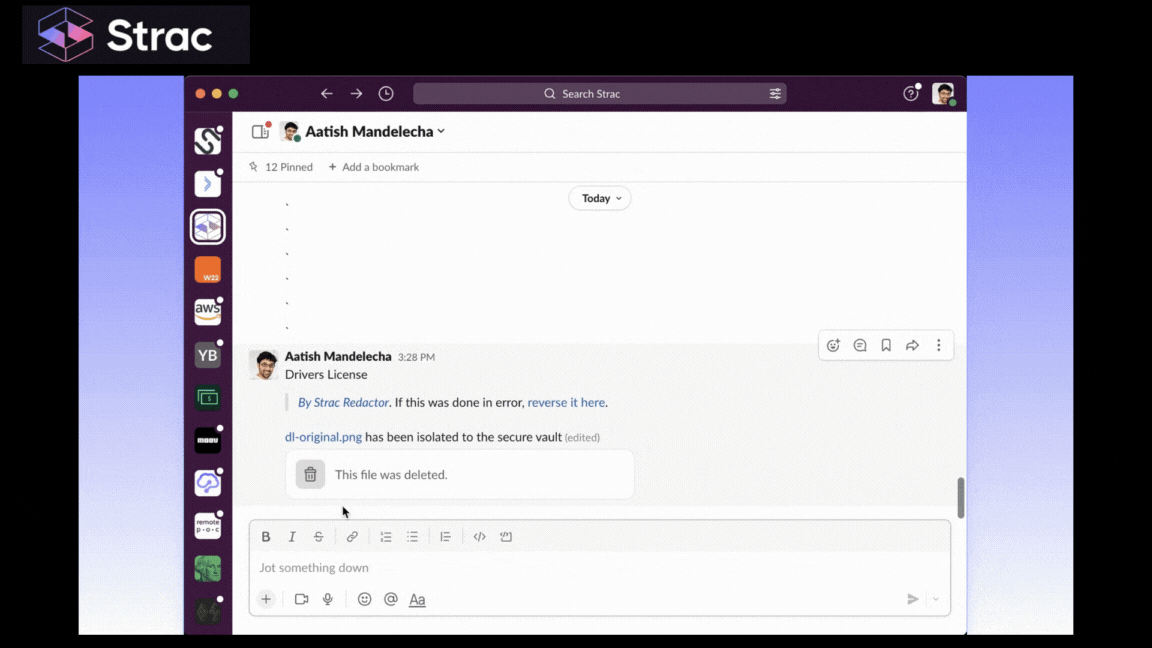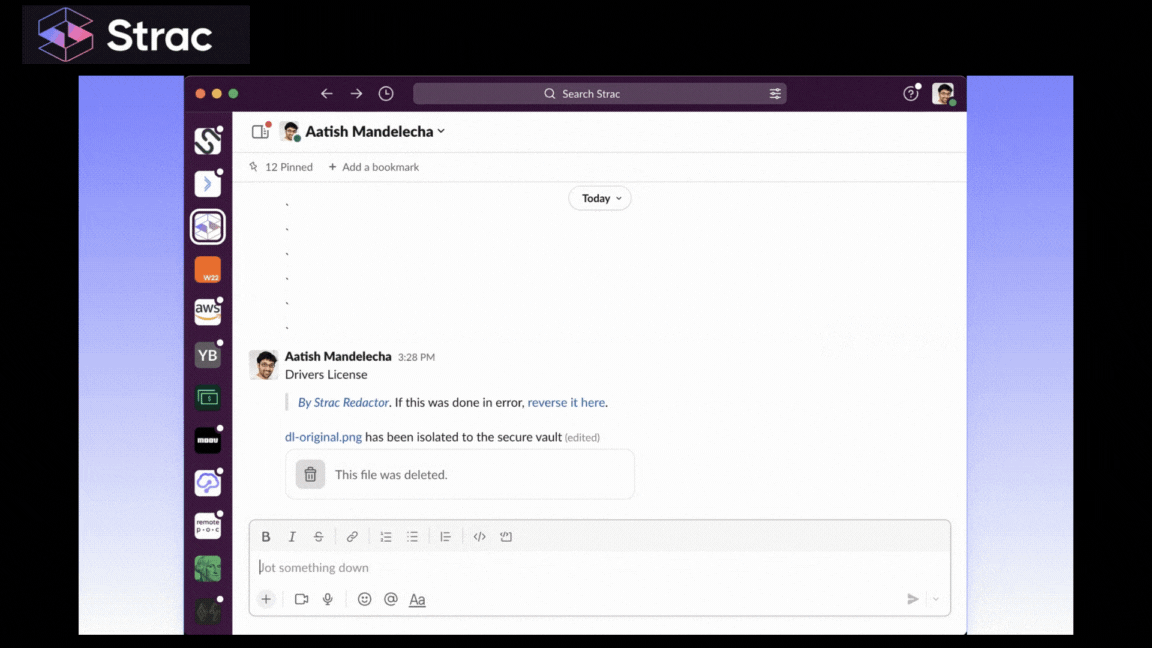

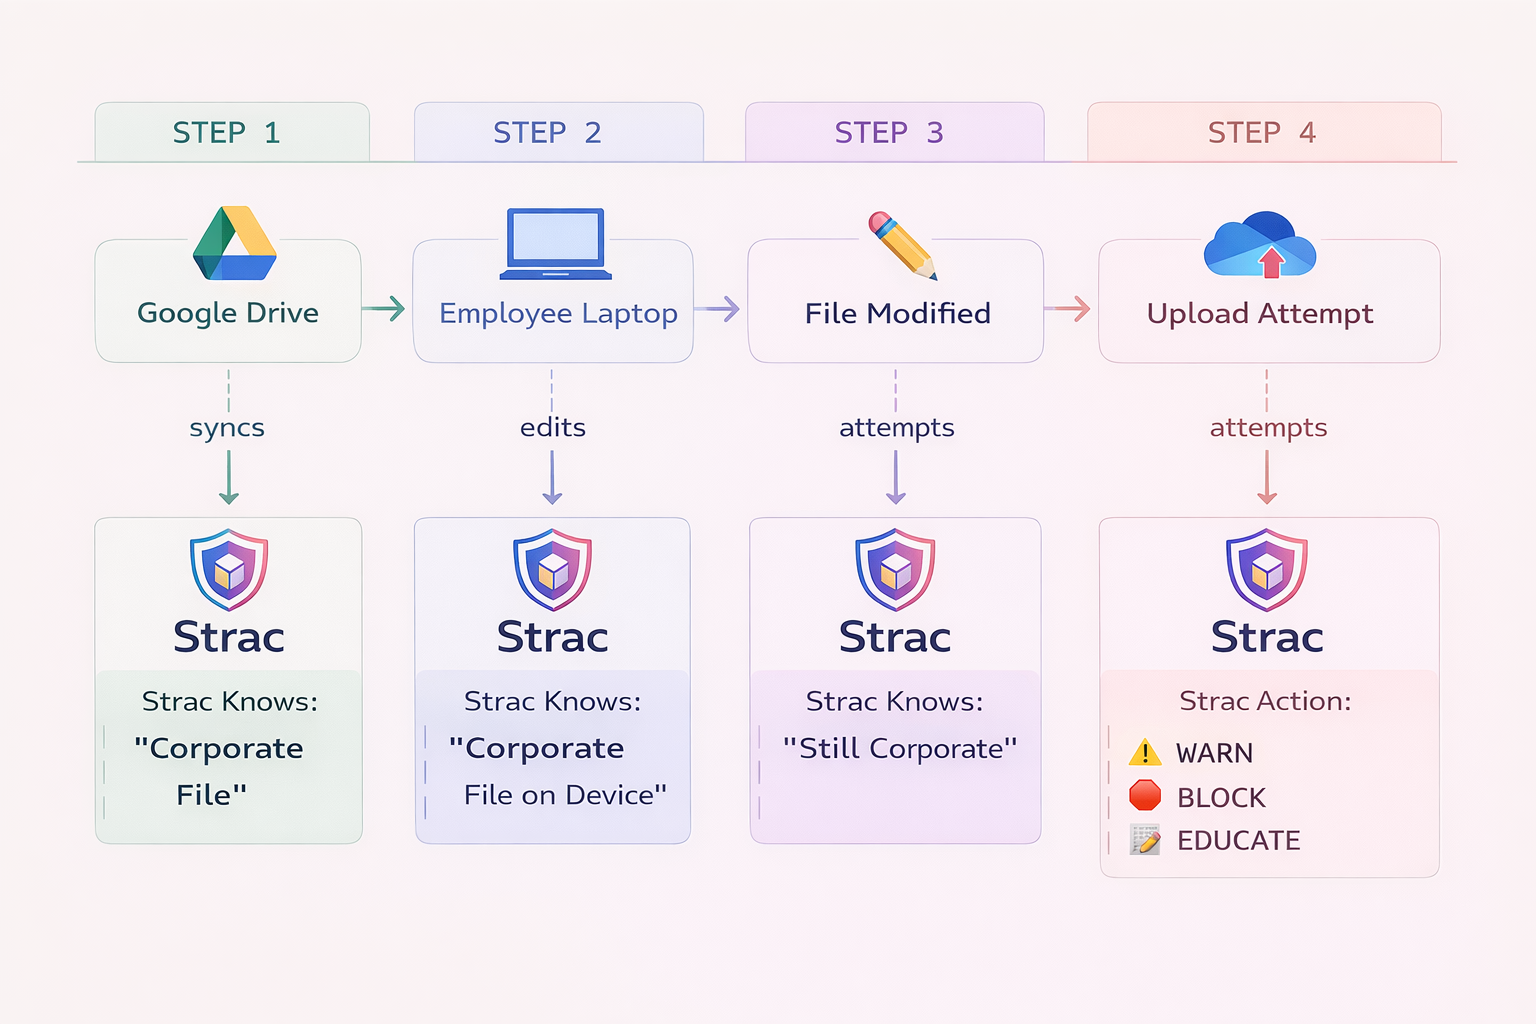
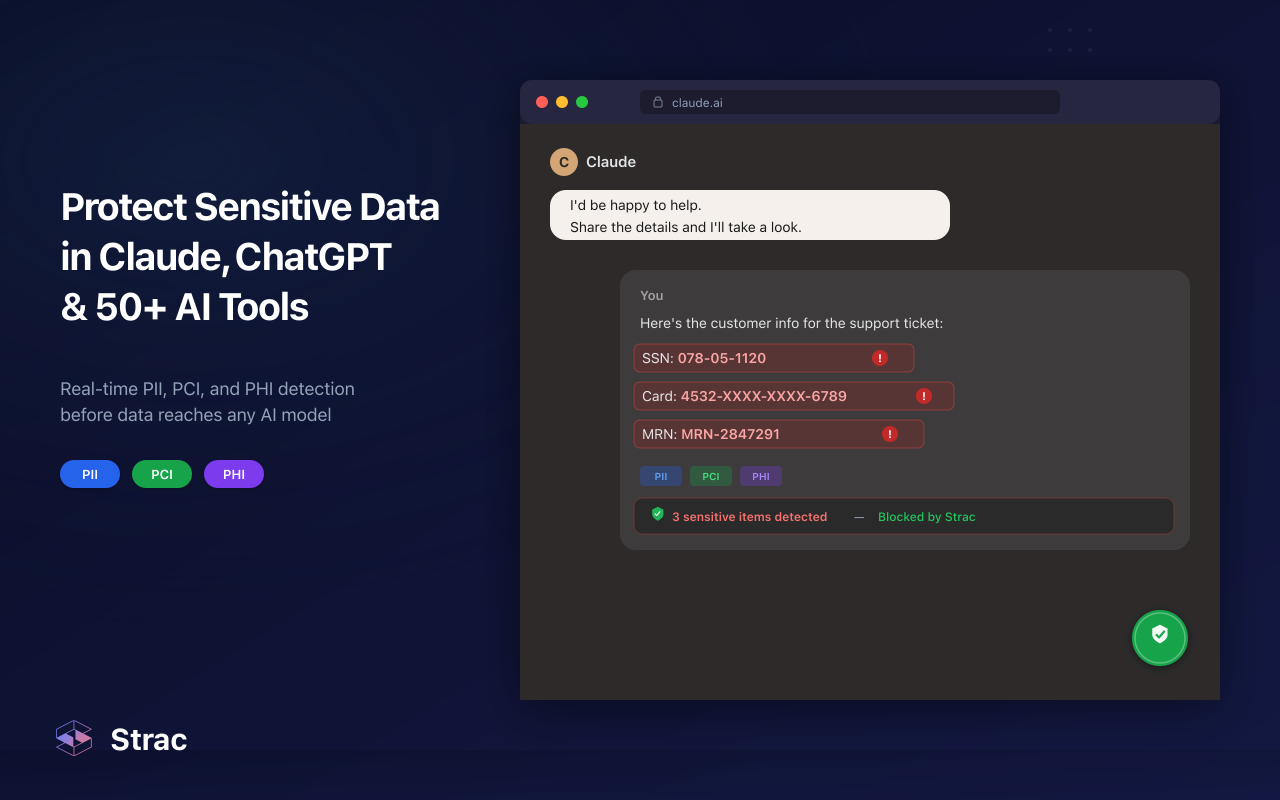
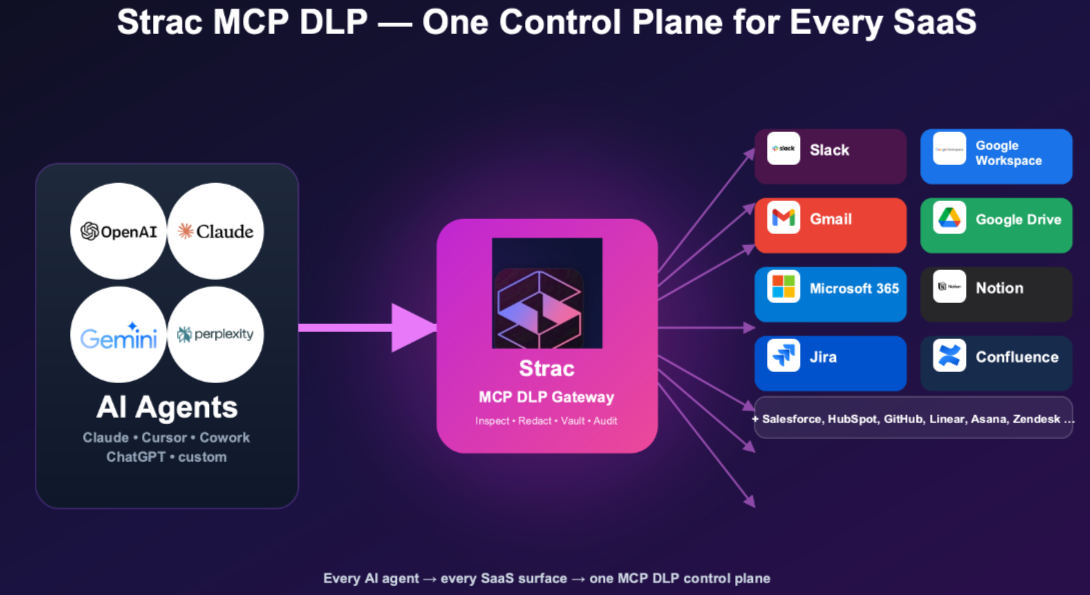
For audit evidence, Strac Comply runs continuous tests and maps one piece of evidence to SOC 2, ISO 27001, PCI DSS, GDPR and HIPAA at once, so the deletion log and the control test sit in the same place.
Related reading:
Retention schedules, app settings and annual purge jobs all fail eventually: a copy lands in a tool the schedule never listed, a blanket rule deletes the wrong record, an AI vendor keeps what you thought was gone. The data layer is the backstop. Classify every record by what it holds, redact or delete it on the clock its data type requires, and keep the log that proves it, and an old record never becomes a breach.
No. Data minimization limits what you collect and keep in the first place. A retention policy sets how long each record lives and when it is deleted. Minimization shrinks the pile; retention puts a clock on what remains. See data minimization.
They delete by age and location, not by content. A workspace rule cannot tell a card number from a meeting note, so it either keeps regulated data for years or deletes records you were required to keep. Content-aware deletion closes that gap.
Yes, by redacting rather than deleting. Strac removes the card number, Social Security number or health detail from the message or ticket and leaves the conversation intact. The context stays useful; the regulated data is gone on schedule.
Only partly. Enterprise plans offer retention settings, but consumer accounts follow the vendor's terms, and court orders can override both. The reliable control is upstream: redact sensitive fields before the prompt is sent, so there is nothing to retain.
For the system of record, usually the longer keep rule, such as seven years for SOX or six for FINRA, with access limited to those who need it. Every other copy falls under the delete rules. See data loss prevention compliance for how evidence maps across frameworks.
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath









Customers include