Mercedes-Benz Dealer ISO 27001 and TISAX Requirement
What Mercedes-Benz requires from dealerships: ISO 27001 or TISAX AL2, the 30 September 2026 deadline that has now passed, how to choose between the two, and the controls expected.
Mercedes-Benz requires dealerships to prove an effective information security programme through ISO 27001 certification or a TISAX AL2 label. Equivalent recognised programmes are also accepted.
The stated deadline was 30 September 2026, which has now passed.
Both paths are genuinely accepted, so the choice is about which asset is worth more to the dealership afterwards.
TISAX AL2 is the narrower, lighter lift. ISO 27001 is broader and reusable across franchises, lenders and insurers.
The expectations are ordinary: an accountable owner, a written programme that matches reality, monitoring and logging, risk assessments, access reviews, incident response, and training.
The agreement decides this, not a judgement about which standard is better.
The requirement, stated plainly
Mercedes-Benz asks its dealers to demonstrate that an information security programme is actually operating, and accepts either ISO 27001 certification or a TISAX AL2 label as the proof. Equivalent recognised programmes are also accepted. The deadline that circulated through the network was 30 September 2026.
That date has passed. If you are reading this having not started, the useful framing is not that you have missed a window but that you are now in a remediation conversation rather than a preparation one, and those are won by showing a credible programme in motion.
It is worth being clear about what kind of obligation this is. It is contractual, sitting under the dealer agreement, not a statute. There is no regulator issuing fines. The exposure is to the franchise relationship, which for most dealer principals is the more serious of the two.
✨ ISO 27001 or TISAX AL2: how to choose
Because both are accepted, this is a genuinely free choice, and it should be made on what the dealership gets to keep.
TISAX AL2
ISO 27001
Scope
Automotive-specific, built on ISO 27001 controls
General-purpose information security management
Effort
Narrower, and often described as the lighter lift for a retail dealer
Broader, more management system to build and maintain
How the result is shared
A label in the ENX portal that the manufacturer looks up
A certificate you can send to anyone who asks
Useful elsewhere
Mainly with automotive customers
Banks, insurers, other franchises, any enterprise customer
Prerequisites before you can start
Register with ENX and secure an accredited assessment provider
Engage a certification body, no central registration needed
Validity
Three years
Three years with annual surveillance audits
The honest default for a single-franchise dealership under time pressure is TISAX AL2, because it is the narrower project. The honest default for a multi-franchise group, or any dealership that also wants to answer its lender and its cyber insurer with the same work, is ISO 27001. We go deeper on that trade-off in TISAX vs ISO 27001, and the TISAX certification guide covers what a TISAX project actually involves.
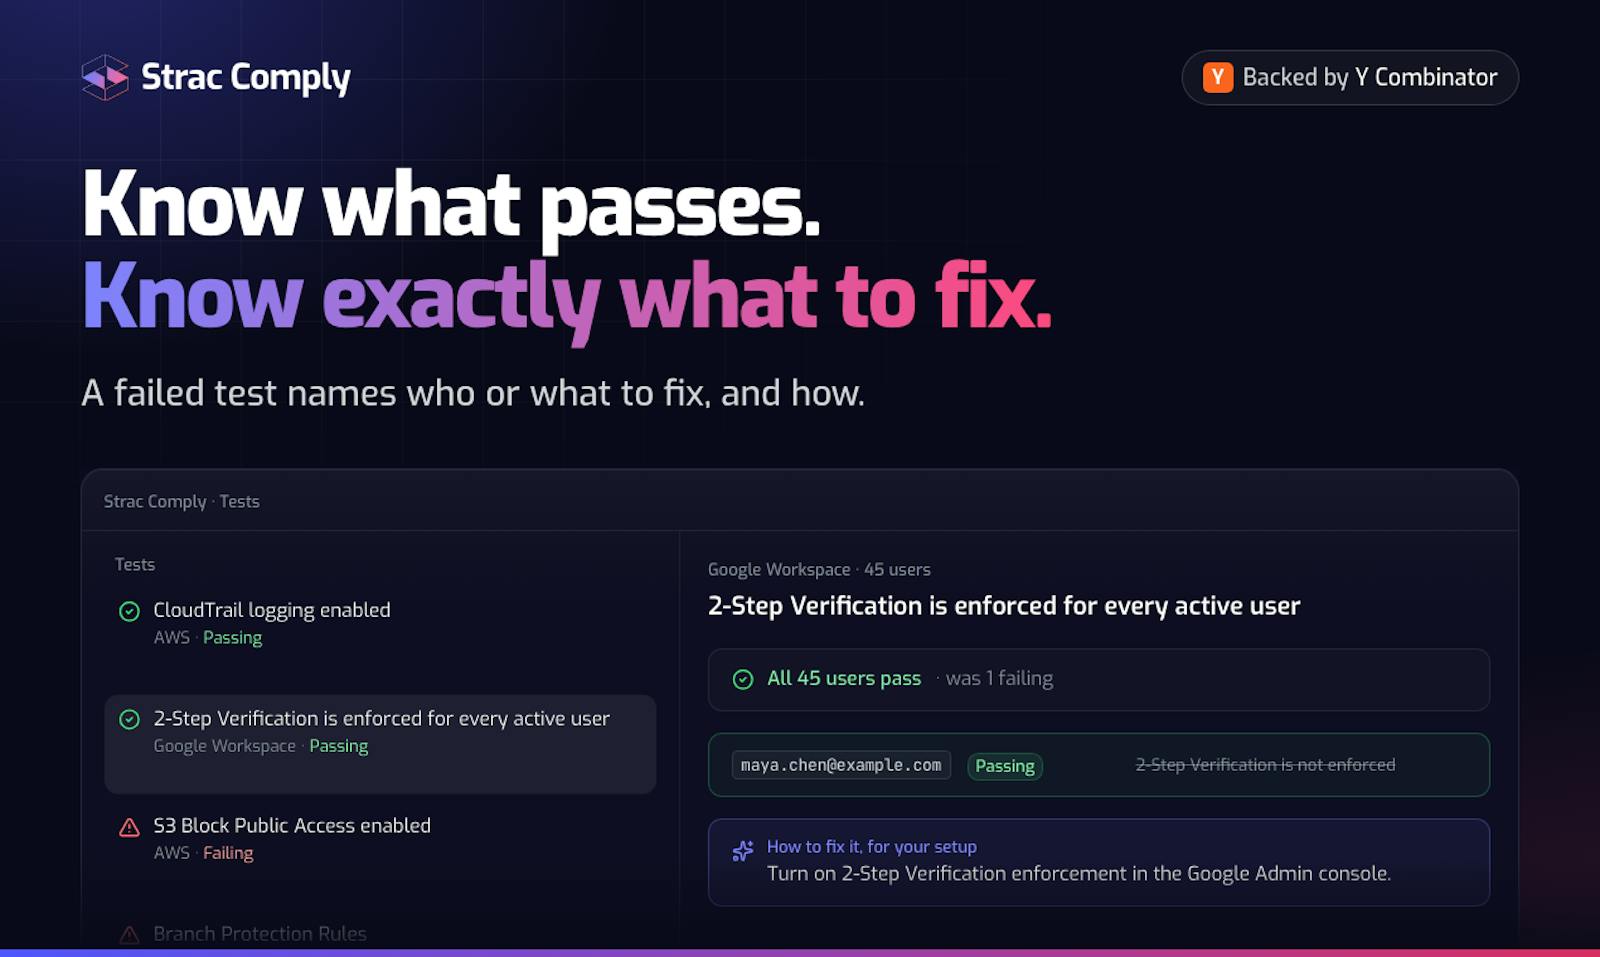
Readiness against each framework in one view, rather than a spreadsheet per auditor.
✨ What a dealership is actually being asked to have
Stripped of framework language, the expectations are these.
Expectation
What it looks like in a dealership
An accountable owner
One named person responsible for dealership security. Not 'IT', not the vendor, a person.
A written programme
Policies that describe how this dealership genuinely operates. The common failure is a downloaded template describing a business nobody recognises.
Monitoring and logging
Continuous logging, retained, and actually looked at. An assessor will ask who reviews it and when.
Regular risk assessments
A repeating exercise with recorded outcomes, not a one-off document from the year you started.
Ongoing access reviews
Periodic confirmation of who has access to the DMS, the CRM, financing systems and manufacturer portals, and removal of those who should not.
Incident response planning
A written plan, with named contacts, that someone has walked through.
Training
Delivered, recorded, and repeated. Completion records are evidence.
None of this is technically difficult. What makes it hard is that almost all of it recurs, and the proof is the point. A policy document is not evidence that access reviews happen. The completed access reviews are.
Continuous tests are what turn 'we have a policy' into the evidence an assessor accepts.
Why dealerships specifically
A dealership holds financing applications, credit files, driver licence scans, insurance details and service history, which is a richer set of personal and financial data than most small businesses of comparable size. It also holds a live connection into manufacturer systems, which makes a dealer group an attractive route into a much larger target.
That combination is why manufacturers have moved from accepting attestations to asking for assessed programmes. The question changed from whether you signed something to whether the controls are running.
✨ The fastest honest route from here
Five steps, in this order, and the first one is not buying software.
Name the accountable person. Confirm with your field contact which standard your agreement will accept and whether a programme in progress buys you room. Scope what is actually in play: which systems hold customer data, which staff touch them, which locations. Then build the control set and, critically, set up the evidence collection so it keeps producing proof rather than needing a scramble before each review. Only then book the assessment.
Most dealerships can run the first three steps this week. It is the fourth that decides whether this becomes an annual fire drill.
No demo gatekeeping, which matters when the deadline is already behind you.
✨ Getting a dealership compliant with Strac Comply
Both routes your agreement accepts are supported. ISO 27001 is included on every plan from $4,995 a year with no per-framework fee, and TISAX is supported alongside it, so the choice described above is not constrained by the tooling.
For a dealership the binding constraint is rarely understanding the controls. It is that nobody has time to run them. Access reviews across the DMS, the CRM, financing systems and manufacturer portals, training records, monitoring evidence: all of it recurs, and all of it is what an assessor asks to see.
That is the part Strac Comply automates. The AI Evidence Agent captures evidence from the systems a dealership actually uses, controls carry a named owner so accountability is real rather than nominal, and the same platform shows where customer and financing data is sitting.
ISO 27001 is included on every plan rather than priced as an add-on.
One control set, reported against each framework the dealership is asked for.
🎥 Watch Strac Comply skip the sales call
The same platform, the same control set, no demo gatekeeping before you can see it work.
🌶️ Spicy FAQs on the Mercedes-Benz dealer security requirement
What exactly does Mercedes-Benz require from dealers?
Proof of an effective information security programme, satisfied by either ISO 27001 certification or a TISAX AL2 label, with equivalent recognised programmes also accepted. The stated deadline was 30 September 2026. It is a contractual expectation under the dealer agreement rather than a government regulation, which changes who enforces it but not whether you need it.
The deadline has passed. What now?
Start immediately and be able to show a credible programme in progress. A dealership that registered, scoped its ISMS, assigned a named owner and is working through controls is in a very different conversation with its field team than one that has done nothing. The realistic fastest route is ISO 27001, because it does not require an ENX registration and an external assessment provider slot before you can begin.
Should a dealership choose ISO 27001 or TISAX AL2?
Both are accepted, so choose on what you want afterwards. TISAX AL2 is narrower and purpose-built for automotive, which is why it is often described as the lighter lift for a retail dealer operation. ISO 27001 is broader but it is an asset you can show your bank, your insurer and any other manufacturer whose franchise you hold. For a multi-franchise group, ISO 27001 usually wins on reuse alone.
Does this apply to dealers outside the US?
The requirement discussed here is the Mercedes-Benz USA dealer programme. Manufacturers run their own supplier and dealer security requirements by region, and the European automotive supply chain has used TISAX through the ENX portal for years. If you hold a franchise outside the US, ask your field contact which requirement applies to your agreement rather than assuming this one does.
What controls does a dealership actually have to put in place?
The named expectations are a designated person accountable for dealership security, a written information security programme that reflects how the dealership genuinely operates, continuous monitoring and logging, regular risk assessments, ongoing access reviews, incident response planning, and training. None of that is exotic. The common failure is a written programme that describes a dealership nobody works at.
Why are manufacturers suddenly asking dealers for this?
Dealerships hold exactly what an attacker wants: financing applications, credit files, driver licence scans, service records, and a live connection to manufacturer systems. A dealer group is also a soft entry point into the manufacturer's own network. The shift is from checklist attestations to evidence that a programme is operating.
Can we satisfy this without hiring a compliance team?
Yes, and most dealerships will have to. The work that consumes the time is evidence collection: access reviews, configuration screenshots, monitoring records, training completion. That is the part worth automating, because it recurs forever and it is where a thin programme gets exposed.
Customer story
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath
What exactly does Mercedes-Benz require from dealers?
Proof of an effective information security programme, satisfied by either ISO 27001 certification or a TISAX AL2 label, with equivalent recognised programmes also accepted. The stated deadline was 30 September 2026. It is a contractual expectation under the dealer agreement rather than a government regulation, which changes who enforces it but not whether you need it.
The deadline has passed. What now?
Start immediately and be able to show a credible programme in progress. A dealership that registered, scoped its ISMS, assigned a named owner and is working through controls is in a very different conversation with its field team than one that has done nothing. The realistic fastest route is ISO 27001, because it does not require an ENX registration and an external assessment provider slot before you can begin.
Should a dealership choose ISO 27001 or TISAX AL2?
Both are accepted, so choose on what you want afterwards. TISAX AL2 is narrower and purpose-built for automotive, which is why it is often described as the lighter lift for a retail dealer operation. ISO 27001 is broader but it is an asset you can show your bank, your insurer and any other manufacturer whose franchise you hold. For a multi-franchise group, ISO 27001 usually wins on reuse alone.
Does this apply to dealers outside the US?
The requirement discussed here is the Mercedes-Benz USA dealer programme. Manufacturers run their own supplier and dealer security requirements by region, and the European automotive supply chain has used TISAX through the ENX portal for years. If you hold a franchise outside the US, ask your field contact which requirement applies to your agreement rather than assuming this one does.
What controls does a dealership actually have to put in place?
The named expectations are a designated person accountable for dealership security, a written information security programme that reflects how the dealership genuinely operates, continuous monitoring and logging, regular risk assessments, ongoing access reviews, incident response planning, and training. None of that is exotic. The common failure is a written programme that describes a dealership nobody works at.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.