✨ What Is Netwrix Endpoint Protector (Formerly CoSoSys)?
Netwrix Endpoint Protector is an endpoint data loss prevention product that started life as Endpoint Protector by CoSoSys, a Romanian vendor best known for USB and peripheral device control. Netwrix acquired CoSoSys on February 1, 2024, and the product now ships under the Netwrix brand. If you are searching for CoSoSys Endpoint Protector, Endpoint Protector 4, or My Endpoint Protector, these all refer to the same lineage.
Per the Netwrix product page, the current product is organised around four capabilities:
- Device and Port Control, enforcing access policies for USB drives, removable media and, in Netwrix's words, "45+ peripheral devices"
- Content-Aware DLP, inspecting sensitive data moving through applications, browsers, email and AI tools
- Data Discovery and Remediation, finding regulated data sitting on endpoints and removable media
- USB Encryption, with FIPS 140-3 validated encryption, remote wipe and password reset
It runs on Windows, macOS and Linux. Netwrix claims "full DLP feature parity" across the three, and the acquisition release describes "functional parity across Windows, macOS and Linux endpoints." Deployment is either SaaS or a single on-premises virtual appliance. For background on how this class of tool works, see our guide to endpoint data loss prevention and what a DLP endpoint agent actually does.
✨ Netwrix Endpoint Protector Pricing in 2026
Netwrix does not publish Endpoint Protector pricing. The product page offers "Request pricing" and "Get a demo" rather than a price, and the free 14-day trial advertised on that page is for Netwrix 1Secure, their unified platform, rather than a self-serve Endpoint Protector purchase. Historically CoSoSys sold Endpoint Protector in modules, so what you pay depends on which of the four capabilities you license and for how many endpoints.
That modular, quote-only model is the single most common complaint we hear from teams evaluating it. You cannot size the budget without a sales conversation, and adding content-aware DLP or encryption later is a new line item rather than a feature you already own. If you want to see pricing before you talk to anyone, that is worth weighing. Our DLP pricing guide covers how the rest of the market prices.
✨ What Endpoint Protector Does Well
Credit where it is due. Endpoint Protector is a mature product with real strengths, and for some buyers it is the correct answer.
- Device and port control depth. This is its heritage and it shows. Granular control over USB, removable media and peripheral classes is better developed than in many broader platforms. If your core requirement is USB blocking, it does that job properly.
- Genuine Linux support. Most DLP vendors treat Linux as an afterthought. Endpoint Protector does not. If you have a real Linux estate, see our Linux DLP guide for what to require.
- An on-premises and air-gapped story. The single virtual appliance model suits defence, manufacturing and other environments that cannot send telemetry to a vendor cloud.
- FIPS 140-3 USB encryption built in rather than bolted on.
✨ Where Endpoint Protector Falls Short
The limitation is structural rather than a list of missing checkboxes. Endpoint Protector protects the endpoint. In 2026 most sensitive data does not leave through a USB port. It leaves through a browser tab, a SaaS app you do not control, or a prompt box.
- No agentless SaaS or cloud coverage. If a contractor shares a Google Drive folder publicly or a Salesforce export lands in a personal inbox, an endpoint agent never sees it. That work needs cloud and SaaS DLP, which is a different architecture.
- GenAI is the new exfiltration path. Pasting customer records into a chatbot is the dominant modern leak, and it needs purpose-built AI DLP plus visibility into which AI tools employees actually adopted.
- Nothing for AI agents. Tool calls through MCP servers pull real records out of real systems. That surface needs MCP DLP, and endpoint agents have no view of it.
- Quote-only pricing and a modular licence that grows as you add capability.
✨ The 8 Best Endpoint Protector Alternatives in 2026
1. Strac, the best Endpoint Protector alternative overall
Strac is the strongest replacement because it does the endpoint job Endpoint Protector does and then keeps going into the places your data actually goes. One lightweight agent covers Windows, macOS and Linux, and the same platform covers SaaS, cloud, browsers, GenAI and AI agents without an agent.
Strac governs 14 exits on the endpoint, and every one is set independently to Audit, Warn, Block or Off, so you can roll out quietly and tighten later instead of breaking workflows on day one.
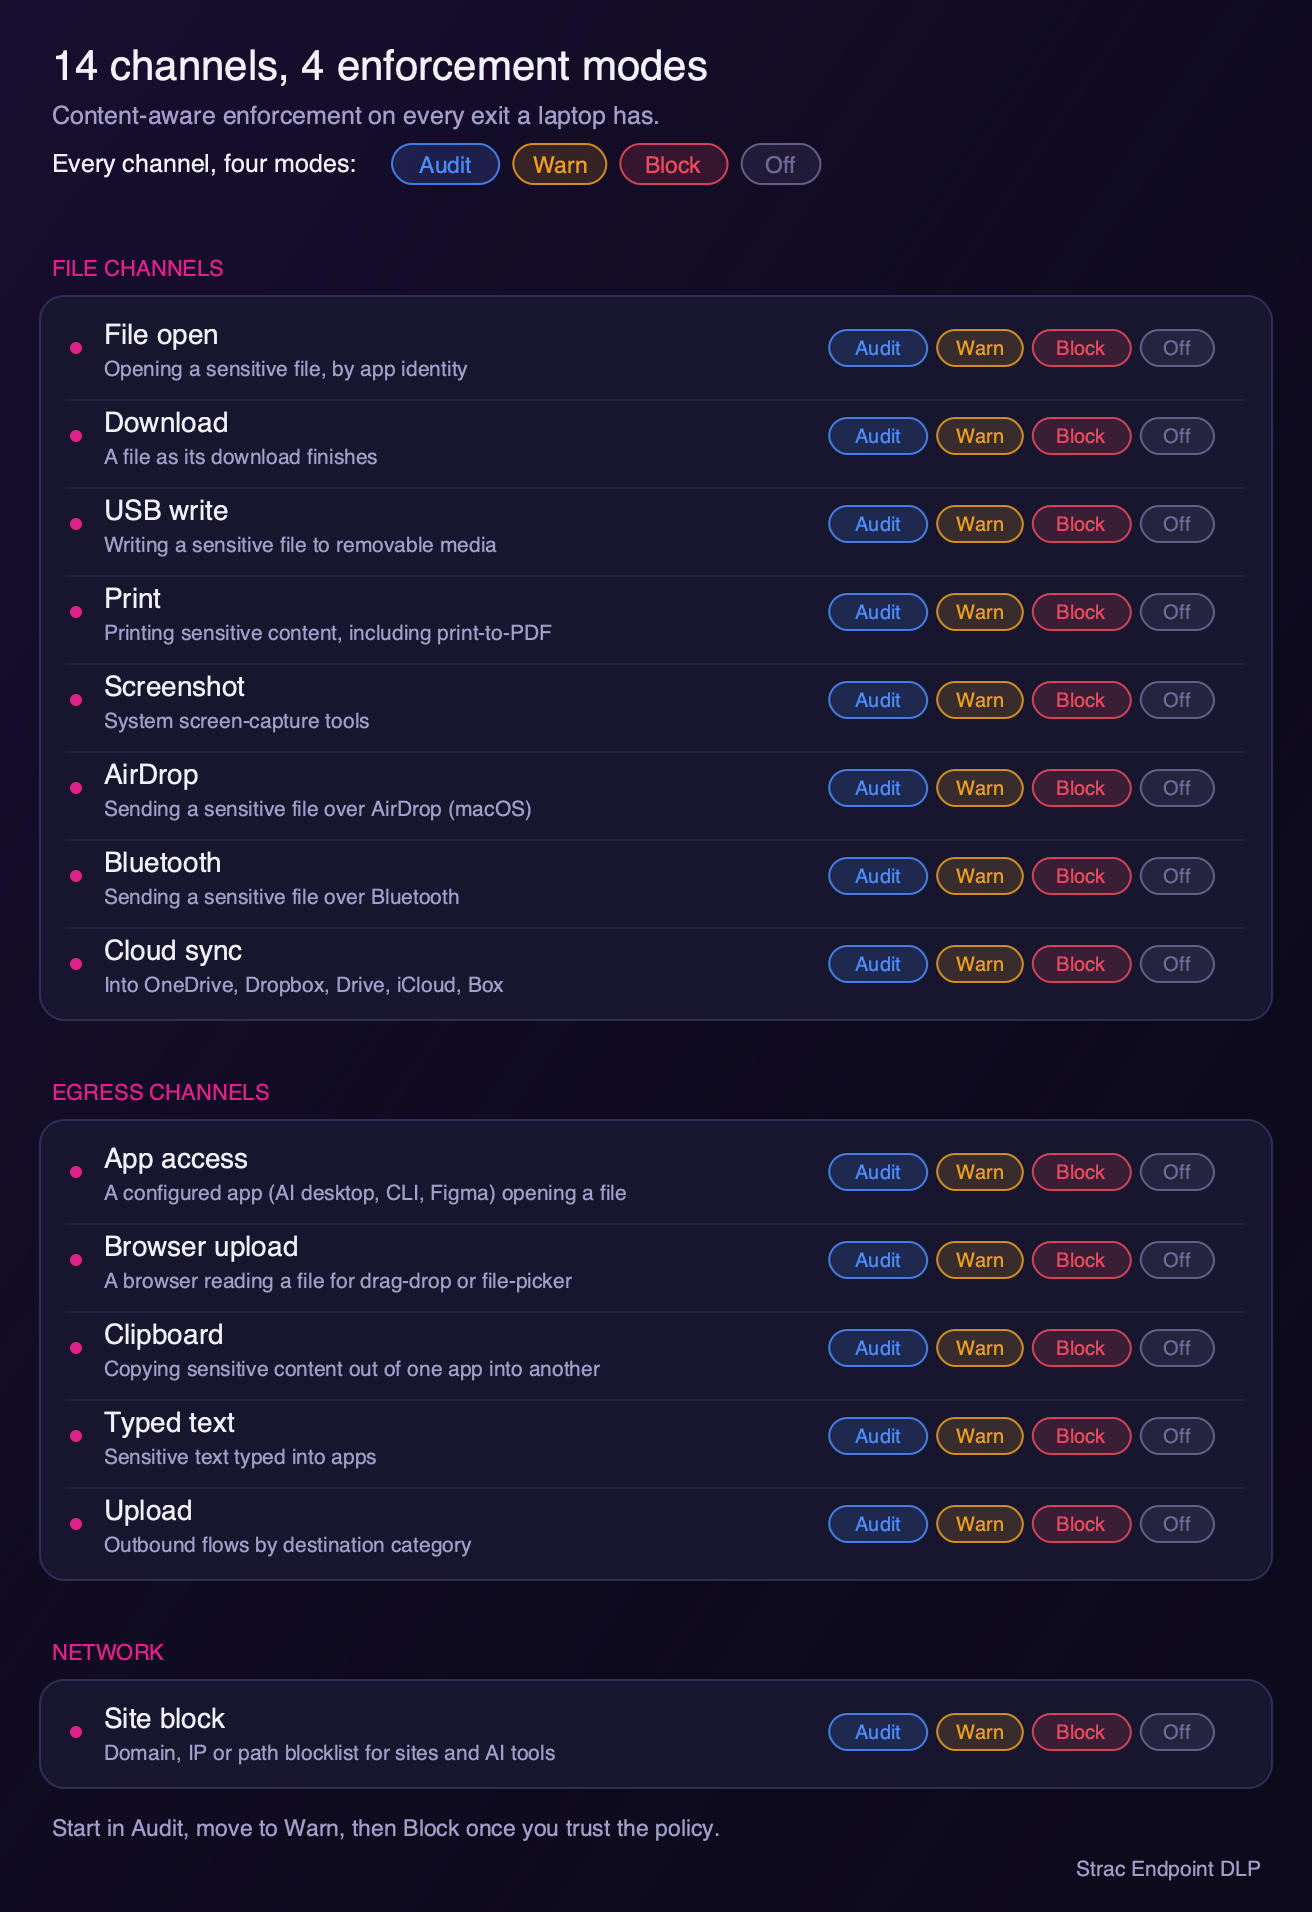
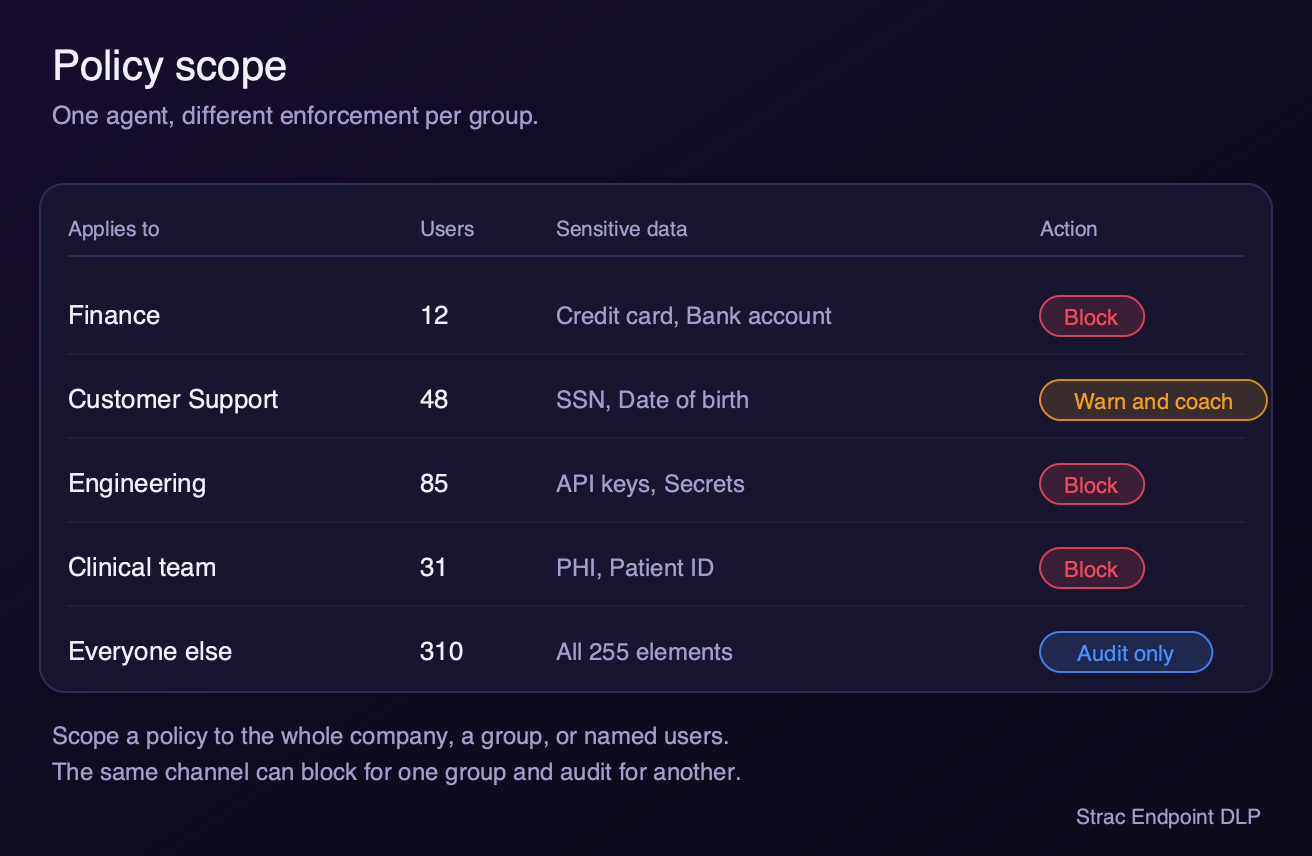
It is content aware, so it inspects the actual data (SSN, card number, PHI, API key, source code) across 255 detected elements including 160 national ID formats, and stops the sensitive file or action rather than the whole application. Policies scope to the whole company, a group, or a handful of named users, and the same channel can block for Finance while silently auditing everyone else.
Strac also runs in your own AWS or Azure tenant if regulated data cannot leave your environment, which covers much of what buyers want from an appliance without running the appliance. See the Strac Endpoint DLP overview.
2. Microsoft Purview Endpoint DLP
The default if you are deep in Microsoft 365 and already hold E5 licences, since the agent is built into Windows. It is Windows-centric, leans toward block-only enforcement, and is weaker on browser paste and GenAI. Full detail in our Microsoft Purview endpoint DLP guide.
3. Forcepoint DLP
A long-standing enterprise suite with deep policy capability and a correspondingly heavy deployment. Common on shortlists where Endpoint Protector appears. See Forcepoint alternatives.
4. Trellix DLP
The former McAfee DLP line, mature on endpoint and well understood by large security teams, with the tuning burden that comes with it. See how we cut Trellix false-positive noise.
5. Symantec DLP (Broadcom)
The most established enterprise DLP estate in the market, strong on detection breadth, slow to deploy and change. See Symantec DLP alternatives.
6. Digital Guardian (Fortra)
Endpoint-first with strong data lineage and insider-risk framing, which puts it closest to Endpoint Protector in philosophy. See Digital Guardian alternatives.
7. CrowdStrike Falcon Data Protection
Attractive when you already run the Falcon agent and want data protection without deploying another one. Narrower DLP depth than a dedicated platform. See CrowdStrike DLP.
8. Zscaler and Netskope
Cloud-delivered inline DLP that inspects traffic rather than the device. Good at egress to the internet, blind to what happens locally, which is the mirror image of Endpoint Protector's limitation. See Zscaler alternatives and Netskope alternatives.
✨ Endpoint Protector Alternatives Compared
| Platform | Endpoint agent | Agentless SaaS / cloud | Browser + GenAI | AI agent (MCP) | Published pricing |
|---|
| Strac | Windows, macOS, Linux | ✅ 50+ apps | ✅ | ✅ | Contact for DLP |
| Netwrix Endpoint Protector | Windows, macOS, Linux | ❌ | Partial | ❌ | ❌ Quote only |
| Microsoft Purview | Windows-centric | Microsoft 365 only | Partial | ❌ | E5 licensing |
| Forcepoint DLP | Windows, macOS | Limited | Partial | ❌ | ❌ Quote only |
| Trellix DLP | Windows, macOS | Limited | ❌ | ❌ | ❌ Quote only |
| Symantec DLP | Windows, macOS, Linux | Limited | ❌ | ❌ | ❌ Quote only |
| Digital Guardian | Windows, macOS, Linux | Limited | Partial | ❌ | ❌ Quote only |
| CrowdStrike | Windows, macOS | ❌ | Partial | ❌ | ❌ Quote only |
Primary source for Endpoint Protector capabilities and platform support: Netwrix Endpoint Protector product page, verified November 2026.
✨ Endpoint Protector on Mac, Windows and Linux
Cross-platform parity is one of Endpoint Protector's genuine selling points, and it is the reason it shows up on so many Mac-heavy shortlists. Netwrix states functional parity across all three operating systems.
Strac matches that and adds the exits Mac teams actually worry about. On macOS that means AirDrop and Bluetooth transfers alongside USB writes, iCloud and other cloud sync folders, print, screenshots, browser uploads, clipboard, typed text and full site or AI tool blocking by domain. Our platform guides cover each: Mac DLP, Windows DLP and Linux DLP.
✨ How Strac Replaces Endpoint Protector
The practical difference is what happens when a policy fires. Endpoint Protector is built to allow or deny. Strac can also remediate in place, redacting the sensitive values and letting the legitimate work continue, which is what keeps security teams from being switched off by the business.

Three things to check on any replacement shortlist:
- Does it cover the exits you actually have? USB matters, but so do browser uploads, clipboard, AirDrop, cloud sync and GenAI prompts.
- Does one policy follow the data off the device? If your endpoint tool and your SaaS tool are different products with different rules, you will maintain both forever.
- Can you phase it in? Audit, then Warn, then Block, per channel and per group, is the difference between a rollout and an incident.
If you are still scoping the category, start with endpoint DLP solutions or compare the whole market in the best DLP tools.