October 13, 2026

8
min read
GDPR Compliance Cost: What It Actually Costs in 2026
GDPR compliance cost ranges from ~$10K to $100K+ depending on size, DPO, and tooling. Full breakdown, and how Strac automates data mapping, RoPA, and DSAR to cut it.
Short answer: GDPR compliance cost runs from about $10,000 for a lean small-business program to $100,000 or more for a mid-size enterprise, across a DPO or consultant, data mapping and RoPA, DSAR tooling, Article 32 security controls, and legal work. There is no GDPR certificate to buy, so most of the cost is tooling and staff time, which is exactly where Strac cuts it.

"GDPR compliance cost", "GDPR compliance software pricing", and "cost of GDPR compliance" come down to the same stack. Here are the line items with typical market ranges and what changes when the data work is automated.
| Cost component | Typical market range | With Strac |
| Data Protection Officer (DPO) or consultant | $10,000 (fractional) to $120,000 / year | Still your own role |
| Data mapping, inventory, and RoPA | $10,000 to $40,000 | Automated by Strac DSPM (sensitive data discovery) |
| DSAR intake and fulfillment tooling | $5,000 to $30,000 / year | Strac locates the subject data across SaaS and cloud |
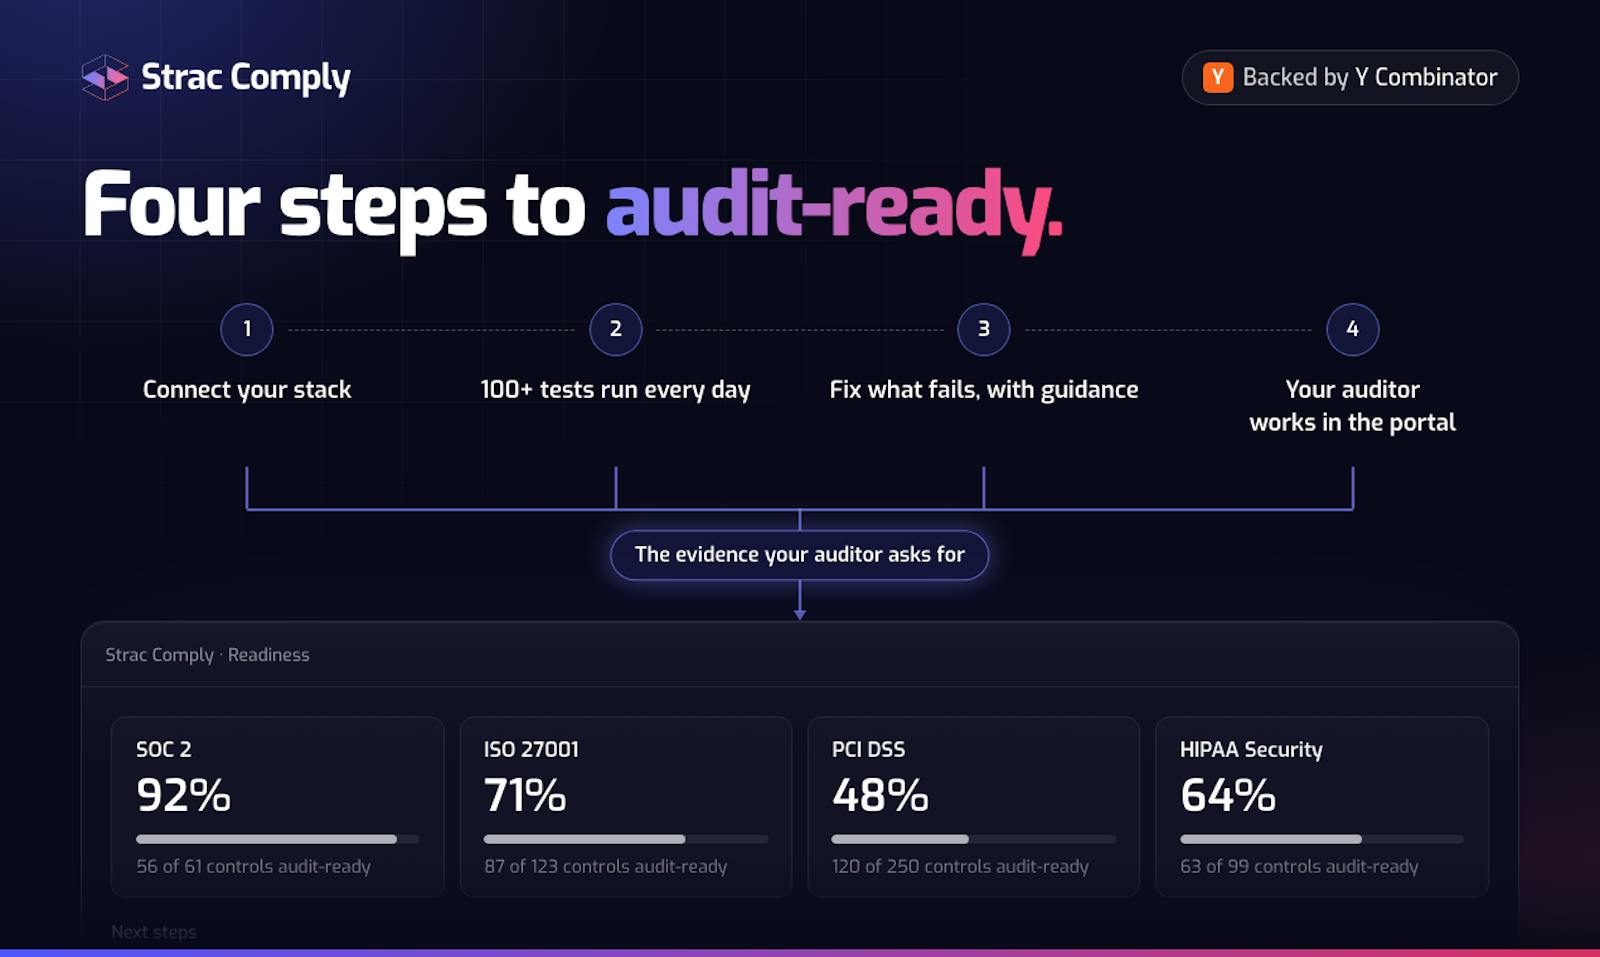
| Security controls (GDPR Article 32) | $15,000 to $50,000 | Strac Comply runs the ISO 27001 program from $4,995 / year |
| Legal review, policies, and staff training | $5,000 to $25,000 | Still external |
| Typical first-year total | $10,000 to $100,000+ | Strac removes the data-mapping, RoPA, and DSAR line items and runs Article 32 security from $4,995 |
GDPR compliance cost scales with how much personal data you process and how many systems hold it.
| Company size | Typical first-year GDPR cost |
| Startup / small business (under 25 employees) | ~$10,000 to $25,000 |
| Mid-size (25 to 250 employees) | ~$25,000 to $60,000 |
| Enterprise (250+ employees) | $60,000 to $150,000+ |
The audit-style fee people expect does not exist for GDPR. The spend is ongoing: knowing where personal data lives, keeping your Record of Processing Activities (RoPA) current, answering DSARs on time, and proving Article 32 security. Those recurring tasks, not a one-off exam, are what make GDPR expensive, and they are the parts a data-security platform automates.
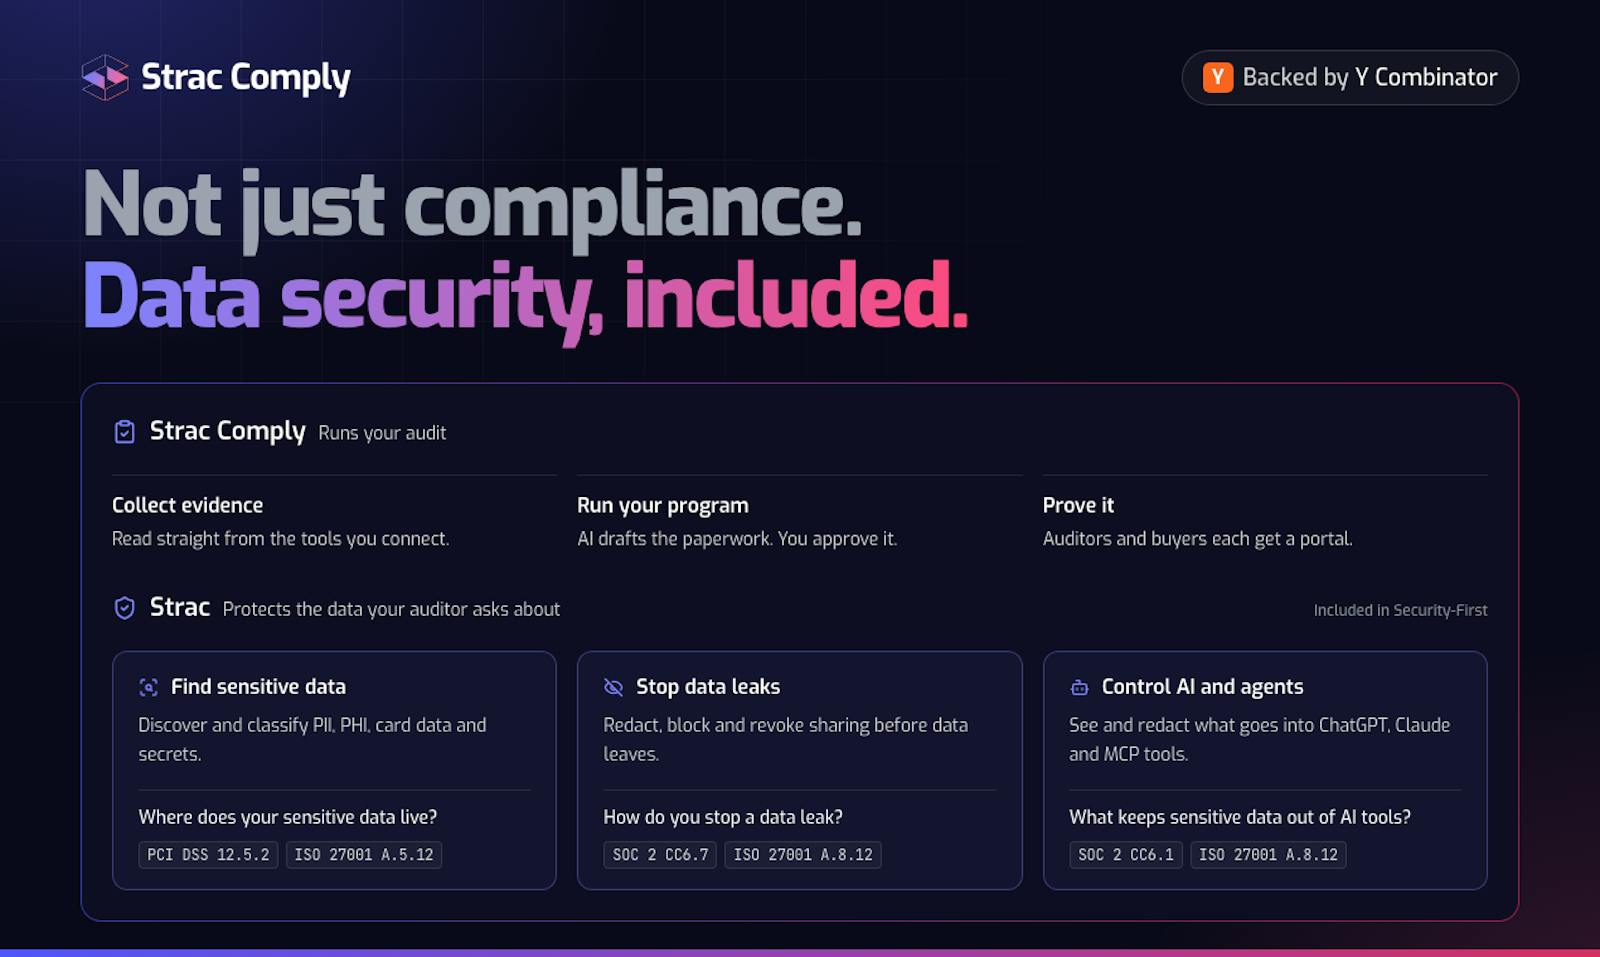
One honest clarification, since this is on Strac.io. Strac is a data-security platform, DSPM and DLP, that automates the GDPR data work. There is no official GDPR certification, and Strac does not sell one. Strac Comply (from $4,995 per year) automates the ISO 27001 security program behind GDPR Article 32; it covers SOC 2, ISO 27001, PCI DSS, HIPAA, and NIST CSF, not a standalone "GDPR" audit. So $4,995 is the price of the security program, not a GDPR certificate.
Book a Strac demo to see automated data discovery, RoPA, and DSAR support on your own data, or start Strac Comply from $4,995 per year to run the ISO 27001 security program GDPR Article 32 requires.
GDPR compliance cost ranges from about $10,000 for a small company doing it leanly to $100,000 or more for a mid-size enterprise, driven by a DPO or consultant, data mapping and RoPA, DSAR tooling, Article 32 security controls, and legal work. The ongoing data-mapping, RoPA, and DSAR work is where Strac removes most of the recurring cost.
No. Unlike SOC 2 or ISO 27001, there is no single official GDPR certificate you buy. GDPR is a regulation you demonstrate compliance with through records (like a RoPA), security controls, and DSAR processes. That is why most GDPR cost is tooling and staff time, not an exam fee.
For most teams it is the ongoing data work: finding where personal data lives, keeping a Record of Processing Activities (RoPA) current, and fulfilling data subject access requests. Strac automates all three with sensitive data discovery across SaaS, cloud, and endpoints, which is why it cuts the recurring GDPR bill.
Strac is a data-security platform (DSPM and DLP). It discovers and classifies personal data automatically, keeps your data inventory and RoPA current, and pinpoints where a subject's data sits for DSARs. Strac Comply then automates the ISO 27001 security program that satisfies GDPR Article 32, from $4,995 per year. Strac is not a GDPR certification product, because none exists.
Only some organizations must appoint a DPO (for example, large-scale monitoring or special-category processing). Many use a fractional DPO or consultant for roughly $10,000 or more per year. The DPO cost is separate from the tooling and security costs Strac addresses.