October 10, 2026

9
min read
How Much Does ISO 27001 Certification Cost? 2026 Breakdown
ISO 27001 certification cost runs $25K to $90K+ in year one. Full breakdown of the audit and readiness cost, and how Strac Comply automates it from $4,995.
Short answer: A traditional ISO 27001 certification cost is roughly $25,000 to $90,000 or more in year one once you add readiness consulting, a compliance platform, the Stage 1 and Stage 2 audit by an accredited certification body, annual surveillance audits, and a penetration test. Strac Comply automates the readiness, Annex A mapping, and evidence from $4,995 per year, so the only separate line left is the accredited certification body’s audit fee. This post breaks down every line item so you can compare apples to apples.
One thing to keep straight, because this lives on Strac.io. The prices here are Strac Comply prices: $4,995 for the platform, $8,995 once the CPA audit is folded in, and $12,995 with a penetration test and Strac DLP for Slack, Google Workspace, and AI tools added. The full Strac data-security suite, endpoint DLP, cloud DSPM, and MCP DLP, is a separate purchase, so do not read $4,995 as the cost of Strac’s DLP or DSPM.
"ISO 27001 cost" and "ISO 27001 certification cost" are several separate line items quoted separately. Here is the full stack with typical market ranges and what each costs inside Strac Comply.
| Cost component | Typical market range | With Strac Comply |
| Readiness / gap assessment and consulting | $10,000 to $30,000 | Included (guided, in-app) |
| Compliance automation platform | $7,500 to $25,000 / year | $4,995 / year (all 5 frameworks) |
| Stage 1 + Stage 2 audit by an accredited certification body | $10,000 to $40,000 | Separate (must be an accredited body) |
| Annual surveillance audits | $5,000 to $15,000 / year | Evidence stays audit-ready year round |
| Penetration test | $4,000 to $15,000 | Included on $12,995 Security-First (or $3,995 add-on) |
| Typical first-year total | $25,000 to $90,000+ | $4,995 for automation + the accredited CB audit fee |
For the control-by-control detail, see our ISO 27001 compliance software guide.
ISO 27001 certificates must be issued by an accredited certification body, so that audit fee is always separate from any tool, and no vendor can include it. What Strac Comply removes is the expensive, recurring part: readiness consulting, the automation platform, and manual evidence collection. Year one carries the Stage 1 and Stage 2 audit; years two and three are lighter surveillance audits, which stay cheap when your Annex A evidence is collected automatically. See our ISO 27001 compliance software guide.
From $4,995 a year, Strac Comply covers the full ISO 27001 lifecycle, not just a checklist.
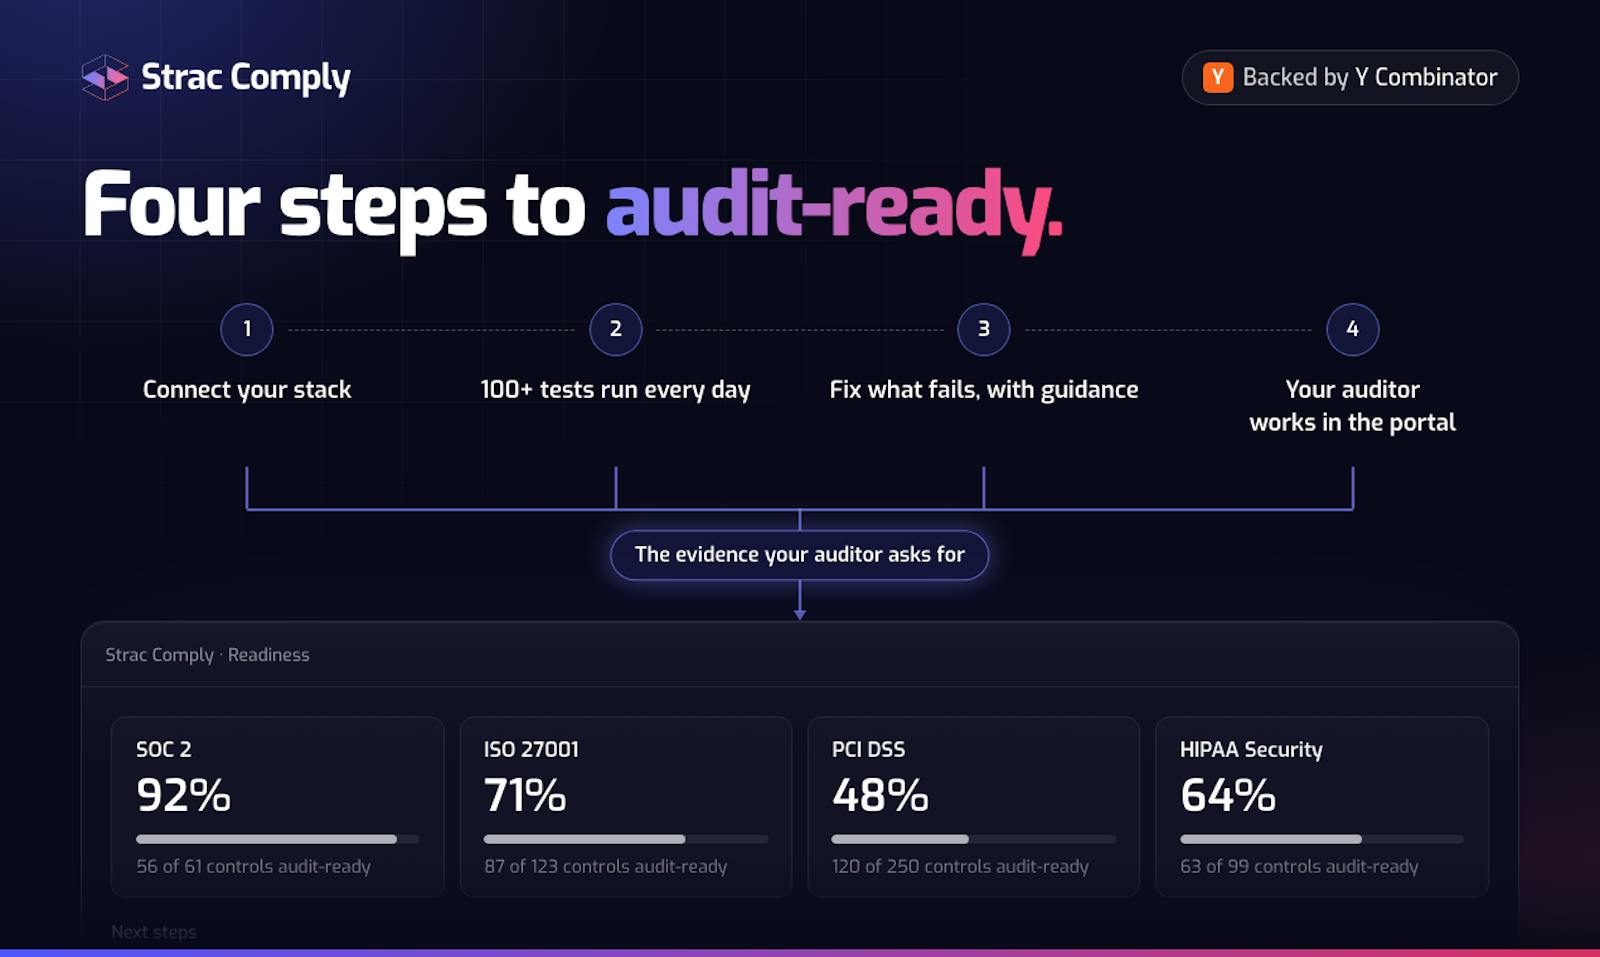
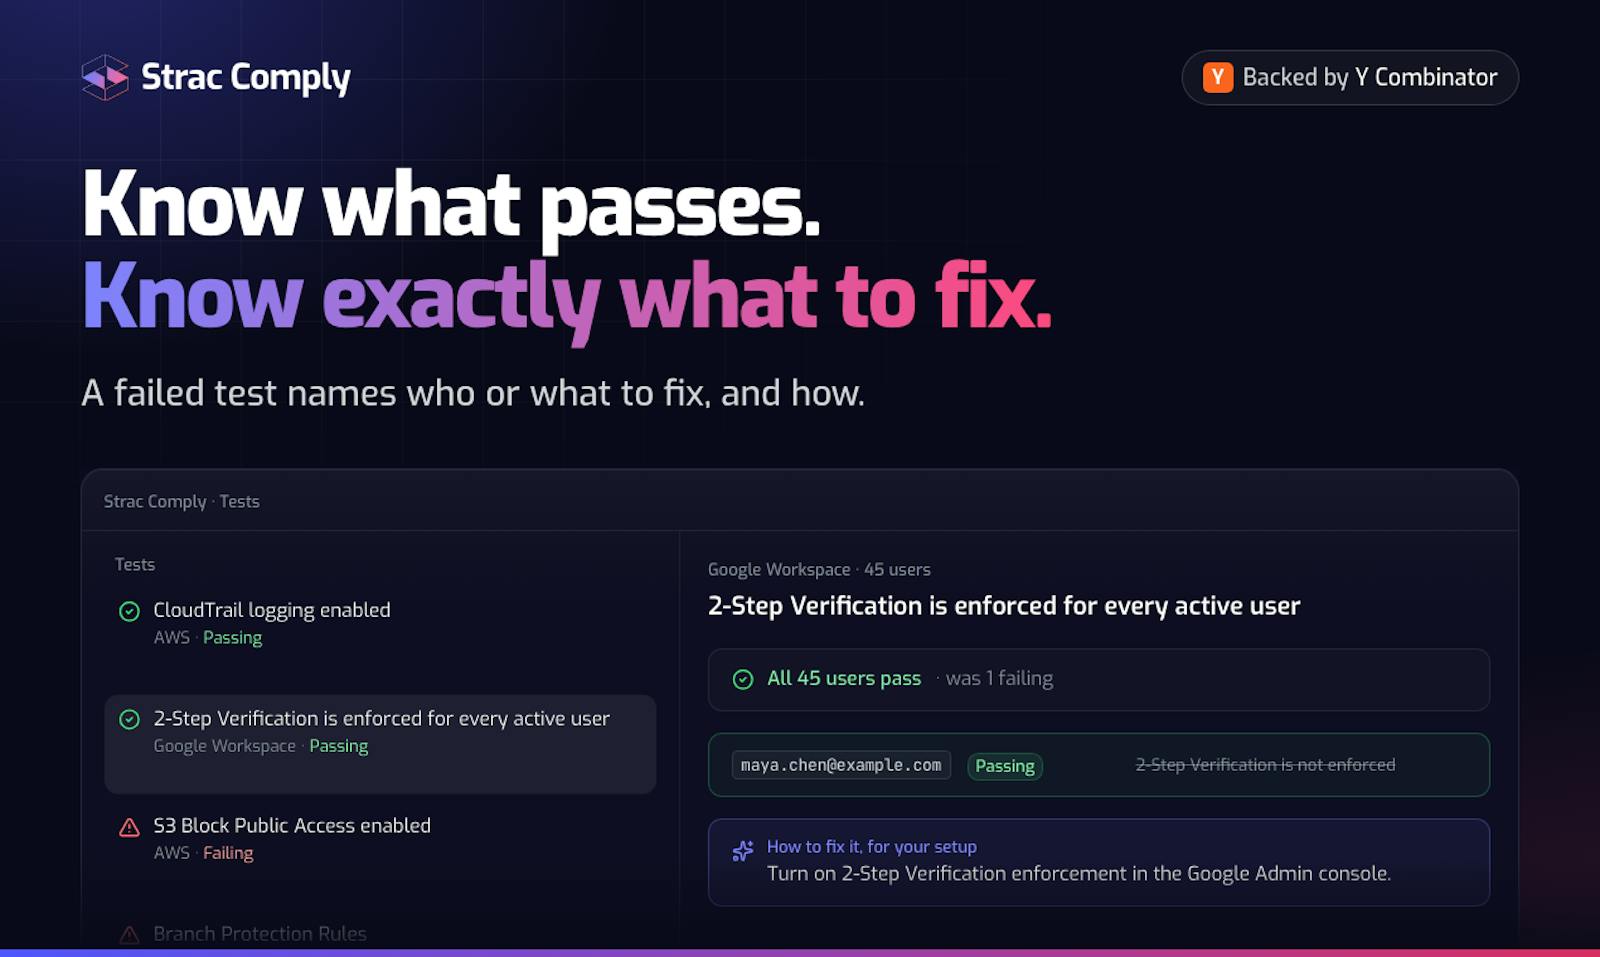
Strac Comply tests your environment against ISO 27001 Annex A controls, 100-plus of them, and every failure comes with the who, the what, and the how, so your ISMS stays evidence-ready between audits.
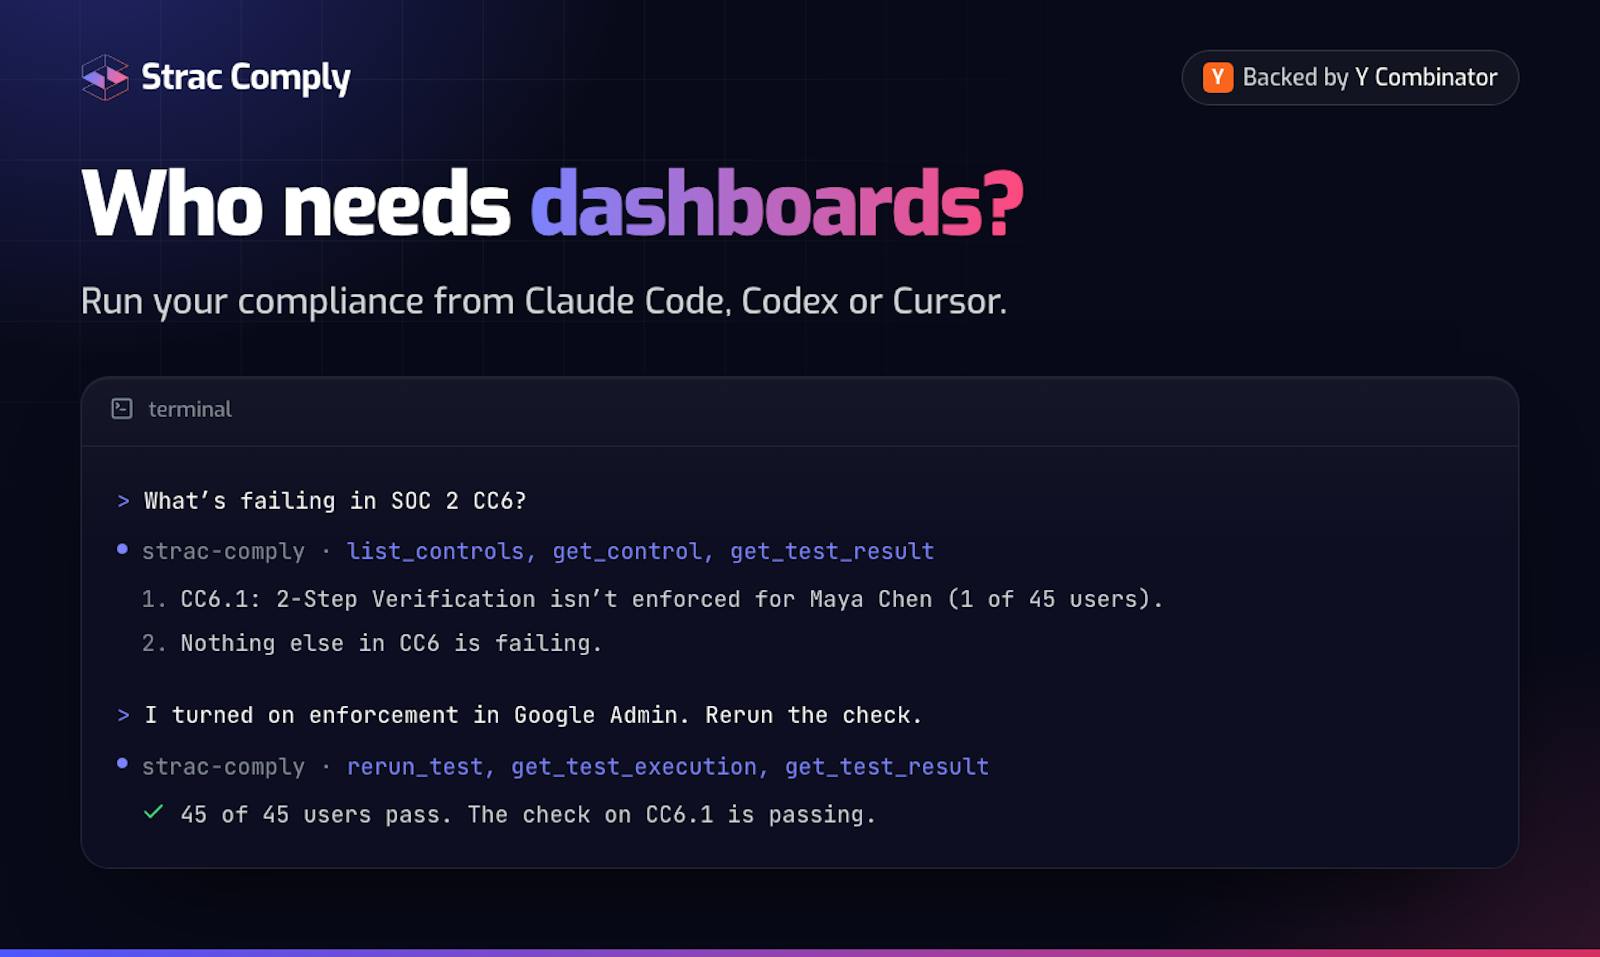
The MCP server lets you query Claude Code, Cursor, or Codex for the Annex A controls that are off track and remediate them in your terminal, something the sales-led tools simply cannot do.
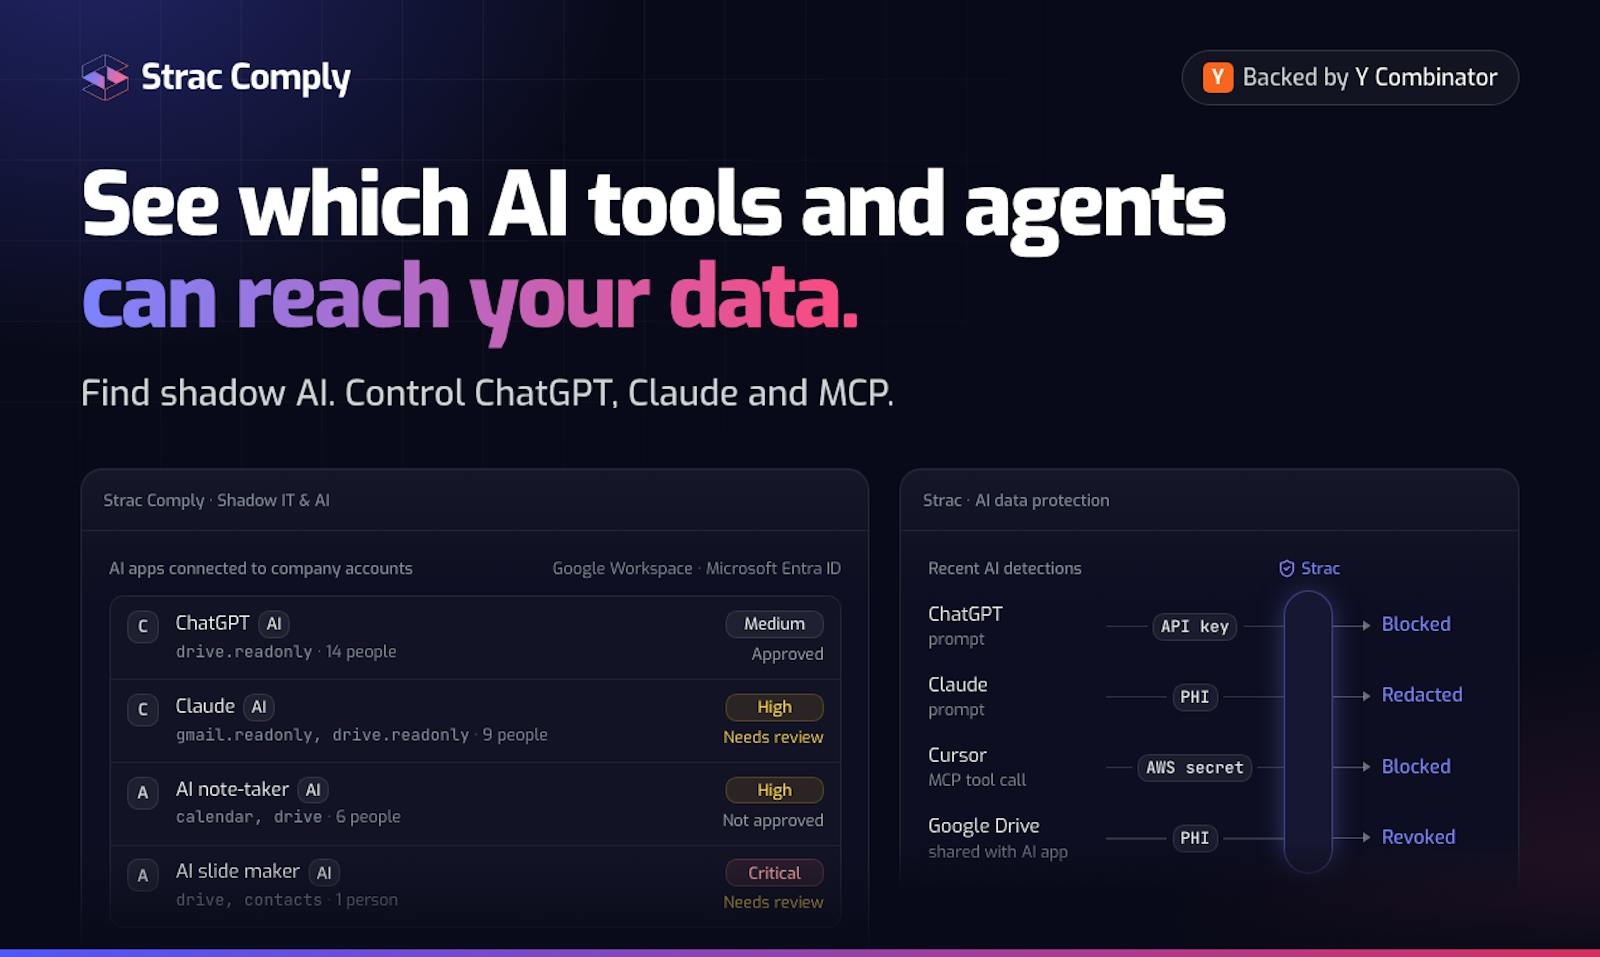
Strac Comply shows the unsanctioned SaaS and AI tools in use, so a stray app does not become a nonconformity at your Stage 2 audit. Included on the $12,995 Security-First plan.
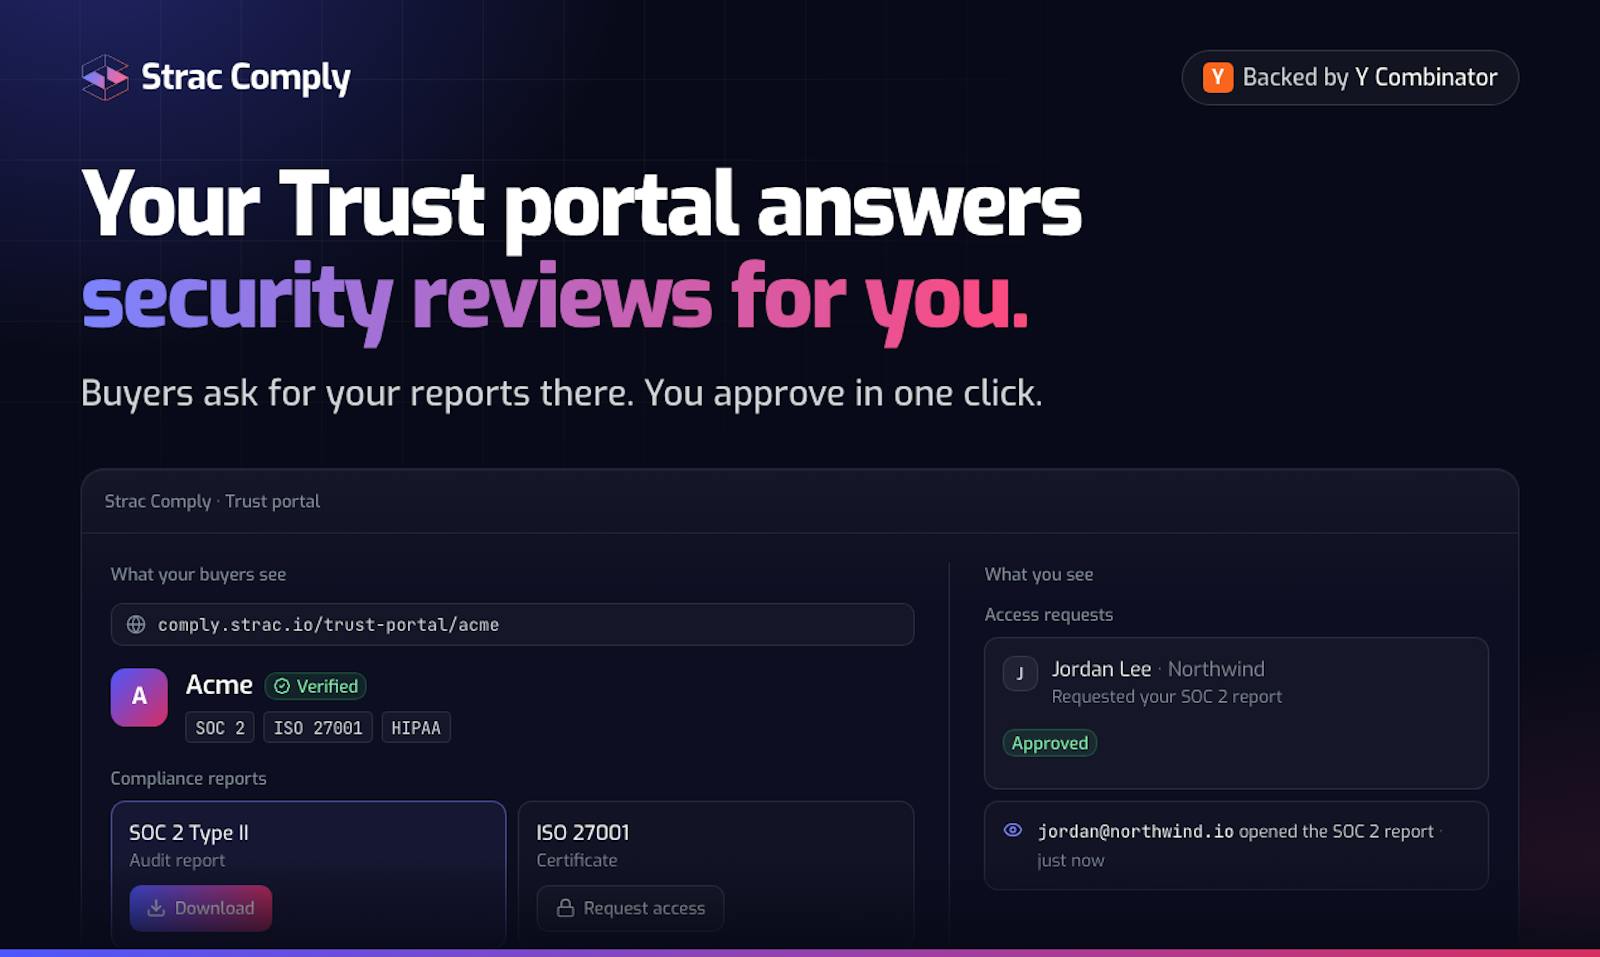
Share your ISO 27001 certificate and Statement of Applicability through the trust portal, approving each request in a click instead of mailing documents.
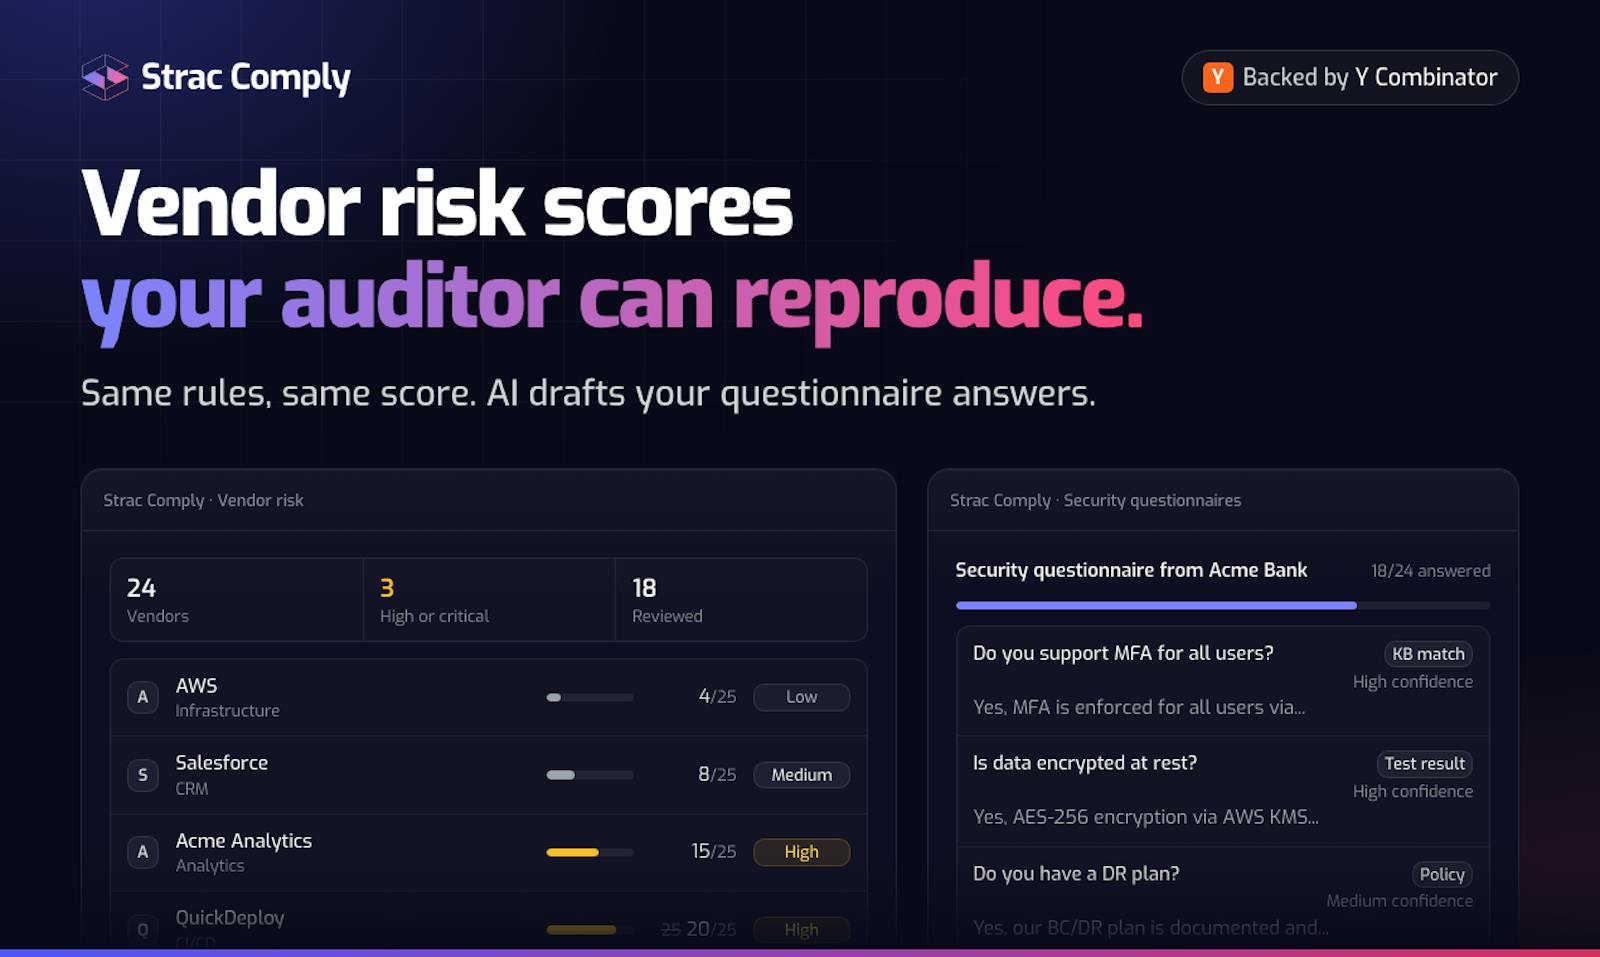
vendor risk scores follow consistent rules and live next to your Annex A evidence, with AI drafting the questionnaire responses your customers send.
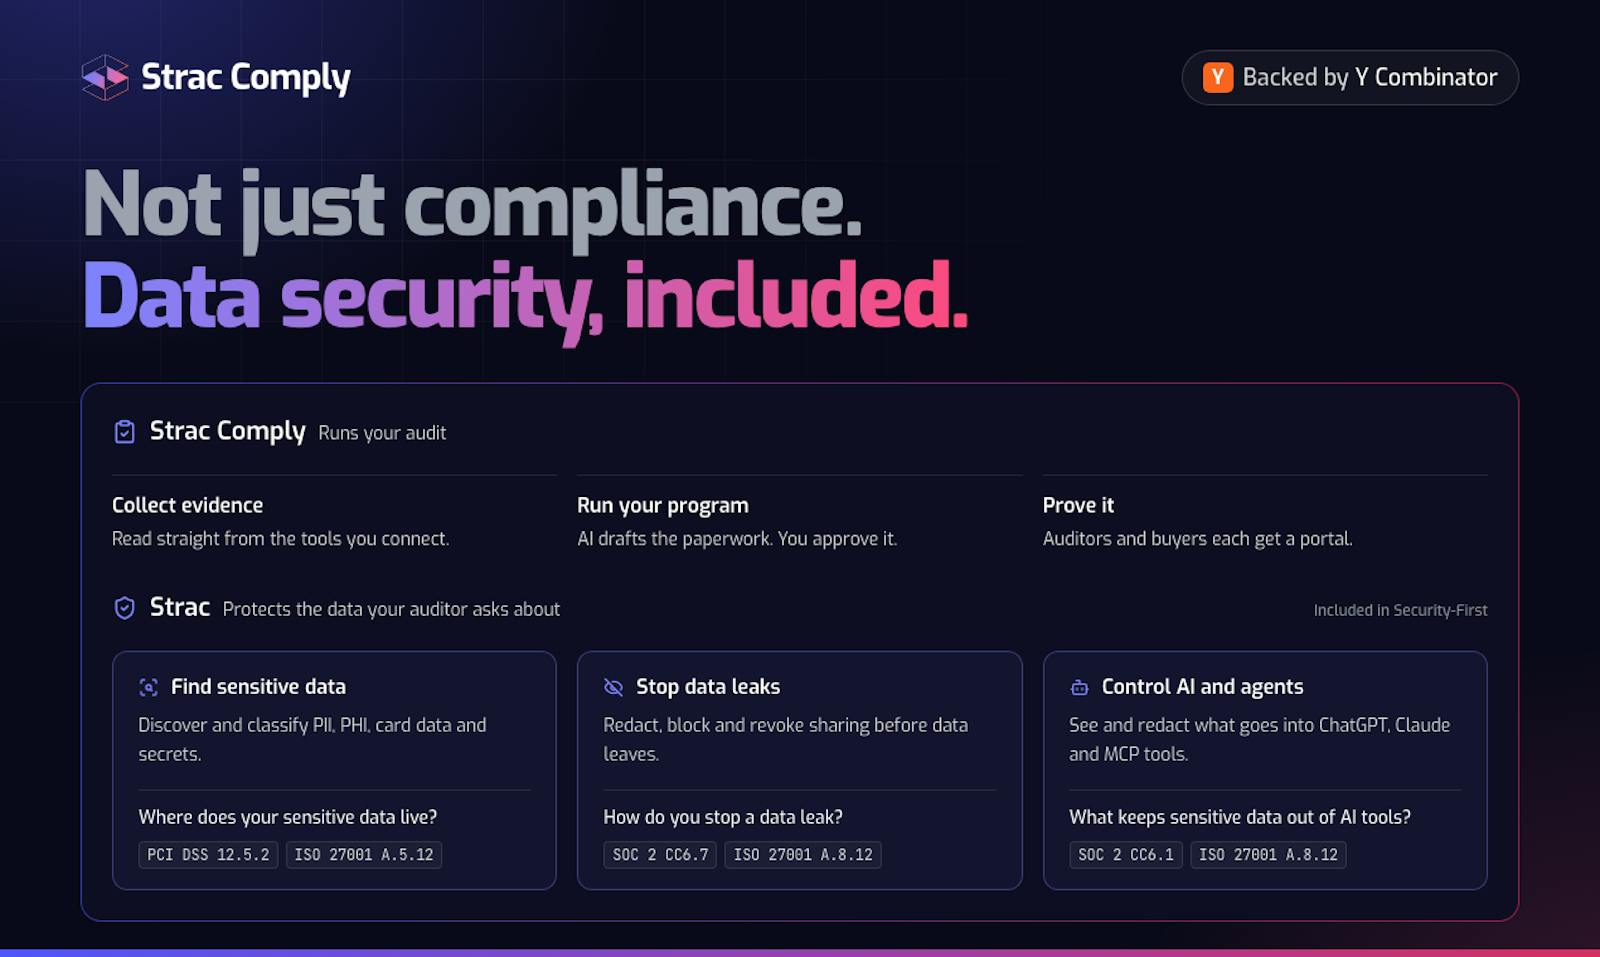
Strac is a data-security platform first, so Strac Comply discovers sensitive data and controls AI access, each mapped to ISO 27001 Annex A.8 controls. That is coverage Vanta and Drata lack.
Strac Comply publishes its full price ladder, no sales call required to see a number:
Every plan covers up to 10 employees (11 to 200 adds $1,995 a year) and has no per-framework fees. Platform is self-serve; Certified and Security-First are set up on a short call. Backed by Y Combinator.
Start free in minutes. Sign up at comply.strac.io and begin your 14-day free trial of the Platform plan. Self-serve, no credit card, no sales call.
One thing to keep straight, because this lives on Strac.io. The prices here are Strac Comply prices: $4,995 for the platform, $8,995 once the CPA audit is folded in, and $12,995 with a penetration test and Strac DLP for Slack, Google Workspace, and AI tools added. The full Strac data-security suite, endpoint DLP, cloud DSPM, and MCP DLP, is a separate purchase, so do not read $4,995 as the cost of Strac’s DLP or DSPM.
Strac Comply: transparent pricing, no sales call.
Ready to start? Sign up at comply.strac.io for a 14-day free trial of the Platform plan, self-serve and no credit card, or compare the field in our Vanta alternatives guide.
Want the real ISO 27001 number for your team? Start a free Strac Comply trial, no credit card.
Expect $25,000 to $90,000 or more in year one across readiness consulting, a compliance platform, the Stage 1 and Stage 2 audit by an accredited certification body, surveillance audits, and a penetration test. Strac Comply automates the readiness and evidence from $4,995 per year, leaving only the accredited body's audit fee separate.
No, and no tool can. ISO 27001 certificates must be issued by an accredited certification body, so that audit is always separate. Strac Comply from $4,995 removes the expensive recurring work: readiness, Annex A mapping, and continuous evidence collection across all five frameworks.
Year one carries the Stage 1 and Stage 2 audit and all the readiness work. Years two and three are lighter surveillance audits. Automating evidence keeps those years cheap.
Yes. Strac Comply prices flat from $4,995 per year up to 10 employees and is backed by Y Combinator, so small teams only pay the certification body's audit fee on top.