Calendar Icon White
October 30, 2026
Clock Icon
7
 min read

Data Loss Prevention SlideShare

A Guide to Robust Data Protection

LinkedIn Logomark White
Data Loss Prevention SlideShare
ChatGPT
Perplexity
Grok
Google AI
Claude
Summarize and analyze this article with:

TL;DR

  • A data loss prevention SlideShare is the deck a security leader uses to explain data loss prevention to a board, a team, or a buyer: where sensitive data lives, how it leaks, and how the company stops it.
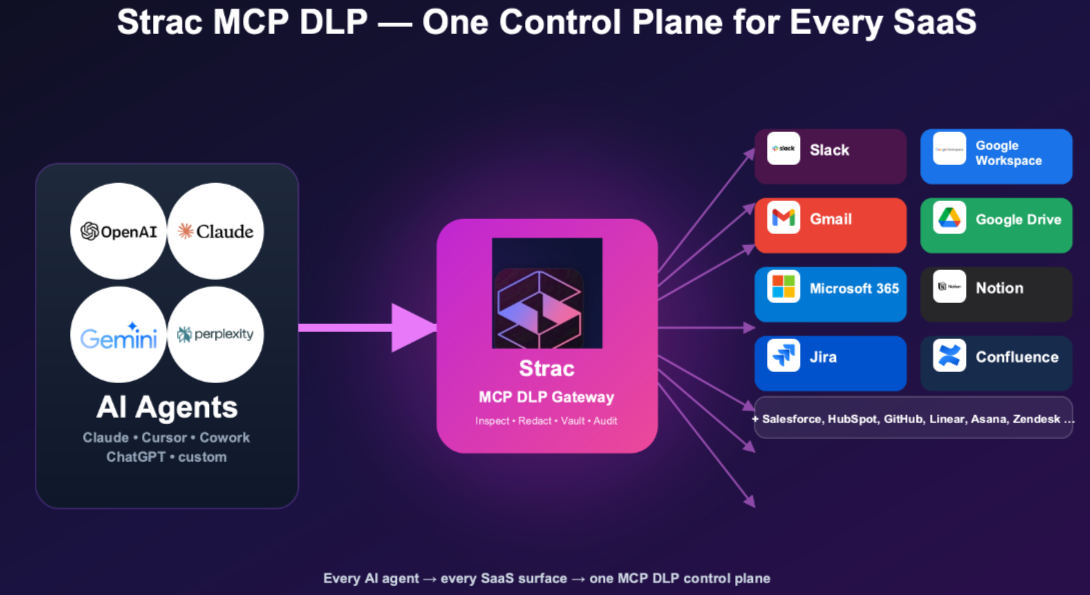
  • Most DLP decks still show network, email, and USB. In 2026 data leaks through Slack threads, public Google Drive links, ChatGPT prompts, and AI agents working over MCP DLP paths.
  • The decks themselves are a leak path. A board deck shared with "anyone with the link" or a training slide with a customer screenshot exposes the same data the deck is meant to protect.
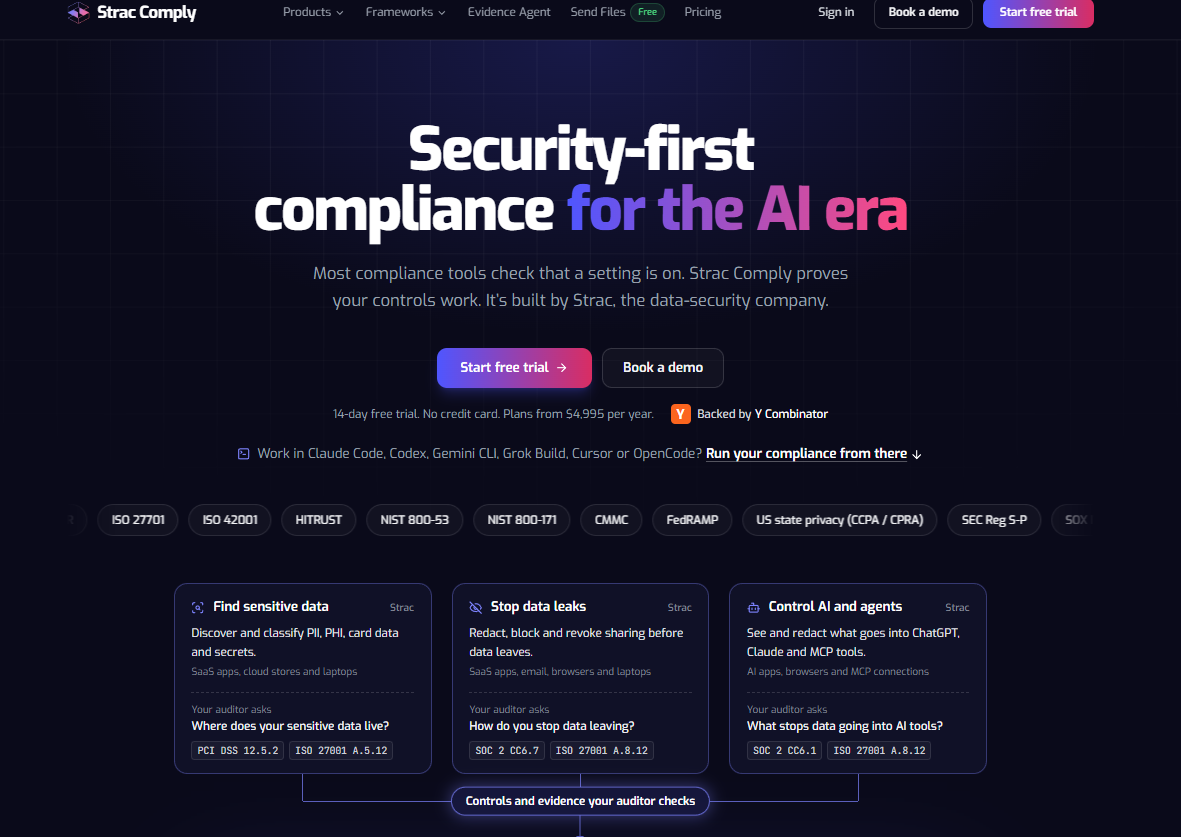
  • Strac covers every slide in one platform: SaaS DLP, DSPM, browser DLP, endpoint DLP, AI DLP, and MCP DLP, with redaction built in.
  • For the full background, start from the data loss prevention guide.

What Is a Data Loss Prevention SlideShare?

A data loss prevention SlideShare is a short presentation that explains a company's DLP program. It shows what counts as sensitive data, where that data lives, how it can leave, and which controls stop it. Security leaders use it to win budget, train staff, and walk auditors through their controls.

A good deck is specific. It names the real tools in use, such as Slack, Google Workspace, Microsoft 365, Salesforce, and Zendesk. It names the data types that matter, such as PII, PHI, card numbers, and API keys. A vague deck gets a nod; a specific deck gets a decision.
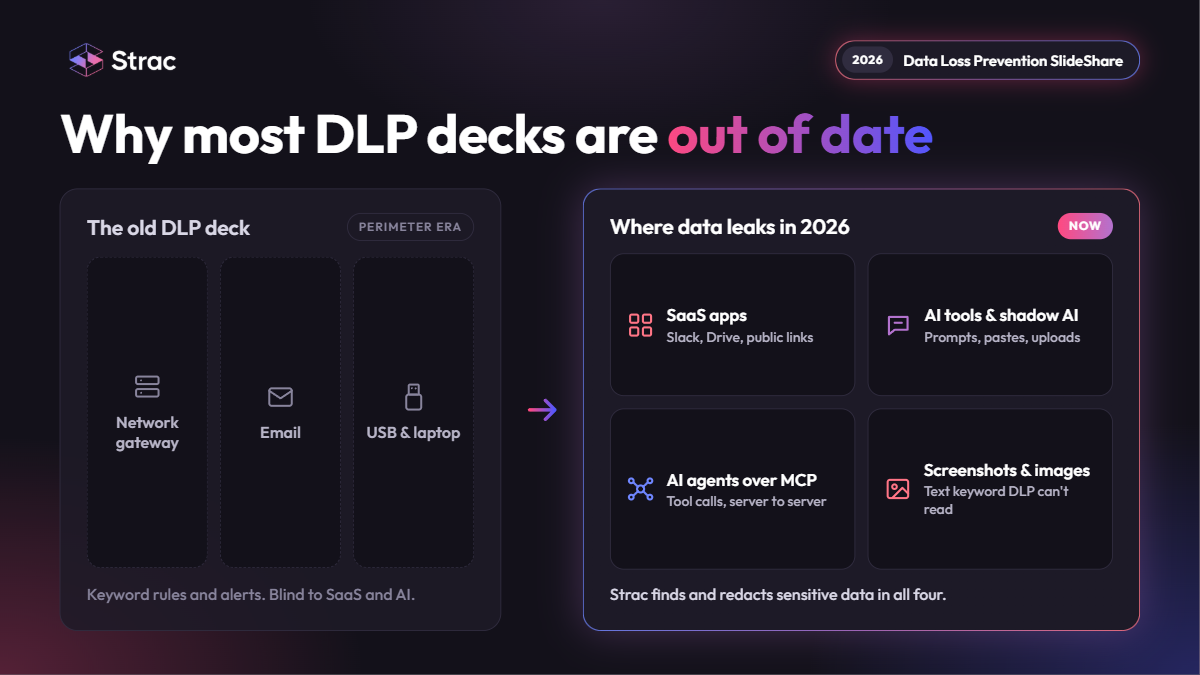
✨ Why Most DLP Decks Are Out of Date in 2026

Most DLP presentations online were built for a time when data stayed inside the office. They describe three pillars: network, email, and endpoint. That picture misses where data actually goes now.

  • Data lives in SaaS, not on file servers. Customer records sit in Slack channels, Jira tickets, and shared Drive folders. A network gateway never sees them.
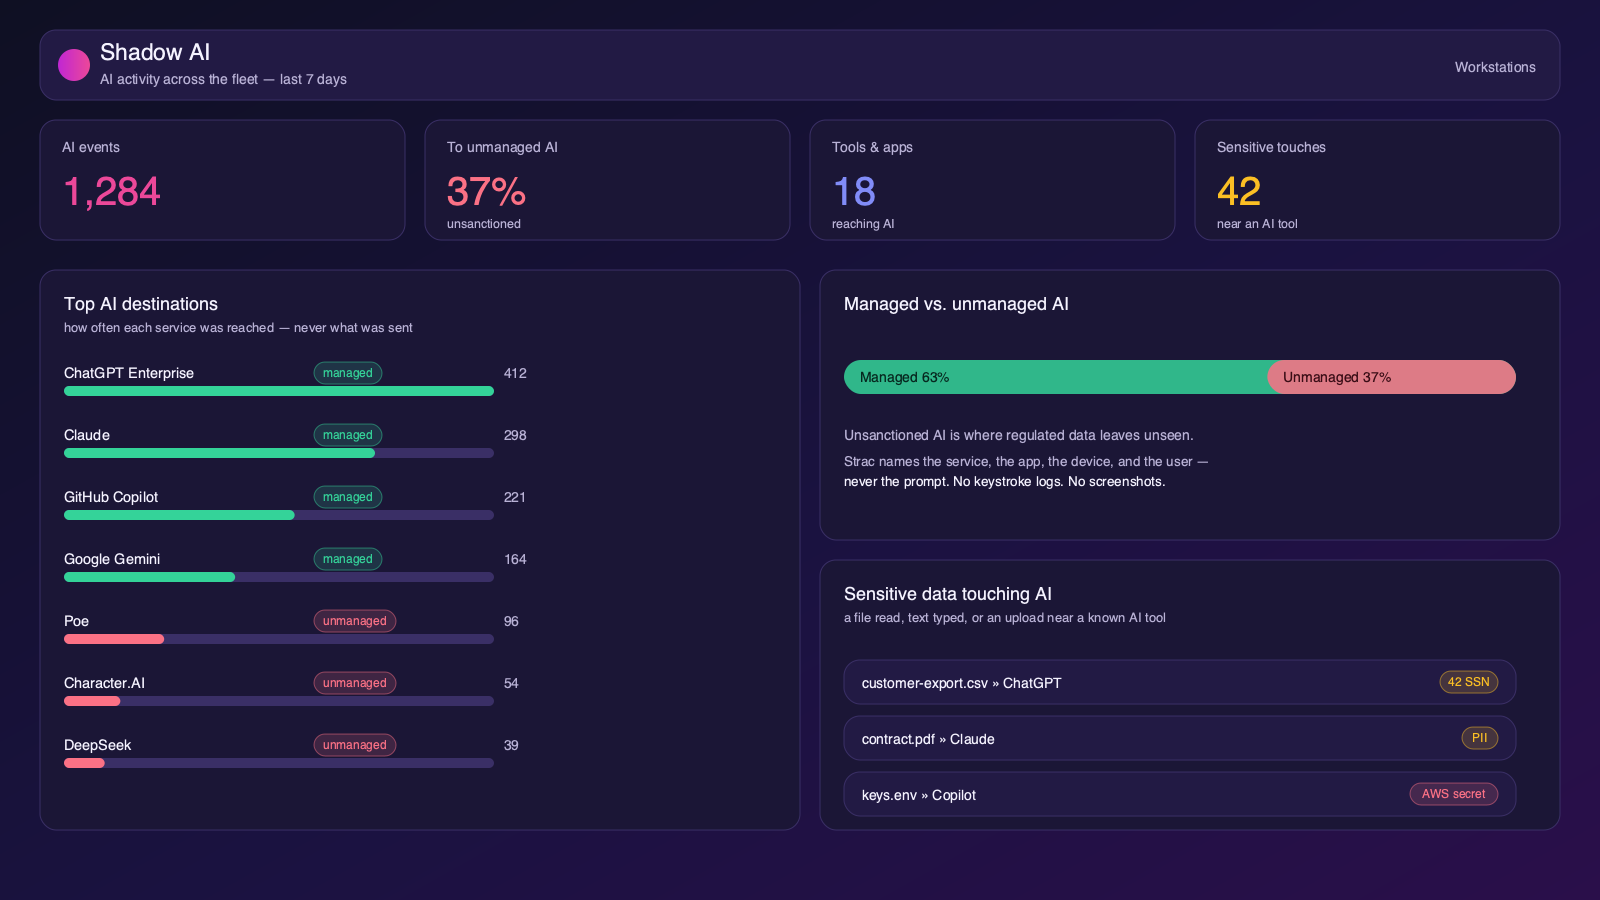
  • Data leaves through AI. Employees paste contracts into Claude, upload spreadsheets to Gemini, and ask Copilot to summarize customer data. Teams also adopt AI tools that security never approved. That is shadow AI.
  • AI agents move data on their own. Agents read Drive, Slack, and databases through MCP connectors, server to server. A legacy endpoint agent watches files on disk, not tool calls made by an agent.
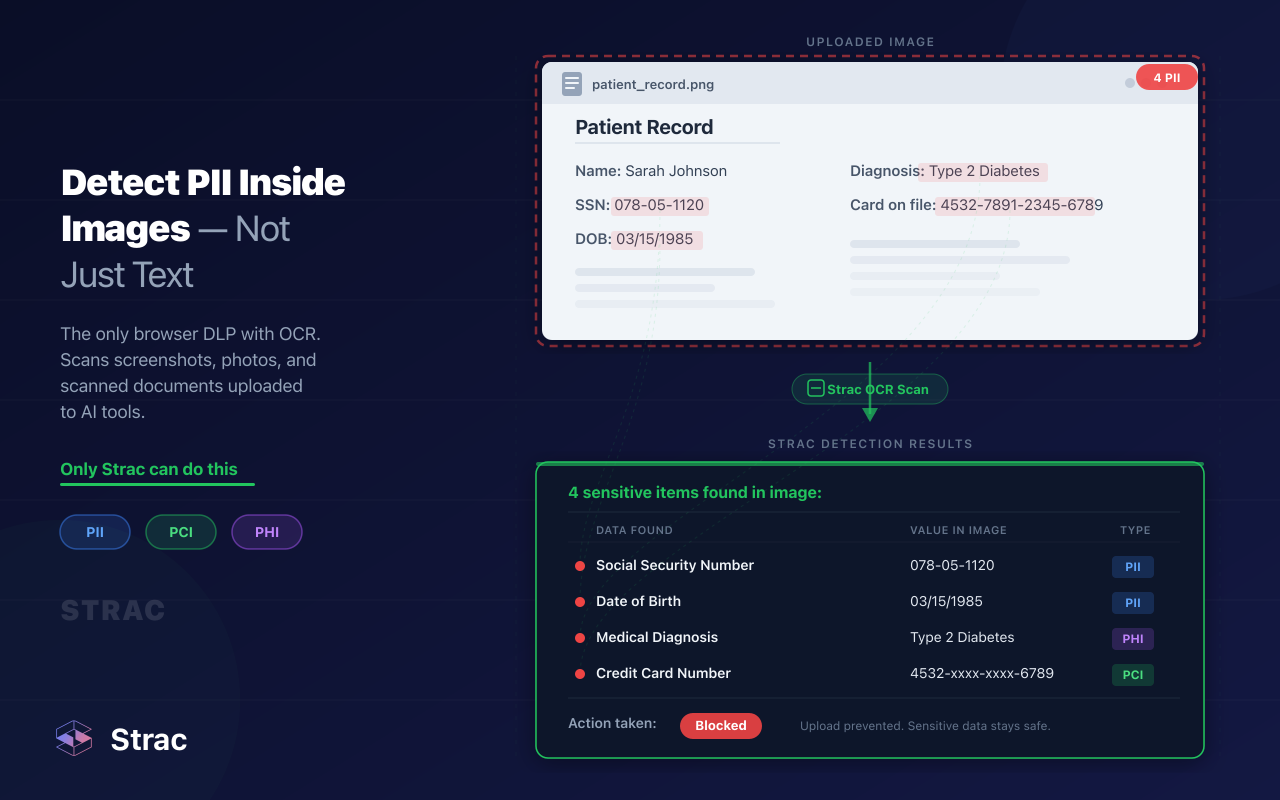
  • Images hide sensitive data. A screenshot of a support ticket or a photo of a driver's license is still sensitive data. Text-only scanning misses all of it.

An old deck describes the risk you had. A current deck describes the risk you have. For a deeper look at the gap, read why legacy DLP fails for AI.

Your Slide Decks Are a Leak Path Too

Presentations are one of the easiest ways for sensitive data to get out, because nobody treats a deck as a data file. A quarterly review carries customer names and revenue. A board deck carries financials and the roadmap. A support training deck carries real ticket screenshots with real customer data.

  • Public links. A deck in Google Drive or OneDrive is set to "anyone with the link" and stays that way for years.
  • Outside users. A former agency or contractor can still open a shared folder in Box or SharePoint.
  • Screenshots in slides. A Zendesk ticket with a Social Security number is pasted into a training slide as an image.
  • Decks in chat. The deck is posted to a Slack channel that includes guests.
  • Decks in AI tools. Someone uploads the board deck to ChatGPT to write a summary.
  • Decks on public sites. A deck goes to SlideShare or a conference portal with internal data still on slide 14.

Scanning text finds the risk you can read; reading images finds the risk you can see. Strac does both, so a slide full of screenshots is not a blind spot.

✨ Redaction in Practice: A Screenshot Inside a Deck

Here is the same leak handled two ways. A support manager uploads a training deck to an AI tool to tighten the wording. Slide 9 holds a ticket screenshot with a customer's Social Security number.

With legacy DLP, the upload goes through. The tool reads text, not images, and it does not watch the browser. The customer's number now sits in a third-party AI service.

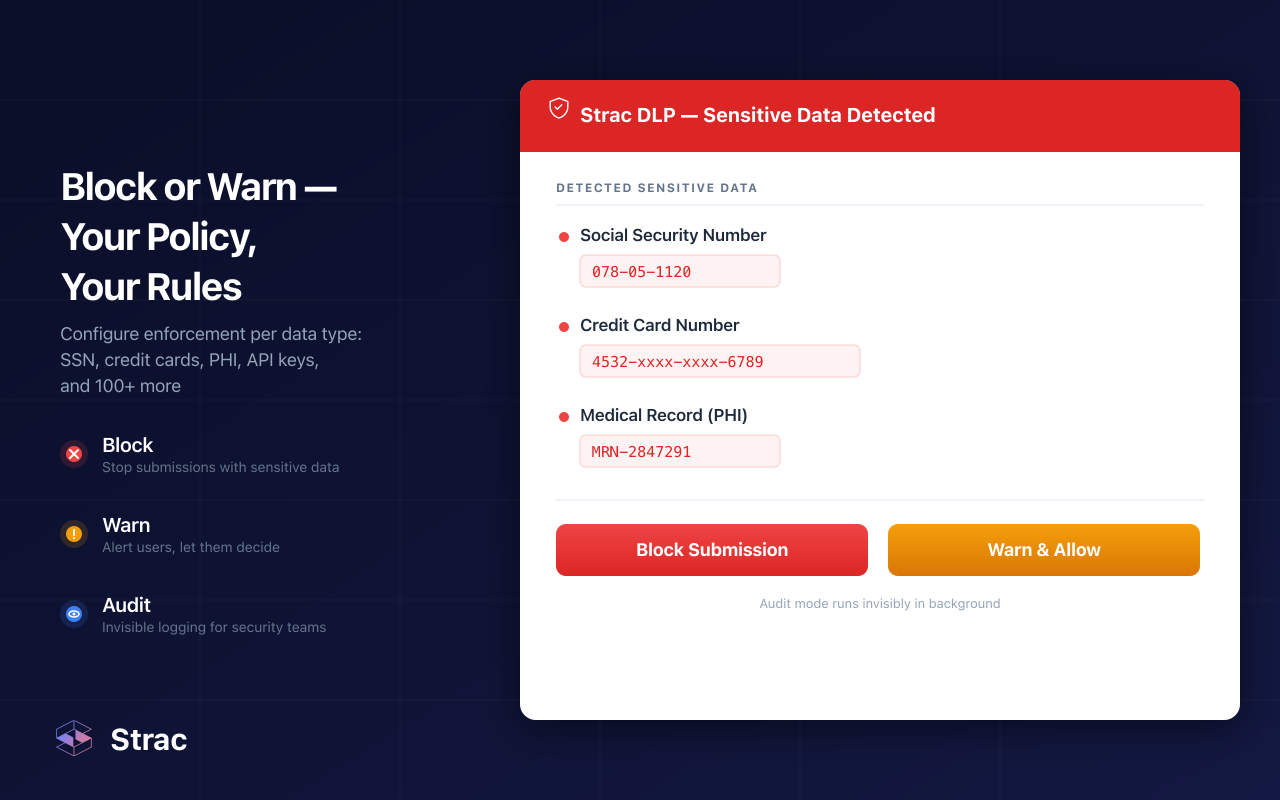
With Strac, browser DLP inspects the file before it leaves. OCR reads the screenshot, finds the number, and redacts it. The manager sees a short note explaining why, and the event is logged as audit evidence. The work continues; the sensitive value stays home.
✨ Strac: One Platform Behind Every Slide

Strac covers each slide in the deck with one set of detectors and one policy engine, across SaaS, cloud, endpoint, browser, generative AI, and MCP.
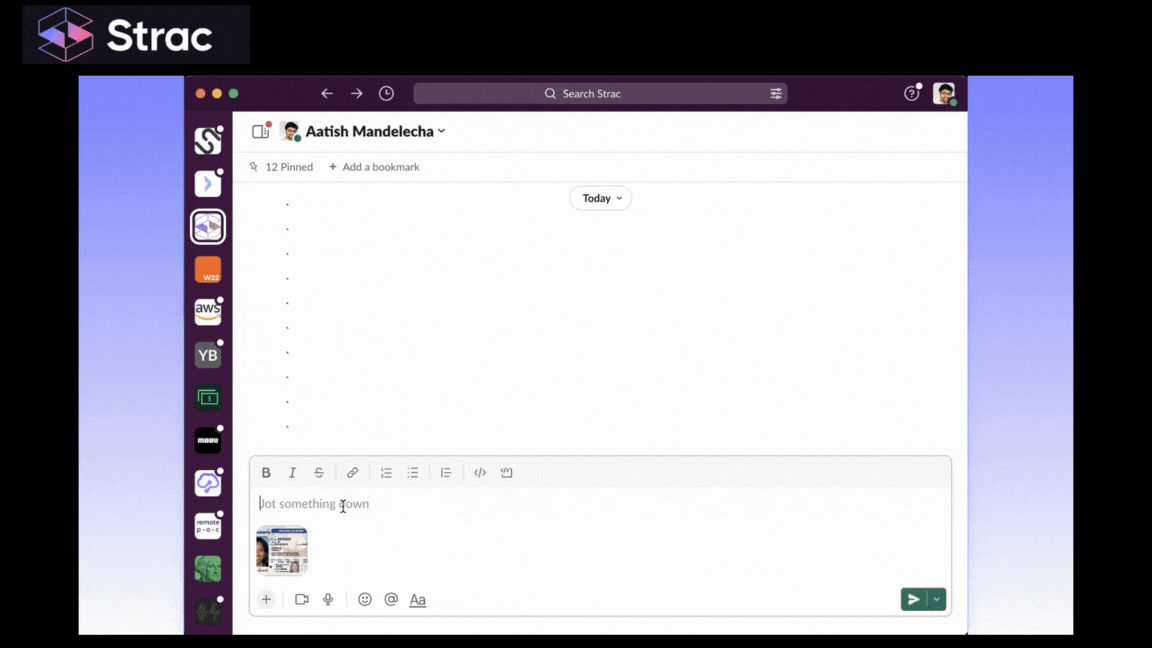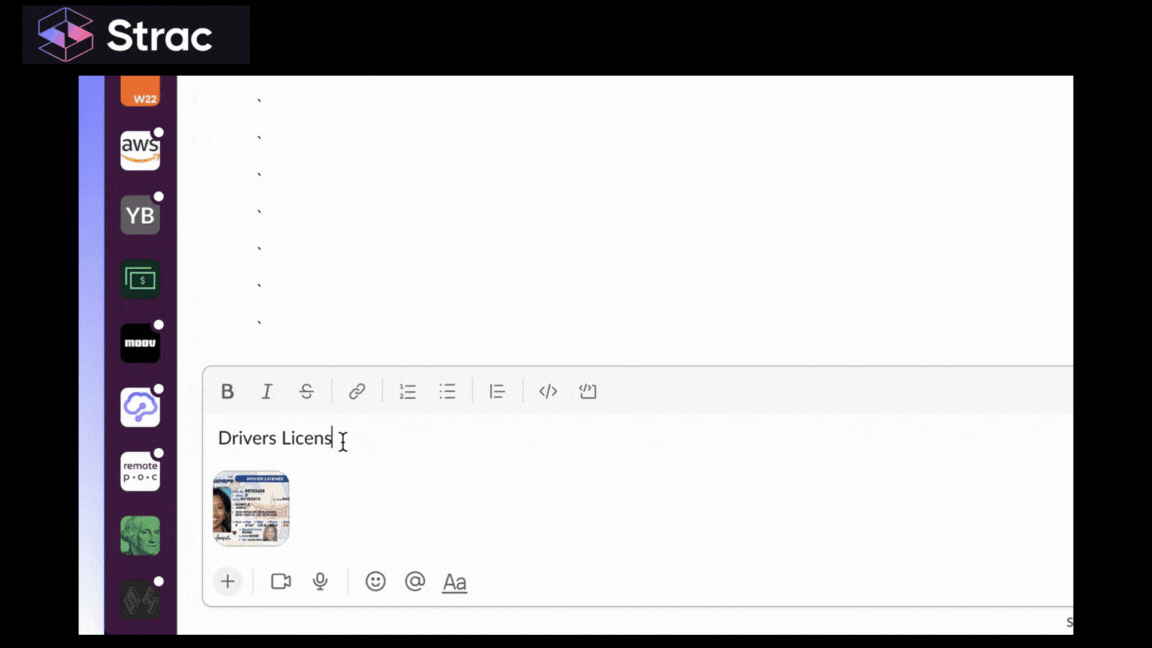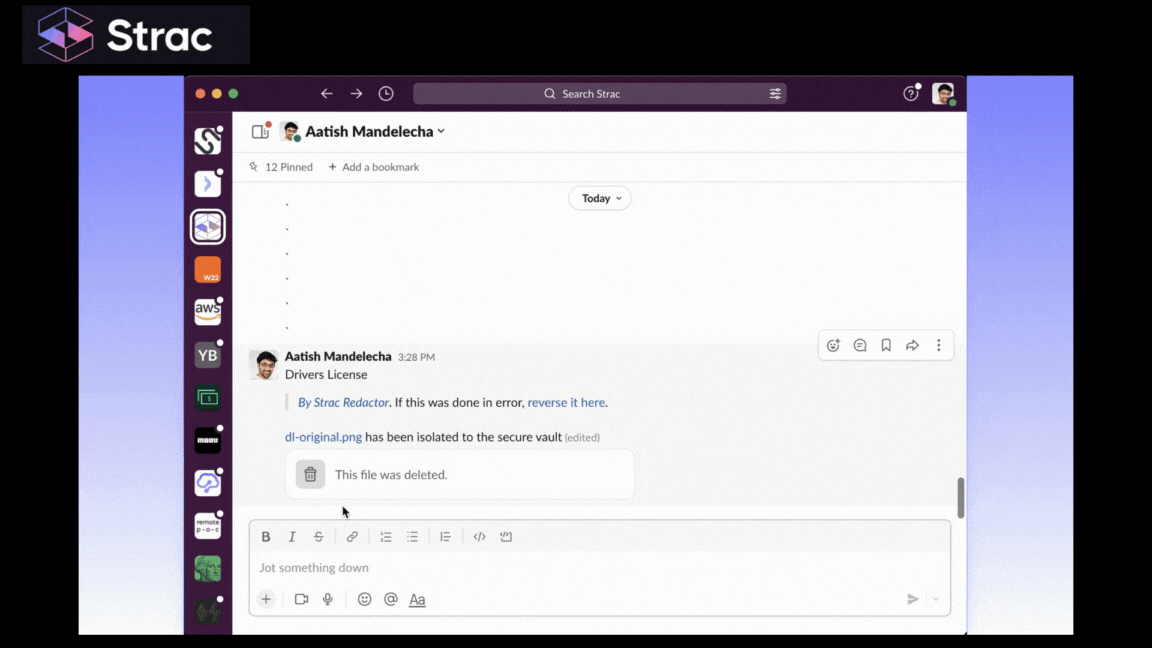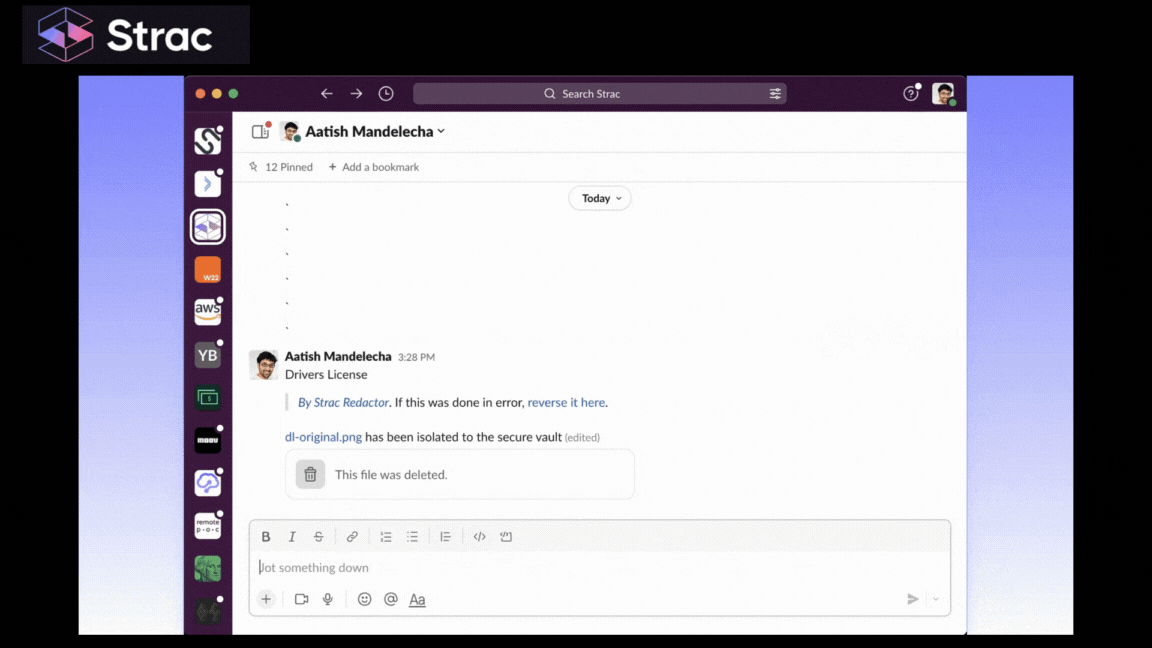
  • Discovery and posture. DSPM scans history across every connected app, including old decks with public links, and ranks risk in one view. The PII scanner does the same for PII, PCI, and PHI.
  • Images and files. OCR reads PDFs, images, screenshots, Word files, spreadsheets, and ZIP archives, so a slide built from screenshots gets the same scan as plain text.
  • Endpoint. One light agent for Mac, Windows, and Linux controls downloads, USB, printing, screenshots, AirDrop, clipboard, browser uploads, and AI prompt text. Each channel runs in Block, Warn, or Audit mode. Read how an endpoint DLP agent works.‍
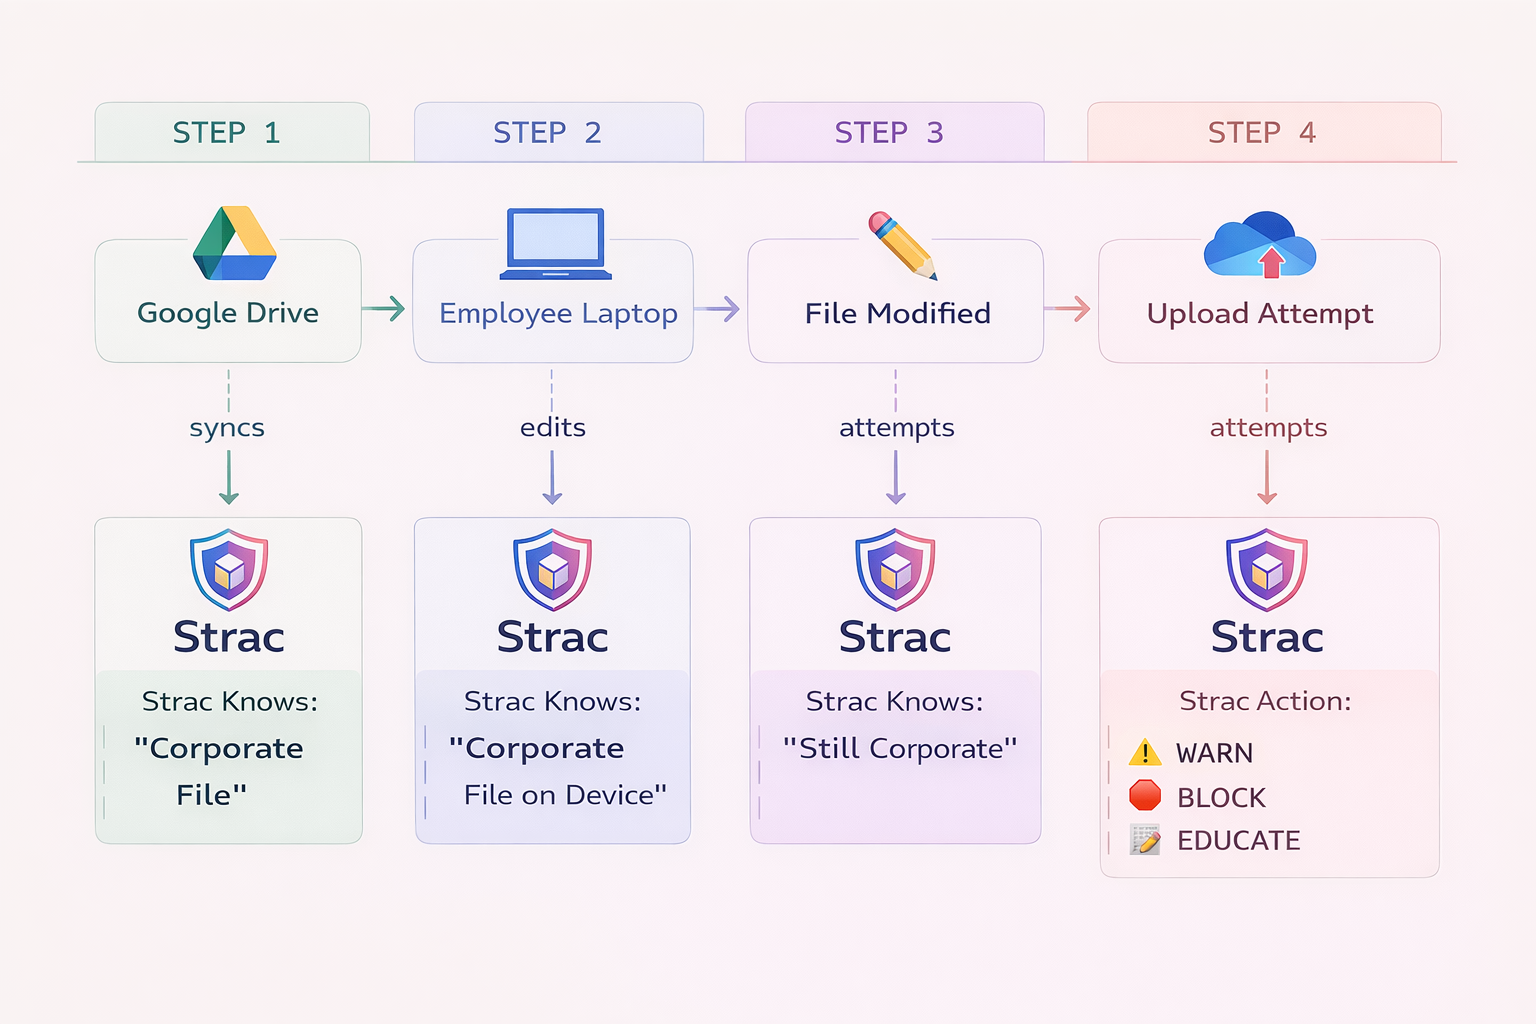
  • Data lineage. Data lineage DLP follows a deck after it is downloaded, copied, or renamed, so you know where it went.
  • Shadow AI. Strac shows every AI app people actually use, approved or not, and the sensitive data going into each, with no keystroke logging or screen recording. Start with how to detect shadow AI.
  • AI agents. MCP DLP redacts sensitive data inside each agent tool call, so an agent reading Drive or a database gets safe data only. Browse the MCP connector directory.
  • Remediation in a fixed order. When Strac finds sensitive data, it follows your policy:
    • Redact / mask. Removes or hides the value in Slack, email, tickets, docs, Google Drive, SharePoint, and Box. See data masking.
    • Block. Stops a share, a USB copy, an upload, or an AI prompt when redaction is not enough.
    • Warn and coach. Tells the person what was found and why, at the moment they act.
    • Revoke access. Removes public links and outside users from decks and folders that hold sensitive data.

Your DLP Deck Checklist

  • ☐ The deck lists every data type you protect
  • ☐ It names the real apps where that data lives
  • ☐ It covers AI tools, shadow AI, and AI agents
  • ☐ It shows remediation, not just alerts
  • ☐ Your own decks have no public links or stale outside users
  • ☐ Screenshots in slides are scanned with OCR
  • ☐ Uploads of sensitive decks to AI tools are inspected in the browser
  • ☐ Metrics on slide 11 come from real audit logs

Related reading:

The Bottom Line

A DLP deck is only as good as the risk it describes, and in 2026 that risk lives in SaaS apps, browsers, AI tools, AI agents, and the decks themselves. Networks, identities, and filters will fail eventually, so the data layer is the backstop: find sensitive data everywhere it lives, redact it on every action, and a mistake never becomes a breach.

‍Book a demo to see Strac protect the data behind every slide.
🌶️ Spicy FAQs on Data Loss Prevention SlideShare

Is a DLP presentation the same as a DLP policy?

No. A DLP policy is the written rule set that says what happens to each data type. A DLP presentation explains that policy, the risks behind it, and the plan to enforce it, so leaders and staff understand and approve it.

Why doesn't our existing DLP cover slide decks and AI tools?

Most legacy DLP reads text in email and network traffic. It does not scan SaaS file history, read screenshots inside slides, or watch uploads to AI tools in the browser. Strac connects to those places directly and fixes exposure where it sits.

Will DLP slow down people who build and share decks?

No. Strac redacts only the sensitive value and lets the deck, message, or prompt go through, so work continues. Blocking is kept for the cases that need it, and people see a short explanation instead of a silent failure.

Can any DLP stop every deck from leaking?

Not every one. People find new tools, and sharing settings drift. That is why the data layer matters: if sensitive values are redacted wherever they land, a forgotten public link exposes far less.

What should a data loss prevention presentation include?

It should cover the data you protect, where it lives, how it leaks, and your plan to find, fix, and govern it, including AI tools and agents. Start from the data loss prevention guide and AI data governance

Customer story

“Don’t just alert on problems, fix them.”

Scott Roberts, Chief Information Security Officer, UiPath

  • UiPath
  • Crypto.com
  • Inmar Intelligence
  • thredUP
  • Paymentology
  • Enveda
  • Genesis Molecular AI
  • MeridianLink
More customer stories →
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.

Customers include
  • UiPath
  • Crypto.com
  • Inmar Intelligence
  • thredUP
  • Paymentology
  • Enveda
  • Genesis Molecular AI
  • MeridianLink
Trusted by enterprises
Data Security + Compliance Automation

Latest articles

Browse all

Get Your Datasheet

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Close Icon