TISAX vs ISO 27001: Which One Does Your Company Need?
TISAX vs ISO 27001 compared: when ISO 27001 can satisfy an automotive requirement and when only a TISAX label will do, what the VDA ISA catalogue adds, and which to build first.
ISO 27001 does not replace TISAX when an automotive OEM has demanded a TISAX label. The label is shared through the ENX portal and a certificate is not a substitute.
It does satisfy some automotive requirements. Mercedes-Benz dealers, for example, can use either ISO 27001 or TISAX AL2.
The VDA ISA catalogue TISAX assesses against is built on ISO 27001 Annex A and shares most of its controls, then adds prototype protection and a data protection module.
An existing ISO 27001 ISMS cuts a TISAX project from 12 to 18 months down to 3 to 6.
If you need both, do ISO 27001 first. It is the reusable asset.
The shared base is why an ISO 27001 foundation collapses a TISAX timeline.
The question behind the question
"TISAX or ISO 27001" is usually asked as though the two were competing products and one were objectively better. They are not comparable in that way. ISO 27001 is an international standard you get certified against by an accredited body, and the certificate is yours to show anyone. TISAX is an assessment and exchange mechanism for one industry, run by the ENX Association, where the result is a label published to a portal that automotive customers look you up in.
So the useful question is narrower: what does the contract in front of you actually name? If it names a TISAX label, no amount of ISO 27001 will close it. If it names "ISO 27001 or TISAX AL2", as the Mercedes-Benz dealer requirement does, then you get to choose, and the choice should be made on which asset is worth more to you afterwards.
✨ Where the two standards genuinely overlap
The overlap is real and it is large, which is why the substitution question comes up at all. TISAX assessments are conducted against the VDA ISA catalogue, and that catalogue was built on ISO 27001 Annex A. The majority of its controls are recognisably the same controls: access management, cryptography, supplier relationships, incident handling, physical security, business continuity.
What that means in practice is that the evidence transfers even though the certificate does not. An access review you run for ISO 27001 is the access review a TISAX assessor wants to see. This is the entire reason an ISO 27001 foundation collapses a TISAX timeline.
One control set, tested once, reported against every framework it maps to.
What TISAX adds that ISO 27001 does not have
Three things, and they are the reason the automotive industry built its own scheme rather than adopting ISO 27001 wholesale.
What TISAX adds
Why the automotive industry wanted it
Prototype protection
Unreleased vehicles, parts and designs are physically present at suppliers. ISO 27001 has nothing specific about shielded rooms, camera bans or controlling who can see an unannounced model.
A data protection module
The VDA ISA catalogue carries its own data protection assessment objectives. ISO 27001 treats personal data as one more information asset rather than as a distinct regime.
Shared results through one portal
An OEM with thousands of suppliers does not want to collect and verify thousands of certificates. A label in the ENX portal is checkable centrally, which is the actual product TISAX sells.
That third row is the one people underestimate. TISAX is as much a distribution mechanism as a standard. The assessment criteria could be identical to ISO 27001 and the OEM would still want the label, because the label is what their supplier management system can read.
✨ How the two compare on the things that decide a project
ISO 27001
TISAX
Who it is for
Any organisation, any industry
The automotive supply chain and its dealers
Governed by
ISO, audited by accredited certification bodies
ENX Association, assessed by accredited audit providers
Criteria
The standard plus Annex A controls
The VDA ISA catalogue, built on Annex A
Covers prototype protection
No
Yes, as a dedicated objective
Result
A certificate you can show anyone
A label shared through the ENX portal
Validity
Three years with annual surveillance audits
Three years
Depth options
One certification standard
AL1 self-assessment, AL2 remote, AL3 on-site
Useful outside automotive
Yes, it is the general-purpose answer
Very little
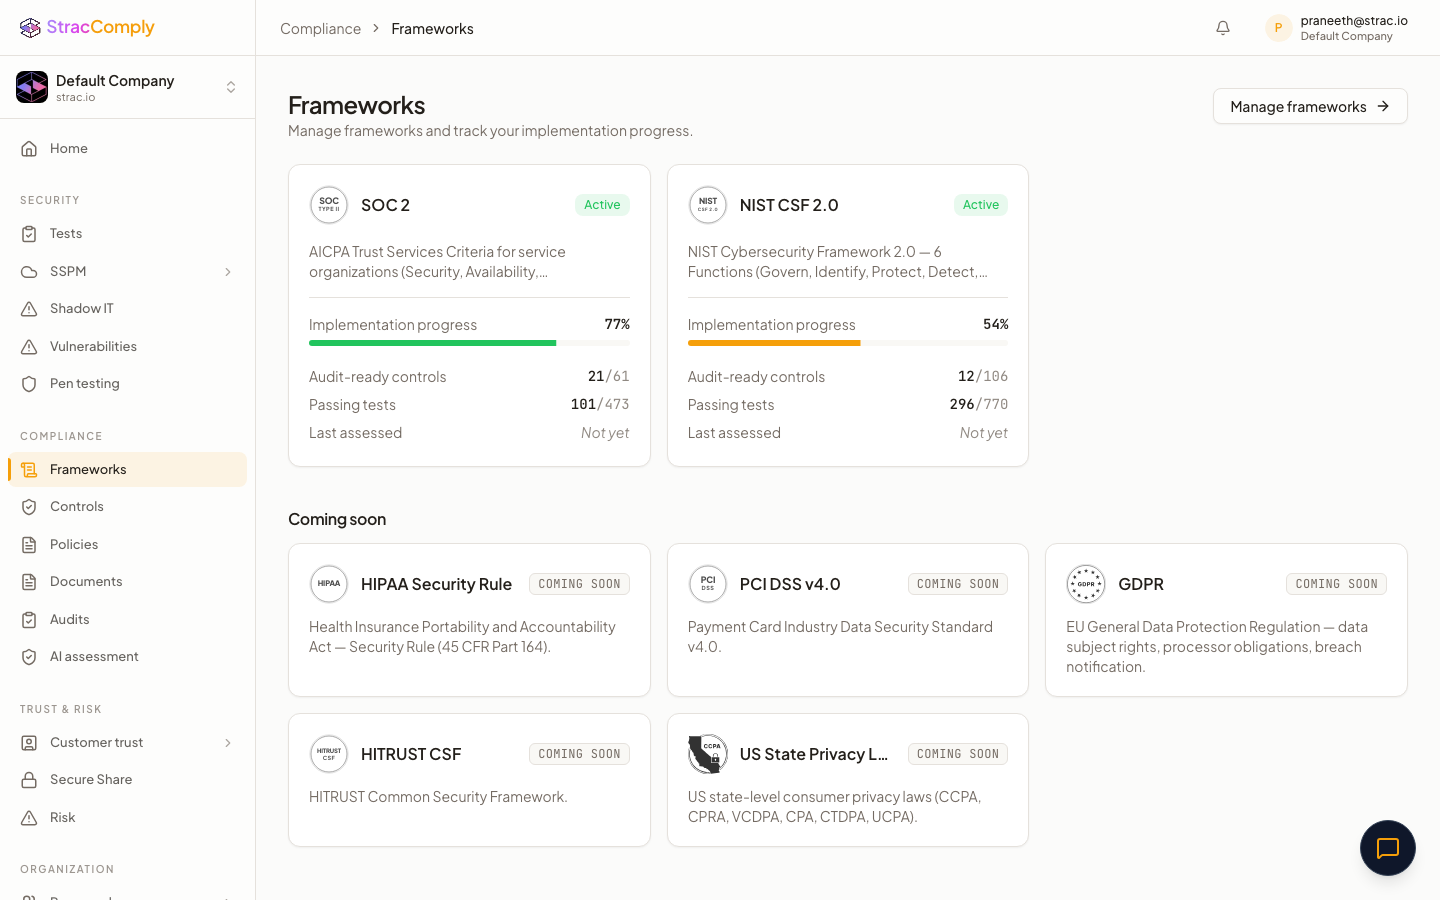
Frameworks sit side by side, which is what makes the shared controls between them worth anything.
✨ The sequencing that actually saves money
If you need both, or you think you might, build ISO 27001 first. Two reasons, and neither is about the standards being better or worse.
The first is reuse. An ISO 27001 ISMS answers your bank, your enterprise prospects, your insurer and your SOC 2 compliance software questionnaire as well as your automotive customer. A TISAX label answers the automotive customer. If you are not exclusively an automotive supplier, one of those assets is worth considerably more than the other.
The second is arithmetic. A TISAX project from a standing start runs 12 to 18 months. On an existing ISO 27001 foundation it runs 3 to 6. The ISMS build is the expensive, slow part, and you only want to pay for it once. If you want the detail on that cost, we broke down what ISO 27001 certification costs separately.
The exception is the company that is purely an automotive supplier, has one OEM customer, and has been given a deadline. Then go straight at the label and come back to ISO 27001 later. Read the TISAX certification guide for what that project involves.
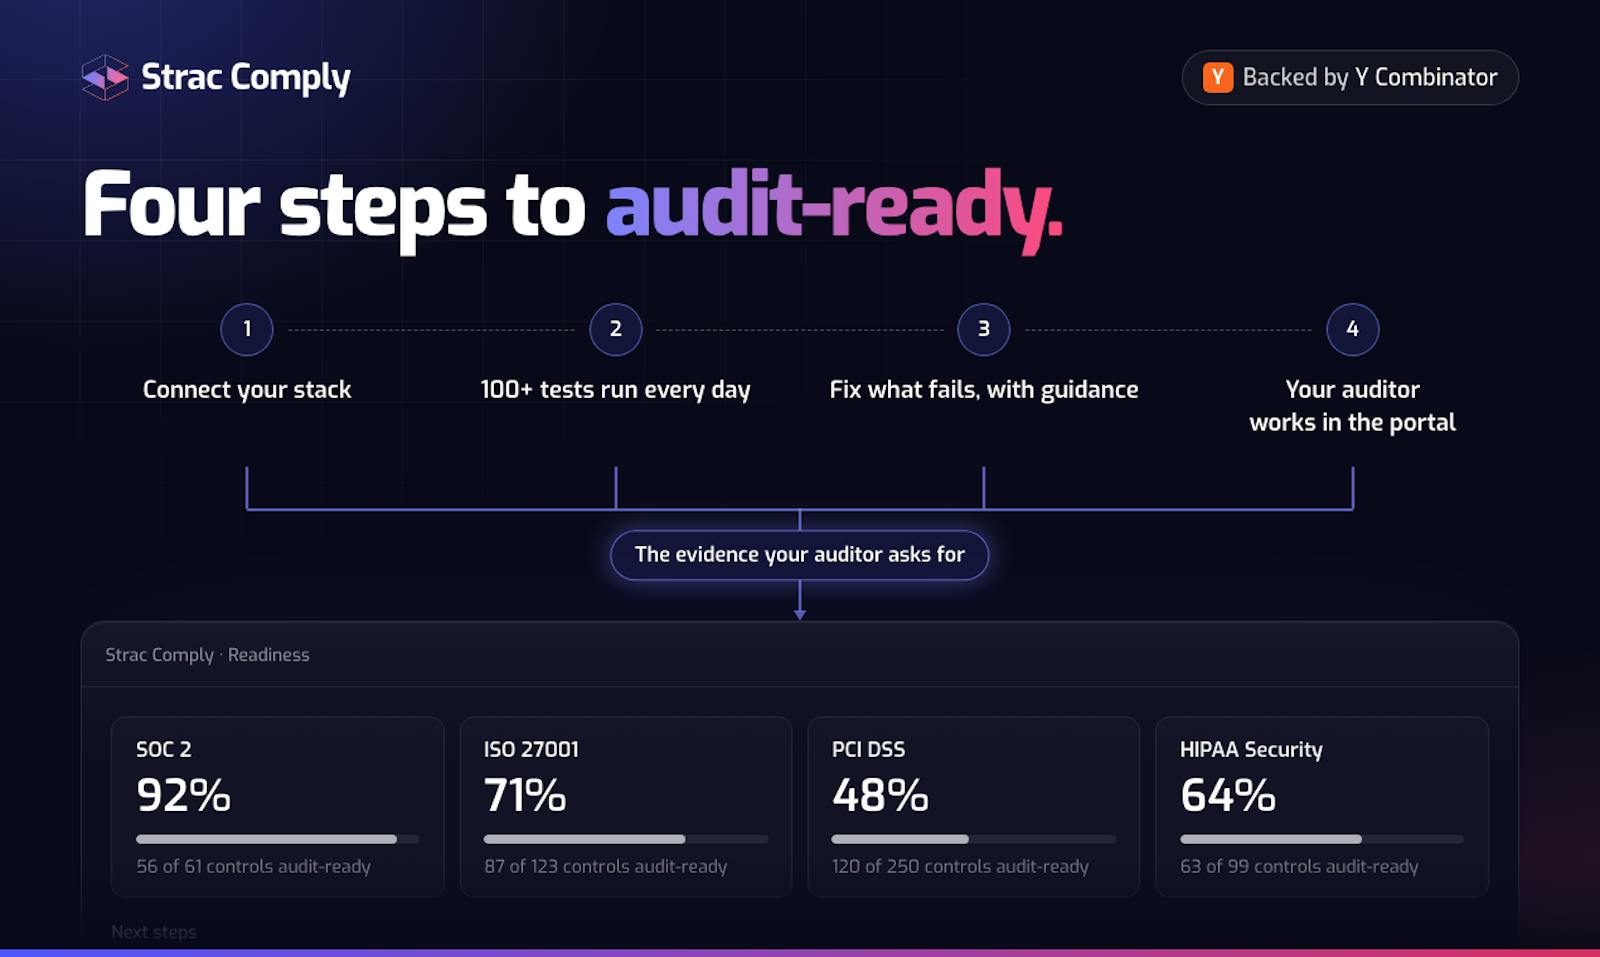
Readiness tracked per framework, so the second certification starts from the first one's evidence.
Who needs which, concretely
Your situation
What you need
An OEM contract names a TISAX label
TISAX at the assessment level and objectives the OEM specifies. ISO 27001 will not substitute.
A Mercedes-Benz dealer agreement
Either ISO 27001 or TISAX AL2. Both are accepted.
You sell to automotive and to everyone else
ISO 27001 first, then TISAX if and when an OEM asks.
You handle unreleased designs or physical prototypes
TISAX with the prototype protection objectives. Nothing else covers this.
You are told to 'get certified' with no standard named
Go back and ask which one. Guessing here is how companies pay for the wrong project.
✨ How Strac Comply runs ISO 27001 and TISAX off one control set
Strac Comply supports both. ISO 27001 is one of the frameworks on every plan from $4,995 a year with no per-framework fee, and TISAX is supported alongside it, mapped onto the same control and evidence model rather than run as a separate project.
That shared model is the whole point of the overlap described above. Because the VDA ISA catalogue is built on ISO 27001 Annex A, a control you implement once is tested once and reported against both. You are not collecting the same access review twice for two assessors.
The part that usually decides whether a programme survives its second year is evidence. Strac Comply's AI Evidence Agent captures the admin-panel screenshots, access reviews and workflow proof that other platforms leave to a person with a screenshot tool, and every control carries a named owner.
Access evidence is captured continuously rather than reconstructed before an assessment.
🎥 Watch Strac Comply skip the sales call
The same platform, the same control set, no demo gatekeeping before you can see it work.
🌶️ Spicy FAQs on TISAX vs ISO 27001
Can ISO 27001 replace TISAX?
It depends entirely on who is asking. If an automotive OEM has demanded a TISAX label, no: the label is shared through the ENX portal and an ISO 27001 certificate is not accepted in its place. If you are a Mercedes-Benz dealer, yes: ISO 27001 and TISAX AL2 are both accepted paths for that requirement. The question is never which standard is better, it is which one your contract names.
Is TISAX the same as ISO 27001 with extra steps?
Close, but not quite. The VDA ISA catalogue that TISAX assesses against is built on ISO 27001 Annex A and shares the majority of its controls, so the overlap is genuinely large. TISAX then adds two things ISO 27001 does not cover: prototype protection, which matters when unreleased vehicle designs are on your premises, and a dedicated data protection module. It also differs in mechanism, with a fixed three-year label shared through a central portal rather than a certificate you hand out yourself.
Which should I do first if I need both?
ISO 27001, in almost every case. It builds a management system you can reuse for every other customer and framework, and it is the foundation that takes a TISAX project from 12 to 18 months down to 3 to 6. Doing TISAX first gives you a label that satisfies automotive customers and very little that transfers elsewhere.
Does an ISO 27001 certificate shorten the TISAX assessment?
It shortens the preparation enormously, not the assessment itself. You still register with ENX, still complete the VDA ISA self-assessment, and still go through an accredited audit provider at AL2 or AL3. What disappears is the year of building an ISMS from nothing, which is where most of the time and cost sits.
What does TISAX cost compared with ISO 27001?
For a single-site small or mid-size company, a TISAX project runs roughly EUR 15,000 to 80,000 all in. ENX registration is EUR 400 to 500 per location and the AL2 or AL3 assessment provider is EUR 3,500 to 10,500; the rest is building and running the management system. That last part is the bulk of it, and it is also the part an existing ISO 27001 programme has already paid for.
Do I need TISAX if I only sell software to an automotive company?
Possibly. TISAX applies to whoever handles the OEM's information, not only to parts manufacturers, so a SaaS vendor processing engineering data or customer records can be asked for a label. The trigger is the contract and the information classification involved, not what industry you think you are in.
Customer story
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath
It depends entirely on who is asking. If an automotive OEM has demanded a TISAX label, no: the label is shared through the ENX portal and an ISO 27001 certificate is not accepted in its place. If you are a Mercedes-Benz dealer, yes: ISO 27001 and TISAX AL2 are both accepted paths for that requirement. The question is never which standard is better, it is which one your contract names.
Is TISAX the same as ISO 27001 with extra steps?
Close, but not quite. The VDA ISA catalogue that TISAX assesses against is built on ISO 27001 Annex A and shares the majority of its controls, so the overlap is genuinely large. TISAX then adds two things ISO 27001 does not cover: prototype protection, which matters when unreleased vehicle designs are on your premises, and a dedicated data protection module. It also differs in mechanism, with a fixed three-year label shared through a central portal rather than a certificate you hand out yourself.
Which should I do first if I need both?
ISO 27001, in almost every case. It builds a management system you can reuse for every other customer and framework, and it is the foundation that takes a TISAX project from 12 to 18 months down to 3 to 6. Doing TISAX first gives you a label that satisfies automotive customers and very little that transfers elsewhere.
Does an ISO 27001 certificate shorten the TISAX assessment?
It shortens the preparation enormously, not the assessment itself. You still register with ENX, still complete the VDA ISA self-assessment, and still go through an accredited audit provider at AL2 or AL3. What disappears is the year of building an ISMS from nothing, which is where most of the time and cost sits.
What does TISAX cost compared with ISO 27001?
For a single-site small or mid-size company, a TISAX project runs roughly EUR 15,000 to 80,000 all in. ENX registration is EUR 400 to 500 per location and the AL2 or AL3 assessment provider is EUR 3,500 to 10,500; the rest is building and running the management system. That last part is the bulk of it, and it is also the part an existing ISO 27001 programme has already paid for.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.