November 13, 2026

5
min read
EDM (Exact Data Match): Data Protection Technique
Learn about EDM (Exact Data Match) in DLP and Data Security
Exact data match is a detection method that identifies sensitive data by checking it against a known set of records you supply. You give the DLP system a source, such as a customer database export or a patient master index, and it learns those exact values. From then on, it flags content only when the content contains one of those values.
That is the difference from pattern detection. A regular expression finds anything shaped like a Social Security number. EDM finds the Social Security numbers that belong to your customers. A pattern tells you something looks sensitive; EDM tells you it is yours.
Because the reference data is itself sensitive, EDM systems do not keep it in readable form. Each value is normalized and hashed before it is stored, and incoming content is hashed the same way for comparison. The detector can confirm a match without ever holding a plain copy of the customer list.
Pattern detectors are good at well formed numbers with checksums, like card numbers. They struggle in three places that now carry most of the risk.
The first is noise. Order numbers, test data and sample cards in engineering tickets all look like real identifiers. Every false alert costs an analyst minutes, and enough of them teach the team to ignore the queue. Strac covers that problem in depth in reducing DLP false positives.
The second is data with no fixed shape. A customer ID, a policy number, an internal account code or a patient's full name tied to a date of birth has no universal pattern. Regex either misses it or matches half the company.
The third is volume of channels. A customer record used to leave through email or a file share. Today it is pasted into a Slack thread, dropped into a Google Doc, typed into a chatbot, or pulled by an AI agent into a summary. Each of those paths needs a detector precise enough to act on without a human checking every hit.
EDM answers all three. It is quiet because it ignores values you do not own, and it handles any format because it matches the value itself, not its shape.
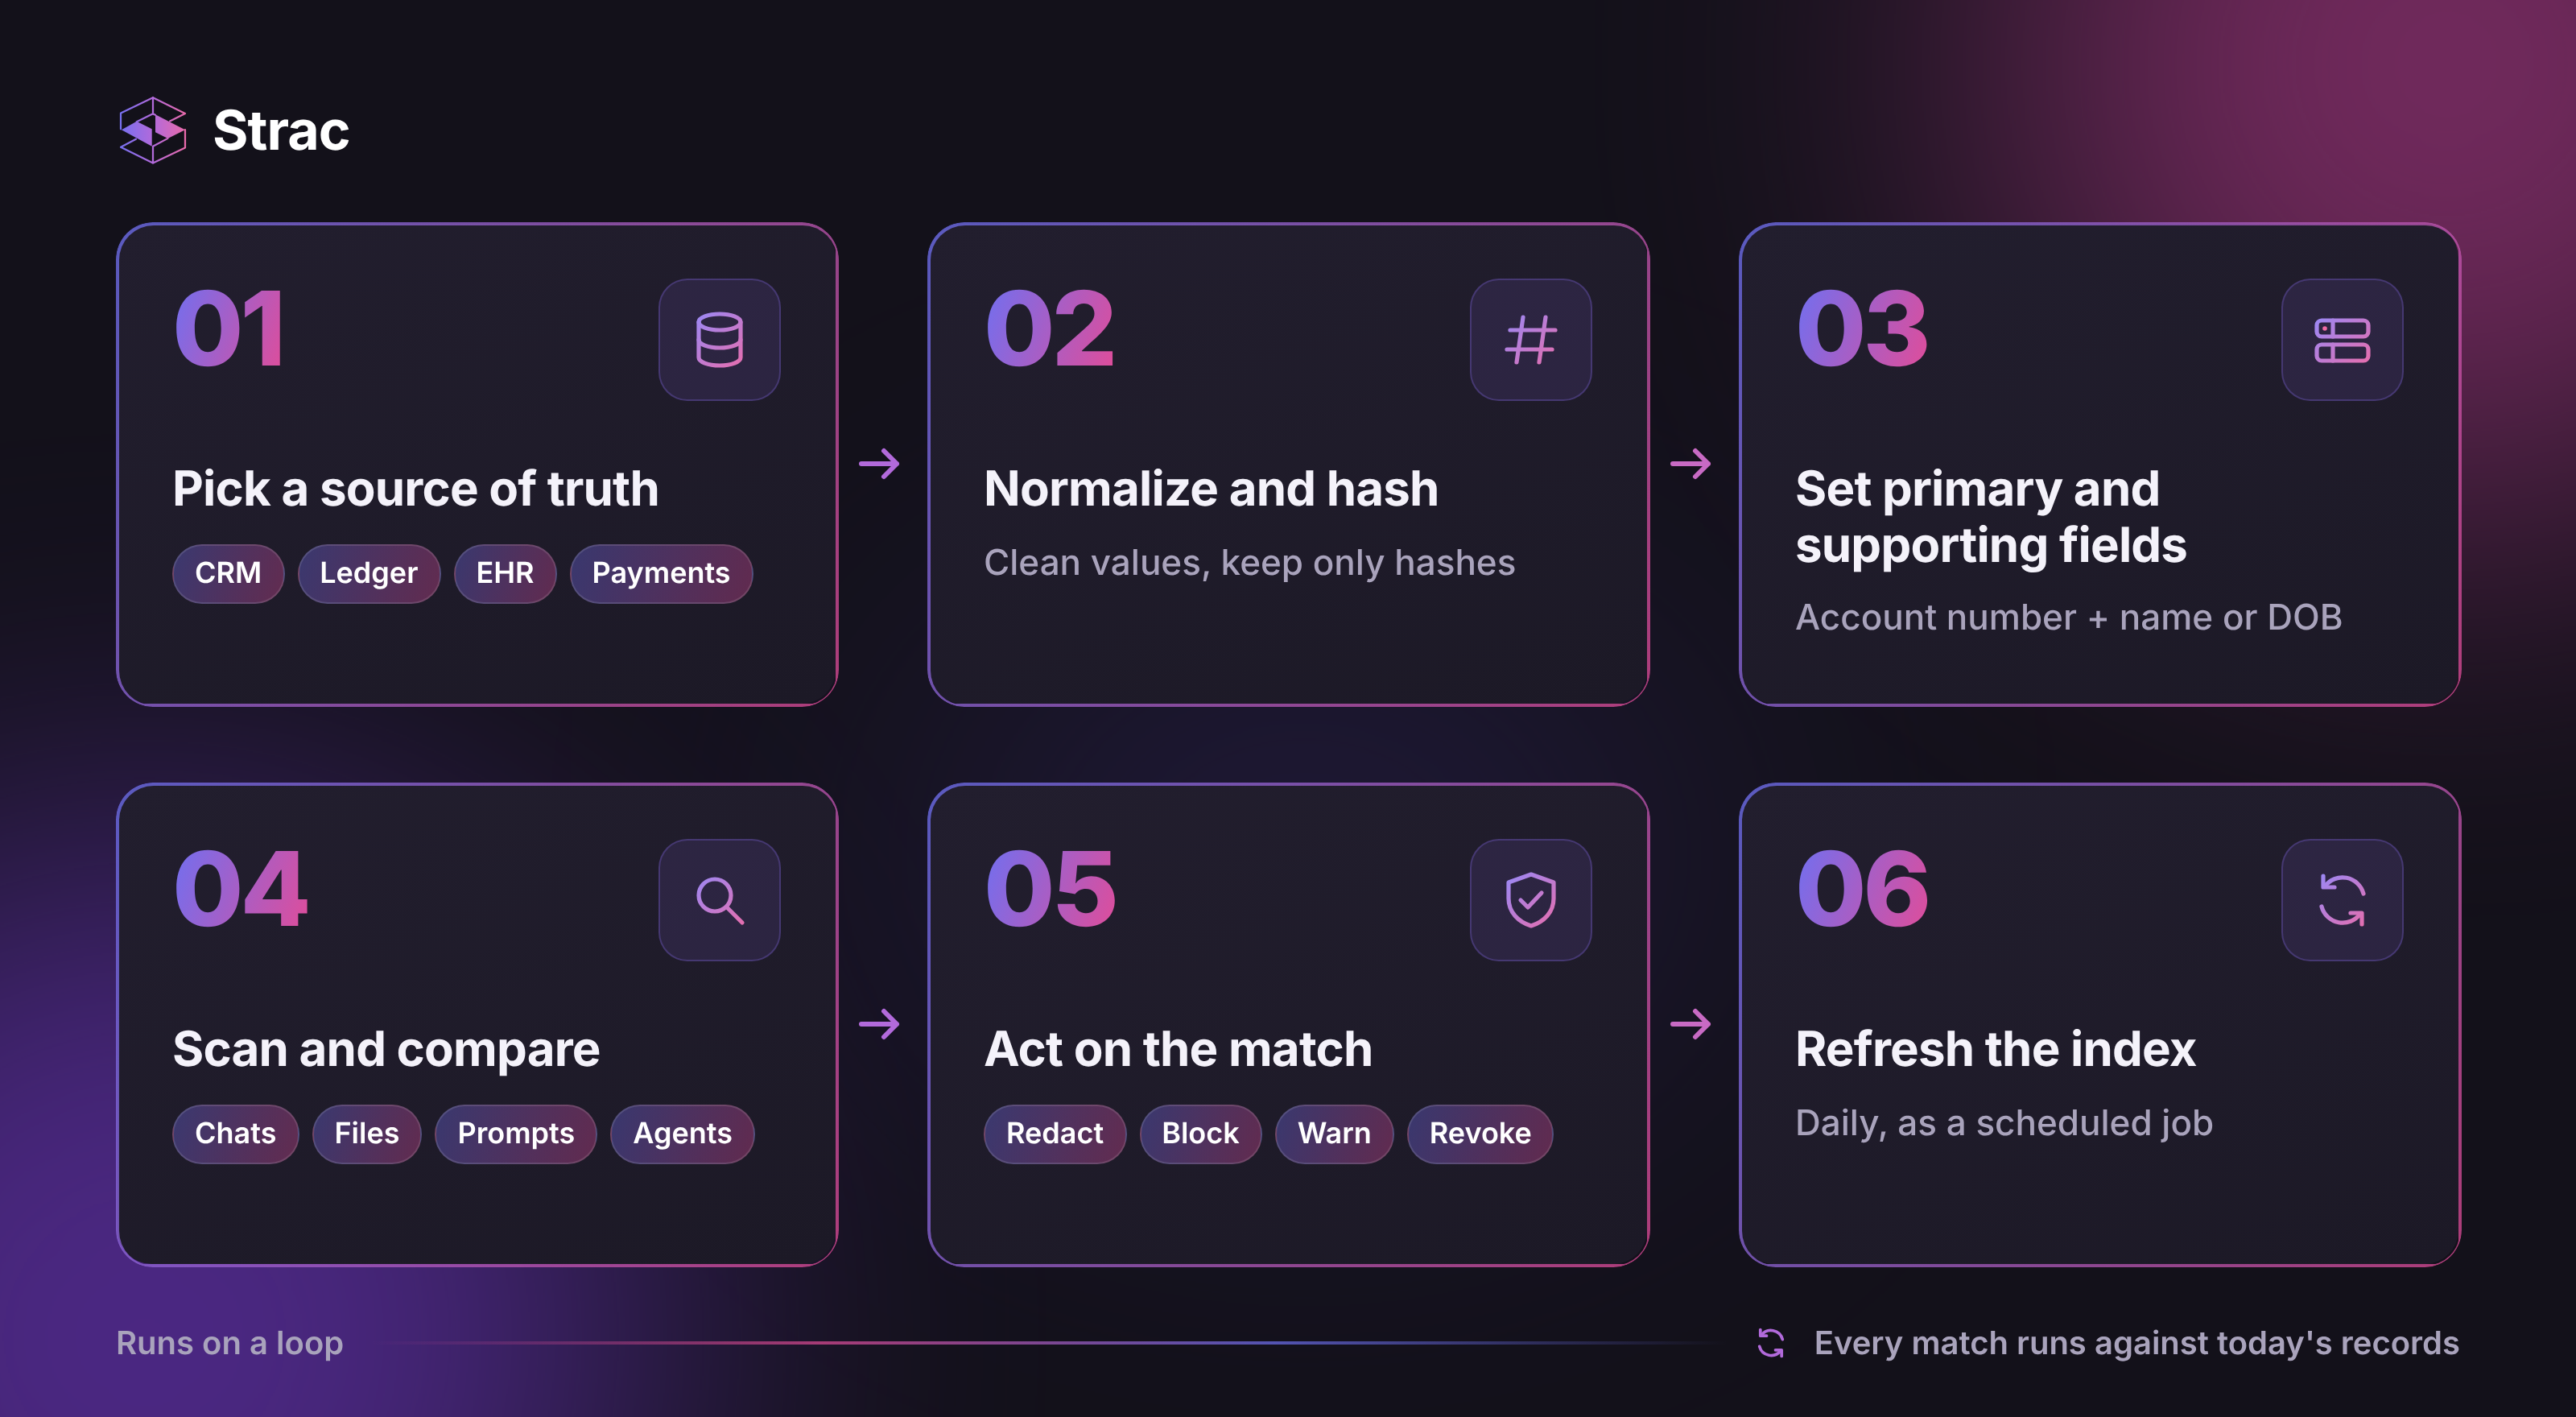
Every EDM implementation follows the same basic steps.
1. Choose the source of truth. Pick the system that holds the records you most need to protect: the CRM, the core banking ledger, the electronic health record, the payments vault. Export only the columns that matter.
2. Normalize and hash. Values are cleaned so that formatting differences do not break matches. Spaces, dashes and letter case are standardized, then each value is hashed. The plain export is deleted once indexing finishes.
3. Set primary and supporting fields. A primary field is the value that must appear, such as an account number. Supporting fields, such as a last name or date of birth, raise confidence when they appear nearby. A policy can require the account number plus one supporting field before it fires, which removes most coincidental matches.
4. Scan content and compare. As messages, files, prompts and tool calls flow through, the detector extracts candidate values, hashes them, and checks them against the index.
5. Act on the match. A confirmed match triggers the policy action: redact, block, warn the user, or revoke a share.
6. Refresh the index. Customers join and leave every day. An index that refreshes weekly protects last week's customers; one that refreshes daily protects today's. Treat the refresh as a scheduled job, not a project.
Financial services. A bank indexes every customer account number. When an employee pastes a statement into a Slack channel with an outside partner, or uploads it to an unapproved tool, EDM confirms the number belongs to a real customer and acts. Random numbers in a spreadsheet of test data pass untouched. See how this applies to PCI DSS scope.
Healthcare. A provider indexes medical record numbers alongside patient names and dates of birth. A support agent who pastes a patient's details into a ticket or a chatbot triggers a match, while generic clinical text does not. This keeps HIPAA controls focused on actual protected health information rather than every number in a chart. The full list of identifiers is in the HIPAA data elements guide.
Retail and payments. A merchant indexes stored card tokens and the card numbers behind them. Card data showing up in email, a shared drive or a customer support macro is caught by value, not by guesswork.
SaaS and technology companies. Customer IDs, tenant identifiers and contract numbers have no public format. EDM is often the only way to detect them reliably when they leak into Jira tickets, Notion pages or Google Drive.
AI prompts and agents. This is the newest use case and the fastest growing one. An analyst pastes a customer export into ChatGPT to summarize churn. An AI agent with database access answers a question and includes ten real customer rows in its reply. EDM checks the prompt, the file upload and the agent's tool output against your records, so the model receives the question and not the customer data.
These three methods are often confused, and a mature program uses all of them.
Pattern detection finds values by shape and checksum. It needs no setup and covers common identifiers out of the box, but it cannot tell your data from anyone else's.
Exact data match finds specific values from structured records you provide, such as rows in a table. It is the most precise option for customer, patient and account data.
Document fingerprinting finds copies or partial copies of specific unstructured files, such as a contract template, a board deck or source code. It answers a different question: is this our document, rather than is this our customer.
Start with pattern detection for broad coverage, add EDM for the records that define your business, and add fingerprinting for the documents that would hurt most if they left.
The detection method only matters if it sits where data actually moves. Five surfaces now carry most sensitive records.
SaaS apps at rest and in motion. Records sit for years in Slack DLP channels, Google Workspace DLP files and support tools like Zendesk DLP. EDM has to scan history, not just new traffic.
Endpoints. Exports land in Downloads folders and leave through USB, uploads and the clipboard. Endpoint DLP is where EDM catches a customer list before it leaves the laptop.
The browser. Web apps and unmanaged devices never touch a network proxy. Browser DLP brings the same detector to any device running the extension.
Generative AI tools. Prompts and file uploads to ChatGPT, Claude, Gemini and Copilot are a direct path for customer data. AI DLP applies EDM before the prompt is sent, and Shadow AI visibility shows which unapproved tools are receiving it.
AI agents over MCP. Agents read databases and call tools on their own. MCP DLP inspects each tool call and response, so an agent that is tricked or misconfigured still cannot pass real customer records to the wrong place.
Strac is a DLP, data discovery and DSPM platform that works at the data layer. EDM is one of its detectors, running alongside built in detectors for PII, PHI, PCI data and secrets, custom detectors, and OCR for images and PDFs.
Ingestion that fits your stack. Strac accepts structured datasets from the systems you already use, including databases, cloud storage and CSV exports. Values are hashed on ingestion, so Strac matches against your records without storing them in readable form.
One index, every surface. The same EDM policy applies across SaaS DLP, endpoint DLP, Browser DLP, AI DLP and MCP DLP. DSPM scans historical data in SaaS and cloud storage, so a customer list shared two years ago is found today.
Remediation, not just alerts. When an exact match is confirmed, Strac acts in this order:
Evidence for auditors. Every match and action is logged with the policy, time and outcome, mapped to SOC 2, ISO 27001, HIPAA, PCI DSS and GDPR. More on the remediation side is in DLP remediation.

👉 Related reading:
Patterns guess, proxies see only what passes through them, and identity controls fail when an account or agent is compromised. The data layer is the backstop: know which records are yours, find them wherever they move, and redact them on every action so a slip never becomes a breach. Strac runs exact data match across SaaS, cloud, endpoints, browsers, generative AI and MCP from one policy.
Book a demo to see EDM working on your own records.
No. EDM matches specific values from structured records, such as account numbers in a customer table. Fingerprinting matches copies of specific unstructured documents, such as a contract or design file. Most programs use EDM for customer data and fingerprinting for intellectual property.
Most DLP tools ship with pattern detectors for public formats like card and Social Security numbers. Internal IDs have no public pattern, so they need EDM or a custom detector. Many older tools also run EDM only on email and network traffic, not inside SaaS or AI tools.
No, and it should not block work either. Matching runs against hashed values, and the right response is usually redaction rather than blocking. The message, ticket or prompt goes through with the matched record removed, so people keep working and the record stays put.
Not on its own. EDM only knows the records you index, so a stale index or a missing table leaves gaps. That is why the data layer needs several detectors at once, and why redacting matches on every action matters more than any single method.
EDM is a detection technique inside data classification, which feeds DLP and DSPM policy. It works best paired with pattern and custom detectors and with remediation that acts on matches. See sensitive data discovery and classification for the full picture.
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath









Customers include