The best compliance management software in 2026 for SOC 2, ISO 27001, HIPAA, GDPR, and AI frameworks — compared on automation, evidence, audit, and price. See why Strac Comply bundles compliance with data security in one platform.
Compliance management software automates the work of getting and staying compliant — mapping controls, collecting evidence, monitoring continuously, and producing audit-ready proof across SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, and now the AI frameworks (ISO 42001, NIST AI RMF, EU AI Act).
The market splits into compliance automation tools (Vanta, Drata, Secureframe, Sprinto), GRC suites (Hyperproof, OneTrust, AuditBoard), and a new AI-native + data-security category led by Strac Comply.
The differentiator that matters in 2026: does the platform also protect the data the compliance is about? Strac Comply is the only one here that bundles compliance with built-in DLP/DSPM — so your data-protection controls are evidenced automatically, not with a second tool.
Choose on: framework breadth, real-evidence vs. checkbox automation, audit model, transparent pricing, and AI-readiness.
Get compliant with Strac Comply, from $4,995 all-in
SOC 2, ISO 27001, PCI DSS, HIPAA, and GDPR in one platform. Transparent pricing, a 14-day free trial, and no mandatory sales call, unlike Vanta and Drata.
Compliance management software replaces the spreadsheets, screenshots, and manual evidence-gathering that used to define an audit. A modern platform:
Maps your controls to one or more frameworks (SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, ISO 42001).
Connects to your stack (cloud, identity, code, HR, SaaS) to pull evidence automatically.
Monitors continuously and flags drift before it becomes an audit finding.
Produces audit-ready evidence, and increasingly, runs the audit through an in-platform network.
The category started with "automate SOC 2." In 2026 the bar is higher: multi-framework, real continuous testing, AI governance, and proof that sensitive data is actually protected.
Modern compliance is only as strong as your coverage of where data actually lives. Browse [all integrations](https://www.strac.io/integrations).
Real evidence, not checkboxes, continuous testing that a control holds, not just an integration toggle.
Audit model, in-platform auditor network vs. bring-your-own, and whether a penetration test is included.
Data-security evidence, can it prove data-protection controls (SOC 2 CC6.7, HIPAA, PCI, GDPR Art. 32) with real DLP/DSPM?
Transparent pricing, flat vs. modular with add-on creep.
AI-native, built for the controls auditors now ask about.
The 8 Best Compliance Management Platforms in 2026
1. Strac Comply, Compliance + Data Security in One, AI-Native
The only platform that bundles compliance automation with built-in data security (DLP/DSPM). Covers SOC 2, ISO 27001, HIPAA, GDPR, and PCI DSS plus the AI frameworks, runs a native penetration test (PentestMate), and lets AI agents write evidence into your binder. Because Strac’s DSPM and DLP discover and inventory the sensitive data behind data-protection controls, the hardest controls (CC6.7, PCI PAN handling, GDPR Art. 32) collect themselves. Best for teams that want compliance and data protection from one vendor.
2. Vanta A large, established compliance automation platform with a broad integration library. Pricing is sales-led, with modular add-ons at renewal. See Vanta alternatives.
3. Drata A large continuous-compliance platform, common in mid-market SaaS. Pricing is sales-led. See Drata alternatives.
4. Secureframe An established compliance automation platform with a clean UI. Pricing is sales-led. See Secureframe alternatives.
5. Hyperproof, Enterprise GRC
Deeper risk and evidence workflows for larger programs managing many frameworks.
6. AuditBoard, Enterprise Audit & Risk
A connected-risk platform for large internal-audit, risk, and compliance teams.
7. OneTrust, Privacy + GRC Suite
Enterprise privacy, governance, and compliance together; absorbed Tugboat Logic.
8. Thoropass, Platform + Audit Bundled
Software plus audit services under one roof, a single vendor for the platform and the audit.
Strac Comply vs. the Field
Strac Comply
Automation tools (Vanta/Drata)
GRC suites (OneTrust/AuditBoard)
Compliance automation
✅
✅
Partial
Built-in data security (DLP/DSPM)
✅ unique
❌ separate tool
❌
Native penetration test
✅
Marketplace
❌
AI frameworks (ISO 42001 / NIST AI RMF)
✅ native
Add-on
Partial
Pricing
Flat
Modular add-ons
Enterprise
Best for
Compliance + data protection in one
First SOC 2, mid-market
Large enterprise GRC
🎥 The Strac Comply Difference: Compliance That Protects the Data
Every tool above manages compliance. Only Strac also protects the data the compliance exists for. The controls teams struggle most to prove are the data ones, SOC 2 CC6.7, HIPAA minimum-necessary, PCI PAN handling, GDPR Art. 32, because they require showing sensitive data is actually discovered, classified, and remediated. Strac's DLP and DSPM do exactly that across SaaS, cloud, GenAI, browser, and endpoints, and that produces the evidence, no second vendor, no manual screenshots.
What Modern Compliance Management Software Should Do in 2026
The category has moved past "connect integrations and watch a dashboard." A 2026-grade platform has to generate evidence, not just check for it; cover the data layer, not just the config layer; and put an AI agent on the repetitive work. Strac Comply was designed around exactly those three shifts.
On evidence, its AI Evidence Agent navigates SaaS admin panels and captures the manual, screenshot-grade proof that legacy tools leave to a human. On the data layer, Comply is powered by Strac's DSPM/DLP core, detecting and redacting sensitive data in real time, which doubles as live evidence for your data-protection controls. On AI, Headless Compliance lets your own AI agent write evidence into the binder over MCP. Surrounding all of it: 100+ continuous tests, native pentesting, SaaS security and shadow-IT/shadow-AI discovery from OAuth grants, a branded Trust Center, AI-answered security questionnaires, and cross-framework deduplication so one piece of evidence satisfies SOC 2, ISO 27001, GDPR (78 controls), PCI DSS (231 controls), HIPAA, ISO 42001, NIST, and FedRAMP at once.
For the head-to-head on the two best-known platforms, see Vanta vs Drata.
For teams pursuing SOC 2, ISO 27001, PCI DSS, HIPAA, or NIST CSF, the best compliance management software combines automated evidence collection, 100+ tests with named fixes, generated policies, vendor risk, and a trust portal. Strac Comply does all of this across all five frameworks from $4,995 per year, transparently priced, where Vanta, Drata, and Secureframe are sales-led.
How much does compliance management software cost?
Sales-led platforms reported at $7,500 to $30,000 or more per year and quote by company size and framework count. Strac Comply publishes $4,995 Platform, $8,995 Certified with the audit, and $12,995 Security-First, with no per-framework fees.
Is compliance management software the same as GRC software?
No. Compliance management software focuses on getting and staying compliant with specific frameworks (SOC 2, ISO 27001, HIPAA). GRC software is broader enterprise governance, risk, and compliance tooling. Most startups and mid-market teams need compliance management software, which is faster and cheaper.
What is the best compliance management software?
The large incumbents, Vanta and Drata, cover a first SOC 2, and OneTrust and AuditBoard serve enterprise GRC, but all are sales-led with pricing behind a call. Strac Comply is the best fit when you want compliance automation and data security in one AI-native platform, its DLP/DSPM discovers and inventories sensitive data for specific data-protection controls such as SOC 2 CC6.7 and PCI DSS 12.5.2 and it includes a native pentest.
What's the difference between compliance management and compliance automation software?
Compliance automation focuses on continuously collecting evidence and monitoring controls (Vanta, Drata, Strac Comply). Compliance management (or GRC) is broader, risk registers, policy management, audits across the enterprise (OneTrust, AuditBoard, Hyperproof). Many modern platforms do both; Strac Comply adds the data-security layer the others lack.
How much does compliance management software cost?
It ranges widely, startup automation tools often start around $7K-$10K/year and scale with frameworks and add-ons; enterprise GRC suites run much higher. Watch for modular pricing that climbs at renewal, and confirm what's included vs. an add-on.
Does compliance management software include data security?
Almost none do, they manage compliance but rely on a separate DLP/DSPM tool for actual data protection. Strac Comply is the exception: it bundles data security so data-protection controls are evidenced automatically.
Which compliance platform is best for AI governance?
Beyond automation, Strac Comply's AI Evidence Agent (a Chrome extension) collects the last-mile evidence other platforms leave to humans, admin-panel screenshots, monthly access reviews, auditor-ready. Its headless compliance MCP server lets Claude Code or Cursor write evidence into your binder, and it dedupes controls across frameworks so you collect once and reuse everywhere. See Strac Comply.
The Bottom Line
The compliance-software market has matured past "automate SOC 2." The large incumbents, Vanta and Drata, lead on brand, and OneTrust and AuditBoard lead on enterprise GRC, but every one is sales-led. But if you want the platform built for 2026, compliance and data security in one, a native pentest, and AI frameworks out of the box, Strac Comply is the one to demo.
✨ How Strac Comply handles compliance management, end to end
Strac Comply runs your entire compliance program from one place: frameworks, controls, automated tests, evidence, documents, vendor risk, and a trust portal, with transparent pricing and no sales call to see a number. Here is what that looks like.
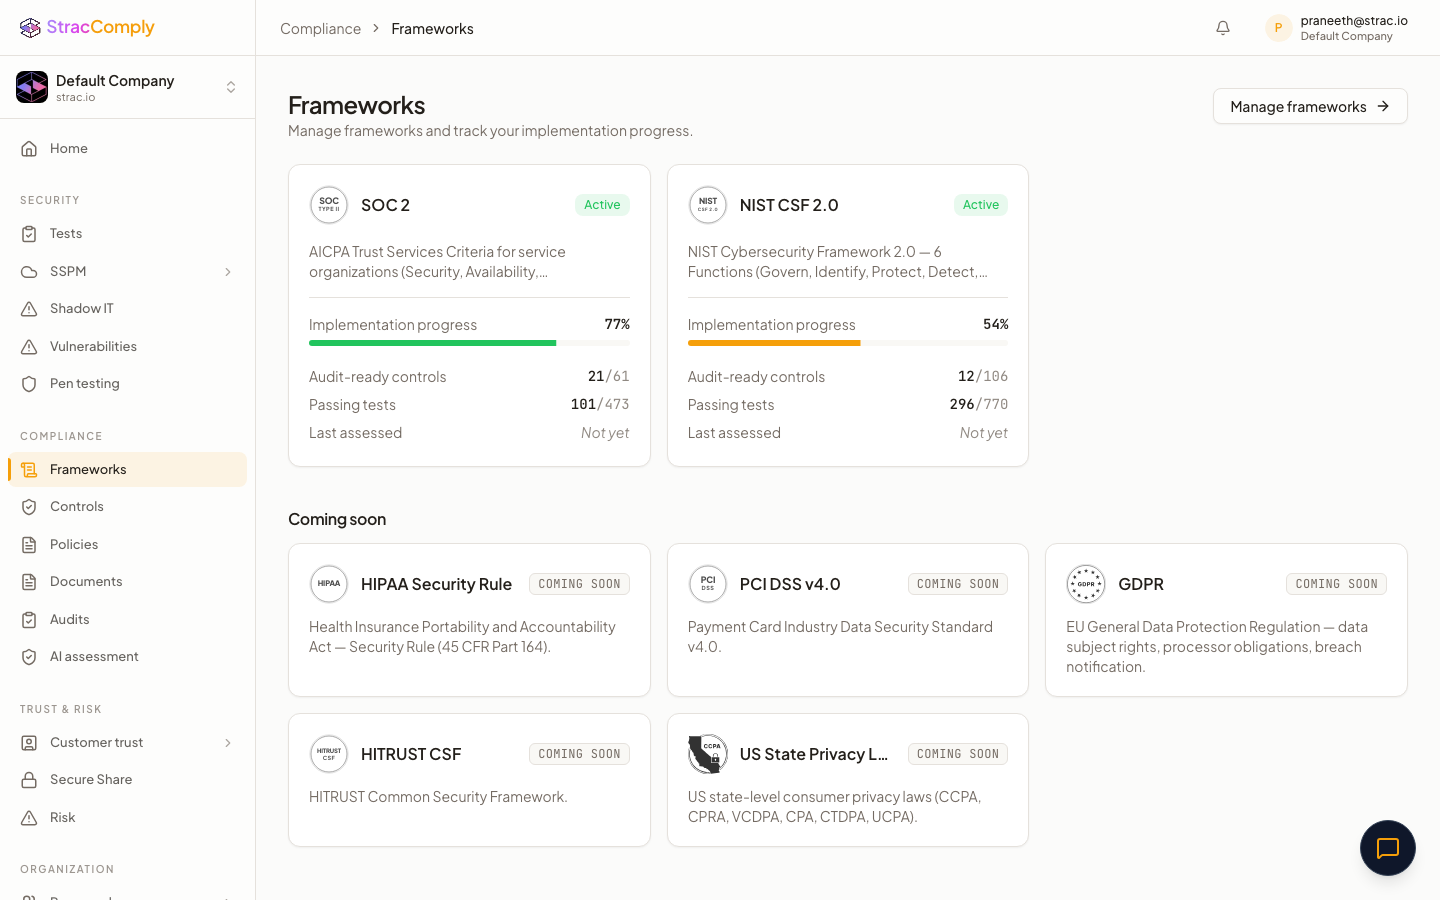
One dashboard, every framework: see exactly where each program stands.
✨ Every framework in one platform
SOC 2, ISO 27001, PCI DSS, HIPAA, and NIST CSF run from a single control set, so evidence you collect for one framework satisfies the overlapping controls in the others. No separate tool per standard.
Five frameworks, one shared control set, map evidence once, reuse everywhere.
✨ Controls tracked to completion, not guesswork
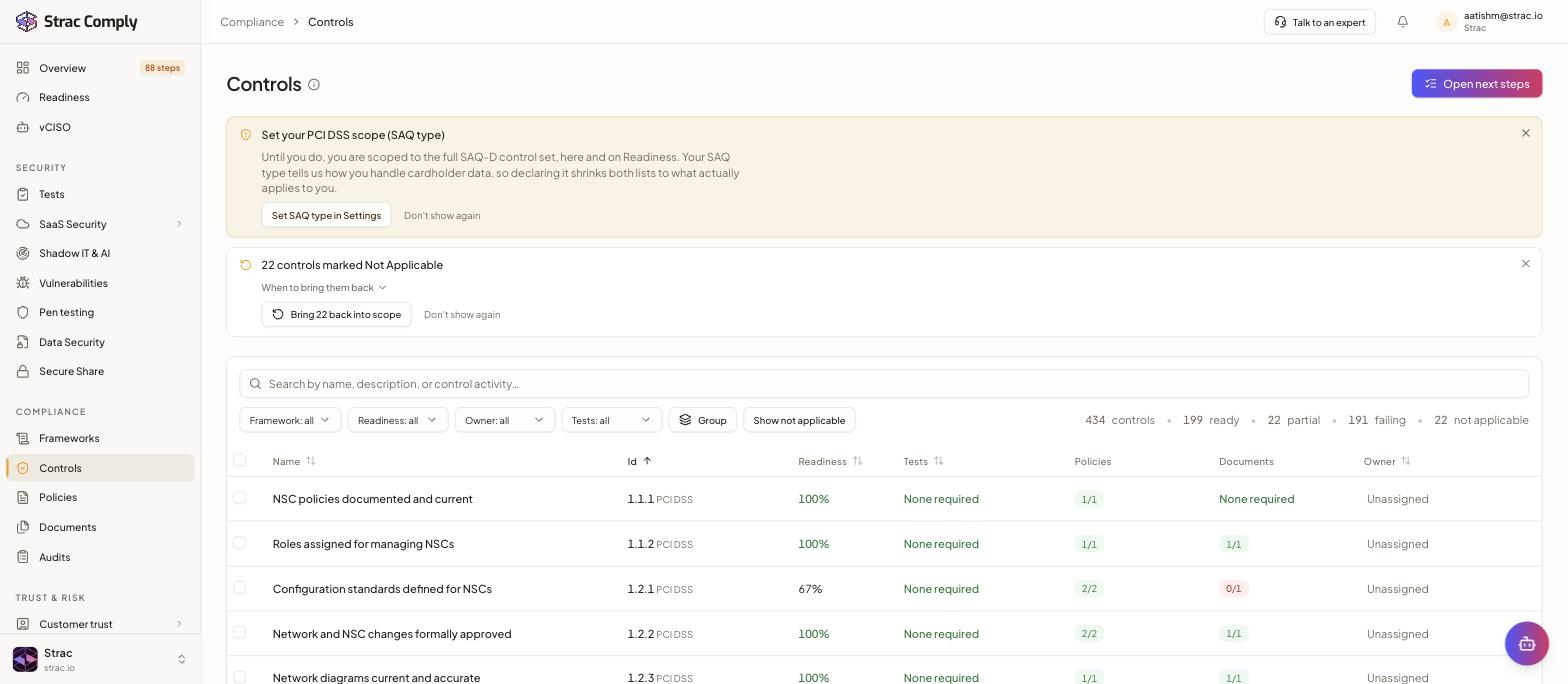
Every control shows its completion status, owner, and what is left. For SOC 2 that is all 65 Common Criteria controls, each tied to the evidence that proves it.
65 SOC 2 controls, each with a status, an owner, and the evidence behind it.
✨ 146 automated tests that name exactly what to fix
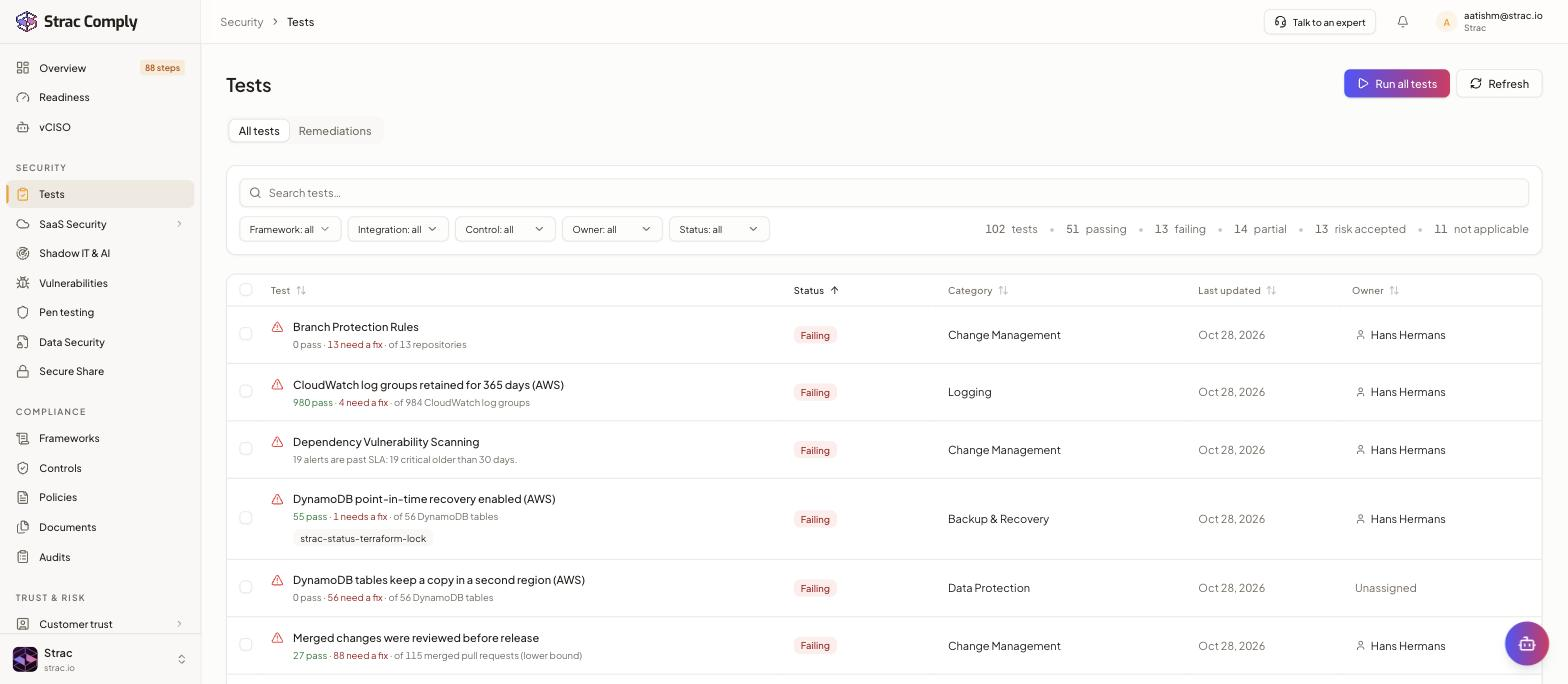
Strac Comply runs 146 automated tests across your connected systems. A failing test does not just flag a gap, it names the system, the owner, and the exact fix, so readiness is a to-do list, not a research project.
146 automated tests, every failure comes with the fix, not just an alert.
✨ Policies and documents generated, not downloaded as templates
The 93 documents SOC 2 requires are generated and tied to the controls they satisfy, so your policies, procedures, and records stay current and audit-ready between audits.
93 SOC 2 documents, generated and linked to the controls they prove.
✨ Vendor risk that lives beside your evidence
Score vendors by inherent risk, track them in the same platform as your controls, and let the AI draft the security-questionnaire answers your own customers send you.
Vendor risk scoring and monitoring, reproducible and beside your framework evidence.
AI drafts your security-questionnaire answers from your own evidence.
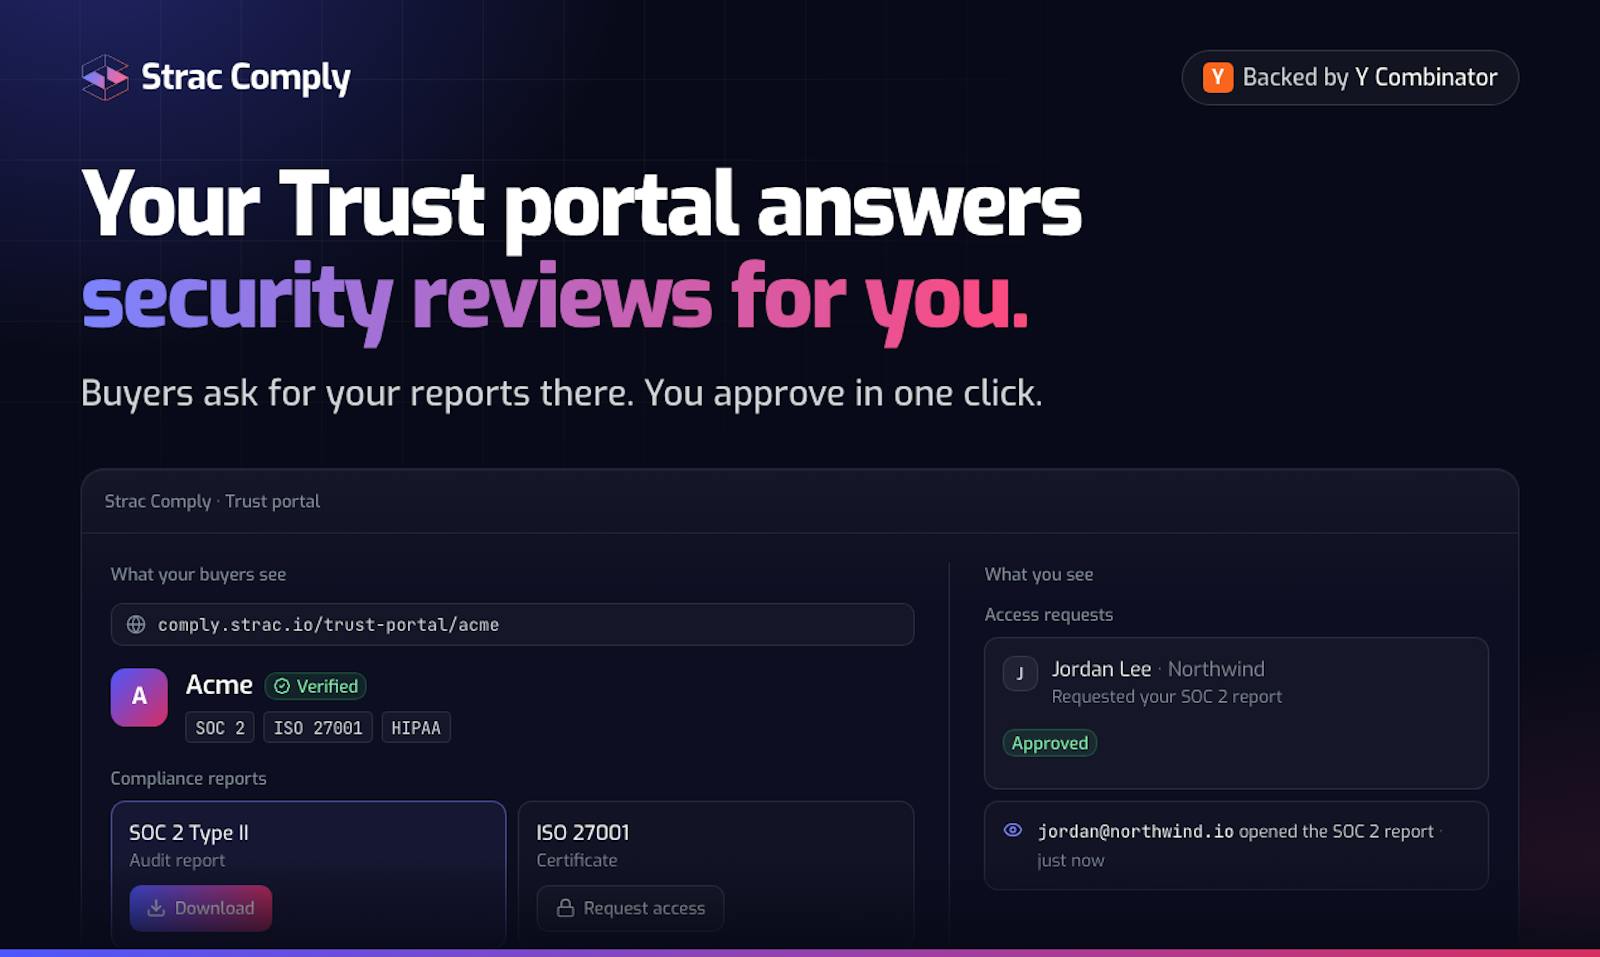
✨ A trust portal that answers security reviews for you
Buyers request your SOC 2 report, ISO certificate, and security documentation straight from a trust portal, and you grant access in one click, replacing the email-a-PDF ritual that slows every deal.
A trust portal that shortens every security review in your sales cycle.
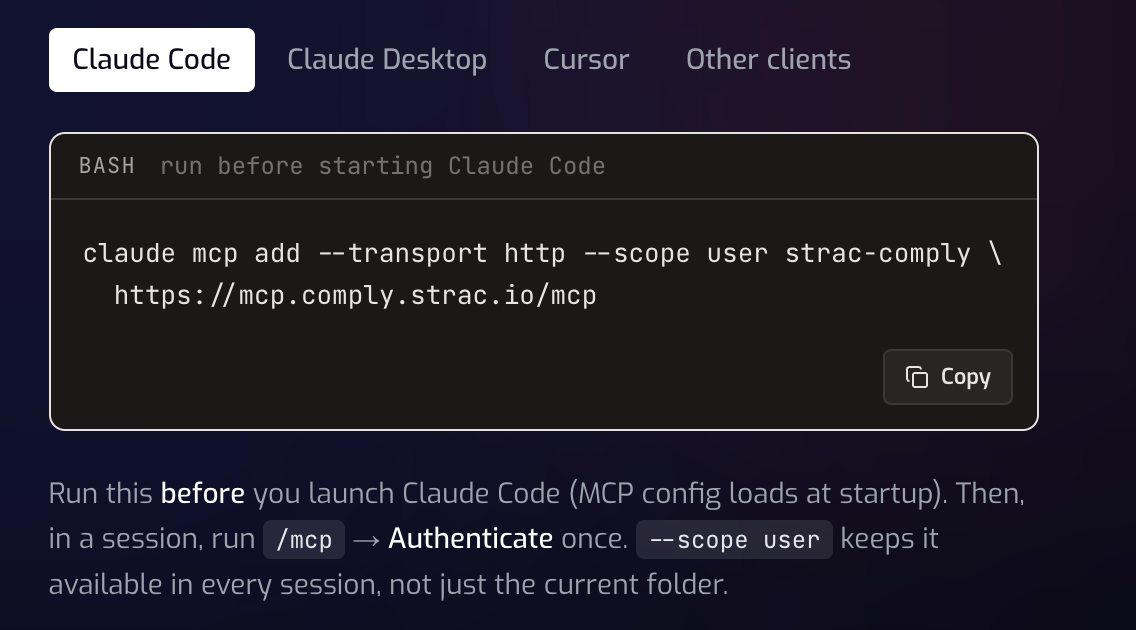
✨ Run compliance from your AI agent over MCP
Connect Strac Comply’s MCP server to Claude Code, Cursor, or Codex and ask your AI agent what is failing, apply the fix, and rerun the test without opening a dashboard. No sales-led compliance tool offers this.
Headless compliance: run your program from Claude Code, Cursor, or Codex.
💳 Strac Comply pricing: transparent, no sales call
Unlike every other platform on this list, Strac Comply publishes its price. Platform is $4,995 per year (all five frameworks, 146 automated tests, trust portal, vendor risk, MCP server, self-serve with a 14-day free trial), Certified is $8,995 per year (adds a SOC 2 Type I or Type II audit by an independent licensed CPA plus a human vCISO), and Security-First is $12,995 per year (adds a penetration test and Strac DLP for Slack, Google Workspace, and AI tools). Start free at comply.strac.io, no credit card. Compare on Vanta pricing, Drata pricing, and the full compliance automation cost breakdown.
Compliance management software vs GRC software: what is the difference?
Compliance management software automates a specific job: getting and staying compliant with frameworks like SOC 2, ISO 27001, and HIPAA, collecting evidence, running tests, and managing audits. GRC (governance, risk, and compliance) software is broader and often enterprise-heavy, covering enterprise risk, policy, and audit across the whole organization. For most startups and mid-market teams pursuing SOC 2 or ISO 27001, dedicated compliance management software like Strac Comply is faster to value and far cheaper than a legacy GRC suite.
How long does compliance management software take to implement?
With the right software, most teams reach audit-readiness in weeks, not months:
Day 1: connect your systems (cloud, identity, HR, code) over API and run the first automated tests.
Week 1: see your readiness score, the failing controls, and the named fixes.
Weeks 2 to 6: remediate gaps, generate policies and documents, and collect evidence continuously.
Audit: the auditor pulls evidence from the platform; for Type II, controls run across your observation window.
Strac Comply Platform is self-serve, so you can start today with a 14-day free trial, no sales call.
Customer story
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath
It depends on your needs: Vanta and Drata for a first SOC 2, Secureframe and Sprinto for budget-friendly startups, OneTrust and AuditBoard for enterprise GRC. Strac Comply is the best fit when you want compliance automation and data security in one AI-native platform — its DLP/DSPM discovers and inventories sensitive data for specific data-protection controls such as SOC 2 CC6.7 and PCI DSS 12.5.2 and it includes a native pentest.
What's the difference between compliance management and compliance automation software?
Compliance automation focuses on continuously collecting evidence and monitoring controls (Vanta, Drata, Strac Comply). Compliance management (or GRC) is broader — risk registers, policy management, audits across the enterprise (OneTrust, AuditBoard, Hyperproof). Many modern platforms do both; Strac Comply adds the data-security layer the others lack.
How much does compliance management software cost?
It ranges widely — startup automation tools often start around $7K–$10K/year and scale with frameworks and add-ons; enterprise GRC suites run much higher. Watch for modular pricing that climbs at renewal, and confirm what's included vs. an add-on.
Does compliance management software include data security?
Almost none do — they manage compliance but rely on a separate DLP/DSPM tool for actual data protection. Strac Comply is the exception: it bundles data security so data-protection controls are evidenced automatically.
Which compliance platform is best for AI governance?
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.