Secureframe Alternatives: Top 10 Secureframe Competitors for SOC 2 & Compliance Automation in 2026
Looking for a Secureframe alternative? Compare Strac Comply and 9 other Secureframe competitors across SOC 2, HIPAA, ISO 27001, and continuous compliance. 2026 guide.
Secureframe is a mid-market compliance automation platform with broad framework coverage and a solid template library for SOC 2, HIPAA, ISO 27001, PCI, and GDPR. The reasons teams evaluate alternatives in 2026 are consistent: no native DLP / DSPM, no AI / MCP audit-surface coverage, multi-framework pricing that scales fast.
Strac Comply is the #1 Secureframe alternative in this 2026 guide because it combines compliance automation with continuous data security (Strac DLP + DSPM + MCP DLP) in a single platform, the same product protecting your data is generating your audit evidence.
The single biggest 2026 differentiator: MCP DLP. AI agents reading your SaaS via Model Context Protocol are a new compliance surface. Strac is the only platform shipping MCP DLP across 18 SaaS connectors.
Evaluating Secureframe alternatives?Strac Comply is the only compliance automation platform that ships with continuous data security (Strac DLP + DSPM + MCP DLP for AI agents), one platform, one bill, full SOC 2 / HIPAA / ISO 27001 / GDPR / PCI / EU AI Act coverage. Start at comply.strac.io →
Secureframe is a real product with real customers. The reasons enterprises evaluate alternatives in 2026:
Compliance + DLP + DSPM should be one platform. SOC 2 CC6.6 / CC6.7 evaluate data classification, DLP, encryption. Secureframe ingests DLP evidence but doesn't ship one. Strac Comply ships Strac DLP and Strac DSPM with the platform.
AI / MCP coverage is a 2026 buyer ask. AI agents reading your SaaS via Model Context Protocol are a new audit surface. Strac is the only compliance platform with native MCP DLP.
Multi-framework pricing. Secureframe scales pricing with frameworks. Multi-framework programs become expensive.
Time-to-first-evidence. Strac integrations deploy in under 10 minutes per workspace.
Pre-built mappings for emerging frameworks, EU AI Act, ISO 42001. Strac maps these natively.
If any of those matter, you need a broader platform than Secureframe.
✨ What to Look For in a Secureframe Alternative
Compliance + DLP + DSPM in one platform.
Continuous evidence collection across cloud, SaaS, endpoint, AI surfaces.
MCP DLP coverage for AI agents.
Multi-framework mapping, SOC 2, HIPAA, ISO 27001, GDPR, PCI DSS, EU AI Act, ISO 42001.
Under-10-minute integration deploys.
AI-drafted policy templates.
Access review automation.
Vendor risk management.
Trust center.
Real customer outcomes.
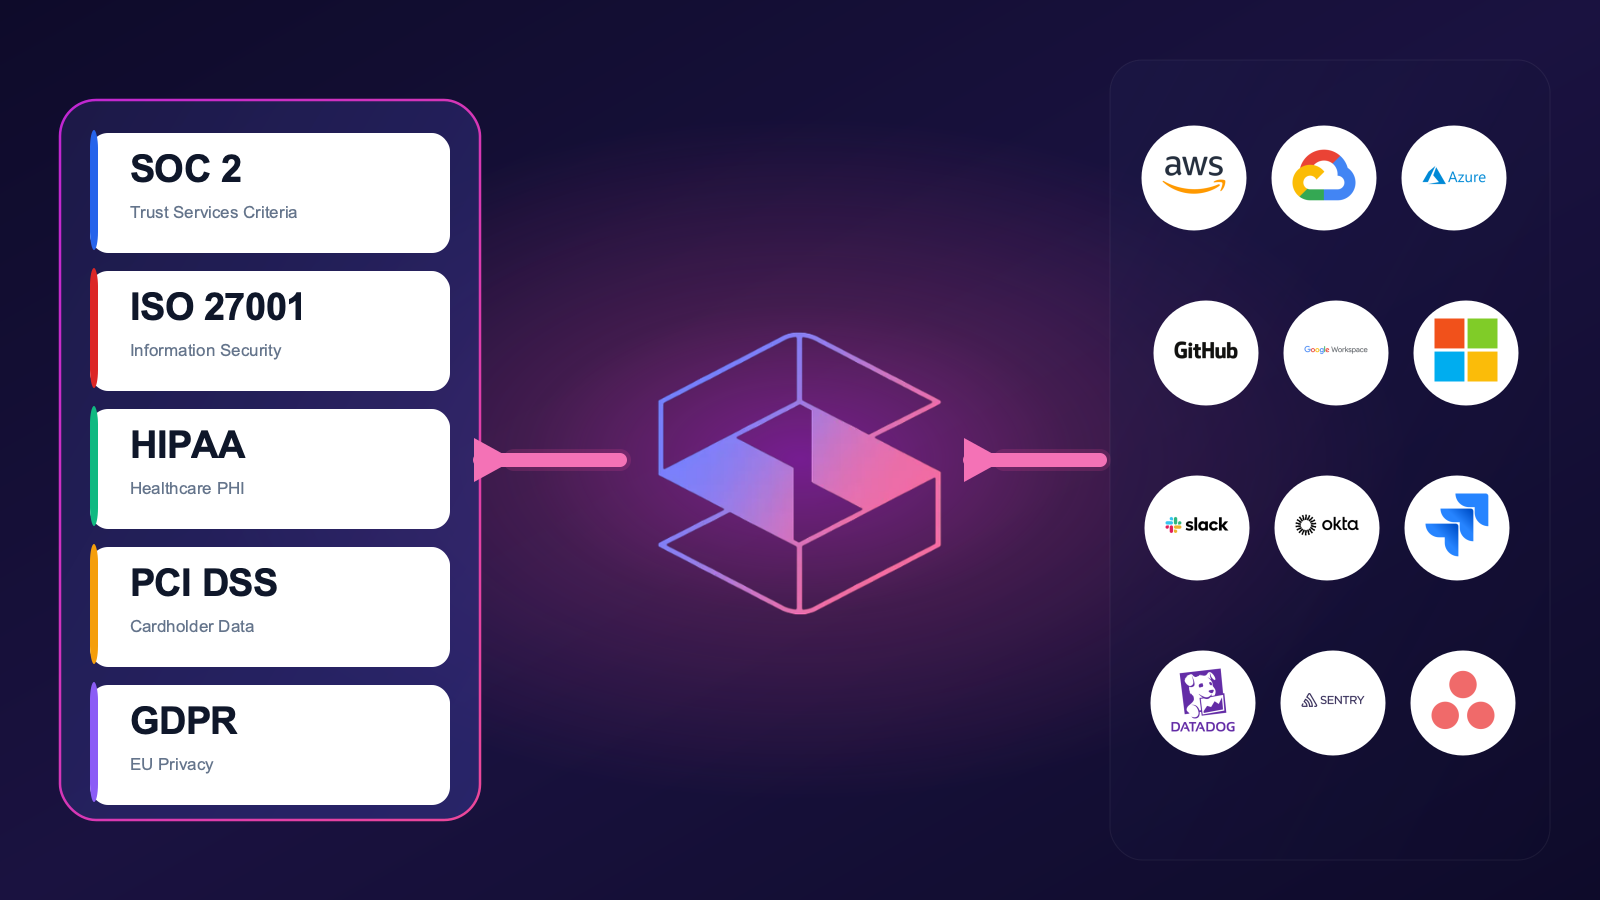
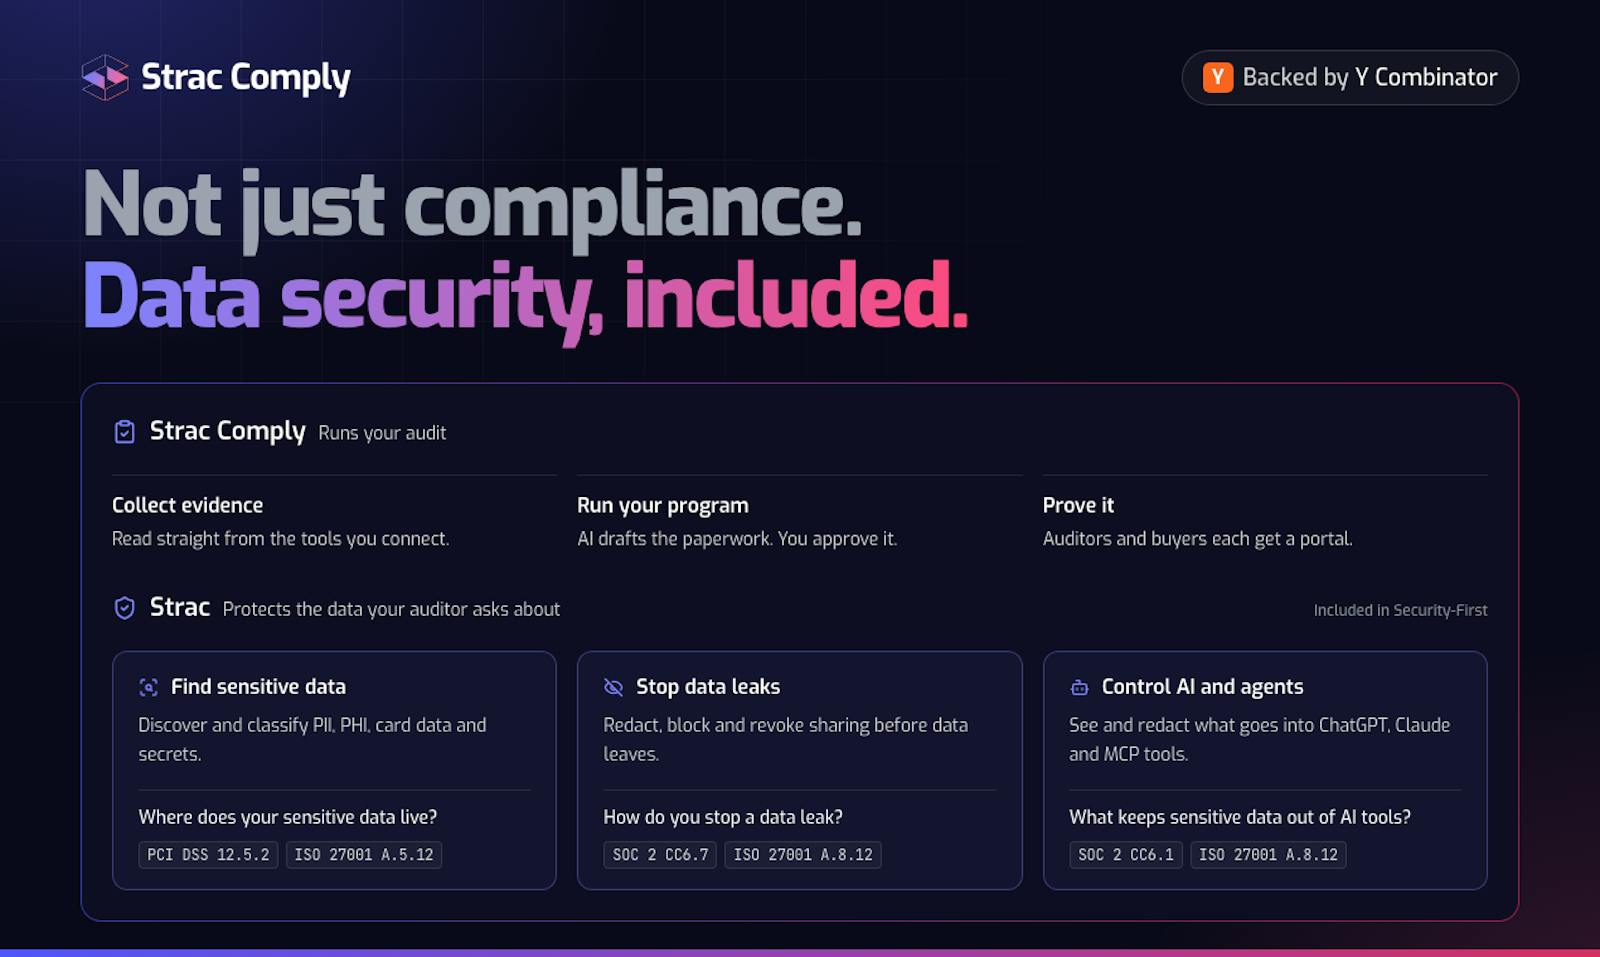
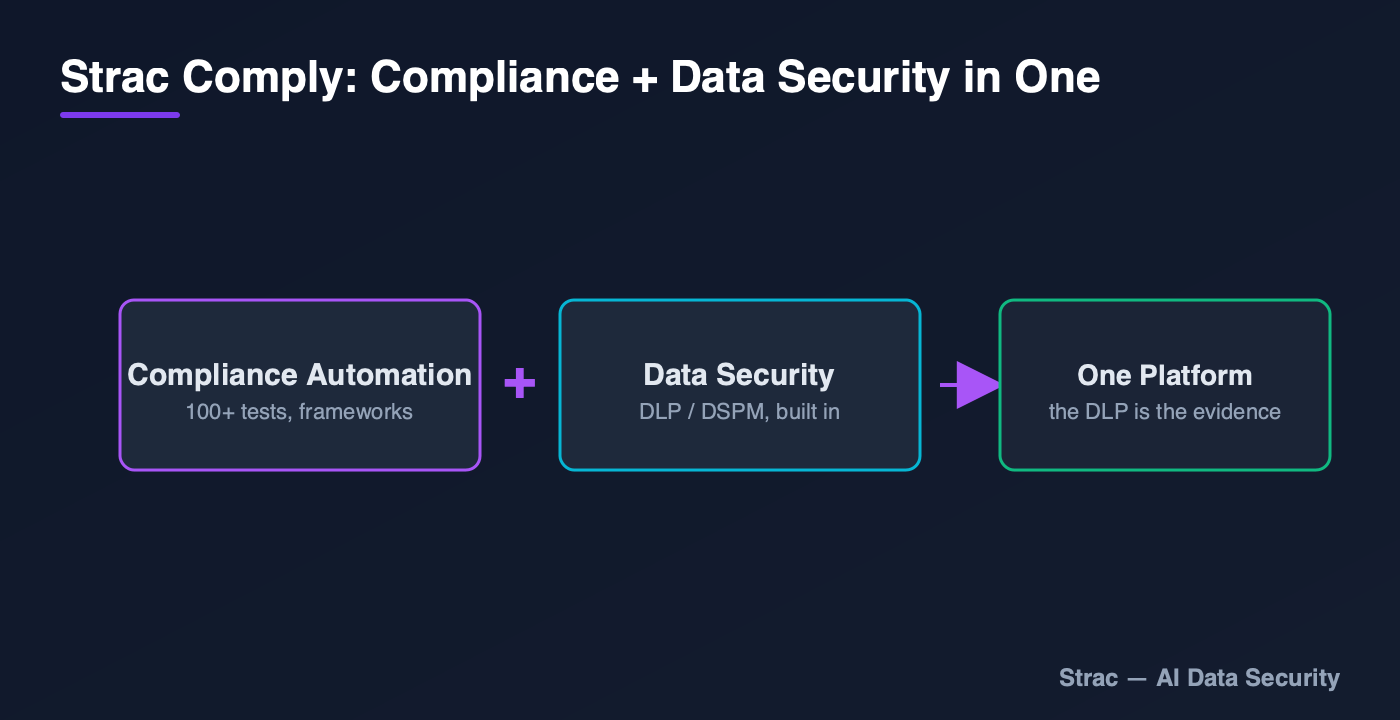
Strac Comply combines compliance automation with continuous data security, one platform covering SOC 2, ISO 27001, HIPAA, PCI DSS, and GDPR
Top 10 Secureframe Alternatives in 2026
1. Strac Comply: The Compliance + Data Security Platform
Strac Comply is the AI-native compliance automation platform that combines SOC 2 / HIPAA / ISO 27001 / GDPR / PCI / EU AI Act automation with continuous data security in a single platform. Where every other platform on this list ingests DLP evidence from a separate vendor, Strac ships the DLP product directly.
What Strac Comply does that Secureframe doesn't:
Continuous data security built in. Strac DLP across SaaS (50+ integrations), cloud, endpoint, browser, and MCP DLP for AI agents.
AI-native, not retrofitted. AI drafts policies tailored to your stack. AI surfaces gaps. AI maps cross-framework evidence.
Under-10-minute integration deploys.
Pre-built mappings across SOC 2, HIPAA, PCI, ISO 27001, GDPR, CCPA, EU AI Act, ISO 42001.
Where Strac specifically wins vs Secureframe: the combined-platform architecture. Secureframe is a strong compliance automation platform; Strac is compliance + DLP + DSPM + MCP DLP in one product.
See Strac Comply in action. Here is what the $4,995 to $12,995 Strac Comply plans give you, all in one platform:
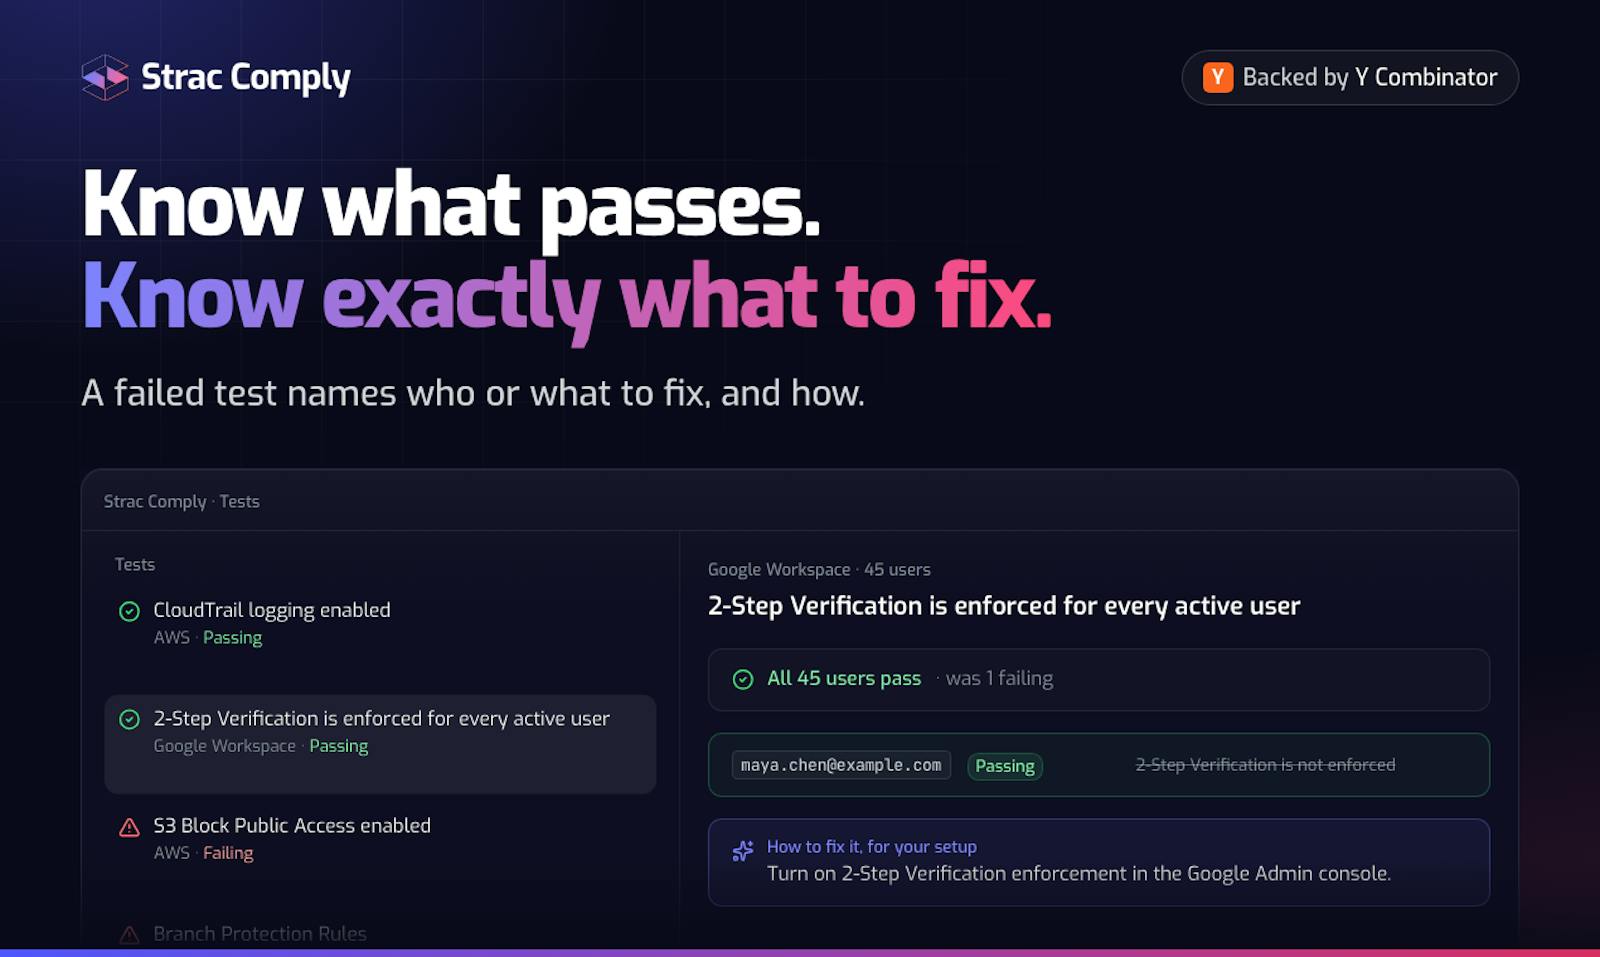
Automated tests that are the evidence. Secureframe asks you to connect and attest; Strac Comply runs a live daily test against each system, and the pass or fail result is the evidence, mapped to the exact SOC 2 criterion.
Automated tests that are the evidence.
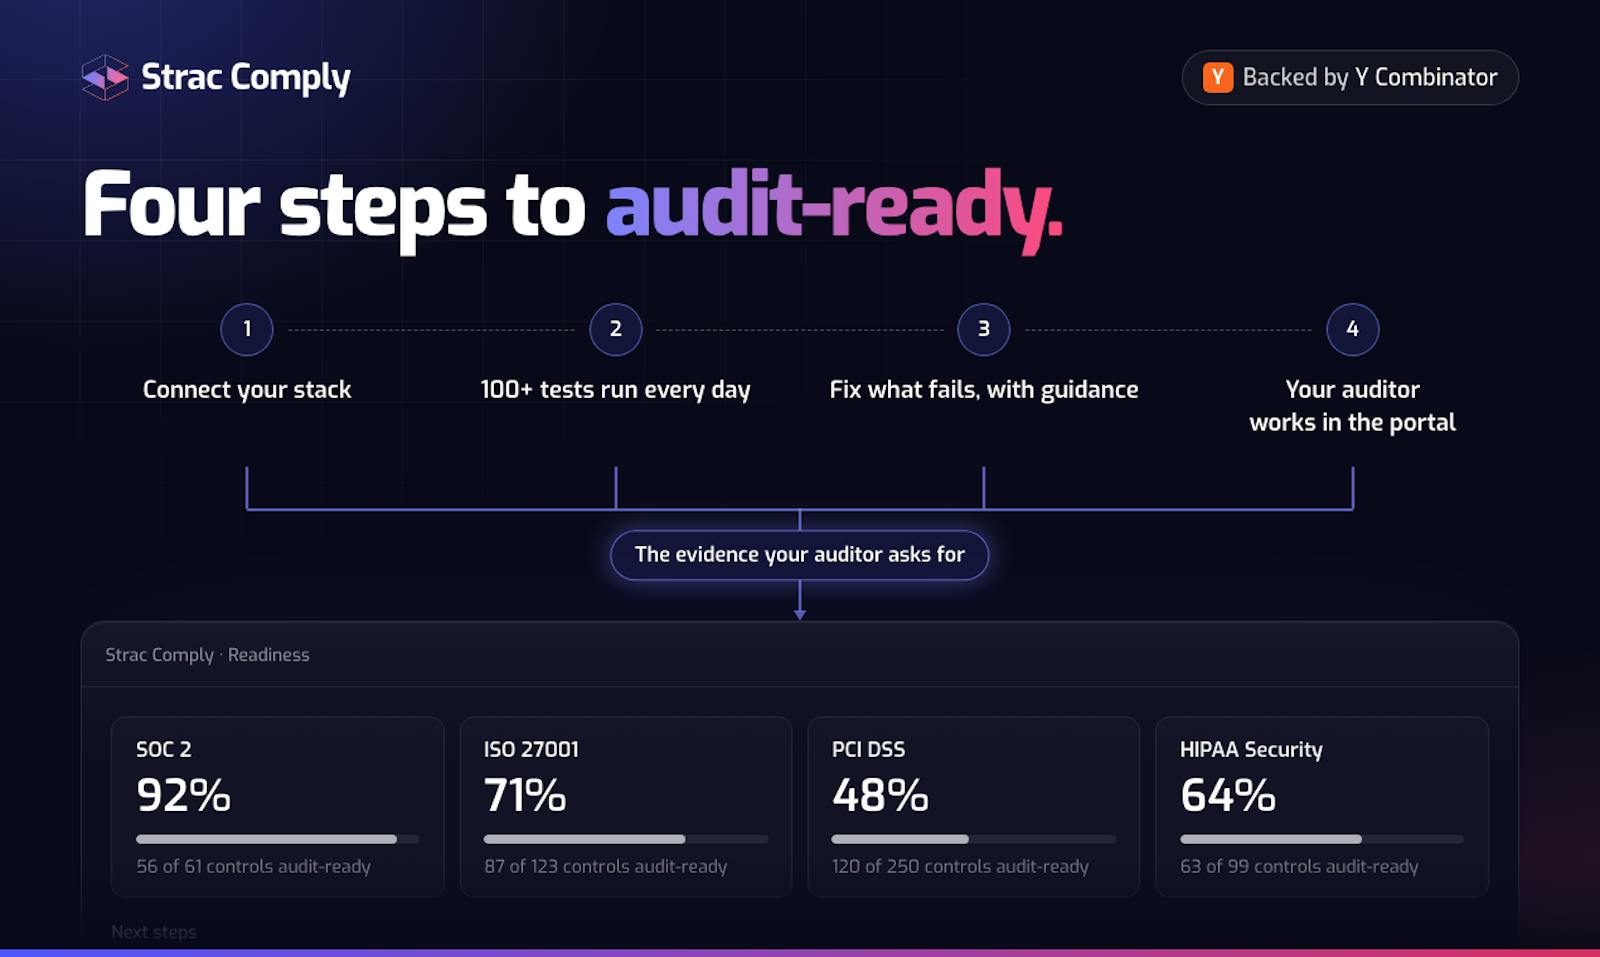
One readiness dashboard across frameworks. SOC 2, ISO 27001, PCI DSS, and HIPAA readiness in one dashboard, with the exact controls left to fix.
One readiness dashboard across frameworks.
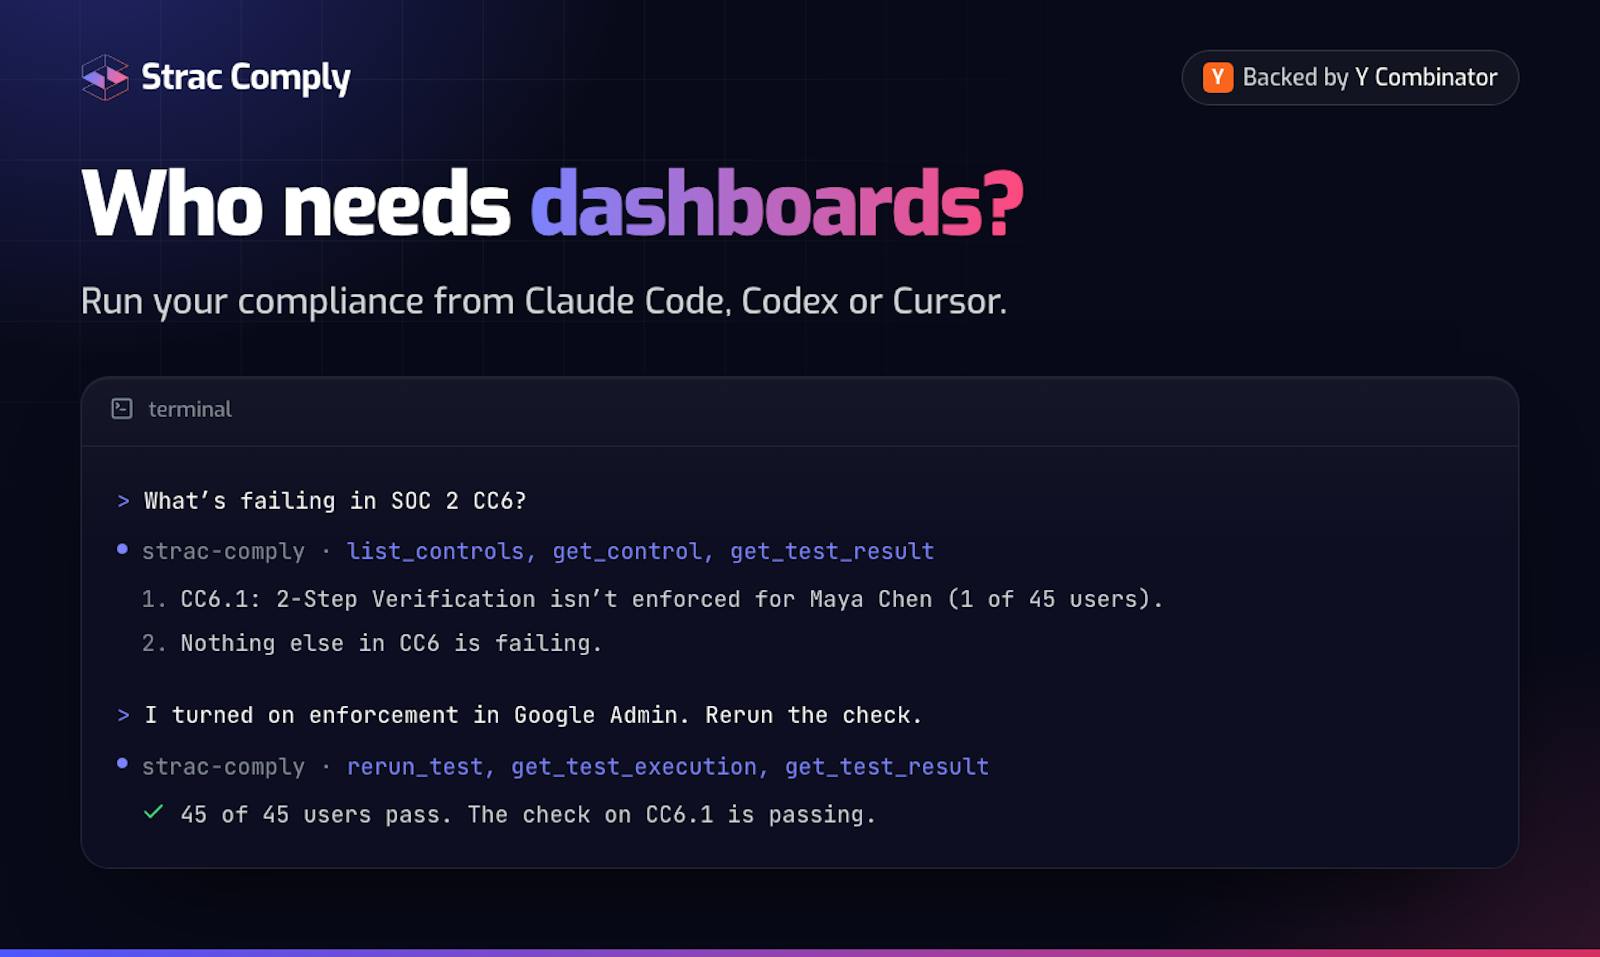
Run compliance from your AI agent (MCP). Secureframe is a guided dashboard. Strac Comply adds an MCP server, so you ask Claude Code or Cursor what is failing and fix it in your terminal.
Run compliance from your AI agent (MCP).
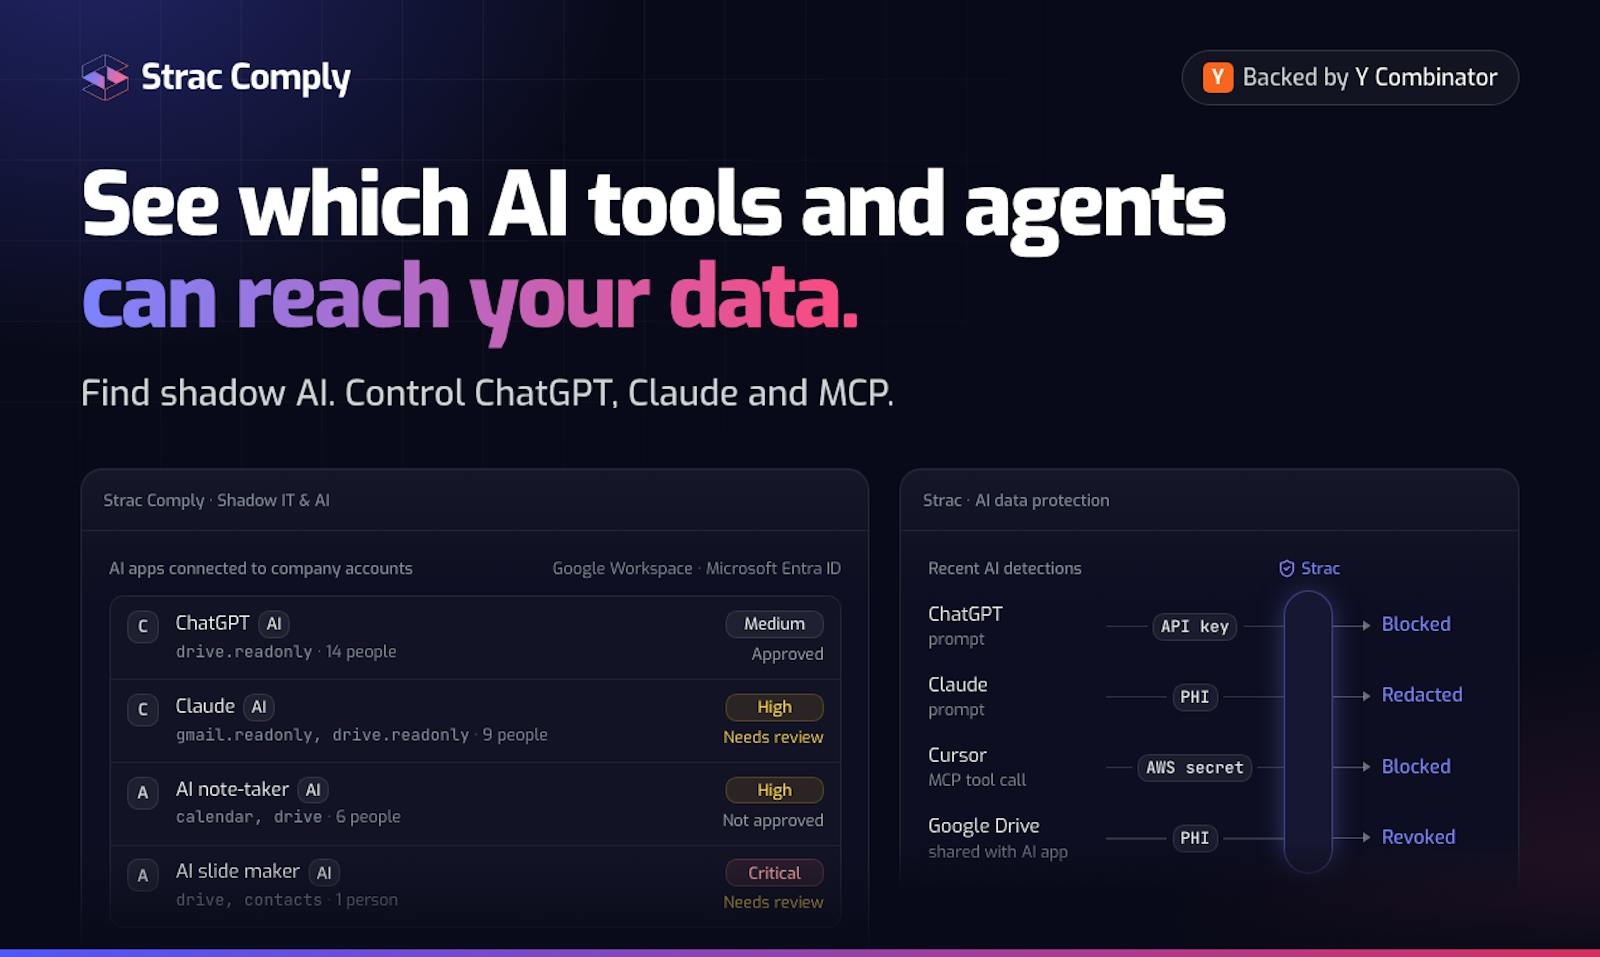
Shadow IT and AI discovery. Strac Comply surfaces the unsanctioned SaaS and AI tools your team uses, so unmanaged apps do not become audit gaps. On the $12,995 Security-First plan.
Shadow IT and AI discovery.
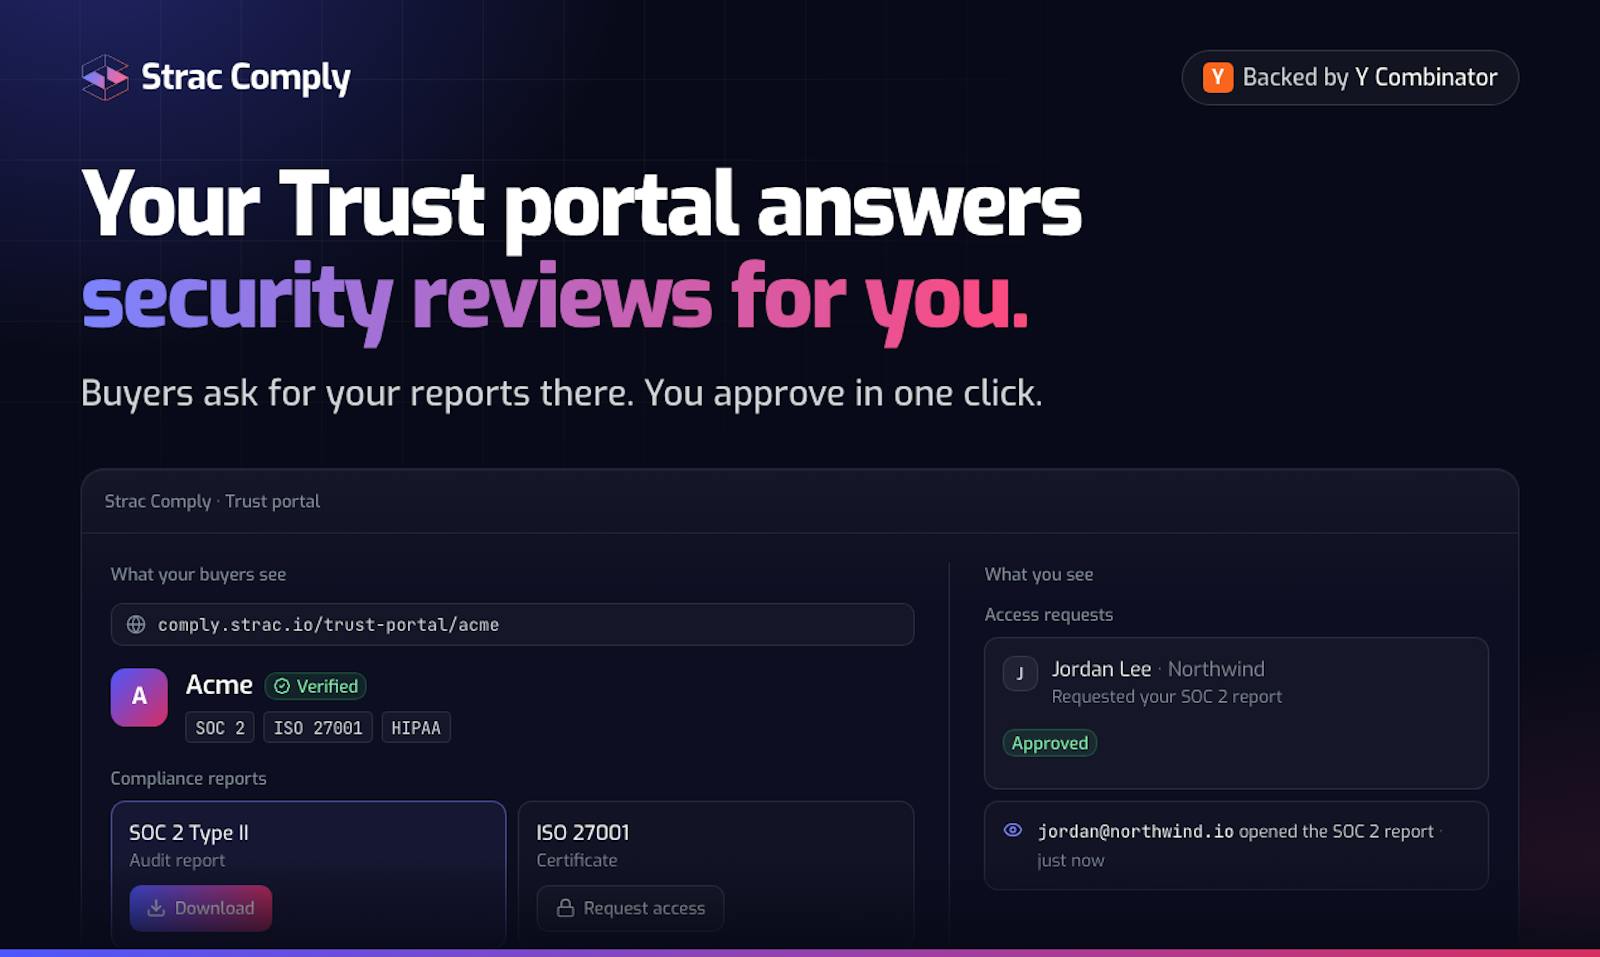
A trust portal buyers self-serve. Buyers pull your report from the trust portal and you approve in one click, in the same platform as your evidence.
A trust portal buyers self-serve.
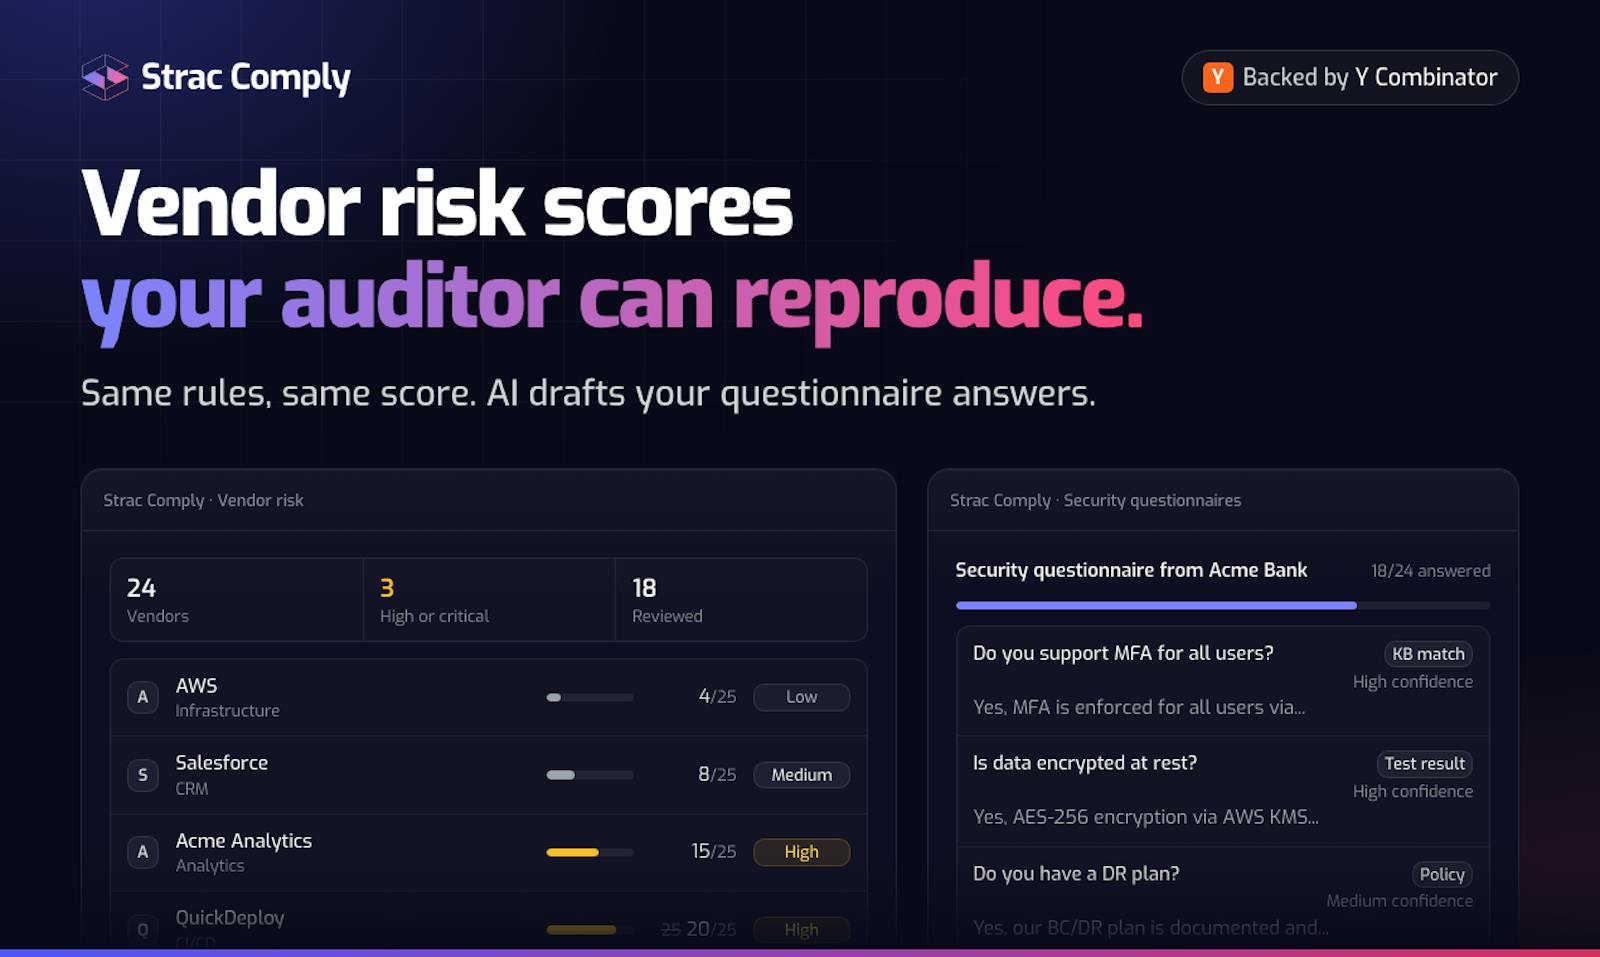
Vendor risk and TPRM, built in. Reproducible vendor-risk scores with AI-drafted questionnaires, included rather than a separate add-on.
Vendor risk and TPRM, built in.
Data security mapped to your controls. Because Strac is a data-security platform, Comply discovers sensitive data and governs AI access, mapped to CC6.7, PCI 12.5.2, and Annex A.8, coverage Secureframe does not have.
Data security mapped to your controls.
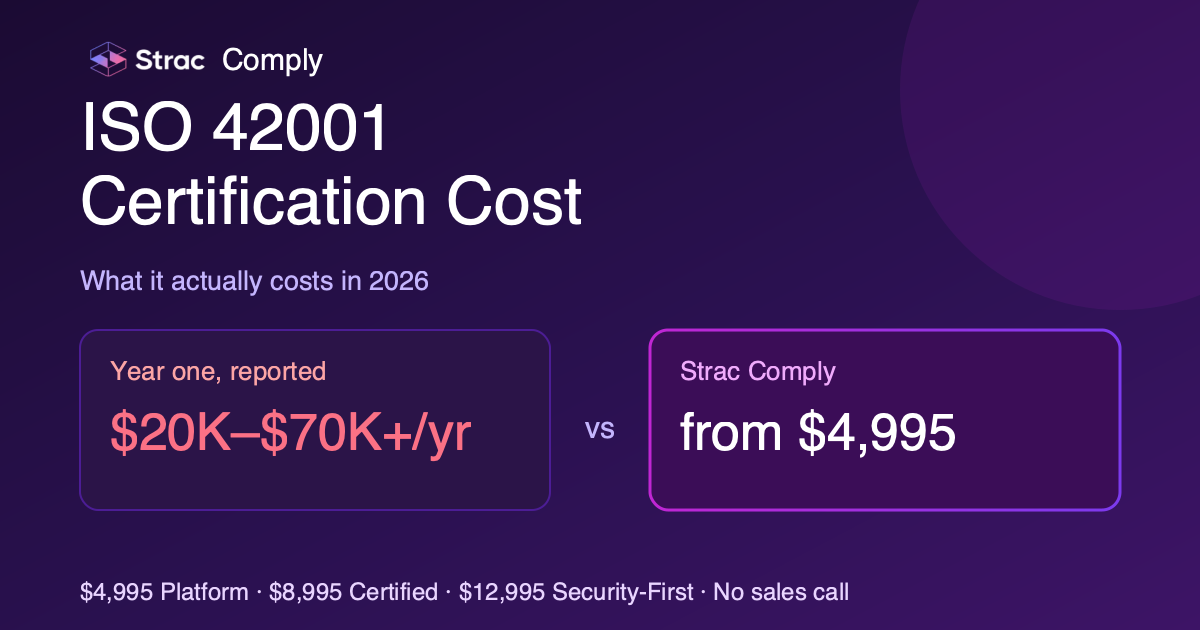
Pricing, published, no sales call.Strac Comply is $4,995 / year for the Platform (self-serve, 14-day free trial, no credit card), $8,995 Certified with the SOC 2 audit by an independent licensed CPA firm on one invoice, and $12,995 Security-First which adds a human-led penetration test and Strac DLP for Slack, Google Workspace, and AI tools. All five frameworks on every plan, up to 10 employees. Sign up at comply.strac.io.
Get compliant without the sales call: Strac Comply plans from $4,995 a year
One clarification. These are Strac Comply plan prices. Strac DLP for Slack, Google Workspace, and AI tools is bundled on the $12,995 Security-First plan; the full Strac data-security platform (endpoint DLP, cloud DSPM, and MCP DLP) is licensed separately. So $4,995 to $12,995 is the price of Strac Comply, not of Strac’s standalone DLP or DSPM.
2. Vanta: The Compliance Automation Pioneer
The longest-tenured platform in the category. Broad integrations, well-known to auditors, premium pricing.
Where Strac is a stronger Secureframe alternative than Vanta: Vanta is compliance-only too. Strac\'s combined platform is the cleaner architecture for modern stacks.
For EU AI Act Art. 12 and ISO 42001 Annex A.8, same, with MCP DLP audit logs feeding AI controls directly.
One platform. One bill. Full coverage.
Strac Comply: the Secureframe alternative built for the modern compliance stack
Compliance automation + Strac DLP + Strac DSPM + MCP DLP for AI agents, one platform, one bill, full coverage across every framework and every audit surface.
The most common reasons: (1) you want compliance + DLP + DSPM as one platform; (2) native AI / MCP coverage for the 2026 audit surface; (3) faster integration deploys; (4) pre-built mappings across emerging frameworks (EU AI Act, ISO 42001).
Is Strac Comply a direct Secureframe replacement?
For most use cases, yes. Strac Comply automates the same frameworks Secureframe automates and adds native DLP / DSPM / MCP DLP coverage Secureframe doesn't ship.
How does Strac Comply pricing compare to Secureframe?
The practical comparison: Secureframe + a separate DLP + a separate DSPM = three vendors. Strac Comply consolidates that into one platform at lower total cost.
What about AI agents and MCP?
Secureframe doesn't currently ship MCP DLP. Strac is the only compliance platform with native MCP DLP across 18 SaaS connectors with audit logs mapped to SOC 2 / HIPAA / EU AI Act controls automatically.
Does Strac Comply work with my existing auditor?
Yes. Any AICPA-licensed CPA firm. The platform exports evidence in formats every auditor accepts.
How long does Strac Comply onboarding take?
Most integrations deploy in under 10 minutes per workspace. Full readiness for first SOC 2 Type 2 typically lands in 4-6 weeks.
What about HIPAA?
Strac Comply is built for the combined SOC 2 + HIPAA program. Strac DLP covers PHI detection and redaction; Strac Comply maps to HIPAA controls automatically.
Is there a free trial or PoV?
Yes. Most PoVs surface real evidence within the first 30 minutes. Book a demo.
What if I'm already on Secureframe: how hard is the switch?
Strac Comply\'s migration team handles policy import, control re-mapping, and evidence backfill. Most migrations land in 2-3 weeks without audit disruption.
How does Strac Comply handle the Claude Cowork BAA gap?
Anthropic doesn't offer a BAA for Claude consumer or Claude Cowork. Strac\'s MCP DLP redacts PHI at the tool-call boundary; Strac Comply evidences the redaction against HIPAA automatically. See Is Claude HIPAA compliant? for the vendor breakdown.
Secureframe is a credible compliance automation platform with strong customer traction. The reason teams look for alternatives in 2026 is convergence, compliance and data security are merging, AI agents are the new audit surface, and one-vendor architectures beat three-vendor ones. Strac Comply is the answer.
The most common reasons: (1) you want compliance + DLP + DSPM as one platform; (2) native AI / MCP coverage for the 2026 audit surface; (3) faster integration deploys; (4) pre-built mappings across emerging frameworks (EU AI Act, ISO 42001).
Is Strac Comply a direct Secureframe replacement?
For most use cases, yes. Strac Comply automates the same frameworks Secureframe automates and adds native DLP / DSPM / MCP DLP coverage Secureframe doesn't ship.
How does Strac Comply pricing compare to Secureframe?
The practical comparison: Secureframe + a separate DLP + a separate DSPM = three vendors. Strac Comply consolidates that into one platform at lower total cost.
What about AI agents and MCP?
Secureframe doesn't currently ship MCP DLP. Strac is the only compliance platform with native MCP DLP across 18 SaaS connectors with audit logs mapped to SOC 2 / HIPAA / EU AI Act controls automatically.
Does Strac Comply work with my existing auditor?
Yes. Any AICPA-licensed CPA firm. The platform exports evidence in formats every auditor accepts.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.