Best Vanta Alternatives 2026: Transparent Pricing From $4,995
The best Vanta alternatives for SOC 2, ISO 27001, HIPAA, and GDPR in 2026, compared on price, automation, audit, and AI. See why teams switch and how Strac Comply (AI-native, with built-in data security) stacks up.
Updated October 2026 for the Strac Comply launch: transparent pricing ($4,995/yr), 100+ tests on day one, all frameworks one price, AI-native.
Vanta is the category leader, but teams shop for alternatives for three reasons: renewal sticker-shock from its modular, add-on pricing; a platform architected before the AI era; and a one-size-fits-all feel as you scale.
The serious Vanta competitors in 2026: Strac Comply, Drata, Secureframe, Sprinto, Oneleet, Thoropass, Scrut, Hyperproof, Scytale, and OneTrust.
Strac Comply is the AI-native pick, it's the only platform on this list that bundles compliance automation + data security (DLP/DSPM) in one, runs a native penetration test, and lets AI agents write evidence into your binder. If you already protect data with Strac, your CC6.7 evidence is collected the day you turn it on.
Pick on: framework coverage, real evidence vs. checkbox automation, audit model, transparent pricing, and whether the platform was built for the AI controls auditors now ask about.
Last updated: October 2026
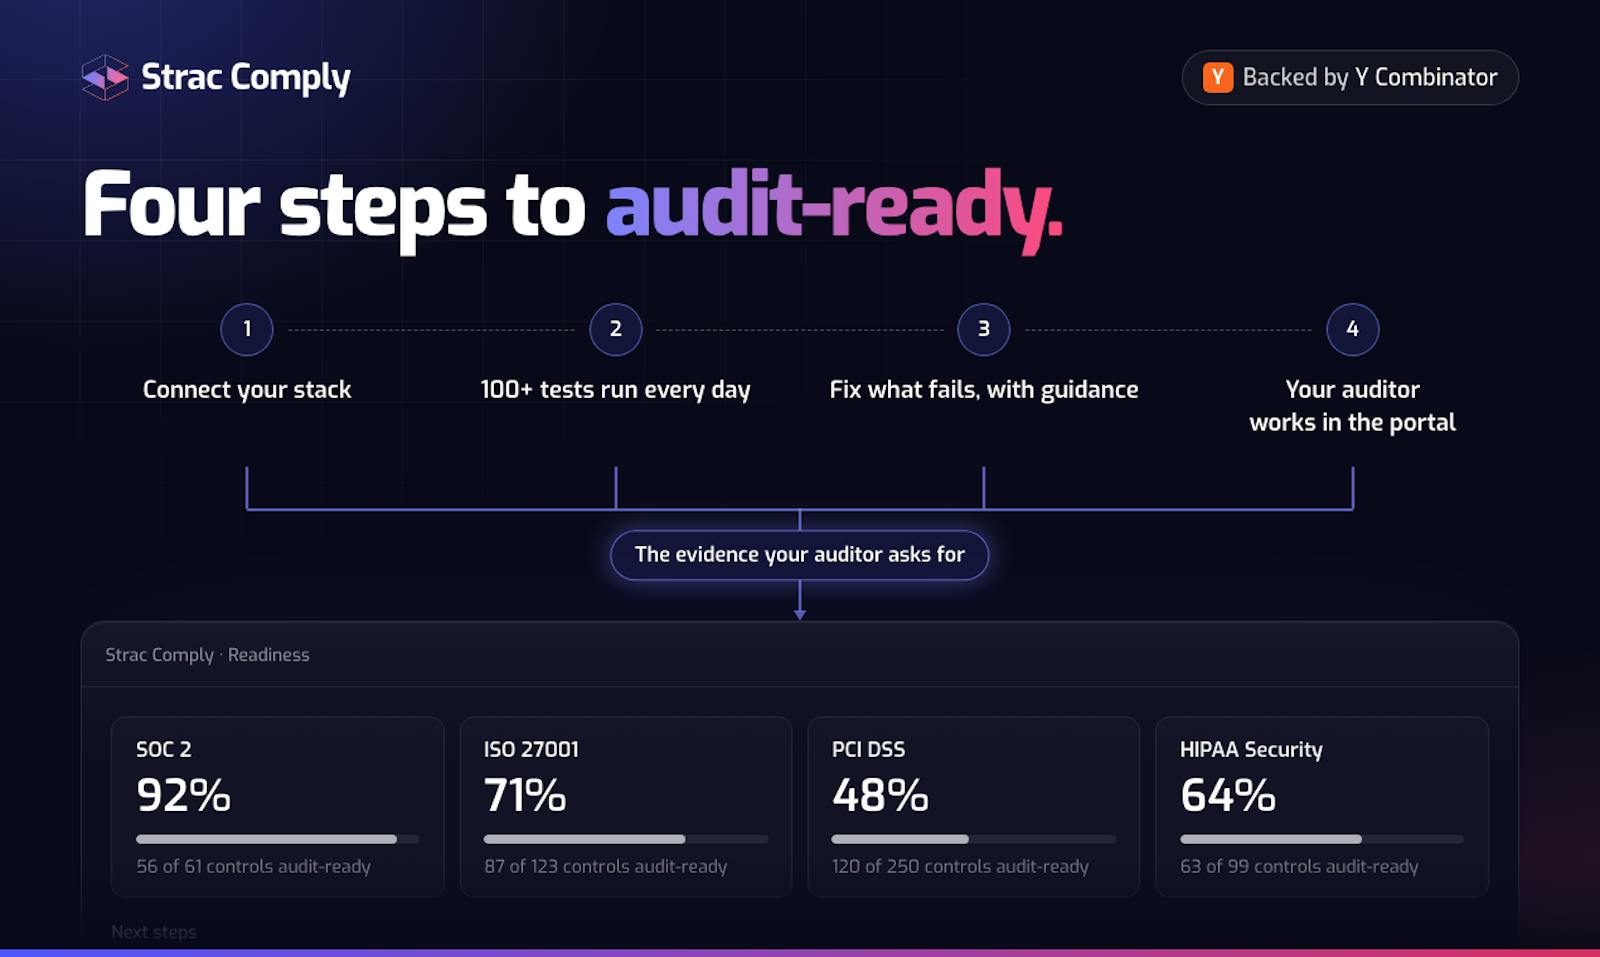
Strac Comply shows exactly what passes and what to fix across every framework, from one dashboard.
On cost specifically, see the full Vanta pricing breakdown for 2026.
Get compliant with Strac Comply, from $4,995 all-in
SOC 2, ISO 27001, PCI DSS, HIPAA, and GDPR in one platform. Transparent pricing, a 14-day free trial, and no mandatory sales call, unlike Vanta and Drata.
Vanta popularized compliance automation and has the broadest brand recognition. The reasons buyers still evaluate alternatives are consistent:
Renewal sticker-shock. Vanta's modular pricing starts a sales-led quote but commonly lands at a five-figure quote once vendor-risk reviews, questionnaire automation, extra frameworks, and support are added. Costs that looked small at signup stack up at renewal. (Sprinto's breakdown)
Built before the AI era. Vanta launched in 2018. The controls auditors and customers now ask about, AI governance, ISO 42001, NIST AI RMF, agent access, were bolted on, not native.
Checkbox automation vs. real evidence. Connecting integrations and checking boxes isn't the same as continuously testing that a control actually holds.
One-size-fits-all as you scale. Great for the first SOC 2; less flexible when you need multiple frameworks, custom controls, or data-security evidence.
Framework breadth: SOC 2, ISO 27001, HIPAA, GDPR, PCI DSS, and the newer ISO 42001 / NIST AI RMF / EU AI Act for AI.
Real evidence, not checkboxes: does it continuously test controls and collect actual proof?
Audit model: in-platform auditor network vs. bring-your-own, and whether a penetration test is included.
Transparent pricing: flat and predictable, or modular with add-on creep?
Data-security evidence: can it prove CC6.7 / data protection with real DLP/DSPM, or just policy docs?
AI-native: was the platform designed for the AI controls now in scope?
Top 10 Vanta Alternatives in 2026
Vanta Alternatives Compared at a Glance
Tool
Best for
Standout strength
Strac Comply
Teams wanting compliance + data security in one
Bundles DLP with Comply; native penetration test included
Drata
The closest like-for-like Vanta substitute
Mature automation and a deep integration catalog
Secureframe
Startups wanting a lower price
Startup-friendly pricing and onboarding
Sprinto
SMB and international teams
Affordable, strong multi-framework and international support
Oneleet
YC-style startups wanting pentest included
Penetration test bundled into the platform
Thoropass
Teams wanting platform + audit together
Compliance platform and audit under one roof
Scrut Automation
Mid-market teams needing GRC depth
Broad GRC and risk coverage
Hyperproof
Enterprise GRC programs
Enterprise-grade risk and control management
Scytale
SMBs wanting AI assistance
AI-assisted evidence and workflows
OneTrust
Enterprise privacy + GRC
Privacy program breadth alongside compliance
Each tool is broken down in detail below, starting with Strac Comply , the only option that pairs SOC 2/ISO/GDPR automation with built-in data loss prevention.
1. Strac Comply, Compliance + Data Security in One, AI-Native
The standout for teams that want more than checkbox automation. Strac Comply covers SOC 2, ISO 27001, HIPAA, GDPR, and PCI DSS, plus the AI frameworks (ISO 42001, NIST AI RMF, EU AI Act). Its unique angle: it's the only option here that bundles compliance with data security, Strac's DLP/DSPM discovers and inventories the sensitive data behind data-protection controls, and it runs a native penetration test (via PentestMate). AI-native from day one. Best for teams that want compliance and data protection from one vendor.
2. Drata, The Closest Vanta Substitute
The heavy-hitter most often shortlisted next to Vanta by mid-market SaaS teams; a near-identical continuous-compliance experience. Strong automation and integrations. Pricing is comparable to Vanta. See Drata alternatives.
3. Secureframe, Startup-Friendly, Lower Price
A clean interface and solid automation for the common frameworks, positioned below Vanta on price, popular with fast-moving startups. See Secureframe alternatives.
4. Sprinto, Affordable, SMB & International
A more affordable option favored by smaller and international startups; lighter integration depth than Vanta or Drata. See Sprinto alternatives.
5. Oneleet, Pentest-Included, YC Favorite
Bundles a real penetration test with the compliance platform; popular with YC and early-stage teams that want security substance, not just badges. See Oneleet alternatives.
6. Thoropass, Platform + Audit Bundled
Combines the compliance platform with audit services under one roof, which appeals to teams that want a single throat to choke for software and the audit.
7. Scrut Automation, Mid-Market GRC Depth
Broader GRC and risk-management depth with multi-framework support; a fit for teams that have outgrown a single-framework tool.
8. Hyperproof, Enterprise GRC
Geared toward larger programs managing many frameworks and controls at scale, with deeper risk and evidence workflows.
9. Scytale, AI-Assisted for SMBs
An AI-assisted platform aimed at small and mid-size businesses getting their first frameworks done with guided support.
10. OneTrust, Enterprise Privacy + GRC
The enterprise privacy and governance suite (which absorbed Tugboat Logic); a fit for large organizations that need privacy, GRC, and compliance together.
✨ Strac Comply vs Vanta: Head-to-Head
⭐ 4.9/5 on G2 · 28 reviews from security & compliance teams , read the reviews
Strac Comply
Vanta
Architecture
AI-native (built for the AI-controls era)
Built 2018, pre-AI
Data security (CC6.7)
Built-in DLP/DSPM for data discovery and inventory
Policy/attestation; needs a separate DLP tool
Penetration test
Native (PentestMate)
Via third-party marketplace
AI frameworks
Maps to ISO 42001, NIST AI RMF, EU AI Act
Add-on / emerging
Pricing
Flat, predictable
Modular, add-on creep at renewal
Evidence
Continuously tested, real
Integration-based automation
Bundle
Compliance + data security, one vendor
Compliance only
What Strac Comply Automates That Vanta Leaves to You
Most compliance platforms get you to roughly 70%, the integration-based checks, and hand the last 30% back to a human with a screenshot folder. Strac Comply is built to close that gap. Its AI Evidence Agent is a Chrome extension that logs into the SaaS admin consoles auditors actually ask about and captures the manual evidence, access reviews, configuration screens, custom-app workflows, automatically. If you can log into it, the agent can capture it.
Underneath that sits the part Vanta has to bolt on: data protection. Strac Comply is powered by Strac's own DSPM/DLP engine, so it detects and remediates PII, PHI, PCI, and secrets in real time, and that live data-protection coverage produces evidence for your data-security controls instead of a policy PDF. The same platform runs 100+ automated tests continuously, includes native penetration testing against a library of vulnerability checks, and discovers shadow IT and shadow AI, every risky OAuth grant and every ChatGPT or Claude login your employees connected.
AI Evidence Agent, the last-mile evidence no GRC tool automates.
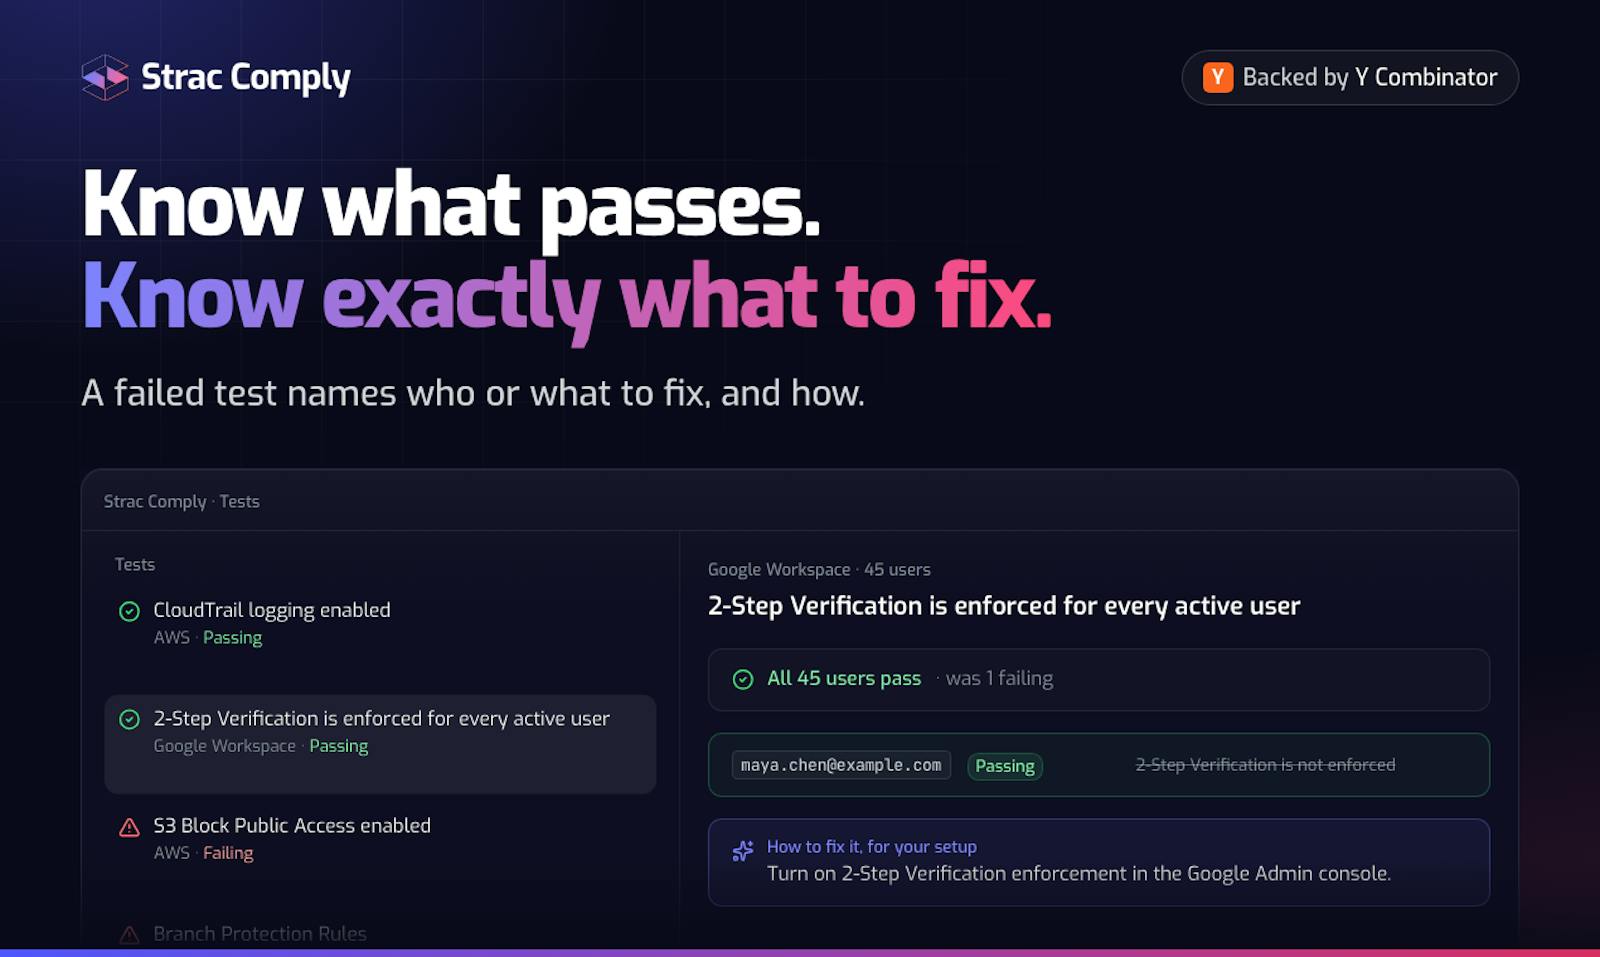
Every one of Strac Comply’s 100+ daily tests checks your real systems. When one fails, it names who or what to fix and how, so compliance is a worklist, not a guessing game.
A failed test names who or what to fix, and how.
✨ Run your compliance from your AI agent
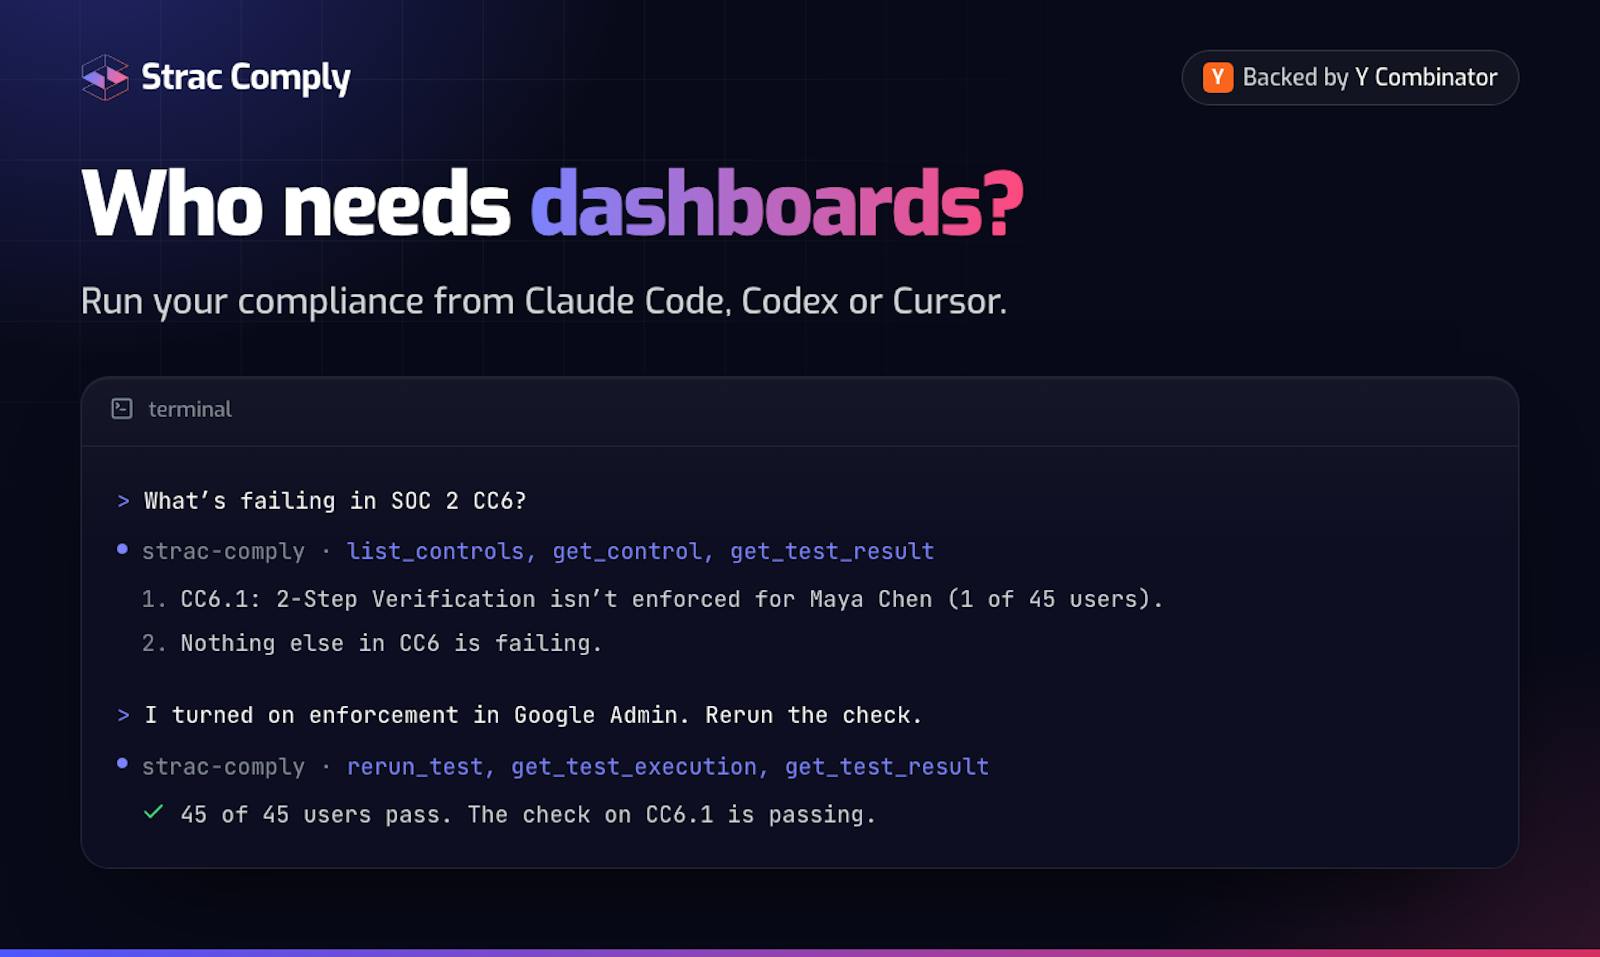
Strac Comply ships an MCP server, so you can ask Claude Code, Codex, or Cursor what is failing and fix it without leaving your terminal. This is the clearest thing Vanta, Drata, and Sprinto cannot do.
Ask your AI agent what is failing in SOC 2 CC6, fix it, and rerun the test.
✨ A trust portal that answers security reviews for you
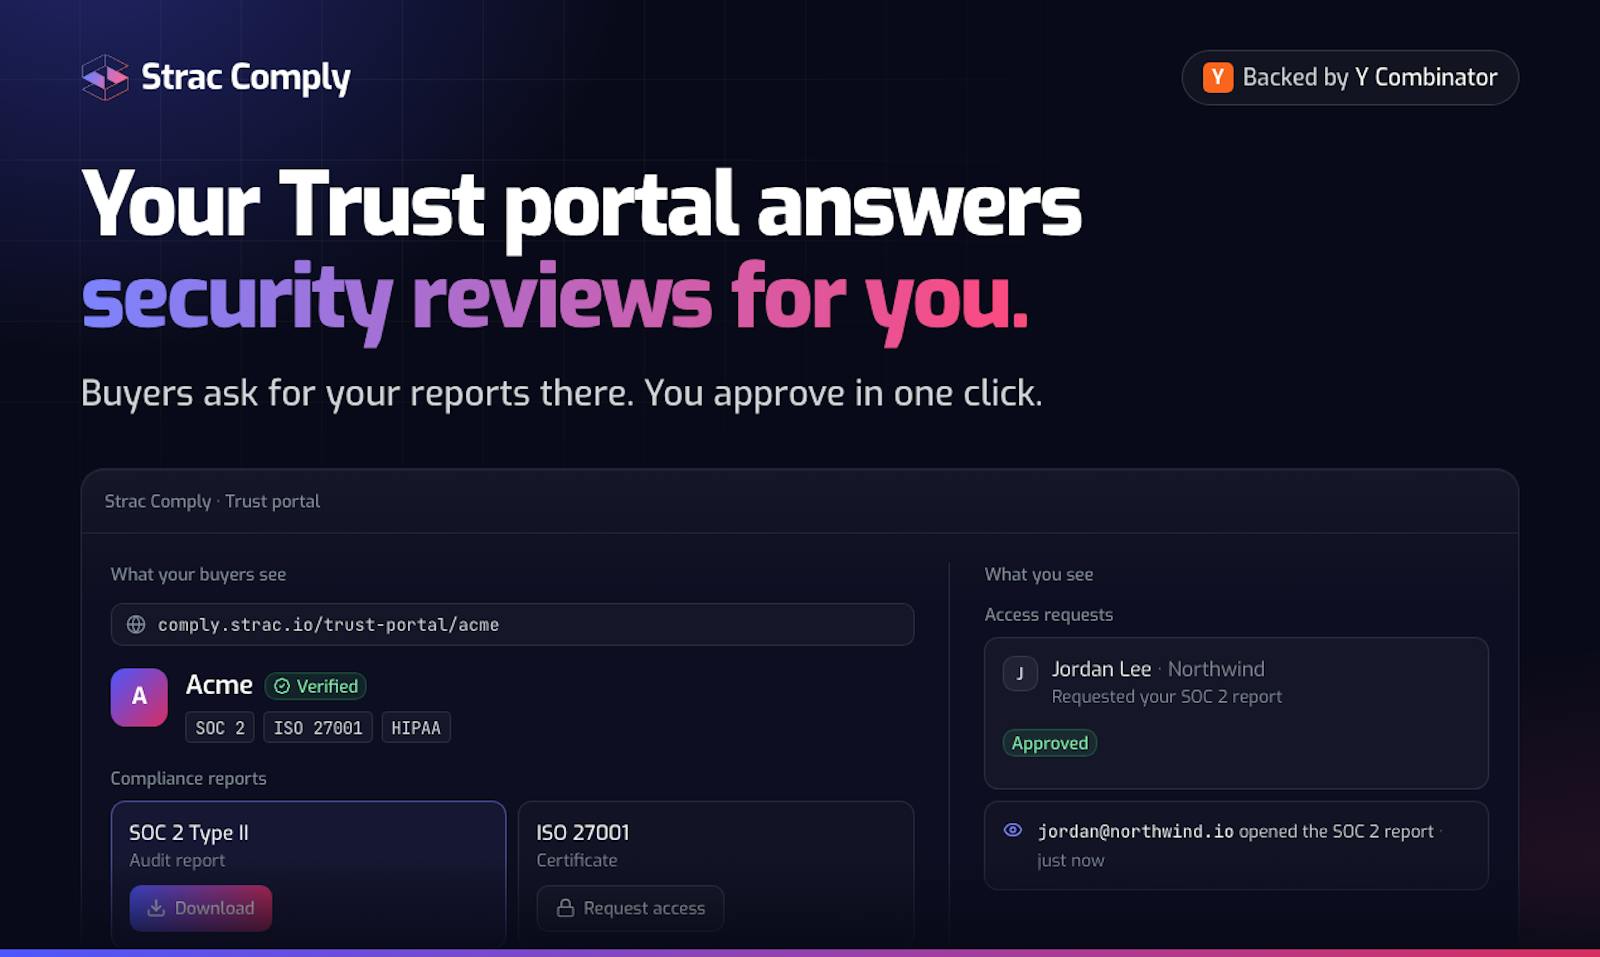
Buyers request your SOC 2 or ISO report in your trust portal and you approve access in one click, instead of emailing PDFs around.
Buyers ask for your reports in the trust portal. You approve in one click.
✨ Vendor risk your auditor can reproduce
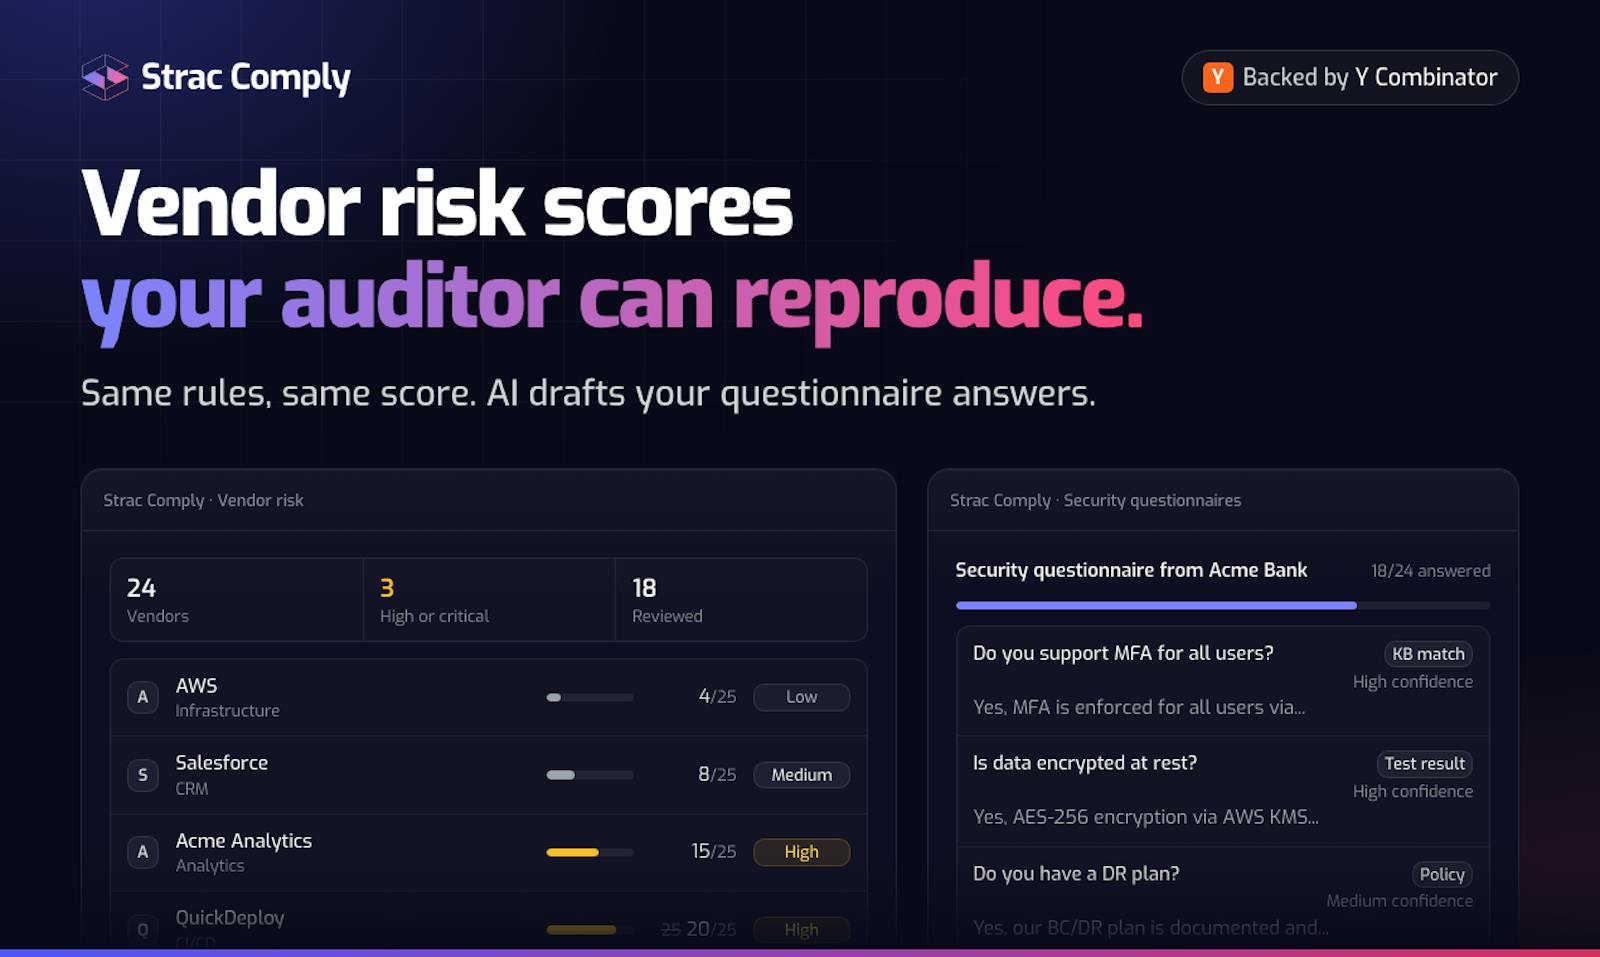
Reproducible vendor risk scores, with AI-drafted security-questionnaire answers, in the same platform as your framework evidence, not a separate tool.
Same rules, same score, and AI drafts your questionnaire answers.
✨ Not just compliance. Data security, included
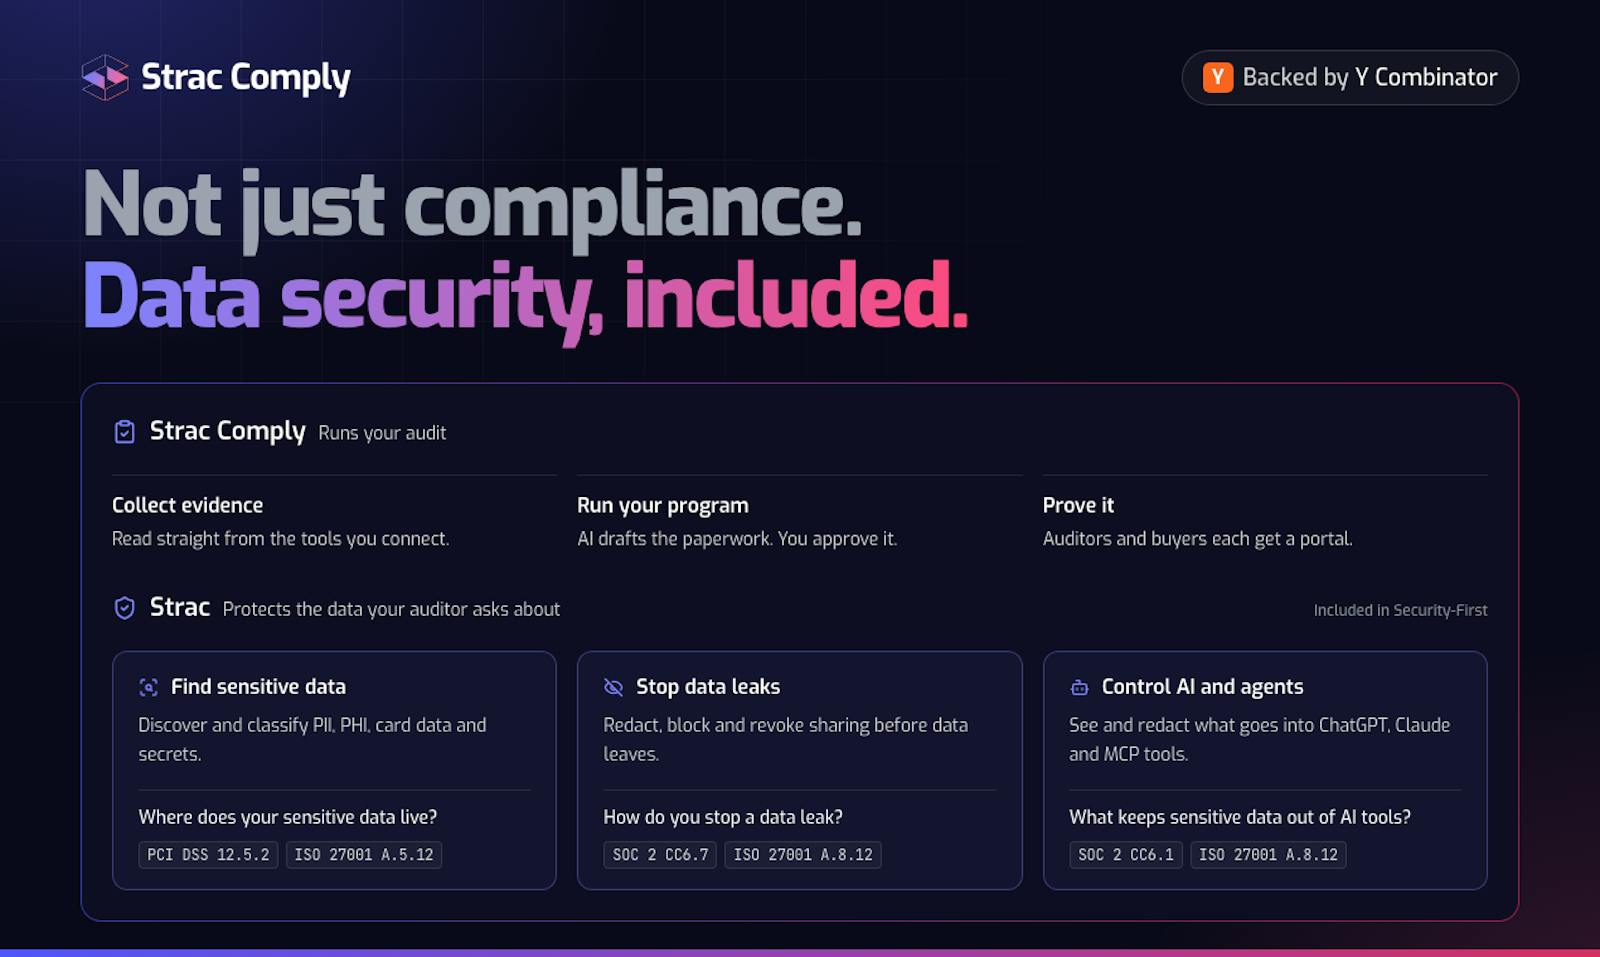
Because Strac is a data-security platform, Strac Comply also discovers sensitive data, stops leaks, and controls what AI tools can reach, each mapped to specific controls such as SOC 2 CC6.7, PCI DSS 12.5.2, and ISO 27001 A.8.12. That is coverage Vanta and Drata do not have.
Compliance automation plus data security, mapped to specific controls.
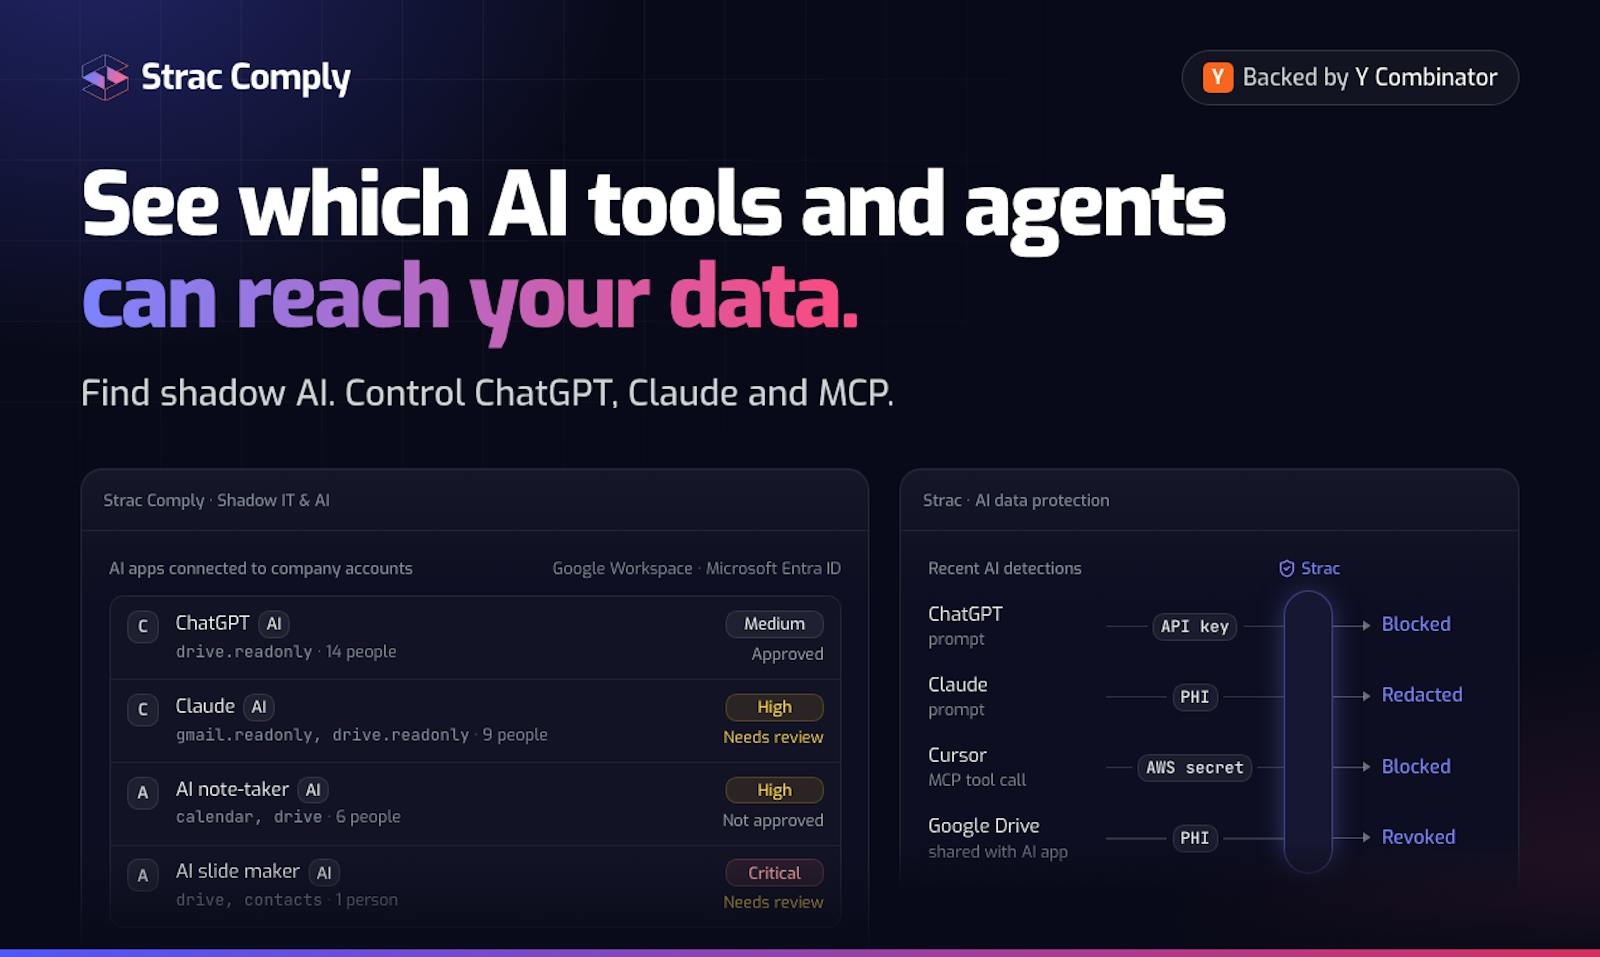
✨ Shadow IT and AI discovery Vanta charges extra for
Strac Comply surfaces the unmanaged SaaS and AI tools in use from real data flows, included rather than an add-on.
Shadow IT and AI discovery Vanta charges extra for.
✨ Vendor risk in the same platform
Reproducible vendor scores and AI-drafted questionnaires live beside your framework evidence, not in a separate module you pay more for.
Vendor risk in the same platform.
✨ Data security Vanta does not have
Because Strac is a data-security platform, Comply discovers sensitive data and governs AI access mapped to controls like SOC 2 CC6.7, which Vanta cannot do.
Data security Vanta does not have.
✨ Strac Comply pricing: transparent, no sales call
The biggest shift this year is pricing transparency. Vanta, Drata, and Sprinto are all sales-led, so you cannot see a number without booking a demo, and Vanta’s modular pricing commonly starts a sales-led quote and climbs with every framework you add. Strac Comply publishes its price and lets you start today: $4,995/yr for the Platform (bring your own auditor) or $8,995/yr for Certified, which includes the SOC 2 audit by an independent licensed CPA firm on the same invoice. All five frameworks (SOC 2, ISO 27001, PCI DSS, HIPAA, NIST CSF 2.0) are included at one price, with a free trial and no credit card. Plans cover teams of up to 10 employees. You sign up, connect your stack, and 100+ automated tests run the same day. It is also AI-native: you can run your compliance from your AI agent over MCP. No sales call required. Note: $4,995 to $12,995 is Strac Comply, the Vanta alternative. Strac’s enterprise DLP and DSPM is a separate product, so these are not the price of Strac’s data-security platform.
Strac Comply publishes its price. Vanta, Drata, and Sprinto require a sales call.
🎥 Watch Strac Comply get you to SOC 2 without the sales call
🌶️ Spicy FAQs for Vanta Alternatives
What is the best Vanta alternative?
It depends on what you need. Drata is the closest like-for-like substitute; Secureframe and Sprinto are cheaper, startup-friendly picks; Oneleet bundles a pentest. Strac Comply is the best fit for teams that want compliance and data security in one AI-native platform, its DLP/DSPM automatically discovers and inventories sensitive data for data-protection controls, and it includes a native penetration test.
Why do companies switch from Vanta?
The top reasons are renewal sticker-shock from Vanta's sales-led, quote-only pricing, a platform built before the AI era, and wanting real continuously-tested evidence over checkbox automation.
How much does Vanta cost vs. alternatives?
Vanta is not public, so you have to book a demo, and costs climb as you add frameworks. Secureframe and Sprinto generally price below that; Drata is comparable to Vanta. Always confirm what's included vs. an add-on. (Source)
Is there a Vanta alternative that includes data security?
Yes, Strac Comply is the only option that bundles compliance automation with DLP/DSPM data security in one platform, so your data-protection controls (SOC 2 CC6.7, HIPAA, PCI, GDPR) are evidenced automatically instead of with a separate tool.
Which Vanta alternative is best for AI compliance?
Strac Comply is AI-native and maps to ISO 42001, NIST AI RMF, and the EU AI Act, the AI controls auditors and enterprise customers increasingly require, which legacy platforms added later.
Vanta vs Drata: which is better?
They're close: Drata offers a near-identical continuous-compliance experience and is the substitute most teams shortlist against Vanta. The bigger question is whether either covers data-security controls and AI governance, where an AI-native, DLP-bundled platform like Strac Comply pulls ahead.
The Strac Comply last mile: what Vanta can't automate
Vanta and Drata close maybe 70% of the evidence gap. The other 30%, admin-panel screenshots, monthly access reviews, custom-app workflows, still falls on humans. Strac Comply's AI Evidence Agent, a Chrome extension, does that last mile: if you can log into it, the agent can capture it, auditor-ready. And with headless compliance, your AI agent (Claude Code, Cursor) writes evidence straight into your binder over MCP. Explore Strac Comply.
The Bottom Line
Vanta built the category, but in 2026 the decision is no longer "Vanta or nothing." If you want a like-for-like swap, Drata; cheaper and startup-friendly, Secureframe or Sprinto; a pentest in the box, Oneleet. If you want the platform built for this era, compliance and data security in one, a native pentest, and AI frameworks out of the box, Strac Comply is the alternative worth a demo.
It depends on what you need. Drata is the closest like-for-like substitute; Secureframe and Sprinto are cheaper, startup-friendly picks; Oneleet bundles a pentest. Strac Comply is the best fit for teams that want compliance and data security in one AI-native platform, its DLP/DSPM automatically discovers and inventories sensitive data for data-protection controls, and it includes a native penetration test.
Why do companies switch from Vanta?
The top reasons are renewal sticker-shock from Vanta's sales-led, quote-only pricing, a platform built before the AI era, and wanting real continuously-tested evidence over checkbox automation.
How much does Vanta cost vs. alternatives?
Vanta is not public, so you have to book a demo, and costs climb as you add frameworks. Secureframe and Sprinto generally price below that; Drata is comparable to Vanta. Always confirm what's included vs. an add-on. (Source)
Is there a Vanta alternative that includes data security?
Yes, Strac Comply is the only option that bundles compliance automation with DLP/DSPM data security in one platform, so your data-protection controls (SOC 2 CC6.7, HIPAA, PCI, GDPR) are evidenced automatically instead of with a separate tool.
Which Vanta alternative is best for AI compliance?
Strac Comply is AI-native and maps to ISO 42001, NIST AI RMF, and the EU AI Act, the AI controls auditors and enterprise customers increasingly require, which legacy platforms added later.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.