Best SharePoint & OneDrive DLP Solutions in 2026 (Top 7 Compared)
A practical comparison of the best SharePoint and OneDrive DLP solutions in 2026. How they detect sensitive data, remediate risky public and external sharing, alert your team, and protect Copilot and MCP agents.
SharePoint and OneDrive hold your most sensitive files, and the risk is rarely a hacker. It is a document shared with Anyone-with-the-link, a site opened to external guests, or Copilot surfacing a file nobody cleaned up. The best SharePoint and OneDrive DLP solution has to do three things most tools skip: detect sensitive data inside files, remediate the risky access (remove public links, revoke external members), and cover the AI path (Copilot and MCP agents). This guide compares the top 7, starting with Strac, which does all three from one agentless platform.
Best SharePoint & OneDrive DLP Solutions in 2026 (Top 7 Compared)
SharePoint and OneDrive are where enterprise work lives, which makes them where sensitive data leaks. The leak is rarely dramatic. It is a contract shared with "Anyone with the link," an HR folder still open to a departed contractor, or Microsoft 365 Copilot cheerfully surfacing a file full of PII because nobody remembered it was over-shared.
A good SharePoint and OneDrive DLP solution has to go past detection and actually fix the exposure. This guide compares the best in 2026 on the three things that matter: detecting sensitive data, remediating risky access, and protecting the AI path.
✨ What a complete SharePoint & OneDrive DLP tool must cover
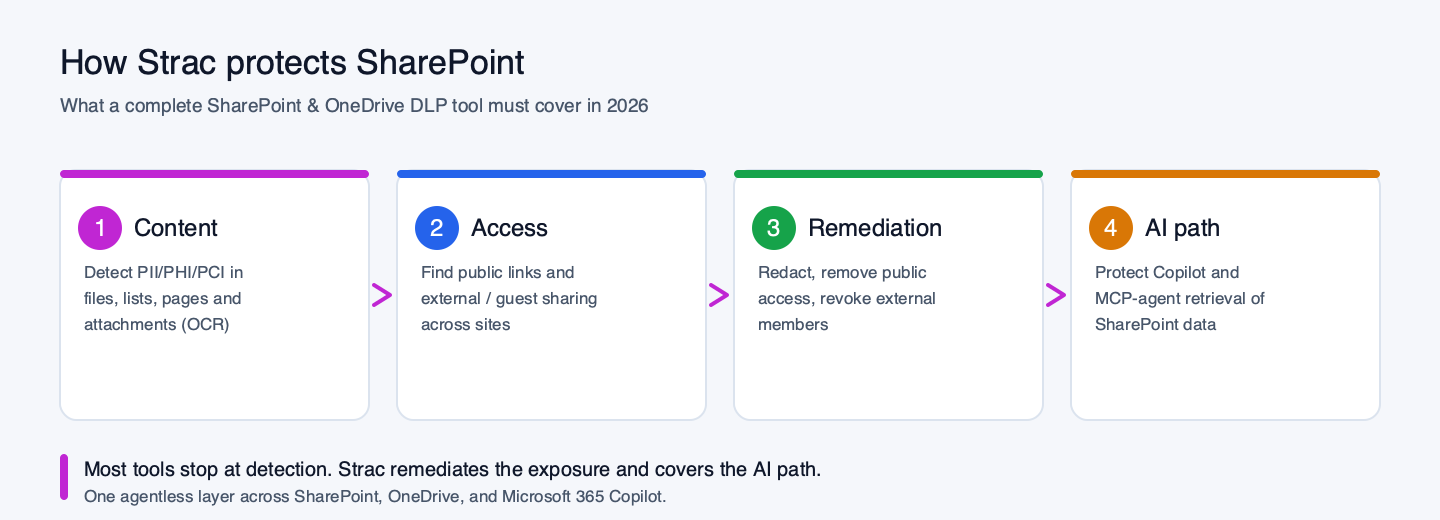
The evaluation comes down to four capabilities:
Content — detect PII, PHI, PCI, secrets, and source code inside files, lists, pages, and attachments (including images via OCR).
Access — find files shared with public links and external / guest members across every site.
Remediation — not just alert: redact the data, remove the public link, revoke the external member.
AI path — protect what Copilot and MCP agents retrieve from SharePoint and OneDrive.
Most tools do the first one well and stop. The differences below are almost entirely about the other three.
Strac is an agentless data security platform that covers SharePoint and OneDrive end to end, and remediates rather than only alerting.
Core capabilities. Strac detects PII, PHI, PCI, secrets, and source code across SharePoint sites, OneDrive folders, lists, pages, and attachments with OCR. It then finds risky access (public "Anyone" links, external and guest members) and remediates automatically: redact the sensitive data, remove the public link, and revoke the external member. Every action fires an alert to the file owner and security in Slack or Teams, with a full audit trail.
Deployment. Agentless, connected in minutes, independent of your Microsoft licensing tier.
Best for. Teams that want to detect and fix SharePoint/OneDrive exposure, cover Copilot and agents, and prove it, without an E5 upgrade or a heavy rollout. See the full SharePoint DLP guide.
2. Microsoft Purview DLP
Purview is the native option, built into Microsoft 365.
Where it fits. If you are all-in on Microsoft and licensed for E5, Purview applies DLP policies to SharePoint and OneDrive from the same admin center you already use.
How it compares to Strac. Purview's strongest DLP features require E5, its remediation leans on policy tips and blocks rather than redaction, and automatically removing public links or revoking external members is not its model. Many teams run Purview for baseline policy and add Strac for redaction, access remediation, and Copilot coverage. See Office 365 DLP limitations.
3. Nightfall AI
Nightfall is an AI-native DLP platform with strong machine-learning detection.
Where it fits. Solid detection accuracy for SaaS and cloud content, delivered API-first.
How it compares to Strac. Nightfall is detection-led. Strac leans harder into access remediation (removing public links and external members, not just flagging them) and into the agentless Copilot/MCP path across SharePoint and OneDrive.
4. Symantec DLP (Broadcom)
A long-established enterprise DLP suite.
Where it fits. Large enterprises with existing Symantec/Broadcom investments that want SharePoint covered under one legacy suite.
How it compares to Strac. Symantec brings breadth and maturity with the deployment weight to match. Strac is a modern, agentless layer that deploys fast and specializes in redaction, access remediation, and the AI path.
5. Forcepoint DLP
Forcepoint offers policy-rich enterprise DLP across channels.
Where it fits. Organizations that want deep policy control and are staffed to tune it.
How it compares to Strac. Forcepoint is policy-breadth oriented. Strac focuses on fixing the exposure automatically (remove public access, revoke external members, redact) and on Copilot/MCP coverage that legacy suites do not reach.
6. Proofpoint Enterprise DLP
Proofpoint extends its email-security heritage into broader DLP.
Where it fits. Teams standardized on Proofpoint for email who want SharePoint under the same vendor.
How it compares to Strac. Proofpoint's center of gravity is email and people-centric risk. Strac is purpose-built for data-centric SharePoint/OneDrive remediation and the AI path.
7. Netskope DLP
Netskope delivers DLP inside its SSE / CASB platform.
Where it fits. Organizations routing traffic through Netskope that want inline cloud and web DLP.
How it compares to Strac. Netskope is inline and network-oriented. Strac operates at the data layer inside SharePoint and OneDrive, remediating access and redacting content an inline gateway never touches, plus the MCP agent path.
🔍 SharePoint & OneDrive DLP compared
Capability
Strac
Purview
Nightfall
Legacy suites*
Detect PII/PHI/PCI in files (OCR)
Yes
E5
Yes
Yes
Find public & external sharing
Yes
Partial
Partial
Partial
Auto-remove public access
Yes
No
No
No
Revoke external / guest members
Yes
No
No
No
Redact data inside a file
Yes
No
Detection-led
Partial
Alert in Slack / Teams
Yes
No
Partial
No
Protect Copilot & MCP agents
Yes
Limited
Partial
No
Deployment
Agentless
E5, native
API
Agent-heavy
*Symantec, Forcepoint, Proofpoint, Netskope. Positioning reflects each platform's primary focus in 2026; validate against your own use case.
Copilot surfacing sensitive files — an over-permissioned site becomes an instant AI leak surface; see Microsoft Copilot DLP.
MCP agents reading raw files — MCP DLP redacts before an agent retrieves.
Compliance exposure — SharePoint data is in scope for HIPAA, PCI, and GDPR.
🌶️ Spicy FAQs
What is the best SharePoint and OneDrive DLP solution in 2026?
It depends on what you need beyond detection. If you want to automatically remediate risky access (remove public links, revoke external members), redact sensitive data inside files, and protect Copilot and MCP agents, Strac is the strongest all-round choice. If you are licensed for E5 and only need baseline native policy, Microsoft Purview may cover the basics.
Does Microsoft Purview cover SharePoint DLP?
Yes, but its strongest DLP features require E5 licensing, and it focuses on policy tips and blocks rather than redaction or automatically removing public/external access. Many teams pair Purview with a tool like Strac for remediation and Copilot coverage.
How do I stop SharePoint files from being over-shared externally?
You need a tool that both finds public and external sharing and acts on it. Strac detects risky access and automatically removes the public link or revokes the external member, then alerts the owner in Slack or Teams.
Does SharePoint DLP protect against Copilot leaks?
Native controls do not fully. Copilot can surface any sensitive file in an over-shared site. Strac redacts the data at the source and inspects Copilot and MCP retrieval so the assistant only returns clean results.
Do I need E5 for SharePoint DLP?
Not with Strac. It connects agentlessly and works independently of your Microsoft licensing tier, so you get detection, access remediation, and redaction without upgrading to E5.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.