October 29, 2026

8
min read
How Data Loss Prevention in Cloud Computing Works?
Learn how data loss prevention in cloud computing works across SaaS, cloud storage, browsers, and AI agents, and how Strac fixes leaks in place
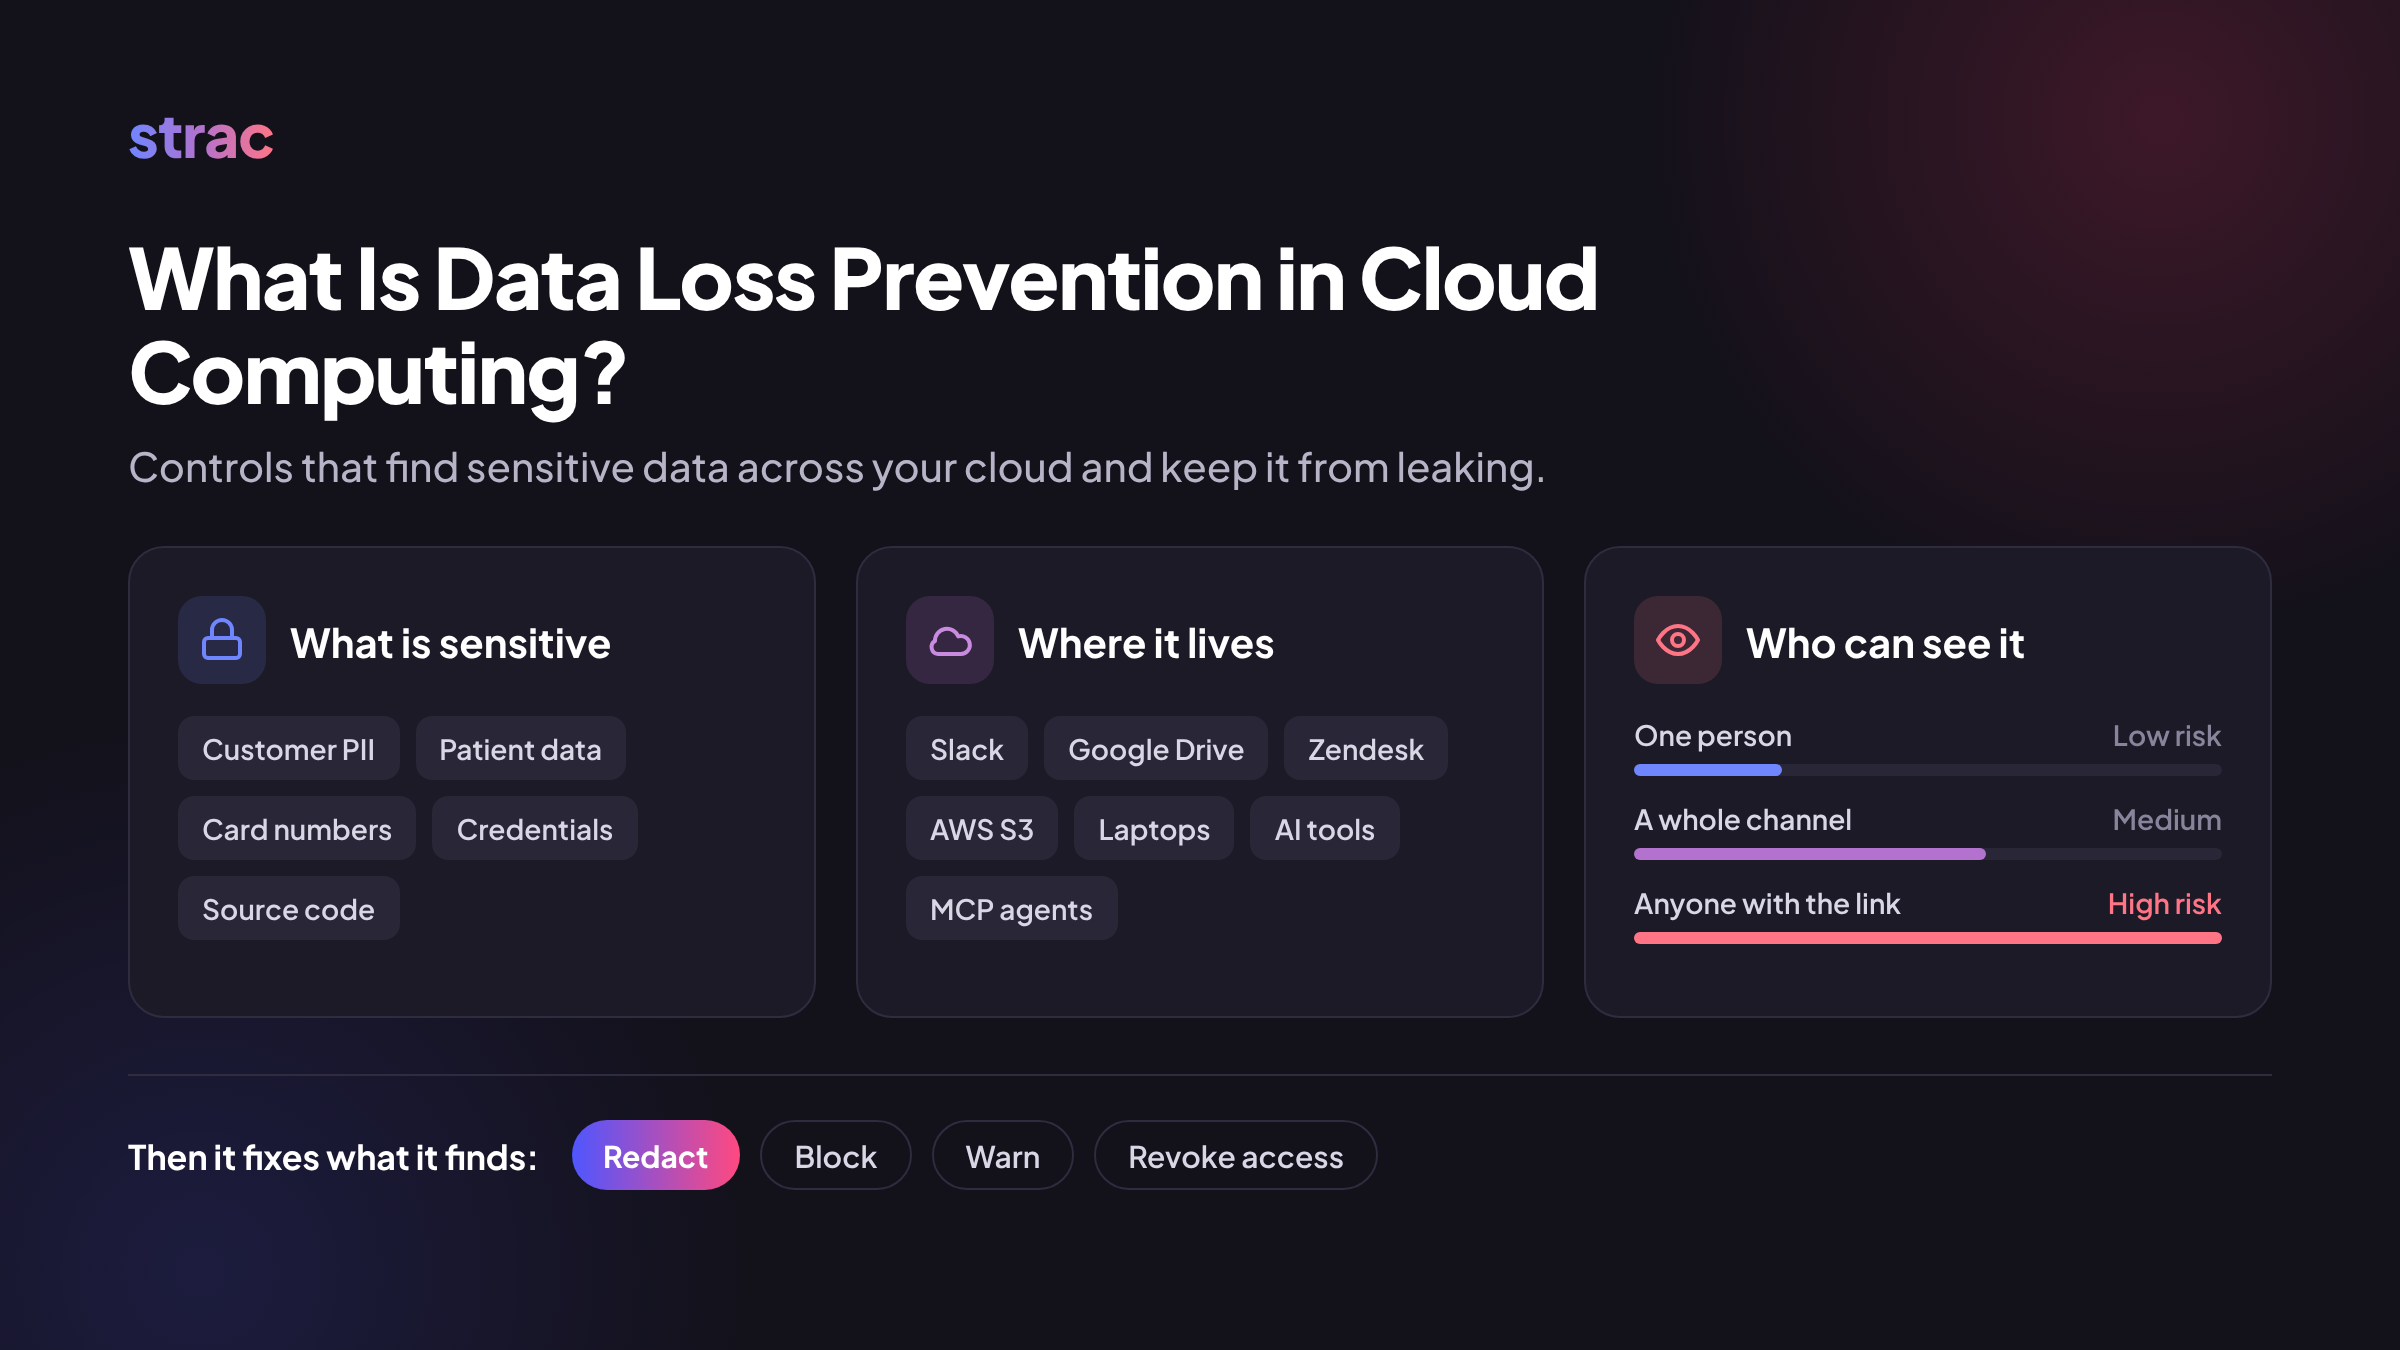
Data loss prevention in cloud computing is a set of controls that finds sensitive data in cloud services and keeps it from leaking. Your cloud provider secures the servers. You secure what you put on them.
Cloud DLP answers three questions:
Then it fixes what it finds. A report tells you where the problem is; remediation makes it go away.
Classic DLP was built for email gateways and the office network. Those exits still exist; they are just no longer the main event.
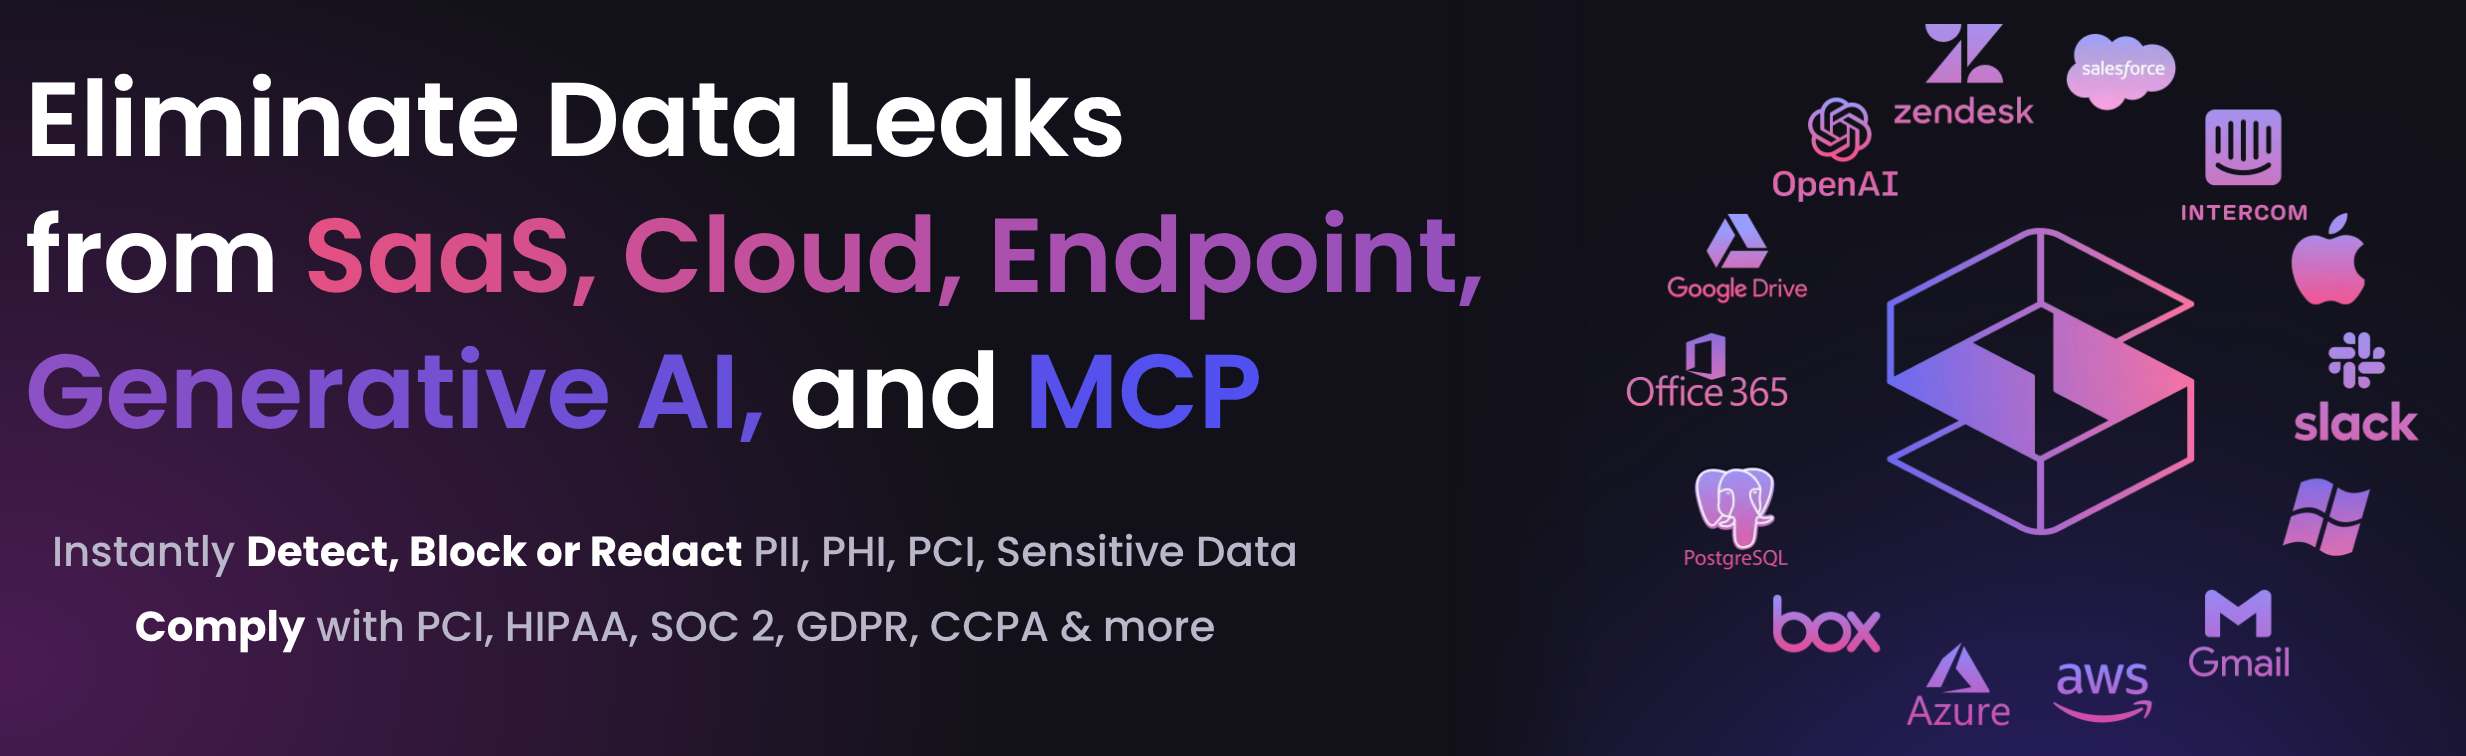
Today the leak looks different:
Network DLP sees encrypted traffic going to these apps. It does not see the Social Security number inside. That is why legacy DLP fails for AI and for SaaS alike.
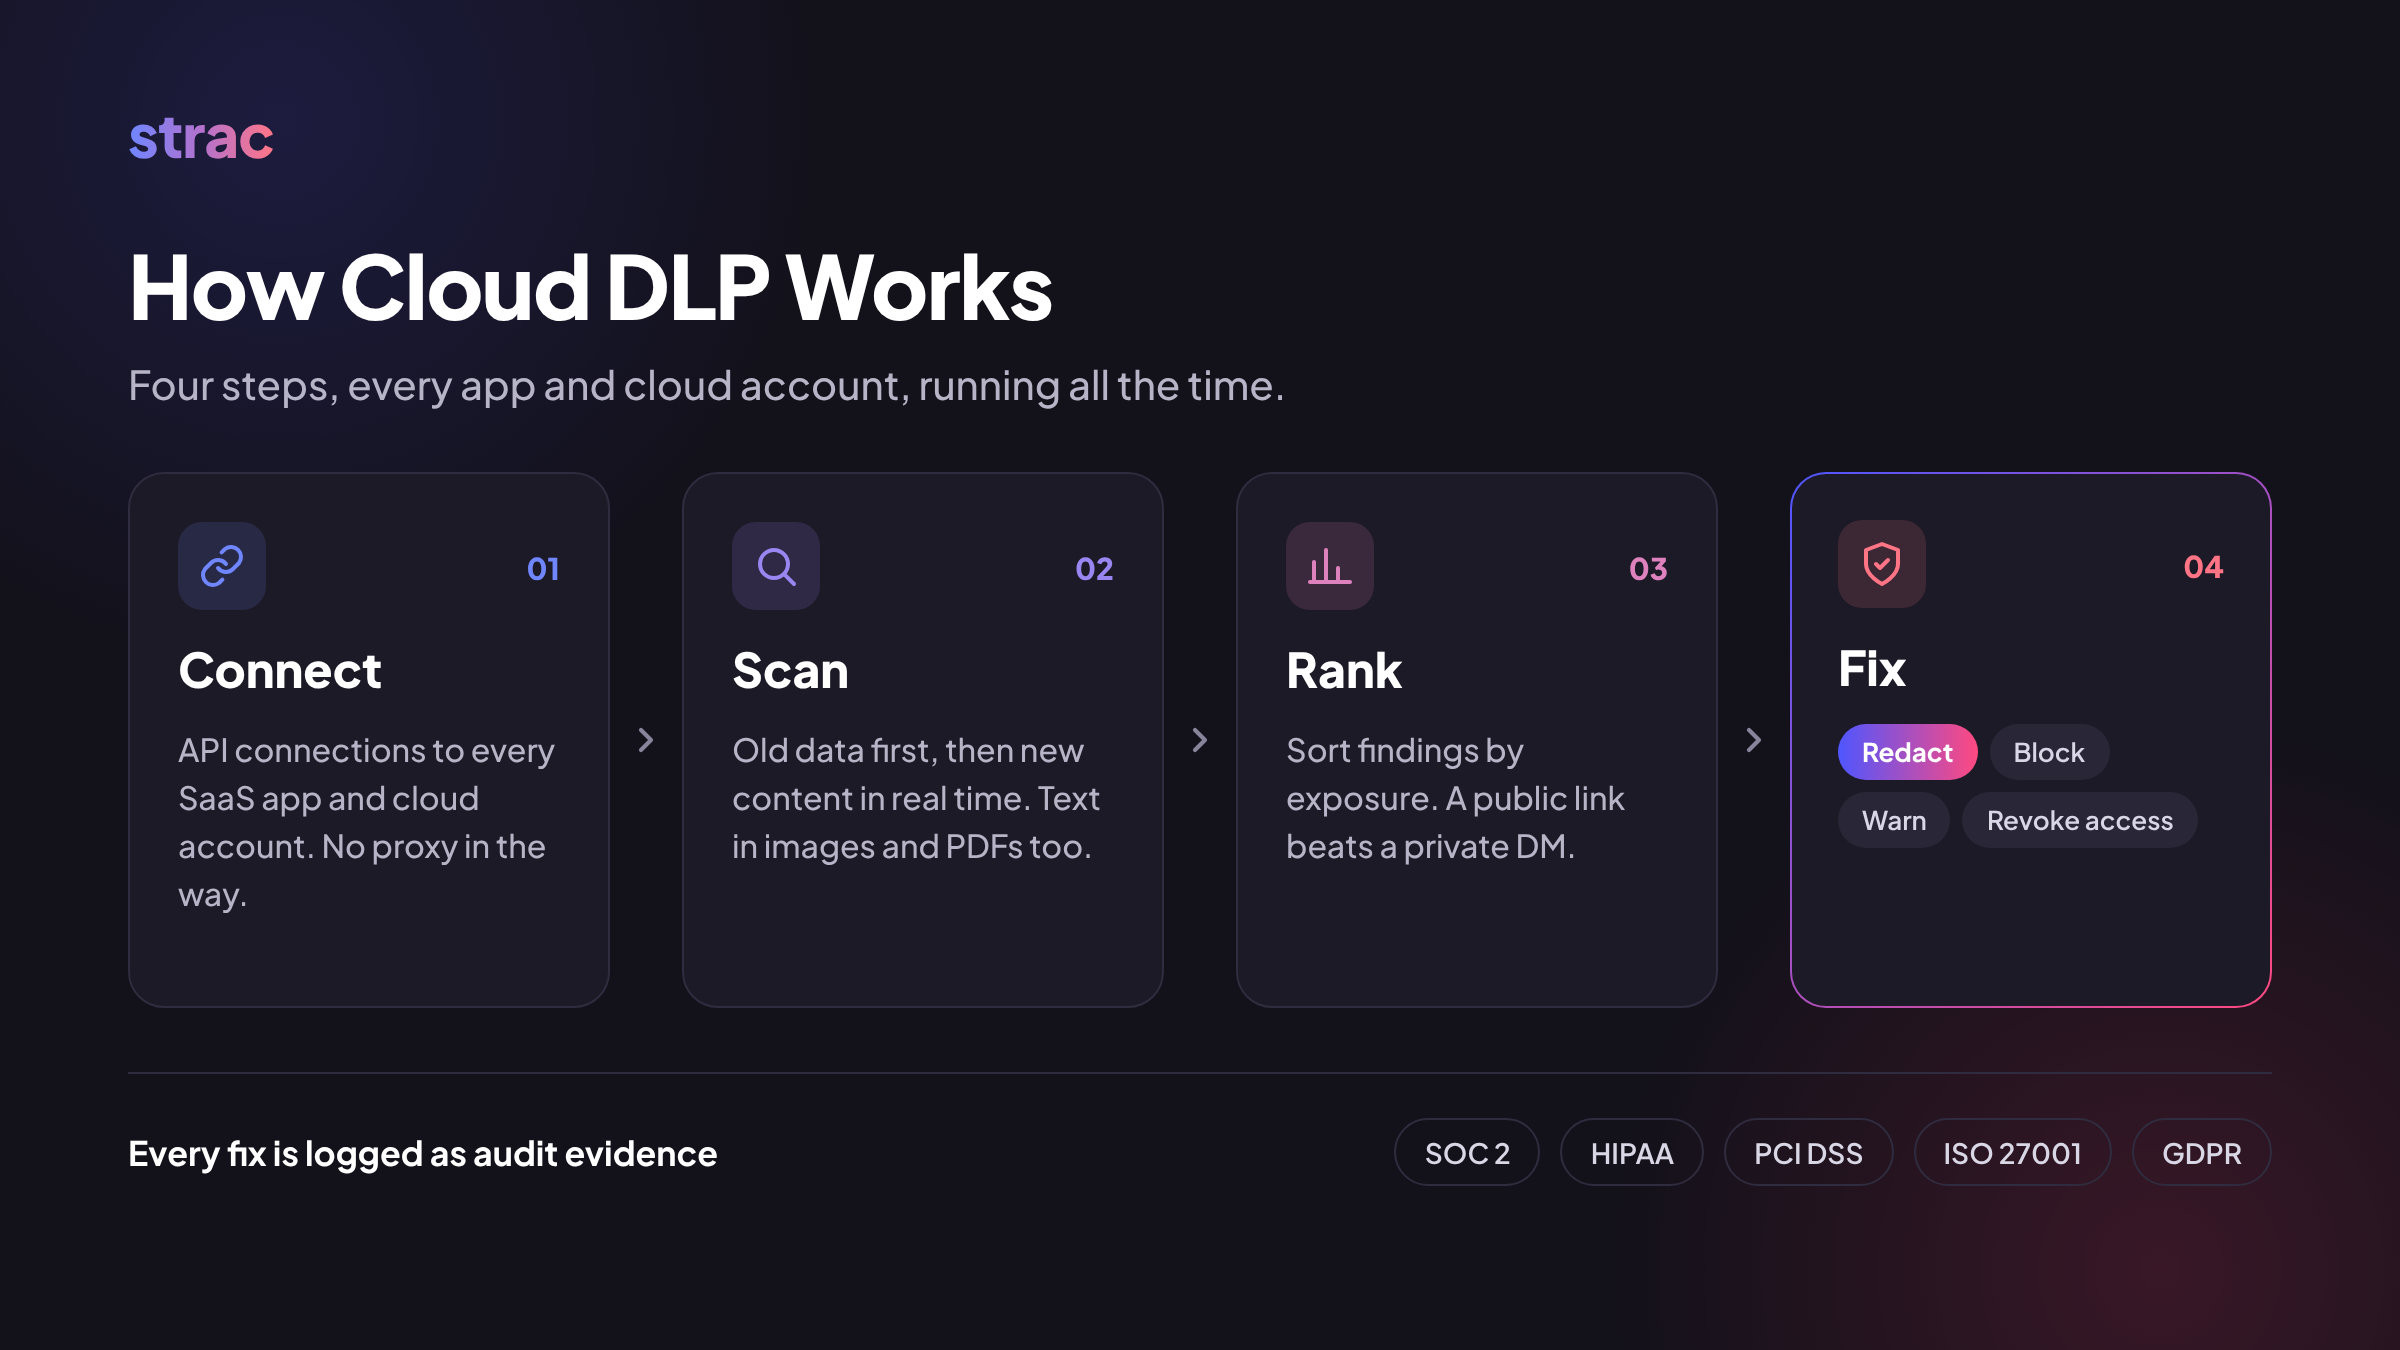
Every working cloud DLP program runs the same four steps:
Every fix is logged, so the same work doubles as audit evidence for SOC 2, HIPAA, PCI DSS, ISO 27001, and GDPR.
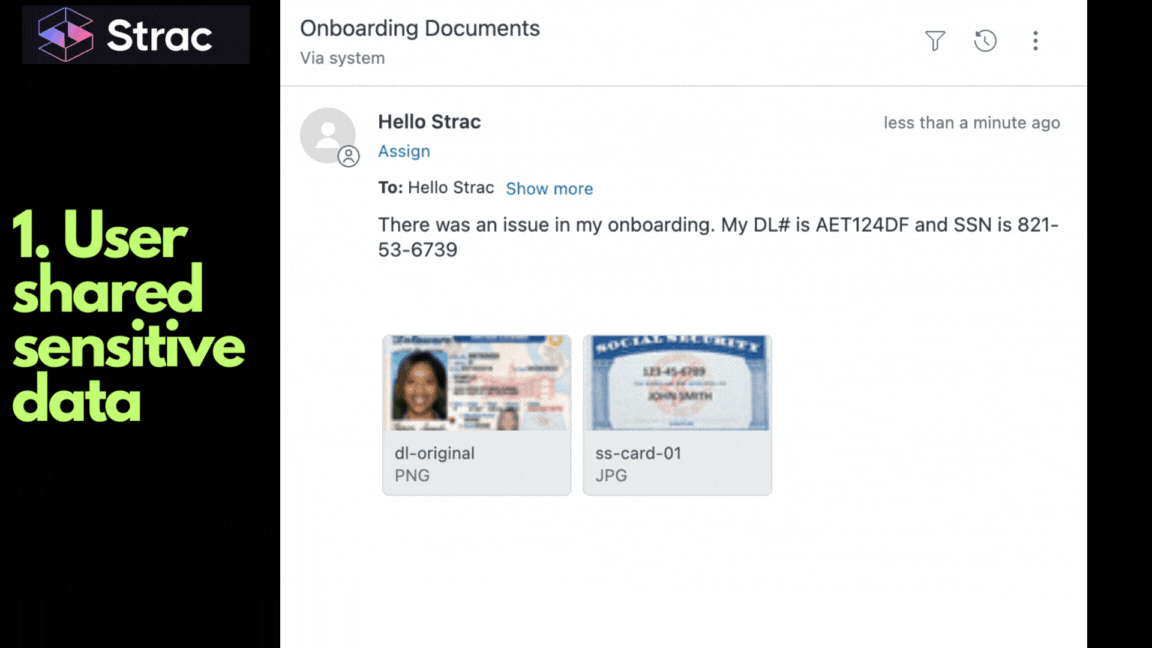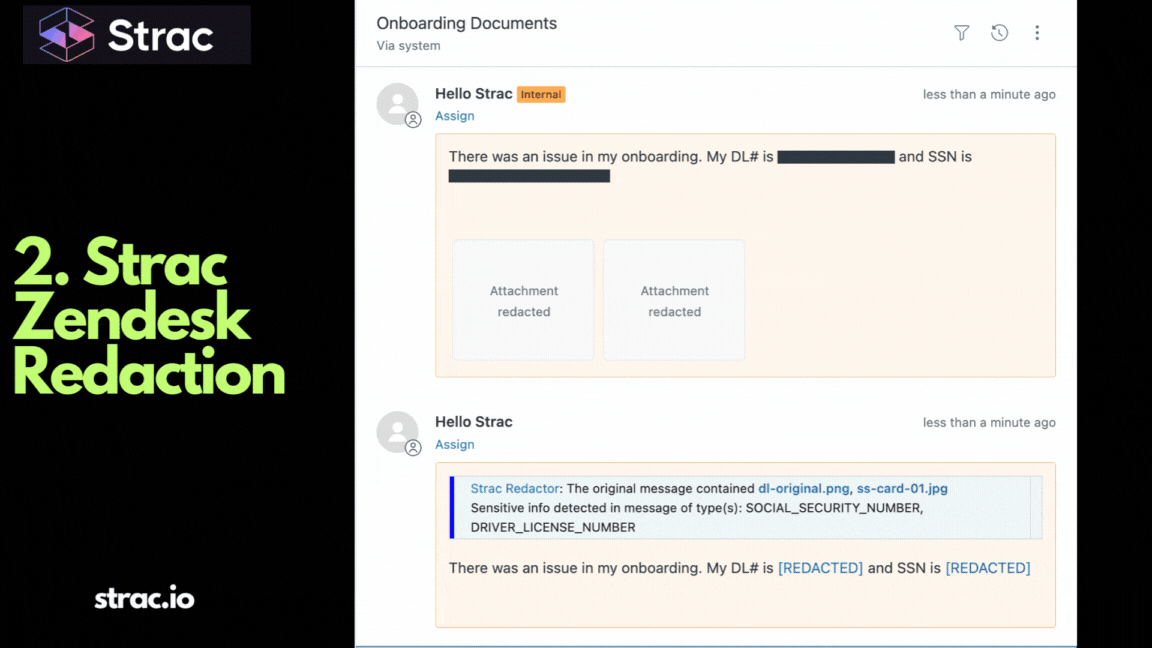
Every leak follows three steps: someone grabs data, sends it somewhere, and the destination keeps it. Access controls target the first step. Enforcement has to sit at the second.
That is where data-layer controls work. When a customer pastes a card number into Zendesk, Strac masks it in the ticket. When an employee pastes it into ChatGPT, AI DLP catches it in the browser. When an agent pulls it through MCP, MCP DLP redacts the response before the model sees it.
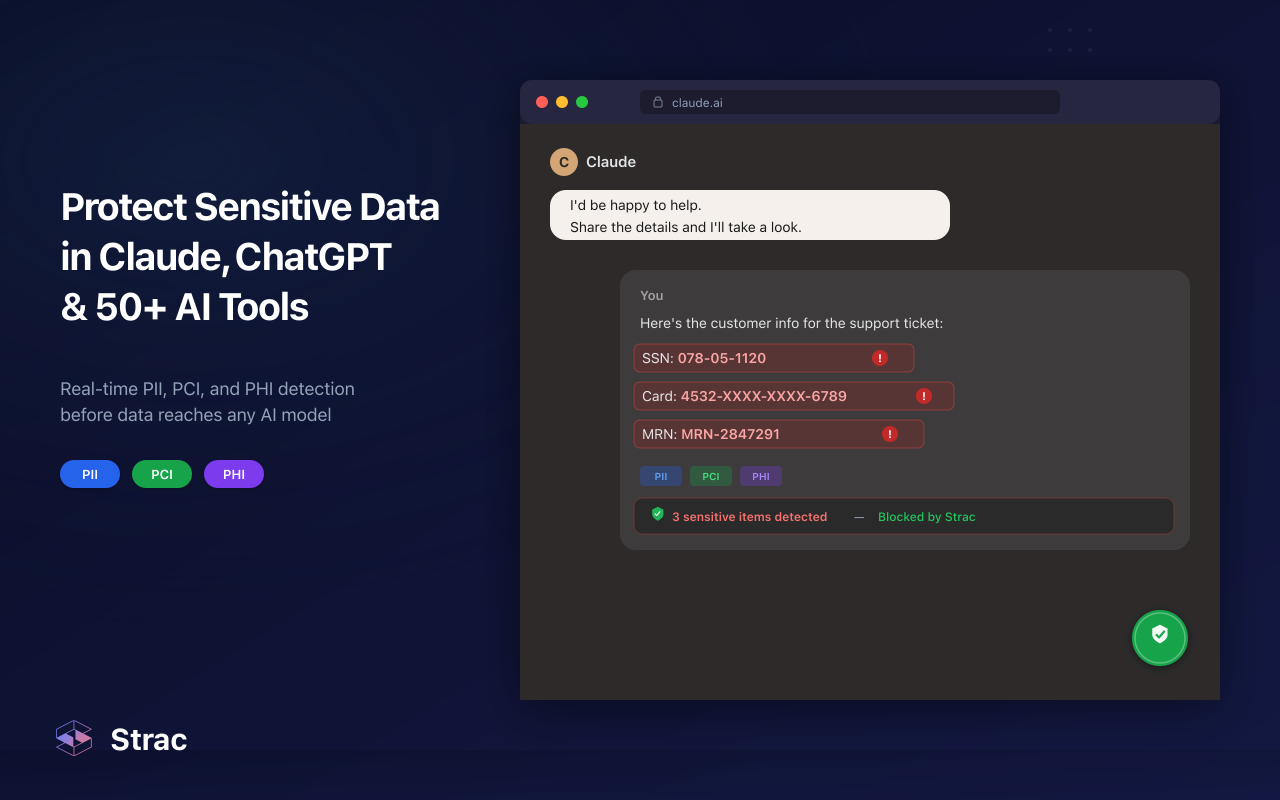
Access control decides who gets in; Strac decides what they can take out.
Strac is a DLP, Data Discovery, and DSPM platform that protects data across every cloud app your team uses.
When Strac finds sensitive data, it acts in this order:
Policies map to SOC 2, HIPAA, PCI DSS, ISO 27001, and GDPR, so the controls double as audit evidence. SaaS integrations connect through APIs in under 10 minutes.
Finding data shows you the risk. Redacting it removes the risk. You need both.
👉 Related reading:
Your cloud provider keeps the servers running. Keeping customer data out of the wrong channel, bucket, prompt, or agent is your job. Identity, network, and model controls all fail eventually, so the data layer is the backstop: redact on every action and a mistake never becomes a breach.
Book a demo to see Strac protect your data across SaaS, cloud, browser, endpoint, and MCP!
No. A CASB controls which cloud apps people use and how they log in. Cloud DLP inspects the data inside those apps and fixes it. Only DLP finds the card number sitting in a Zendesk ticket from 2023.
Because the provider secures the servers, not your data. AWS will keep S3 running, but it will not stop someone making a bucket public. It also cannot see your Slack threads, laptops, or AI prompts.
Not if the default is redaction, not blocking. Strac strips the card number or SSN and lets the message, prompt, or agent request go through. People keep working; only the sensitive fragment stays home.
Not on its own. Nothing stops a phone camera pointed at a screen, and prompt injection is still an open problem. That is why the data layer matters: data that is already redacted is worthless to whoever takes it.
It is the enforcement layer of AI data governance. Policy sets the rules, cloud DLP enforces them on every app and agent, and audit logs prove both. See the AI data governance pillar for the full picture.
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath





Customers include