Is ServiceNow HIPAA compliant? Yes — ServiceNow signs a BAA and offers healthcare products, so it can be HIPAA compliant with proper configuration. See BAA status, where PHI ends up, the AI/MCP gap, and how Strac protects it.
Is ServiceNow HIPAA compliant?Yes, conditionally — ServiceNow signs a BAA on eligible plans, but only for its core surface.
ServiceNow routinely touches PHI in a healthcare context — the moment a covered entity uses it, patient data is in scope.
The newest risk is AI over MCP: ServiceNow now exposes an official MCP server and AI features that can pull that data into an LLM with no BAA behind it.
A signed BAA (where one exists) covers the app’s core workflow — not the AI/MCP layer, integrations, or data leaving its boundary.
Strac keeps PHI safe either way — detecting and redacting it on the MCP path, in the browser, and on the endpoint, and finding PHI already stored at rest.
✨ Is ServiceNow HIPAA Compliant? The Direct Answer
Yes, but only when negotiated — never by default. ServiceNow signs a BAA on an eligible enterprise contract with scoped services, and a default corporate account carries no HIPAA coverage. Its 2026 MCP server and Now Assist AI open the platform to any agent, which is where PHI in tickets can escape. HIPAA compliance is never automatic — it depends on a signed Business Associate Agreement with the vendor plus how you configure and use the tool. Below is exactly where ServiceNow stands, where PHI ends up, the AI/MCP gap most teams miss, and how to close it. Verified August 2026.
Connect ServiceNow to an AI assistant over MCP and PHI can leave your BAA. Strac MCP DLP redacts it on the path.
Does ServiceNow Sign a BAA?
ServiceNow says it “is not a typical business associate” and will sign a BAA on an eligible enterprise contract when explicitly negotiated. The Healthcare and Life Sciences edition is recommended but not mandatory — standard Now Platform products can be configured for HIPAA workloads under a scoped, executed BAA. Engage ServiceNow’s compliance team to confirm which services and environments are HIPAA-eligible before any PHI enters an instance.
Product / surface
PHI status
✅ ITSM, HRSD, CSM & custom apps
When in scope of a signed, negotiated BAA — ServiceNow secures the cloud infrastructure and core platform under a shared-responsibility model
❌ App Store & third-party integrations
Separate vendors with their own terms
❌ Notification email, analytics & connected EHRs
External systems the BAA does not extend to
❌ Any service or environment not named HIPAA-eligible
Must be explicitly scoped in the executed BAA
Source: ServiceNow HIPAA overview. Vendor terms change — reconfirm your plan’s eligibility in writing before sending PHI.
Where PHI Ends Up in ServiceNow
Even teams that never intend to handle PHI accumulate it in ServiceNow. The common places it lands:
ITSM tickets referencing a patient record or a clinical-app error with PHI in the description
HR service cases with employee health data (leave, disability, workers’ comp, benefits)
CSM case notes and attachments involving members or patients
Screenshots and log files attached to incidents that inadvertently contain PHI
✨ The New Risk: ServiceNow + AI Agents via MCP
In 2026 ServiceNow made an MCP Server generally available in every Now Assist and AI-Native SKU, opening the platform to ServiceNow-built, Claude, Copilot, and custom agents, while Now Assist generative AI runs across ITSM, HRSD, and CSM. Actions route through the AI Control Tower for identity and audit — but any of these can move ticket or case content, including PHI, to a model unless governance is configured. See our ServiceNow MCP server guide.
Assume no HIPAA coverage on a default ServiceNow account: eligibility requires an eligible contract, scoped services, and a fully executed BAA in writing — and the BAA never extends to integrations, notification email, analytics, or connected EHRs. This is the leak path traditional HIPAA controls were never designed to see: the data does not breach outward, it is pulled inward by an AI agent on a legitimate, authenticated tool call. Read more on MCP data loss prevention and ServiceNow MCP server.
Strac inspects and redacts sensitive data in real time as it moves toward an AI tool.
🎥 Why a Signed BAA Still Leaves a Gap
A BAA is a contract — it makes the vendor liable for the data it holds. It does not inspect your data, and it does not follow PHI into the AI features, integrations, or exports that sit outside its scope. Whether or not ServiceNow signs one, three gaps remain: PHI a user pastes or uploads where it should not go; PHI an AI agent pulls out over MCP; and PHI already sitting in ServiceNow that no one has found. Closing them needs data-layer DLP, not just paperwork.
Strac detects and redacts PII/PHI in real time across the browser and GenAI tools.
✨ How Strac Protects PHI in ServiceNow
Strac closes the exact gaps a ServiceNow BAA leaves open, across every surface PHI can move:
MCP DLP: Strac inspects every MCP tool call to and from ServiceNow and redacts PHI before it reaches Claude, ChatGPT, or any agent — so an AI assistant with no BAA never sees a patient identifier.
Browser / GenAI DLP: Strac’s browser extension detects PHI as it is typed, pasted, or uploaded into ServiceNow or a GenAI tool and blocks, warns, or redacts it in real time.
Endpoint DLP: When PHI is exported, downloaded, or copied from ServiceNow to a device, Strac’s Mac and Windows agent enforces at the file, USB, print, and upload channels.
DSPM: Strac scans ServiceNow and connected stores to find PHI already sitting at rest, classifies it, and flags oversharing so you can remediate it.
Strac redacts sensitive data automatically — the same detection and redaction engine runs across every surface.
✨ Remediation in Action: Redact, Block, Warn, Revoke
Detection alone does not stop a HIPAA violation — remediation does. Strac does not just alert; it acts the moment PHI appears:
Redact: strip PHI from the message, ticket, record, or MCP response and vault the original for authorized access.
Block: stop a PHI-bearing prompt, upload, or export before it leaves — in the browser and on the endpoint.
Warn & coach: tell the employee in the moment why an action was risky, turning policy into training.
Revoke access: when PHI is found oversharing in a connected store, Strac removes public and external access so no agent or person can reach it.
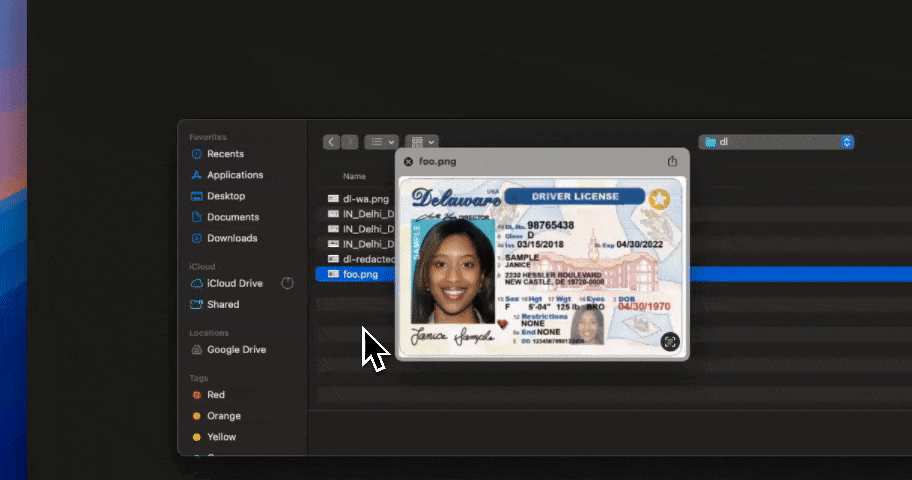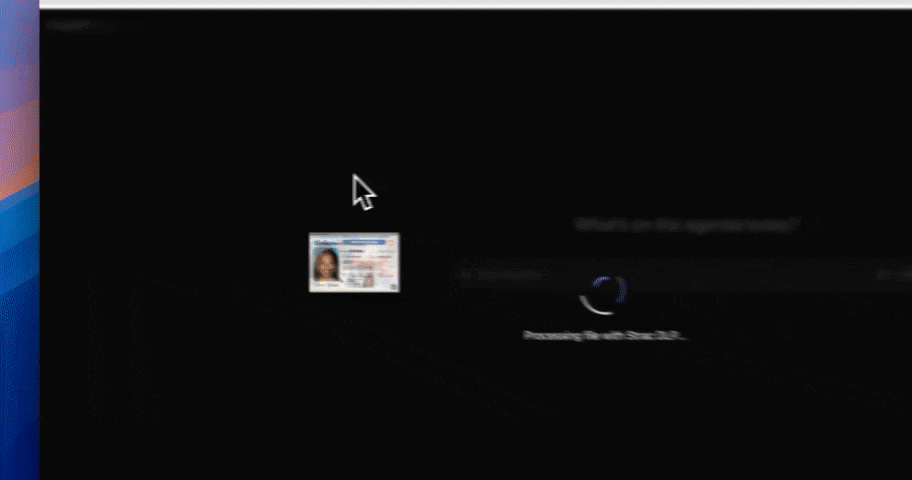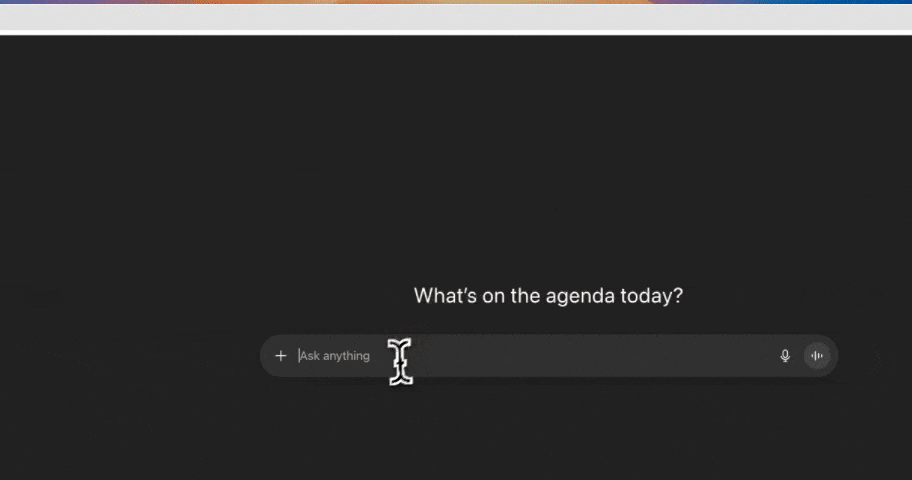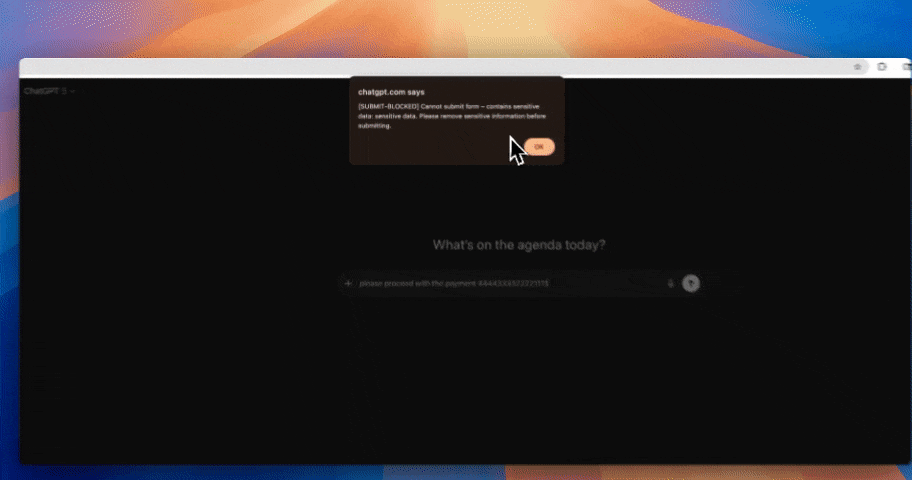
Strac warns and blocks sensitive uploads in real time, then coaches the user — content-aware, not a blunt lock.
✨ One Platform Across Every Surface ServiceNow Touches
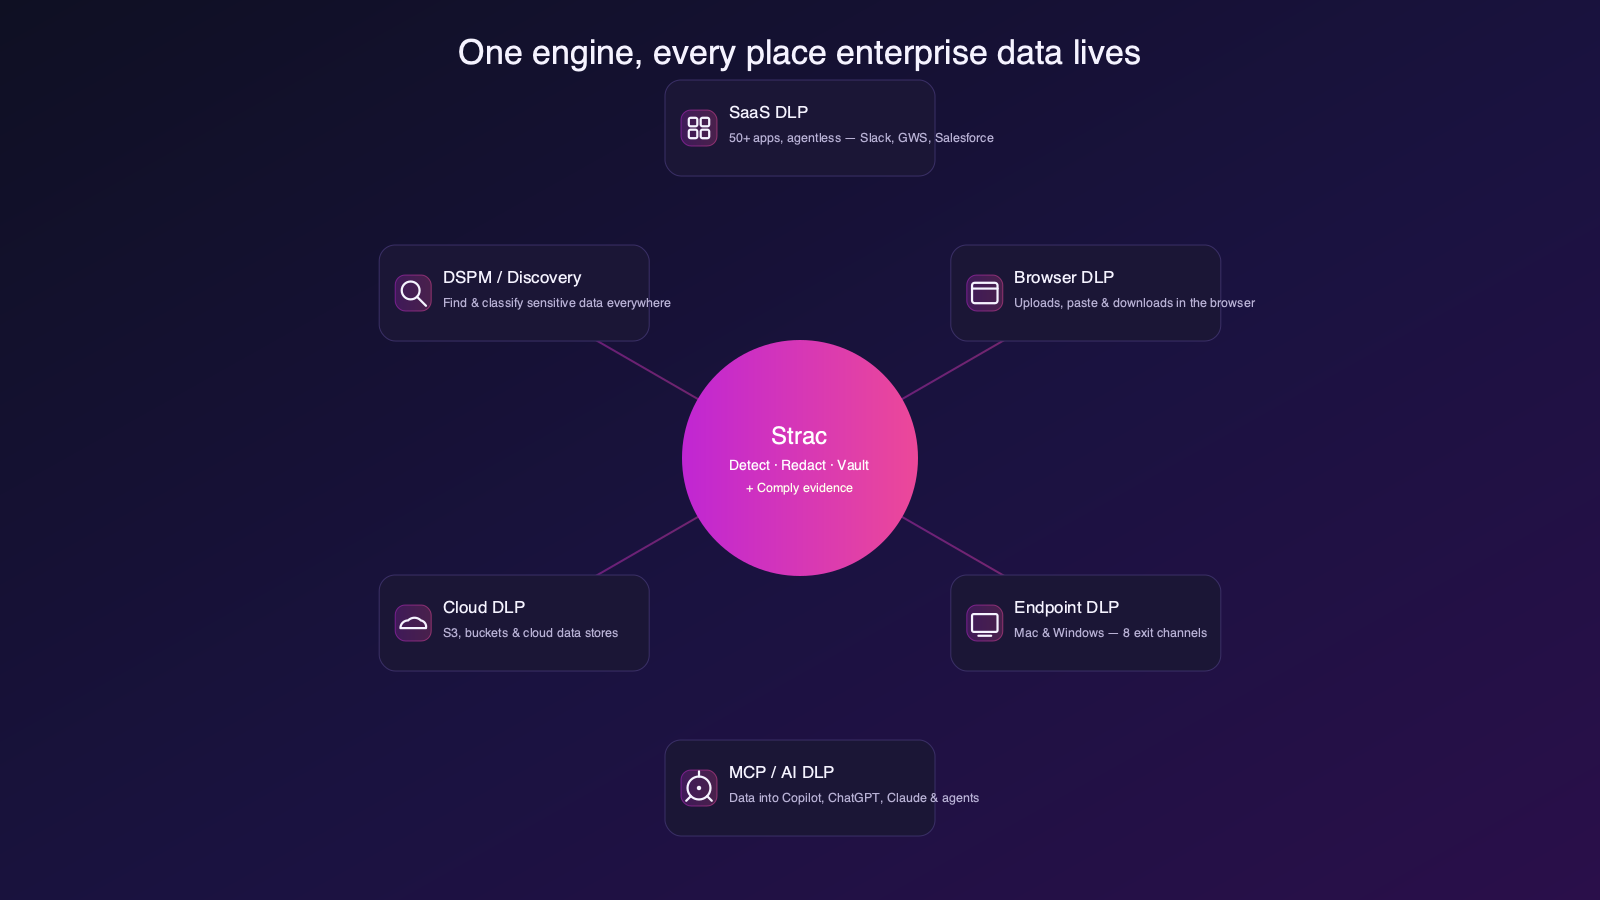
PHI does not stay inside ServiceNow. It flows into email, chat, cloud storage, GenAI tools, and AI agents — so point fixes leave gaps. Strac is one agentless-plus-endpoint platform covering SaaS, cloud, browser, GenAI, endpoint, and MCP under a single policy and classifier, live in minutes.
Strac covers SaaS, cloud, browser, endpoint, GenAI, and MCP from one platform — one policy for every place PHI moves.
A Practical ServiceNow HIPAA Deployment Checklist
Contract: Execute ServiceNow’s BAA on an eligible plan before any PHI, and confirm which services are in scope in writing.
Scope the AI/MCP layer: inventory whether ServiceNow’s MCP server and AI features are enabled, and confirm they are excluded from — or explicitly added to — your coverage.
Deploy Strac MCP DLP: put redaction in front of every ServiceNow MCP tool call so no agent receives raw PHI.
Deploy Browser + Endpoint DLP: block and redact PHI at entry and export across the web app and devices.
Run DSPM: scan ServiceNow for PHI already stored, classify it, and remediate oversharing.
Prove it: keep the audit log of every detection and remediation as HIPAA evidence.
ServiceNow HIPAA Compliance: Quick Reference
Question
Answer
Does ServiceNow sign a BAA?
Yes — eligible plans, executed BAA required
Is the AI / MCP layer covered?
No — outside the BAA; the main leak path
Can PHI be used safely?
Yes, on an eligible plan with a BAA plus data-layer controls
What closes the gap?
Strac MCP + Browser + Endpoint DLP and DSPM
🌶️ Spicy FAQs for Is ServiceNow HIPAA Compliant
Is ServiceNow HIPAA compliant out of the box?
No tool is. You must be on an eligible plan, execute the BAA, and configure controls before PHI.
Does ServiceNow’s BAA cover its AI and MCP features?
No. That is the single most common misread — the AI/MCP layer sits outside the core BAA and is the most likely place PHI leaks to a model.
Can an AI agent pull PHI out of ServiceNow?
Yes. ServiceNow’s official MCP server lets an agent read data on an authenticated tool call. Strac redacts PHI on that path before the agent sees it.
Is a BAA enough for HIPAA?
No. A BAA assigns liability; it does not inspect your data or follow PHI into AI, integrations, or exports. You still need data-layer DLP.
How does Strac help if we already use ServiceNow?
Strac layers on without slowing ServiceNow down — redacting PHI at the MCP layer, blocking it in the browser and on the endpoint, and finding PHI already stored via DSPM.
ServiceNow can be used with PHI on an eligible plan with a signed BAA — but the BAA stops at the core workflow, while the AI/MCP layer keeps moving PHI. Strac closes the gap on every surface — redacting PHI at the MCP layer, blocking it in the browser and on the endpoint, and finding what is already stored. Book a demo to see it on ServiceNow.
Is ServiceNow HIPAA compliant in 2026?
Yes — ServiceNow signs a BAA and offers healthcare products, so it can be HIPAA compliant with proper configuration.
Can I use ServiceNow with Claude or ChatGPT and stay HIPAA compliant?
Only if PHI never reaches a model that isn’t under a BAA. Claude Cowork does not sign one, so connecting ServiceNow over MCP can expose PHI. Strac MCP DLP redacts PHI on the MCP path before it reaches the assistant.
Does ServiceNow store PHI?
It can — patient records in cases and incidents, HR service records with health data, and knowledge articles. Whether or not that’s intended, it needs to be protected.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.