Protect sensitive data with Strac, a superior alternative to Broadcom Data Loss Prevention, offering advanced features, seamless integration, and comprehensive SaaS, Cloud, and Endpoint protection.
Broadcom Data Loss Prevention safeguards sensitive data from unauthorized access and transfers.
Strac offers a superior alternative with advanced features, compliance support, and ease of integration.
Strac provides accurate detection and redaction, extensive SaaS integrations, and AI integration.
Strac's Endpoint DLP solution is comprehensive and accurate, covering SaaS, Cloud, and Endpoint environments.
Strac's customizable configurations and positive customer reviews make it a top choice for data protection and compliance.
✨ What is Broadcom Data Loss Prevention?
Broadcom Data Loss Prevention is a comprehensive security solution designed to protect sensitive data from being lost, stolen, or mishandled. It involves a combination of tools and techniques that monitor, detect, and prevent unauthorized data transfers across networks, endpoints, and cloud environments. Broadcom's DLP solution aims to minimize the risk of data breaches and ensure compliance with regulatory standards.
Best Alternative for Broadcom
Examples of Broadcom Data Loss Prevention in Action
Email Monitoring: Broadcom DLP can scan outgoing emails for sensitive information such as credit card numbers or social security numbers. If any sensitive data is detected, the system can automatically block the email or redact the sensitive information before it is sent.
Endpoint Protection: Broadcom DLP provides endpoint protection by monitoring and controlling data transfers from devices like laptops and smartphones. For instance, if an employee tries to copy sensitive files to a USB drive, the system can prevent the transfer and alert the security team.
Cloud Security: Broadcom DLP extends its protection to cloud environments, ensuring that sensitive data stored or shared in cloud applications is secure. It can identify and protect data across various cloud services, including file-sharing platforms and collaboration tools.
What Risks or Problems Does Broadcom Data Loss Prevention Solve?
Data breaches and unauthorized data access can have devastating consequences for businesses, including financial losses, reputational damage, and regulatory penalties. Broadcom Data Loss Prevention addresses these risks by providing robust security measures to protect sensitive information.
Examples of Risks Addressed by Broadcom Data Loss Prevention
Insider Threats: Employees or contractors with access to sensitive data can pose significant risks. Broadcom DLP helps mitigate these risks by monitoring and controlling data access and transfer within the organization.
External Attacks: Cybercriminals often target businesses to steal sensitive information. Broadcom DLP can detect and block attempts to exfiltrate data, safeguarding the organization against external threats.
Regulatory Compliance: Many industries are subject to strict regulations regarding data protection. Broadcom DLP helps businesses comply with regulations such as GDPR, HIPAA, and PCI DSS by ensuring that sensitive data is adequately protected.
What Does an Ideal Data Loss Prevention Solution Need to Have?
An effective Data Loss Prevention (DLP) solution is essential for safeguarding sensitive information in today's digital landscape. It should encompass several critical features to ensure comprehensive protection across various data formats and environments.
Accurate Detection and Classification: The cornerstone of any DLP solution is its ability to accurately identify and classify sensitive data. This includes structured data (like databases and spreadsheets) and unstructured data (such as documents and emails), whether in transit or at rest. By understanding the context and content of data, DLP systems can effectively apply appropriate security controls.
Comprehensive Coverage: A robust DLP solution should extend its protective measures across all endpoints (including laptops, desktops, and mobile devices), networks (internal and external), and cloud environments. This broad coverage ensures that sensitive data is secure regardless of its location or method of access.
Real-Time Monitoring and Response: Timely detection and response are critical components of effective DLP. Real-time monitoring enables immediate identification of suspicious activities or policy violations. Automated responses, such as blocking or alerting, help mitigate risks promptly, reducing the impact of potential data breaches.
Ease of Integration: Seamless integration with existing IT infrastructure and applications streamlines implementation and operational efficiency. Compatibility with various platforms and services—including SaaS applications and cloud environments—ensures that DLP solutions can protect data wherever it resides within the organization's ecosystem.
Customization and Scalability: Businesses operate with unique data protection requirements that evolve over time. An ideal DLP solution should offer customizable configurations to tailor security policies based on specific needs and compliance obligations. Scalability ensures that the solution can grow alongside the organization, accommodating increasing volumes of data and expanding operational landscapes.
By integrating these essential features, a DLP solution not only enhances data security but also supports regulatory compliance efforts. It empowers organizations to proactively protect sensitive information, mitigate risks effectively, and maintain trust with stakeholders in an increasingly data-driven world.
✨ Strac: A Superior Alternative to Broadcom Data Loss Prevention
Strac is a SaaS/Cloud DLP and Endpoint DLP solution that offers modern features to safeguard sensitive data. Strac stands out as a superior alternative to Broadcom Data Loss Prevention with its advanced capabilities and user-friendly approach.
Built-In & Custom Detectors
Strac supports all sensitive data elements detectors for PCI, HIPAA, GDPR, and any confidential data. It also allows customers to configure their own data elements. Strac is the only DLP solution on the market that performs detection and redaction of images (jpeg, png, screenshot) and deep content inspection on document formats like PDF, Word docs, spreadsheets, and zip files. Check out Strac’s full catalog of sensitive data elements.
Compliance
Strac helps businesses achieve compliance for PCI, SOC 2, HIPAA, ISO-27001, CCPA, GDPR, and NIST frameworks. By ensuring comprehensive data protection, Strac makes it easier for organizations to adhere to regulatory standards. Learn more about compliance by visiting PCI, SOC 2, HIPAA, ISO 27001, CCPA, NIST.
Strac's Data Loss Process Process
Ease of Integration
Strac allows customers to integrate and start seeing DLP/live scanning/live redaction on their SaaS apps in under 10 minutes. This quick integration capability ensures that businesses can promptly implement and benefit from Strac's robust DLP features.
Accurate Detection and Redaction
Strac’s custom machine learning models, trained on sensitive PII, PHI, PCI, and confidential data, provide high accuracy and low false positives and false negatives. This ensures that sensitive data is accurately identified and protected.
Rich and Extensive SaaS Integrations
Strac boasts the widest and deepest number of SaaS and Cloud integrations. This extensive integration capability ensures that Strac can seamlessly protect data across various platforms and services.
AI Integration
In addition to all SaaS, Cloud, and Endpoint integrations, Strac integrates with LLM APIs and AI websites like ChatGPT, Google Bard, Microsoft Copilot, and more. These integrations help protect AI or LLM apps and safeguard sensitive data. Strac Developer Documentation.
Endpoint DLP
Strac offers a comprehensive and accurate Endpoint DLP solution, making it the only DLP that works for SaaS, Cloud, and Endpoint environments. Checkout Endpoint DLP.
API Support
Strac provides developers with APIs to detect or redact sensitive data. This flexibility allows businesses to integrate Strac’s DLP capabilities into their custom applications. Checkout Strac API Docs.
Inline Redaction
Strac can redact (mask or blur) sensitive text within any attachment, providing an additional layer of data protection.
Customizable Configurations
Strac offers out-of-the-box compliance templates with all sensitive data elements to detect/redact, plus flexible configurations to cater to specific business needs. This ensures that data protection measures align with individual requirements.
Strac's G2 Reviews
Happy Customers
Strac’s effectiveness and user satisfaction are reflected in its positive reviews. Check out our G2 Reviews.
In conclusion, while Broadcom Data Loss Prevention provides robust security measures to protect sensitive data, Strac emerges as a superior alternative with its advanced features, ease of integration, and comprehensive coverage across SaaS, Cloud, and Endpoint environments. By choosing Strac, businesses can ensure the highest level of data protection and compliance with regulatory standards.
On-device DLP for the channels a proxy never sees
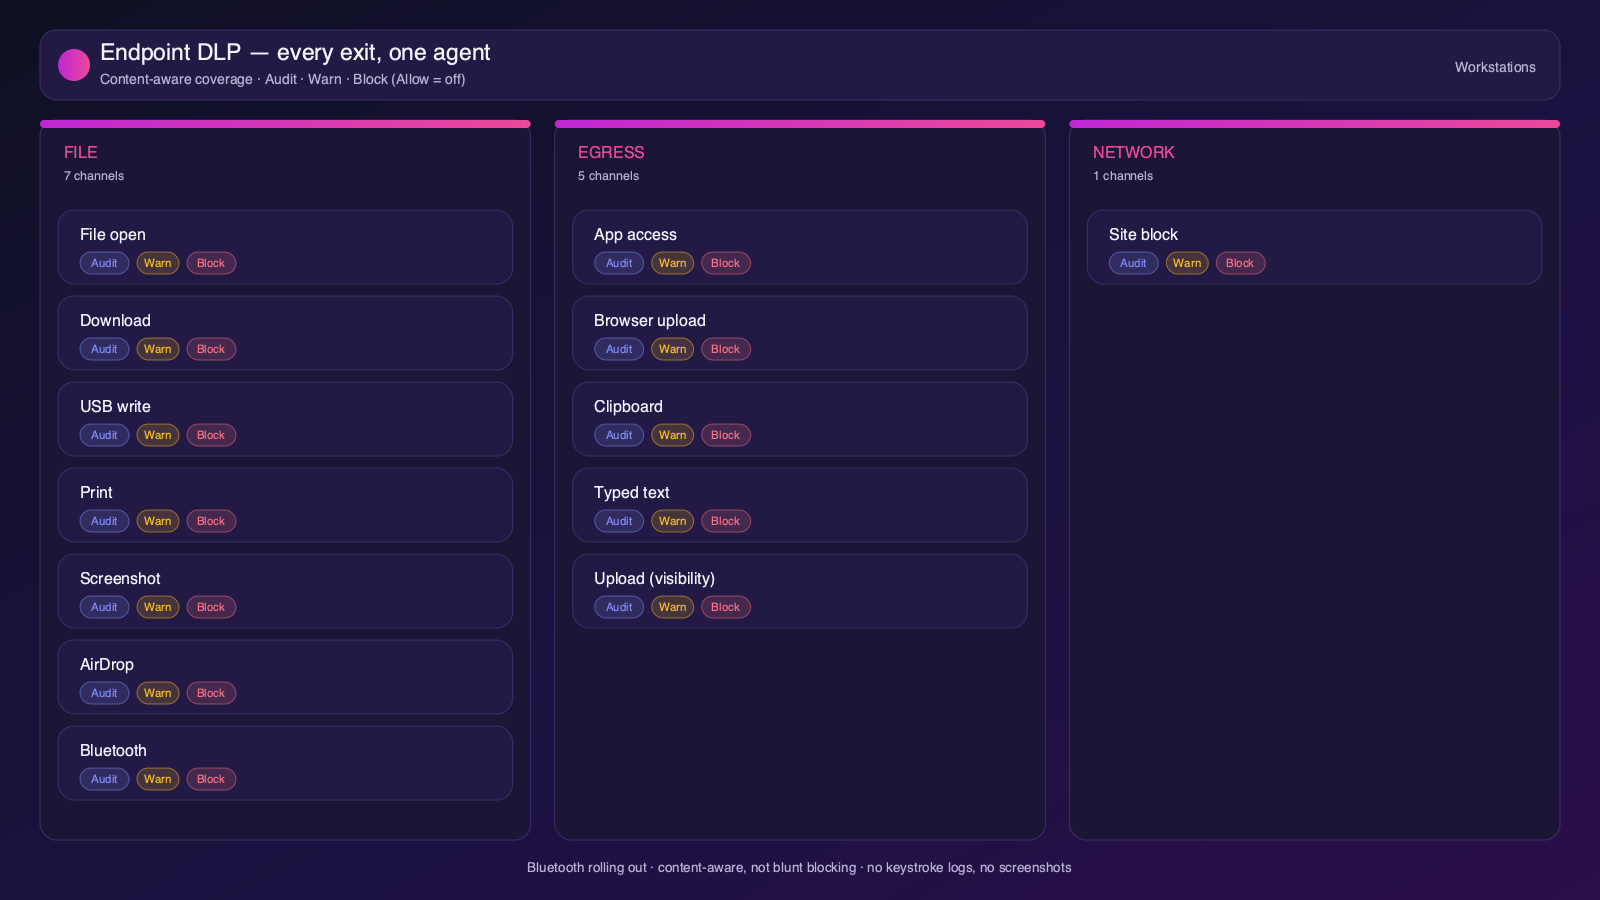
Strac’s endpoint agent enforces where network tools are blind — a file copied to USB, an AirDrop to a personal phone, a local print, a screenshot. It reads the content on the device and applies Block, Warn, or Audit per channel on Mac and Windows, coaching employees in the moment rather than only alerting after the fact.
Strac coaches and blocks at the endpoint — the local exits network DLP can’t observe.
Shadow AI, governed at the data layer
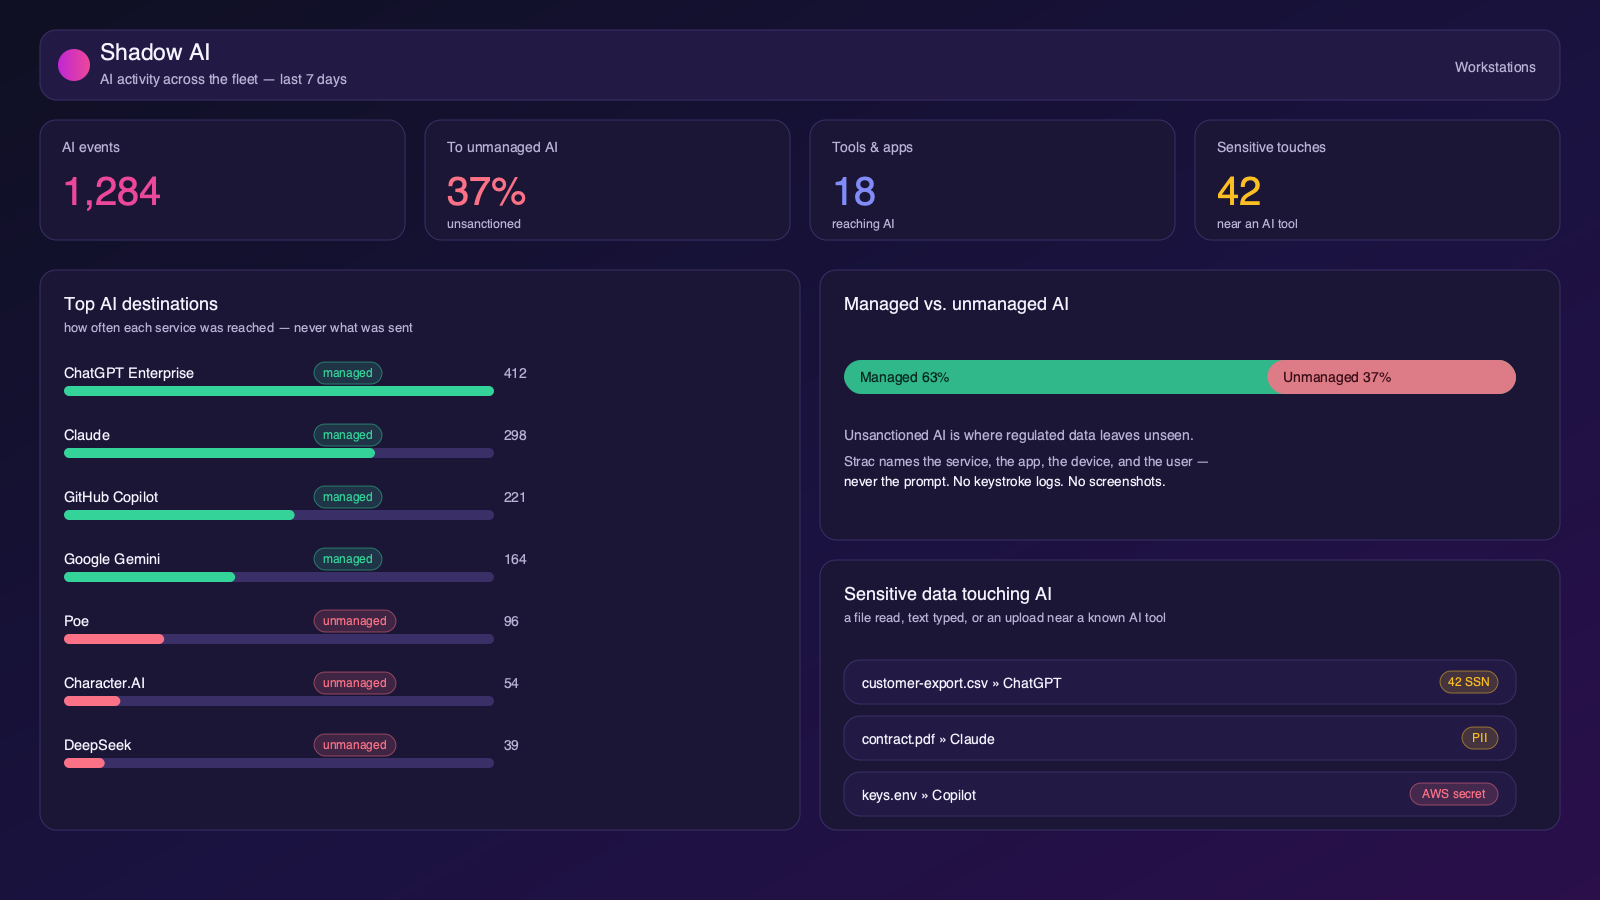
Strac turns Shadow AI from an unknown into a managed surface: it inventories the AI apps and agents in use, scores the data risk of each, and stops regulated content from reaching them — in the browser and at the MCP layer — while respecting employee privacy with no keystroke logs or screenshots.
Strac inventories Shadow AI usage and the data at risk — privacy-first, no keystroke logging.
✨ Strac's Endpoint Agent: A Lightweight Alternative to Broadcom's Endpoint DLP
Broadcom's DLP — the former Symantec suite — is powerful but enterprise-heavy: an on-prem-leaning architecture, an EDM/IDM fingerprinting pipeline to build and maintain, and a licensing-and-support experience that has grown harder since the acquisition. Its endpoint agent was built for a world before browser GenAI and MCP.
Where a legacy endpoint tool blocks bluntly or only alerts, Strac enforces content-aware policy across every exit on the machine — file opens and downloads, USB and removable-media writes, printing, screenshots, AirDrop, clipboard, browser uploads, and text typed directly into a GenAI prompt — each set independently to Block, Warn, or Audit on Mac and Windows.
Content-aware endpoint enforcement without a fingerprinting pipeline or a professional-services rollout.
Strac's endpoint agent needs no fingerprint library. It detects PII, PHI, PCI, secrets, and source code directly and enforces at the exact exit — file, USB, print, screenshot, AirDrop, clipboard, browser upload, or GenAI prompt — on Mac and Windows, each channel independently set to Block, Warn, or Audit.
It also runs Shadow AI detection and Data Lineage in the same agent, without keystroke capture or screenshots, and shares one policy engine with Strac's SaaS, cloud, browser, and MCP coverage. You get Broadcom-class endpoint control as one surface of a platform that is live in minutes, not months.
🌶️ Spicy FAQs on Broadcom DLP Alternatives
Why are teams leaving Broadcom (Symantec) DLP?
Rising costs and thinning support since the acquisition, an on-prem-leaning architecture, and an EDM/IDM fingerprinting pipeline that takes real effort to build and maintain. It was designed before browser GenAI and MCP.
Do I still need to build data fingerprints with Strac?
No. Strac detects PII, PHI, PCI, secrets, and source code directly, so there is no fingerprint library to maintain before it starts working.
Does Strac cover the endpoint like Broadcom does?
Yes — a lightweight Mac and Windows agent enforces content-aware policy at file, USB, print, screenshot, AirDrop, clipboard, browser-upload, and GenAI-prompt channels, in Block, Warn, or Audit mode.
What about GenAI and MCP, which Broadcom never covered?
Strac inspects GenAI prompts in the browser and enforces at the MCP layer on every tool call — the modern leak paths a perimeter-era suite cannot see.
How long is a Strac rollout versus Broadcom?
Minutes to connect SaaS agentlessly and a lightweight endpoint rollout — not the multi-month, services-led projects Broadcom deployments typically require.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.