Sharepoint

SharePoint security best practices + how Strac DSPM/DLP finds and remediates sensitive data

TL;DR:

  • Microsoft SharePoint requires robust security measures to safeguard sensitive data and ensure compliance.
  • Key best practices include enforcing least privilege access, monitoring external user access, and implementing multi-factor authentication.
  • Misconfiguration management involves auditing sharing links, reviewing site settings, and monitoring sensitive data in public sites.
  • Compliance and risk management strategies include deactivating dormant sites, monitoring third-party integrations, and conducting configuration compliance audits.
  • Data discovery and classification, access and sharing monitoring, and threat detection are essential components of a comprehensive SharePoint security strategy.

Short answer: SharePoint is secure when it is configured correctly, but its defaults are permissive, public "anyone with the link" sharing, broad external access, and no built-in data discovery or DLP, which makes oversharing and misconfiguration the top cause of SharePoint data exposure. The best practices below harden the configuration; pairing them with DSPM and DLP (like Strac) closes the data gap by finding and remediating sensitive data in SharePoint automatically.
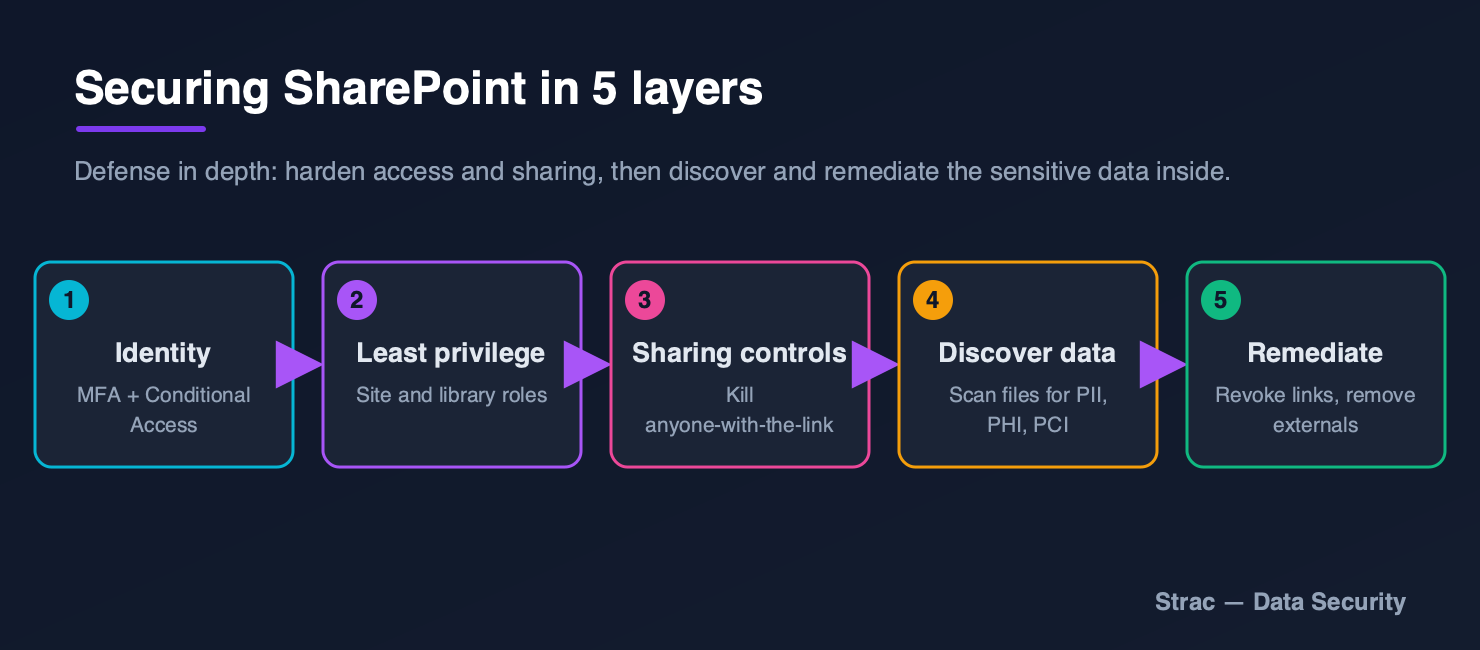
Diagram: securing SharePoint in five layers, identity and MFA, least privilege, sharing controls, sensitive-data discovery, and remediation
Securing SharePoint: harden access and sharing, then discover and remediate the sensitive data inside.

Microsoft SharePoint is a powerful platform for collaboration and content management, but its flexibility can introduce security challenges if not properly configured. To safeguard sensitive data and ensure compliance, organizations must implement robust security measures. In this guide, we outline the best practices for managing and securing your SharePoint environment, focusing on actionable strategies to enhance both your SaaS security posture (SSPM) and data security posture (DSPM).

A Comprehensive Guide to SharePoint Security Best Practices

1. Implementing Access Management Best Practices for SharePoint

Enforcing Least Privilege Access for Enhanced Security

Ensure users only have access to the data and resources necessary for their roles.

Monitoring Guest and External User Access to Safeguard Data

Track and limit external user access to SharePoint sites.

  • Example: Files shared with a vendor during a project should have access automatically revoked once the project is completed. Use SharePoint sharing settings to restrict external access and ensure files are not unnecessarily exposed.
  • Industry Example:  In 2024, Western Sydney University reported a cyber breach affecting around 7,500 individuals, including staff and students. The breach involved unauthorized access to email accounts and SharePoint files, leading to the exposure of sensitive information. Auditing external sharing and implementing stricter access controls could have prevented this issue.

Enforcing Multi-Factor Authentication (MFA) for Added Protection

Add an extra layer of security by enforcing MFA for all SharePoint users, especially administrators.
  • Example: Even if credentials are compromised, MFA provides an additional hurdle for attackers, ensuring better protection for your SharePoint environment.
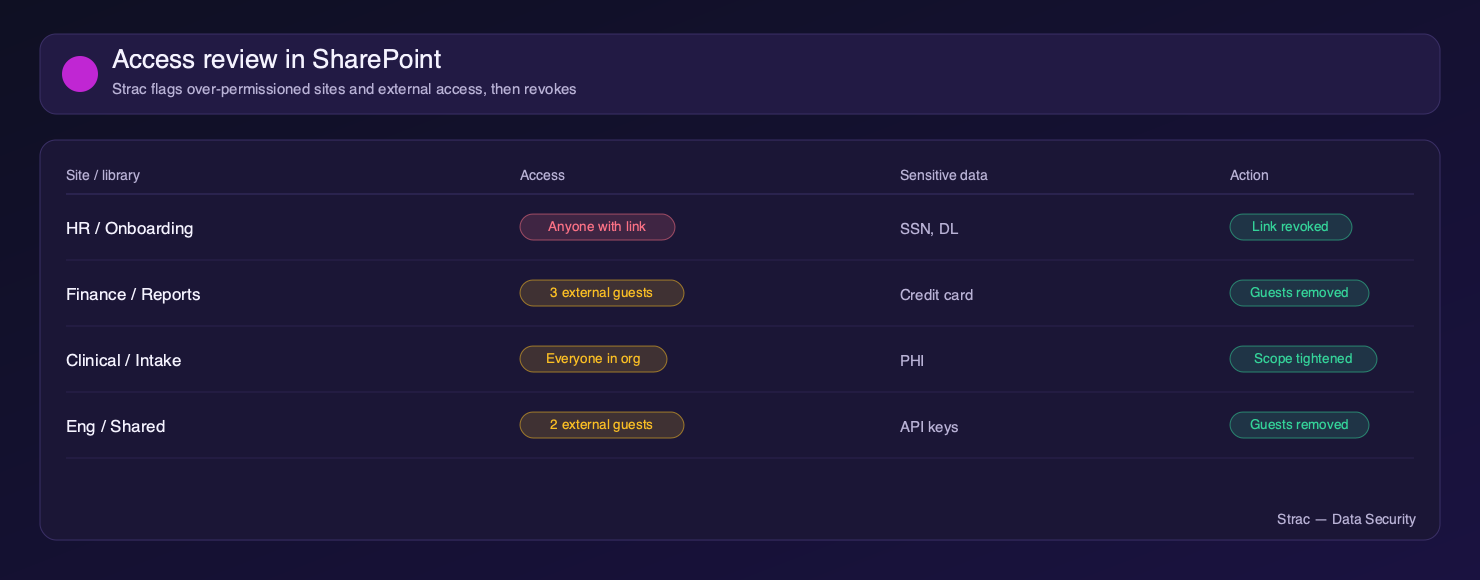
Strac access review in SharePoint: flags over-permissioned sites and external access, then revokes
Access management in action: Strac flags over-permissioned sites and external or public access to sensitive files, then revokes it.

2. Managing Misconfigurations for Improved SharePoint Security

Auditing Sharing Links and Permissions for Tightened Security Controls

Identify and remediate overly permissive sharing links, such as those granting “Anyone with the link” access.

Reviewing Site and Document Library Settings for Security Compliance

Ensure default settings on SharePoint sites align with your organization's security policies.

  • Example: Enable file versioning and disable anonymous access to prevent unauthorized changes and ensure auditability.

Monitoring Sensitive Data in Public Sites to Prevent Data Breaches

Scan public SharePoint sites for sensitive information, such as customer data or intellectual property.

  • Example: Flag and remediate cases where public sites contain confidential sales data.

3. Ensuring Compliance and Managing Risks in SharePoint

Identifying and Deactivating Dormant Sites to Mitigate Risks

Inactive SharePoint sites are an often-overlooked security risk.

  • Example: A project-specific site with no activity for over 90 days should be archived or deactivated to reduce the attack surface.
  • Industry Example: In 2022, a leading financial services firm reduced its SharePoint attack surface by identifying and deactivating 200 dormant sites after a security audit revealed potential vulnerabilities. This significantly minimized their exposure to unauthorized access. (Sour

Monitoring Third-Party Integrations for Enhanced Security Measures

Review all third-party apps integrated with SharePoint to ensure they have appropriate permissions.

  • Example: Revoke access to unused marketing apps that still have access to sensitive documents.

Conducting Configuration Compliance Audits for Regulatory Compliance

Ensure your SharePoint configurations align with compliance standards like GDPR or HIPAA.

  • Example: Verify that encryption at rest is enabled for sensitive libraries and audit logs are retained as required by regulations.

4. Enhancing Data Discovery and Classification in SharePoint

Identifying and Classifying Sensitive Data for Data Protection

Discover sensitive files stored in SharePoint libraries, such as contracts containing payment card information.

  • Example: Use sensitivity labels to classify and protect these files based on their content.
  • Industry Example: A multinational company used Microsoft Information Protection to label and secure financial documents stored in SharePoint, reducing compliance risks.

‍

Scanning Document Libraries for Unstructured Data to Enhance Security

Unstructured data, such as customer details in Excel files or scanned contracts, should be identified and flagged.

  • Example: A document library containing scanned legal agreements can be scanned for keywords to ensure compliance with company policies.

5. Monitoring Access and Sharing Activities in SharePoint

Detecting Unauthorized Sharing of Sensitive Files for Data Protection

Monitor for instances where sensitive files, such as HR records, are shared externally.
  • Example: Automatically revoke access if a file labeled as “Confidential” is shared with an external user.
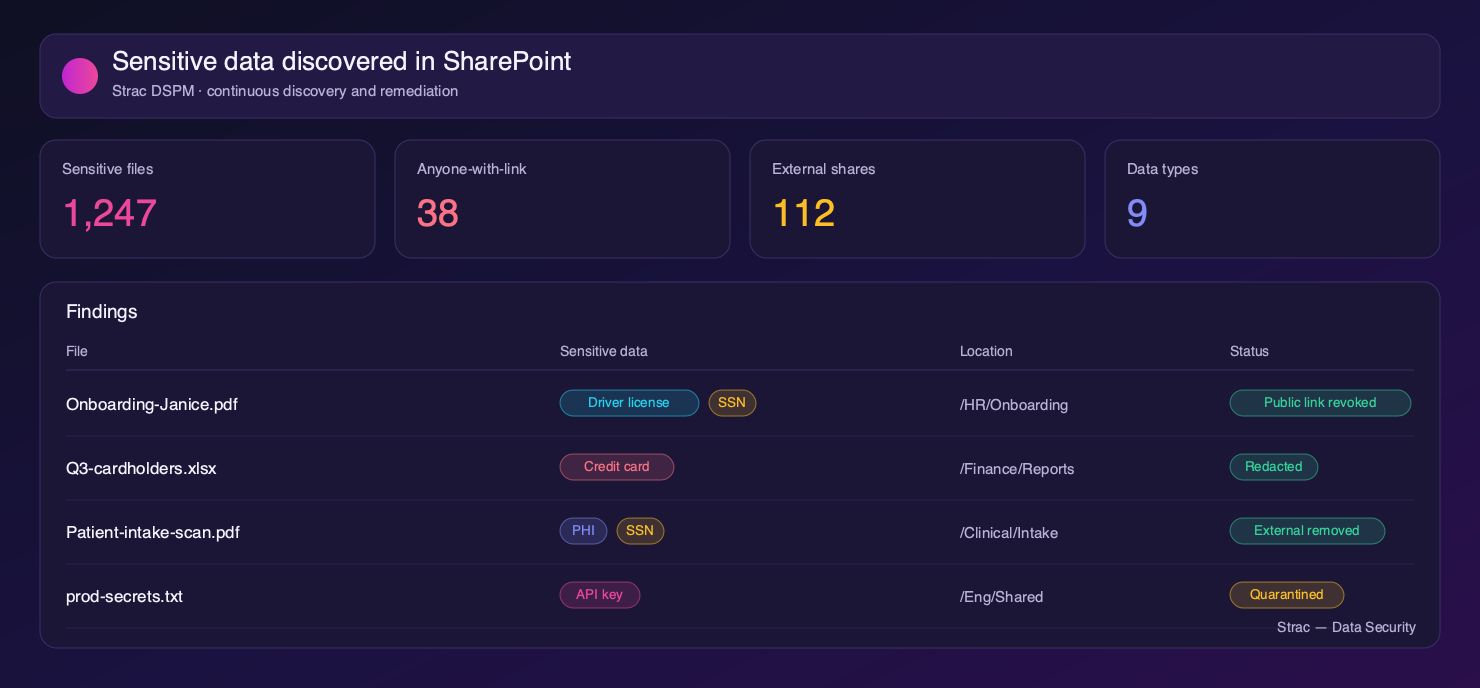
Strac discovers sensitive data in SharePoint and remediates it: revoke public links, remove external members, redact, or quarantine.

Tracking Sharing Activities in Document Libraries for Security Monitoring

Detect unusual access patterns, such as high-volume downloads of files from a document library.

  • Example: Alert admins if a user downloads an excessive number of files labeled as sensitive within a short timeframe.

6. Implementing Threat Detection Measures in SharePoint

Detecting Anomalous Download Behavior for Threat Prevention

Monitor spikes in file download activity, as they may indicate potential data exfiltration attempts.

  • Example: Trigger alerts if a user downloads hundreds of files from a sensitive site within a few minutes.
  • Industry Example: In 2023, a global energy company thwarted an insider threat where an employee attempted to exfiltrate sensitive engineering designs. This was detected through anomalous download behavior flagged by their monitoring systems.

Monitoring Privileged User Actions for Enhanced Security Measures

Track actions performed by site administrators, such as bulk permission changes or file deletions.

  • Example: Alert your security team if an admin changes access levels for a critical site outside of approved business hours.

✨ How Strac secures SharePoint across every surface

SharePoint security best practices close the configuration gaps. Strac closes the data gap: it discovers the sensitive data inside SharePoint, remediates exposure automatically, and extends the same protection to every other place that data flows, AI agents, browsers, and endpoints. One agentless platform across SaaS, cloud, GenAI, MCP, browser, and endpoint.
Strac unified data security platform protecting SharePoint across SaaS, cloud, browser, endpoint, GenAI, and MCP
One platform protecting SharePoint data everywhere it lives and moves.

1. Discover and classify sensitive data in SharePoint (DSPM)

Strac's DSPM continuously scans SharePoint for PII, PHI, PCI, and secrets using ML and OCR across 100+ data types, so you know exactly where your regulated data lives and which items are overshared, public, or out of policy. This is the layer native SharePoint controls skip: they can enforce a setting, but they cannot tell you where all your sensitive data actually sits.

Strac DSPM discovering and classifying sensitive data (PII, PHI, PCI) inside SharePoint
Strac discovers and classifies every sensitive file in SharePoint, automatically.

2. Redact and remediate exposure automatically (SaaS DLP)

Finding exposed data is table stakes. Strac's SharePoint DLP acts on it, under your policy: redact or mask sensitive values in place, revoke public "anyone with the link" sharing, remove external members from files and sites, quarantine or delete items that should not exist, and label and classify, with a full audit trail mapped to HIPAA, PCI DSS, SOC 2, ISO 27001, and GDPR. Most alternatives stop at an alert; Strac fixes the exposure.
Strac automatically remediating sensitive data exposure in SharePoint: redact, revoke public links, remove external members
Strac remediates SharePoint exposure in place, revoke public links, remove external members, redact, quarantine.

3. Govern what AI agents pull from SharePoint (MCP DLP)

AI agents now read directly from SharePoint over the Model Context Protocol. Strac's MCP DLP sits in that path as a reverse proxy and redacts sensitive values in tool responses before the model ever sees them, and governs exactly which agents can reach which SharePoint data. Connect the Microsoft 365 / SharePoint MCP connector once and every agent tool call is inspected.
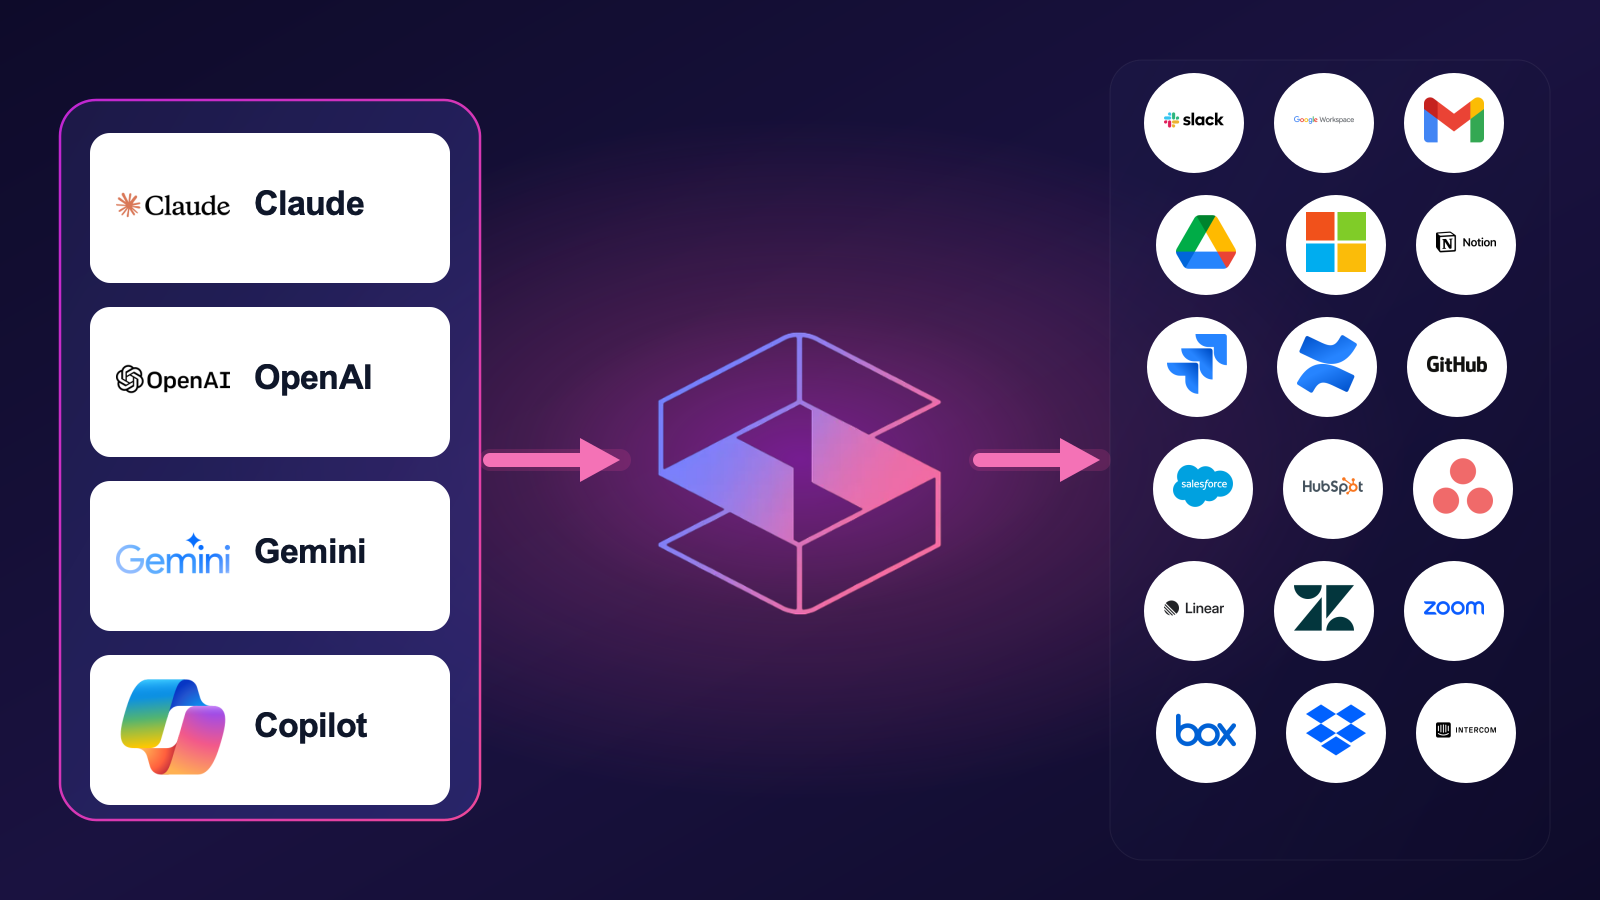
Strac MCP DLP governing AI agent access to SharePoint data, redacting sensitive values at the boundary
Strac governs the MCP boundary so AI agents can use SharePoint without exfiltrating sensitive data.

4. Stop SharePoint data leaks in the browser

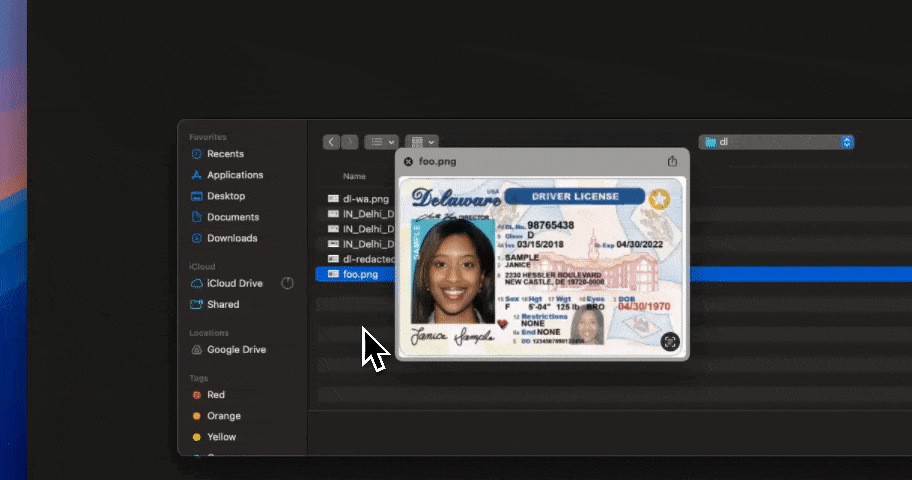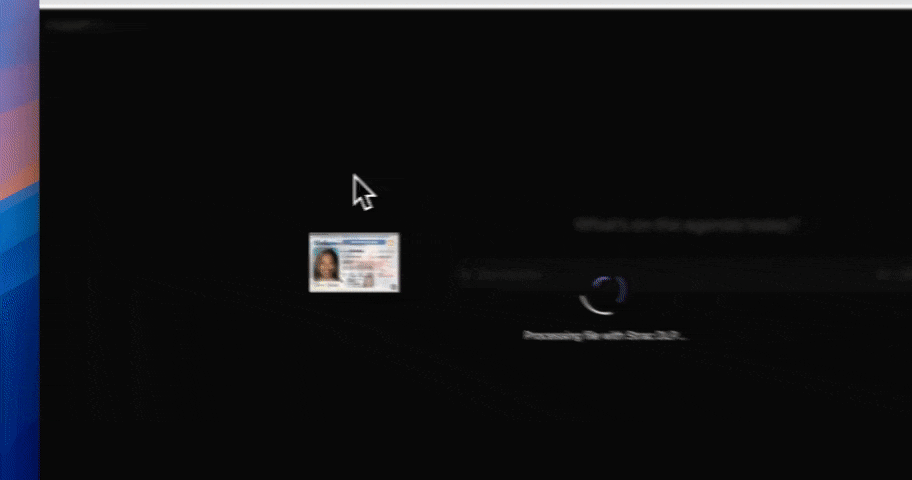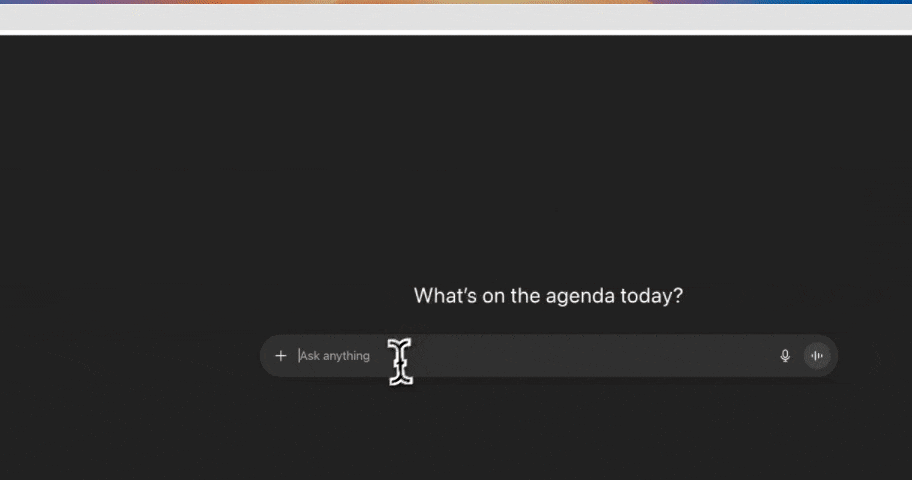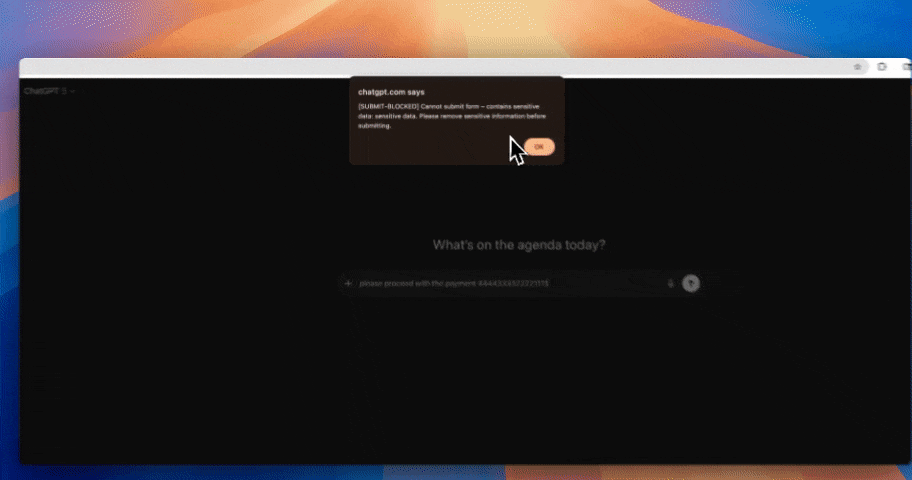
Strac's browser DLP extension for Chrome, Edge, Firefox, and Safari blocks or redacts sensitive uploads, downloads, and pastes to and from SharePoint in real time, including data a user tries to move from SharePoint into an AI tool in another tab.
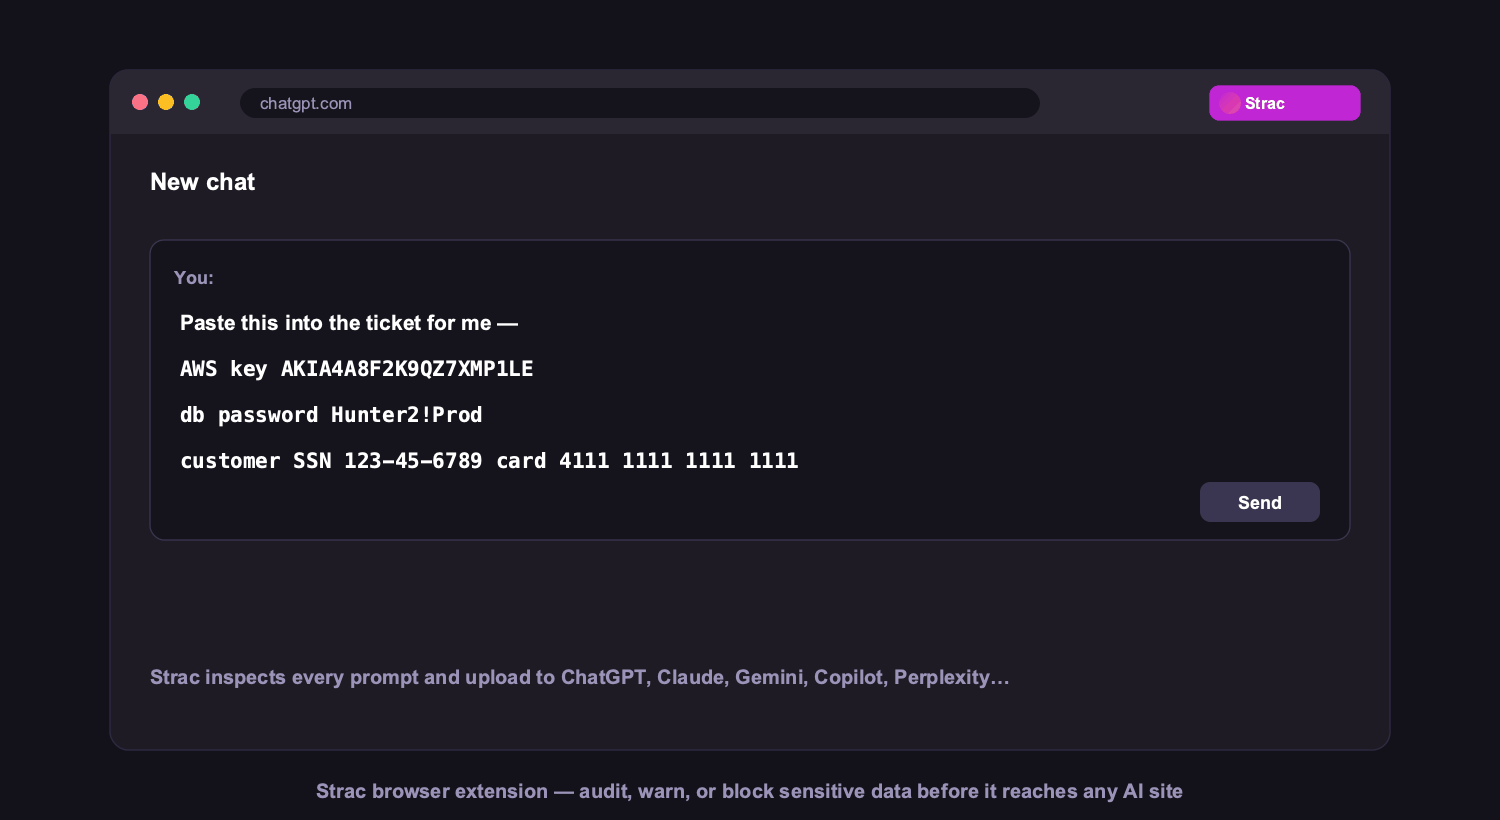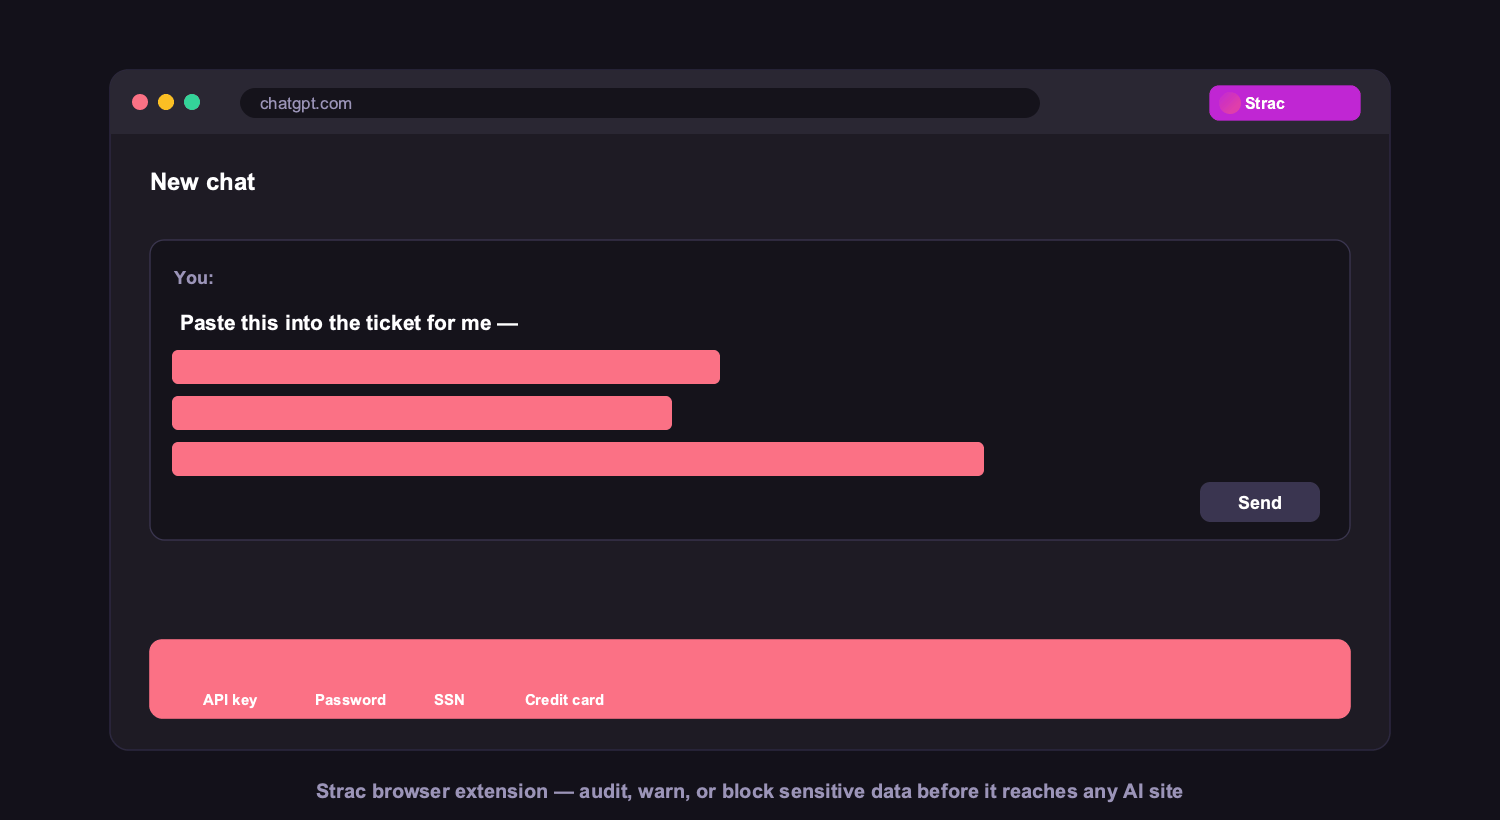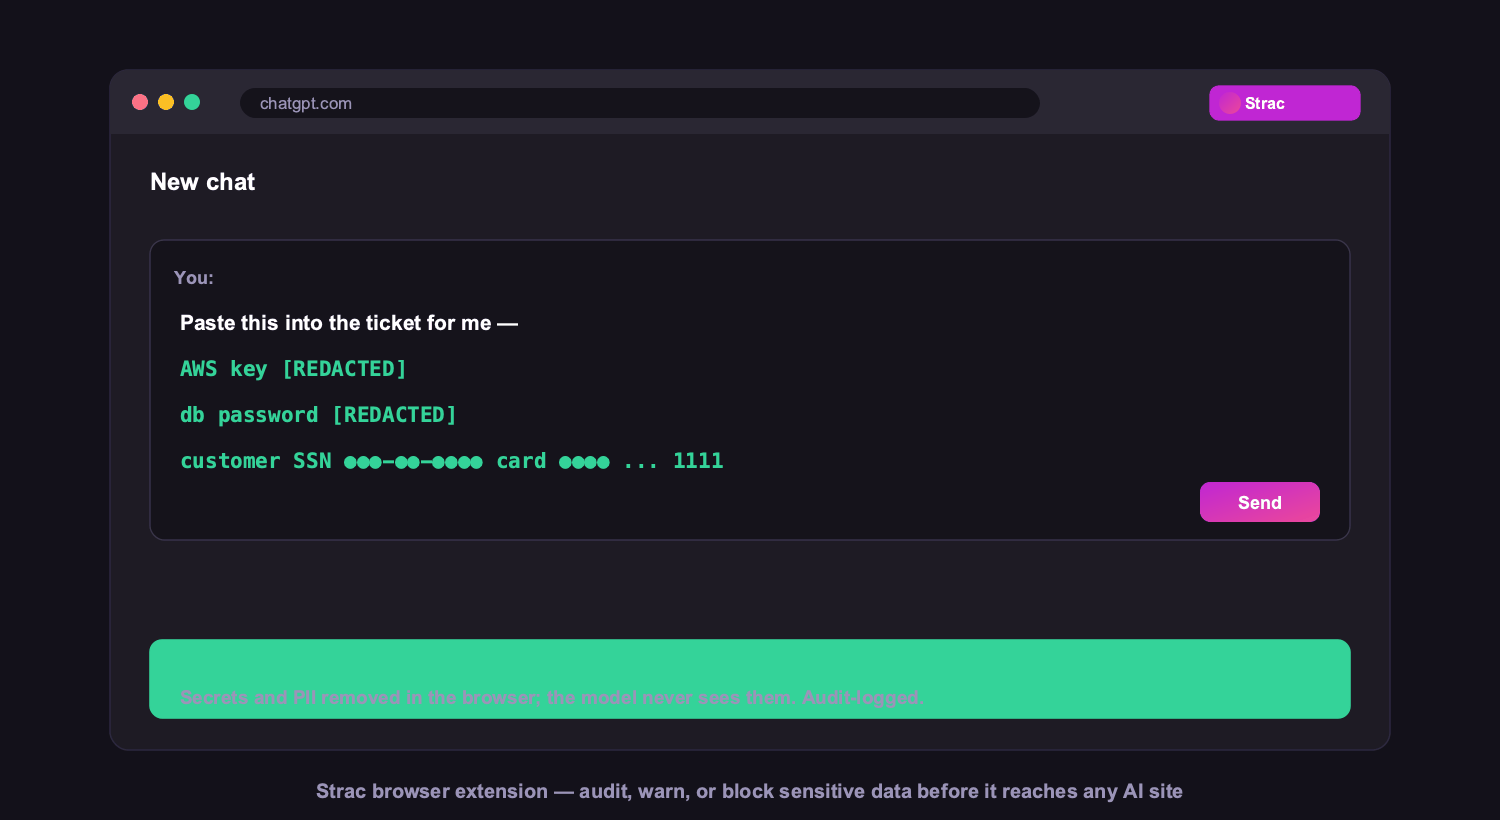
Strac browser DLP blocking a sensitive SharePoint upload in real time
Browser DLP blocks or redacts sensitive SharePoint data in the browser, live.

5. Control SharePoint data on endpoints (Mac and Windows)

Strac's endpoint DLP agent controls SharePoint data as it lands on laptops, with four modes: block, warn, allow, and audit across file downloads, copies, and screenshots on both Mac and Windows.
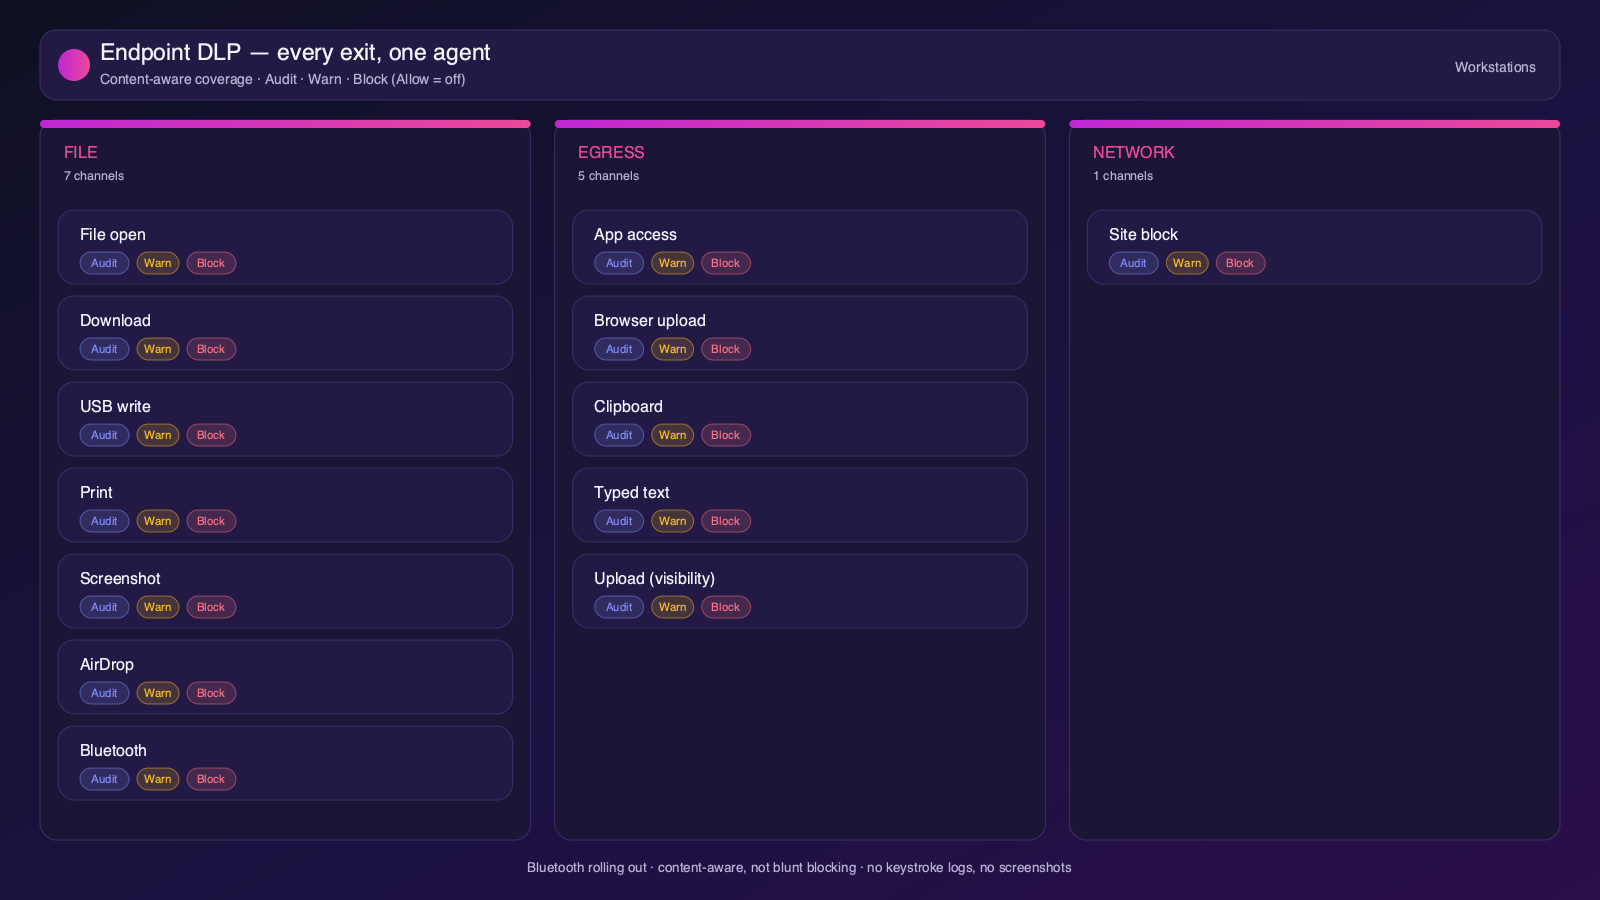
Strac endpoint DLP controlling SharePoint data on Mac and Windows with block, warn, allow, and audit modes
Content-aware endpoint DLP: block, warn, allow, or audit on Mac and Windows.

6. One platform, every surface

SharePoint is one of 50+ places Strac protects. The same engine covers SaaS, cloud, GenAI, MCP, browser, and endpoint, so your SharePoint data stays protected everywhere it flows, not just at rest. That breadth, plus remediation that actually fixes exposure, is why teams consolidate on Strac instead of stacking point tools.

Strac integrations across 50+ SaaS, cloud, endpoint, browser, and AI connectors
50+ integrations across SaaS, cloud, databases, endpoints, browsers, and AI.

Conclusion

Implementing these SharePoint security best practices ensures a well-protected and compliant collaboration environment. By addressing access controls, managing configurations, and proactively monitoring for threats, organizations can minimize risks and safeguard sensitive data.

Are you ready to strengthen your SharePoint security? Strac makes it practical: it discovers the sensitive data inside SharePoint, remediates exposure automatically, and extends the same protection to your browsers, endpoints, and AI agents. Book a demo to see Strac secure your SharePoint data in minutes.

‍

🌶️ Frequently asked: SharePoint security

Is SharePoint secure?

SharePoint is secure when configured correctly, but its defaults are permissive: public link sharing, broad external access, and no built-in data discovery or DLP. Most SharePoint data exposure comes from misconfiguration and oversharing, not a platform flaw. Hardening the configuration and adding DSPM plus DLP (like Strac) to discover and remediate sensitive data closes the gap.

Is SharePoint secure for confidential information?

It can be, with least-privilege access, tight external-sharing controls, encryption, and continuous data discovery. The risk is confidential files sitting in sites shared publicly or with external guests. Strac continuously scans SharePoint for PII, PHI, PCI, and secrets, flags overshared or public confidential files, and automatically revokes public links, removes external members, or redacts the data.

Does SharePoint have DLP?

Microsoft Purview provides DLP for Microsoft 365 including SharePoint, but it is complex to configure and limited on automatic remediation. Strac adds agentless discovery, in-place redaction and masking, automatic revocation of public links and external members, and the same protection beyond SharePoint, across browsers, endpoints, and AI agents.

What are the most important SharePoint security best practices?

Enforce least-privilege access and MFA, audit and restrict external and "anyone with the link" sharing, review site and library settings, deactivate dormant sites, continuously discover and classify sensitive data, monitor access and download activity, and remediate exposure automatically. The sections above cover each in detail.

How does Strac secure SharePoint?

Strac connects to SharePoint agentlessly and runs DSPM discovery across every site and library, then remediates exposure (redact, mask, revoke public access, remove external members, quarantine, label). It extends the same protection to AI agents via MCP DLP, to the browser, and to Mac and Windows endpoints.

Support

Please contact hello@strac.io for any questions