Discord DLP: Detect & Block Sensitive Data in Discord (2026)
Data Loss Prevention for Discord. Detect PII, card numbers, passwords, and secrets shared in channels, DMs, and attachments, and block them before they send with browser and endpoint DLP.
Discord started as a gaming app and quietly became a workplace: dev teams, communities, and support run on it. That means cards, passwords, API keys, and customer data now flow through Discord channels, DMs, and file uploads, with zero native DLP. Strac detects sensitive data in Discord messages and attachments and blocks it before it sends, using browser and endpoint DLP that covers both the web app and the desktop client.
Discord DLP: Detect & Block Sensitive Data in Discord (2026)
Discord is no longer just for gaming. Startups run their engineering in it, communities support customers through it, and vendors coordinate in shared servers. The moment real work moves to Discord, so does real sensitive data: a card number in a #billing channel, a database password in a DM, a customer export dropped as an attachment. Discord has no Data Loss Prevention to catch any of it.
This guide covers DLP for Discord and how Strac detects and blocks sensitive data before it leaves.
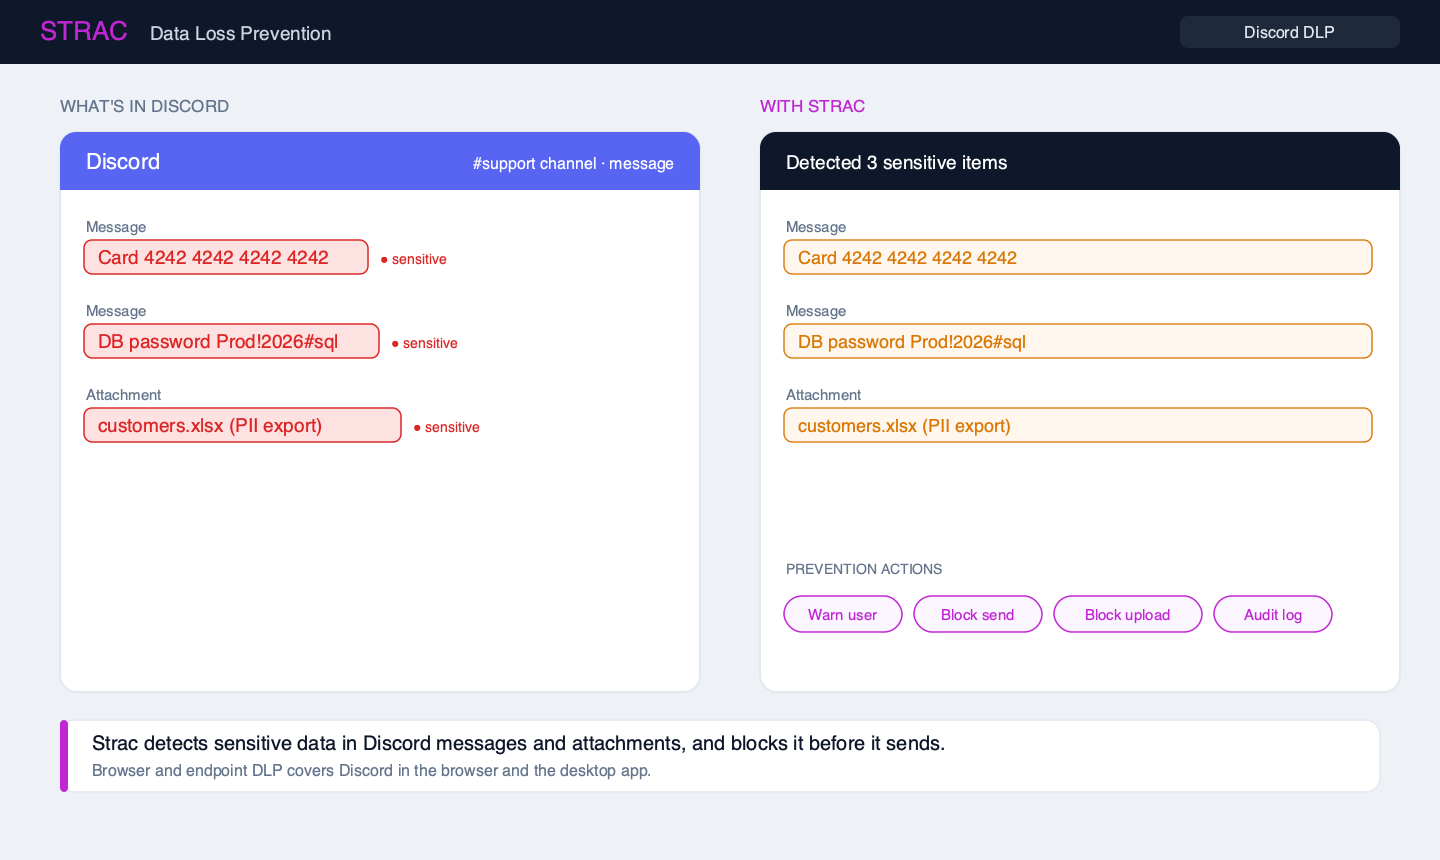
✨ Strac Discord DLP in action
Discord runs in the browser and as a desktop app, and Strac inspects content at the point of use, blocking or warning before a sensitive message or file is sent.
💬 What sensitive data flows through Discord
Payment data — card numbers and billing details pasted into support and sales channels.
Secrets — API keys, tokens, and database passwords shared in dev channels and DMs to unblock a teammate.
Customer PII — names, emails, and account details discussed in support threads.
Attachments — CSVs, screenshots, and logs uploaded to channels, often full of regulated data.
🚧 How Strac protects Discord: detect and block at the source
Discord is a browser-and-desktop app, so Strac prevents leaks at the point of entry rather than trying to claw messages back after the fact. Strac's browser DLP and endpoint DLP:
Detect PII, card numbers, and secrets in messages, and in attachments via content inspection and OCR.
Warn or block the message send and the file upload in real time.
Cover the desktop client as well as Discord in the browser.
Audit every detection so you have evidence for security reviews.
🔀 Discord vs Slack vs Teams
The risk is the same across chat tools, only the logo changes. If your teams also use Slack or Microsoft Teams, Strac covers those too, from one console, so your chat DLP policy is consistent no matter where a conversation happens.
🕵️ Discord and shadow IT
Because Discord is adopted informally, it is a textbook shadow IT risk: it rarely appears in the security team's DLP scope, yet it carries production secrets and customer data daily. Strac gives you visibility into what sensitive data is flowing through Discord and the control to stop it.
📋 Discord and compliance
PCI DSS 4.0 — a single card number in a channel can drag your environment into scope; blocking it at send is scope reduction.
Secrets hygiene — leaked API keys and passwords are among the most common breach roots; Strac flags and blocks them.
GDPR / CCPA — customer PII shared in chat is regulated data in an unmanaged place.
🌶️ Spicy FAQs on Discord DLP
Does Discord have built-in DLP?
No. Discord provides moderation and permission tools, but nothing that classifies content or stops PII, card numbers, or secrets from being posted. A dedicated tool like Strac is required to detect and block sensitive data.
How does Strac stop a sensitive Discord message if it can't delete messages?
Strac blocks at the point of entry. Its browser and endpoint DLP detect the sensitive content as it is typed or uploaded and can warn or block the send in real time, so the message or file never leaves. This prevention model fits chat tools better than after-the-fact deletion.
Does it work on the Discord desktop app?
Yes. Strac's endpoint DLP covers the desktop client and its browser DLP covers Discord in the browser, so both are protected.
Can it catch sensitive data inside an uploaded file or screenshot?
Yes. Strac inspects attachments and runs OCR on images, so a customer export or a screenshot full of PII is detected before it uploads.
We use Discord and Slack. Do we need two tools?
No. Strac covers Discord, Slack, Teams, and any other web app from one console, so your policy is consistent. See our best DLP solutions roundup for the full picture.
Does Discord have built-in DLP?
No. Discord provides moderation and permission tools, but nothing that classifies content or stops PII, card numbers, or secrets from being posted. A dedicated tool like Strac is required to detect and block sensitive data.
How does Strac stop a sensitive Discord message if it can't delete messages?
Strac blocks at the point of entry. Its browser and endpoint DLP detect the sensitive content as it is typed or uploaded and can warn or block the send in real time, so the message or file never leaves. This prevention model fits chat tools better than after-the-fact deletion.
Does it work on the Discord desktop app?
Yes. Strac's endpoint DLP covers the desktop client and its browser DLP covers Discord in the browser, so both are protected.
Can it catch sensitive data inside an uploaded file or screenshot?
Yes. Strac inspects attachments and runs OCR on images, so a customer export or a screenshot full of PII is detected before it uploads.
We use Discord and Slack. Do we need two tools?
No. Strac covers Discord, Slack, Teams, and any other web app from one console, so your policy is consistent. See our best DLP solutions roundup for the full picture.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.