September 25, 2026

7
min read
How Data Loss Prevention Apps are Evolving
Discover the essentials of a Data Loss Prevention App. Learn its importance, key features, and how Strac can help secure your data with advanced DLP solutions.
· A Data Loss Prevention (DLP) app in 2026 mustprotect sensitive data across SaaS, cloud, endpoints, browsers, GenAI tools,and AI agent workflows; traditional email and network monitoring is no longerenough.
· Modern DLP combines continuous data discoveryand classification with real-time enforcement to protect PII, PHI, PCI,credentials, source code, intellectual property, and other confidential data.
· Effective DLP should act on risk, not simplygenerate alerts. Depending on the policy, organizations should be able toblock, warn, redact, mask, quarantine, revoke access, or audit sensitive-dataactivity.
· AI has created new data-loss paths throughChatGPT, Claude, Gemini, Copilot, Shadow AI, and Model Context Protocol (MCP)connections, making GenAI and MCP DLP increasingly important.
· Straccombines DLP and Data Security Posture Management (DSPM) to discover, classify,monitor, and remediate sensitive data across SaaS, Cloud, GenAI, Browser,Endpoint, and MCP environments.
A Data Loss Prevention (DLP) app is security software designed to discover sensitive data, understand where it is located and how it moves, and prevent it from being exposed to unauthorized users, applications, devices, or AI systems.
The definition of a DLP app has expanded significantly in 2026. Sensitive data no longer moves primarily through corporate email and networks. Employees work across SaaS platforms, cloud storage, browsers, endpoints, collaboration tools, GenAI applications, and increasingly AI agents connected directly to enterprise systems.
Modern DLP therefore needs to follow the data across the entire workflow.
Sensitive data can include personally identifiable information (PII), protected health information (PHI), payment card information (PCI), financial records, API keys, credentials, source code, customer information, intellectual property, and organization-specific confidential data.
Rather than simply detecting a potential violation after it happens, modern DLP can intervene while the activity is occurring; for example, blocking an upload, redacting sensitive information, warning the employee, revoking access, or creating an audit trail.
Financial institutions: Banks, fintech companies, and payment providers use DLP to protect account information, payment data, customer PII, financial documents, and credentials as information moves across SaaS applications, endpoints, cloud environments, and AI tools.
Healthcare organizations: Healthcare organizations use DLP to discover and protect PHI across applications, files, support systems, cloud storage, endpoints, and AI workflows. This is particularly important when employees or AI agents can move patient information between systems.
Technology companies: SaaS and technology organizations need to protect much more than PII. Source code, API keys, credentials, customer records, product roadmaps, proprietary algorithms, and internal documents can all become targets for accidental or intentional exfiltration.
Sensitive data can leave an organization through far more channels than email. Employees can upload files to personal cloud accounts, copy information to USB devices, paste source code into AI assistants, move customer information through SaaS apps, or expose data through browser-based tools.
A modern DLP app identifies sensitive information and applies policies at the point where the risky activity occurs.
Example: An employee attempts to upload a spreadsheet containing customer information to a personal cloud-storage account. Instead of discovering the incident later through logs, DLP can identify the sensitive content and block or warn on the upload in real time.
Organizations handling regulated information must maintain appropriate controls around how that information is stored, accessed, shared, and transferred.
DLP can support compliance programs for frameworks and regulations such as GDPR, HIPAA, PCI DSS, SOC 2, ISO 27001, CCPA/CPRA, and NIST by discovering sensitive information, enforcing protection policies, and creating evidence of how data is handled.
Example: A healthcare organization can identify PHI appearing inside SaaS applications or AI prompts and automatically apply policies to prevent unauthorized exposure.
Not every data leak is malicious. Employees routinely move information between applications to complete everyday work; a single incorrect recipient, personal account, USB drive, or AI prompt can create exposure.
Modern DLP provides contextual controls such as warn, block, redact, or audit so organizations do not have to choose between productivity and security.
Example: A developer attempts to paste proprietary source code into an unsanctioned GenAI tool. DLP can detect the sensitive code before submission and enforce the organization's policy.
GenAI has become one of the biggest changes to the DLP threat model. Employees can paste sensitive information directly into ChatGPT, Claude, Gemini, Copilot, and other AI tools; they can also upload complete documents, screenshots, datasets, or source code.
Traditional DLP tools were not designed for these interactions.
Modern GenAI DLP needs visibility into prompts, pasted text, file uploads, and AI usage so security teams can discover Shadow AI and enforce different policies based on the sensitivity of the information.
AI agents introduce another layer of risk because employees no longer need to manually copy data into an AI model.
Through Model Context Protocol (MCP), an AI agent can connect directly to systems such as Slack, Google Drive, Microsoft 365, Salesforce, Jira, Confluence, GitHub, Zendesk, and other enterprise applications.
That means sensitive information can move from enterprise systems into an AI model's context through tool calls.
MCP DLP provides a control point between the agent and the connected system; sensitive information can be detected and remediated before it reaches the model.

Modern DLP starts with understanding the data itself.
Organizations need to continuously discover and classify PII, PHI, PCI, credentials, secrets, source code, intellectual property, financial information, and custom confidential data wherever it exists.
Detection also needs to go beyond plain text. Sensitive information can appear inside PDFs, Word documents, spreadsheets, screenshots, images, archives, and other file formats.
Custom detectors are equally important because every organization has information that generic compliance templates cannot recognize; such as internal identifiers, customer IDs, project names, proprietary formats, or confidential business data.
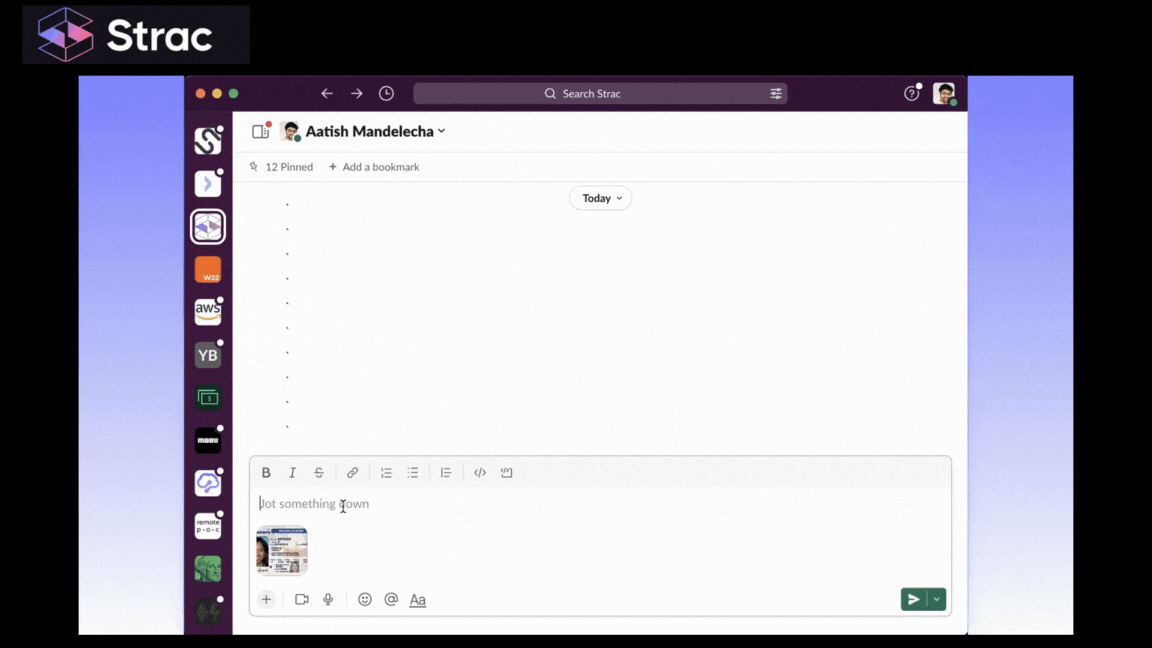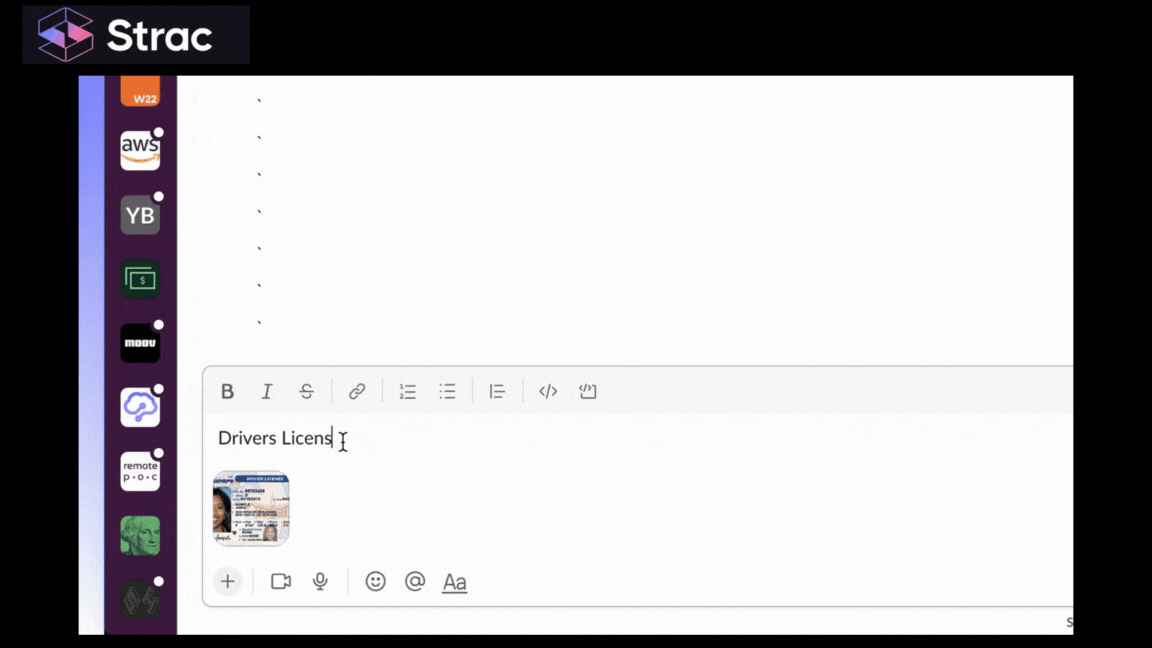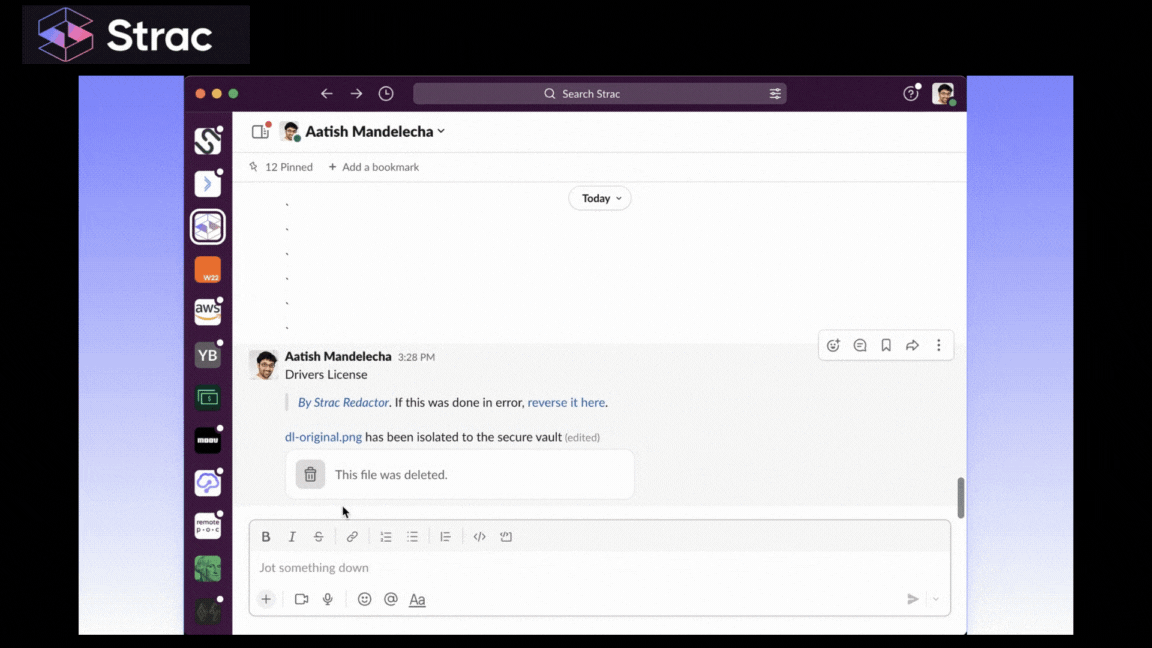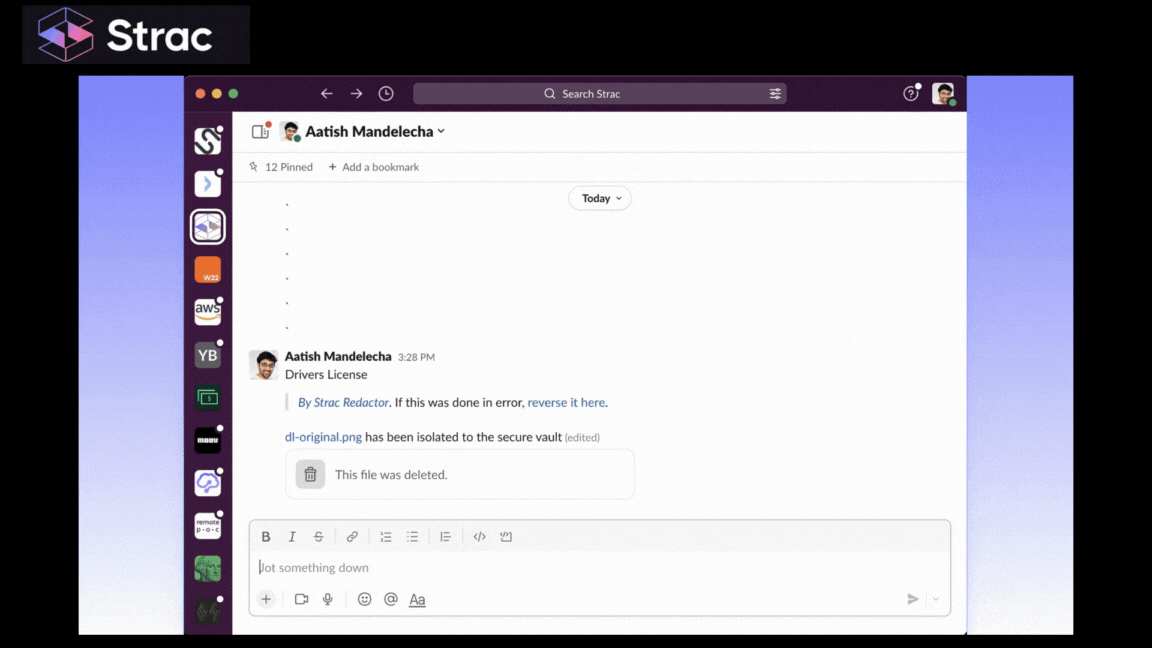
Alert-only DLP creates another security queue.
Modern DLP should be capable of taking action when sensitive data is discovered. Depending on the data type, destination, user, and organizational policy, this can include blocking, warning, redacting, masking, quarantining, revoking access, deleting exposed data, or auditing the event.
The goal is not simply to tell security teams that a leak occurred. It is to prevent or reduce the exposure while allowing legitimate work to continue whenever possible.
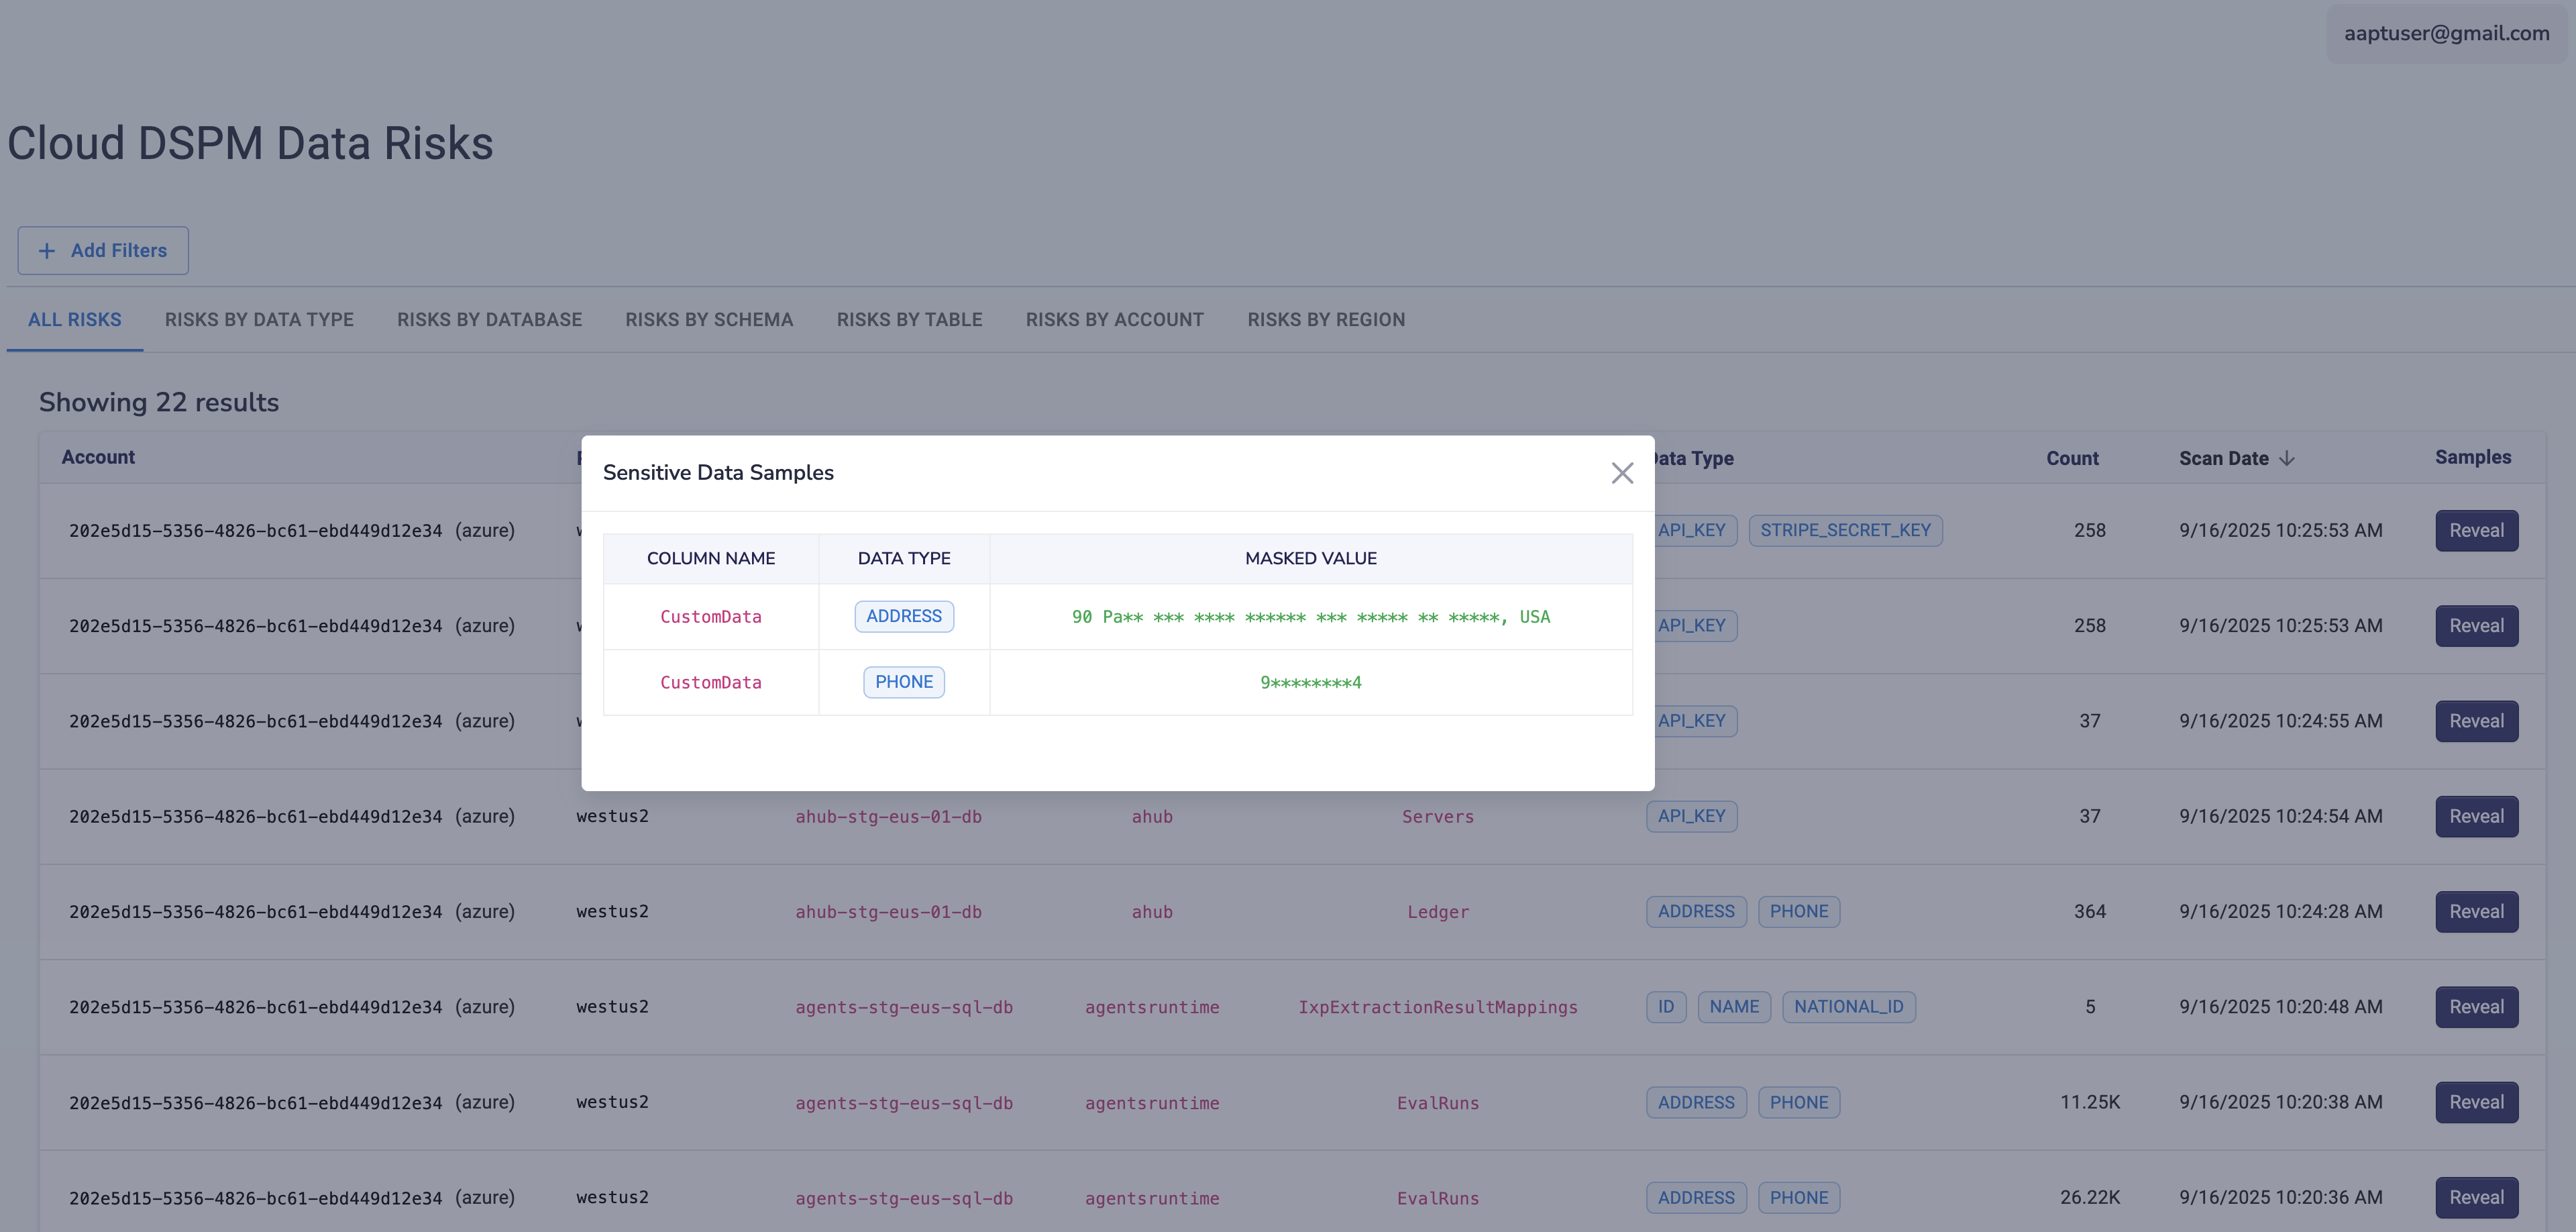
Sensitive information now lives throughout the SaaS stack.
A DLP app should discover and protect data across collaboration platforms, support systems, productivity tools, cloud storage, CRM applications, and cloud infrastructure.
This requires integrations that can inspect existing data as well as monitor new activity, giving security teams visibility into both data at rest and data in motion.

Endpoints remain a major exfiltration point, but endpoint security cannot stop at monitoring files stored on a laptop.
Modern Endpoint DLP needs visibility into how corporate information moves through Windows and macOS devices, browsers, desktop applications, USB storage, uploads, copy-paste workflows, SaaS applications, and GenAI tools.
Browser-level enforcement is particularly important because many modern data transfers happen directly through web applications rather than traditional corporate networks.
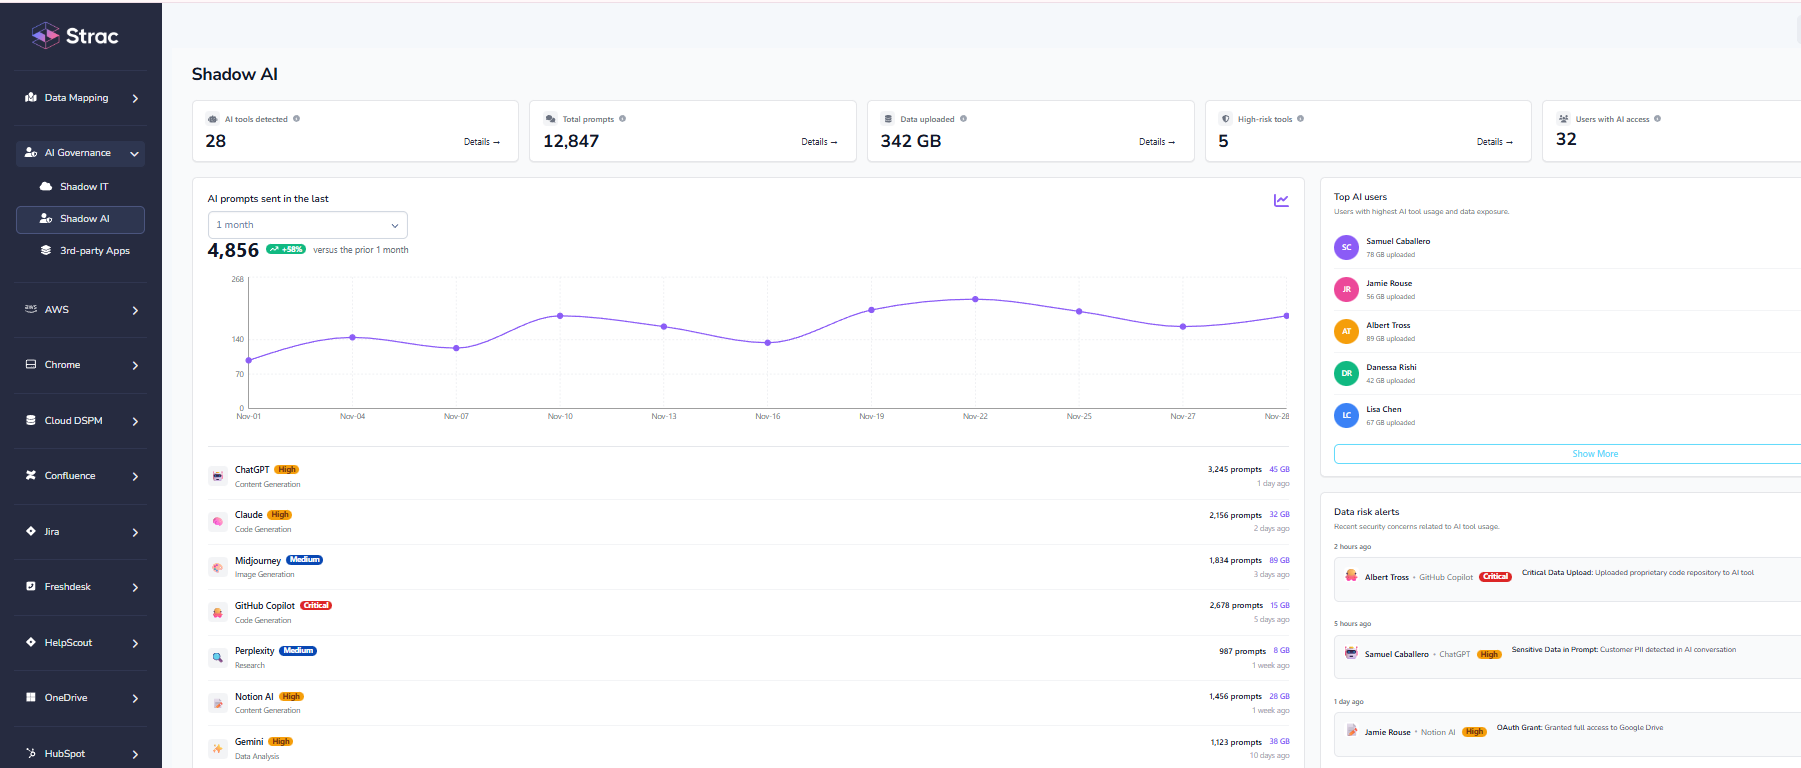
DLP in 2026 must understand AI as its own data channel.
Organizations need visibility into employees using ChatGPT, Claude, Gemini, Copilot, and other AI tools, including what sensitive information is being submitted.
Policies should allow organizations to audit AI activity, warn users, request justification, redact sensitive information, or block risky submissions depending on the situation.
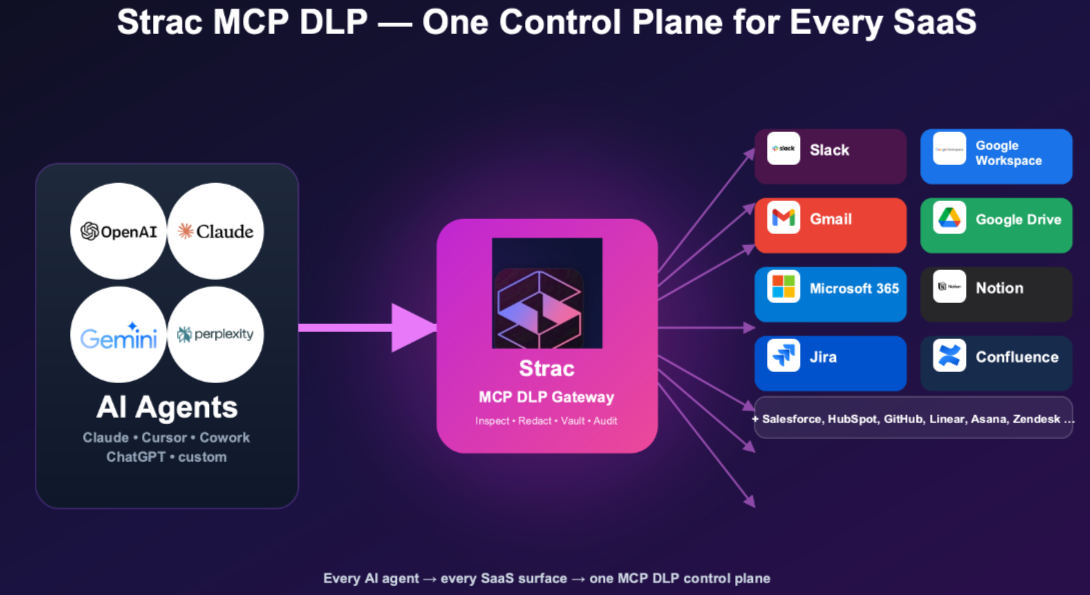
As AI agents gain access to enterprise systems, DLP must extend to machine-to-machine data flows.
MCP DLP can inspect tool calls and responses between AI agents and connected enterprise systems, identify sensitive information, and enforce policy before that information becomes part of the model context.
This is increasingly important because an AI agent can retrieve sensitive information automatically; there may be no employee manually copying or uploading the data for traditional DLP controls to intercept.
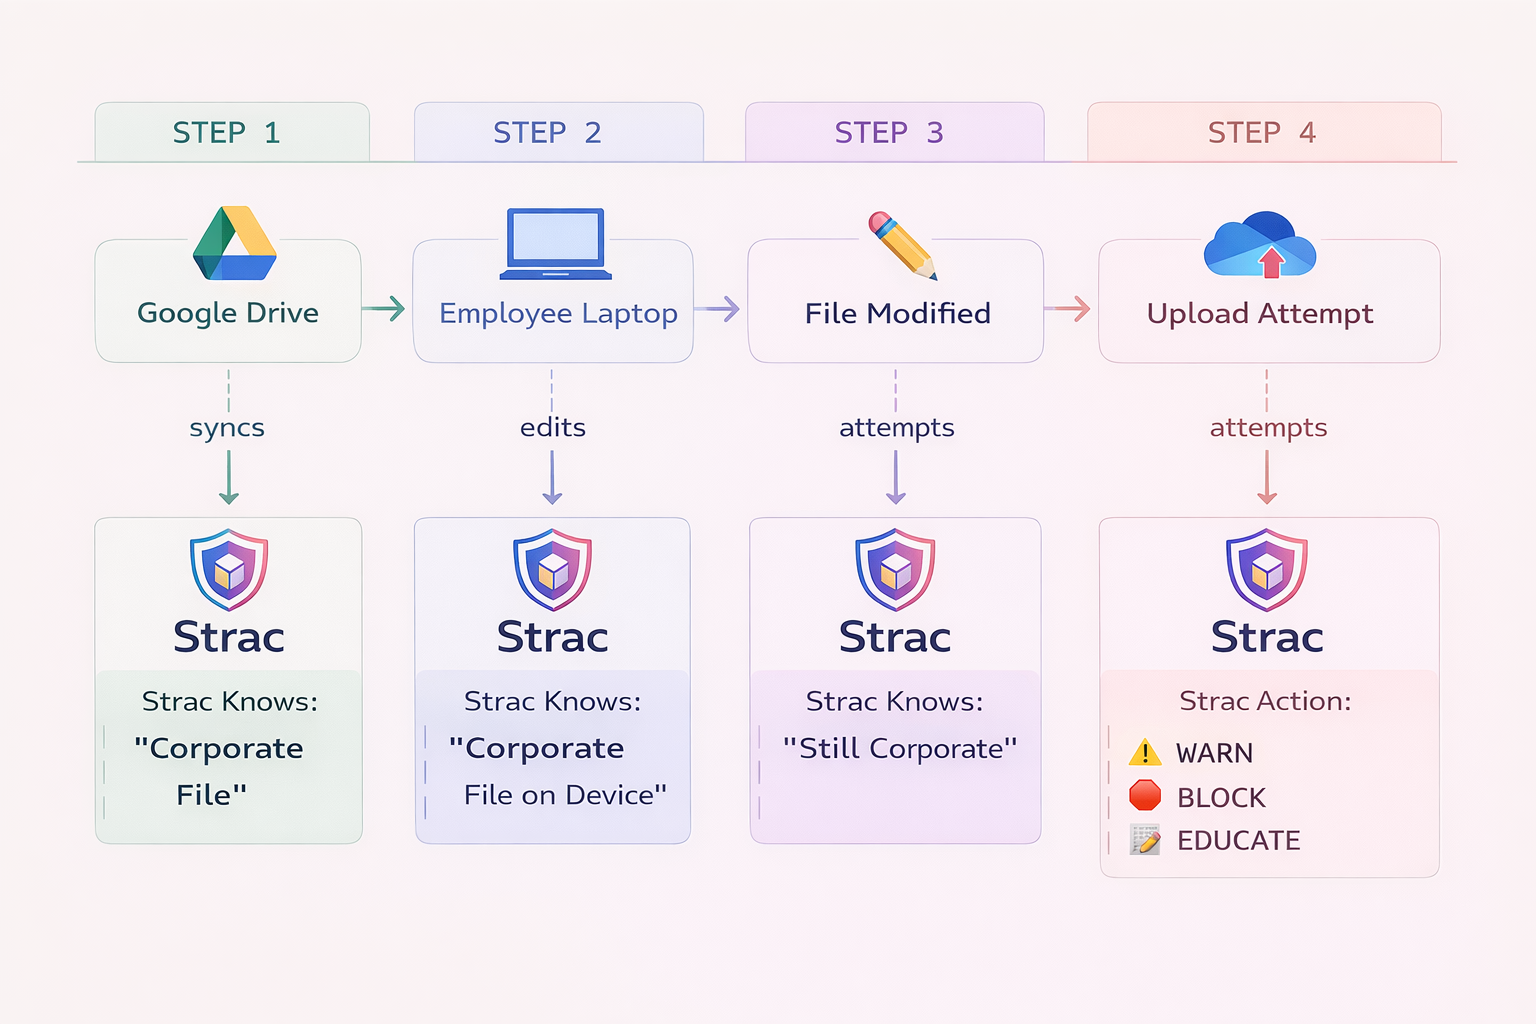
Content classification alone does not always tell the full story.
Organizations increasingly need to understand where a file originated and where it moves. Persistent data lineage can identify corporate files downloaded from systems such as Box, Google Drive, OneDrive, and SharePoint and continue tracking them even if employees rename, edit, or copy the files locally.
This enables DLP policies based not only on what a file contains, but also where that file came from.
Modern data protection increasingly combines Data Security Posture Management (DSPM) with DLP.
DSPM answers questions such as: Where does sensitive data live? Who has access? Where is it overexposed?
DLP answers the next question: What should happen when that sensitive data is accessed, shared, uploaded, or moved somewhere risky?
Combining the two gives organizations both visibility and enforcement rather than forcing security teams to operate separate discovery and protection systems.
Strac has evolved beyond traditional DLP into a unified DSPM and DLP platform designed around how enterprise data actually moves in 2026.
Strac discovers, classifies, monitors, and protects sensitive information across SaaS, Cloud, GenAI, Browser, Endpoint, and MCP environments. Instead of stopping at visibility and alerts, policies can be used to remediate sensitive-data exposure directly inside the workflow.
MAke it bulet points
Built-In and Custom Sensitive Data Detection
Unified DSPM + DLP
SaaS and Cloud DLP
GenAI and Shadow AI DLP
MCP DLP for AI Agents
Endpoint DLP
Endpoint Data Lineage
Real-Time Detection and Remediation
Compliance
APIs for Developer Workflows
Flexible Deployment and Policy Controls
A Data Loss Prevention App in 2026 cannot stop at scanning email, monitoring endpoints, and generating alerts. Sensitive data now moves continuously across SaaS, cloud, browsers, employee devices, GenAI applications, and AI agents connected to enterprise systems through MCP.
Modern DLP therefore needs to answer three questions: Where is sensitive data? Where is it going? What should happen before it becomes exposed?
Strac addresses those questions by combining DSPM with real-time DLP across SaaS, Cloud, GenAI, Browser, Endpoint, and MCP environments; giving organizations one data-centric layer for discovering sensitive information and protecting it wherever humans or AI systems use it.
Traditional DLP is not dead, but traditional DLP alone is no longer enough. Sensitive data now moves through SaaS apps, browsers, endpoints, GenAI tools, and AI agents, not just email and corporate networks. Modern DLP needs to follow the data across these channels and enforce policies in real time rather than simply generating alerts after something goes wrong.
Yes, if the DLP solution has GenAI and browser-level enforcement. Modern DLP can inspect prompts, pasted content, and file uploads to tools such as ChatGPT, Claude, Gemini, and Copilot; then warn, audit, redact, or block sensitive data before it is submitted. This is particularly important for controlling Shadow AI without completely banning employee AI usage.
Because with MCP, employees do not necessarily need to copy and paste sensitive information into an AI tool. AI agents can retrieve enterprise data directly from connected systems. MCP DLP provides a security layer around these interactions by inspecting tool calls and responses for PII, PHI, PCI, credentials, secrets, source code, and other confidential information before it reaches the model.
Usually, no. Overly aggressive DLP creates false positives, frustrated employees, and endless workarounds. Modern DLP should apply controls based on context; one activity might be blocked, another redacted, another trigger a warning, and a low-risk event might simply be audited. Good DLP protects data without making legitimate work impossible.
DSPM tells you where sensitive data is and where it is exposed; DLP controls what happens when someone or something tries to move or use it. Combining the two closes the gap between discovering risk and actually fixing it. Platforms like Strac bring discovery, classification, monitoring, and enforcement together across SaaS, Cloud, GenAI, Browser, Endpoint, and MCP environments.