






TL;DR: Strac ServiceNow DLP in a nutshell
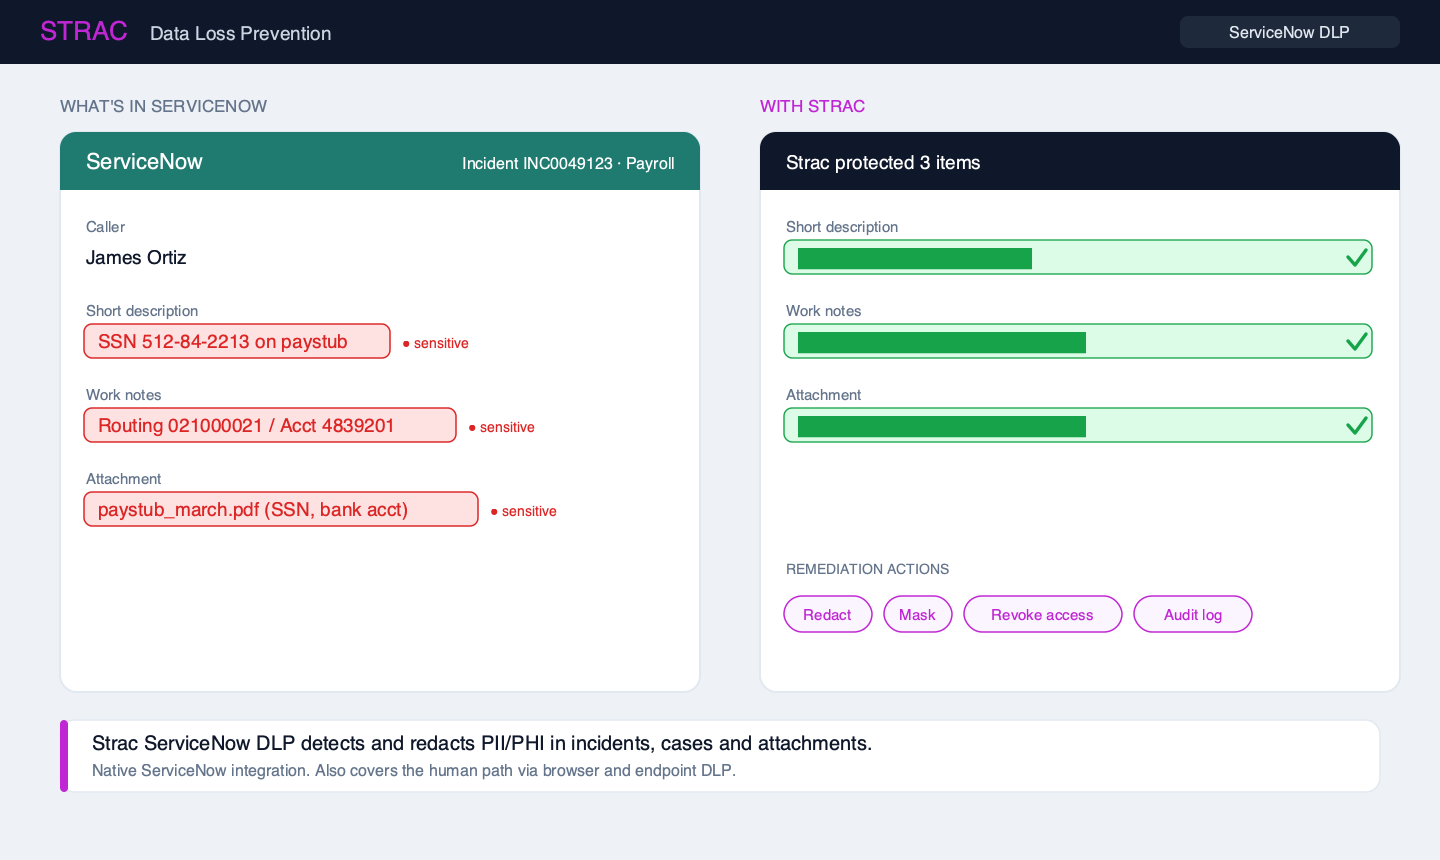
ServiceNow incidents, cases, HR tickets, and their attachments are full of regulated data: SSNs in a payroll incident, card numbers in a billing case, patient details in an HR request. Strac connects natively to ServiceNow, detects PII, PHI, and PCI across short descriptions, work notes, comments, and file attachments, and redacts or masks the sensitive values in place, while keeping the ticket usable. Every action is logged for your auditors.
What sensitive data hides in ServiceNow
- PII - SSNs, dates of birth, and home addresses in HR and payroll tickets.
- PHI - member IDs, diagnoses, and intake documents in employee health requests.
- PCI - card numbers and bank details pasted into billing and finance cases.
- Attachments - PDFs, spreadsheets, and screenshots where the real sensitive payload usually lives.
How Strac protects ServiceNow: detect, redact, revoke, prove
Strac runs four jobs against your ServiceNow instance:
- Detect sensitive data in incident/case fields, work notes, comments, and attachments (including images via OCR).
- Redact or mask the sensitive value in place and store the original in an encrypted vault for authorized retrieval.
- Revoke access and restrict who can view a record that still contains regulated data.
- Prove it with a full audit log of every detection and access event.
The 2026 risk: Now Assist and MCP
ServiceNow's Now Assist and MCP-connected AI agents can read across tickets to answer a prompt, which turns an over-shared instance into an AI data-leak surface. Strac redacts sensitive data at the source so what an assistant retrieves is already clean. See how we govern the agent path in our ServiceNow MCP and AI DLP guides.
Covering the human path: browser and endpoint DLP
Sensitive data does not only sit inside ServiceNow, it gets pasted in, uploaded as an attachment, and downloaded to laptops. Strac's browser DLP and endpoint DLP detect and block sensitive data at the point of paste, upload, and download, so you close the human path as well as the API path.
Compliance
ServiceNow data is in scope for HIPAA, PCI DSS 4.0, GDPR, and SOC 2. Strac's redaction plus access logging gives you the technical safeguard and the evidence. Read the full playbook in our ServiceNow DLP guide, and compare tools in our best DLP solutions roundup.
Agentless setup
Strac connects to ServiceNow via a native, agentless integration. You choose which sensitive data elements to detect and the action per type (redact, mask, revoke, or audit-only). Most teams are live the same day.


