October 3, 2026

5
min read
How to Label PII in Google Drive Automatically
Learn how to automatically detect and label personal data (PII) in Google Drive using Strac’s classification engine to support GDPR and CPRA compliance.
Google Drive stores large volumes of personal data across HR directories, Shared Drives, customer folders, and internal collaborations. However, Drive does not have native PII detection or automatic labeling capabilities. GDPR Article 30 requires identifying where personal data resides; CPRA requires tracking Sensitive Personal Information such as contact data, household identifiers, and account numbers. Without labeling, organizations have no visibility into where PII sits inside Drive.
Strac solves this by classifying and labeling PII across Google Drive instantly, enabling privacy visibility, compliance tracking, and remediation workflows.
Google Drive does not inspect file contents, cannot detect personal data, cannot classify files at scale, and cannot apply metadata labels based on content. As a result, PII lives unmonitored across public folders, externally shared directories, and internal team drives. GDPR and CPRA require organizations to know where personal data exists, and Drive alone cannot provide that visibility.
Google Drive lacks:
Strac fills this gap with continuous scanning and labeling of PII across all Drive storage surfaces.
Labeling provides visibility, governance, and risk prioritization. Strac detects PII across documents, spreadsheets, images, and PDFs; then applies labels to files, helping teams classify, organize, and remediate exposure in accordance with GDPR and CPRA.
Strac labels files containing:
• Names, emails, and phone numbers
• Home or mailing addresses
• Employee or customer identifiers
• Demographic information
• Personal forms and applications
• HR onboarding documents
• Screenshots containing personal data
• Scanned images with PII
Labels can include:
• “Contains PII”
• “Sensitive Personal Information”
• “GDPR High Risk”
• “PII – Action Required”
Labels drive next-step actions such as alerts, blocking, redaction, or deletion.
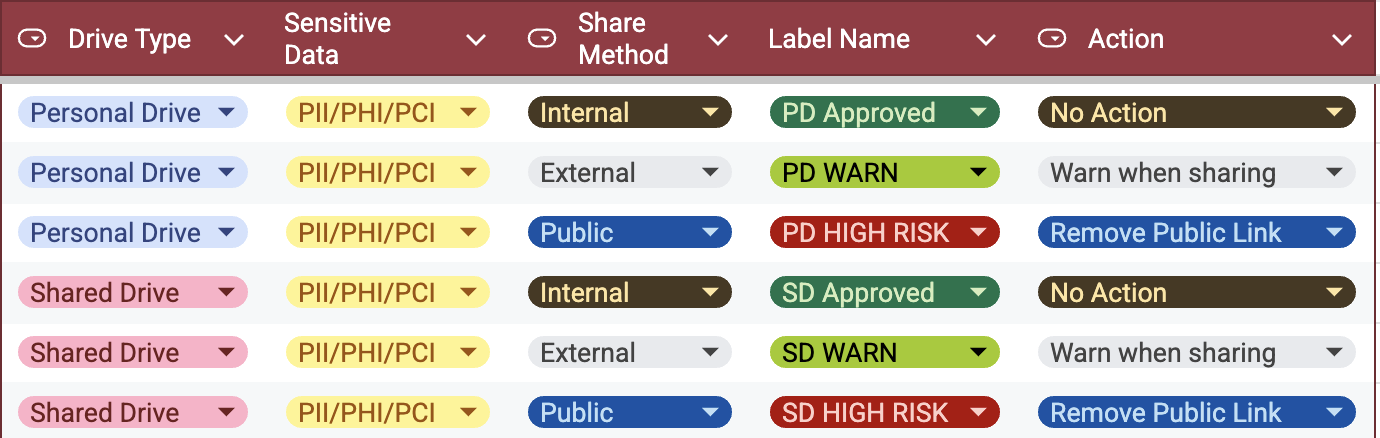
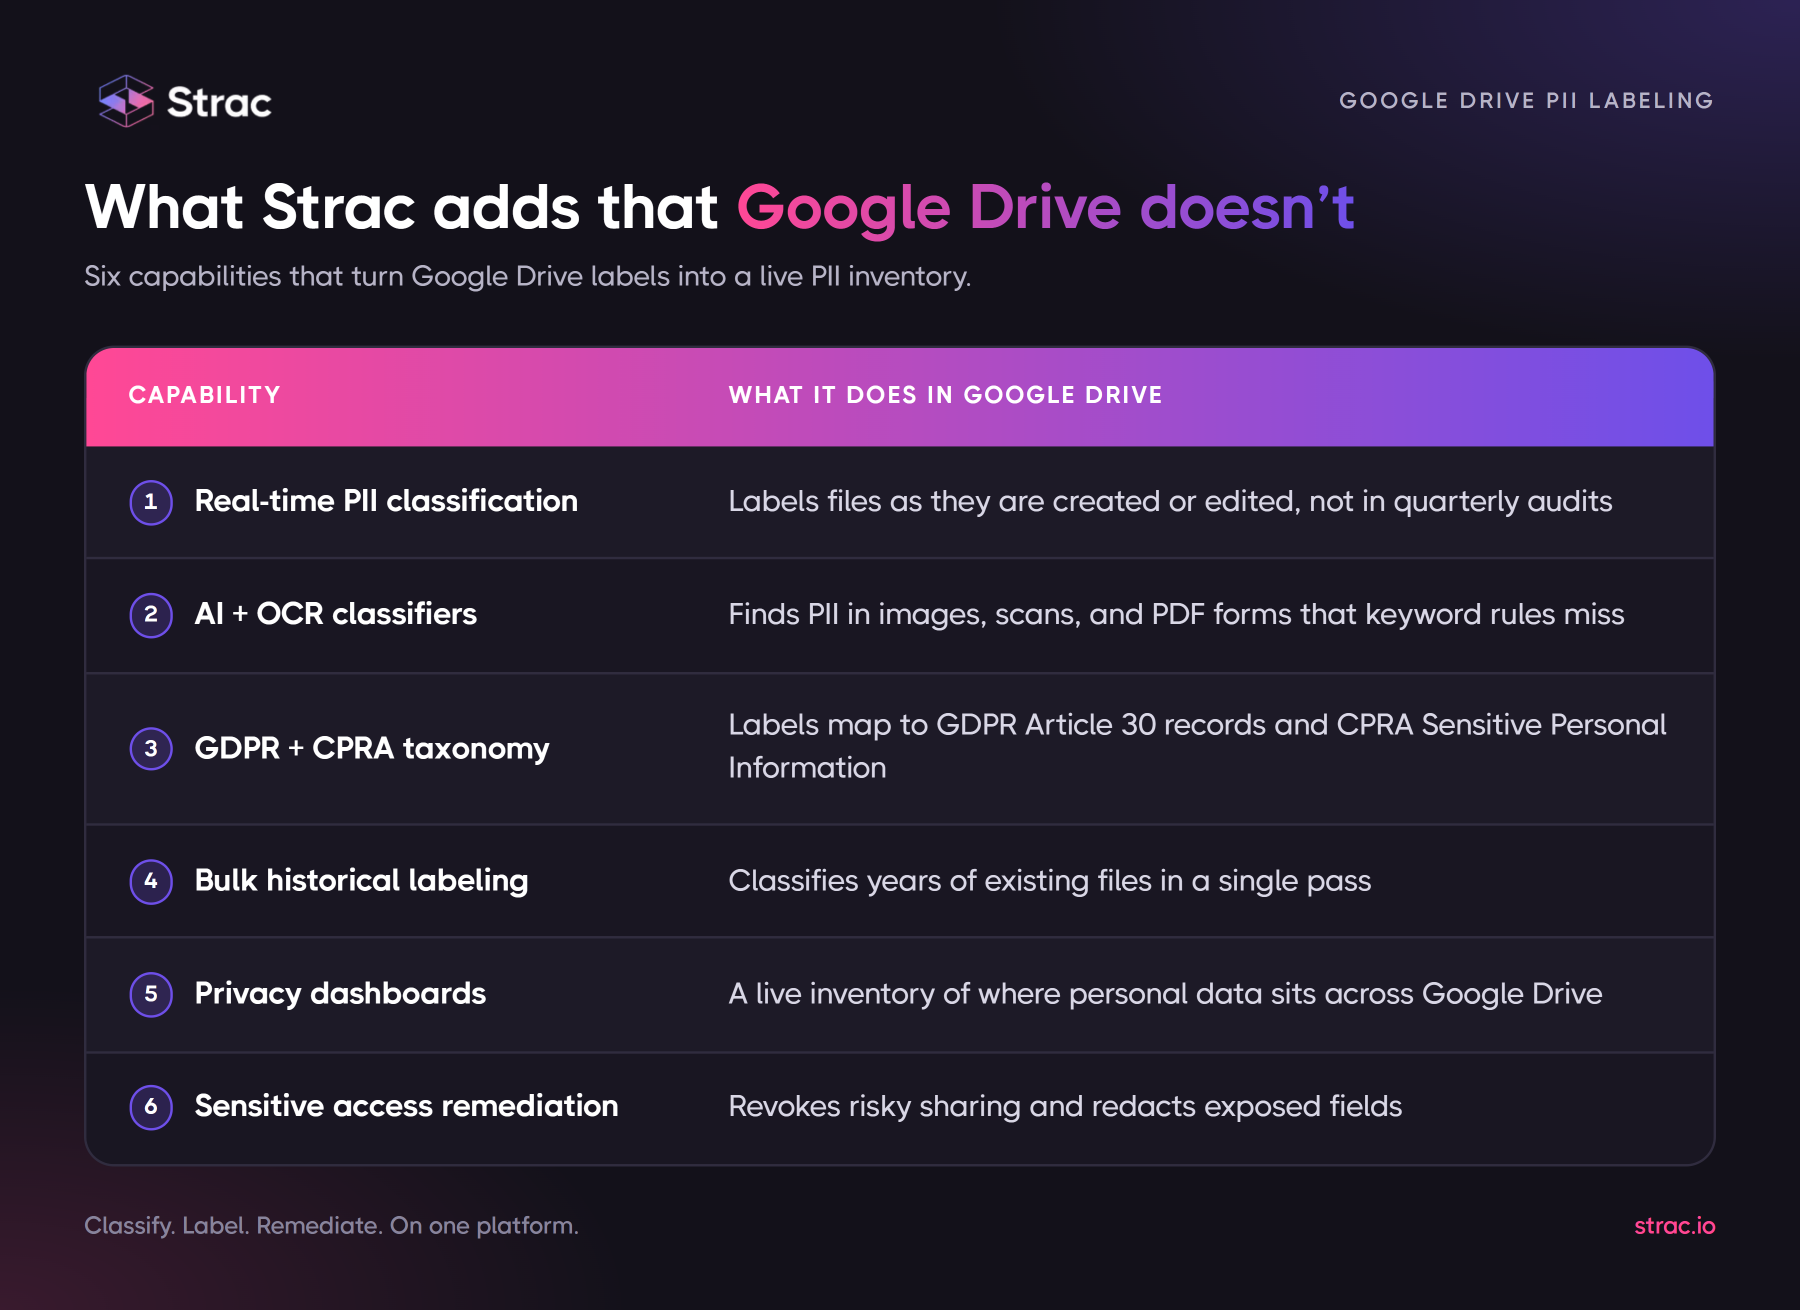
Strac continuously scans Drive; classifies files using AI and OCR; and applies metadata labels automatically. This builds a real-time inventory of personal data; enabling GDPR/CPRA compliance and data governance workflows.
Labeling workflows include:
• Automated labeling during upload
• Retroactive labeling of historical files
• Folder-level bulk tagging
• Label-triggered alerts and remediation
• Privacy dashboards and inventory lists
• Misconfiguration checks for public or external access
This creates a complete map of personal data across Drive.

Strac scans every file in Google Drive, detects personal data, and applies Google Drive labels that match your privacy taxonomy. The result is a complete PII inventory that stays current, supports GDPR and CPRA compliance, and triggers remediation automatically.
PII labeling in Google Drive is the starting point for protecting personal data. Teams need to understand which files contain sensitive information, who can access them, and where action is required.
Strac’s Google Drive DLP connects sensitive data discovery and automatic labeling with remediation, including alerts and removal of public or unauthorized external access. This helps teams turn classification into practical protection and support their privacy compliance workflows.
No; Drive cannot detect or classify personal data.
Yes; OCR supports all visual formats.
Yes; labels can activate multi-step workflows.
Yes; it helps organizations track, audit, and control personal data.
Yes; Strac supports complete historical classification.