How to Handle and Share Credit Card Data Securely and Comply with PCI DSS ?
PCI DSS regulates the secure storing and sharing of PCI data . Explore the key ways to handle credit card data in SaaS ,Cloud and Endpoints with DLP solution like Strac.
· Securely sending a credit card number meanstransmitting a token or a masked value instead of the PAN — never the raw 16digits, on any channel, to anyone.
· The risk is not the payment gateway; it is theimprovised path around it. A customer pastes a card into a chat widget, anagent forwards it to billing, and the PAN is now in a mailbox, a ticket, and aSlack thread that no one will ever scope for an audit.
· PCI DSS 4.0.1 already forbids this outright, andevery future-dated requirement is now mandatory — but the standard tells youwhat must not happen, not how to stop it. Encryption in transit does nothingabout a PAN sitting in a message someone was allowed to send.
· The control that closes the gap is PCI DSS PAN masking at the data layer:inspect every message, file, and upload, and redact the card number before itis delivered.
· Strac applies that across SaaS,cloud, browser, endpoint, and MCP. Start from the pillar on how to become PCI DSS compliant.
Securely sending a credit card number is the practice of moving cardholder data between people or systems without ever exposing the full PAN — using a token, a masked value, a one-time secure link, or a PCI-scoped form instead of the digits themselves.
The word doing the work is never. PCI DSS does not grade you on how well you protected a card number you emailed; it treats the emailed card number as the failure. A PAN in a mailbox is in scope, a PAN in a Zendesk ticket is in scope, and a PAN in a Slack channel drags that channel, its exports, and its integrations into scope with it.
That is why credit card masking is a transmission control, not just a storage one. Storage is a decision you make once, deliberately. Transmission is a decision your employees and customers make hundreds of times a day, under time pressure, on whatever channel is open.
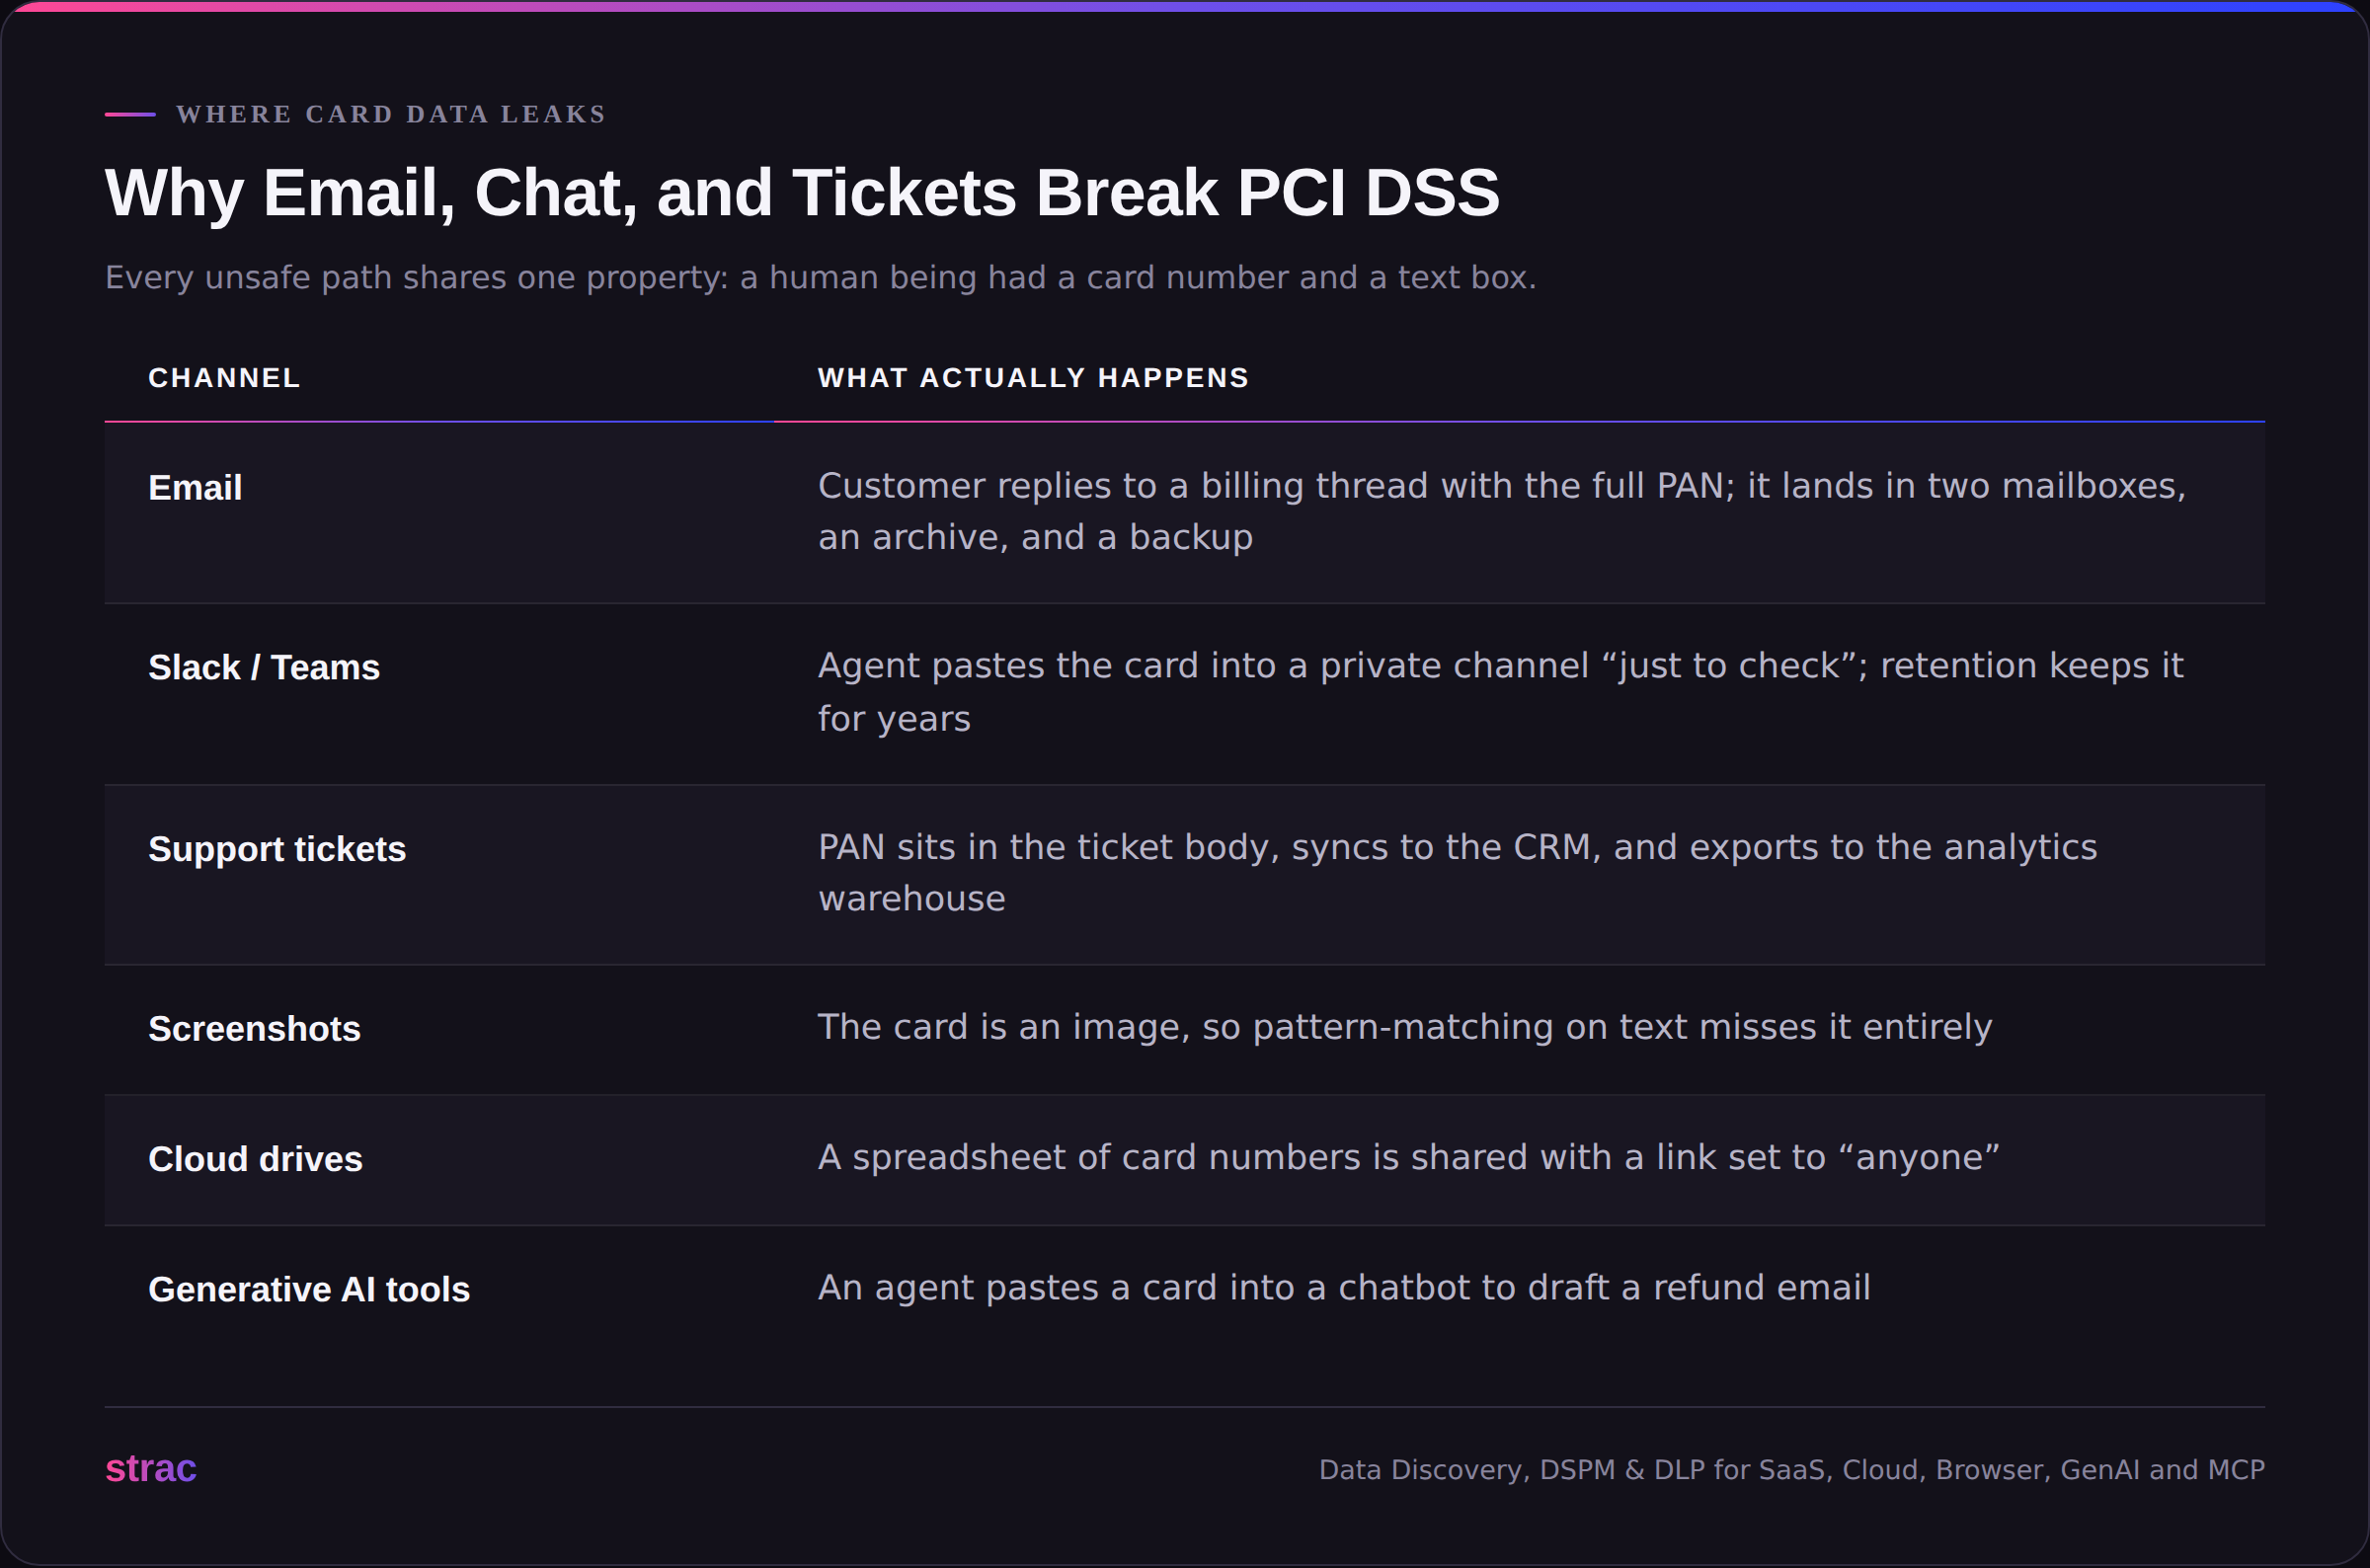
✨ Why Email, Chat, and Tickets Break the Standard
Every unsafe path shares one property: a human being had a card number and a text box.
Six ordinary channels, one shared failure: the card number was delivered somewhere no one will scope for an audit.
Encryption protects the card number in transit; redaction makes sure there is nothing worth stealing when it arrives. TLS on a mail server is not a defense against a PAN that is legitimately delivered to the wrong mailbox, indexed, and retained.
That last row is the newest one. A support agent asking a chatbot to rewrite a refund email will paste the whole ticket, PAN included — which is why AI DLP and MCP DLP now belong in a PCI conversation that used to end at email.
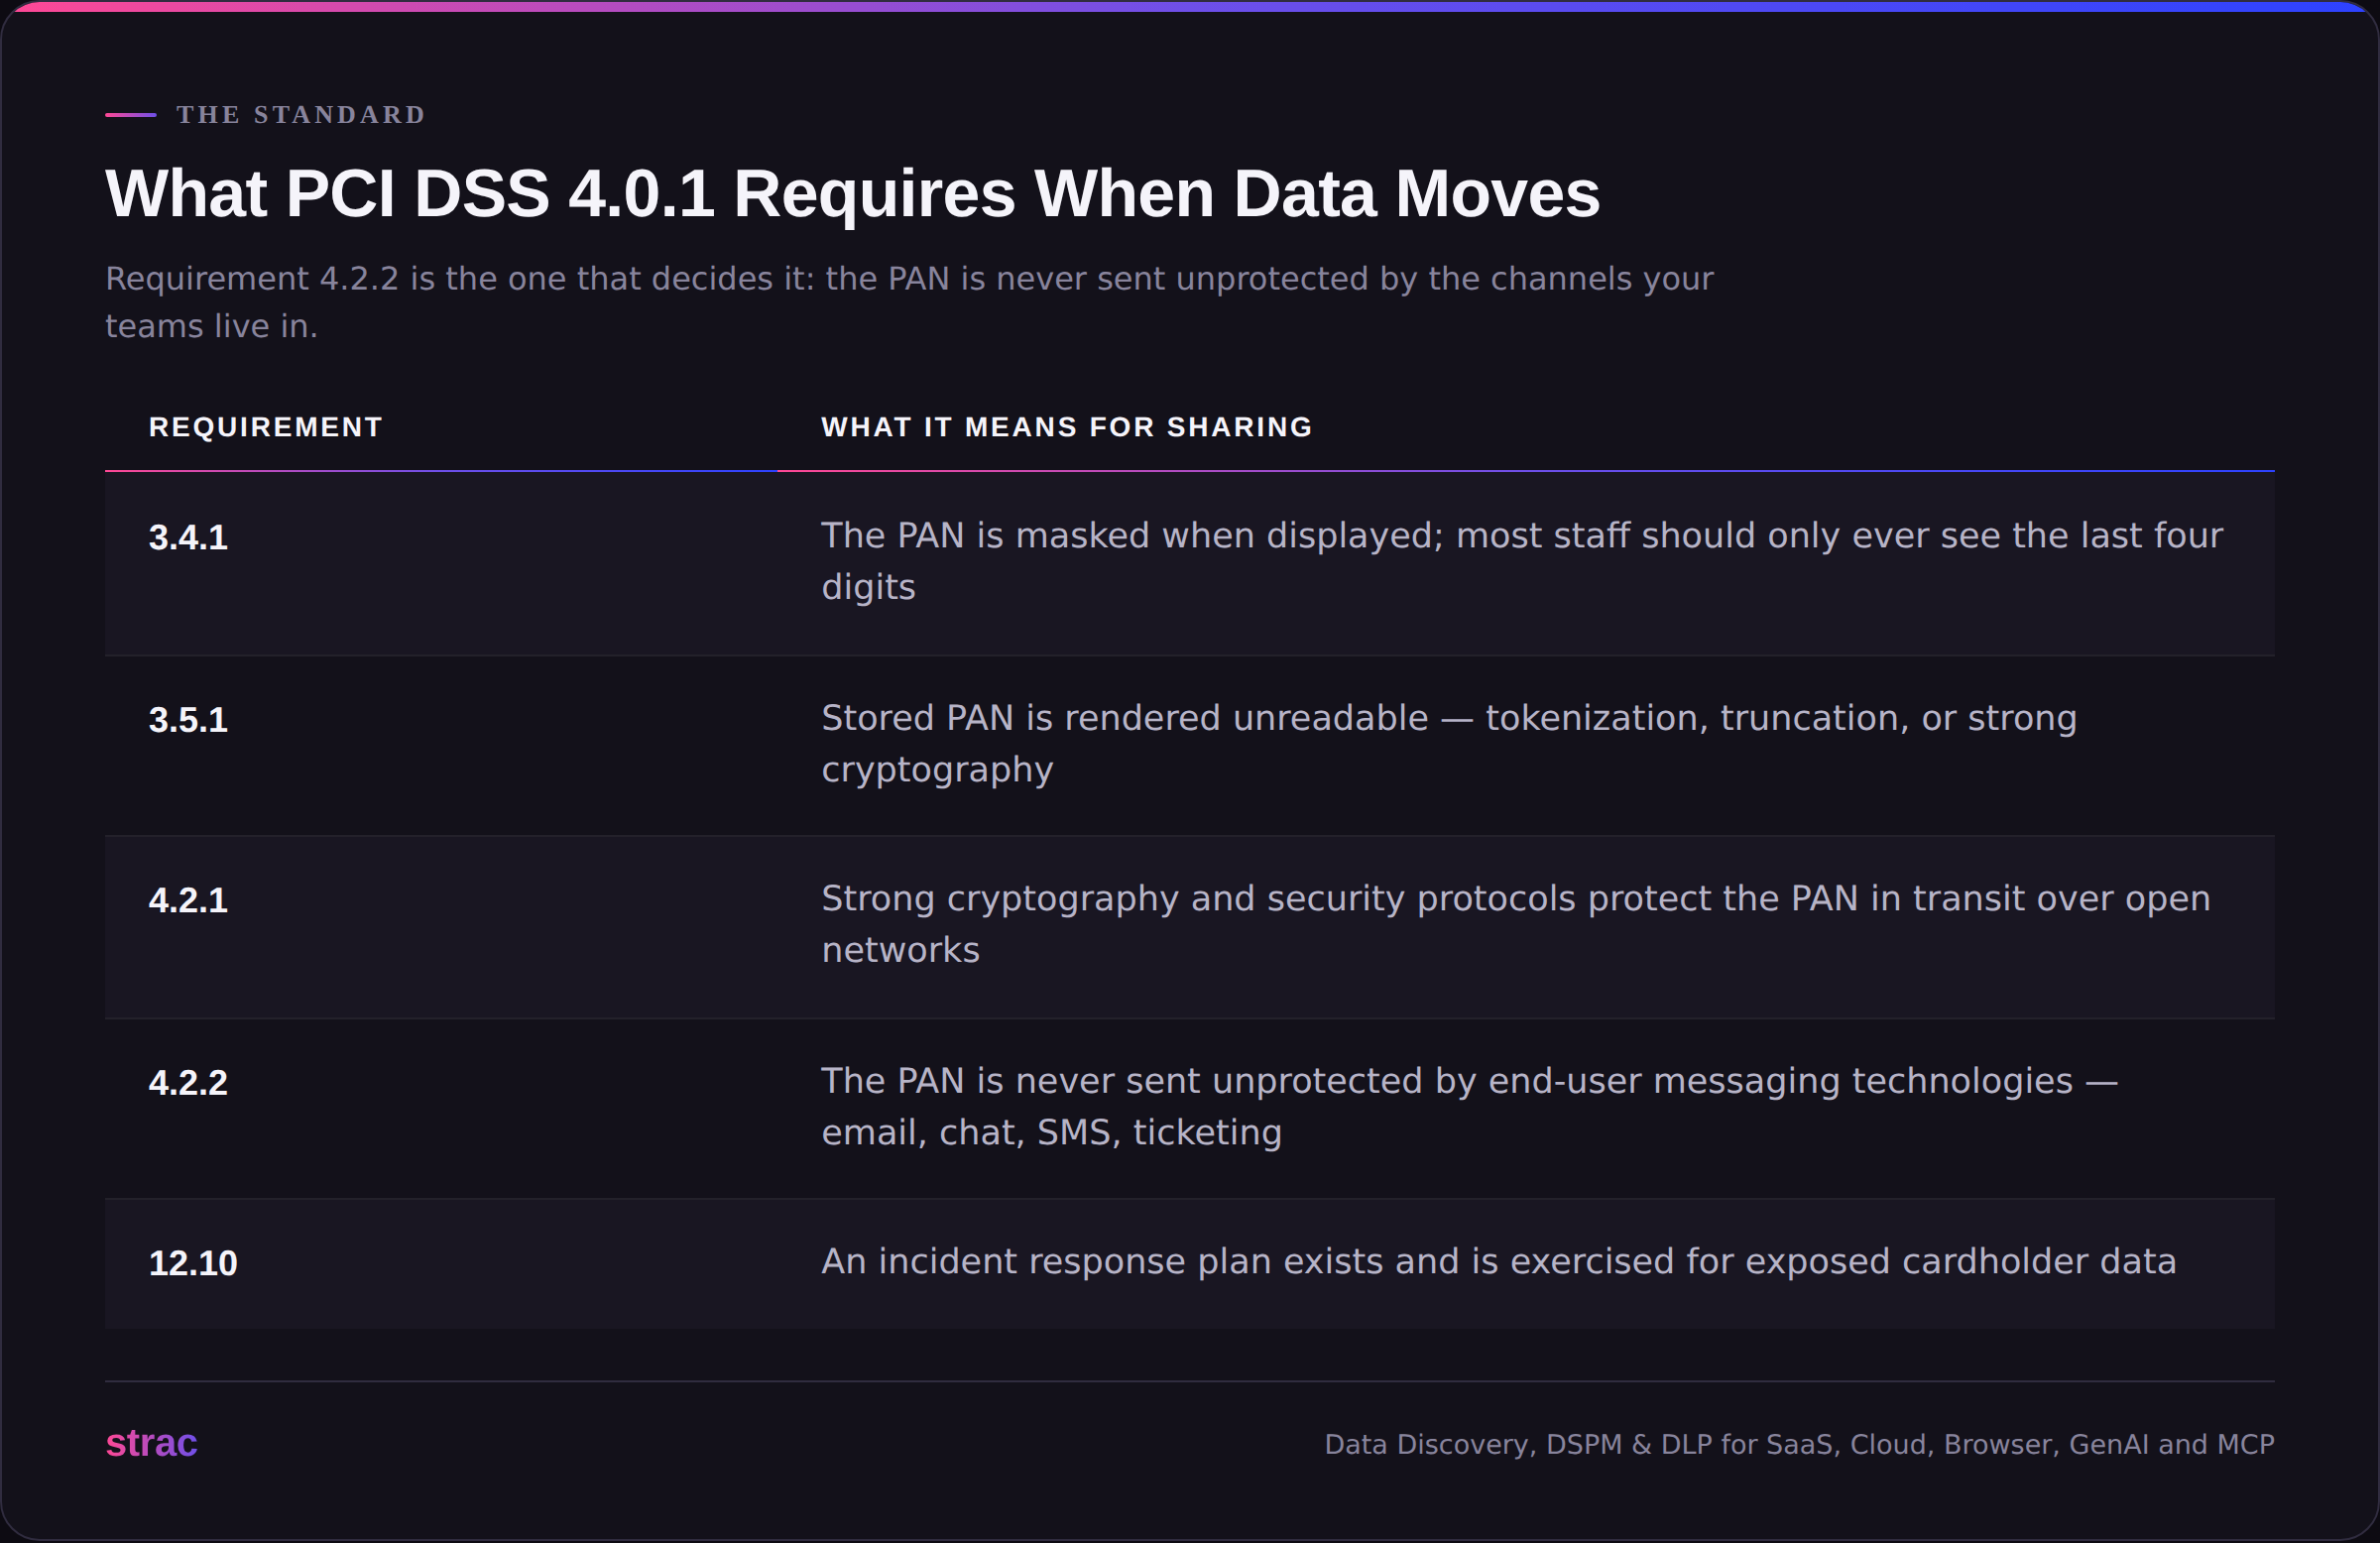
✨ What PCI DSS 4.0.1 Requires When Data Moves
The relevant clauses are short and unambiguous.
Four of these five clauses are satisfied by removing the PAN from the message — not by protecting the message.
Requirement 4.2.2 is the one that decides this article. It does not say encrypt the message. It says the PAN is never sent unprotected by the channels your teams live in. Meeting it means either removing the card number from the message or removing the ability to send it.
A policy that tells employees never to email a card number is a hope; a control that strips the PAN before the message sends is a guarantee. For the audit-side view of the same clauses, see how to test for PCI compliance.
The Four Safe Ways to Send a Card Number
(screenshot: Strac policy view showing card-number detection across email, Slack, and a ticketing tool)
Don't send it — send a token.Data tokenization replaces the PAN with a reference value that is useless outside the vault. Systems keep working; the digits stay in one place.
Send a payment link. Route the customer to a PCI-scoped hosted page. The card never touches your mailbox, your ticket system, or your agent's screen.
Send the last four. Requirement 3.4.1 exists because almost every internal workflow — reconciliation, refunds, dispute handling — resolves on four digits and an expiry.
Send a redacted copy of the original. When a customer has already pasted a PAN, the safe artifact is the message with the number stripped out and an audit record of what was removed.
Every safe path ends in the same place: the person receiving the message does not need the card number, and does not get it.
How Redaction Works at the Moment of Sharing
(product video: a card number pasted into Slack and redacted in place, with the audit event)
The mechanism is simple and it runs before delivery. Strac inspects the content of every message, attachment, upload, and agent action, classifies the PAN — in text, in a PDF, in a screenshot via OCR — and applies the policy in this order:
Redact / mask — the card number is replaced in place across Slack, email, tickets, docs, Google Drive, SharePoint, and Box, and the original is vaulted.
Block — the send, upload, or download is stopped when the destination is unsanctioned.
Warn and coach — the sender sees why the action was risky and what the safe path is.
Revoke access — an over-shared file holding cardholder data is unshared automatically.
Redaction is the only remediation that leaves the workflow intact — the ticket still resolves, the PAN is simply gone from it.
🎥Strac: PCI DLP Across the Channels People Actually Use
Strac discovers cardholder data wherever it already sits, then keeps it from moving. Discovery and DSPM scan SaaS apps, cloud storage, and endpoints for historical PANs. Endpoint DLP and browser controls catch the paste into a chat window or a generative AI tool. Slack DLP and Google Workspace DLP cover the two channels where most accidental sharing happens. AI DLP and MCP DLP redact the PAN before a model or an agent ever receives it.
Tokenization protects the systems you designed. PCI DSS PAN masking protects the ones your employees improvise. Both matter, and only the second one is optional in most programs — which is exactly why most programs still fail Requirement 4.2.2.
Days 0–30 — Discover. Scan SaaS, cloud storage, and endpoints for existing card numbers. Most teams find PANs in ticket archives and shared drives they had scoped out.
Days 30–60 — Protect. Turn on redaction for email, Slack, tickets, and the browser. Start in warn-and-coach mode, then move to redact.
Days 60–90 — Prove and scale. Extend to generative AI and MCP surfaces, and hand the assessor the audit trail rather than a policy document.
Every control above the data layer eventually fails. Training lapses, a customer pastes a PAN into the wrong box, a well-meaning agent forwards a ticket, and an approved channel carries cardholder data it was never scoped for. The data layer is the backstop: redact the card number on every action and a mistake never becomes a breach. Book a demo to see Strac find and redact cardholder data across the channels your teams already use.
🌶️ Spicy FAQs for Sending Credit Card Numbers
Is encrypted email enough to send a credit card number?
No. Requirement 4.2.2 prohibits sending an unprotected PAN by end-user messaging technologies, and encryption protects the transport, not the message. Once delivered, the PAN sits in a mailbox, an archive, and a backup — all now in scope.
A gateway secures the path you designed. It has no visibility into the customer who pasted a card into a chat widget or the agent who forwarded it to billing. Those paths are where credit card masking at the data layer applies.
Can we stop this without blocking our support team?
Yes — the default action is redaction, not blocking. The message, ticket, or file is delivered with the PAN removed and vaulted, so the agent keeps working and the assessor gets an audit record. Blocking is reserved for unsanctioned destinations.
Can you catch a card number inside a screenshot?
Yes, through OCR on images and attachments — though no detection is perfect, and a deliberately obfuscated number can evade any classifier. That is why redaction is paired with discovery: what slips through in transit is still found and remediated at rest.
Where does this fit in a wider PCI program?
Secure transmission is one control in a twelve-requirement standard covering network security, access control, monitoring, and policy. Start from the pillar on how to become PCI DSS compliant and work outward.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.