Why Redacting Sensitive Data is Necessary for PCI Compliance
Redacting sensitive data for PCI compliance removes card numbers from Slack, email, tickets, and AI tools. See what PCI DSS 4.0.1 requires and how Strac does it.
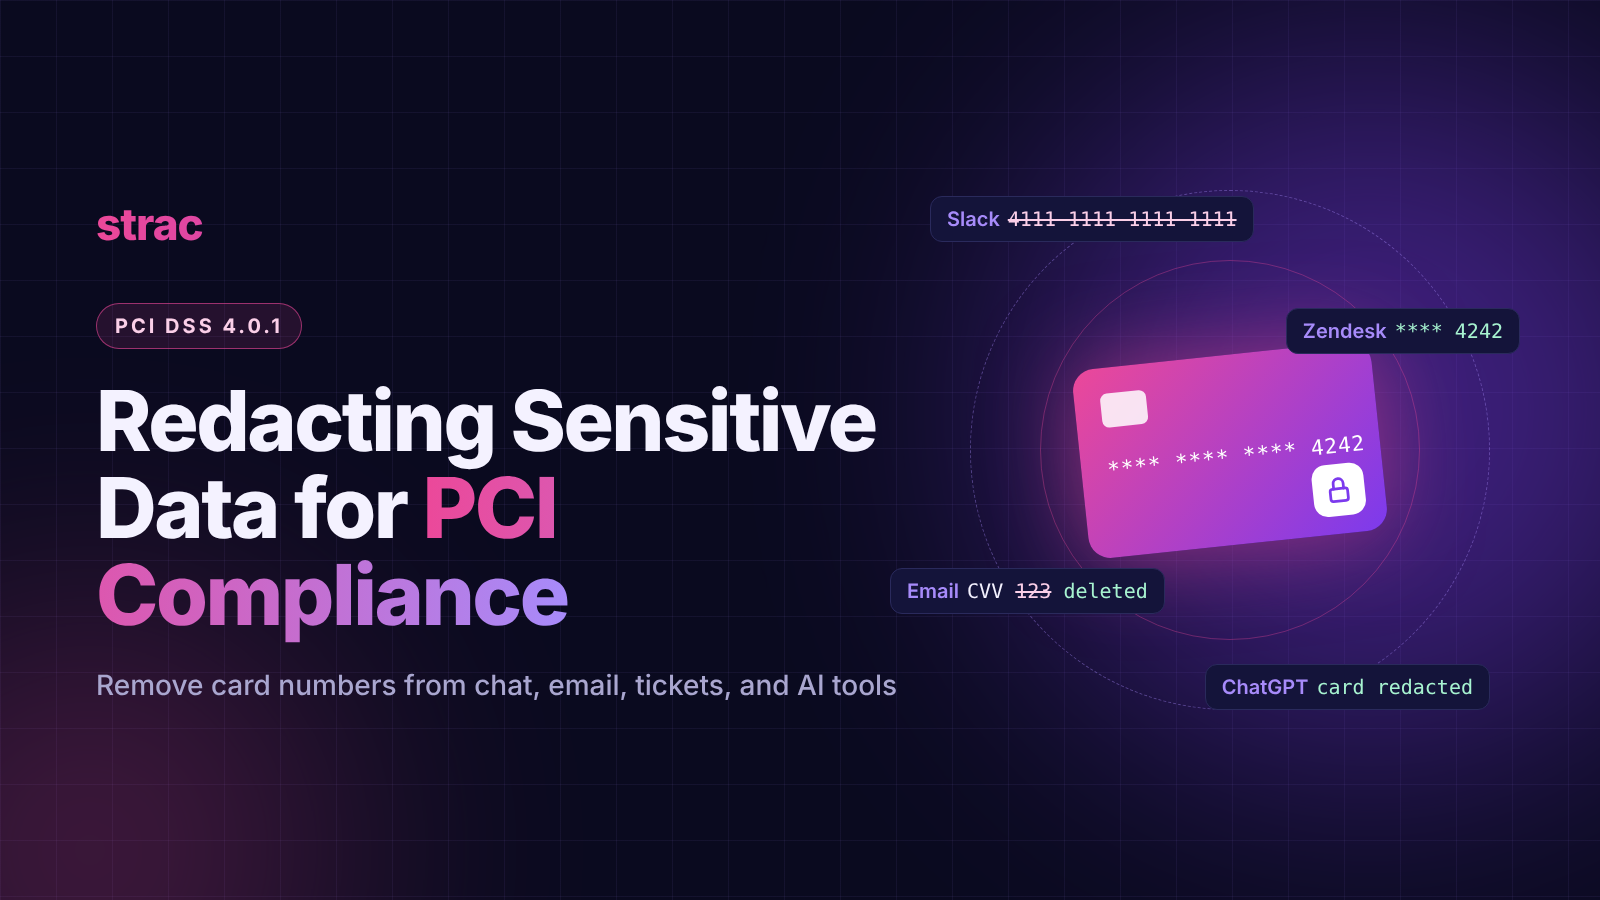
PCI redaction replaces a full card number (PAN) with a masked version, usually the last four digits, and deletes CVVs outright, everywhere card data lands by accident.
Card numbers rarely leak from the payment system. They leak when a customer pastes a card into a support chat, an agent forwards a receipt by email, or someone drops a ticket thread into an AI tool.
PCI DSS 4.0.1 is fully in force, and requirements 3.3.1, 3.4.1, 3.4.2, 4.2.2, and 12.10.7 all reach those everyday tools. Access controls and encryption do not take the card number out of the message.
Strac finds and redacts card data across SaaS, email, browsers, endpoint DLP, generative AI tools, and MCP DLP, and logs every fix as audit evidence.
PCI redaction is the removal of cardholder data from a place it should not be. A full card number becomes **** **** **** 4242. A CVV is deleted. The rest of the message, ticket, or file stays as it was.
It covers three kinds of data:
PAN: the 13 to 19 digit card number. Mask it to the last four digits, or remove it.
Sensitive authentication data (SAD): CVV, full track data, and PINs. These cannot be kept after authorization, so redaction means deletion.
Images and files: photos of cards, screenshots of billing pages, and scanned PDFs. Redaction blurs the card number inside the image.
Masking hides the number on screen. Redaction removes it from the stored copy. PCI cares about both, and only the second one shrinks your scope.
Who Has to Care
PCI DSS applies to any business that stores, processes, or transmits card data, or can affect the security of systems that do. That includes companies that use a payment processor like Stripe and never meant to touch a card number.
Using a processor keeps cards out of your payment flow. It does not stop a customer from typing one into your Zendesk widget. Once that ticket exists, the card number is in your systems, and the PCI DSS rules apply to it.
✨ The PCI DSS 4.0.1 Requirements Redaction Supports
PCI DSS 4.0.1 is the only active version of the standard. Every requirement that was future-dated in 4.0 has been mandatory since March 31, 2025. These are the ones that reach chat, email, tickets, and AI tools:
3.2.1, keep as little as you can. Account data is stored only as long as there is a business need, then deleted. A card number sitting in a 2023 Slack thread fails this test.
3.3.1, no SAD after authorization. CVVs cannot be stored, even encrypted. A CVV in a support ticket is a finding the day an assessor sees it.
3.4.1, mask PAN when displayed. Staff without a business need see no more than the first six and last four digits.
3.4.2, control copying over remote access. Technical controls must stop staff from copying or moving PAN when they work through remote access, unless they are explicitly authorized.
4.2.2, protect PAN sent through messaging. If a PAN is sent by email, chat, SMS, or collaboration tools, it must be protected with strong cryptography. Most messaging tools cannot do that for a card number pasted in plain text.
12.5.2, confirm your scope. Every location where account data is stored, processed, or sent must be identified and confirmed at least once a year. Service providers do it every six months under 12.5.2.1.
12.10.7, respond to PAN found where it should not be. You need incident response steps that kick in when stored PAN turns up somewhere unexpected.
Redaction is how you meet these rules in tools you do not control. For a full walkthrough of what changed, see PCI DSS 4.0 changes.
Strac Slack PCI Redaction
Where Card Data Needs Redacting in 2026
Team chat. A refund request with the full card number lands in Slack, Microsoft Teams, or Zoom chat.
Email. A customer replies with their card details in Gmail or Office 365, sometimes as a photo.
AI tools. A support lead pastes a ticket thread into ChatGPT, Claude, Copilot, or Gemini to draft a reply, card number included.
AI agents. An agent connected to Stripe or Salesforce through MCP pulls a full customer record into its context and sends it to a model provider.
The last two are new, and most PCI programs do not check them yet. That is the gap AI DLP and MCP DLP close.
🎥 How Strac Redacts Card Data in Real Time
Strac checks every new message, ticket, file, and prompt as it arrives. It confirms a real card number with a Luhn check and nearby context, so order numbers and tracking codes are left alone. OCR reads card numbers inside photos, screenshots, and scanned PDFs.
When Strac finds card data, it acts in this order, based on your policy:
Redact / mask. Replaces the PAN with the last four digits and deletes the CVV in Slack, email, tickets, docs, Google Drive, SharePoint, and Box.
Block. Stops the card number from reaching an AI tool, a personal upload site, a USB drive, or an agent's context.
Warn and coach. Tells the person what was caught and where card details should go instead, at the moment they paste.
Revoke access. Removes public links and outside sharing from files that hold card data.
Strac is one DLP and DSPM platform, so the same card detectors and policies run everywhere.
Find it first. DSPM scans SaaS apps, cloud storage, and databases for PAN and CVV, including years of history, and ranks findings by who can see them. The PII scanner reads PDFs, spreadsheets, ZIP files, and images.
Support and CRM.Zendesk DLP, Intercom DLP, and Salesforce DLP mask PAN and delete CVVs in tickets, chats, and cases. Agents keep working on the rest of the conversation.
Browser and AI tools.Browser DLP and AI DLP mask card numbers in prompts and uploads before they leave the tab. The question reaches the model. The card number does not.
AI agents.MCP DLP redacts PAN in what MCP servers hand back to agents, so an agent can summarize a billing history without ever holding the card number.
Laptops and remote access. One endpoint DLP agent for Mac, Windows, and Linux controls copy, paste, USB, and print for files with card data. This is the 3.4.2 control.
Copies that move.Data lineage recognizes a card export even after it is renamed or copied.
Cards you need to keep.Data masking and tokenization swap a PAN for a token, which takes those systems out of PCI scope.
Every finding and fix is logged with time, location, data type, and action. That log is your 12.5.2 scope evidence and your 12.10.7 response record. SaaS integrations connect through APIs in under 10 minutes.
☐ Chat, email, and support tools redact card numbers as they arrive
☐ No CVV or full track data is stored anywhere after authorization
☐ Historical messages, tickets, and files have been scanned and cleaned
☐ Images, PDFs, and attachments are scanned, not only text
☐ Prompts to AI tools and MCP agent responses are checked for PAN
☐ Laptops block copying card data to USB and personal storage
☐ Every redaction is logged and exports as evidence for your QSA
Finding card data shows you the risk. Redacting it removes the risk.
The Bottom Line
PCI DSS 4.0.1 does not stop at your payment page. It follows card numbers into chat, email, tickets, laptops, and AI tools. Access controls and encryption fail eventually, so the data layer is the backstop: redact card data the moment it lands, and a careless paste never becomes a breach.
Book a demo to see Strac redact card data across your stack.
🌶️ Spicy FAQs on Redacting Sensitive Data for PCI Compliance
Is redaction the same as PAN masking?
No. Masking hides digits on screen while the full number stays stored underneath. Redaction removes the full number from the stored copy. PCI DSS 3.4.1 asks for masking on display; redaction is what takes the card out of scope.
We use Stripe. Why do we still need PCI redaction?
Stripe keeps cards out of your payment flow, not out of your inbox. When a customer pastes a card into a support chat or email, that copy lives in your systems, and PCI DSS applies to it.
Will redaction slow down our support team?
No. Strac masks only the card number and leaves the rest of the ticket or message in place. Agents see the last four digits, which is all they need to confirm the right card with the customer.
Can redaction catch every card number?
Not every one. A card read out on a phone call or written on paper never reaches a scanner. That is why redaction at every digital entry point matters: what does reach your systems is cleaned before anyone can take it.
How does PCI redaction work with AI tools and agents?
It works the same way, at the prompt and at the agent's data source. Strac masks card numbers before a prompt reaches ChatGPT or Claude, and before an MCP server hands records to an agent. See AI data governance for the full picture.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.