

August 24, 2026

8
min read
Data Loss Prevention Policy
Data loss prevention policy guide for 2026: protect sensitive data across SaaS, cloud, endpoints, GenAI, and MCP with Strac.

Data loss prevention policy guide for 2026: protect sensitive data across SaaS, cloud, endpoints, GenAI, and MCP with Strac.

A data loss prevention policy should do more than satisfy an auditor. It should give employees clear rules, give security teams enforceable controls, and give the business a safe way to use SaaS, cloud, endpoints, GenAI and MCPs.
That is harder in 2026 because sensitive data no longer moves through only email and corporate networks. It can appear in a Slack message, a Zendesk attachment, a browser upload, a ChatGPT prompt, an MCP tool call, a file copied to USB, or an AI agent's response. A modern DLP policy must govern all of those paths without turning normal work into a maze of blanket restrictions.
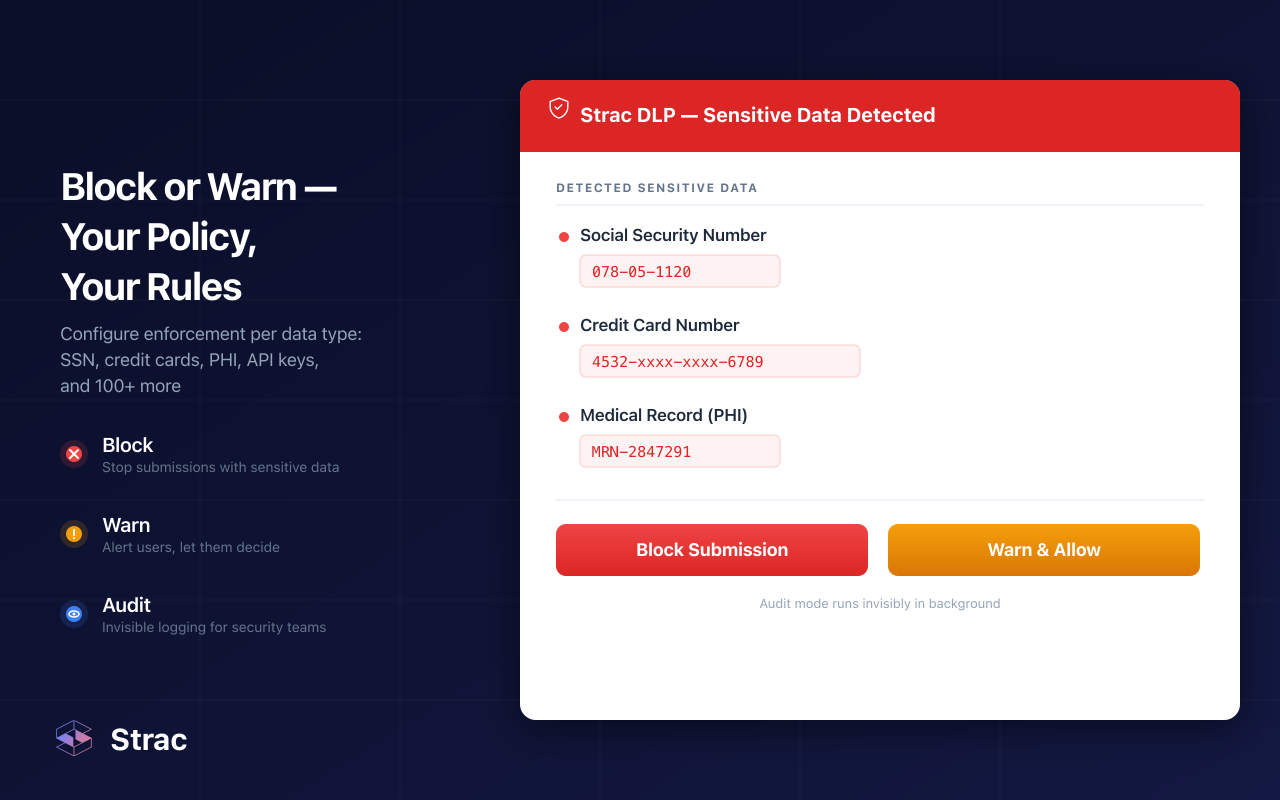
A data loss prevention policy is a formal set of rules for identifying, handling, monitoring, and protecting sensitive information. It defines:
The policy is the governance layer. DLP technology is the enforcement layer. A policy that says employees must not paste customer records into public AI tools has little practical value if the organization cannot detect the data, identify the destination, and stop or redact the prompt before submission.
Traditional DLP programs focused on email, network traffic, managed endpoints, and removable media. Those channels still matter, but the data environment has expanded.
Employees now move sensitive information across collaboration tools, cloud drives, CRM and support systems, browsers, AI assistants, and hundreds of SaaS applications. AI agents can also retrieve information from connected systems and send it to models or external tools through APIs and the Model Context Protocol (MCP). Shadow AI and unsanctioned SaaS add destinations that security teams may not know exist.
A current DLP policy should therefore address data across:
The goal is not to block every movement of sensitive data. It is to make a context-aware decision based on the data type, user, channel, destination, and business purpose.
An effective policy should help the organization:
Begin by stating why the policy exists and exactly what it covers. Avoid vague language such as “all confidential information must be protected.” Name the people, data, systems, and workflows that fall within scope.
The scope may include:
The policy should also state whether controls apply to data at rest, in use, and in motion.
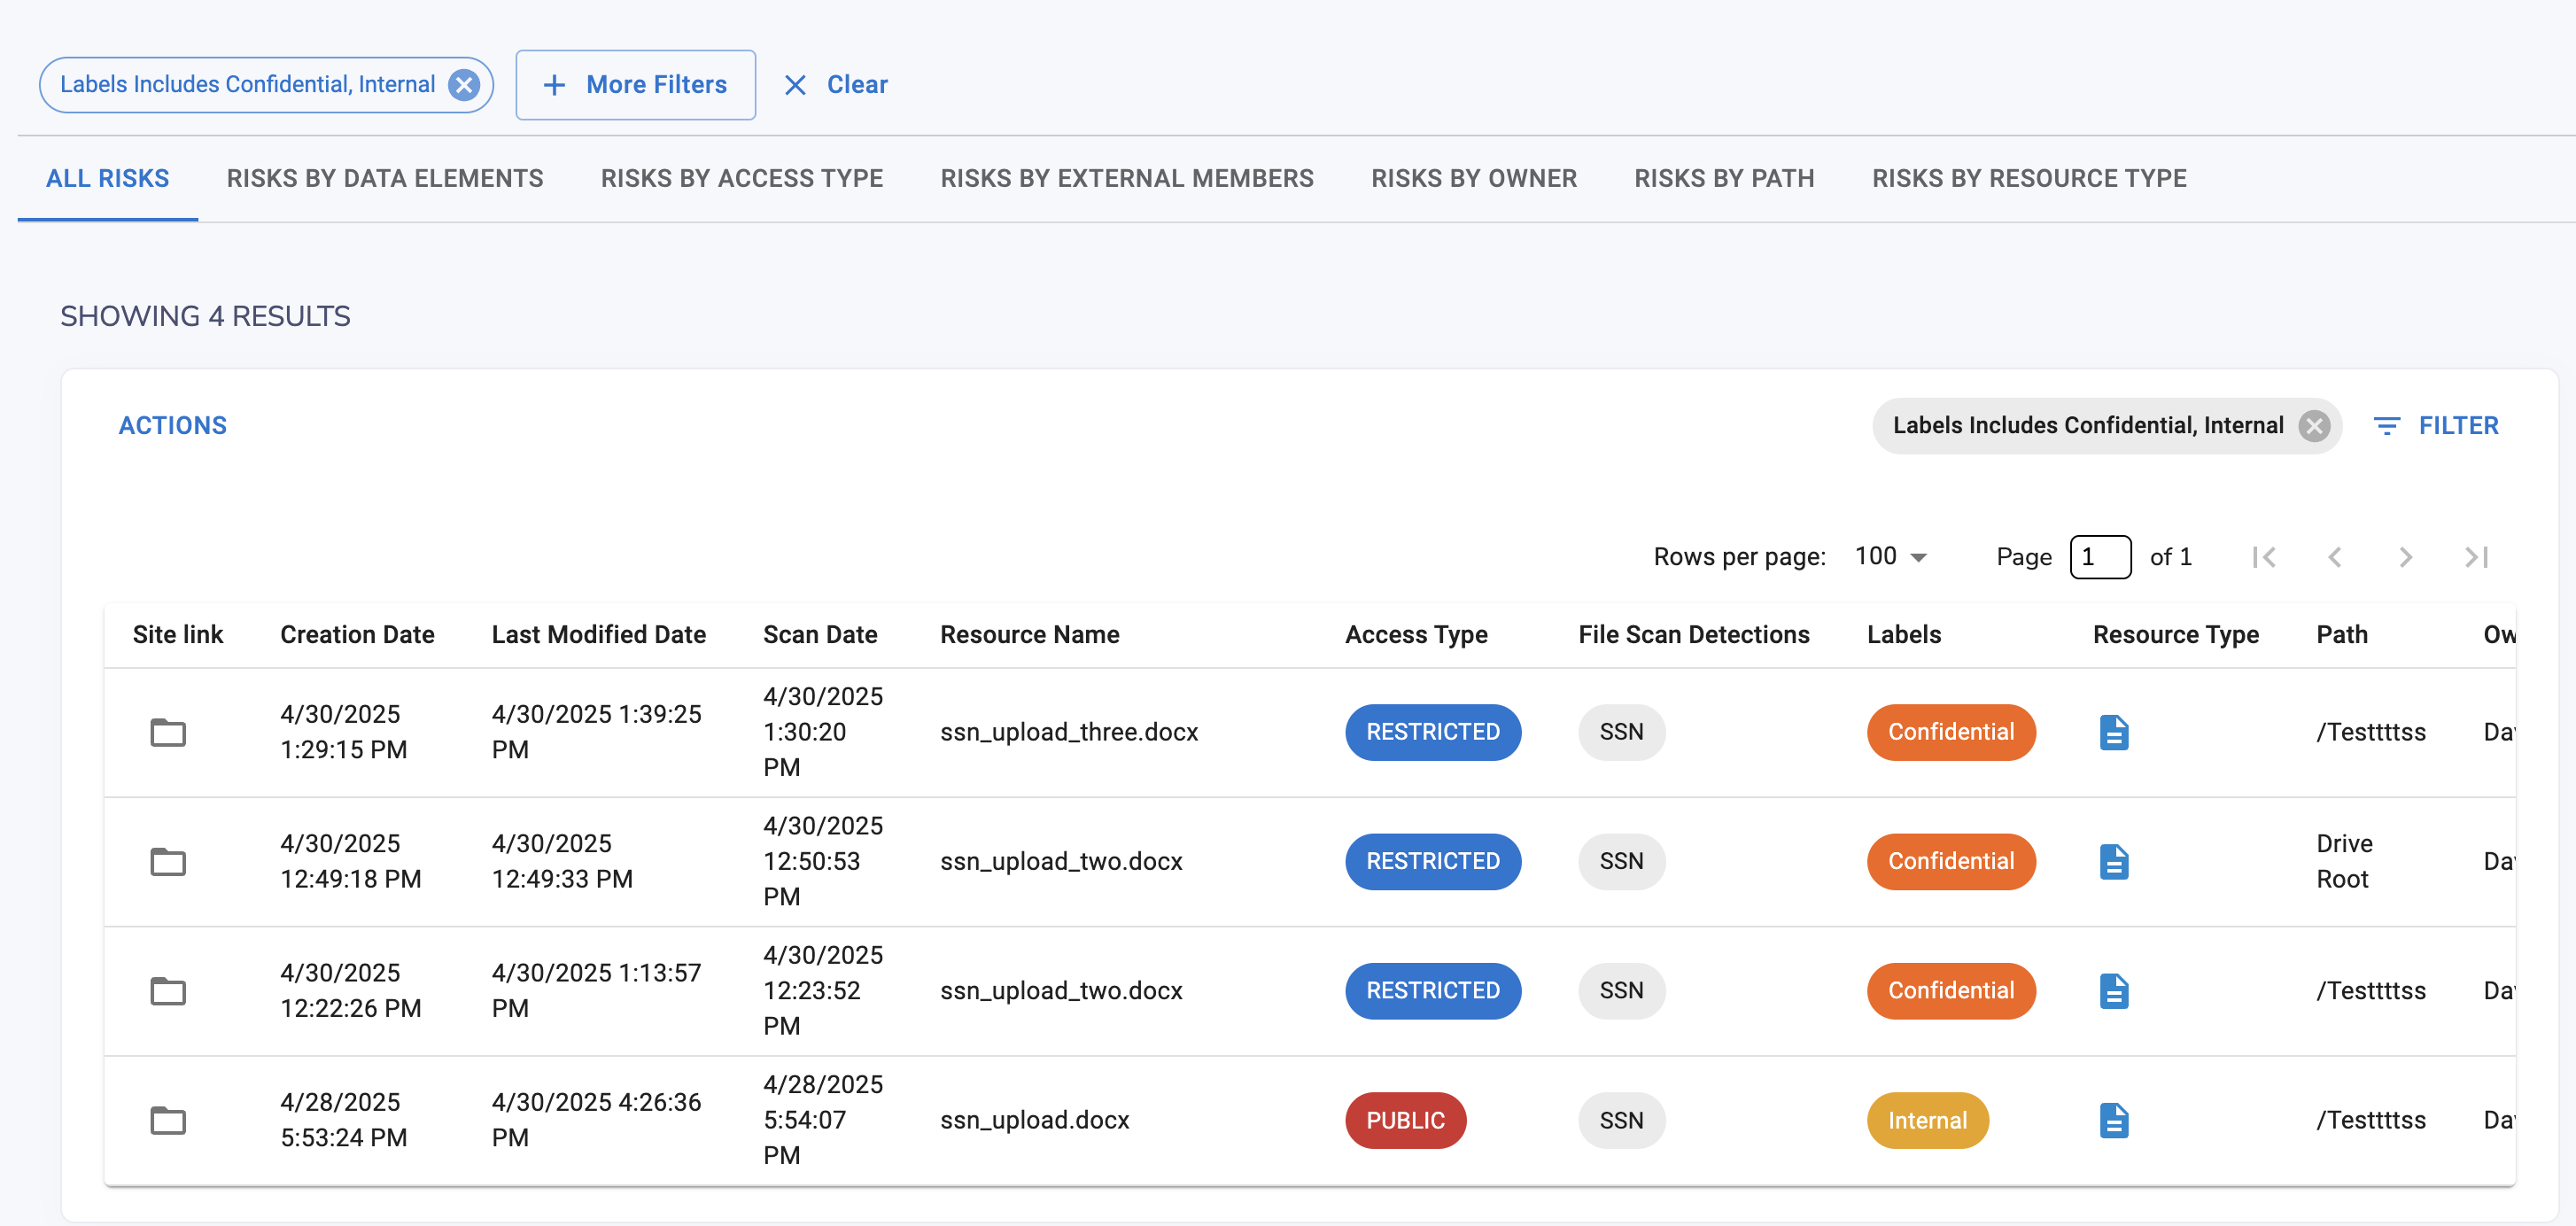
Use a small number of classifications that employees can understand and security teams can enforce. A practical model is:
Restricted data may include:
Classification must work beyond plain text. Sensitive data frequently appears inside PDFs, spreadsheets, screenshots, scanned documents, images, ticket attachments, and compressed files. Detection should therefore include document parsing, OCR, image analysis, and custom detectors, not only exact keyword or regex matching.
See Strac's catalog of sensitive data elements for examples of data types that can be detected and governed.

You cannot write precise rules for data you cannot see. Use automated sensitive data discovery and classification to answer:
This is where DSPM and DLP should work together. DSPM identifies sensitive data at rest and posture risks such as excessive access or unsafe sharing. DLP governs what happens when the same data is copied, uploaded, shared, prompted, downloaded, or transferred.
Endpoint data lineage adds valuable context by showing where a sensitive file originated and how it moved across applications, devices, and destinations. That context can separate a legitimate workflow from a suspicious exfiltration attempt.
Set handling requirements for each classification and channel. Apply least privilege, but do not assume access control alone will prevent data loss. Authorized users can still send data to the wrong recipient, upload it to an unapproved AI tool, or copy it to a personal device.
Rules should cover:
For example, the policy might allow customer names in an approved enterprise AI assistant but block PHI, payment card data, and authentication secrets from every public GenAI tool.
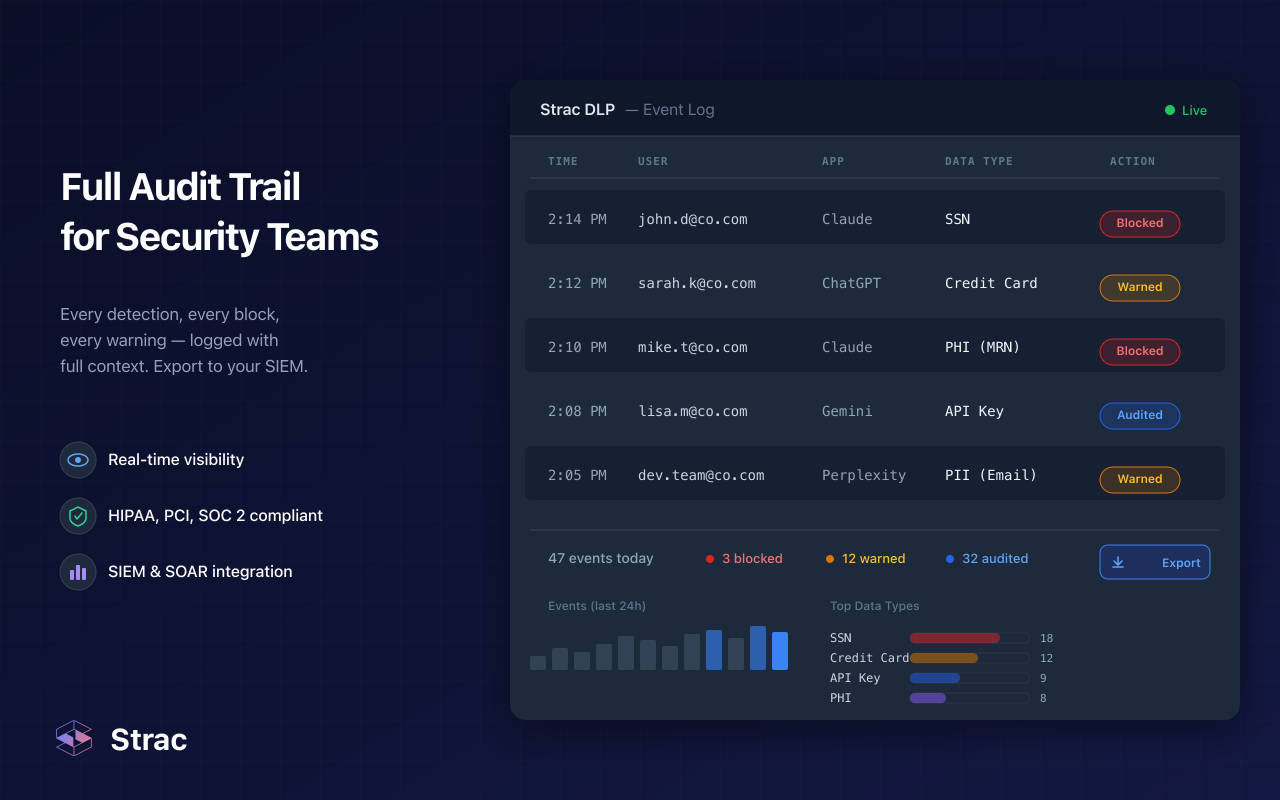
“Do not share restricted data” is not an enforceable technical policy. Define what the DLP system should do when it detects a specific data type in a specific channel.
Common actions include:
Granular actions are usually more effective than blanket blocking. A support team may need the rest of a Zendesk ticket even when a customer accidentally submits a credit card number. Inline redaction removes the card data while preserving the usable conversation.
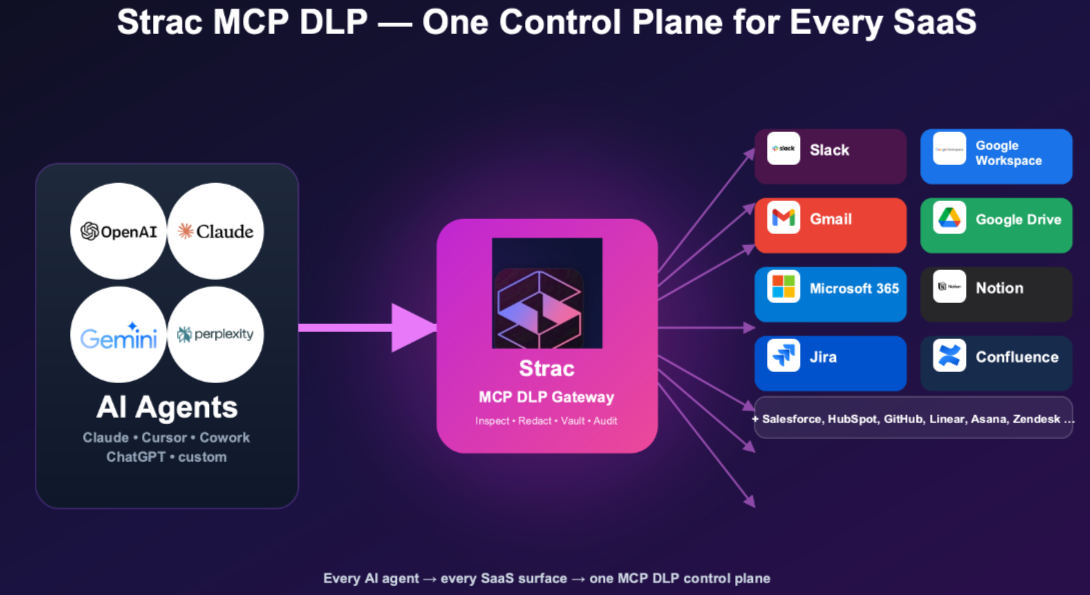
AI-specific controls can no longer be an appendix to an acceptable-use policy. They need to be part of the core DLP program.
The policy should define:
MCP deserves specific attention because it allows AI systems to interact with tools and business data. A model may be approved, but a connected MCP server can create a new path between that model, a sensitive repository, and an external destination. MCP DLP should inspect data entering and leaving these workflows and apply policy before sensitive information reaches the wrong model, tool, or user.
Shadow AI controls should also identify and govern unsanctioned tools accessed through the browser. Blocking every unknown service may be impractical; organizations can combine discovery, risk-based warnings, and data-aware blocking.
A DLP policy is cross-functional. Assign clear ownership to:
Some business workflows will require exceptions. A controlled exception process should document:
Permanent, undocumented exceptions are policy debt. Review and retire them regularly.
Define what happens after a DLP event, including:
Not every alert is an incident. Context and data lineage help analysts prioritize genuine risk instead of investigating isolated matches with no understanding of origin or intent.
Begin in audit mode to learn where sensitive data lives and how teams use it. Use the findings to correct exposed data, establish baselines, and identify high-risk destinations before activating restrictive controls.
Do not attempt to enforce every rule on day one. Start with highly regulated or exploitable data such as payment cards, PHI, government IDs, credentials, secrets, and large customer-data exports. Protect the channels where exposure is most likely, including email, support tools, browsers, GenAI, endpoints, and cloud drives.
Redaction, masking, encryption, and coaching can reduce risk while preserving the workflow. Reserve blocking for actions that cannot be made safe or destinations outside the organization's risk tolerance.
Test text, files, images, screenshots, spreadsheets, archives, and custom data. Validate both positive detection and allowed activity. A policy that catches a test credit card number but misses the same number in a scanned attachment is incomplete.
Useful metrics include:
Review controls when the company adopts a new SaaS platform, AI model, agent, MCP server, acquisition, data type, or regulatory obligation. Annual review is the minimum, not the only trigger.
Strac is a modern data security platform that combines DSPM and DLP across SaaS, cloud, GenAI, browsers, endpoints, email, APIs, and MCP-connected workflows. It helps security teams move from finding sensitive data to automatically acting on it.
Strac discovers PII, PHI, PCI data, secrets, credentials, and confidential information across structured and unstructured content. Built-in and custom detectors support company-specific policies, while ML, document inspection, OCR, and image detection extend coverage beyond plain text.
Strac can apply controls across SaaS applications, cloud environments, browsers, endpoints, GenAI tools, email, support systems, and custom applications through integrations and APIs. This gives security teams a consistent policy layer across channels that are otherwise managed in silos.
Depending on the channel and risk, Strac can audit, warn, block, redact, mask, quarantine, delete, or encrypt sensitive data. Inline remediation can remove the risky data while allowing the safe part of a business workflow to continue.
Strac helps govern sensitive data submitted to AI websites and applications, including prompts, responses, and file uploads. MCP DLP extends policy enforcement to agent and tool interactions so sensitive data can be inspected before it crosses a boundary between enterprise systems, models, connectors, and external tools.
Endpoint DLP applies data-aware controls to endpoint channels, while data lineage helps teams understand a file's origin and movement. Policies can be tailored by data type and channel, allowing an organization to audit one action, warn on another, and block a genuinely dangerous transfer.
Strac helps organizations implement technical controls relevant to PCI DSS, SOC 2, HIPAA, ISO 27001, CCPA, GDPR, and NIST. DLP does not create compliance by itself, but discovery, enforcement, logging, and remediation provide important safeguards and audit evidence.
Organizations can deploy Strac as SaaS, self-hosted, or in a hybrid model based on security, data residency, and operational requirements. Centralized policy and reporting also help teams manage multiple workspaces and business environments without rebuilding the program for every application.
A data loss prevention policy is effective only when its rules can follow sensitive data across the places it is stored, used, and moved. In 2026, that means protecting not only email and endpoints, but also SaaS, cloud, browsers, GenAI, AI agents, MCP connections, APIs, files, attachments, and images.
The strongest programs pair clear governance with continuous discovery and precise enforcement. Strac brings DSPM, DLP, advanced detection, data lineage, and inline remediation together so organizations can reduce sensitive data exposure without unnecessarily blocking productive work.
A data loss prevention policy should define sensitive data types, classification levels, approved storage and sharing methods, access rules, technical controls, incident response procedures, and exception management. In 2026, it should also cover SaaS apps, cloud storage, endpoints, browsers, GenAI tools, AI agents, APIs, and MCP connections.
Start by discovering where sensitive data lives and how it moves across your organization. Then classify the data, define who can access it, set handling rules by channel, and assign actions such as audit, warn, redact, block, quarantine, or encrypt. Test policies in audit mode first, then refine enforcement based on real business workflows.
A DLP policy is the set of business and security rules that explain how sensitive data should be handled. DLP software enforces those rules by discovering, detecting, monitoring, and remediating risky data activity. A strong program needs both: the policy defines the standard; the technology applies it across real workflows.
Employees and AI agents can move sensitive data through prompts, file uploads, AI responses, APIs, and MCP-connected tools. Without AI-specific DLP controls, PII, PHI, PCI data, credentials, and confidential files can be exposed to unapproved models or external services. A modern DLP policy should define approved AI tools, permitted data types, and enforcement actions for risky prompts, agent activity, and MCP tool calls.
Strac combines DSPM and DLP to discover, classify, and protect sensitive data across SaaS, cloud, browsers, endpoints, email, GenAI, APIs, and MCP workflows. Its advanced detection can identify sensitive text, documents, files, images, and custom data types, then apply actions such as redaction, masking, blocking, quarantine, deletion, encryption, warnings, or audit logging.







