September 25, 2026

7
min read
Critical Capabilities for Enterprise Data Loss Prevention
Critical capabilities for enterprise data loss prevention: see sensitive data on every surface, detect it accurately, and redact it automatically with Strac.
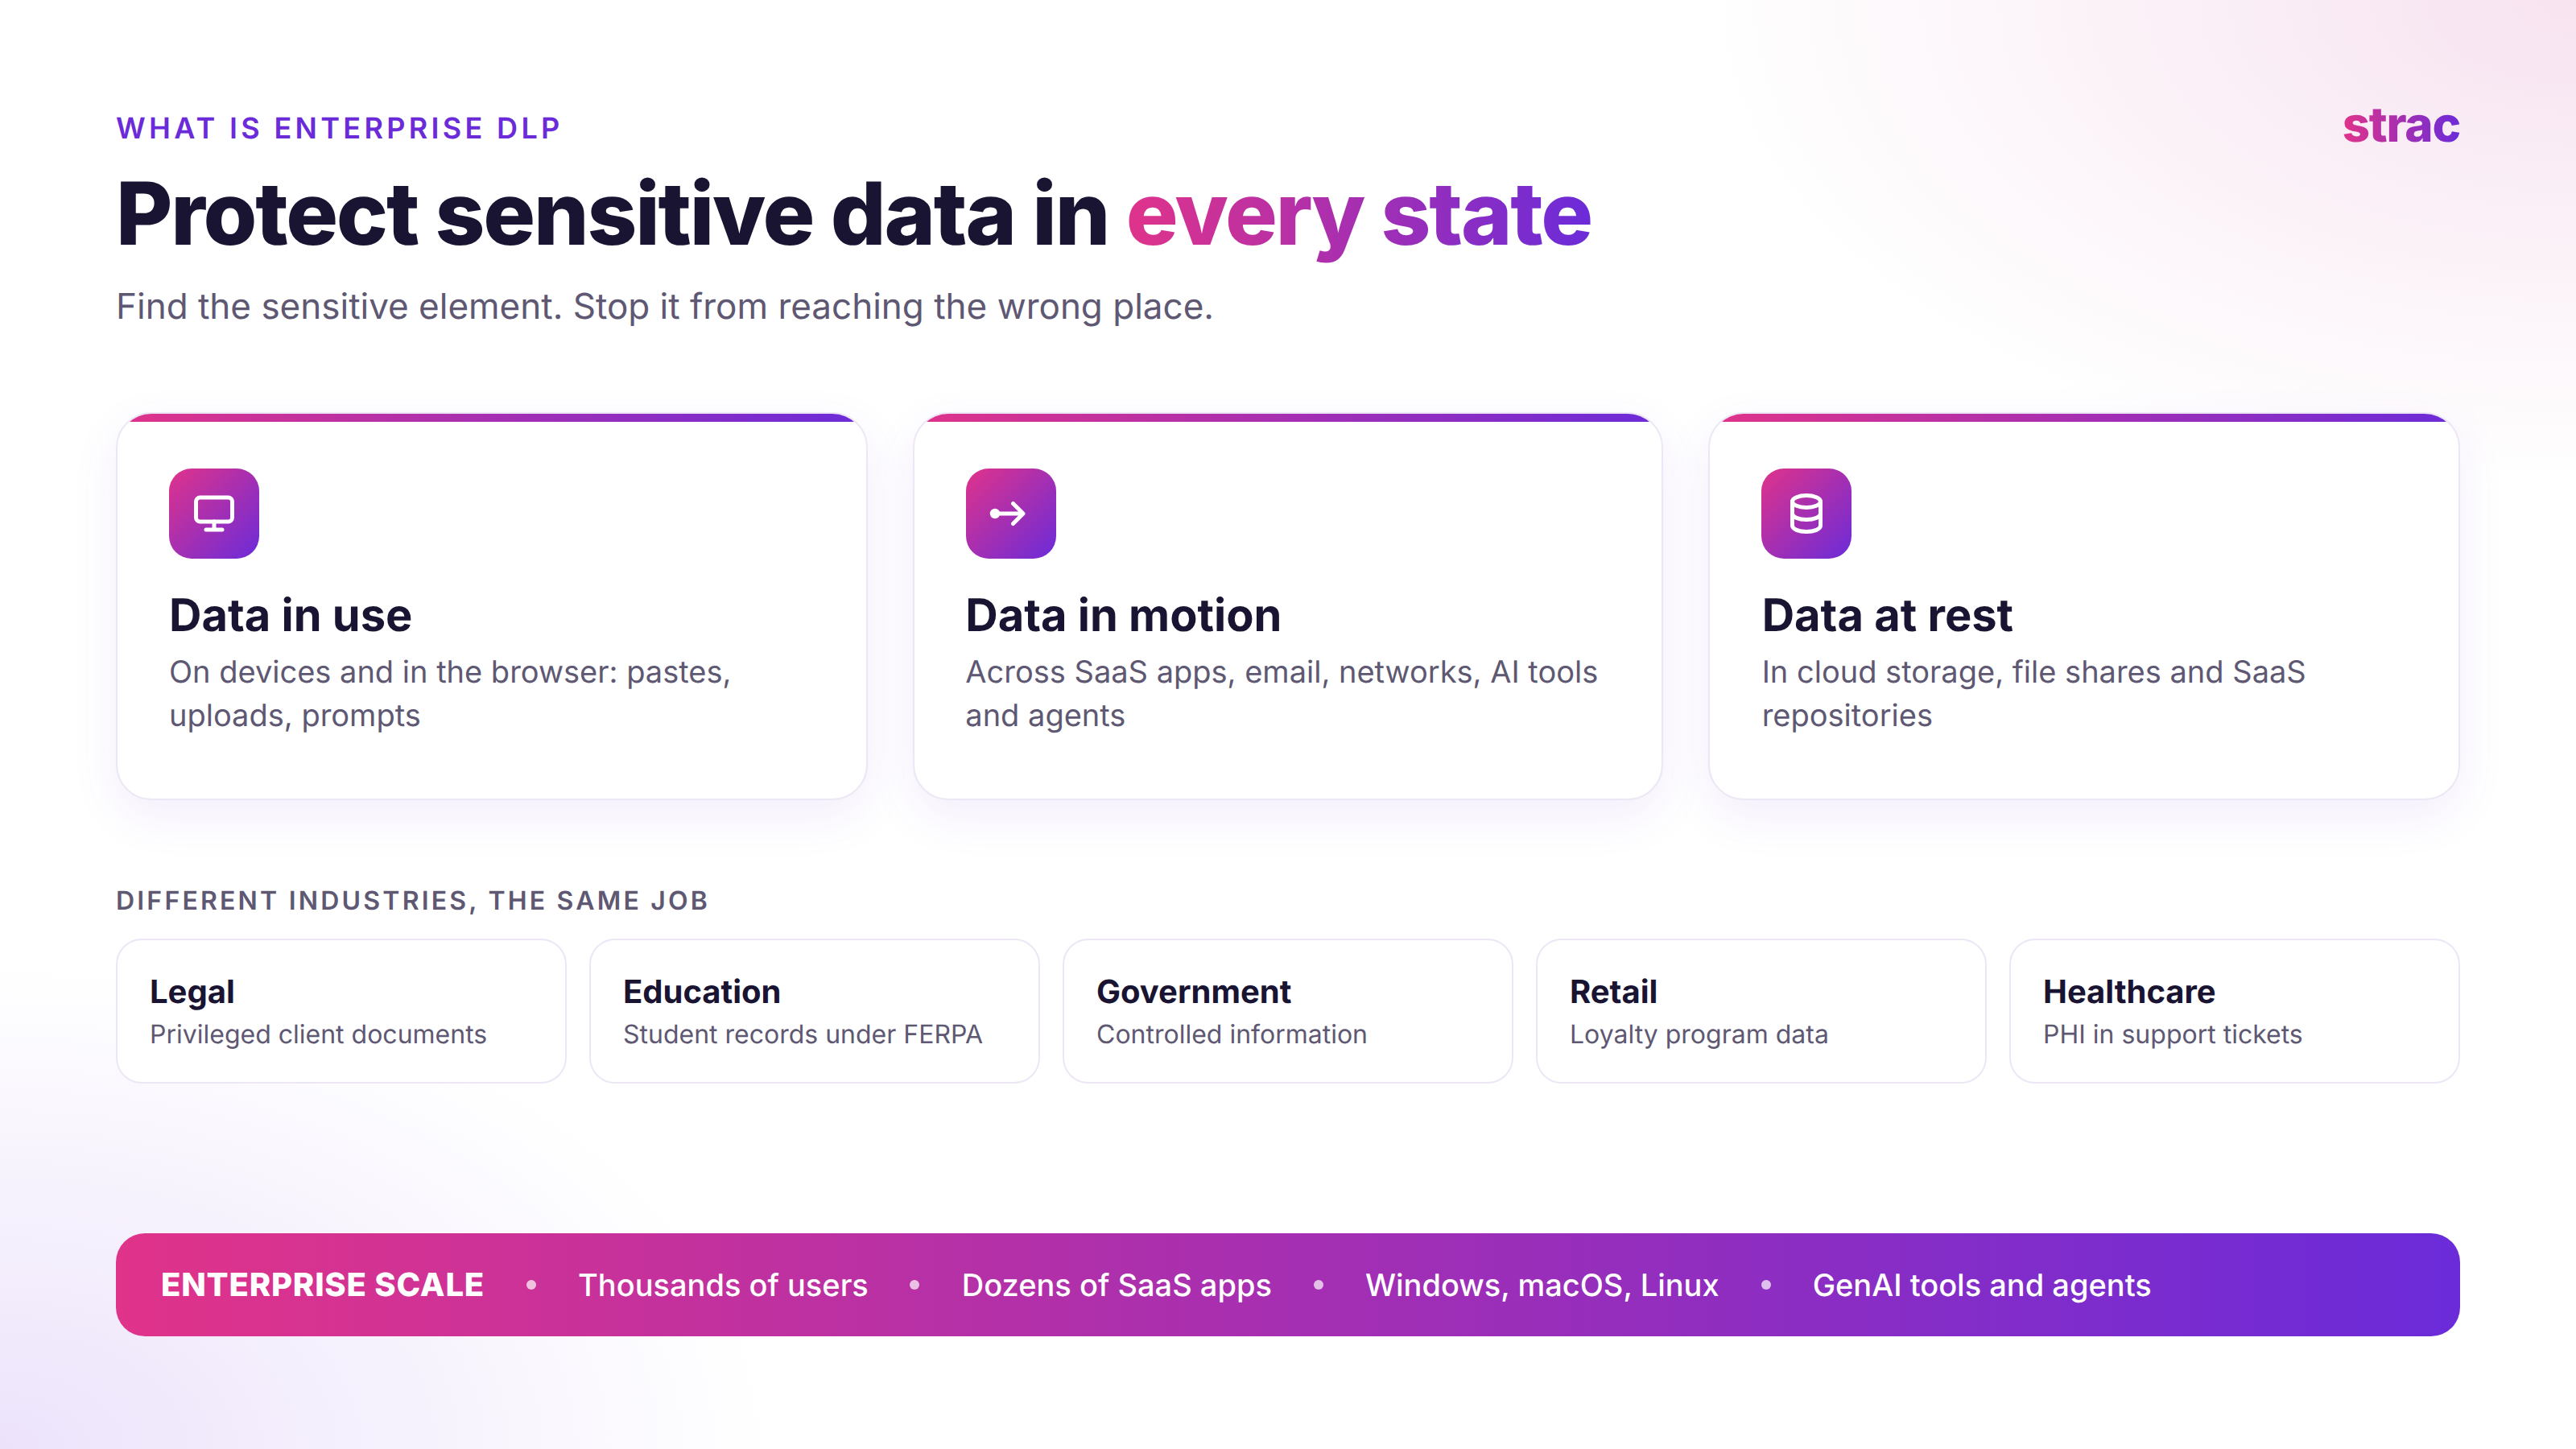
Enterprise data loss prevention is a strategy and a platform for ensuring sensitive data is not lost, misused, or accessed by people who should not have it. It identifies, monitors and protects data in three states: in use on a device or in a browser, in motion across apps and networks, and at rest in storage and SaaS.
The use cases look different by industry and identical underneath. A law firm keeps privileged client documents from being shared outside the matter team. A university protects student records under FERPA. A government agency keeps controlled information inside approved systems. A retailer protects loyalty program data, and a healthcare provider keeps PHI out of support tickets. In every case, the job is to find the sensitive element and stop it from reaching the wrong place.
What "enterprise" adds is scale and spread: thousands of users, dozens of SaaS apps, several operating systems, and now generative AI tools and agents that touch the same data.
Four risks drive the requirement, and the fourth is new.
Data breaches. Unauthorized access to customer records, credentials or financial data causes direct cost, notification obligations and lasting reputational damage.
Regulatory non-compliance. GDPR, HIPAA, PCI DSS, CCPA, SOC 2 and ISO 27001 all require you to know where regulated data lives and prove it is controlled.
Intellectual property theft. Source code, product plans and pricing models leak through personal cloud uploads, external shares and departing employees.
AI data leakage. Shadow AI tools appear on managed devices without procurement, and data enters them through a paste. Agents connected over MCP pull raw records into model context in seconds. A network proxy sees an encrypted session to a chat domain; it does not see the patient record inside the prompt.
The first three risks are why DLP exists. The fourth is why most DLP deployments no longer cover the risk.
Score any platform on these ten capabilities before you look at a feature matrix.
A DLP platform is only as strong as its narrowest surface, because that surface becomes the exfiltration path. Enterprise coverage in 2026 means SaaS apps (Slack, Google Drive, Gmail, Microsoft 365, Zendesk, Salesforce, Jira, Notion), cloud storage (AWS S3, Azure, Google Cloud), managed endpoints on macOS, Windows and Linux, the browser, generative AI tools, and MCP servers.
Detection has to read what people actually share. That means trained detectors for PII, PHI, PCI data and secrets, custom detectors for your own identifiers, and OCR that reads screenshots, scanned PDFs, DOCX and spreadsheets. A screenshot of a customer table is still a customer table.
Regex alone floods the queue and teaches people to ignore alerts. Machine learning models, checksum validation and context scoring separate a real card number from a string of digits. A detector that cries wolf is a detector nobody trusts; a precise one is a control people stop fighting.
Daily scans find the leak after it has been read, forwarded and indexed. Enterprise DLP inspects the message as it is posted, the file as it is uploaded, and the prompt as it is submitted, so enforcement happens before the data lands.
Remediation actions should run automatically and in this order:
An alert tells you data leaked. Redaction means it did not.
You cannot protect data you have not found. Sensitive data discovery and classification scans historical content across SaaS and cloud storage, and DSPM flags overexposed files, misconfigured sharing and stale access, then fixes them automatically.
Content classification tells you what a file contains; data lineage tells you where it came from. Persistent fingerprinting follows a file from the source system to every copy, so a renamed export from Salesforce is still treated as customer data when it reaches a personal drive.
Enterprise DLP now has to see which AI tools are in use, which data classes are heading to them, and redact before the prompt is sent. Blocking the domain pushes usage to personal devices and removes visibility entirely. See how to detect shadow AI for the discovery side.
Agents do not just answer questions; they call tools. Every MCP tool response is a data path that can carry raw PII, PHI or secrets into model context. MCP DLP inspects each call and response, redacts sensitive fields, logs activity and flags prompt injection attempts, which is how you protect AI agents without removing their tools.
Policies should be configurable by data class, surface, user group and action, with built-in templates for PCI DSS, HIPAA, GDPR and CCPA. Evidence should map to each framework without a rebuild per audit. And deployment should be API-first, measured in minutes, with a clear dashboard and a developer API for custom pipelines. Appliances and kernel agents that take a quarter to deploy leave a quarter of exposure behind them.
Most legacy suites were designed around three chokepoints: the mail gateway, the network egress point and the file server. They are deep on the surface they started on and thin everywhere else.
The gaps show up in predictable places. A card number posted in a Zendesk ticket stays there until someone deletes it by hand. A screenshot of a spreadsheet passes text-only detection. A prompt travels inside an encrypted browser session the proxy cannot read. An MCP response carries a full customer record to a model that needed one field. And detection without remediation turns into an alert queue nobody clears. For the AI side of this argument, read why legacy DLP fails for AI.
Strac is a DLP, data discovery and DSPM platform that maps directly to the ten capabilities above, from one console and one policy set. One policy, three surfaces: Strac removes the sensitive element and leaves the work intact, which is what makes enforcement survivable for the people doing the work.
SaaS and email. SaaS DLP connects by API to Slack DLP, Google Drive DLP, Gmail DLP, Office 365 DLP, OneDrive DLP, Zendesk DLP, Salesforce DLP, Jira DLP, Box DLP, Notion DLP, Intercom DLP and HubSpot DLP. It redacts, masks, labels, deletes and revokes sharing in place. The full list lives on the integrations page.
Endpoint and browser. Endpoint DLP covers Windows, Mac DLP and Linux DLP, watching USB transfers, uploads and clipboard activity. Browser DLP in Chrome and Edge inspects pastes, uploads and form submissions at the moment of the action. Strac keeps no keystroke logs or screenshots.
Generative AI and MCP. AI DLP and ChatGPT DLP redact sensitive data before it reaches ChatGPT, Claude, Gemini or Copilot, with dashboards showing which tools are in use. MCP DLP inspects every agent tool call, redacts PII, PHI and secrets, logs activity and flags prompt injection.
Detection, discovery and lineage. The PII scanner reads PDFs, DOCX, XLS, PNG and JPEG through OCR, with built-in detectors for PCI, HIPAA and GDPR data plus custom detectors. Strac scans SaaS, AWS S3, Azure and Google Cloud at rest, runs DSPM to remediate posture risks, and applies data lineage through persistent fingerprinting. Data masking protects fields inside your own systems, and the API docs let developers redact inside their applications.
Compliance. Controls map to HIPAA, PCI DSS, SOC 2, ISO 27001, CCPA and GDPR, and SaaS connectors deploy in minutes rather than quarters.
Other platforms tell you where sensitive data went; Strac changes what arrives there.
A longer operational version lives in the DLP security checklist.
👉 Related reading:
Coverage, accuracy and real-time enforcement are the entry ticket; automated remediation is what turns them into protection. Identity, network and endpoint controls all fail eventually, and the data layer is the backstop: redact sensitive data on every action across SaaS, cloud, endpoint, browser, generative AI and MCP, and a compromise never becomes a breach.
No. DSPM finds sensitive data at rest and fixes risky posture such as public links and stale access. DLP enforces policy as data moves. Enterprise programs need both, which is why Strac runs DLP and DSPM on the same detectors and policy set.
Because it was designed for email, network and file channels. Prompts travel inside encrypted browser sessions, and MCP responses travel between an agent and a tool; neither passes through the chokepoints legacy DLP was built to inspect. Coverage has to sit at the browser and the tool call.
Not when remediation defaults to redaction and vaulting. The sensitive element is removed and the message, ticket or prompt goes through, so people keep working. Blocking is reserved for the few data classes and destinations that can never be allowed.
No. Every detector has a false negative rate, and people find new channels. That is why the data layer matters: when remediation defaults to redaction on every action, whatever escapes a missed control is already stripped of its sensitive parts.
Automated remediation across every surface, because coverage without action produces an alert queue and action on one surface moves the leak to another. For the AI side of the program, start from the AI data governance pillar.