The Ultimate Guide to Checkpoint Data Loss Prevention
Discover how Checkpoint Data Loss Prevention protects sensitive information, ensures compliance and mitigates insider threats with Strac's comprehensive and modern DLP solutions.
· Checkpointdata loss prevention is the practice of inspecting and controlling sensitivedata at defined control points, so that a file, a message, a paste or an APIcall is checked before the data leaves.
· The checkpoints moved. Data now leaves through abrowser tab, a personal AI assistant, a synced folder, or an agent calling atool over Model Context Protocol (MCP), and none of those cross the old networkchokepoint.
· Network-era gateways still inspect traffic theycan see, but they cannot read an encrypted paste into a chat box, a screenshotdropped into a ticket, or a tool response an agent hands back to a model. Thatis why legacy DLP fails forAI.
· Strac places the checkpoint at the data itself:discovery and redaction across endpoint DLP, SaaS, cloud, browser, AI DLPand MCP DLP, with automated remediation on everyhit.
· CheckpointDLP is one layer of a wider program. Start from the pillar on AI data governance.
What Is Checkpoint Data Loss Prevention?
Checkpoint data loss prevention is a control model: pick the points where sensitive data can move, inspect what passes through them, and act before the data lands somewhere it should not. A checkpoint is a decision point, not a product.
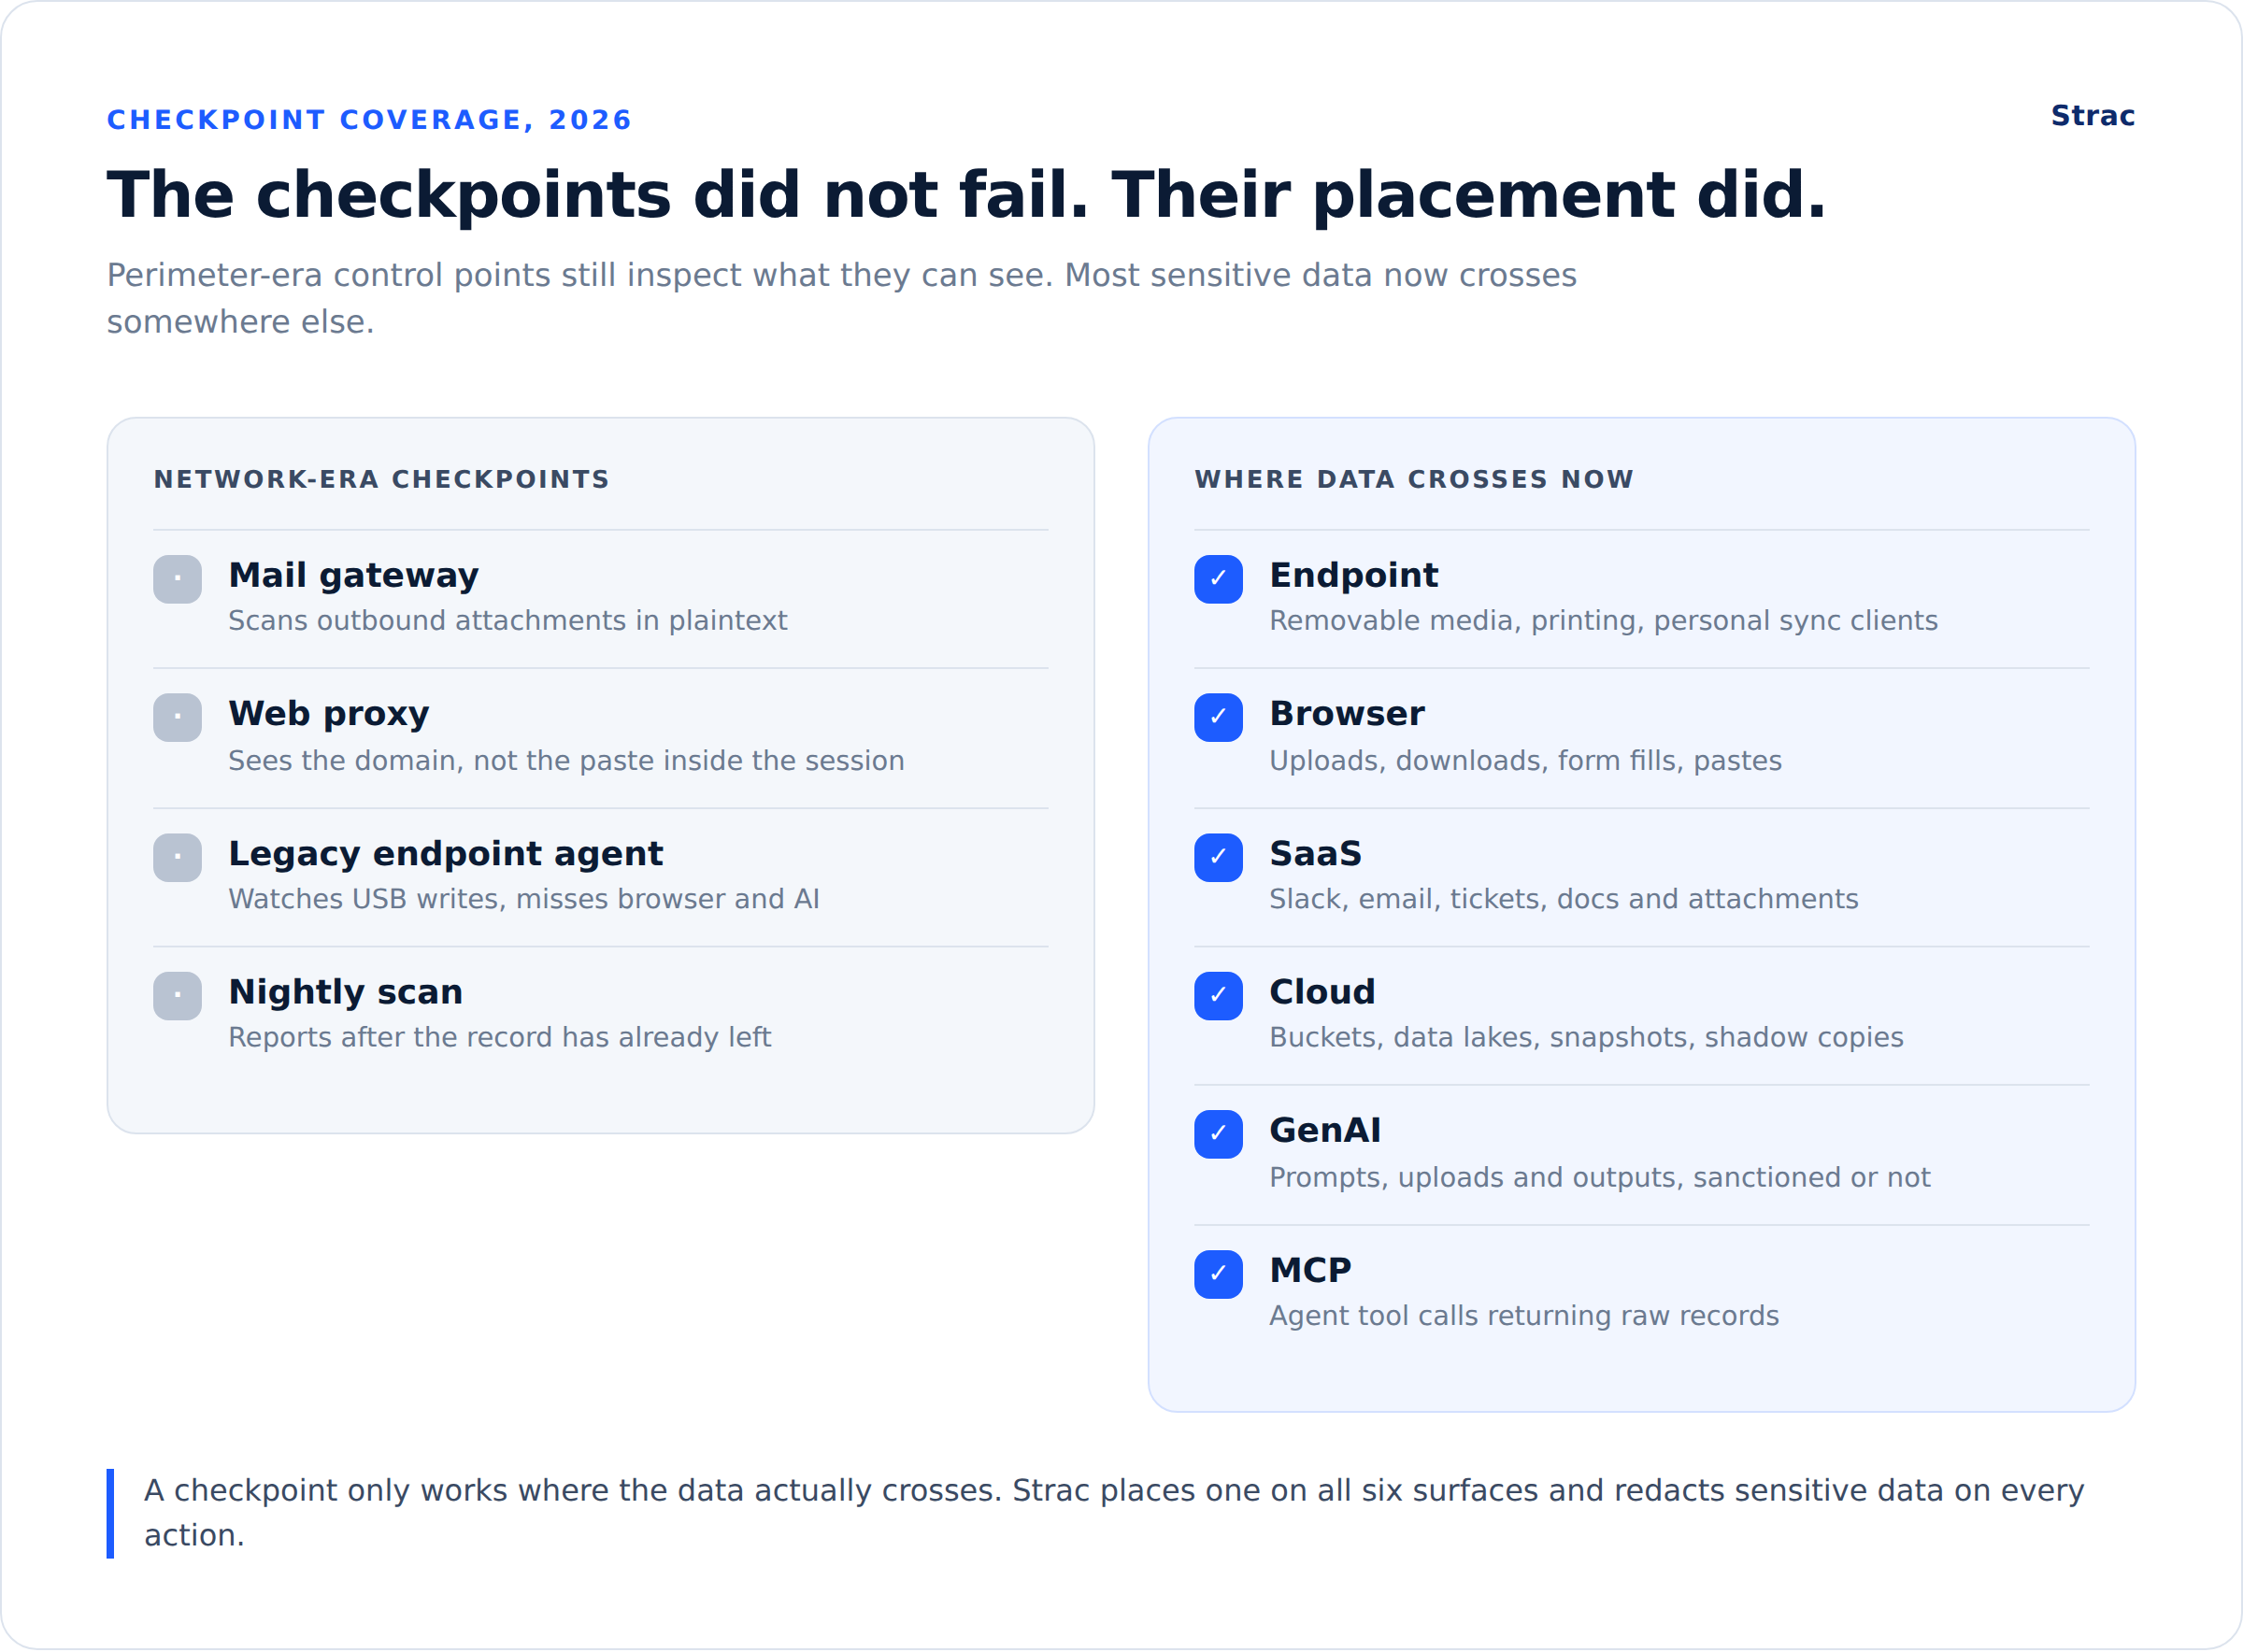
Classic checkpoints were network-shaped. Mail gateways scanned outbound attachments. Web proxies inspected uploads. Agents on managed laptops watched USB writes. Each one sat on a path, and every path ran through the corporate perimeter.
The model is sound. The placement is what aged. A checkpoint only works where the data actually crosses, and in 2026 most sensitive data crosses in places the perimeter never sees.
✨ Where the Checkpoints Sit in 2026
Six surfaces now carry the traffic that used to run through a gateway:
Endpoint. Files copied to removable media, synced to personal cloud drives, printed, or dragged into an unmanaged app.
Browser. Uploads, downloads, form fills and pastes into any web app, sanctioned or not.
SaaS. Slack messages, email, tickets, docs, spreadsheets and their attachments, shared internally and externally.
Cloud. Object stores, buckets, data lakes and snapshots holding data nobody has inventoried.
GenAI. Prompts, uploads and outputs across every assistant an employee can reach, including the ones nobody approved. That is Shadow AI.
MCP. Agent tool calls, where a model asks a connected system for data and receives raw records in reply.
A perimeter checkpoint sees a fraction of that. An analyst pasting a customer export into a free summarizer does not touch the mail gateway. An agent pulling a support ticket over MCP does not touch the proxy.
Why Network-Era Checkpoints Miss Modern Data Flows
Three gaps show up in almost every assessment.
Encryption and structure. A gateway can classify a plaintext attachment. It cannot read a customer record pasted character by character into a chat box, or a Social Security number sitting inside a screenshot dropped into a ticket. Detection has to happen where the content is rendered, which means the endpoint and the browser.
Identity that is not a person. Agents and service accounts act continuously and at machine speed. A checkpoint that authorizes by user session has nothing to hold onto when a non-human identity (NHI) makes the request.
Speed. A paste exfiltrates a customer record in one second. Nightly scanning tells you what happened; an inline checkpoint decides what happens.
Legacy checkpoints tell you a breach occurred. Data-layer checkpoints stop the data from being readable in the first place.
✨ What an Ideal Checkpoint DLP Solution Needs in 2026
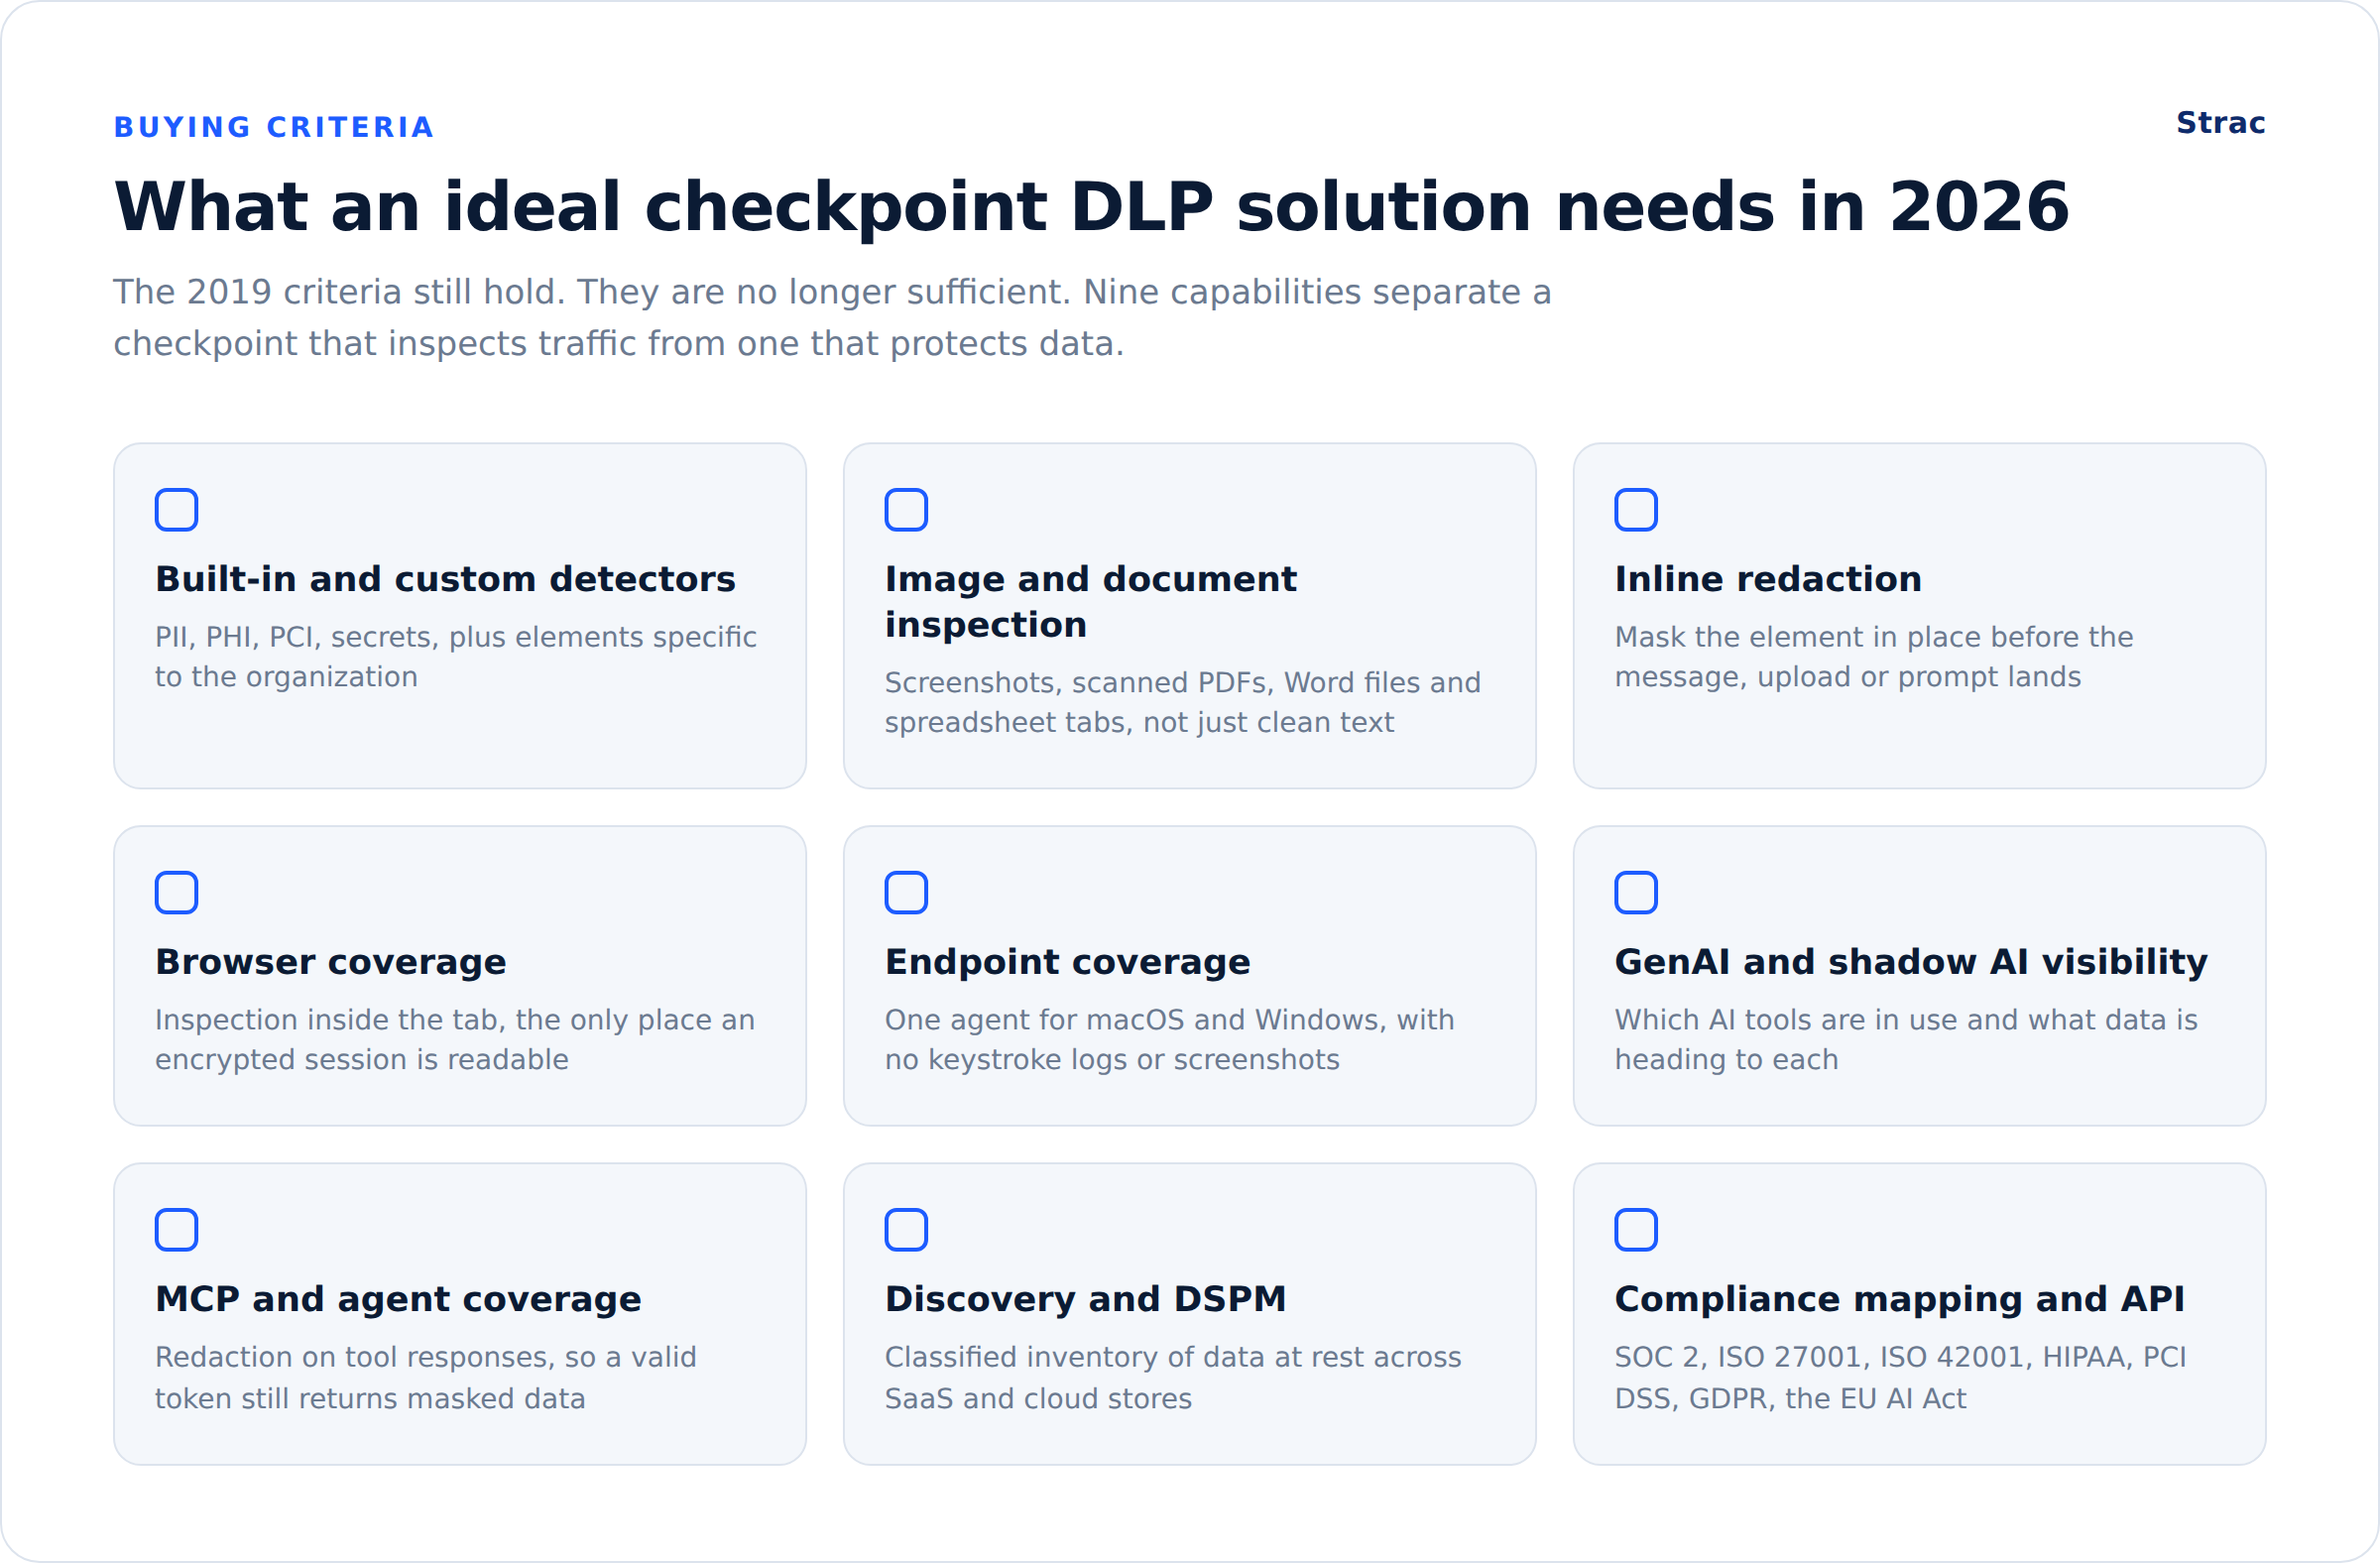
The 2019 buying criteria (built-in detectors, compliance templates, easy integration) still hold. They are no longer sufficient. Use this as the current bar:
Show Image
Nine capabilities separate a checkpoint that inspects traffic from one that protects data.
Two of those deserve a note. Image and document inspection matters because sensitive data increasingly travels as a screenshot, a scanned PDF or a spreadsheet tab rather than as clean text. MCP coverage matters because an agent with a valid token is an authorized user by every other control in the stack, and only the data layer can decide what the agent is allowed to receive.
✨ How Inspection and Redaction Work at Each Checkpoint
Strac inspects content at the moment of the action, not on a schedule. The sequence is the same on every surface:
Discover. Scan the store or intercept the action, and classify what is there: PII, PHI, payment data (PCI), credentials and secrets, and any custom element the organization defines.
Decide. Match the finding against policy, scoped by user, group, destination and data class.
Act. Apply remediation inline, before the message posts, the file uploads, the prompt sends or the tool response returns.
Strac detects and redacts sensitive data in real time, which is the backstop when identity, network and model controls fail.
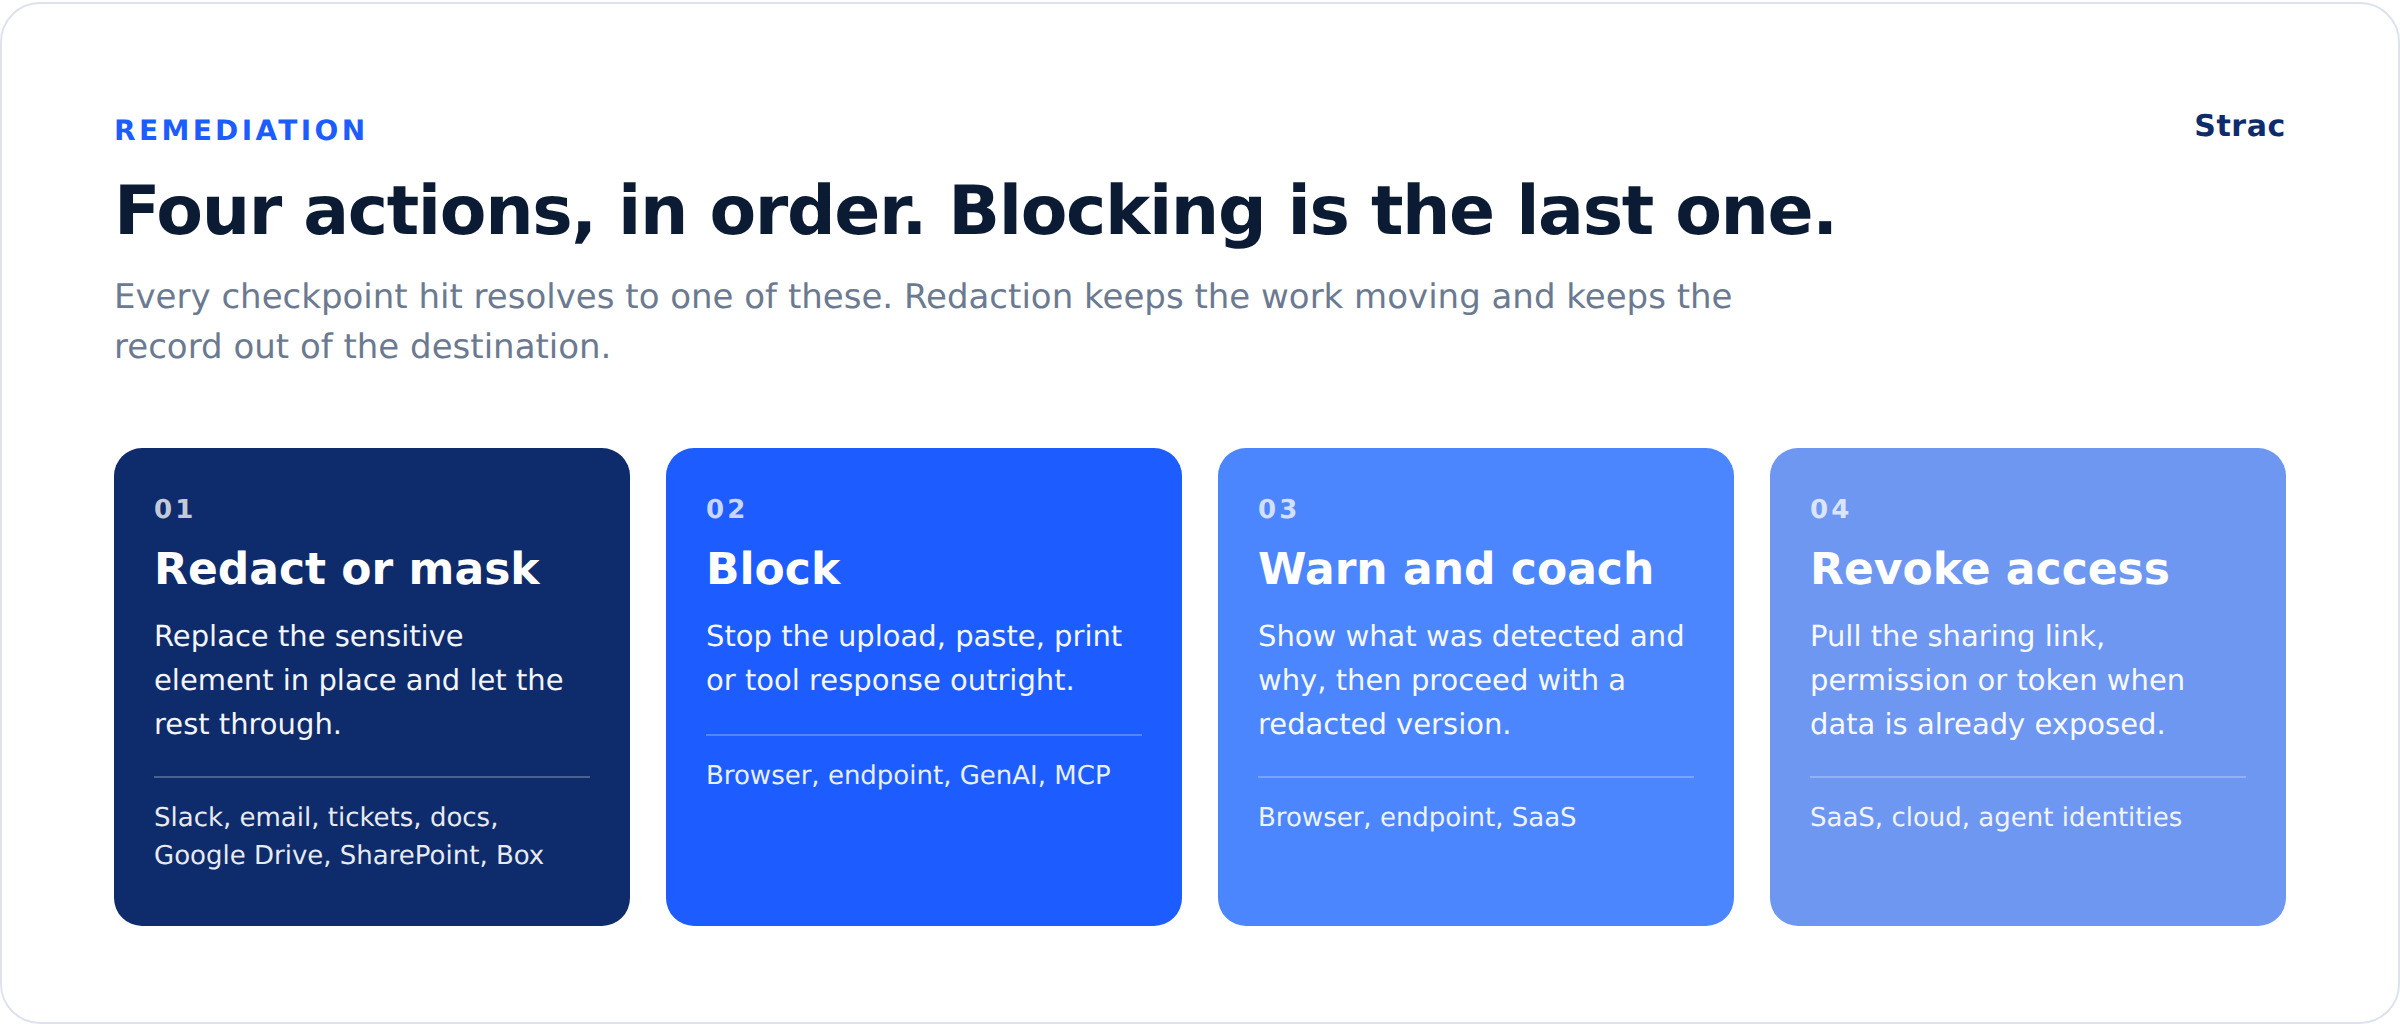
Remediation is always one of four actions:
Redact or mask. Replace the sensitive element in place and let the rest of the message or file through, on Slack, email, tickets, docs, Google Drive, SharePoint and Box.
Block. Stop the upload, paste, print or tool response outright when the data class and destination combination is never acceptable.
Warn and coach. Show the user what was detected and why, then let them proceed with a redacted version. This is where policy becomes training.
Revoke access. Pull the sharing link, the file permission or the token when data is already exposed.
🎥 Strac: Checkpoint DLP Across Every Surface
Strac is a Data Loss Prevention (DLP), Data Discovery and Data Security Posture Management (DSPM) platform, and it places a checkpoint on each surface where data moves:
Endpoint DLP covers macOS and Windows devices: removable media, printing, personal sync clients and unmanaged apps, from one agent that syncs policy roughly every 30 seconds and keeps no keystroke logs or screenshots.
Browser DLP inspects uploads, downloads and pastes in the tab itself, which is the only place an encrypted web session is readable.
SaaSDLP connects to the systems the business actually runs on, including Slack DLP and Google Workspace DLP, and redacts inside messages, attachments and shared documents.
Cloud and DSPM discover and classify data at rest across buckets and stores, then flag exposure by posture rather than by alert volume.
AI DLP governs prompts, uploads and outputs across sanctioned assistants and the unsanctioned ones, which is how Shadow AI becomes visible and controllable instead of merely forbidden.
MCP DLP sits on agent tool calls and redacts sensitive data in the response, so a hijacked or over-permissioned agent receives a masked record rather than a raw one.
Detection runs on models trained on PII, PHI, PCI and confidential content, including images, screenshots, PDFs, Word files and spreadsheets, with custom detectors for organization-specific elements. An API exposes the same detection and redaction to internal applications. Compliance mapping covers SOC 2, ISO 27001, ISO 42001, HIPAA, PCI DSS, GDPR and the EU AI Act.
A 90-Day Checkpoint Rollout
Days 0 to 30, discover. Connect SaaS and cloud stores, deploy the endpoint agent to one department, and turn on monitoring only. Produce an inventory of data classes by surface and a list of the AI tools in use.
Days 30 to 60, protect. Enable redaction on the two highest-volume surfaces (usually Slack and email), add browser coverage for uploads and pastes, and switch the top three data classes from monitor to warn and coach.
Days 60 to 90, prove and scale. Extend to MCP DLP for agent traffic, move warn-and-coach classes to redact, and report on incidents prevented, mean time to remediate, and coverage by surface.
The checkpoint model is still right; the 2019 map of where to put the checkpoints is not. Identity, network and model controls all fail eventually, and when they do the only thing standing between a compromise and a breach is whether the data itself was readable. Strac places that control at the data layer across endpoint DLP, SaaS, cloud, browser, AI DLP and MCP DLP, and redacts sensitive data on every action. Book a demo to see checkpoint DLP running on the surfaces your data actually crosses.
🌶️ Spicy FAQs for Checkpoint Data Loss Prevention
Is checkpoint DLP the same as network DLP?
No. Network DLP is one checkpoint, placed at the egress. Checkpoint DLP is the broader model of inspecting data wherever it moves, which in 2026 means the endpoint, browser, SaaS, cloud, GenAI and MCP as well as the network.
Because the gateway sees an encrypted session to an allowed domain and nothing else. It cannot read the paste, the uploaded file or the model's response. Inspection has to happen in the browser and on the endpoint, which is what AI DLP does.
Does adding checkpoints slow employees down?
No, when the default action is redaction rather than blocking. The message posts, the file uploads and the prompt sends; the sensitive element is masked on the way through. Blocking is reserved for combinations that are never acceptable.
Can checkpoint DLP stop a determined insider?
Not entirely. Someone can photograph a screen, and no data control reaches that. What checkpoint DLP does is remove the easy, high-volume paths and make the remaining ones slow, manual and visible in the audit trail.
Where does checkpoint DLP fit in an overall data security program?
It is the enforcement layer. Discovery and DSPM tell you where sensitive data lives, identity controls decide who may reach it, and checkpoints decide what actually leaves. See AI data governance and MCP DLP for the full picture.
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.