September 16, 2026

9
min read
The Role of a DLP Engineer
A DLP engineer builds and tunes the controls that stop sensitive data leaving. Inside the role in 2026: day-to-day work, skills, salary bands and career path.
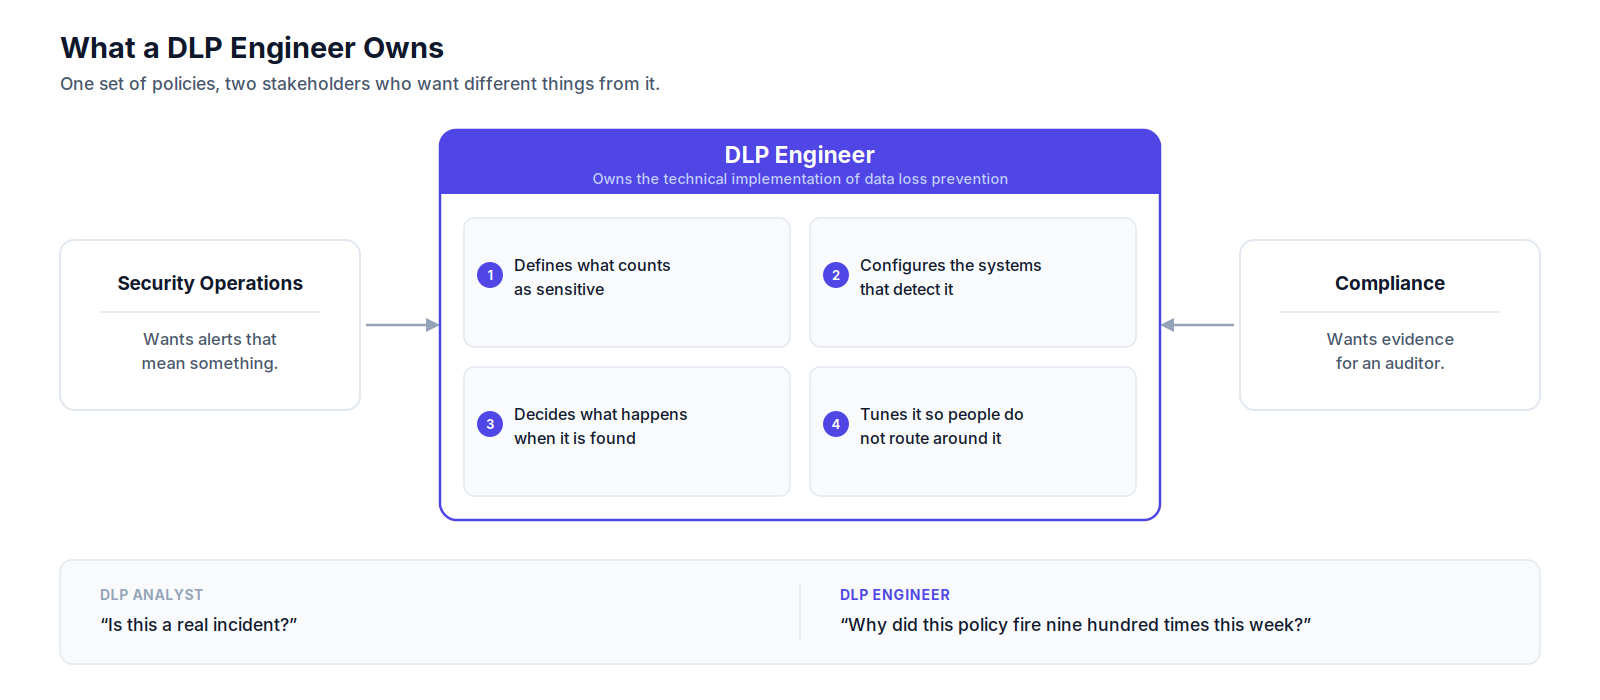
A DLP engineer, sometimes titled data loss prevention engineer or data protection engineer, owns the technical implementation of data loss prevention inside a company. They decide what counts as sensitive, configure the systems that detect it, choose what happens when it is found, and keep the whole thing accurate enough that people do not route around it.
The role sits between security operations and compliance. Security operations wants alerts that mean something. Compliance wants evidence for an auditor. The DLP engineer is the person who has to satisfy both with the same set of policies.
It is usually a mid career move rather than a first job. Most people arrive from a security analyst, SOC, endpoint administration or systems engineering background, because the work assumes you already know how endpoints, identity and SaaS administration behave before you start writing detection logic on top of them.
A quick disambiguation, because the titles get used loosely. A DLP analyst triages alerts the system produces. A DLP engineer builds and tunes the system that produces them. The analyst answers "is this a real incident." The engineer answers "why did this policy fire nine hundred times this week."
Job descriptions list the same seven responsibilities everywhere. The honest version of the DLP engineer job description is narrower and more repetitive.
Tuning policies. The largest share of the week. A rule fires on test data, on a template file, on an internal document that happens to contain a number shaped like a card. Each of those is an investigation and a policy change.
Triaging what the system flagged. Not every alert goes to the SOC. The engineer filters, and the filtering criteria are themselves a deliverable.
Onboarding new data sources. A team adopts a new SaaS tool, a new repository, a new storage bucket. It arrives uncovered and someone has to bring it into scope.
Building detection for the organization's own data. Generic detectors find card numbers and social security numbers. Nobody ships a detector for your internal customer ID format or your proprietary schema. That is custom work.
Producing evidence. Reports showing what was found, what was remediated, and who approved an exception, in the shape an auditor for SOC 2, ISO 27001, HIPAA, PCI DSS or GDPR will accept.
Absorbing exception requests. A team says the policy is blocking legitimate work. Sometimes they are right. Deciding which is which, repeatedly, is the political half of the job.
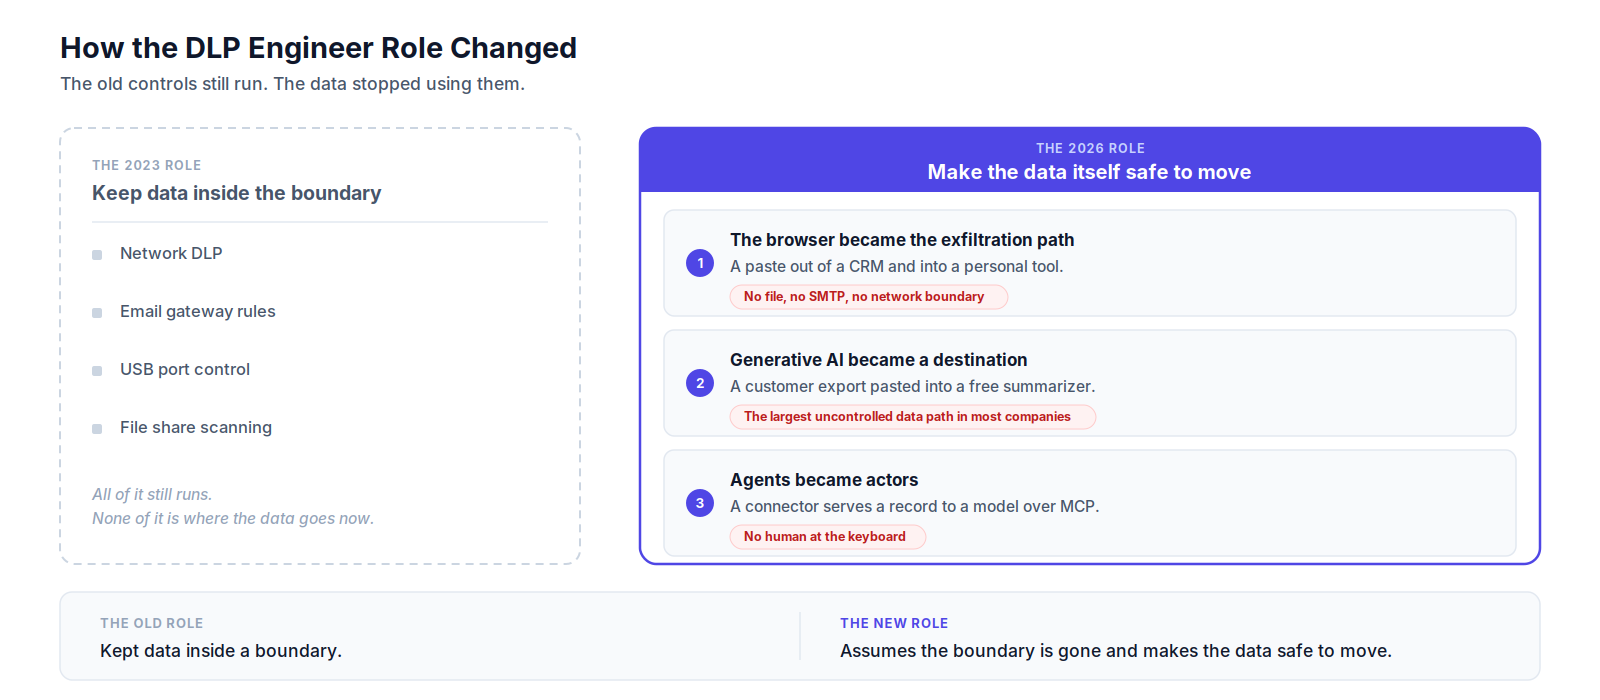
Most DLP engineer job descriptions still in circulation describe a job that mostly stopped existing. They ask for network DLP experience, email gateway rules, USB port control and file share scanning. All of that still runs. None of it is where the data goes now.
Three shifts rewrote the role.
The browser became the exfiltration path. Work happens in tabs. A paste out of a CRM and into a personal tool touches no file, no SMTP server and no network boundary, so the classic stack never sees it. Browser coverage is now a named requirement rather than a nice to have.
Generative AI became a destination. An analyst pasting a customer export into a free summarizer is not an attacker. It is an ordinary employee moving faster than policy, and it is the single largest uncontrolled data path in most companies. A DLP engineer in 2026 is expected to discover which AI tools are in use, which is the shadow AI problem, and to inspect prompts before they leave the device, which is AI DLP.
Agents became actors. A connector exposes a helpdesk, a repository or a warehouse to a model over the Model Context Protocol, and the tool response carries whatever the record contained. The engineer now has to inspect a data path with no human at the keyboard.
Here is the antithesis worth putting in your own job description. The old role kept data inside a boundary; the new role assumes the boundary is gone and makes the data itself safe to move. That is why why legacy DLP fails for AI is worth reading before you plan a stack refresh.
The technical baseline is not the hard part, and it is fairly stable:
The skills that separate people are softer and rarer. The ability to say no to an exception request and keep the relationship. The instinct to measure a policy before enforcing it. The willingness to run in monitor mode for two weeks when everyone wants enforcement on Monday.
And the judgment to pick redaction over blocking. Blocking creates tickets and workarounds. Redaction keeps work flowing and removes the value anyway. Engineers who learn that early have much quieter quarters.
Public salary aggregators disagree, mostly because some report base pay and others report total compensation. Taken together they put the United States market roughly here:
Reported averages cluster between roughly $128,000 and $155,000 depending on the source and on whether bonus and equity are included.
Three things move the number materially. Financial services and healthcare pay a premium, because the regulatory exposure is larger. Roles requiring a security clearance pay a premium. And candidates who can demonstrate browser, generative AI and MCP coverage experience are currently scarce enough to negotiate well, because most of the available talent pool was trained on the network era stack.
There is no single entry path and no universally required certification. The common route looks like this.
Start adjacent. Security analyst, SOC analyst, endpoint or systems administrator, or IT operations with a security lean. You need the operational grounding first.
Get hands on a platform. This is the real gate. Hiring managers want to know you have tuned policies in production, not that you have read about them. Home labs and trial tenants count for more than most candidates assume.
Add certifications selectively. Security+ or GSEC for the foundation, CySA+ or SSCP at the intermediate level, CCSP if your environment is cloud heavy, and a privacy credential such as CIPP if you sit close to compliance. CISSP matters more for advancement into architecture and management than for getting the first DLP role.
Build the 2026 skills deliberately. Prompt inspection, browser coverage and connector security are on very few resumes. Learning them now is the cheapest differentiation available in this job market.
Then advance. The usual next steps are data security engineer, security architect, or manager of a data protection program.
Strac is a Data Loss Prevention (DLP), Data Discovery and DSPM platform covering SaaS, Cloud, Browser, GenAI and MCP, with automated remediation on every surface.
For an engineer, the practical difference is console count. Discovery runs by content across SaaS applications, AWS, Azure and GCP, endpoints, browsers, generative AI tools and MCP connectors, with attachments and screenshots read using optical character recognition rather than judged by file type. Detection covers names, addresses, dates of birth, government identifiers, medical record numbers, card data, API keys and access tokens, and custom detectors are configurable without professional services.
Remediation runs in a fixed order:
Depth on the applications where the work happens is worth checking specifically, starting with Slack DLP and Google Workspace DLP.
Days 0 to 30, discover. Inventory what is already deployed and what it actually covers. Scan the back catalog, not just new data. Produce one number: how many records holding PII, PHI or card data exist, broken down by application. That number is your mandate.
Days 30 to 60, tune. Run in monitor mode. Measure the false positive rate per policy before anything enforces. Fix the top three noisiest rules before you touch anything else.
Days 60 to 90, enforce and prove. Turn on redaction for the highest confidence data types. Extend to the browser and the endpoint. Route events into the SIEM and produce the first evidence pack for your auditor.
Run this checklist before you call the program healthy:
The DLP engineer role is no longer about holding a perimeter. It is about making data safe wherever it moves, because it now moves through tabs, prompts and connectors that no network control can see. The engineers worth hiring in 2026 are the ones who tune for accuracy rather than coverage theater, who choose redaction over blocking, and who treat the data layer as the backstop when identity, model and network controls fail. Strac gives that engineer one console across SaaS, Cloud, Browser, GenAI and MCP, so a compromise never becomes a breach. Book a demo to see what the job looks like with the surfaces already covered.
The engineer builds and tunes the detection and remediation system. The analyst triages the alerts it generates. Engineers own policy accuracy and coverage; analysts own incident response on what those policies surface.
No. No certification is universally required. Security+, CySA+ or a privacy credential such as CIPP help more at entry level, and hands on policy tuning experience outweighs all of them. CISSP matters more for moving into architecture or management later.
No, and the opposite is happening. Generative AI created a new uncontrolled data path, so demand for people who can govern prompts, browsers and connectors is rising. Model assisted classification changes how detection is built, not whether someone has to own it.
No. Free text is open ended, insiders have legitimate access, and no detector catches everything a person can describe in their own words. That is why the data layer matters: redaction limits what any compromised account or connector can pull out in bulk, even when detection misses.
Browser, generative AI and MCP coverage, because almost nobody has it on a resume yet and every program is short on it. Start from the pillar on AI data governance.