Calendar Icon White
October 29, 2026
Clock Icon
7
 min read

How to Enhance Fintech Cybersecurity in 2025?

Fintech cybersecurity in 2026: why card and account data now leaks through SaaS, AI tools, and AI agents, the rules you must meet, and how Strac fixes it.

How to Enhance Fintech Cybersecurity in 2025?
ChatGPT
Perplexity
Grok
Google AI
Claude
Summarize and analyze this article with:

TL;DR

  • Fintech cybersecurity protects customer financial data, such as card numbers, bank account details, and SSNs, along with the systems that store and move it, from theft, leaks, and misuse.
  • The risk has moved. Card numbers sit in Zendesk tickets and Slack threads, employees paste account exports into ChatGPT, and AI agents read Stripe and Salesforce through MCP DLP paths most security tools never see.
  • Firewalls, identity tools, and legacy DLP guard the perimeter and the payment flow. They do not take a card number out of a support ticket or an AI prompt.
  • Strac finds and redacts financial data across SaaS DLP, browser DLP, endpoint DLP, AI DLP, and MCP, and logs every fix as evidence for PCI DSS, NYDFS, GLBA, and DORA.
  • This post is the fintech slice of the data loss prevention guide. For card data specifically, start with the card data discovery tool guide.

Fintech cybersecurity is the set of controls a financial technology company uses to keep customer money and customer data safe. It covers payment systems, banking integrations, and identity, but the hardest part in 2026 is the data itself: card numbers, account and routing numbers, SSNs, tax forms, and KYC documents.

That data used to stay inside a payment processor and a core database. Today it spreads into every tool a fintech runs. A customer pastes a card into a support chat. An analyst shares a transaction export in a channel. A KYC folder in Google Drive stays open to anyone with the link.

Perimeter security keeps attackers out; data security decides what they find if they get in. Fintech cybersecurity in 2026 has to do both, and the second is where most programs fall short. For the full picture of how DLP fits, read data loss prevention compliance.

✨ Why Fintech Data Is Harder to Protect in 2026

Attackers still want the same thing: customer financial records they can sell, ransom, or use for fraud. What changed is how many places those records now sit, and how many of those places no security tool is watching.

1. Extortion runs on stolen data

Ransomware crews now copy data out before they encrypt anything. Restoring from backup no longer ends the incident, because the threat is publishing the records. The less sensitive data you keep in everyday tools, the less there is to ransom.

2. Card numbers leak through support and chat

A customer pastes a card into an Intercom chat. An agent copies it into a Salesforce case. A refund request with the full number lands in Slack. None of it is malicious, and all of it is exactly what an attacker finds first after a phished login.

3. Old files stay exposed for years

Tax forms, bank statements, and transaction exports sit in shared drives long after anyone needs them, often shared outside the company. Finding that old exposure is the job of sensitive data discovery and classification.

4. Employees paste account data into AI tools

An analyst drops a customer spreadsheet into Claude to build a summary. A support lead pastes a ticket thread, card number included, into Copilot to draft a reply. Often it happens through personal accounts nobody approved. See shadow AI for how far this spreads.

5. AI agents read financial systems directly

Through MCP connectors, agents in Claude, ChatGPT, and Cursor can search a mailbox, pull charges from Stripe, or query a data warehouse. The records flow straight into a model's context without anyone choosing to share them. A network gateway sees an encrypted call; it does not see the account numbers inside it.

6. Vendors and connected apps widen the gap

Every SaaS tool, OAuth grant, and outside share adds a door. A compromised vendor or a forgotten integration exposes whatever data sits behind it. Regulators now say plainly that vendor risk stays your responsibility.

Detection tells you a leak happened. Remediation is what stops it.

🎥 The Regulations Fintech Teams Must Meet in 2026

Every major framework that touches fintech has finished its phase-in. Examiners now expect proof, not policy documents, and each one assumes you know where regulated data lives.

  • PCI DSS 4.0.1. Every future-dated requirement has been mandatory since March 31, 2025. Requirement 12.5.2 asks you to confirm where card data lives at least once a year, and 12.10.7 requires a response when card numbers turn up somewhere unexpected, like a Slack DM. See PCI DSS 4.0 changes and PCI DSS compliance.
  • NYDFS 23 NYCRR Part 500. The final phase took effect on November 1, 2025, making MFA for all users and a written, maintained asset inventory mandatory. NYDFS also made clear that covered entities cannot hand Part 500 responsibility to their vendors.
  • GLBA Safeguards Rule. The FTC applies it to lenders, brokers, payment firms, and other non-bank financial companies. It requires a written security program, encryption, access controls, and notice to the FTC when unencrypted customer data is exposed.
  • SEC Regulation S-P. The updated customer data rules now apply to large and small firms alike, and public companies face a four business day disclosure clock for material incidents.
  • DORA. The EU's Digital Operational Resilience Act has applied since January 17, 2025. It expects a full map of ICT assets and third parties and fast reporting of major incidents.
  • Privacy and assurance. GDPR and CCPA cover customer personal data, and banking partners usually ask for SOC 2 and ISO 27001 reports on top.

None of these rules says buy a DLP tool. Each one assumes you can answer three questions on demand: where is our sensitive data, who can reach it, and what did we do when it showed up in the wrong place?
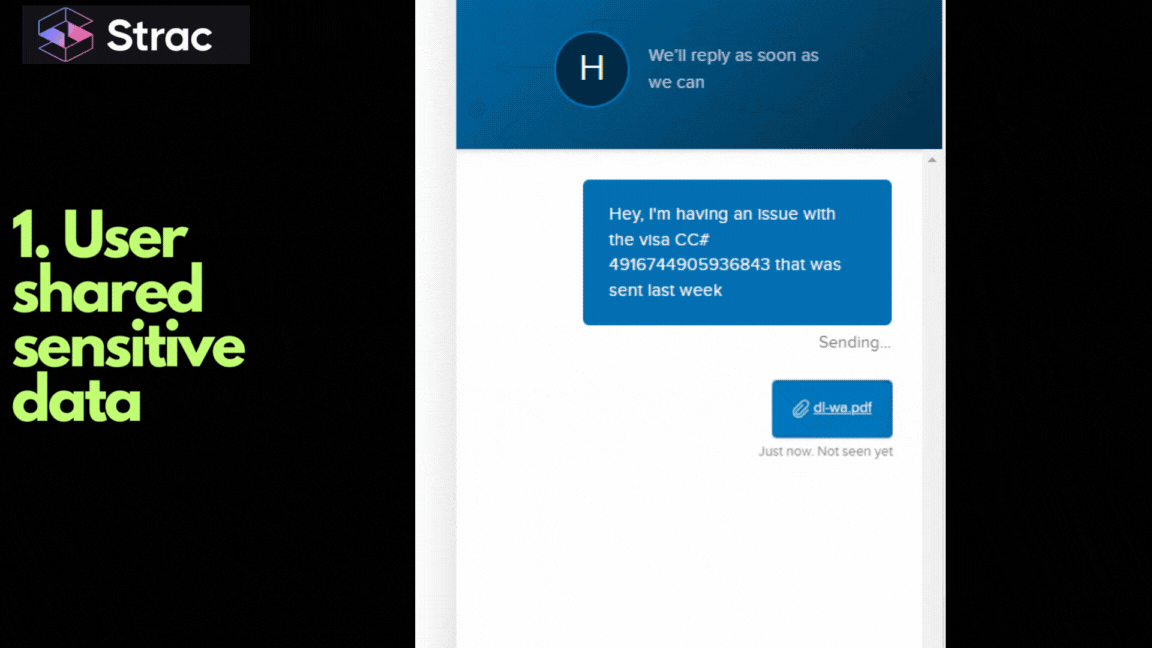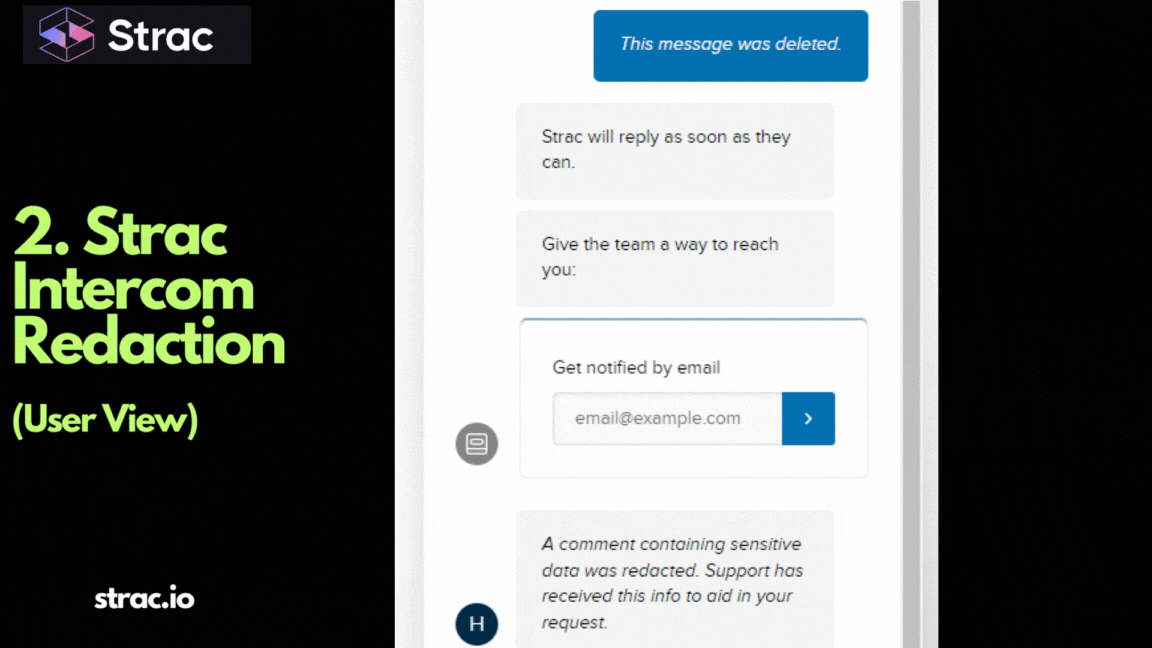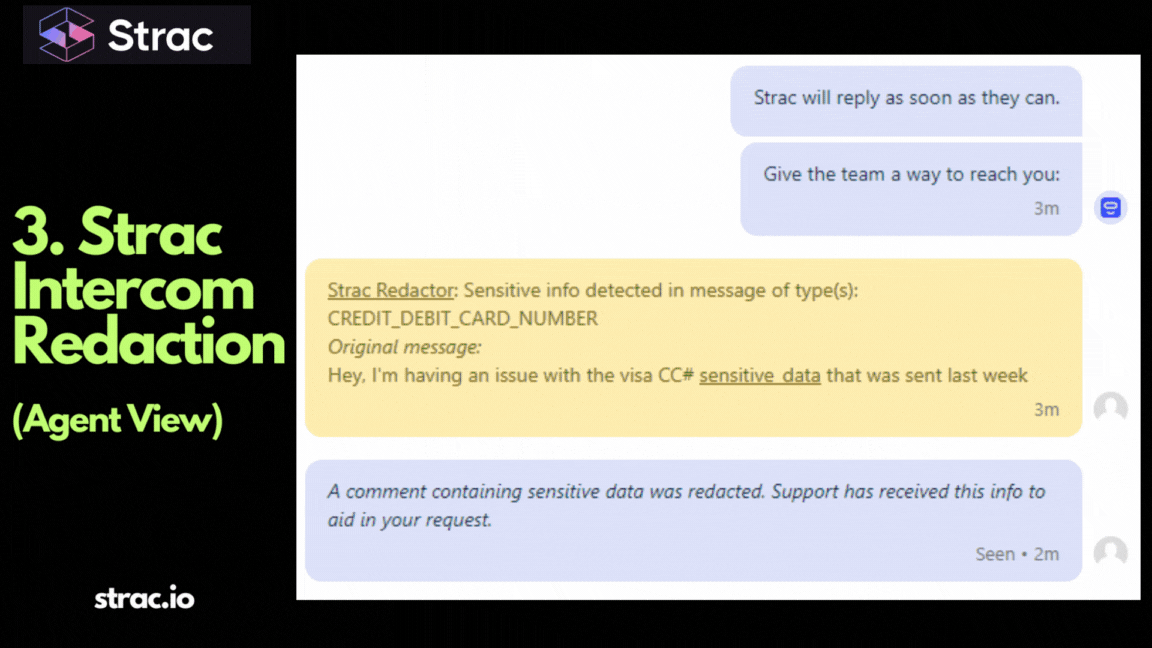
✨ How Strac Stops a Card Number Leak in Real Time

A legacy tool would have opened a ticket. Strac removed the card number before anyone else read it.

Here is the same leak handled two ways. A support agent posts a customer's full card number in a shared channel to ask about a refund.

With an alert-only tool, a notice lands in a queue. An analyst opens it hours later and asks the agent to delete the post. The card number is readable by the whole channel the entire time, and nobody can prove when it was removed.

With Strac, Slack DLP confirms the number with a Luhn check, masks it to the last four digits, and tells the agent why. The event is logged as 12.10.7 evidence. The conversation keeps going; the card number does not stay. The same flow runs in Gmail, Zendesk, and Intercom.

✨ Strac: Fintech Data Protection Across SaaS, AI & MCP

Strac is one DLP and DSPM platform, so the same detectors for card numbers, bank accounts, SSNs, and secrets run on every surface a fintech uses. It finds the data, fixes it in place, and logs every action as audit evidence.

  • Find it first. DSPM scans SaaS apps, cloud storage, and databases for PAN, account numbers, and SSNs, including years of history, and ranks findings by who can see them. The PII scanner reads PDFs, spreadsheets, ZIP files, and images, so a photo of a check or a scanned bank statement is caught like typed text. This is your PCI DSS 12.5.2 scope evidence and your NYDFS asset inventory.
  • Chat and email. Slack DLP, Gmail DLP, and Office 365 DLP redact card and account numbers in messages and attachments as they are posted. The conversation keeps going; the card number does not stay.
  • Support and CRM. Zendesk DLP, Intercom DLP, Salesforce DLP, and HubSpot DLP mask PAN and delete CVVs in tickets, chats, and cases. Agents see the last four digits, which is all they need.
  • Files and cloud storage. Google Drive DLP, OneDrive DLP, Box DLP, and AWS S3 scanning find KYC documents, tax forms, and transaction exports, then remove public links and outside sharing. The full list is on the integrations page.
  • Browser and AI tools. Browser DLP for Chrome and Edge inspects prompts and uploads before they reach ChatGPT, Claude, Gemini, or Copilot. The question reaches the model. The account number does not. See all GenAI DLP coverage.
  • Shadow AI. Strac shows every AI app people actually use, approved or not, and the financial data heading to each, with no keystroke logging and no screen recording. Start with how to detect shadow AI.
  • AI agents and MCP. MCP DLP sits between AI agents and the systems they read, controls what each agent can reach, and redacts sensitive data in every tool call before the model sees it. Fintech teams start with the Stripe MCP, QuickBooks MCP, NetSuite MCP, and Snowflake MCP connectors. Browse the MCP connector directory.
  • Laptops. One endpoint DLP agent for Mac, Windows, and Linux controls USB, cloud sync, print, clipboard, screenshots, and desktop AI apps, each in Block, Warn, or Audit mode.
  • Copies that move. Data lineage DLP recognizes a customer export from Salesforce even after it is renamed, edited, or copied.
  • Card and account data you need to keep. Data masking, tokenization, and the Strac document vault swap sensitive values for tokens, which takes those systems out of PCI scope. Engineering teams call Strac's detection and redaction APIs to clean data inside their own apps and logs.
  • Remediation in a fixed order. When Strac finds sensitive data, it follows your policy:
    • Redact / mask. Replaces the PAN, account number, or SSN in Slack, email, tickets, docs, Google Drive, SharePoint, and Box. See DLP remediation.
    • Block. Stops the value from reaching an AI tool, a personal upload site, a USB drive, or an agent's context.
    • Warn and coach. Tells the person what was caught and where customer data should go instead, at the moment they act.
    • Revoke access. Removes public links and outside sharing from files that hold financial data.
  • Compliance evidence. Every finding and fix is logged with time, location, data type, and action, and maps to PCI DSS, SOC 2, ISO 27001, CCPA, and GDPR. That log is your 12.10.7 response record and the proof NYDFS, GLBA, and DORA examiners ask for. See how Strac supports fintech teams.

SaaS integrations connect through APIs in under 10 minutes, with no proxy and no code.

Your Fintech Data Security Checklist

  • ☐ Every SaaS app and storage bucket scanned for card numbers, account numbers, and SSNs, including history
  • ☐ Card and account numbers redacted automatically in chat, email, and support tools
  • ☐ No CVVs stored anywhere after authorization
  • ☐ Public links and outside shares removed from files with financial data
  • ☐ Prompts and uploads to AI tools checked before they leave the browser
  • ☐ Every AI agent and MCP connector inventoried, scoped, and logged
  • ☐ Laptops control USB, cloud sync, print, and desktop AI apps
  • ☐ Every finding and fix logged as evidence for PCI DSS, NYDFS, GLBA, and DORA

Finding financial data shows you the risk. Redacting it removes the risk.

👉 Related reading:

The Bottom Line

Fintech data no longer stays in the payment system. It moves through chat, tickets, shared drives, laptops, AI tools, and AI agents, and regulators now expect you to know where it is at all times. Firewalls, identities, and vendors all fail eventually, so the data layer is the backstop: find financial data everywhere it lives, redact it on every action, and a compromise never becomes a breach.

‍Book a demo to see Strac protect customer financial data across SaaS, AI, and MCP.
🌶️ Spicy FAQs on Fintech Cybersecurity

Is fintech cybersecurity the same as PCI compliance?

No. PCI DSS covers card data only. Fintech cybersecurity also covers bank account numbers, SSNs, KYC documents, and the systems that hold them, under rules like NYDFS Part 500, GLBA, and DORA. PCI is one part of the program.

We use Stripe. Why do we still need DLP?

Stripe keeps cards out of your payment flow, not out of your inbox or support queue. When a customer pastes a card into a chat, or an agent pulls charges into an AI tool, that copy lives in your systems and needs protecting.

Do we have to block ChatGPT to protect customer data?

No. Blocking pushes people to personal phones, where you lose all visibility. Strac redacts card and account numbers in the prompt and lets the rest through, so employees keep using AI and customer data stays out of the model.

Can any tool stop every fintech data leak?

Not every one. People find new tools, and attackers find new paths. That is why the data layer matters: if sensitive values are redacted wherever they land, a stolen login or a missed alert exposes far less.

How does this map to PCI DSS, NYDFS, and DORA?

Each framework asks you to know where regulated data lives and prove you control it. Strac's scan results and redaction logs cover PCI DSS 12.5.2 and 12.10.7, the NYDFS asset inventory, and DORA's asset mapping. See data loss prevention compliance for the full picture.

Customer story

“Don’t just alert on problems, fix them.”

Scott Roberts, Chief Information Security Officer, UiPath

  • UiPath
  • Crypto.com
  • Inmar Intelligence
  • thredUP
  • Paymentology
  • Qventus
  • Genesis Molecular AI
  • MeridianLink
More customer stories →
Discover & Protect Data on SaaS, AI, MCP, Endpoints & Cloud
Strac provides end-to-end data loss prevention for all SaaS and Cloud apps. Integrate in under 10 minutes and experience the benefits of live DLP scanning, live redaction, and a fortified SaaS environment.

Customers include

  • UiPath
  • Crypto.com
  • Inmar Intelligence
  • thredUP
  • Paymentology
  • Qventus
  • Genesis Molecular AI
  • MeridianLink
Trusted by enterprises
Data Security + Compliance Automation

Latest articles

Browse all

Get Your Datasheet

Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
Close Icon