

August 28, 2026

7
min read
Explore the Benefits of Data Loss Prevention Services
Learn how modern DLP services protect sensitive data across SaaS, cloud, endpoints, GenAI, browsers, and MCP workflows with real-time remediation.
· Modern DLP services protect sensitive dataacross SaaS, cloud, endpoints, browsers, GenAI, email, and other data movementchannels.
· DLP should go beyond alerts and actively block,redact, mask, quarantine, encrypt, or coach users when sensitive data isexposed.
· DSPM and DLP increasingly work together: DSPMfinds and classifies sensitive data; DLP controls what happens when that datamoves.
· AI creates new data-loss paths through prompts,uploads, AI agents, Shadow AI, and MCP-connected tools.
· Stracbrings DSPM and DLP together to discover, classify, monitor, and remediatesensitive data across modern enterprise environments.
Data Loss Prevention (DLP) services help organizations discover, monitor, and protect sensitive information from accidental exposure, insider risk, unauthorized sharing, and data exfiltration.
But DLP in 2026 looks very different from traditional DLP.
Sensitive data no longer moves only through corporate email and managed laptops. It travels through SaaS applications, cloud storage, browsers, support tickets, collaboration tools, GenAI prompts, and increasingly Model Context Protocol (MCP) connections.
Modern DLP therefore needs to answer three questions: Where is sensitive data? Where is it moving? What should happen when it reaches a risky destination?
Legacy DLP was largely built around predictable enterprise boundaries: corporate endpoints, email gateways, networks, and approved applications.
Those boundaries are disappearing.
An employee can download customer records from Salesforce, paste them into ChatGPT, upload a spreadsheet to Google Drive, copy it to a USB drive, send it through Slack, or expose it to an AI agent connected to multiple enterprise systems.
The security problem is no longer simply where data is stored.
It is how sensitive data moves across interconnected applications, users, endpoints, and AI systems.
That is why modern DLP is becoming less about static rules and more about continuous data visibility and policy enforcement.
SaaS applications have become one of the largest surfaces for sensitive enterprise data.
Customer records can appear in Salesforce. PHI may enter Zendesk or Intercom support tickets. Employees can share PCI or PII through Slack, Gmail, Microsoft 365, Google Drive, or other collaboration platforms.
Modern SaaS DLP should inspect both messages and files, identify sensitive information, and enforce policy without requiring security teams to manually review every incident.
Depending on the application and policy, enforcement can include redaction, masking, blocking, deletion, quarantine, or auditing.
Cloud environments can accumulate enormous amounts of sensitive and forgotten data.
A modern data protection program therefore needs visibility into where PII, PHI, PCI, credentials, secrets, intellectual property, and other confidential information are stored.
This is where Data Security Posture Management (DSPM) complements DLP.
DSPM discovers and classifies sensitive data and identifies risky exposure. DLP then helps control what happens when that data is accessed, shared, uploaded, downloaded, or moved.
Together, they provide protection for both data at rest and data in motion.
Endpoints remain a major exfiltration path.
Employees interact with sensitive data through browsers, applications, local files, clipboard actions, screenshots, printing, USB devices, and file transfers.
Modern Endpoint DLP should provide granular policies rather than simply blocking entire applications or devices.
For example, an organization might allow normal files to be copied to removable storage while blocking files containing customer PII or source-code secrets.
The decision becomes based on what is inside the data, not simply which application or device is being used.
The browser has effectively become the operating system for modern work.
Employees use browsers to access SaaS applications, upload files, interact with AI tools, enter information into forms, and move data between corporate and personal environments.
Browser DLP provides another enforcement point for detecting sensitive information before it leaves approved workflows.
This becomes particularly important for unsanctioned SaaS and Shadow AI tools that may sit outside traditional security controls.
Generative AI has created an entirely new data-loss surface.
Employees can paste source code, customer records, credentials, financial information, contracts, or internal documents directly into AI applications.
AI DLP can inspect prompts, uploads, and other interactions before sensitive information reaches an unauthorized AI service.
Instead of banning AI entirely, organizations can apply policies based on the data being shared, the AI application being used, and the context of the interaction.
That makes secure AI adoption much more practical.
Model Context Protocol is expanding what AI agents can access.
An AI system may no longer interact only with the text a user enters. Through MCP servers and connectors, an agent can potentially interact with enterprise applications, files, databases, repositories, and internal tools.
That creates a new security question:
What happens when an AI agent can retrieve sensitive enterprise data and send it somewhere it should not go?
MCP DLP introduces a policy enforcement layer around these interactions so organizations can inspect sensitive data moving between AI agents, MCP servers, connected tools, and enterprise systems.
As agentic AI adoption grows, protecting these machine-to-machine data flows will become an increasingly important part of enterprise DLP.
Not every breach is malicious.
An employee might paste customer information into ChatGPT, upload the wrong spreadsheet to Google Drive, attach a document containing PHI to a support ticket, or send financial information to the wrong recipient.
DLP can identify sensitive content at the point of interaction and enforce policy before an accidental mistake becomes a security incident.
Employees and contractors often need legitimate access to sensitive information.
The risk appears when that information is copied, downloaded, uploaded, emailed, or transferred somewhere it should not be.
DLP provides controls around those actions while allowing legitimate business workflows to continue.
Employees are adopting AI tools faster than many security teams can approve them.
Blocking every AI application can hurt productivity, while allowing unrestricted access creates obvious data exposure risks.
DLP provides a middle ground by controlling the sensitive data entering AI applications rather than relying entirely on application-level blocking.
Organizations frequently do not know how much sensitive information exists across SaaS applications, cloud repositories, support systems, endpoints, and collaboration tools.
Combining DSPM with DLP helps teams first find the sensitive data, then apply controls to protect it.
Frameworks and regulations such as HIPAA, PCI DSS, GDPR, SOC 2, ISO 27001, CCPA, and NIST require organizations to implement appropriate controls around sensitive information.
DLP can help organizations detect regulated data, enforce handling policies, maintain audit trails, and provide evidence that data protection controls are operating.
DLP does not automatically make an organization compliant, but it can become an important technical control within a broader compliance program.
A DLP platform should not protect only email or endpoints.
Organizations should evaluate whether it can follow sensitive data across:
The more fragmented the coverage, the more blind spots security teams have to manage.
Basic regex can identify predictable patterns, but modern enterprise data is rarely that simple.
Sensitive information can exist inside PDFs, spreadsheets, Word documents, ZIP files, screenshots, images, support tickets, messages, and other unstructured content.
Modern DLP therefore needs content-aware detection capable of understanding more than simple keyword and pattern matching.
Attackers and employees do not move sensitive information only as plain text.
DLP should inspect sensitive information inside files such as PDF, DOCX, XLSX, CSV, ZIP, JPEG, PNG, and screenshots where supported.
OCR and image-aware detection are increasingly important because sensitive information can easily bypass text-only inspection.
Finding sensitive data after it has leaked is not enough.
Modern DLP should be able to take action.
Depending on the channel and policy, that can mean:
Detect → Redact → Mask → Block → Quarantine → Delete → Encrypt → Coach → Audit
This moves DLP from passive monitoring to active data protection.
Every company has information that does not fit standard definitions of PII, PHI, or PCI.
That might include customer identifiers, internal project names, proprietary formulas, API secrets, financial records, intellectual property, or organization-specific confidential data.
Custom detectors allow DLP policies to reflect what is actually sensitive to the business.
Not every appearance of sensitive data represents the same level of risk.
A customer identifier inside an approved Salesforce workflow is very different from the same identifier being pasted into an unsanctioned AI application.
Policies should therefore consider both what the data is and where it is going.
A security product that generates thousands of meaningless alerts eventually becomes ineffective.
DLP should minimize unnecessary noise, support fast deployment, and provide remediation workflows that security teams can realistically operate.
The goal is not to stop employees from working.
The goal is to prevent sensitive data from going where it should not.
Strac approaches DLP as a unified data security problem rather than a collection of isolated channels.
Instead of deploying separate tools for discovery, SaaS DLP, endpoint controls, AI protection, and remediation, Strac combines DSPM + DLP to discover sensitive information and enforce policies as data moves.
Strac discovers and classifies sensitive data while providing DLP controls for protecting it.
This connects posture management with enforcement.
Security teams can understand where sensitive information exists and then apply policies to how that information is shared, transferred, or used.
Strac protects sensitive information across modern SaaS and cloud workflows, including collaboration, productivity, CRM, support, and storage applications.
Rather than relying entirely on alerts, Strac can apply remediation such as redaction and other policy actions where supported.
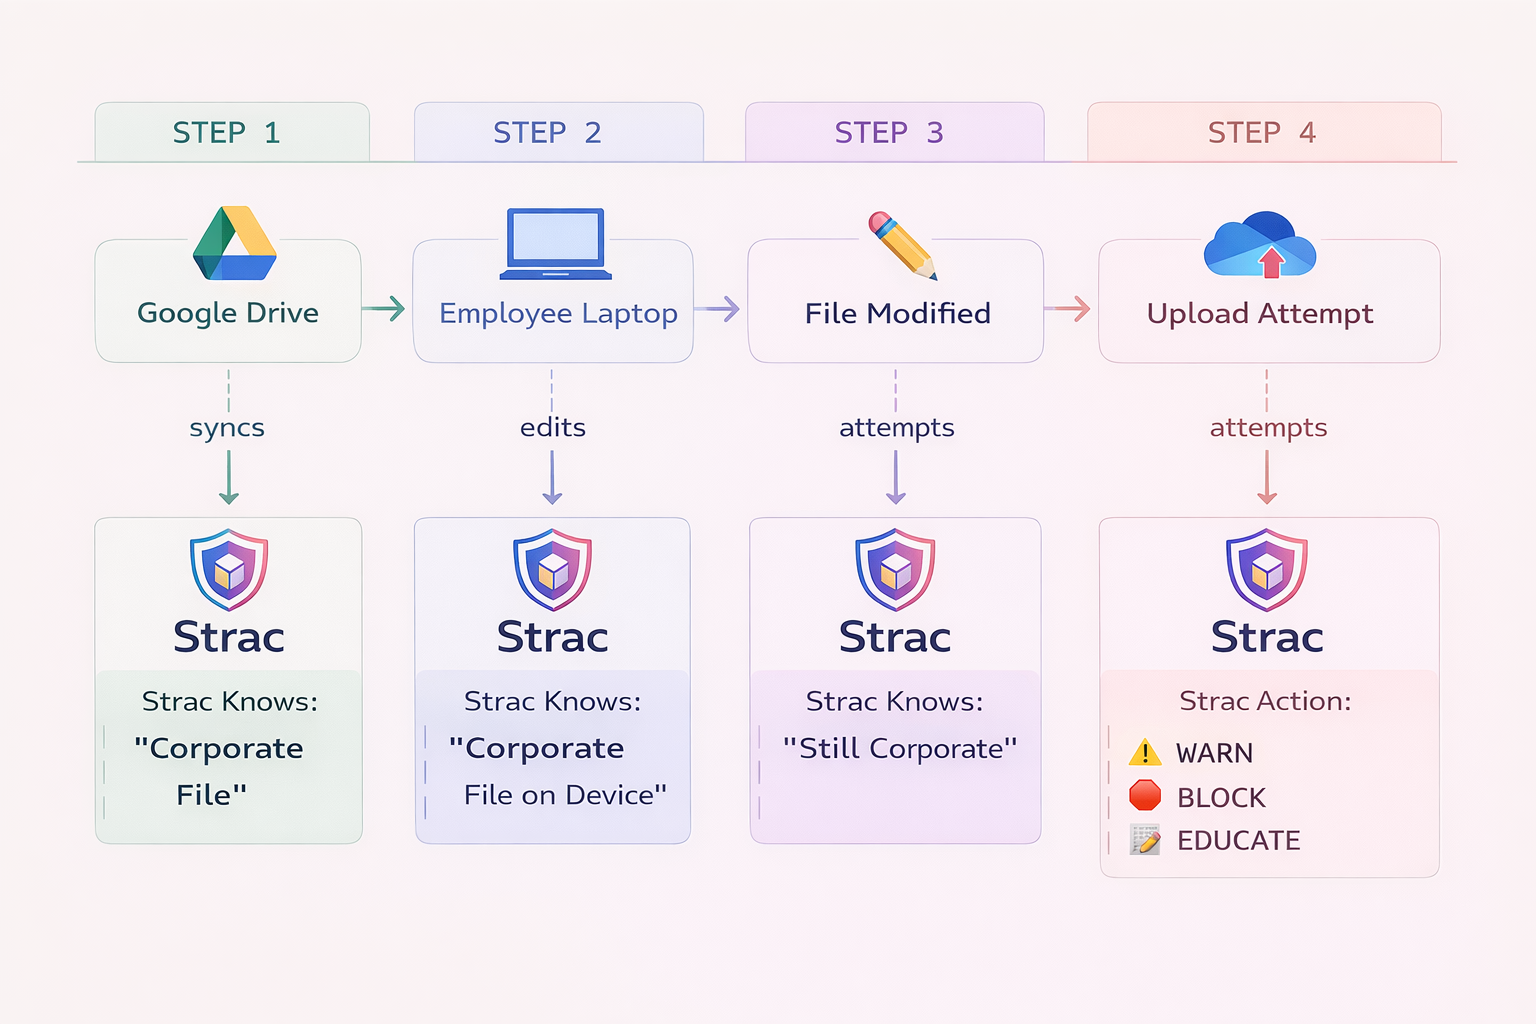
Strac Endpoint DLP extends data protection to employee devices and data movement channels.
Policies can be based on the sensitive content itself, allowing organizations to control risky transfers without unnecessarily blocking legitimate employee activity.
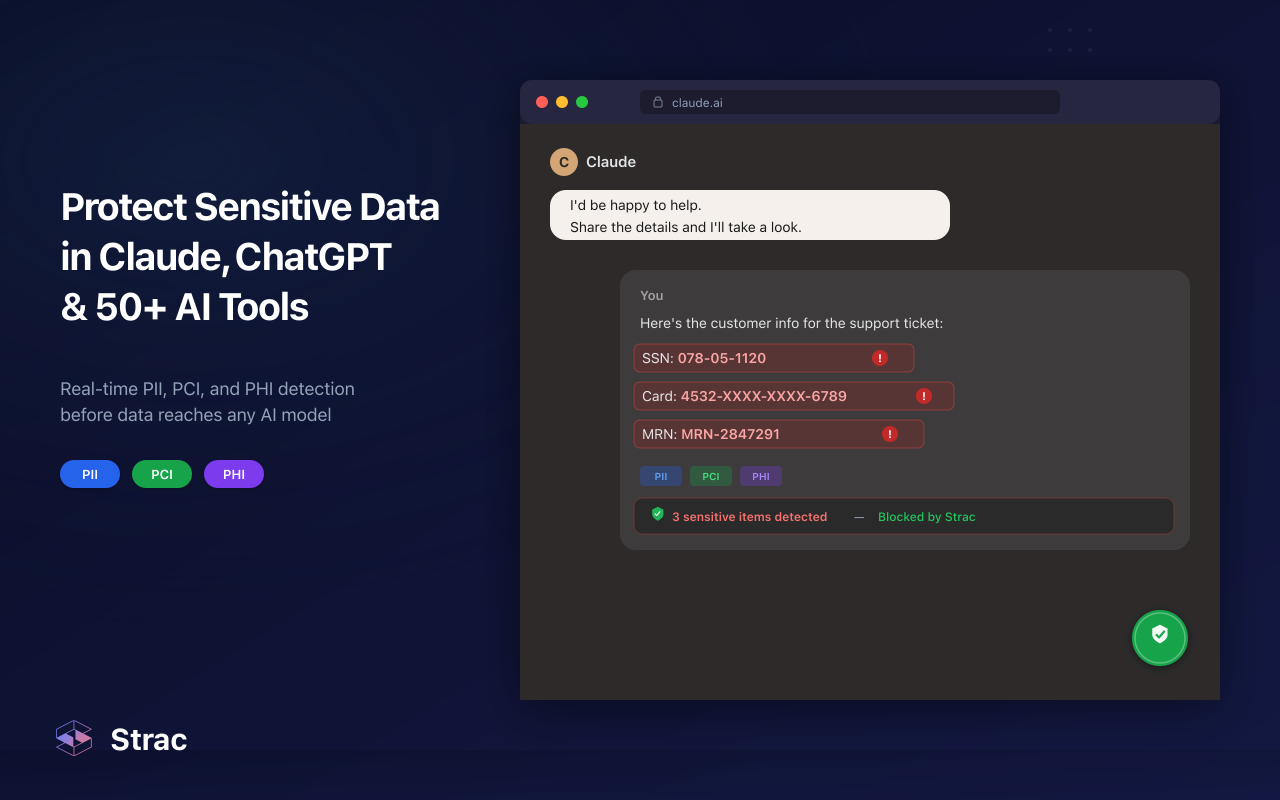
Strac helps organizations govern sensitive information entering AI applications.
Security teams can identify sensitive content such as PII, PHI, PCI, credentials, secrets, and confidential information before it is exposed through GenAI workflows.
This allows enterprises to adopt AI while maintaining control over what corporate data employees can share with AI systems.
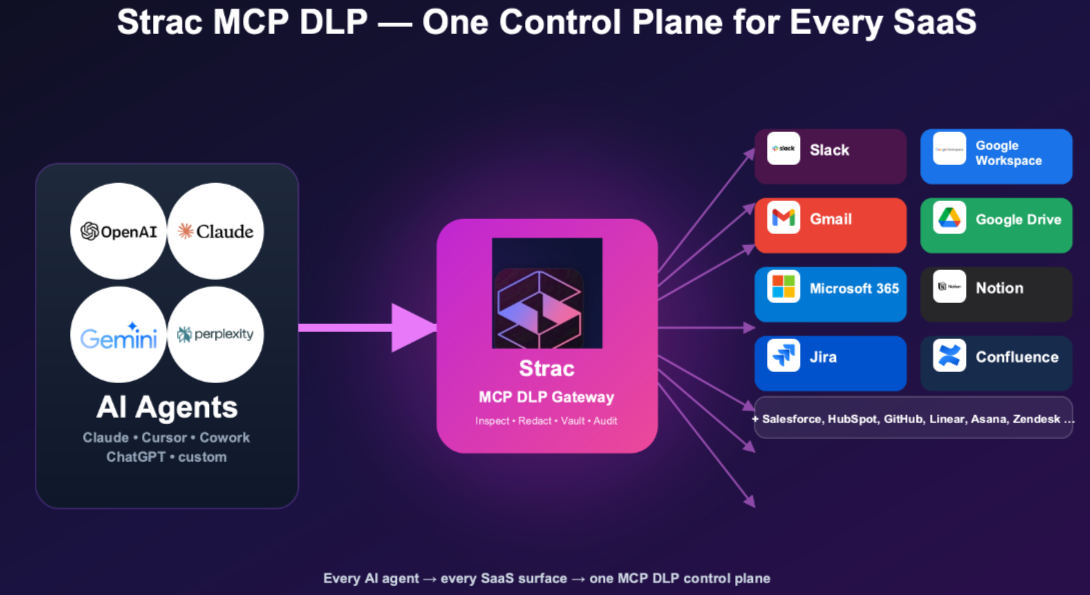
Strac extends DLP into MCP-connected AI workflows.
As AI agents gain access to enterprise applications and data sources, MCP becomes another channel through which sensitive information can move.
Strac provides visibility and policy enforcement around these interactions, helping organizations control sensitive data as AI agents communicate with MCP servers, connectors, and enterprise tools.
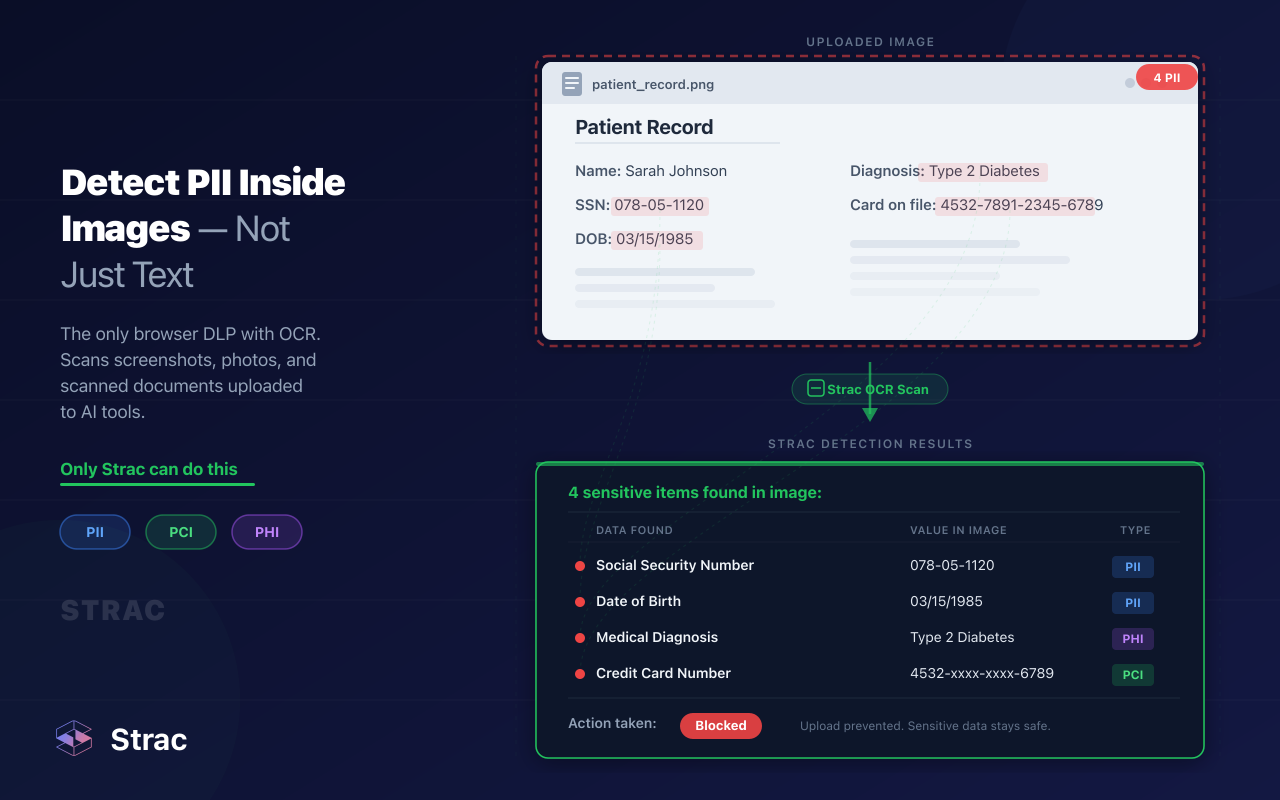
Sensitive information does not always appear as plain text.
Strac can inspect structured and unstructured content across supported documents and images, using technologies such as machine learning and OCR to identify sensitive information inside files and visual content.
This is particularly important for spreadsheets, PDFs, screenshots, uploaded documents, and support attachments.

Strac provides built-in detectors for common sensitive data categories including PII, PHI, PCI, credentials, secrets, and other regulated information.
Organizations can also create custom detectors for proprietary or business-specific sensitive information.
Explore Strac's sensitive data elements.
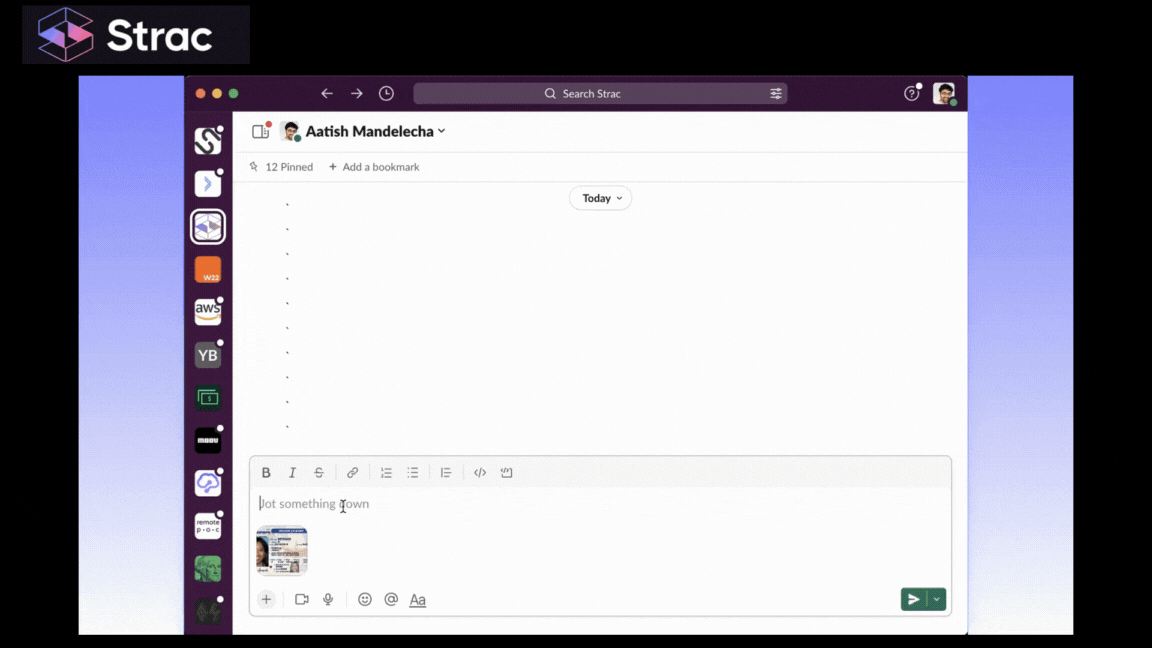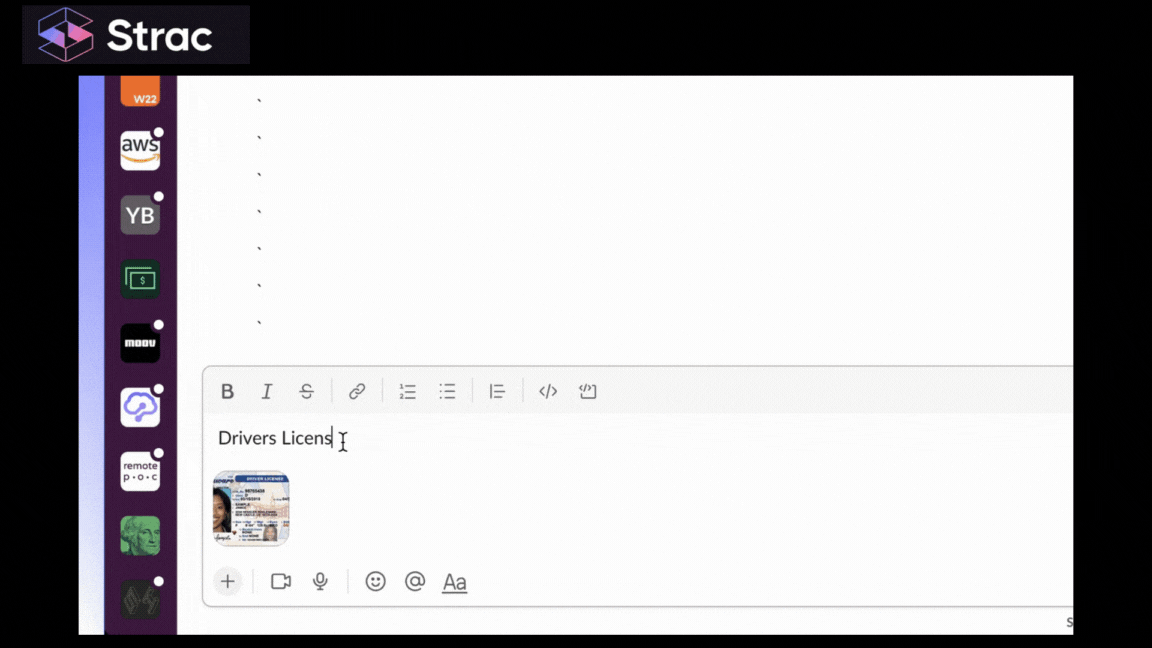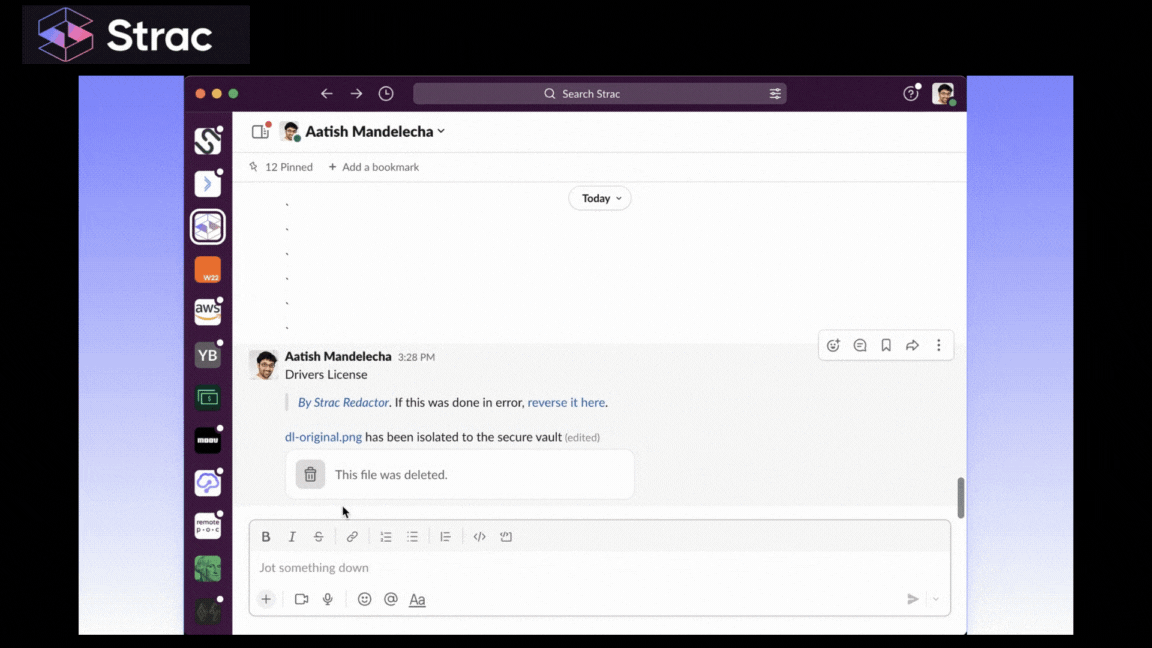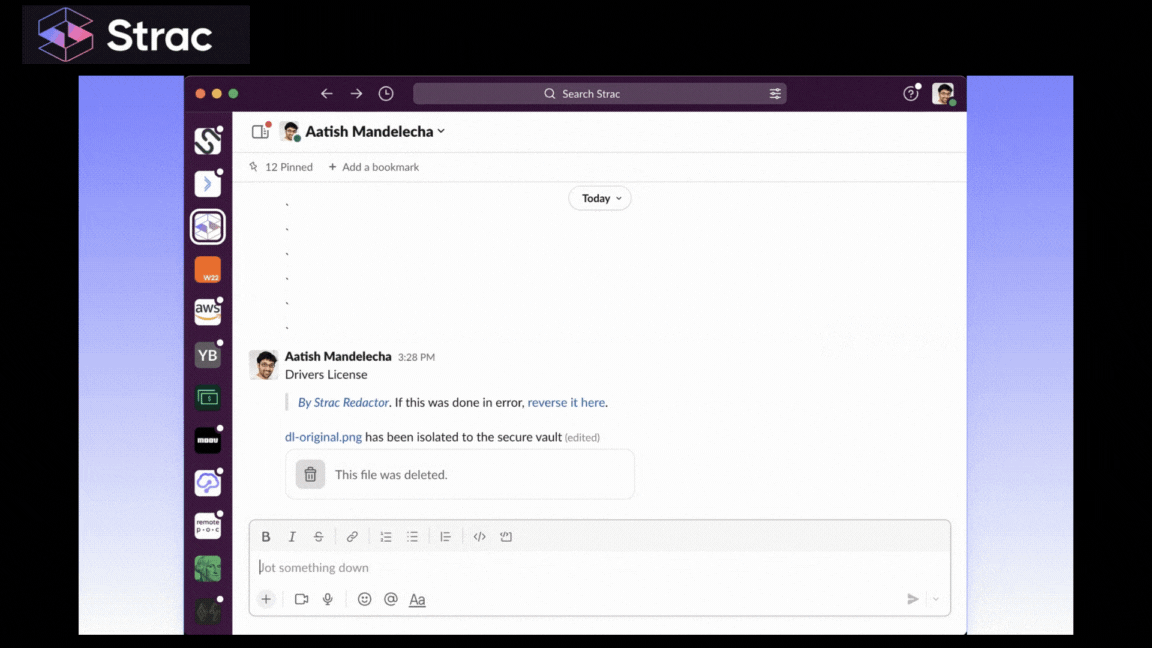
Strac is designed around enforcement, not just visibility.
Depending on the integration and policy, organizations can take actions such as redacting, masking, blocking, quarantining, deleting, encrypting, auditing, or coaching users when sensitive data is detected.
That means security teams can stop exposure closer to the moment it happens instead of investigating an alert after the data has already left.
Strac offers complience support relevant to frameworks and regulations including:
These capabilities help organizations identify regulated information, enforce handling policies, and maintain evidence around sensitive data protection.
Organizations also need DLP inside their own applications and workflows.
Strac's APIs allow developers to integrate sensitive data detection and redaction directly into applications, products, and internal systems.
This extends DLP beyond pre-built integrations into organization-specific data flows.
Traditional DLP was largely designed to answer:
“Is sensitive data leaving the corporate network?”
Modern DLP has to answer something much harder:
“Where is sensitive data, who or what is interacting with it, where is it going, and should that action be allowed?”
That distinction matters because the enterprise perimeter now includes SaaS applications, cloud infrastructure, employee browsers, endpoints, GenAI platforms, APIs, and autonomous AI agents.
DLP must follow the data rather than depend on a fixed perimeter.
Data Loss Prevention services are evolving from static monitoring tools into active data security enforcement platforms.
The strongest DLP strategies in 2026 combine discovery, classification, context, and real-time remediation across SaaS, cloud, endpoints, browsers, GenAI, and emerging AI-agent workflows.
Strac is built around that model. By combining DSPM with modern DLP, deep content inspection, AI-aware protection, and inline remediation, organizations can protect sensitive data without forcing security teams to choose between visibility and enforcement.
Related reading:
Not dead, but definitely outdated on its own. DLP that only watches email, networks, or managed endpoints misses where sensitive data now moves: SaaS apps, browsers, GenAI tools, cloud environments, and AI agents. Modern DLP needs to follow the data, not the old corporate perimeter.
Because detecting a leak and stopping one are two different things. Alert-heavy DLP can tell security teams that PII, PHI, PCI, credentials, or confidential data was exposed after the fact. Modern DLP should be able to redact, mask, block, quarantine, encrypt, delete, or otherwise remediate sensitive data when policy is violated.
Usually, no. Employees will use AI because it makes them more productive, and blanket blocking can simply push usage into Shadow AI. A better approach is AI DLP that controls what sensitive data can be shared with AI, allowing safe AI usage while blocking risky prompts, uploads, and data transfers.
If AI agents can access enterprise systems through Model Context Protocol, MCP becomes a new data movement channel. MCP DLP applies sensitive-data inspection and policy enforcement to interactions between AI agents, MCP servers, connectors, and enterprise tools. As agentic AI adoption grows, this is quickly becoming a real DLP problem rather than a theoretical one.
Strac combines DSPM + DLP so organizations can discover sensitive data and protect it as it moves across SaaS, cloud, endpoints, browsers, GenAI, and emerging MCP workflows. It also focuses on deep content inspection and inline remediation, helping security teams move from simply finding exposure to actually preventing it.







