October 11, 2026

5
min read
Data Loss Prevention: Achieving Regulatory Compliance
DLP regulatory compliance in 2026: what GDPR, HIPAA, PCI DSS, SOX and the EU AI Act require, and how Strac enforces it across SaaS, endpoint, AI and MCP.

DLP regulatory compliance in 2026: what GDPR, HIPAA, PCI DSS, SOX and the EU AI Act require, and how Strac enforces it across SaaS, endpoint, AI and MCP.

Data loss prevention regulatory compliance is the use of DLP to satisfy legal obligations over specific classes of sensitive data. The law defines the data and the duty. DLP is the technical control that carries the duty out.
Every major regulation asks the same three questions in its own vocabulary. Where is the regulated data? Who and what can move it? Can you prove it stayed where it belongs? GDPR calls the answer "appropriate technical and organisational measures." HIPAA calls it safeguards for electronic protected health information. PCI DSS calls it protecting stored account data and restricting it to a defined scope.
A DLP policy document answers none of those questions on its own. A regulator does not fine you for a missing paragraph; it fines you for the record that left.
The laws did not change their definition of a breach. The channels did.
Regulated data used to leave through systems a company owned and logged: the mail server, the file share, the USB port. In 2026 it leaves through a browser tab and an API call. A support rep pastes a card number into a Slack thread. An analyst uploads a claims export to a free summarizer. An agent with a database connector reads a full patient table and returns it to a model over MCP.
Each of those is an unauthorized disclosure under the relevant law. None of them crosses a mail gateway. Three shifts explain the gap:
Legacy DLP inspects the channels it was built for. Regulators inspect the outcome.
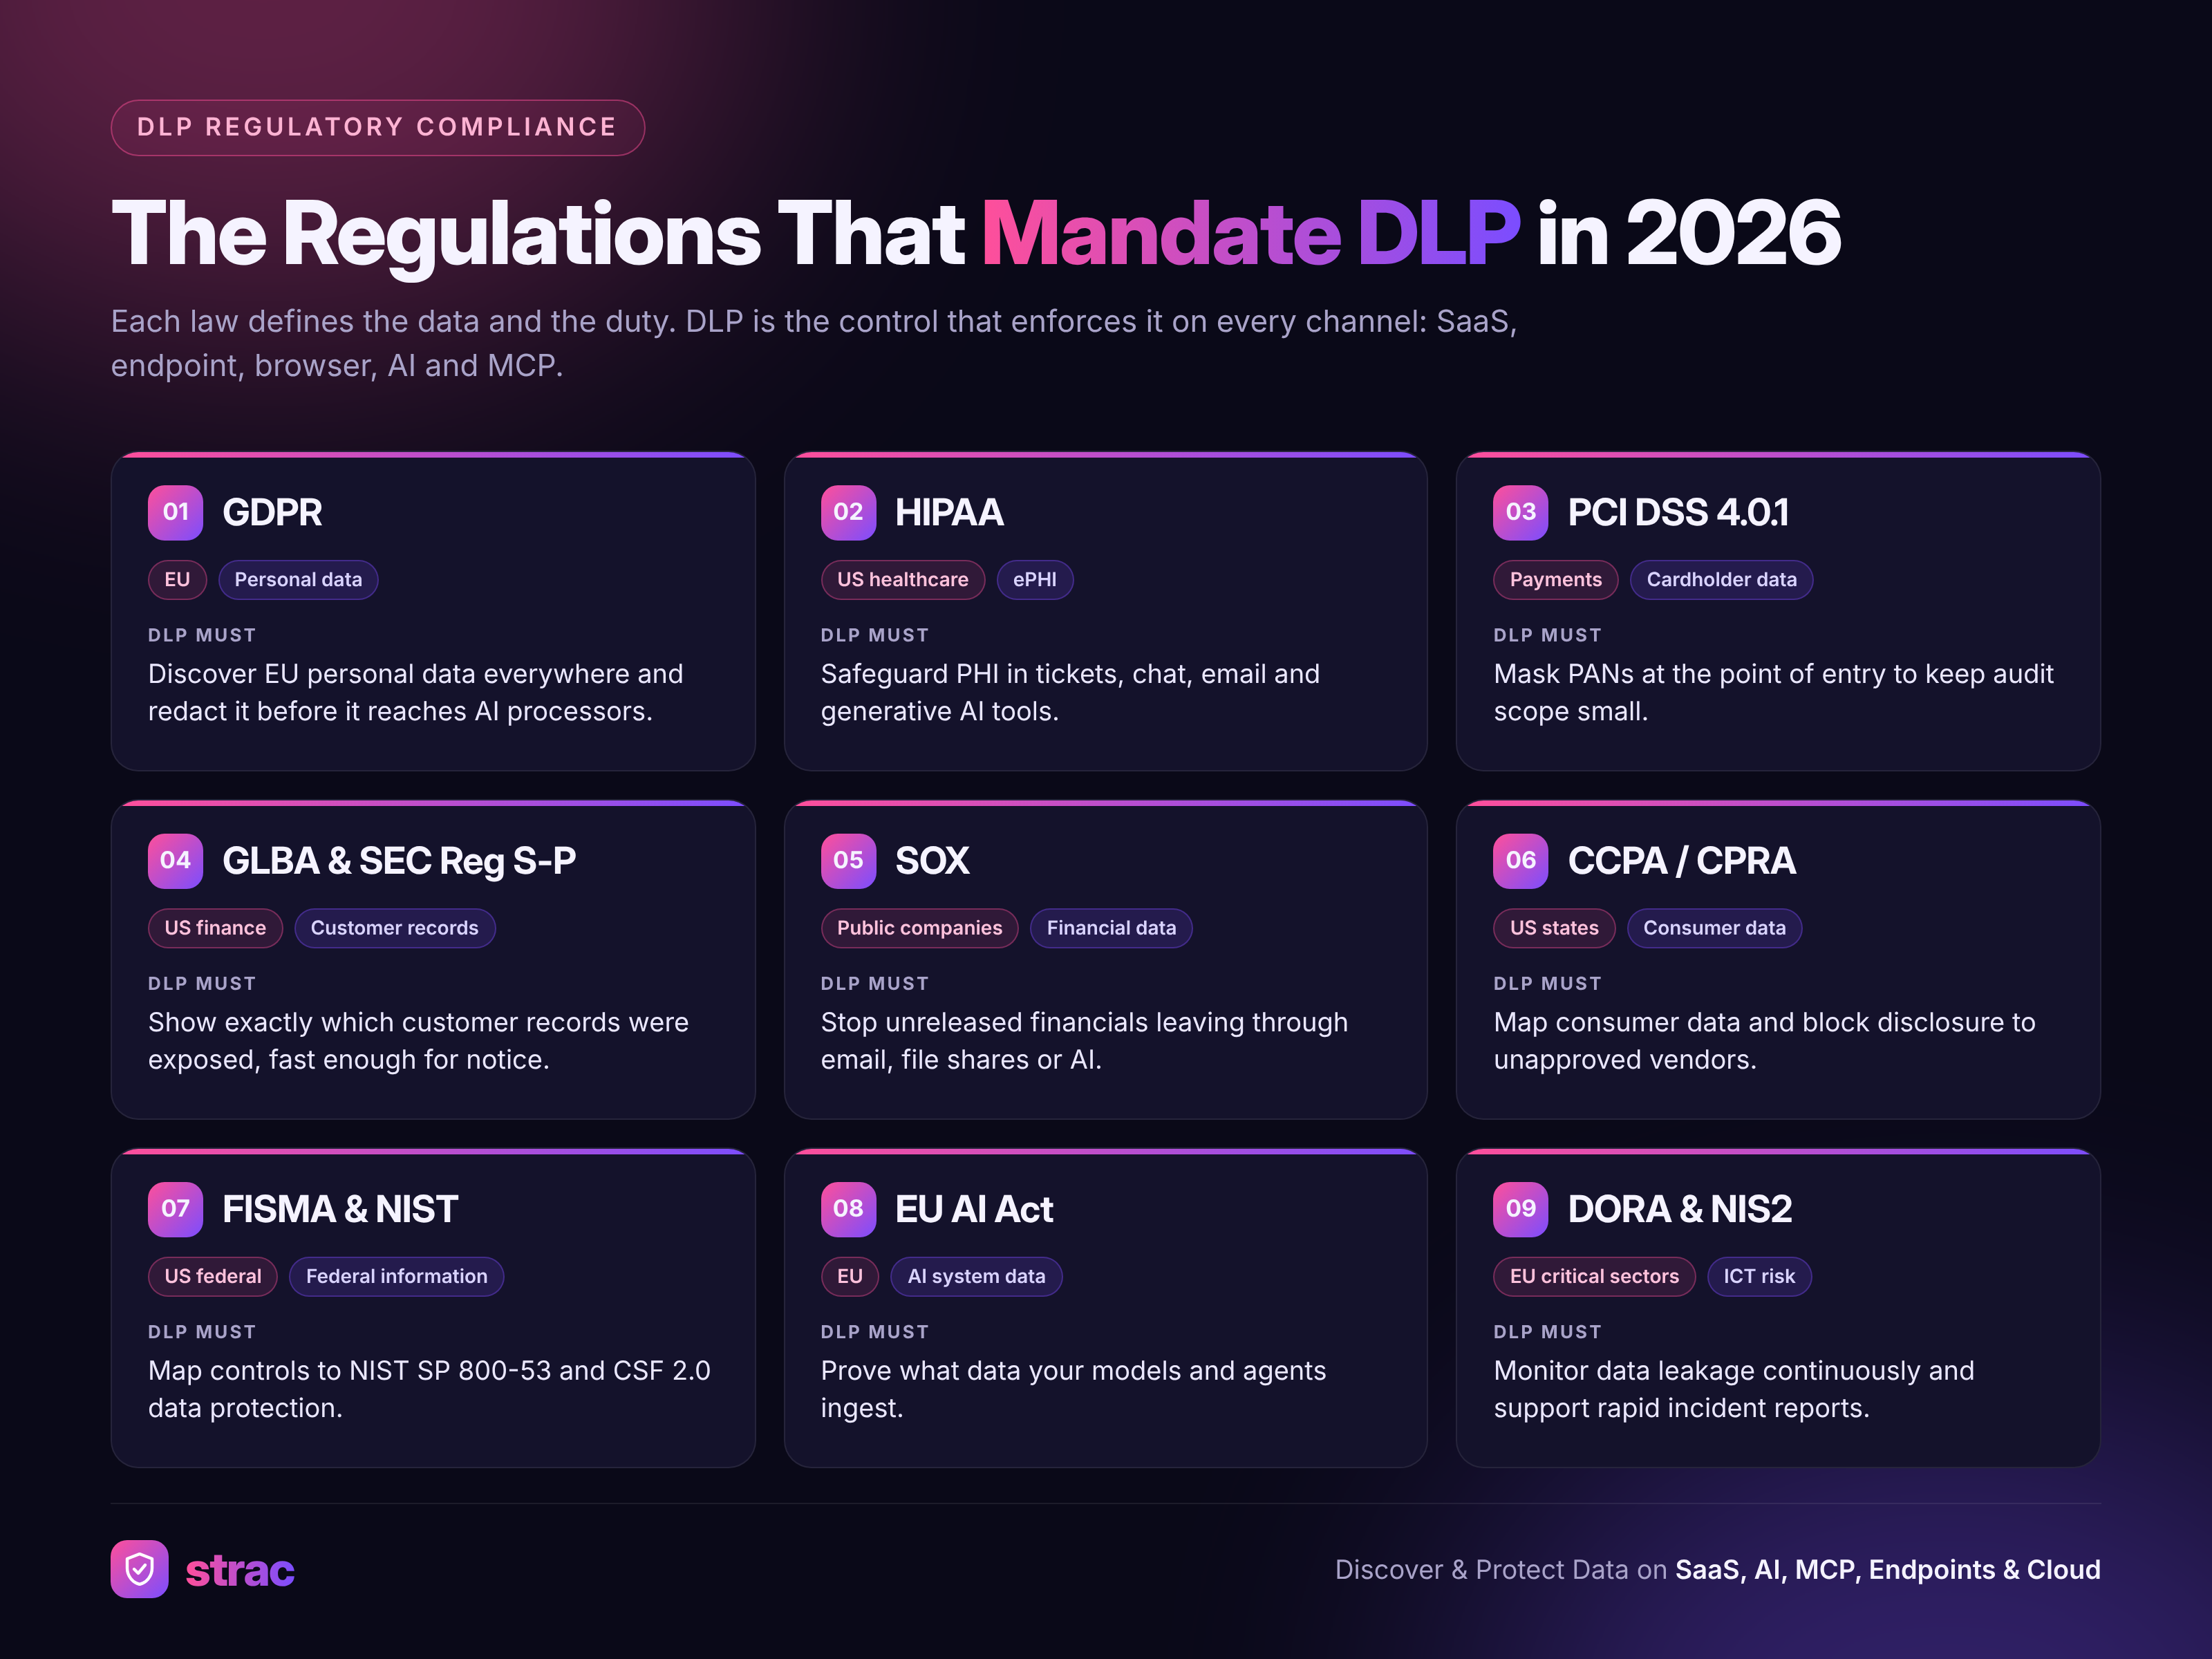
GDPR requires appropriate technical measures to protect personal data, data minimization, and breach notification to the supervisory authority within 72 hours. Fines reach 4% of global annual turnover. For DLP, that means sensitive data discovery and classification across every system holding EU personal data, plus redaction before personal data reaches a third-party AI processor.
The HIPAA Security Rule requires safeguards for ePHI wherever it is created, stored or transmitted. The proposed Security Rule update from HHS would make encryption, asset inventories and data flow mapping far less optional, and covered entities are preparing now rather than waiting for the final rule. HIPAA DLP has to cover the places PHI actually travels today: tickets, chat, email and generative AI tools. See data loss prevention in healthcare for the clinical workflow view.
PCI DSS 4.0.1 made its future-dated requirements mandatory in 2025, including stronger scope confirmation and protection of primary account numbers outside the cardholder data environment. A PAN in a Zendesk ticket or a Slack message pulls that system into scope. PCI DLP with PCI DSS PAN masking keeps scope small by removing the number at the point of entry.
GLBA's Safeguards Rule requires financial institutions to protect customer financial information with a written security program. The amended SEC Regulation S-P adds incident response programs and 30-day customer notification for broker-dealers and advisers, with smaller firms required to comply from June 2026. Both reward knowing exactly which customer records were exposed, which is a DLP question before it is a legal one.
SOX requires internal controls over financial reporting data. DLP supports it by stopping unreleased financials and material nonpublic information from leaving through email, file sharing or AI tools, and by logging who accessed what.
California and a growing list of states give consumers rights over personal information and require reasonable security. CCPA DLP controls focus on knowing where consumer data sits, so access and deletion requests are answerable, and on preventing disclosure to unapproved vendors.
Federal agencies and their contractors follow FISMA through NIST controls. NIST data loss prevention maps DLP to the data protection, access control and monitoring families in NIST SP 800-53 and NIST CSF 2.0.
The EU AI Act adds data governance duties for AI systems. Transparency obligations under Article 50 applied from August 2026, while the Digital Omnibus agreement moved standalone high-risk obligations to December 2027. Either way, the act assumes you know what data your AI systems ingest, which is exactly what AI data governance and AI DLP are built to show.
DORA requires EU financial entities to manage ICT risk, including data leakage, and to report major incidents fast. NIS2 extends similar security and reporting duties to essential and important entities across sectors. Both expect continuous monitoring rather than an annual review.
Strip away the legal vocabulary and the regulations converge on five requirements:
The remediation ladder that meets all five, in order:
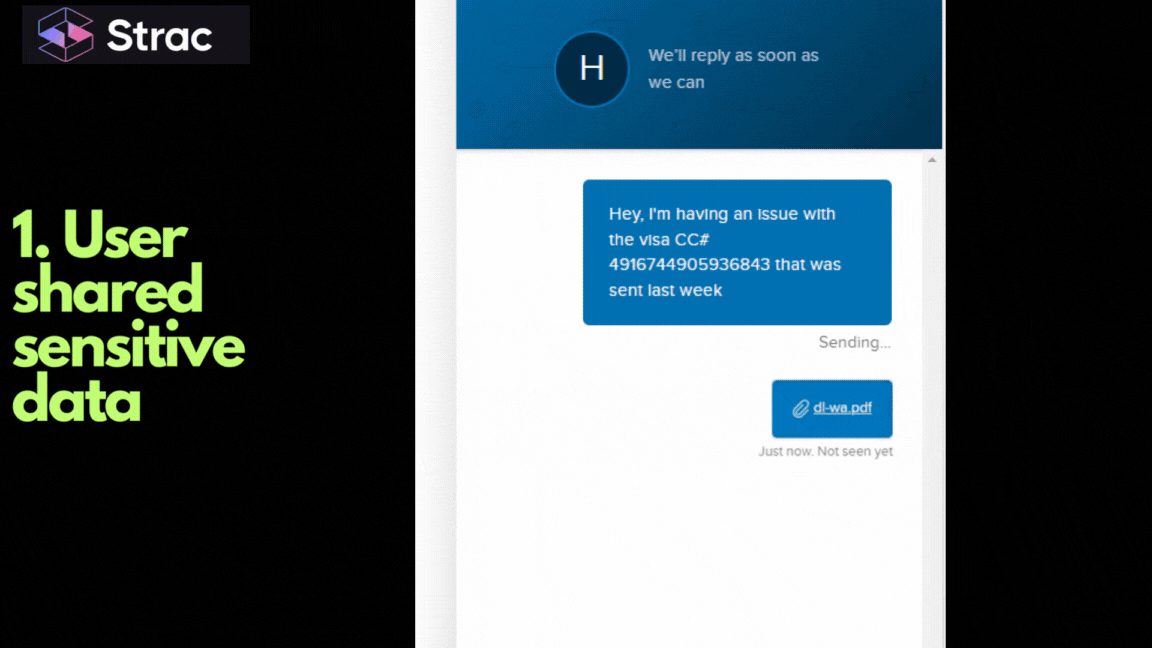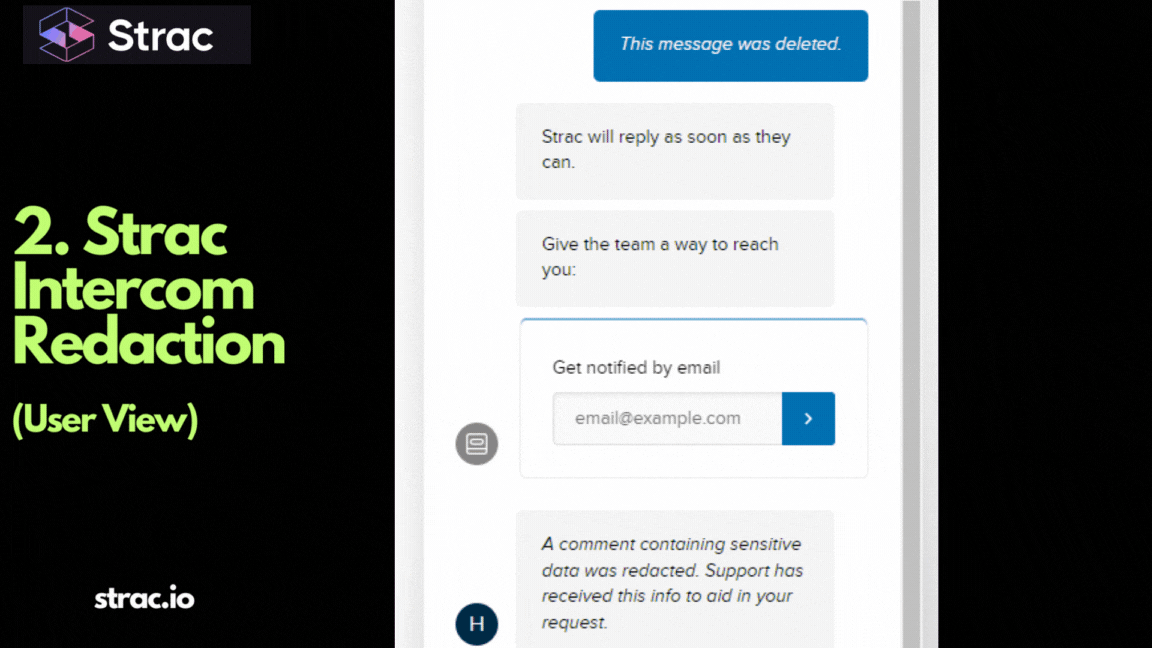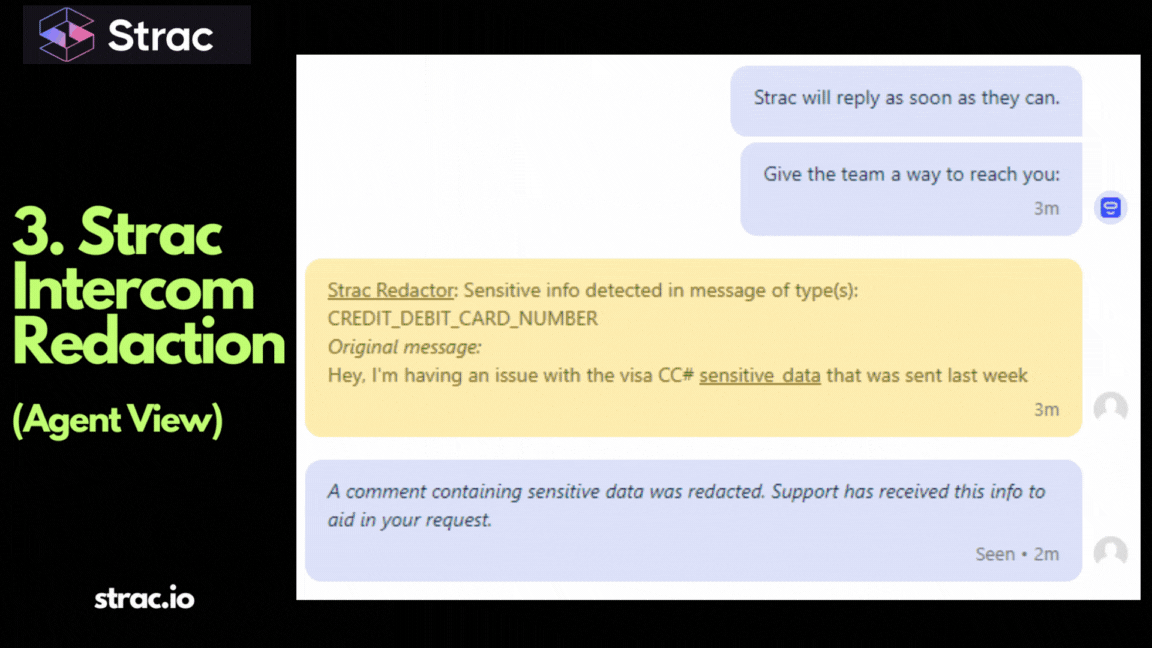
A regulator does not ask whether you detected the record; it asks whether the record left. Strac makes the answer "no" at the moment of the action.
Redaction is the control most regulations quietly prefer. Blocking stops the workflow and pushes people to personal devices, which removes the audit trail entirely. Redaction keeps the workflow and removes only the regulated element, so the record of the control and the protection of the data happen in the same step.
Strac applies one set of detectors and policies to every channel regulated data touches.
SaaS. SaaS DLP scans and remediates in real time and historically across Slack DLP, Gmail DLP, Google Drive DLP, Zendesk, Salesforce, Jira, Box, OneDrive and more. OCR reads screenshots, PDFs and scanned forms, where card numbers and IDs often hide.
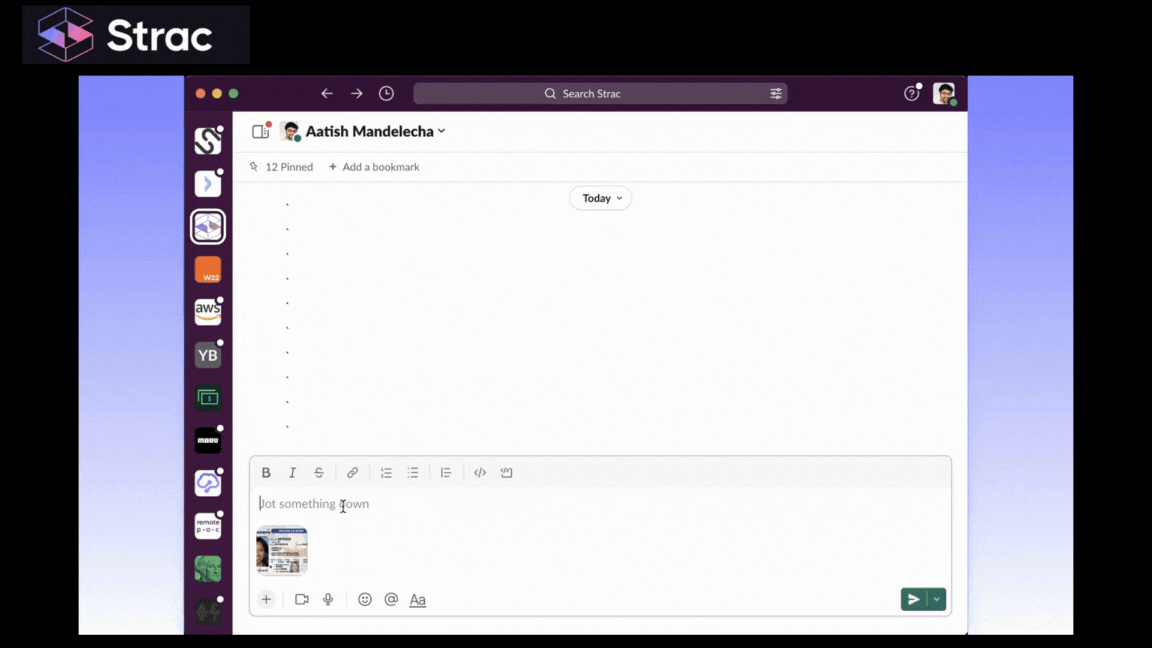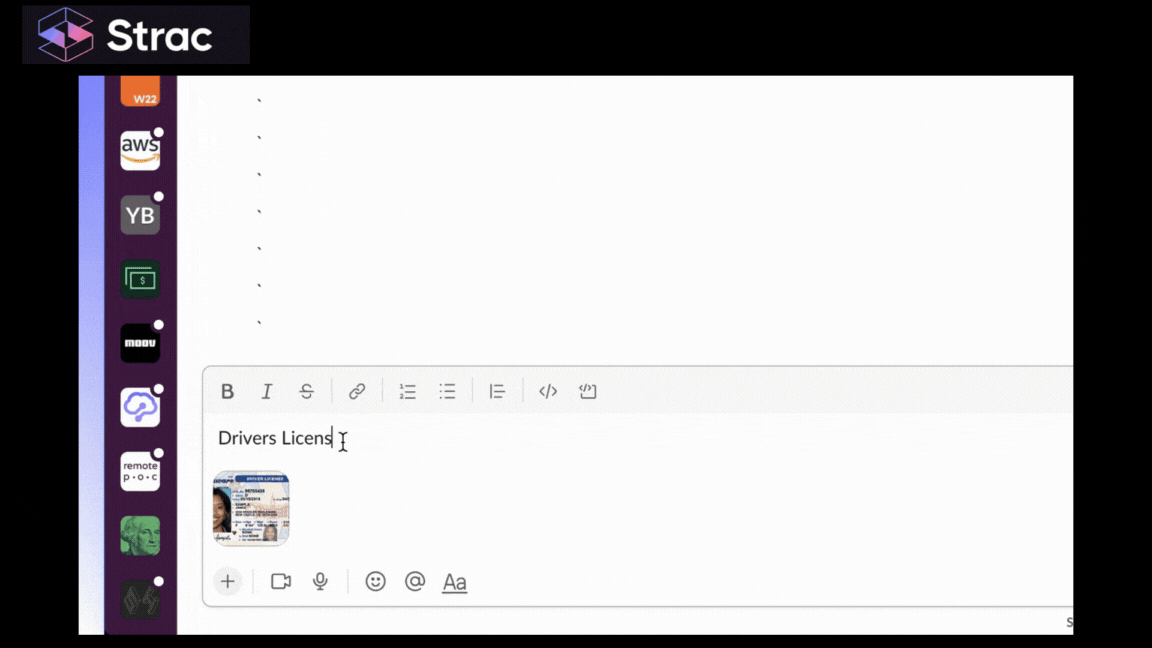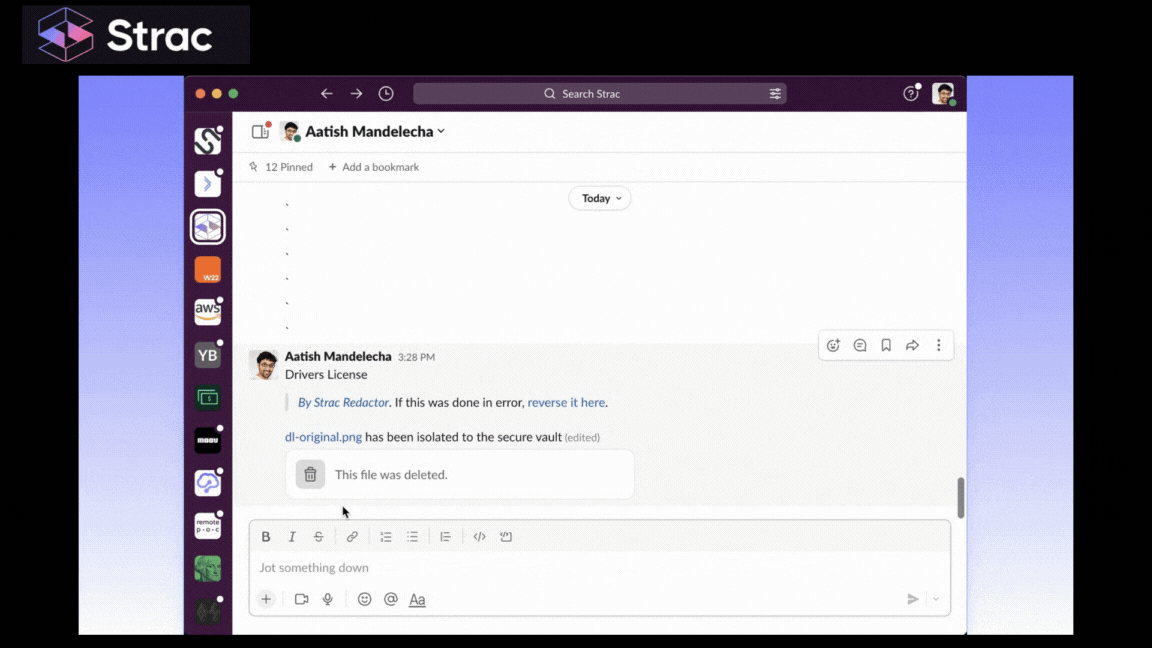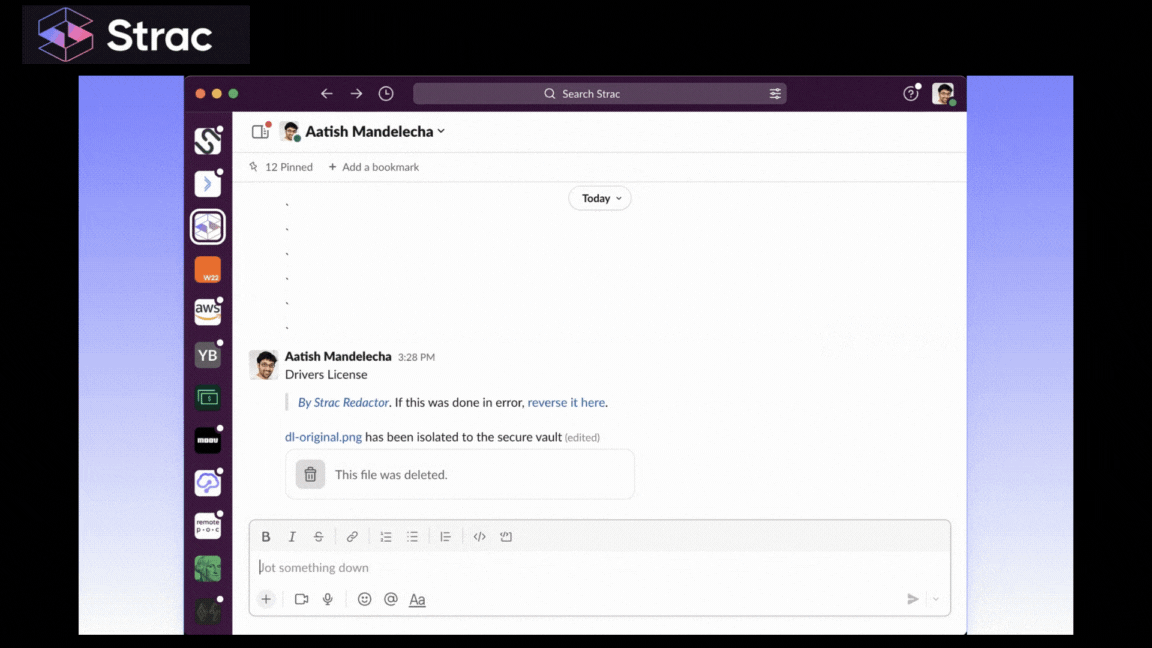
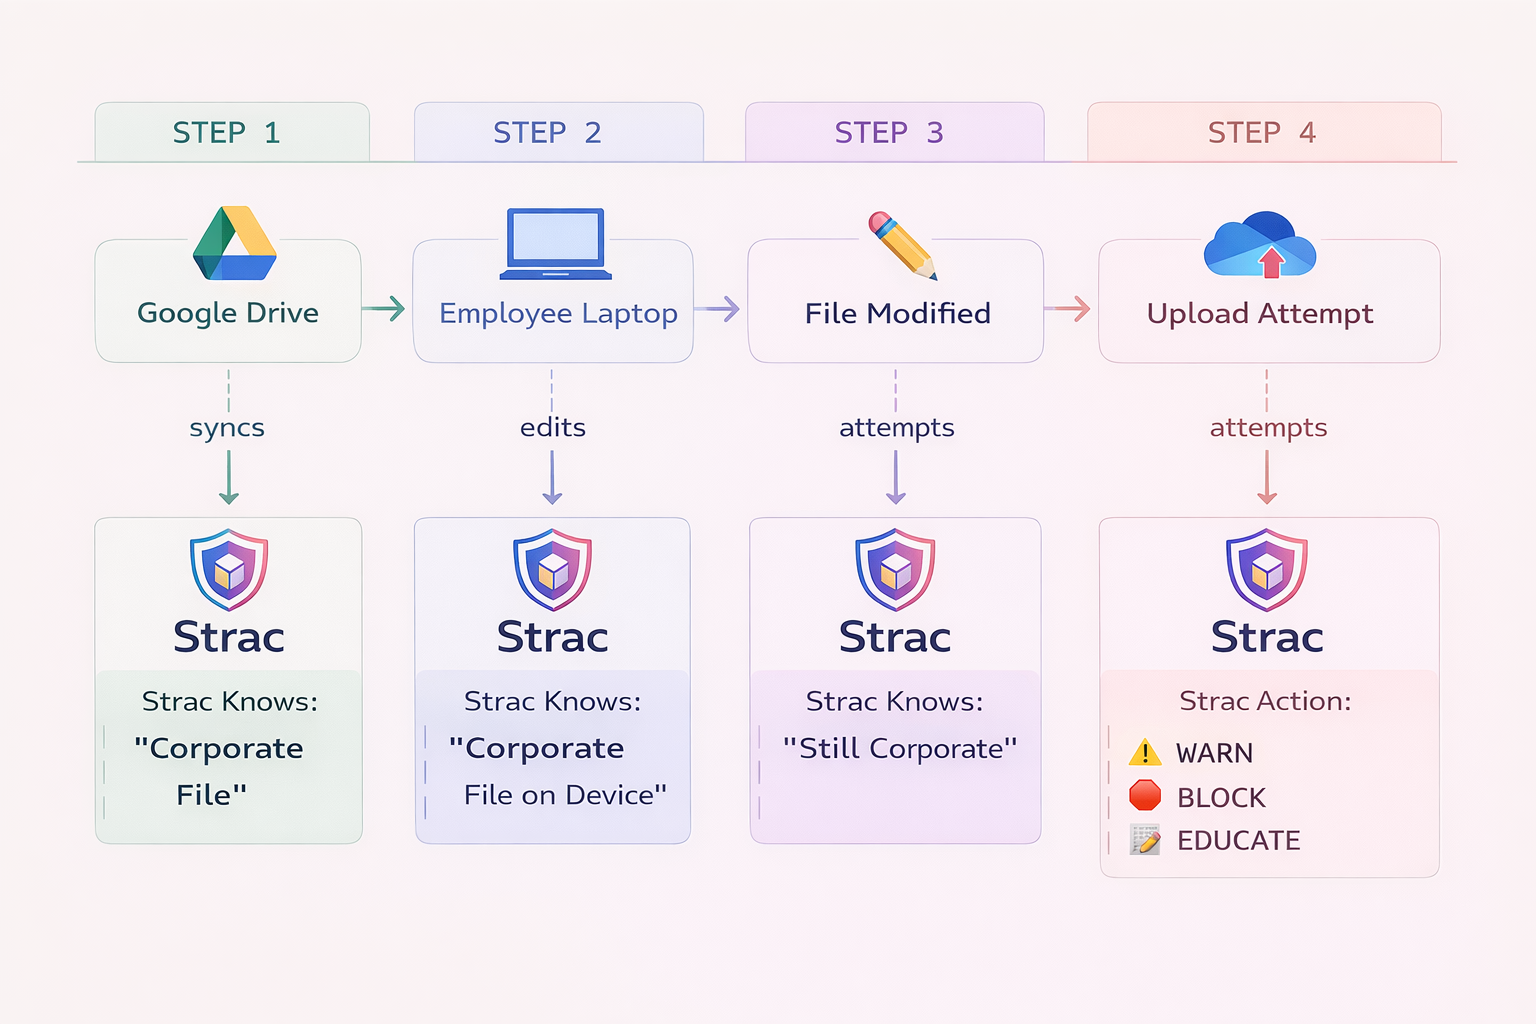
Endpoint. Endpoint DLP on Windows, Mac and Linux adds data lineage: Strac fingerprints files that originate in Google Drive, SharePoint, Box or OneDrive and follows them through renames and edits, blocking exfiltration to unapproved destinations.
Browser and generative AI. Browser DLP and AI DLP inspect pastes and uploads to ChatGPT, Claude, Gemini and unsanctioned tools, with warn, nudge, redact or block per policy. ChatGPT DLP covers the most common destination natively.
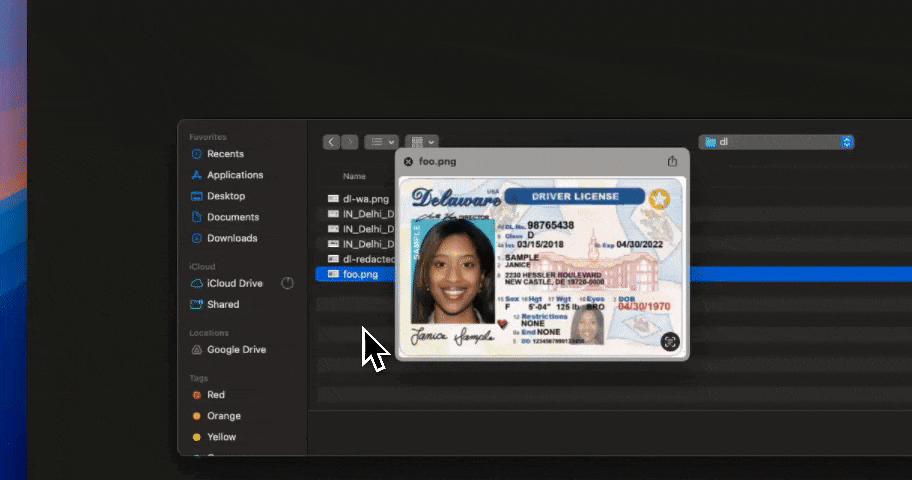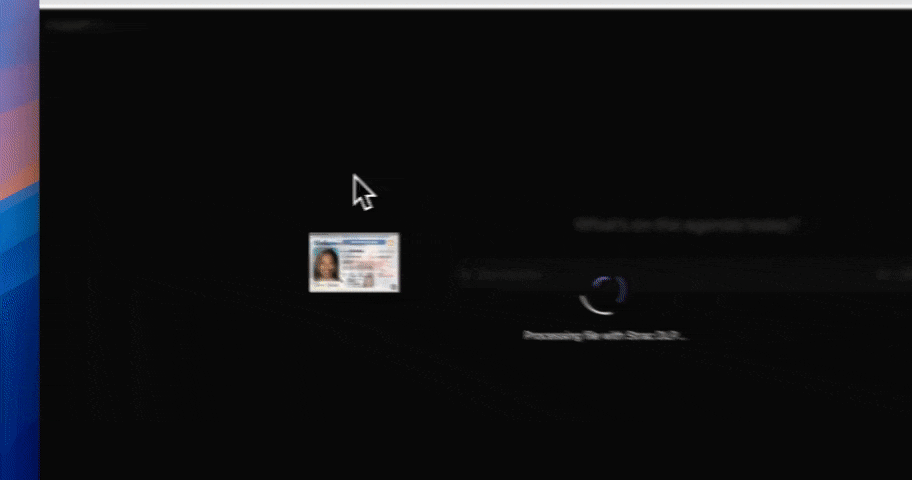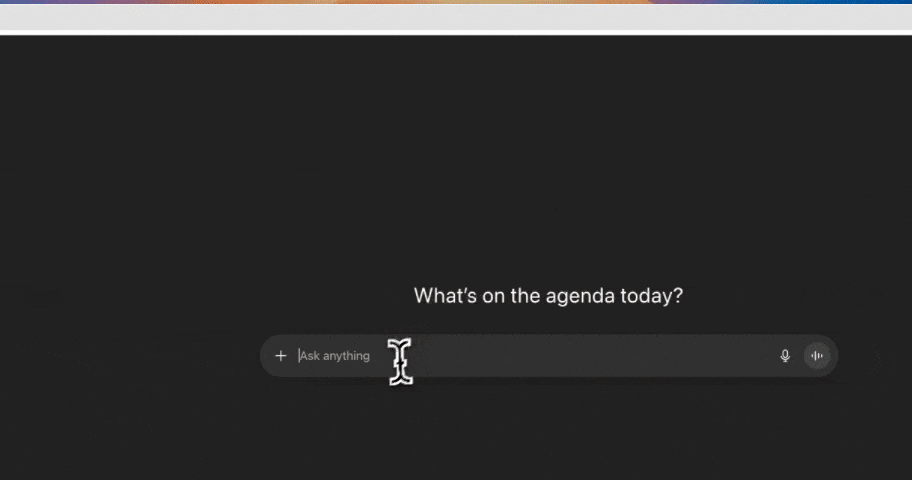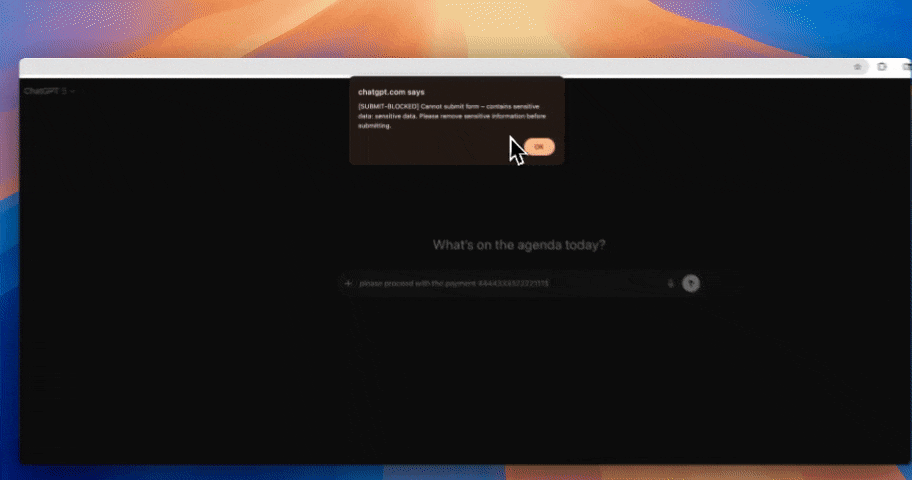
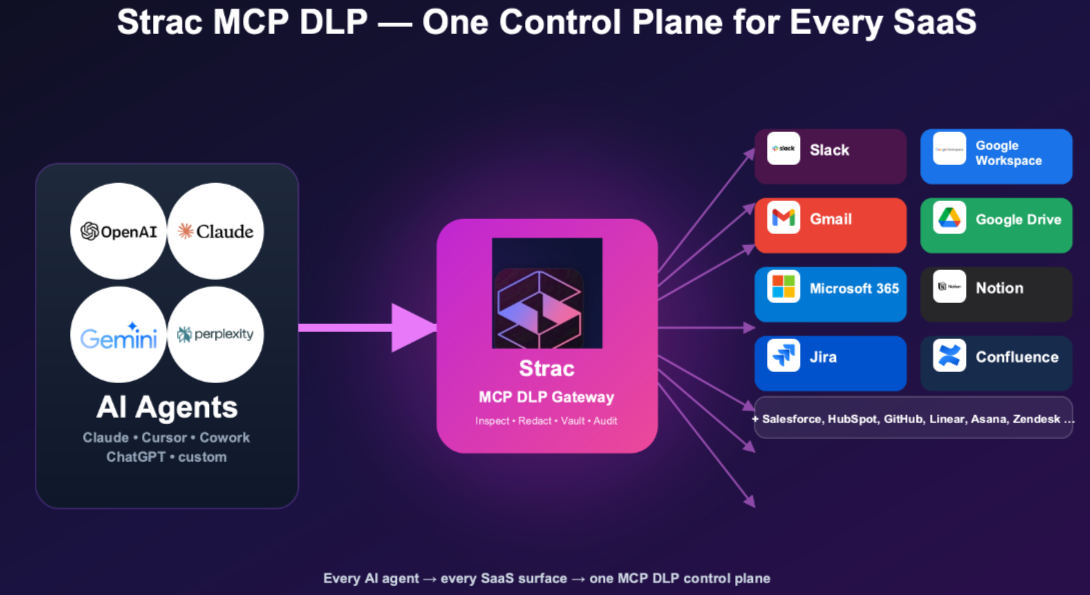
Agents. MCP DLP redacts regulated data before it reaches a model, monitors agent tool calls, and flags prompt injection patterns.
Posture. DSPM revokes public and external sharing, applies classification labels, and monitors for misconfigurations continuously.
Proof. Strac Comply runs automated tests and maps evidence across SOC 2, ISO 27001, PCI DSS, GDPR, HIPAA and NIST CSF 2.0, so one remediation event answers several regulators at once. Framework detail lives on the SOC 2 DLP and ISO 27001 DLP pages.
Integration takes minutes, and detectors for PII, PHI, PCI data, secrets and source code ship built in, with custom detectors for your own identifiers.
Days 0 to 30: Discover. List every regulation in scope. Run discovery across SaaS, cloud and endpoints, and inventory the generative AI tools and MCP servers in use. Test detectors with the PII scanner on real files.
Days 30 to 60: Protect. Turn on redaction for PCI data and PHI in chat, email and tickets. Apply Browser DLP and AI DLP policies to generative AI. Revoke public links on files holding regulated data.
Days 60 to 90: Prove and scale. Map each policy to its regulation and control ID. Export evidence on a schedule. Extend MCP DLP to every agent that touches customer data, and name an owner per regulation.
Policies, access controls and vendor contracts all fail eventually, and regulators judge the outcome, not the paperwork. The data layer is the backstop: redact regulated data on every action and a compromise never becomes a reportable breach. Strac enforces that control across SaaS, endpoint, browser, AI and MCP, and maps the proof to every regulation you carry.
Not by name. None of them says "buy DLP." Each requires you to protect a defined class of data and prove it, and DLP is the most direct technical control for doing that across SaaS, endpoints and AI tools.
Because it inspects email and file shares, not browser pastes, AI uploads or agent tool calls. Regulated data that leaves through ChatGPT or an MCP server is still a reportable disclosure, and legacy DLP never sees it.
Yes. Redaction removes the regulated element before the prompt reaches the model, so people keep using the tool and the data never leaves. Bans push usage to personal devices, which is worse for compliance, not better.
No. Detection has false negatives and attackers find new channels. That is why the data layer matters: when regulated data is redacted by default, a bypassed control exposes far less, and the incident may never meet the notification threshold.
It adds data governance duties to AI systems, so you need to show what data your models and agents ingest. AI DLP and MCP DLP produce that record. See AI data governance for the full program.