October 29, 2026

8
min read
A Complete Guide to Credential Exposure: Causes & Prevention
Learn what credential exposure is, the 9 types of exposed credentials, how they leak in 2026, and how to stop leaked keys and tokens from becoming breaches.
One leaked key can open a cloud account, a production database or a customer support system. In 2025 alone, developers pushed 28.65 million new hardcoded secrets to public GitHub, a 34% jump in a single year (GitGuardian). This guide covers the credential types that matter, how they leak in 2026, and the steps that actually lower the risk.
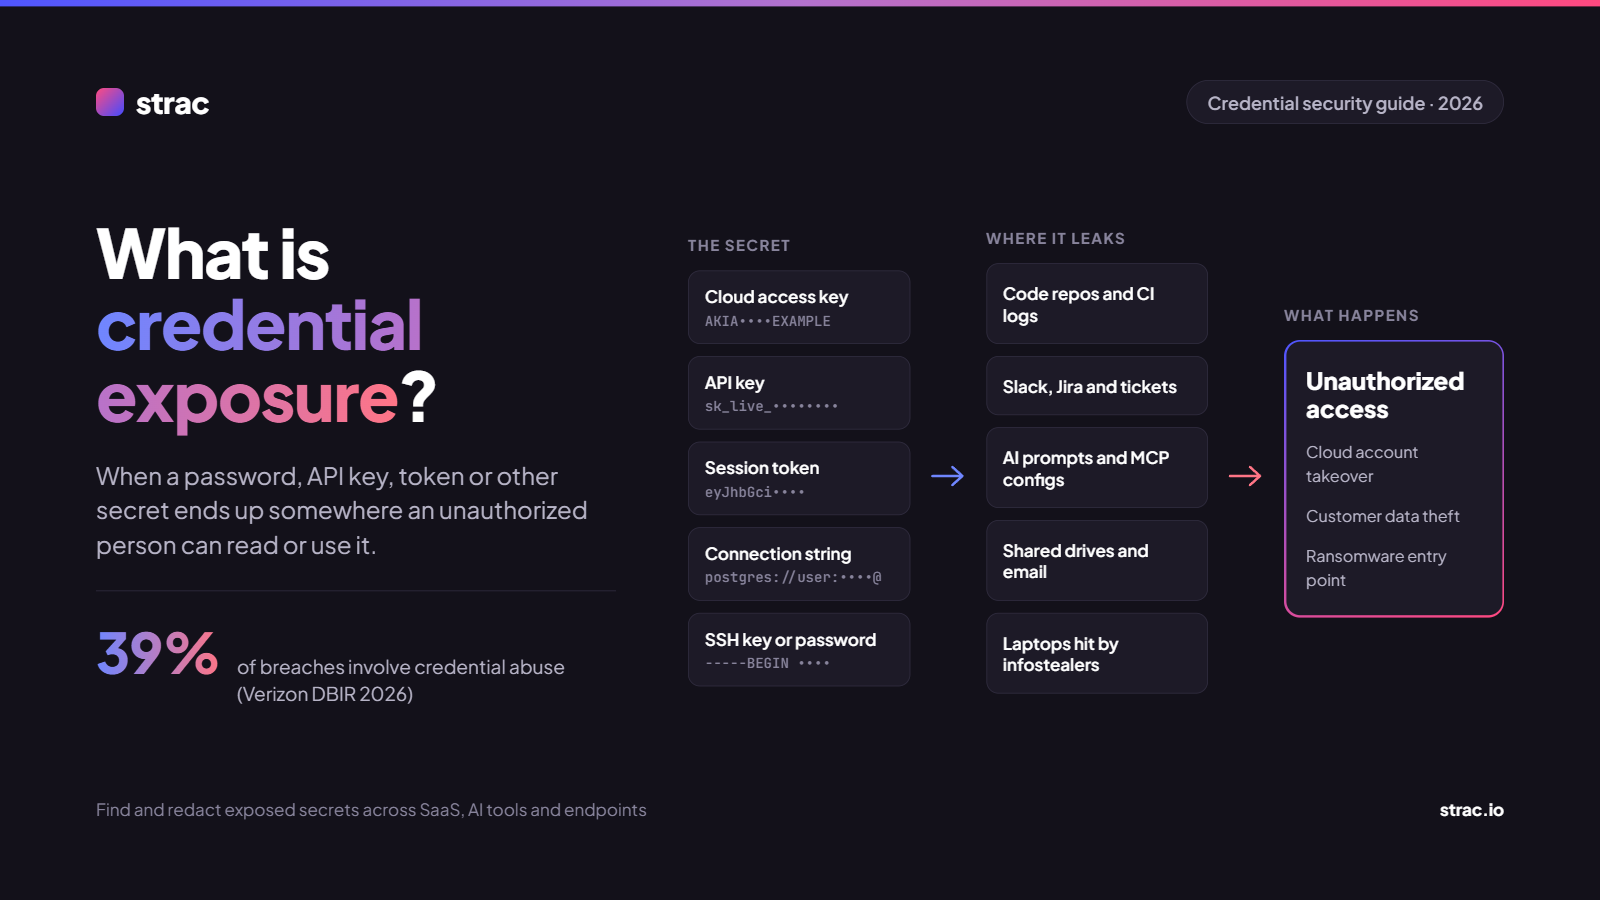
Credential exposure is the unauthorized disclosure of anything that proves identity or grants access. That includes usernames and passwords, API keys, cloud access keys, OAuth and session tokens, SSH and private keys, database connection strings and CI/CD tokens.
Credentials come in two kinds. Human credentials belong to people and usually sit behind a login page. Machine credentials, also called non-human identities, belong to services, scripts, pipelines and AI agents. Machine credentials now far outnumber human ones, and they rarely have MFA in front of them.
Exposure is not the same as compromise, but the gap between the two keeps shrinking. A key pushed to a public repository or pasted into a shared Slack channel can be picked up by automated scanners or curious insiders long before anyone notices it is there.
Stolen credentials remain the main way attackers move inside a company, even when they get in some other way.
The 2024 Snowflake campaign shows how this plays out. Attackers used credentials stolen by infostealer malware, some dating back to 2020, to reach about 165 customer environments. The accounts had no MFA, the passwords had never been rotated, and about 80% of the accounts used had prior credential exposure (SecurityWeek).
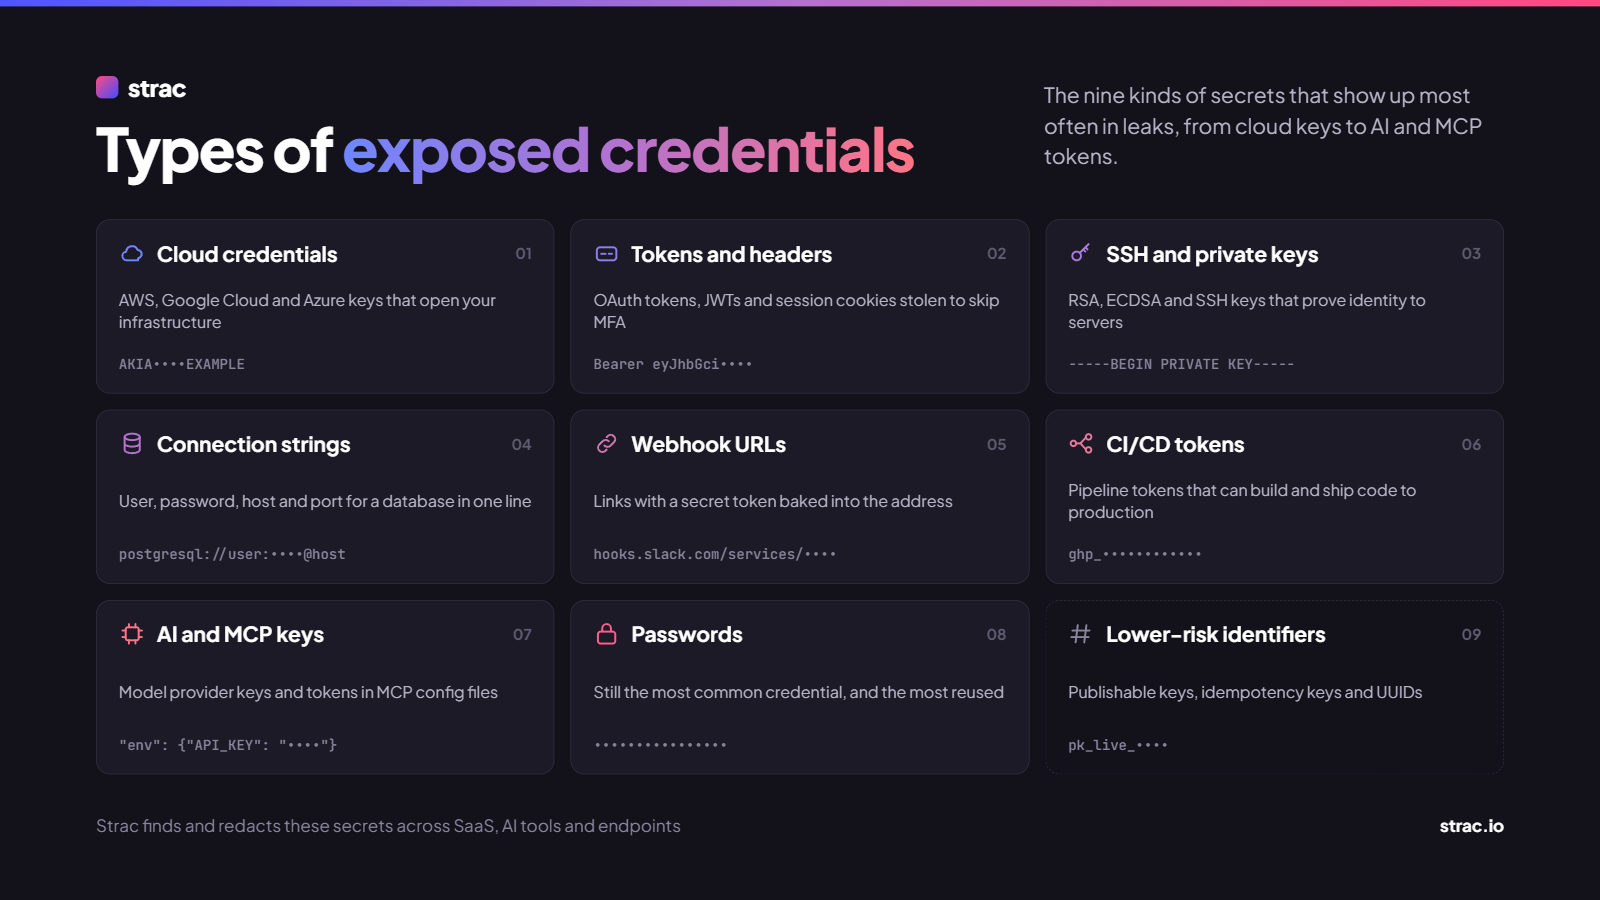
The credentials below are the ones that show up most often in leaks. For a longer list of sensitive data types, see the Strac sensitive data catalog.
Cloud keys give direct access to infrastructure, so they are the first thing attackers search for. Cloud data loss prevention matters most here.
AKIAIOSFODNN7EXAMPLE. Real keys follow the same AKIA pattern, which makes them easy for scanners to find.Symmetric keys, such as AES keys, use one key to encrypt and decrypt, so the key itself must stay secret. Asymmetric keys, such as RSA and ECDSA, come in public and private pairs, and only the private half needs protecting. SSH private keys work like an ID badge for servers. A private key that lands in a repo, a ticket or a shared drive gives anyone who finds it the same access as its owner. Older algorithms like DES should no longer be used at all.
A connection string bundles the username, password, host, port and database name into one line, for example postgresql://user:password@host:5432/dbname. That makes it convenient for developers and dangerous when it ends up in a log file, a Jira ticket or a Postgres dump shared for debugging.
Many webhook URLs carry a secret token inside the URL itself. Anyone with a Slack incoming webhook URL, for example, can post messages into that channel. Treat webhook URLs as secrets, not as plain links.
Tokens for GitHub Actions, GitLab CI, Jenkins and CircleCI can build and deploy code, so a stolen one can push malicious code straight to production. CI systems also hold many other secrets as environment variables, which makes them a prime target.
This category barely existed two years ago. API keys for OpenAI, Anthropic and other model providers are now one of the fastest-growing types of leaked secret. MCP (Model Context Protocol) servers add another layer: their config files often hold tokens for GitHub, Slack, databases and cloud accounts in plain text. Prompts sent to ChatGPT or Claude can also carry pasted keys. See MCP DLP for how to control what flows through MCP tool calls.
Passwords are still the most common credential. Current NIST guidance favors long passphrases (at least 15 characters when a password is the only factor), checks against lists of breached passwords, and a password manager, rather than complex rules and forced changes.
Some values look like secrets but carry less risk. They still deserve care.
pk_. They are safe to expose, but their secret counterparts (sk_) are not.Most leaks are not clever attacks. They are secrets left in places people use every day.
Developers hardcode keys to get something working and forget to take them out. Private repos are not safe either: GitGuardian found internal repositories are about six times more likely to contain hardcoded secrets than public ones (Superblocks summary). AI coding assistants make it worse. Commits written with AI help leaked secrets at about double the normal rate, 3.2% against a 1.5% baseline (GitGuardian data via Vibe Graveyard).
Engineers share keys to unblock each other, support agents paste customer logins into tickets, and nobody cleans up afterwards. Common places to find live credentials include:
These messages stay searchable for years, so one compromised Slack or Google account can expose every key ever shared there.
People paste config files, stack traces and .env files into ChatGPT, Claude and other generative AI tools to get help debugging. AI agents connected through MCP can read and pass along tokens they find. Once a key leaves your environment in a prompt, you lose control of where it is stored.
Infostealers pull saved passwords, session cookies and local files from browsers and laptops, often from personal or contractor devices used for work. The Snowflake campaign above ran almost entirely on infostealer logs. Plain-text keys sitting in .env files, shell history and notes apps on a Mac or Linux machine are easy pickings.
When one site is breached, attackers try the same email and password everywhere else. The LinkedIn breach is a classic example: passwords stolen in 2012 resurfaced for sale in 2016, when more than 100 million account credentials were offered online and used against other services (Fortune).
Default and guessable passwords still turn up in serious incidents. The 2017 Equifax breach started with an unpatched Apache Struts flaw. During the fallout, reporters also found that an Equifax employee portal in Argentina used "admin" as both its username and password (CNBC).
Storing passwords in plain text, using weak hashing, or logging secrets by accident all leave credentials readable to anyone who gets inside. In 2019, Facebook admitted that hundreds of millions of user passwords had been stored in plain text and were searchable by thousands of employees (KrebsOnSecurity).
A key that never expires and can do everything turns a small leak into a full breach. Many machine credentials are created once, given broad permissions, and never rotated because nobody is sure what will break.
Every app your team connects to Google Workspace, Microsoft 365 or Slack holds a token into your data. The 2026 DBIR found a third party involved in 48% of breaches (NHI Mgmt Group summary). Old integrations and AI apps nobody approved are common blind spots.
Prevention comes down to three things: make credentials harder to steal, make stolen ones less useful, and find leaked ones before attackers do. Use the steps below alongside a DLP security checklist.
MFA is still the single best defense against stolen passwords, but not all MFA is equal. The final NIST SP 800-63B-4 guidance lists SMS and phone-call codes as its only "restricted" authenticator, and it requires services at AAL2 to offer a phishing-resistant option (MojoAuth summary of NIST 800-63B-4).
NIST no longer recommends forced password changes on a schedule. Rotate a password only when there is a sign it was exposed (Optro summary of NIST 800-63B Rev 4).
You cannot stop every person from pasting a key into Slack. You can find it within seconds and redact it. Scan your SaaS apps, email, ticketing tools and file storage for API keys, tokens, private keys and connection strings, and remove old ones that have been sitting there for years. Do the same for prompts sent to AI tools through a browser DLP extension for Chrome or Edge.
A stolen password is less useful if it only works from known networks or managed devices. Use IP allowlists, device checks and conditional access for databases, data warehouses and admin consoles. The Snowflake victims had none of these in place.
Sometimes a person really does need to hand a key to a vendor or a teammate. Never send it in chat or email. Use an encrypted link that expires, such as Strac's free secure send tool, and rotate the key once the job is done.
CAPTCHA once slowed down credential stuffing, but modern bots and solving services get past most of them. Pair it with rate limiting, breached-password checks at login, and alerts for logins from new devices or locations.
Run regular security awareness training, review who has access to what every quarter, and remove access as soon as someone changes roles or leaves. Insiders, including contractors and partners, can expose credentials by accident or on purpose, so give everyone the least access they need.
Strac finds secrets and other sensitive data wherever your team works, removes them before they spread, and gives you the evidence auditors ask for.
Strac connects without code and starts scanning in minutes. Book a demo to see it on your own Slack, Google Workspace or AI tools, or start a free Strac Comply trial.
Credential exposure is no longer mostly about weak passwords. In 2026, the bigger risk is the steady pile of keys, tokens and connection strings sitting in code, Slack threads, support tickets, AI prompts and laptops, many of them still valid years later.
You will not stop every leak, so plan for them. Put phishing-resistant MFA in front of every account, swap long-lived keys for short-lived ones, keep secrets in a vault instead of in code, and scan the tools where people paste things so a leaked key is caught in minutes, not months. When a secret does get out, revoke it first and ask questions later.
Strac handles the finding and redacting across your SaaS apps, AI tools and endpoints, and Strac Comply proves to auditors that those controls are running every day.
Exposure means a credential is somewhere it should not be. A breach means someone used it, or other weaknesses, to access data. Exposure is the warning sign. Catching it early is how you stop the breach.
Not for user passwords. NIST now advises changing a password only when there is evidence it was exposed. Machine credentials are different: rotate them on a schedule, or better, replace them with short-lived tokens.
It is far better than no MFA, but NIST classes it as restricted because codes can be intercepted or phished. Use passkeys or security keys for admins and sensitive systems, and plan to move everyone else off SMS over time.
Revoke or rotate it immediately. Removing it from the repo or deleting the Slack message does not help, because copies and forks may already exist. Then check logs for any use of the key.
Yes. AI-assisted commits leak secrets at about twice the normal rate, and MCP config files often store tokens in plain text. Treat AI tools as another place secrets can end up, and scan them like any other app.
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath





Customers include