

November 13, 2026

6
min read
A Quick Guide on CCPA and GDPR Data Minimization Essentials
Learn what GDPR and CCPA data minimization require in 2026, what changed in California and the EU, and how to put it into practice across SaaS and cloud apps.
Companies collect more personal data than they use. It ends up in support tickets, Slack threads, email attachments, spreadsheets and AI prompts. Every extra record is one more thing to protect, disclose, delete on request and explain to a regulator.
Data minimization is the rule that keeps this in check. This guide covers what the GDPR and the CCPA require, what changed between 2024 and 2026, where companies usually fall short, and how to put minimization into practice across your SaaS and cloud stack.
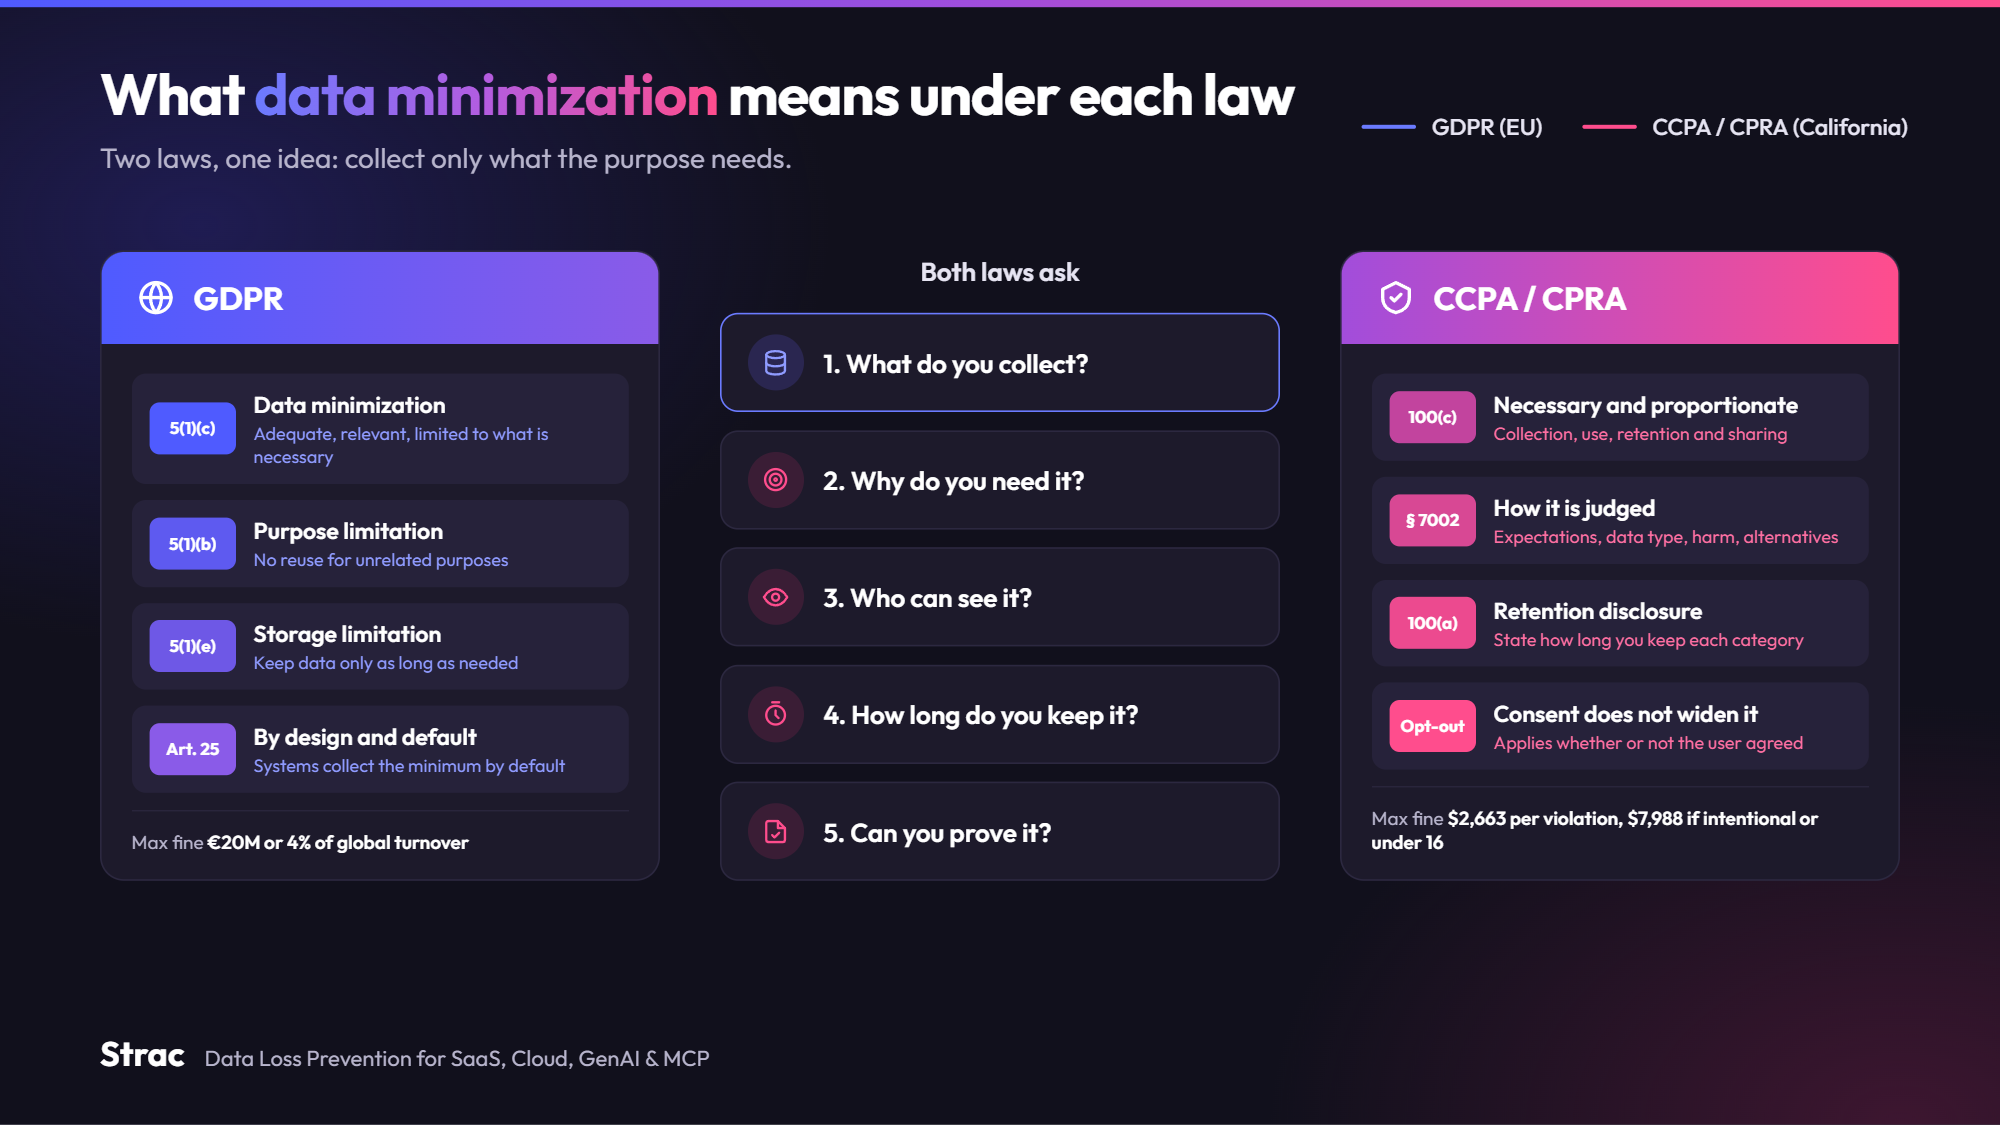
GDPR data minimization comes from Article 5(1)(c). Personal data must be adequate, relevant and limited to what is necessary for the purposes it is processed for.
Three other parts of the GDPR work alongside it:
Breaking the Article 5 principles falls in the GDPR's higher fine tier: up to 20 million euros or 4% of worldwide annual turnover, whichever is higher.
The original 2018 CCPA focused on transparency and the right to opt out. The CPRA amendments, in force since 2023, added a direct duty on the business. Under Civil Code section 1798.100(c), collecting, using, retaining and sharing personal information must be reasonably necessary and proportionate to the purpose it was collected for, or to a compatible purpose you disclosed.
The CCPA regulations at section 7002 explain how to judge this. They look at the consumer's reasonable expectations, the type of data involved, the possible harm, and whether a less intrusive option would do the job. The law also requires you to tell consumers how long you keep each category of personal information.
For a deeper look at the California side, see our guide to CPRA data minimization and our CCPA compliance page.
Both laws ask the same practical questions. What do you collect? Why? Who can see it? How long do you keep it? Can you prove all of this? If you can answer those for every system that holds personal data, you are most of the way there for both.
In April 2024, the California Privacy Protection Agency (CPPA) issued its first Enforcement Advisory, and it was about data minimization. It used consumer requests as the example. If a consumer asks to opt out of sale or sharing, you should not ask them for more personal information than that request needs.
Enforcement followed. In May 2026, General Motors was fined $12.75 million over connected-vehicle data sales and data minimization violations. Regulators are no longer only checking for a missing opt-out link. They are asking whether you needed the data at all.
CCPA fines are adjusted for inflation in odd-numbered years. Since January 1, 2025, the CPPA can fine up to $2,663 per violation, or $7,988 for intentional violations and those involving consumers under 16. Each affected consumer can count as a separate violation, so the totals add up fast.
The CPPA finalized a package of regulations in September 2025 covering risk assessments, cybersecurity audits and automated decision-making technology. There was no grace period. Risk assessments ask businesses to document what personal information they process and why, which is hard to do without a current data inventory.
The European Commission published the Digital Omnibus on November 19, 2025. It proposes changes to how personal data is defined, rules for AI training, cookie rules and a longer breach notice window. As of late July 2026 it was still awaiting a committee decision in the European Parliament. Until it passes, plan against the GDPR as written, including Article 5(1)(c).
Employees now paste customer data into ChatGPT, Claude and other assistants, and agents connect to internal systems through MCP. Personal data sent to a third-party model for a purpose the consumer never heard about is a minimization and purpose-limitation problem under both laws.
"If the user consents, we can collect it." Not true under either law. Under the GDPR, consent is one of six lawful bases in Article 6, next to contract, legal obligation, vital interests, public task and legitimate interests. Whatever basis you use, Article 5(1)(c) still limits how much you collect. The CCPA is mostly an opt-out law, and section 1798.100(c) applies whether or not the consumer agreed to anything.
"Minimization is only about collection." It also covers use, sharing and retention. Data you needed last year may be data you should delete this year.
"Our main database is clean, so we are fine." Most excess personal data is unstructured. Think of a credit card number in a Zendesk ticket, a passport scan in Google Drive, or a customer list exported to Google Sheets.
"A privacy policy covers it." A policy says what you intend to do. Regulators look at what your systems actually hold.
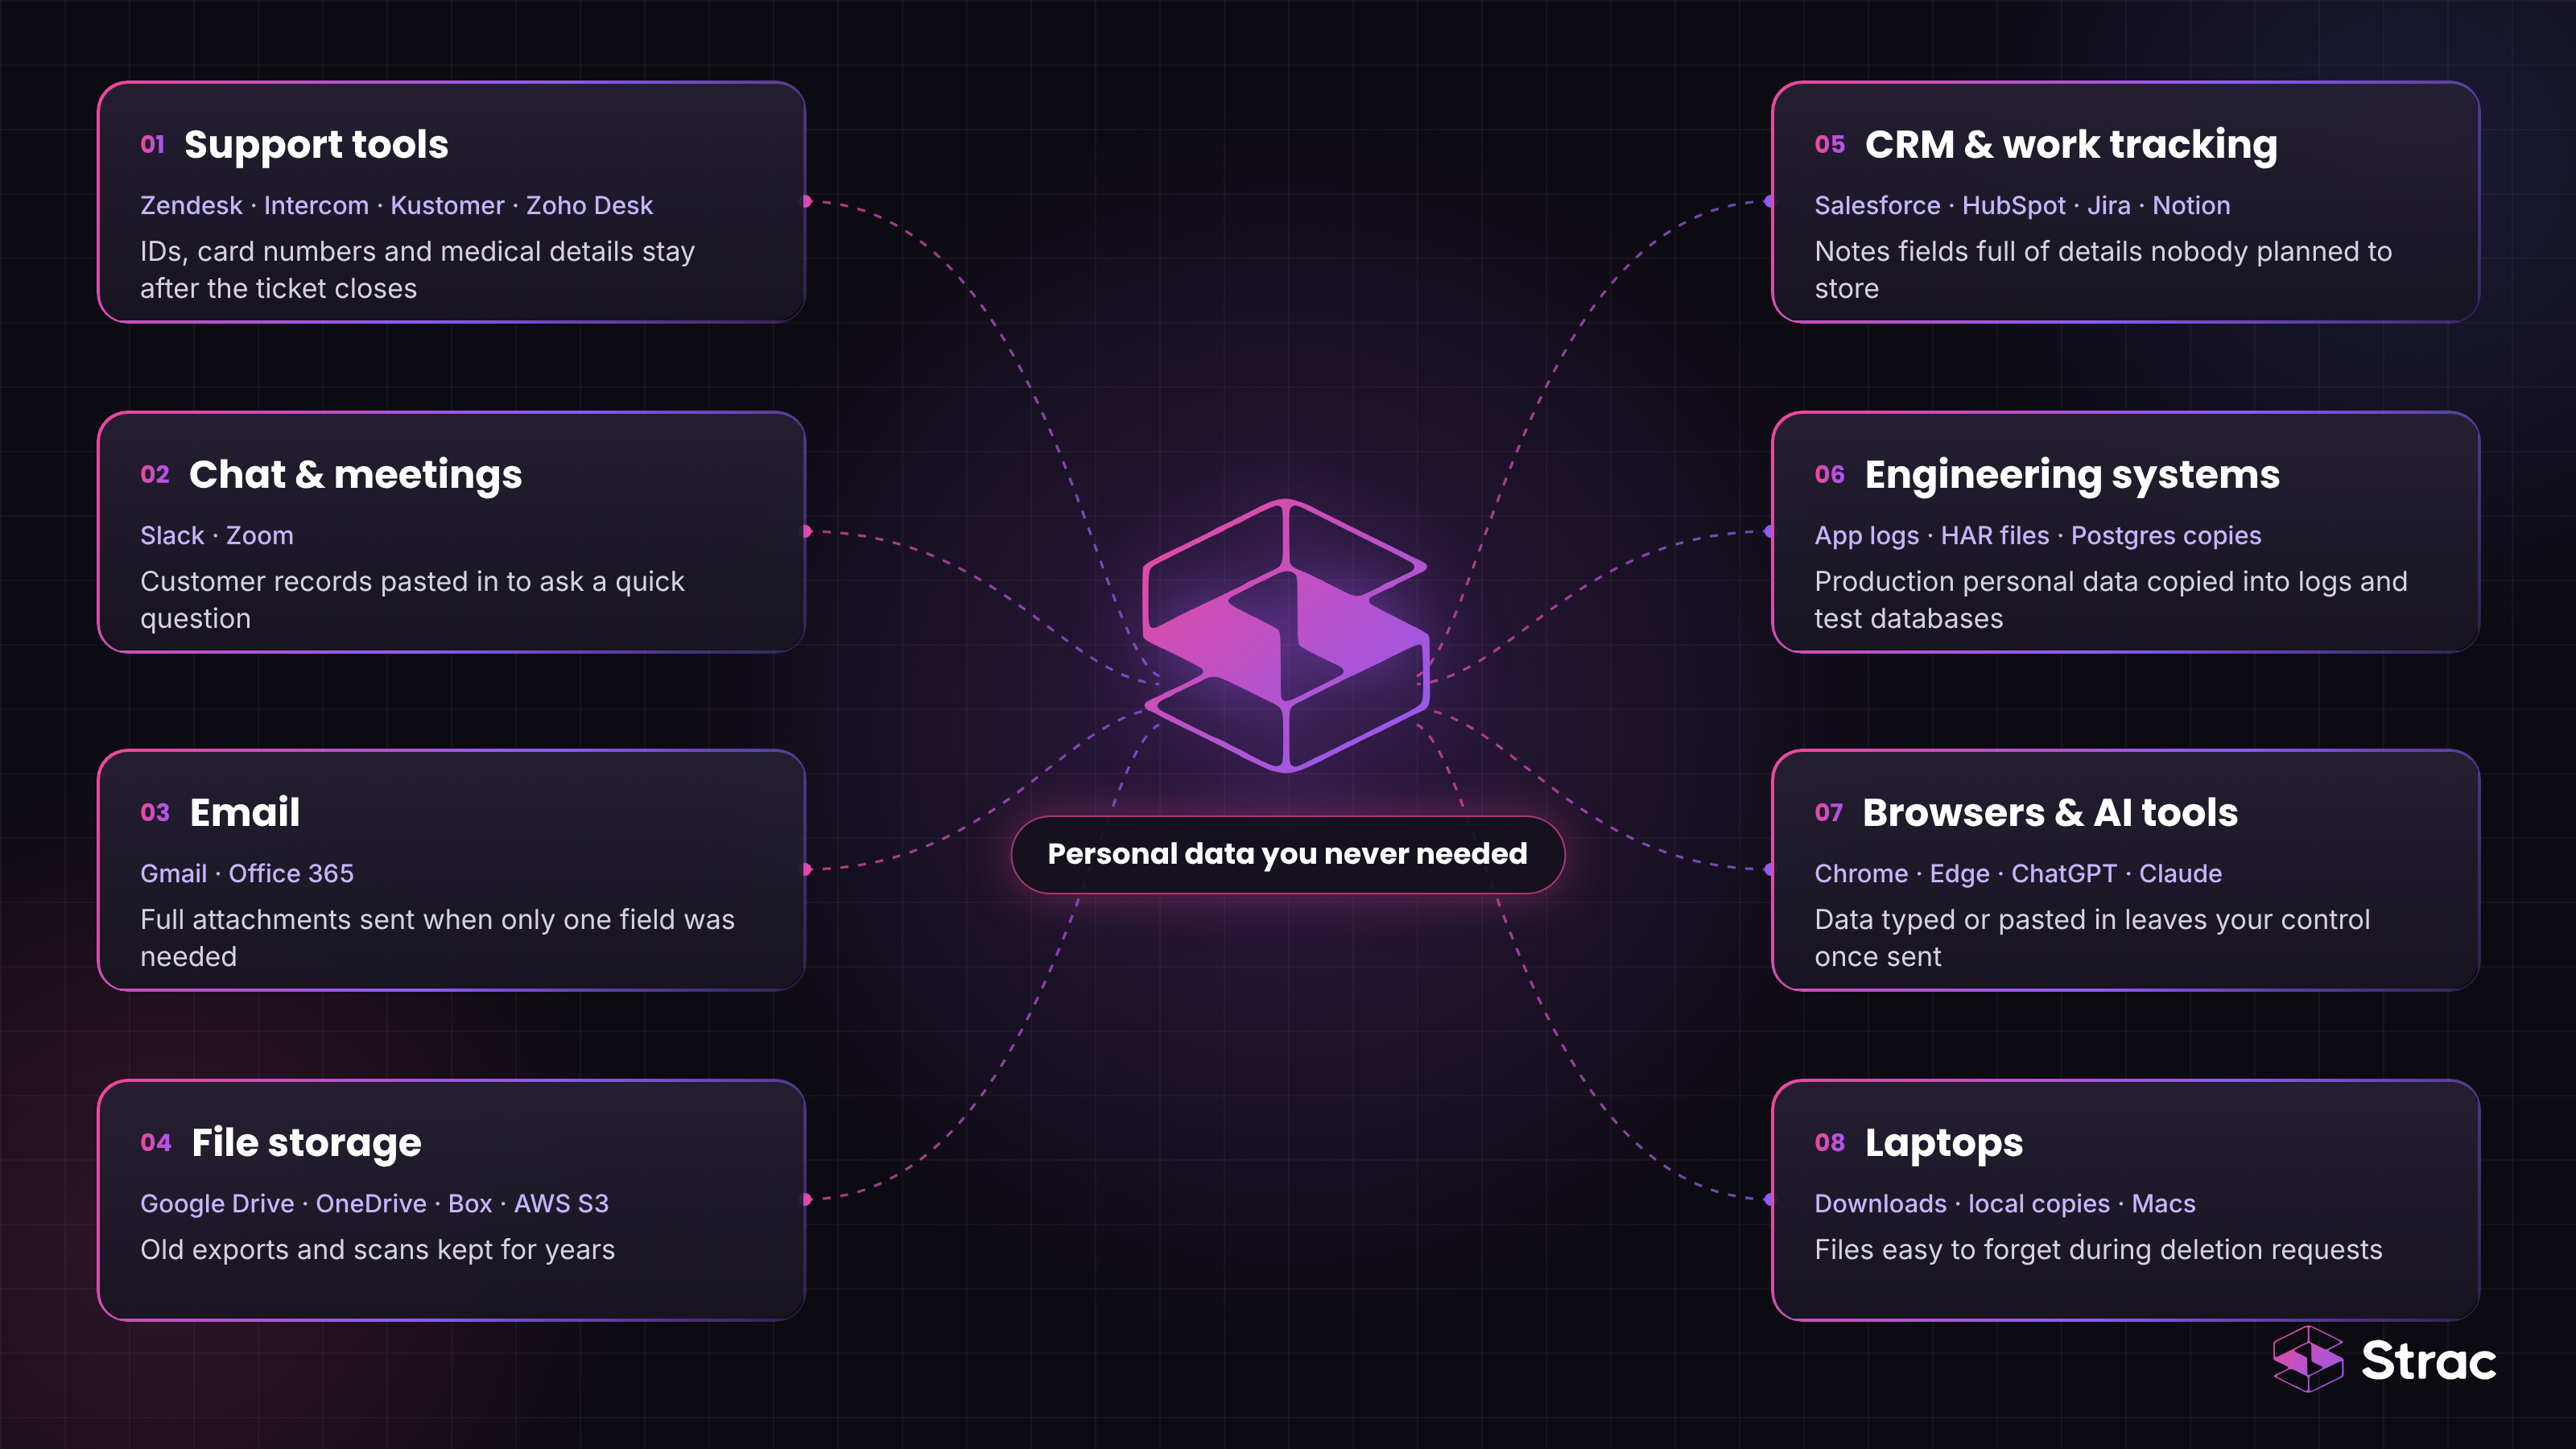
Personal data spreads because people share it to get work done. These are the places it piles up most often:
None of this shows up in a data map built from interviews. You have to scan the systems themselves.
Strac finds personal data where it actually lives and removes what you do not need.
Discovery and classification. Strac's DSPM scans SaaS apps, cloud storage and endpoints for personal and sensitive data, including GDPR special category data. It reads text inside PDFs, images, Word files and spreadsheets using OCR.
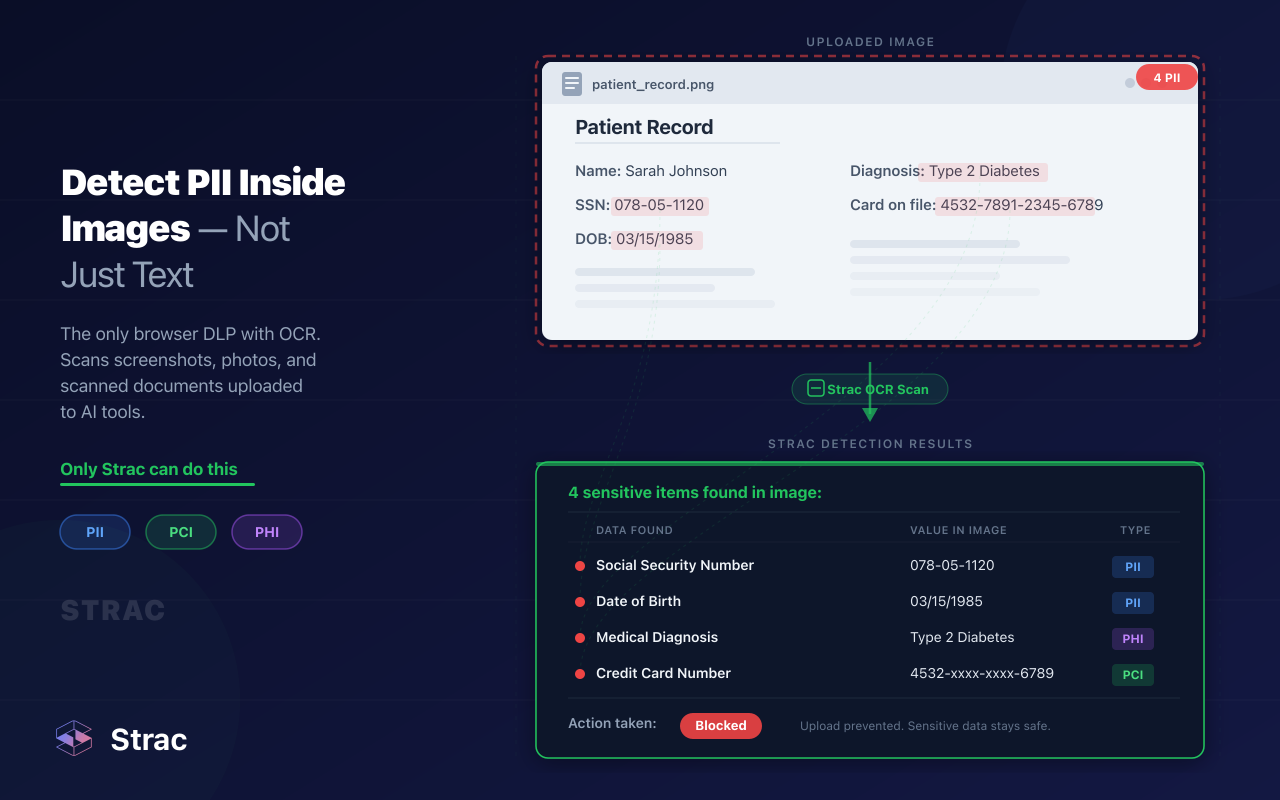
Redaction and deletion. Strac can redact sensitive values inline in tickets, messages and emails, or delete attachments once their purpose is done. This is how retention rules move from a policy document into practice. See how it works in our DLP remediation guide.
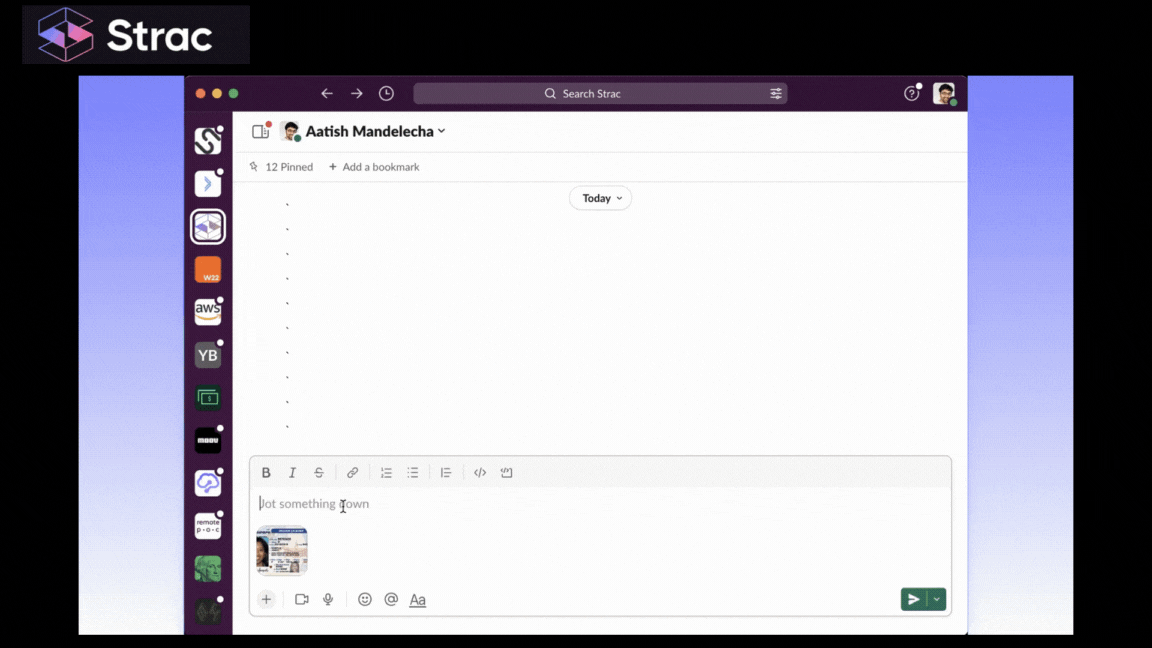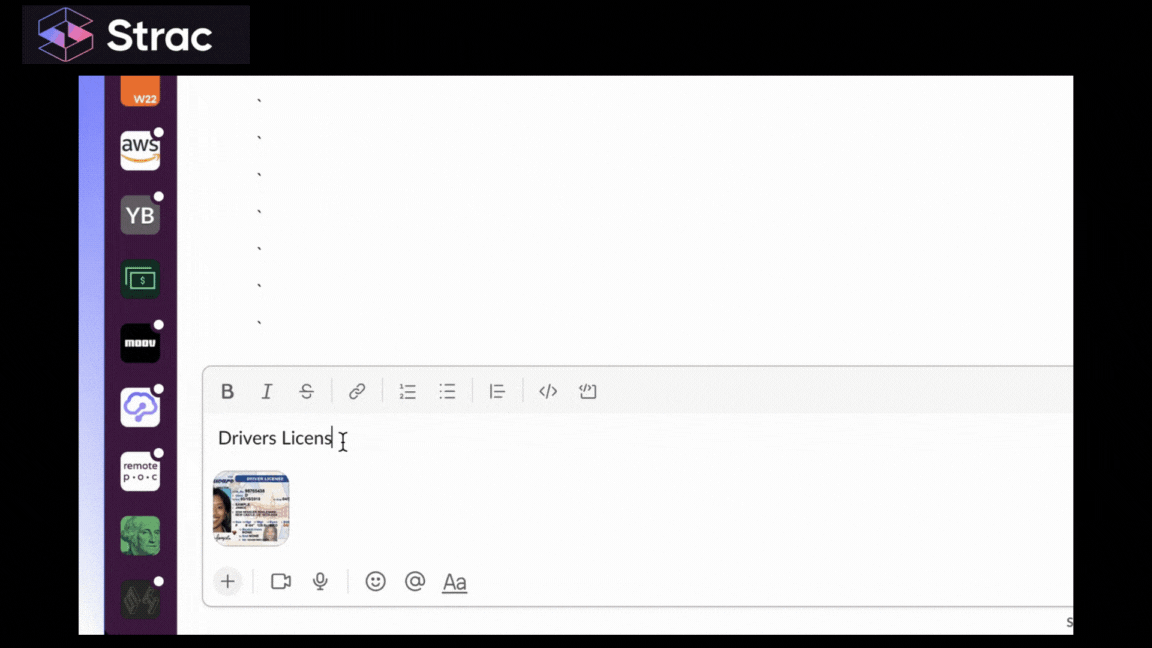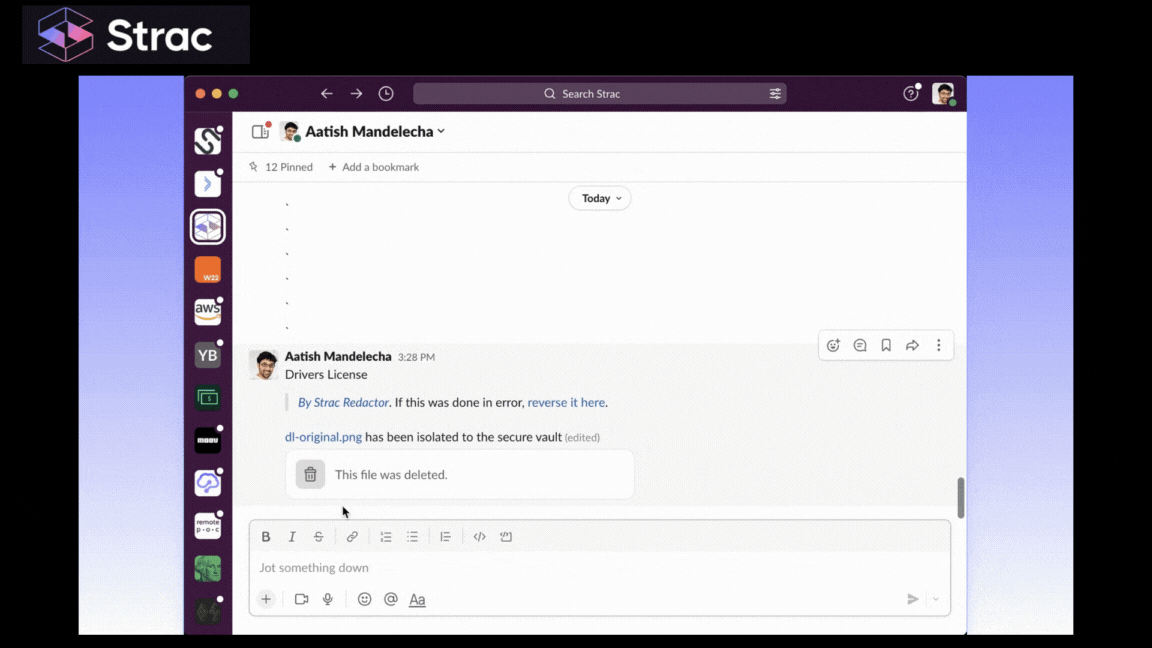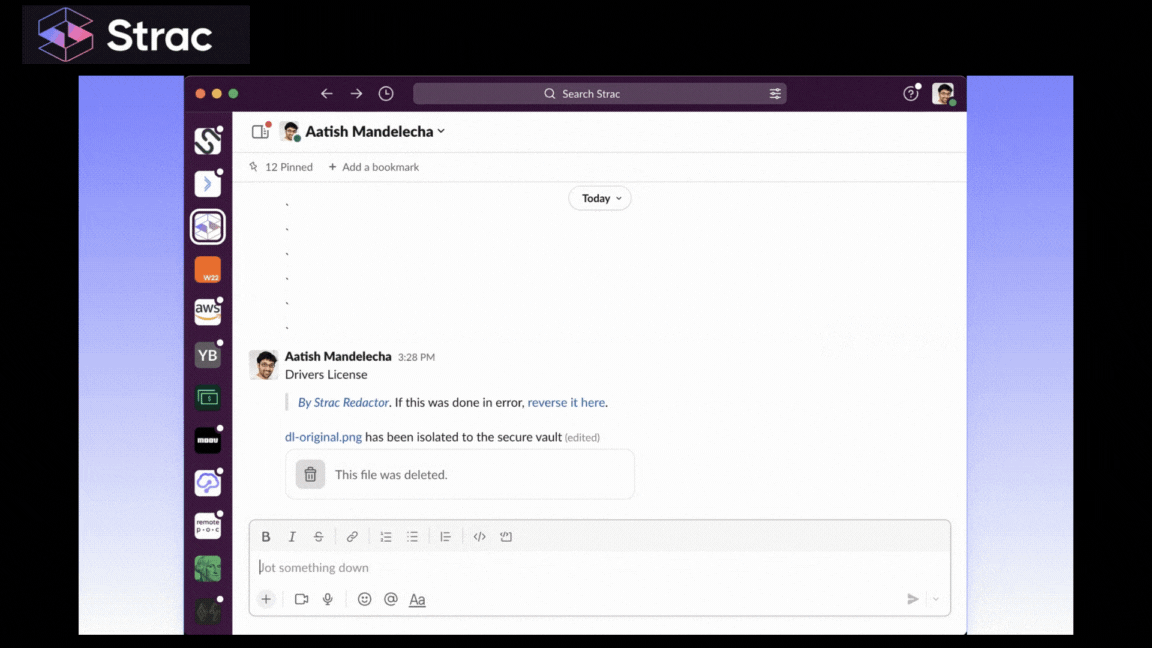
Real-time prevention. SaaS DLP, browser DLP, email protection and endpoint DLP stop sensitive data from being shared where it should not go, including ChatGPT, Claude and MCP connections.

No-code integrations. Strac connects to Slack, Gmail, Office 365, Zendesk, Intercom, Salesforce, HubSpot, Google Drive, OneDrive, Box, Jira, Notion, AWS S3 and many more.
Tokenization. Strac's tokenization lets your systems use a stand-in value instead of storing the raw sensitive data on your own servers. Less stored data means less to protect and less to disclose.
Audit-ready reporting. Every finding and remediation is logged, which gives you evidence for CCPA risk assessments and GDPR accountability.
Book a demo to see what personal data is sitting in your SaaS and cloud apps today.
Data minimization is no longer a principle you can cover with a privacy policy. California regulators are fining companies for holding data they did not need, and the GDPR has required it since 2018. The Digital Omnibus may change parts of the GDPR, but minimization still applies today.
The gap for most companies is not the database. It is the personal data spread across support tickets, chat, email, shared drives and AI tools. Find it, tie it to a purpose, remove what you do not need, and keep a record that you did.
Strac does this across your SaaS, cloud and endpoint systems.
Yes. Since the CPRA amendments, section 1798.100(c) requires that collecting, using, keeping and sharing personal information be reasonably necessary and proportionate to the disclosed purpose.
Article 5(1)(c). It says personal data must be adequate, relevant and limited to what is necessary. Article 25 adds that systems should do this by default.
No. Consent is one possible legal basis under the GDPR. It does not lift the minimization limit under either law.
The Digital Omnibus is still a proposal and has not changed the GDPR. Article 5 applies as written today.
Up to $2,663 per violation, or $7,988 for intentional violations and those involving minors under 16. These amounts apply from January 1, 2025 and are next adjusted in 2027.
Scan them for personal data, redact or delete what is no longer needed, and block new sensitive data from being shared. Strac does this for Slack, Zendesk and other SaaS apps.
Read our complete guide to data minimization, our GDPR data minimization guide, our CPRA data minimization guide and our data loss prevention guide.
“Don’t just alert on problems, fix them.”
Scott Roberts, Chief Information Security Officer, UiPath









Customers include






