October 11, 2026

6
min read
Why do you need a Endpoint DLP for MacOS Security?
macOS protects the Mac, not the data on it. See why Macs need DLP and how Strac stops data leaking via AirDrop, USB, browsers, and AI tools.
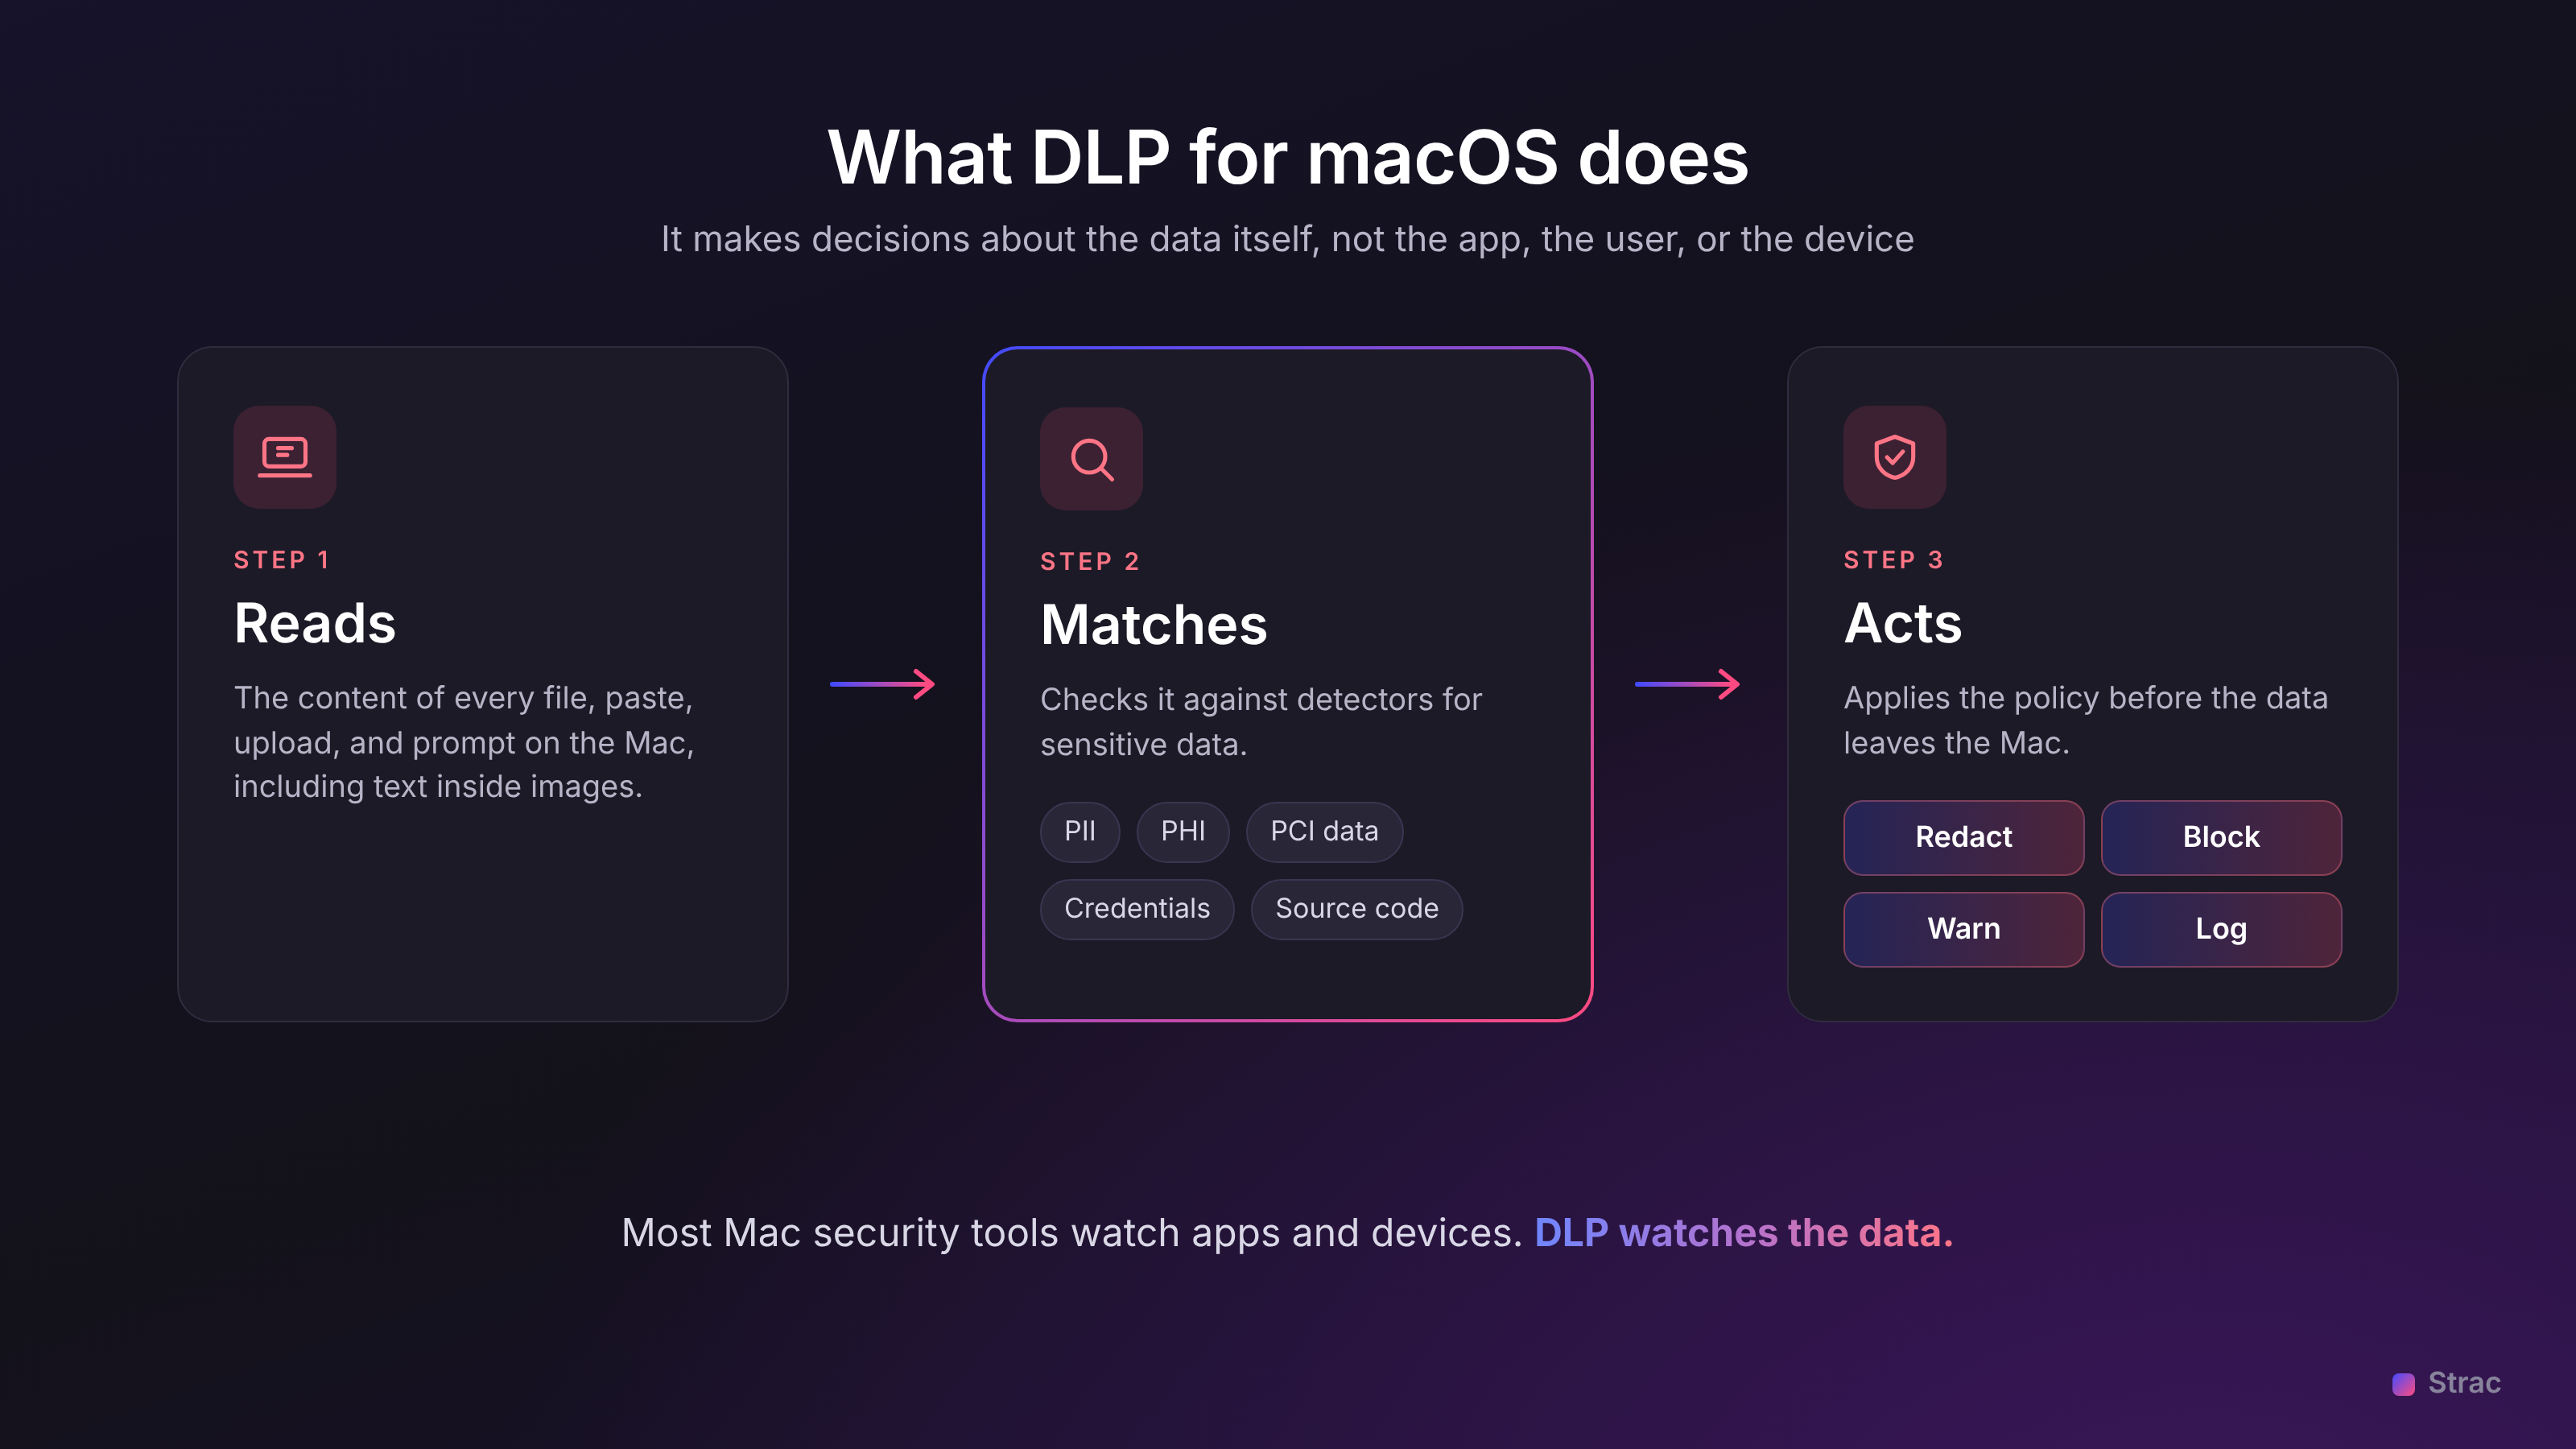
DLP for macOS is software on the Mac that finds sensitive data, watches where it goes, and acts when it heads somewhere it should not. It reads the content of a file or a paste, matches it against detectors for PII, PHI, PCI data, credentials, and source code, and then redacts, blocks, warns, or logs based on policy.
The key word is content. Most Mac security tools make decisions about apps, users, and devices. A DLP agent makes decisions about the data itself, which is the only thing a regulator, an auditor, or a customer actually cares about after an incident.
Strac's Mac data loss prevention runs as a lightweight agent on the device, so it sees the actions that never touch a corporate network or a SaaS API.
Macs have a strong security reputation, and much of it is earned. The problem is that the reputation answers a different question. It answers "will this laptop get infected?" when the question that matters for compliance is "can this laptop leak a customer list?"
Three things changed that make the second question urgent.
Macs are no longer the design team's machine. Engineering, finance, sales, and support run on them, so the data on a typical Mac now includes customer exports, contracts, payroll files, and production secrets.
Work moved to the endpoint. Remote and hybrid teams download, edit, and share files locally, often on home networks, which puts the device itself at the center of data exfiltration risk.
AI moved into every window. A Mac user can paste a spreadsheet into ChatGPT, Claude, Gemini, or Copilot in seconds, and many teams now run local AI agents that read files and call tools on their own. Malware is still a risk. A well-meaning employee with a chat window is the more common one.
Apple ships real controls, and they are worth configuring before anything else is added.
Gatekeeper and XProtect check that apps are signed and scan for known malware. System Integrity Protection keeps the operating system files from being changed. FileVault encrypts the disk, so a stolen MacBook does not hand over its contents. Privacy permissions make apps ask before reading the camera, the screen, or protected folders. MDM profiles pushed through Jamf, Kandji, or Intune can switch AirDrop off, make external drives read-only, or restrict iCloud.
Every one of those controls is about the device or the app. Not one of them looks inside a file.
That gap shows up in ordinary work. An analyst AirDrops a quarterly export to a personal iPhone. A support lead copies a page of ticket data, card numbers included, into a free summarizer. An engineer drags a folder with a .env file into a personal Dropbox. A recruiter prints a stack of offer letters with Social Security numbers to a home printer. FileVault, Gatekeeper, and XProtect all stay quiet, because nothing about those actions looks like an attack.
MDM can help, but only bluntly. Turning AirDrop off for everyone stops the leak and also stops the designer sending a mockup across the room. Making USB read-only breaks the video team. Restrictions decide which doors exist. DLP decides what is allowed to walk through them.
A useful DLP review starts by listing the exits. On a managed Mac in 2026, these are the ones that matter most.
Close one of these and the data takes another. That is why a Mac program built on a single blocked channel always leaks around the edges.
The Strac agent installs through your MDM, picks up policy from the console, and starts inspecting file activity and user actions on the Mac. When a file or a paste matches a detector, Strac acts in this order:
Policies keep working when the Mac is offline, and changes from the console reach the device in about 30 seconds once it reconnects.
A Mac-only control is a Mac-shaped hole. Strac covers the device and every place the data goes next, with the same detectors and the same policy.
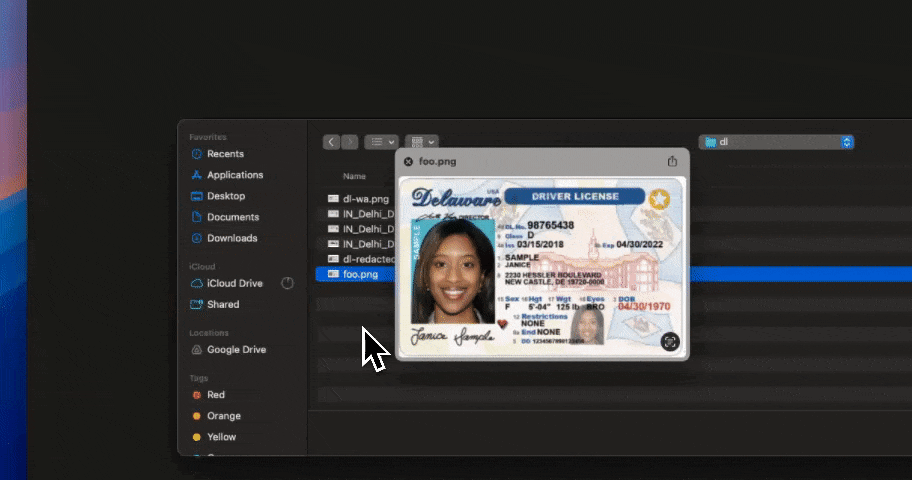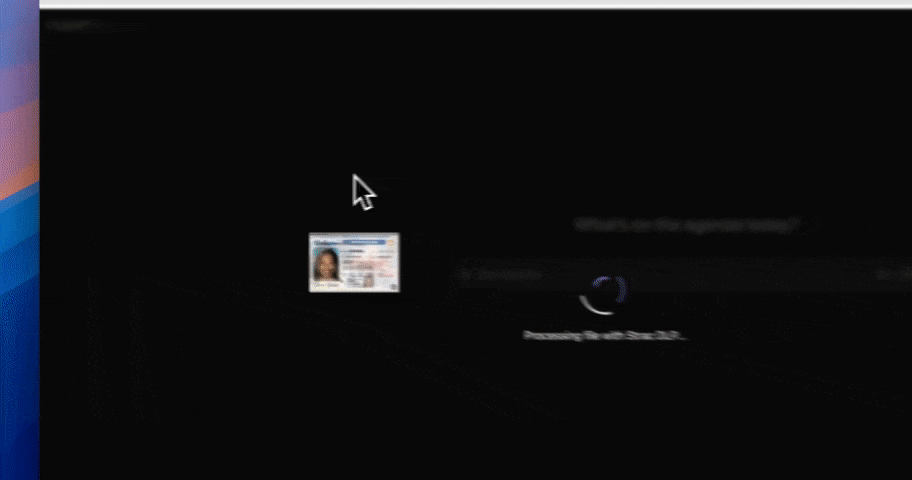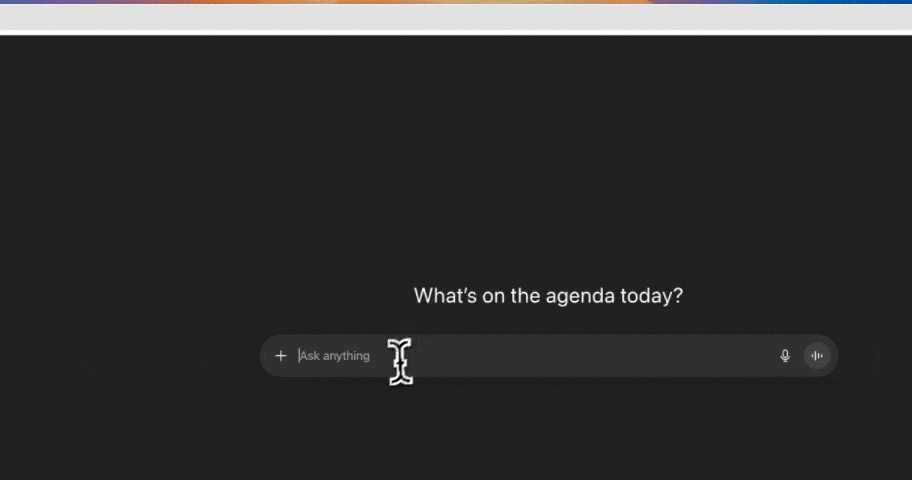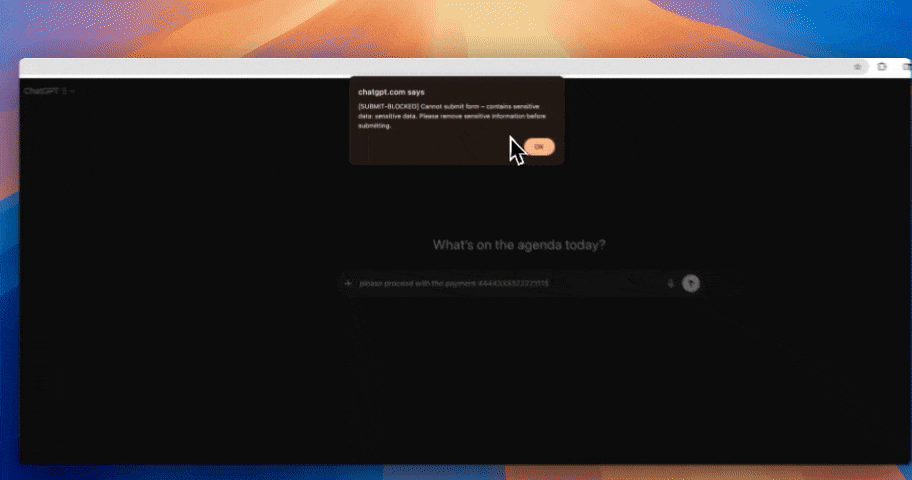
Endpoint DLP for the device. One agent for Mac, Windows, and Linux controls AirDrop, USB and external drives, clipboard, printing, screenshots, and cloud sync folders. It scans files at rest and in motion, including PDF, DOCX, XLSX, ZIP, and images through OCR with the PII scanner.
Browser DLP for uploads and forms. Extensions for Safari, Chrome, Edge, and Firefox inspect pastes, uploads, and form fields before they are sent.
AI DLP for prompts. Strac redacts sensitive data in prompts and file uploads to ChatGPT, Claude, Gemini, and Copilot. The question reaches the model. The customer record does not.
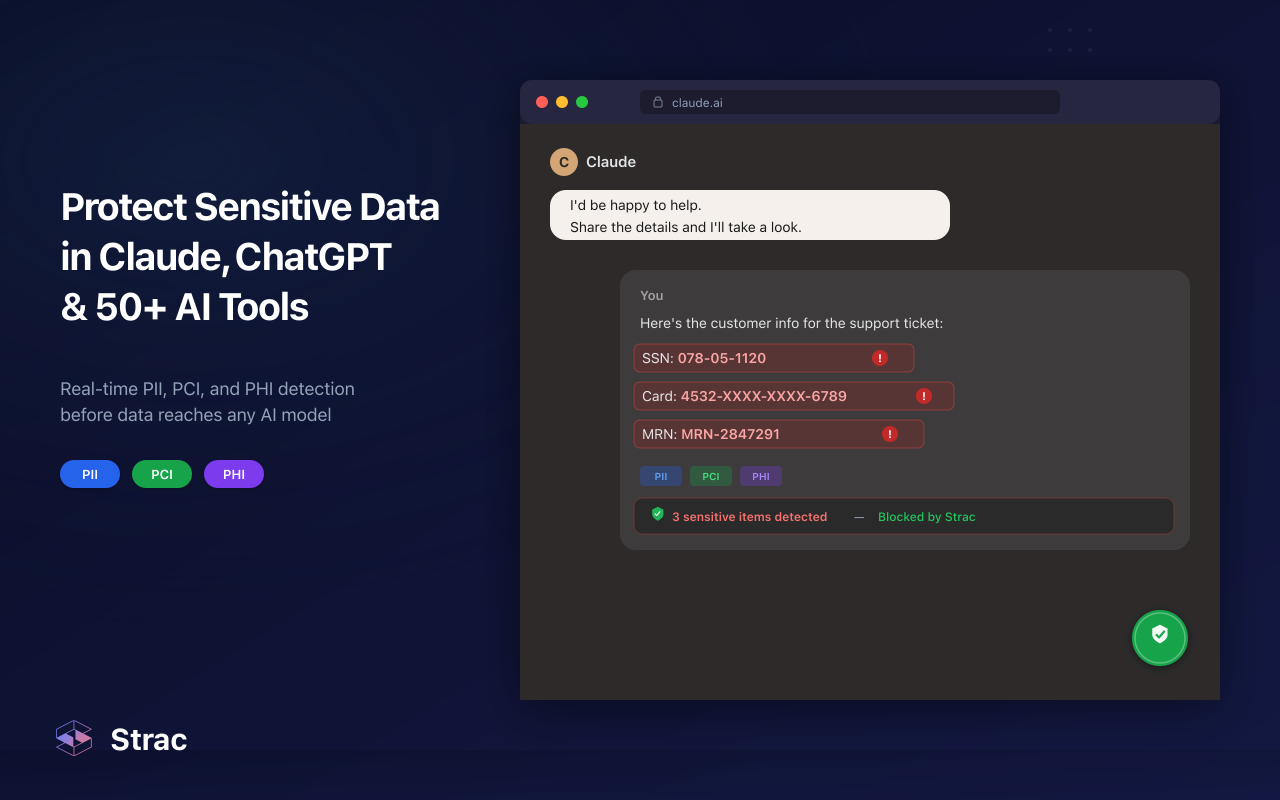
Shadow AI discovery for the tools nobody approved. The same agent shows which AI apps and sites are in use on each Mac and what data is going to them, with no keystroke logs and no screenshots of the user's screen. The method is covered in how to detect shadow AI.
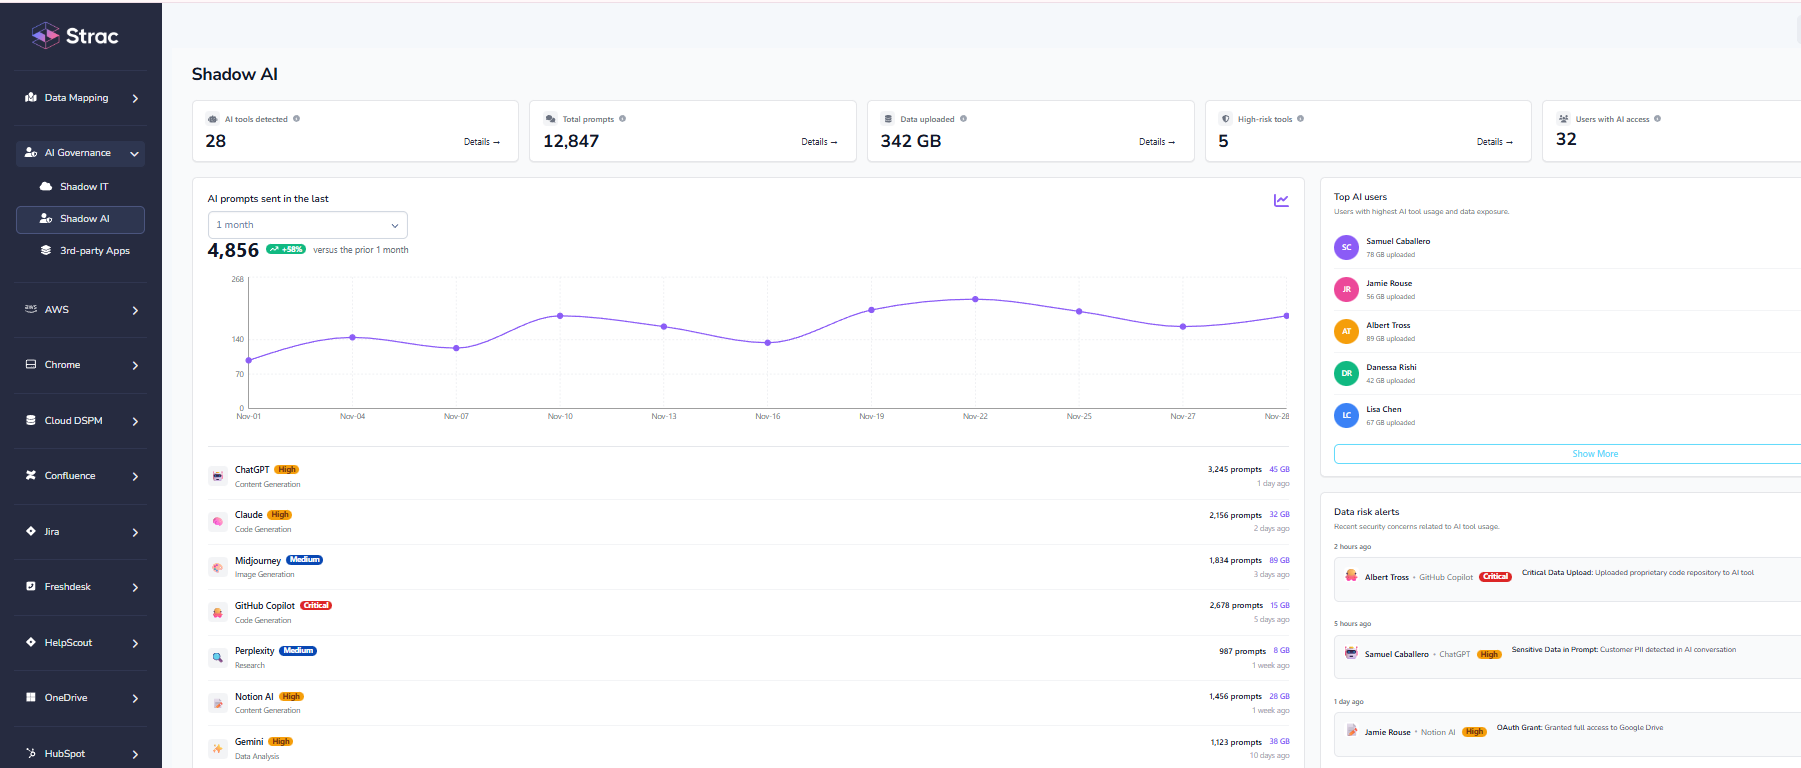
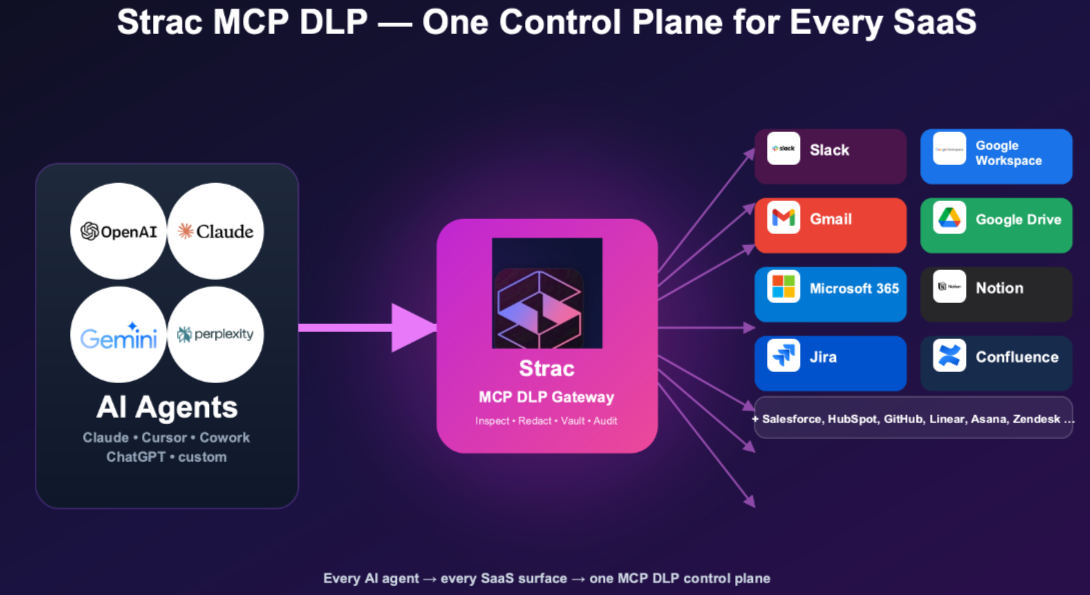
MCP DLP for local agents. Developers increasingly run AI agents on their Macs that connect to Slack, Google Drive, GitHub, and Salesforce through MCP servers. Strac inspects each tool call and response, so an agent gets masked fields instead of raw records.
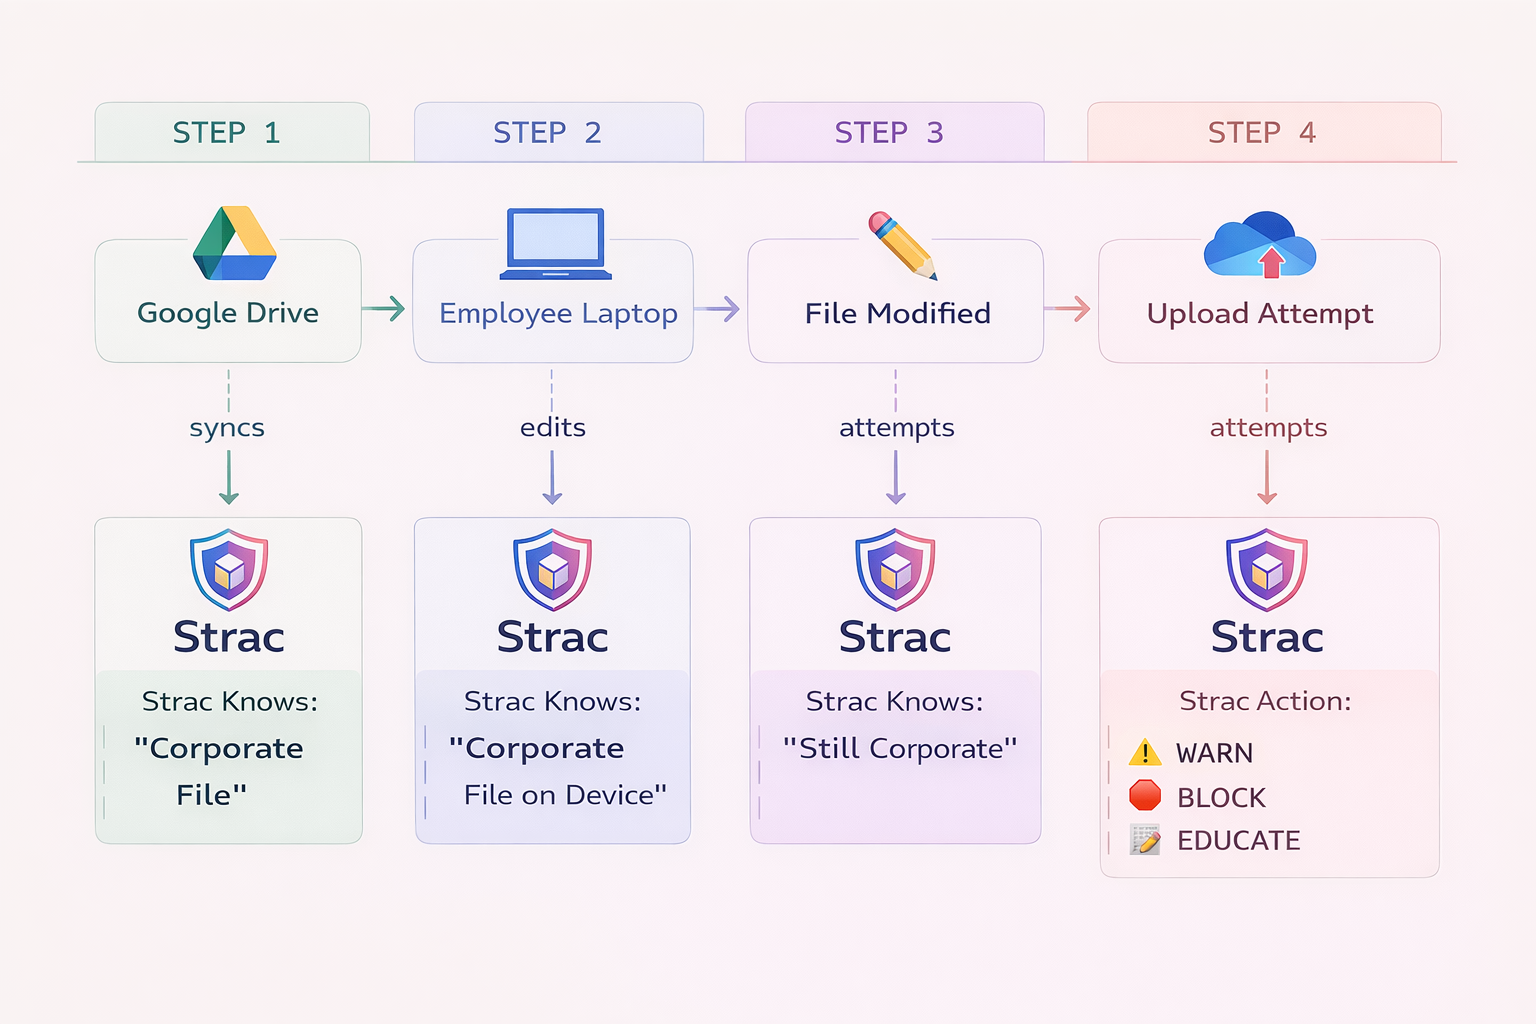
Data lineage for renamed copies. Files synced from Google Drive, OneDrive, and Box carry a lasting fingerprint, so a renamed or lightly edited copy is still recognized on its way off the Mac.
SaaS DLP and DSPM for what already left. If a file reached Slack or a shared drive before the agent was installed, Strac finds it there, redacts it in place, and removes public exposure.
Findings map to HIPAA, PCI DSS, SOC 2, ISO 27001, and GDPR, so every Mac event is also audit evidence.
Days 0 to 30, discover. Deploy the agent through Jamf, Kandji, or Intune in audit mode. Scan every Mac for sensitive files, list the channels data actually leaves through, and see which AI tools are in use.
Days 30 to 60, protect. Turn on redaction for prompts and browser uploads, block USB and AirDrop for regulated data types only, and set warn and coach on the rest. Measure false positives before tightening.
Days 60 to 90, prove and scale. Extend the same policy to Windows and Linux, connect SaaS apps, map events to your frameworks, and loosen the blanket MDM restrictions you no longer need.
Before you call the rollout done, check each of these:
Strac closes the gap behind all of it. Start with endpoint DLP, or read what an endpoint DLP agent is and endpoint agent DLP vs. agentless SaaS DLP.
Gatekeeper, FileVault, and MDM all do their jobs, and none of them was built to read a file and decide whether it may leave. The data layer is the backstop. Inspect what is in the file, redact the sensitive part on every exit from the Mac, and a careless paste or a lost AirDrop never becomes a breach. Book a demo to see Strac protect the data on your Macs.
Yes. Malware protection and DLP solve different problems. XProtect stops bad software; DLP stops good employees from sending sensitive data to the wrong place. Most Mac data leaks involve no malware at all, just AirDrop, a paste, or an upload.
No. MDM can switch channels like AirDrop or USB on or off for everyone, but it cannot read a file. It treats a payroll export and a lunch menu the same way, which forces you to choose between leaking data and blocking work.
Yes, by redacting instead of blocking. Strac strips the card number or SSN from a prompt, paste, or upload and lets the rest through, with a short note to the user. Blocking is kept for the narrow cases that should never leave.
Not fully. No software stops a camera pointed at a display. Strac reduces what is on screen to photograph by masking sensitive fields in SaaS apps and AI results, and it controls screenshots, printing, and copying on managed Macs.
It is endpoint DLP running on macOS. The detectors and policies should be identical across Mac, Windows, and Linux so one rule covers every device. See endpoint DLP and the Mac DLP guide for the full picture.