October 14, 2026

4
min read
How to protect your Intercom account?
Eliminate Security and Compliance Risks From Intercom Account
Intercom is no longer just a chat widget or "CRM." In 2026 it is a full customer service platform: Fin, its AI agent, answers customers directly, Copilot drafts replies for human agents, and an MCP server lets outside AI tools read conversations, contacts and tickets.
That makes Intercom one of the highest-risk SaaS apps for sensitive data. Every conversation is unstructured text written by customers, who don't know or care what your compliance team wants. They paste full card numbers to fix a failed payment. They upload a driver's license to verify an account. Patients describe symptoms. Developers share API keys while debugging.
All of it lands in your Intercom workspace, often stays there indefinitely unless someone deletes it, and is now readable by more people and more AI agents than ever. This guide covers how to lock down access with Intercom's built-in settings, where those settings stop, and how to protect the data itself with DLP and DSPM.
Breaches are more expensive and more often start with people and partners. According to IBM's 2026 Cost of a Data Breach Report, the global average breach now costs $4.99 million, a record and up 12% year over year; in the US it is $11.5 million, and healthcare stays the costliest industry at $6.64 million (Baker Donelson summary). Customer PII showed up in 52% of breaches (Passwork summary). Verizon's 2026 DBIR found the human element in 62% of breaches and a third party in 48% (Abnormal summary).
For Intercom specifically, the risk comes from five places:
Regulators expect you to control this data wherever it lives. PCI DSS forbids storing full card numbers where they aren't needed. HIPAA applies the moment a covered entity's patient writes into chat. GDPR and the growing list of US state privacy laws give customers the right to have their data deleted, which you can't honor if you don't know where it is.
These settings are free, quick, and the foundation for everything else. Do them first.
Stolen credentials remain a common way into SaaS apps. Intercom supports two-factor authentication, Google sign-in and SAML SSO. Enforce SAML SSO through your identity provider (Okta, Entra ID, Google Workspace) so access is removed automatically when someone leaves. If SSO isn't an option, require 2FA for every teammate, not just admins.
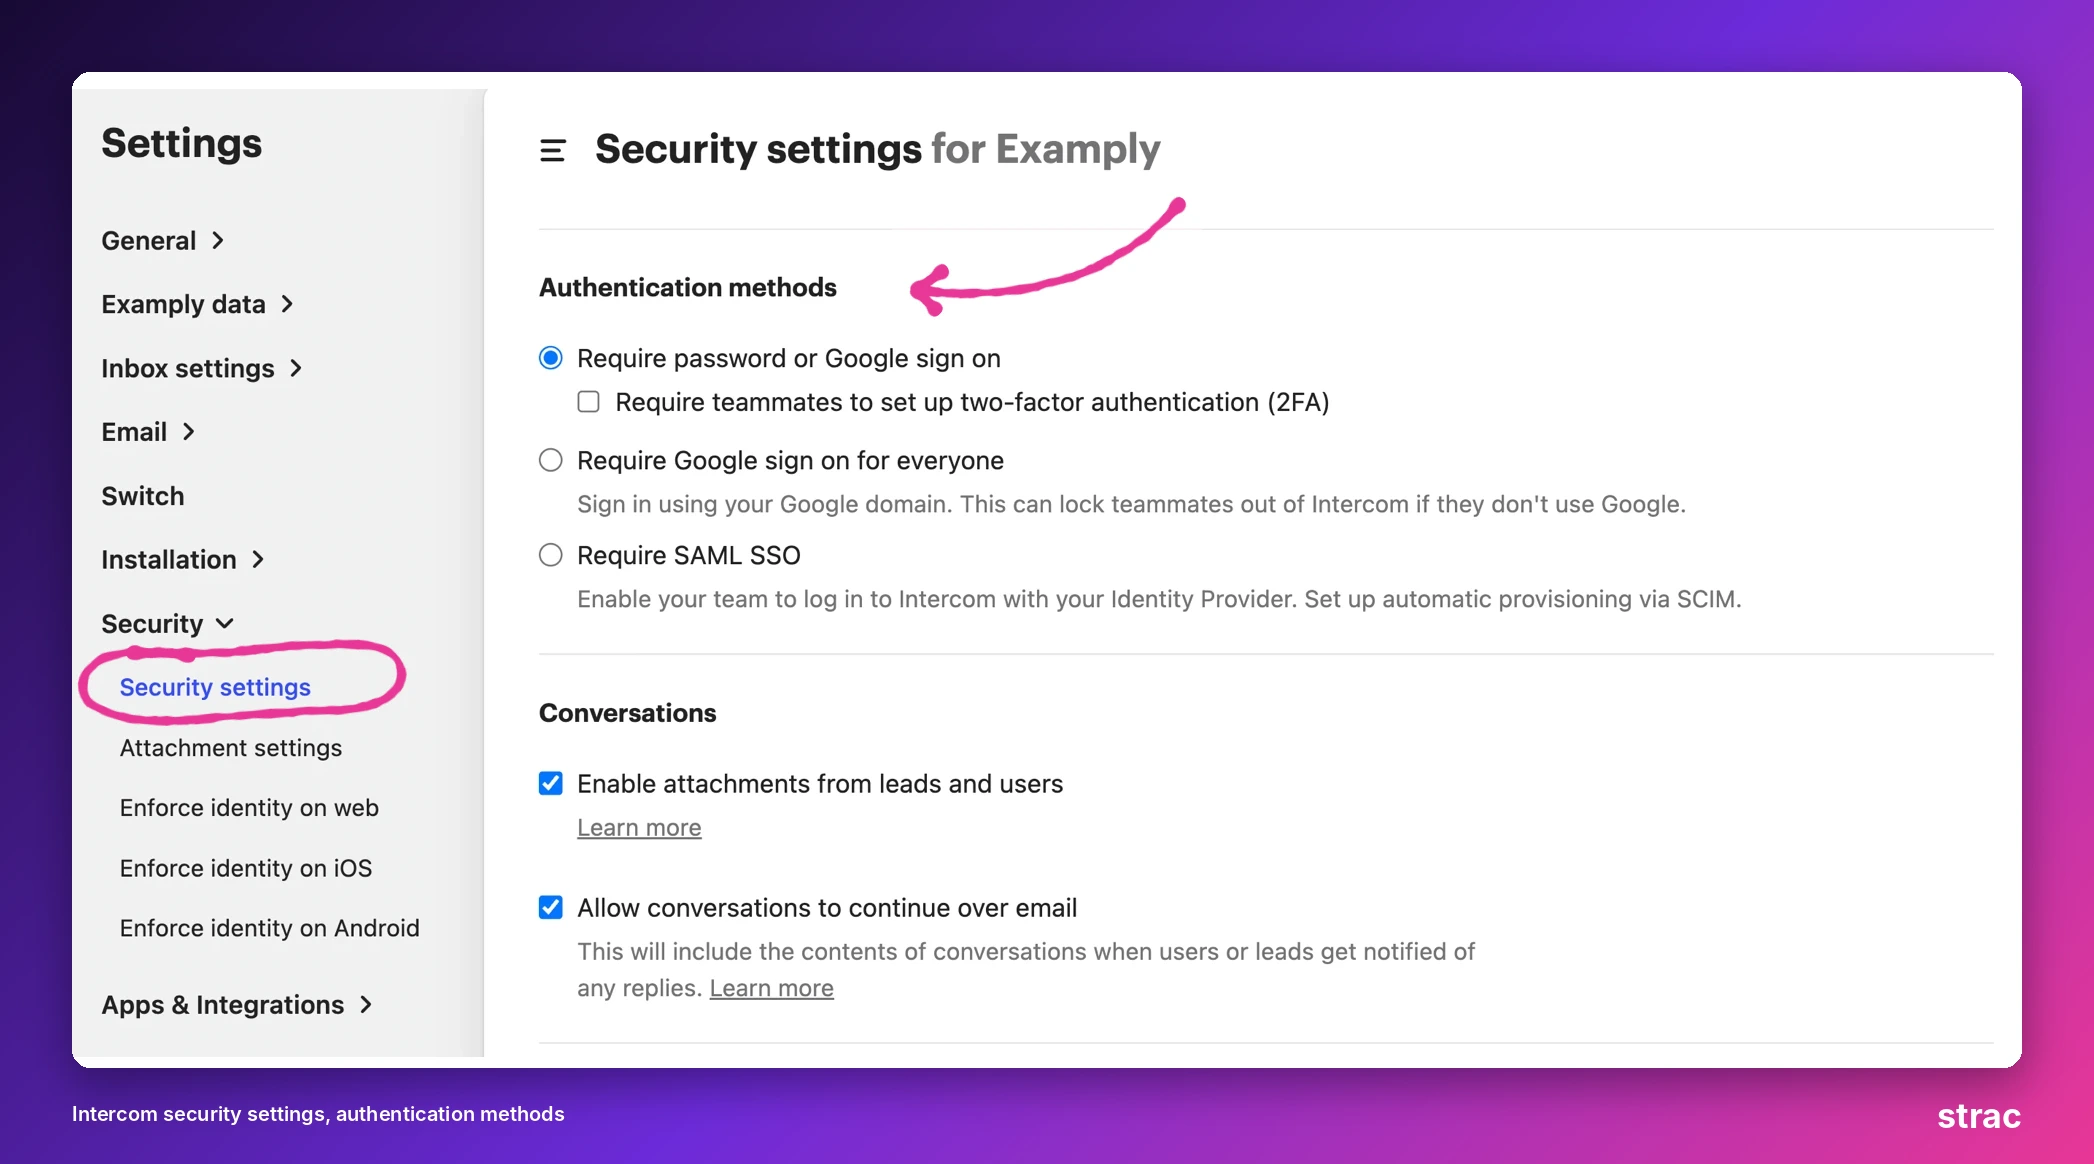
Many older Intercom security guides still tell you to turn on Identity Verification. That advice is out of date. Intercom has deprecated Identity Verification, the HMAC "user hash" method, and now recommends Messenger security with JSON Web Tokens.
Your server signs a JWT with the user's user_id and your Messenger API secret, and Intercom checks it on every request. This stops one logged-in user from impersonating another and reading their conversations. Set it up under Messenger security settings, enforce it on web, iOS and Android, and rotate the secret under Workspace > Security > Messenger (Intercom developer docs). Already on HMAC? Follow Intercom's migration guide.
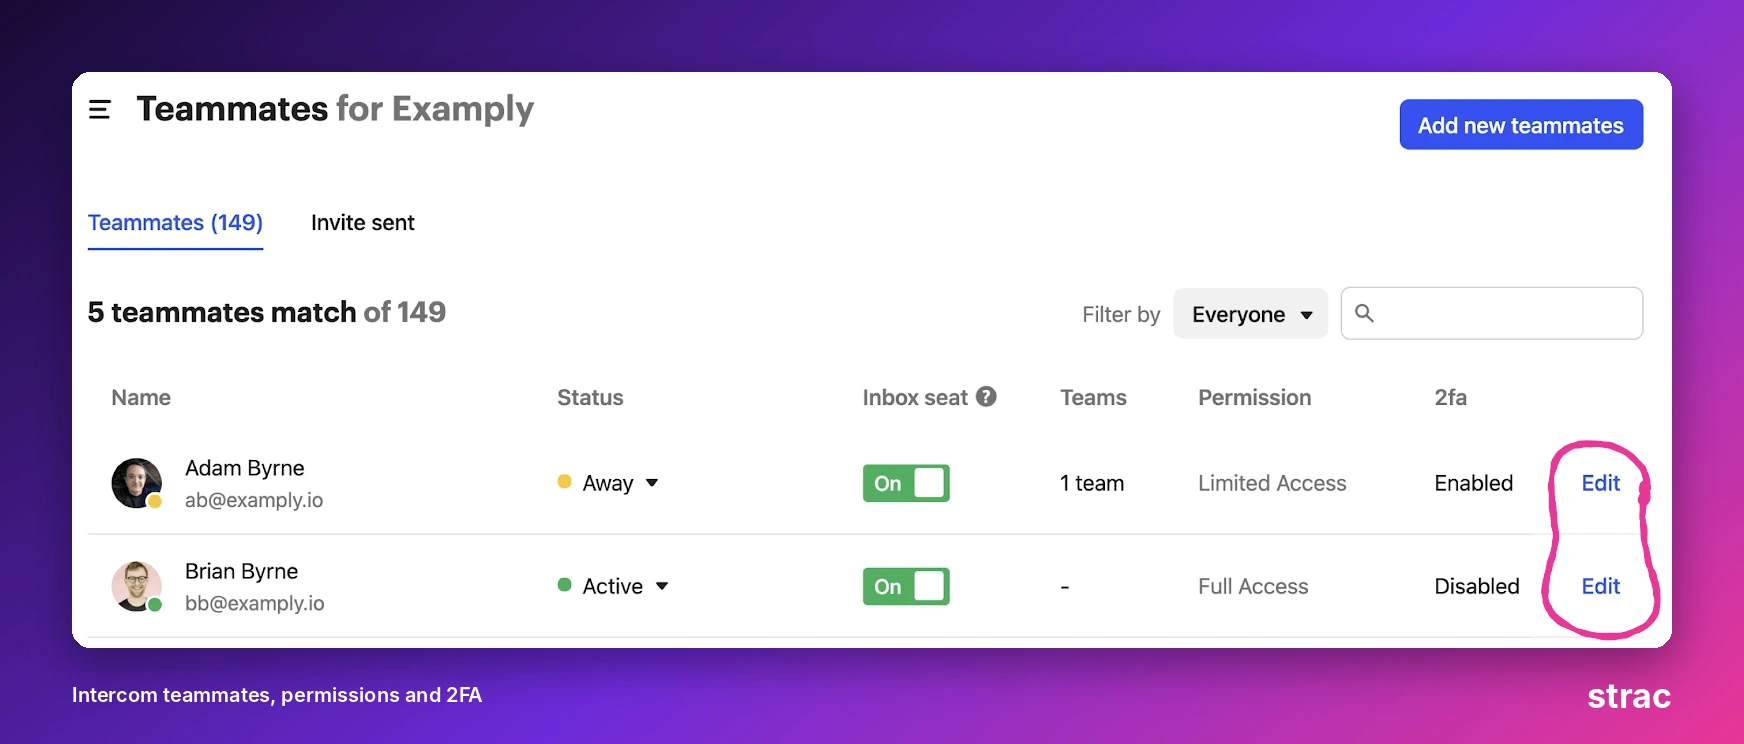
Give each teammate the smallest role that lets them do their job. Use custom roles to restrict exports, app installs, billing and workspace settings to a few admins. Then limit which conversations each team can see, so a billing contractor can't browse VIP or healthcare inboxes.
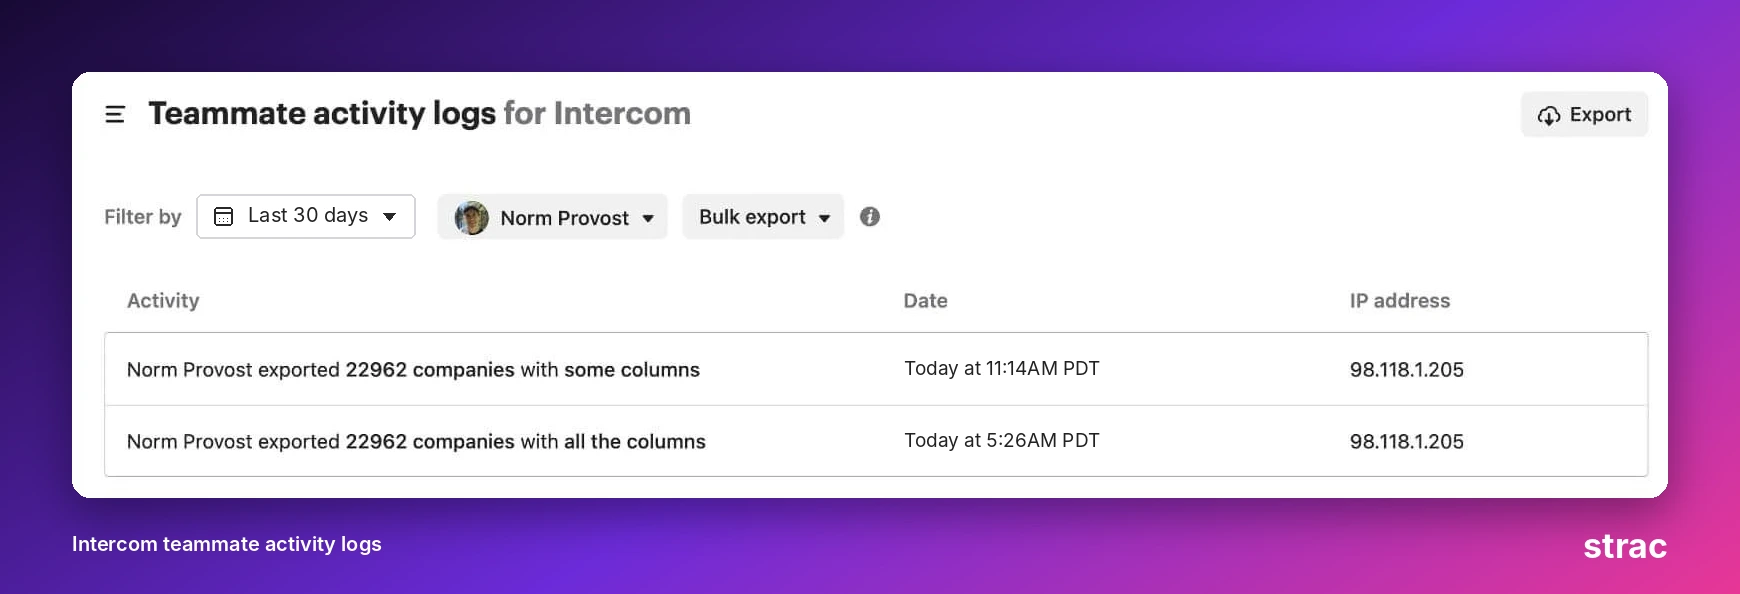
Teammate activity logs show logins, invites, permission changes, setting changes and data exports. Review them at least monthly, and alert on bulk exports, new admin invites and logins from unusual locations.
Every App Store app, webhook, OAuth app and access token is another path out of Intercom. Remove what nobody uses, and check that the rest only have the scopes they need. Review which content sources Fin can draw on, and inventory which external AI tools connect over the Intercom MCP server.
Teammates can manually redact individual messages that contain sensitive data, and you can delete user data to meet GDPR and CCPA requests. This works for one-off cases. It does not scale to thousands of conversations a day, which is where the next section comes in.
Native controls answer who can open a conversation. They don't answer what is inside it. That leaves five gaps:
Closing these gaps takes data-level controls: DLP that inspects and redacts content in real time, and DSPM that finds and remediates what is already stored.
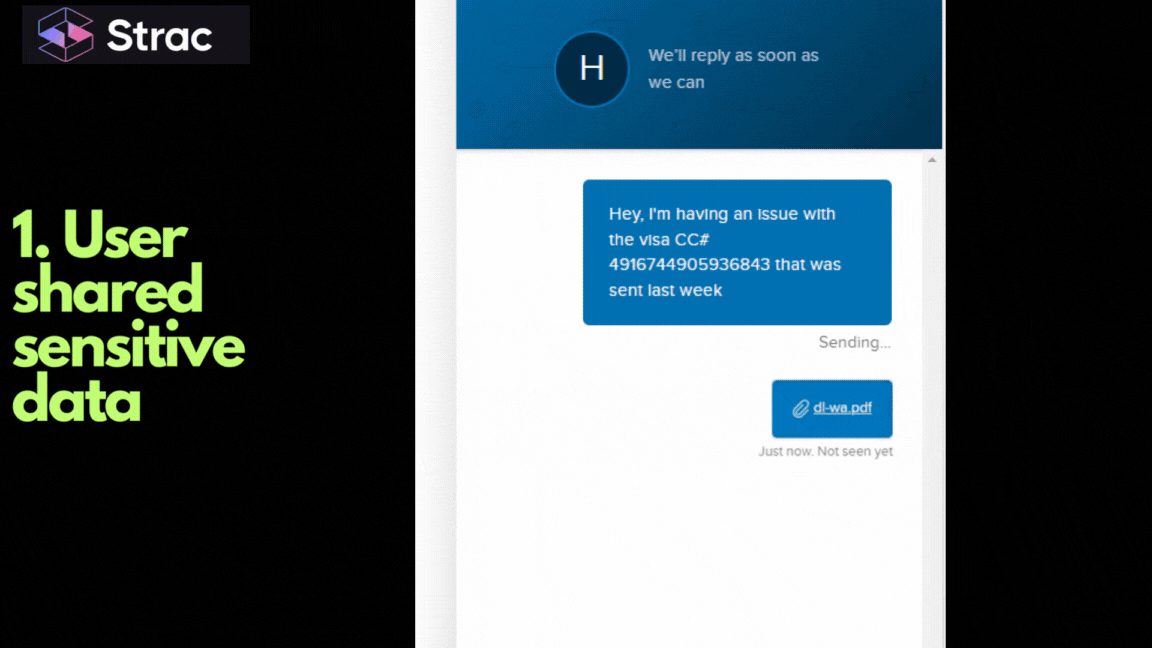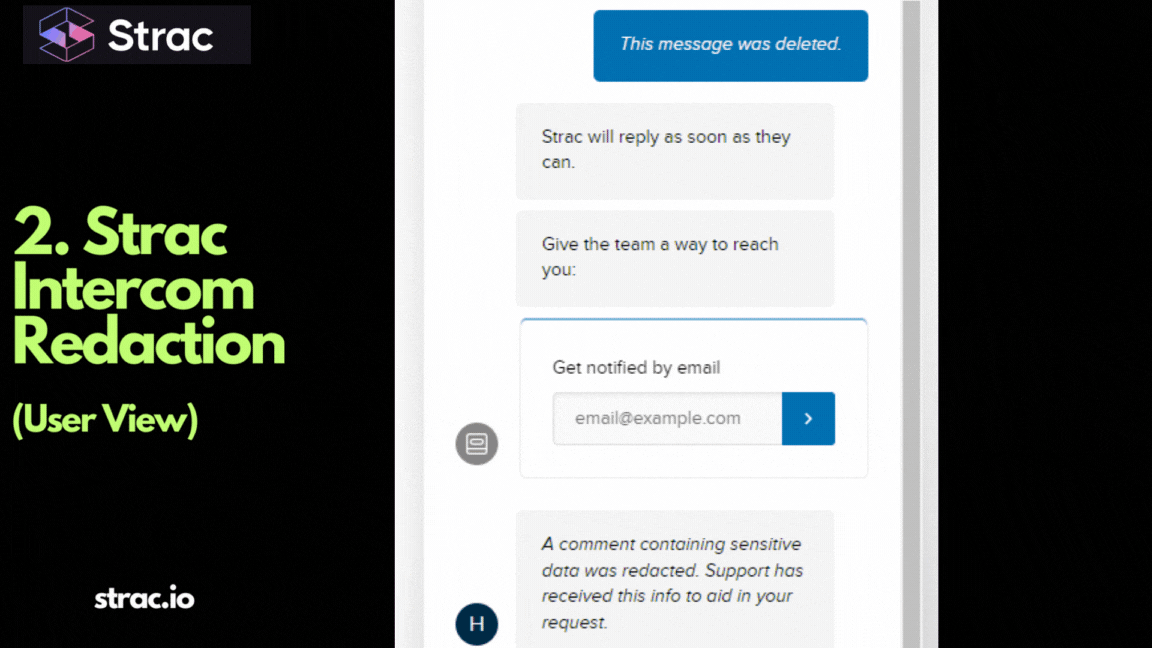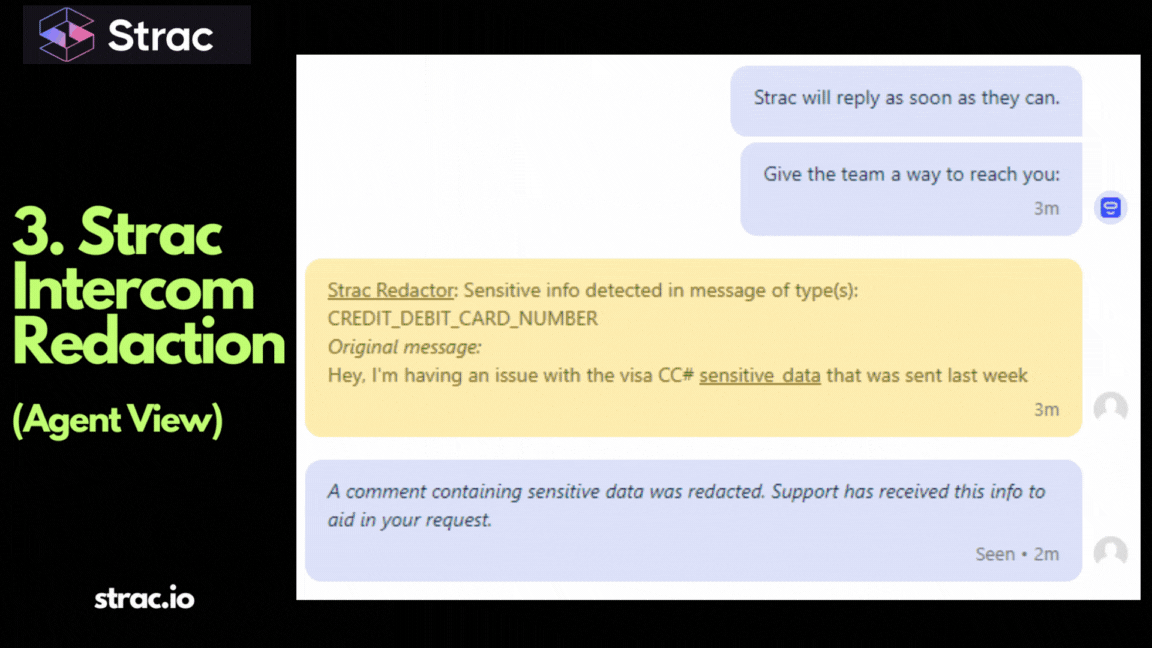
Strac Intercom DLP protects the data itself, at three layers: as it enters Intercom, as it sits in Intercom, and as AI agents read it. It's published on Intercom's App Store, needs no software installed, and connects in under 10 minutes.
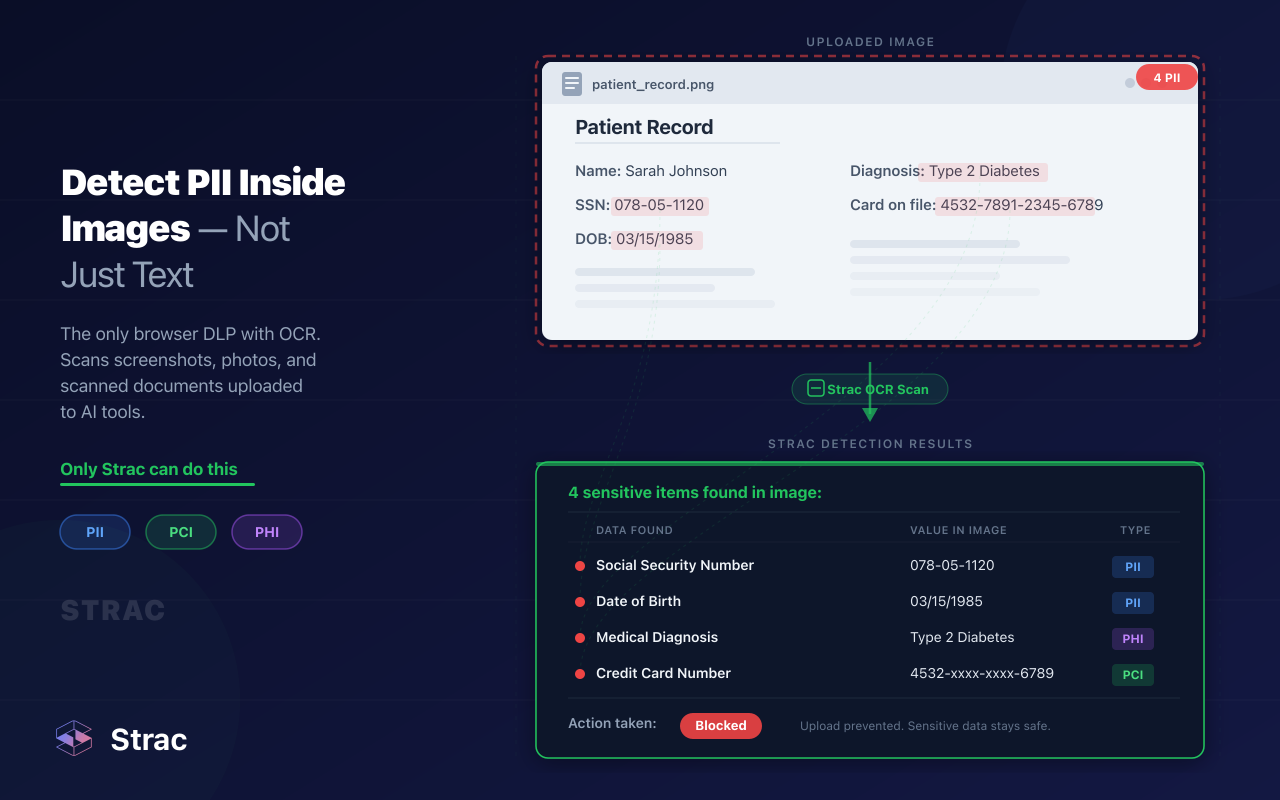
Strac inspects every message and attachment as it arrives, using its catalog of sensitive data elements: SSNs, driver's licenses, passports, card numbers, bank accounts, dates of birth, PHI, API keys and custom data types you define. OCR reads the text inside screenshots, ID photos and image-based PDFs.
You choose the mode per policy:
A customer who pastes a card number to fix a payment gets help; the card number never sits in your inbox. That is the core control for PCI DSS PAN masking.
Real-time DLP stops new exposure. Strac DSPM scans existing conversations and attachments, classifies what it finds, and lets you redact or delete in bulk. You get a clear picture of how much PII, PCI and PHI sits in Intercom today, and a practical way to honor deletion requests.
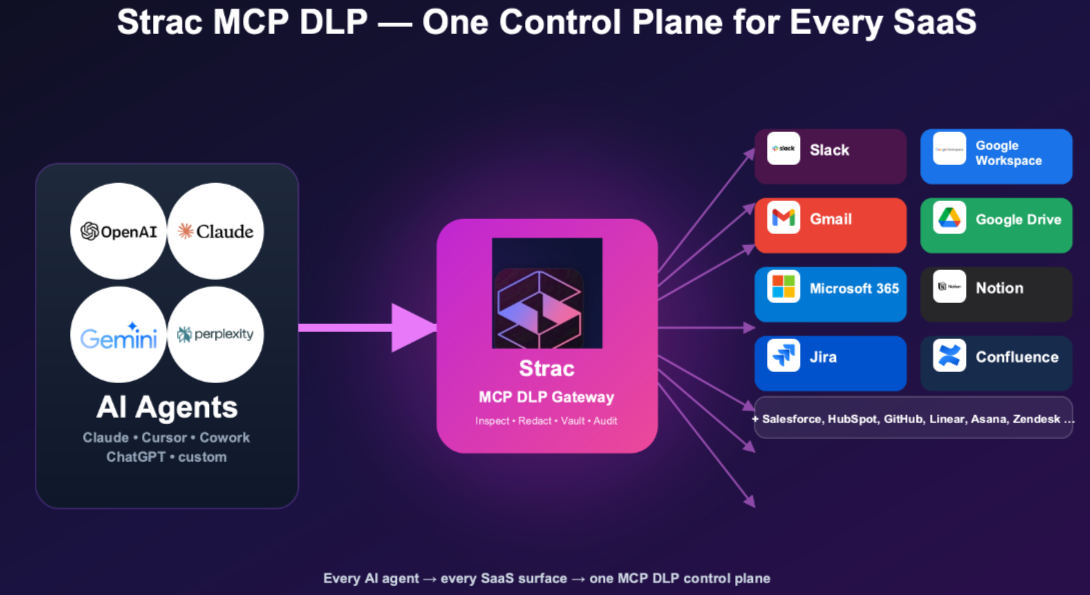
When Claude, ChatGPT, Cursor or a custom agent reads Intercom through the MCP server, Strac sits between the AI tool and Intercom. It checks every request and redacts, masks or blocks sensitive data before the AI tool sees it. Risky actions, like reading many conversations at once or sending a message, can require approval. Every request is logged with who made it, which AI tool, what data was found and what Strac did. The Intercom MCP Server guide covers the setup in detail.
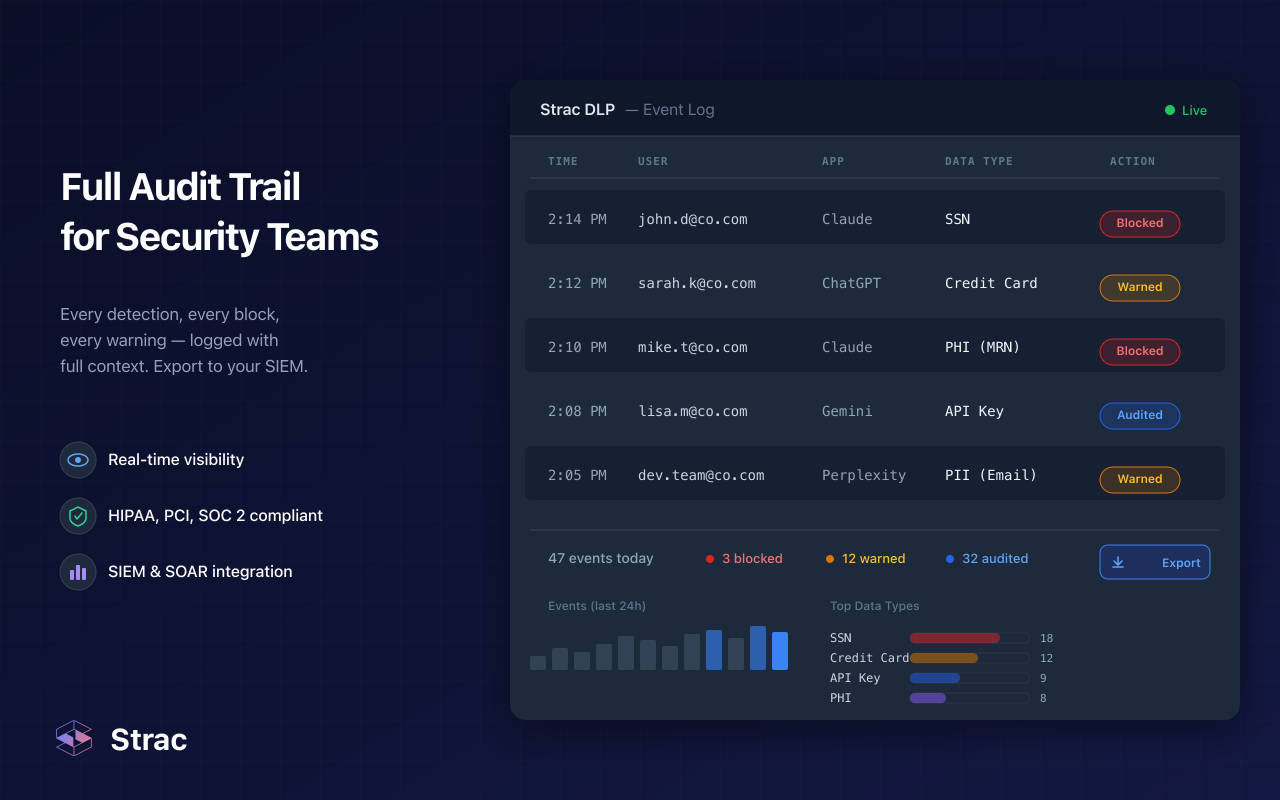
Every finding, redaction and vault access is logged and can stream to your SIEM (Splunk, Microsoft Sentinel, Datadog). The same evidence supports PCI DSS, HIPAA, SOC 2, ISO 27001, GDPR and CCPA audits.
Support data rarely stays in one app. The same Strac policies cover Zendesk, Slack, Gmail, Google Drive, Salesforce, HubSpot, ChatGPT and endpoints, so a card number blocked in Intercom is also caught when someone copies it into Slack or an AI chat.
Access
Monitoring
Data protection
Lock down access with Intercom's built-in settings, then protect the data itself. Intercom holds some of the most sensitive data your customers ever share, and in 2026 more people and more AI tools can read it than ever. Strac gives you real-time redaction, cleanup of old conversations and control over AI tools for Intercom, in one platform with nothing to install and setup in under 10 minutes.
Book a demo to see Strac redact a live Intercom conversation.
Intercom provides strong platform security, including SSO, 2FA, role-based access and audit logs. But security of the platform is not the same as security of your data inside it. Intercom can't stop customers from pasting card numbers or uploading ID photos; that is your responsibility under the shared responsibility model.
Identity Verification (the HMAC user hash) is deprecated. Intercom now recommends Messenger security with JSON Web Tokens and offers a migration guide. New installations should use JWTs.
Intercom lets teammates redact messages by hand. To redact automatically, use a DLP tool such as Strac Intercom DLP, which detects and masks PII, PCI, PHI and secrets in messages and attachments in real time.
They will, whether you allow it or not. Storing full card numbers in a support tool expands your PCI DSS scope. Real-time redaction masks the number on arrival, keeping it out of the inbox.
Intercom supports HIPAA use on certain plans with a signed BAA. A BAA covers Intercom's obligations, not what your teammates and AI tools do with PHI. Redacting PHI from conversations and attachments reduces exposure.
AI tools work from the conversations and content they can access. If a conversation holds a card number or PHI, an AI tool that reads it sees that data too. Redacting at the source, and using Strac MCP DLP for outside AI tools, keeps it out.
You can delete a user's data in Intercom, but first you need to know everywhere it appears, including attachments and synced tools. A DSPM scan maps where personal data lives, so deletion is complete rather than best-effort.