

August 28, 2026

6
min read
Is Google Workspace HIPAA Compliant?
Discover how to make G Suite HIPAA compliant with our detailed guide. Learn about HIPAA requirements, signing BAAs, and enhancing security for managing PHI.
Google Workspace (formerly G Suite), formerly known as Google Workspace, is a suite of cloud-based productivity and collaboration tools including popular applications like Gmail, Docs, Drive, and Calendar. These tools are designed to streamline communication and enhance productivity.
Managing protected health information (PHI) within these digital environments presents specific challenges, particularly due to the severe penalties associated with noncompliance. Improperly configured Google Workspace can expose healthcare information to significant compliance vulnerabilities, risk financial penalties, and cause reputational harm.
This guide provides a detailed roadmap for configuring Google Workspace to meet HIPAA standards. We’ll discuss the specifics and resolve the pressing concern, "Is Google Workspace HIPAA compliant?" Let’s begin.
The Health Insurance Portability and Accountability Act (HIPAA) of 1996 is a federal law designed to ensure the protection and confidential handling of protected health information (PHI). Besides safeguarding medical information, HIPAA also modernizes the flow of healthcare information, setting forth a series of regulatory standards for the privacy and security of PHI.
HIPAA defines how personally identifiable information maintained by the healthcare industry should be protected from fraud and theft. Understanding whether Google Workspace (formerly Google Workspace) is HIPAA compliant requires considering the HIPAA requirements and how they relate to Google services. Here are the key components:
The HIPAA Privacy Rule establishes national standards to protect individuals’ medical records and other personal health information. It applies to health plans, healthcare clearinghouses, and healthcare providers that conduct certain healthcare transactions electronically. This rule mandates appropriate safeguards to protect the privacy of Protected Health Information (PHI) and sets conditions on its use and disclosure.
This rule specifies administrative, physical, and technical safeguards to ensure the confidentiality, integrity, and availability of electronic PHI (ePHI). It applies to ePHI that a covered entity creates, receives, maintains, or transmits, requiring protections against reasonably anticipated threats.
Under this rule, the US Department of Health and Human Services (HHS) establishes standards for identifying individuals, employers, health plans, and healthcare providers in electronic transactions, enhancing the efficiency of health information transmission.
This rule requires adopting standardized methods for electronically exchanging health information related to billing and payment for services. Essentially, it mandates that health information be exchanged electronically and diagnoses and procedures be coded using national code sets.
The HIPAA Enforcement Rule contains provisions regarding compliance and investigations, civil money penalties for violations, and hearing procedures. It lays out the investigation process.
By understanding these rules, healthcare providers can better assess how to configure and use Google Workspace in compliance with HIPAA standards, ensuring that their use of cloud-based tools aligns with federal requirements for data protection.
Google Workspace can be configured to meet the compliance requirements set forth by the Health Insurance Portability and Accountability Act (HIPAA). However, achieving HIPAA compliance with Google Workspace involves meeting certain prerequisites.
It's crucial to enter into a Business Associate Agreement (BAA) with Google to align your use of Workspace with HIPAA. This agreement is a legally binding document that outlines the responsibilities of both parties in managing and protecting PHI.
To comply with HIPAA, organizations must subscribe to a paid Google Workspace plan, such as Business Standard, Business Plus, Enterprise, or Education editions. The free versions of Google Workspace do not provide the necessary features for HIPAA compliance, such as advanced security settings and audit capabilities.
With Google Workspace, getting a HIPAA Business Associate Agreement (BAA) is very straightforward:
By following these steps, you can ensure that your use of Google Workspace is compliant with HIPAA standards, safeguarding the confidentiality, integrity, and availability of PHI.
Google specifies several core services within Google Workspace that, when properly configured and used in accordance with the signed BAA, can support HIPAA compliance:
While the above services are covered by Google’s BAA, achieving HIPAA compliance also requires that they be configured correctly. One must constantly evaluate if Google Suite is HIPAA compliant by ensuring all settings and features align.
Ensuring HIPAA compliance using Google Workspace (formerly Google Workspace) involves several critical steps. Each step is designed to safeguard PHI by adhering to HIPAA's stringent requirements.
Despite taking robust precautions, accidental HIPAA breaches can still occur. Thus, compliance must be managed effectively through a comprehensive solution.
Google Workspace runs your email, Docs, Drive, Sheets, and Calendar — where teams accumulate patient emails, records, and forms. With a signed BAA and the right configuration it can be HIPAA compliant, but the newest risk isn’t Google Workspace itself: it’s connecting it to an AI assistant over the Model Context Protocol (MCP). Many teams now use Claude Cowork, and Anthropic will not sign a BAA for it. The moment an agent queries Gmail or Drive over MCP, that PHI can flow straight to a model outside your BAA — a reportable exposure even though Google Workspace is configured correctly.
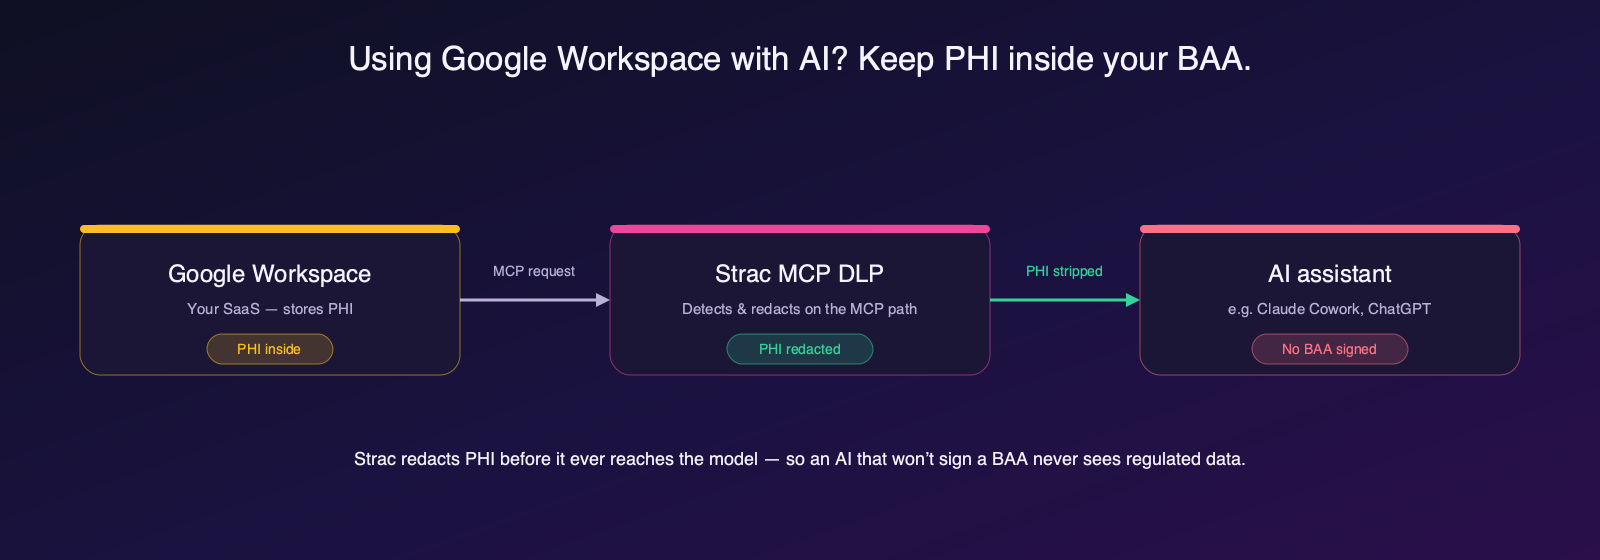
Strac MCP DLP closes that gap. It sits on the MCP path, detects PHI in every request and response, and redacts, masks, or blocks it before it reaches the assistant — so an AI that won’t sign a BAA never sees regulated data. Every action is audit-logged for HIPAA. See MCP integrations and Google Workspace MCP server.
Is Google Workspace HIPAA compliant in 2026? Yes — Google will sign a BAA and offers HIPAA-covered services (Gmail, Drive, Docs, Sheets, Calendar, Meet), but only if you execute the BAA, enable the covered services, and configure access and sharing correctly. The apps outside the BAA (and third-party add-ons) are not covered.
Can I use Google Workspace with Claude or ChatGPT and stay HIPAA compliant? Only if PHI never reaches a model that isn’t under a BAA. Claude Cowork does not sign one, so connecting Google Workspace over MCP can expose PHI. Strac MCP DLP redacts PHI on the MCP path before it reaches the assistant.
Is Gmail HIPAA compliant on its own? Gmail is HIPAA-capable under the Google Workspace BAA, but the free consumer version is not. See is Gmail HIPAA compliant.
Related reading:
Strac is a modern, intelligent DLP (Data Loss Prevention) platform that significantly simplifies HIPAA compliance for Google Workspace users. Here’s how Strac's features enhance compliance efforts:
Strac leverages advanced machine learning models to accurately detect and redact PHI across various Google Workspace applications such as Gmail, Drive, and Chat. Automating this crucial aspect of compliance helps prevent the unauthorized disclosure of sensitive information.
The platform's DLP capabilities extend beyond Google Workspace to include popular applications such as Slack, Zendesk, and Salesforce. This comprehensive approach ensures consistent HIPAA compliance across all tools handling digital PHI.
Designed for seamless integration and flexibility, Strac can be deployed quickly and is scalable. This ease of deployment allows for rapid compliance with HIPAA requirements within Google Workspace environments.
To further enhance data security, Strac offers tokenization and proxy APIs to process PHI without it ever residing on servers. This "Zero Data architecture" aligns perfectly with HIPAA’s stringent data protection requirements, significantly easing compliance efforts.
Strac also provides continuous monitoring and auditing features to detect policy violations or potential data breaches involving PHI. This constant vigilance helps organizations maintain ongoing compliance with HIPAA regulations, ensuring that any issues are promptly identified and addressed.







