August 28, 2026

6
min read
Data Encryption in the Age of the Hacker
Learn how data encryption works, where it falls short, and how Strac strengthens protection with DLP across SaaS, GenAI, MCP, cloud, and endpoints.
· Encryption protects sensitive data by making itunreadable without the correct cryptographic key, but it does not prevent everyform of data loss.
· Organizations need encryption for data at restand in transit; data in use requires additional controls because authorizedusers, applications, and AI agents can access decrypted information.
· Encryption and Data Loss Prevention servedifferent purposes. Encryption protects confidentiality; DLP discoverssensitive data, monitors how it moves, and enforces policies.
· Strac combines DSPM and DLP across SaaS, cloud,GenAI, MCP, browsers, and endpoints to discover sensitive data and remediateexposure through actions such as redaction, masking, blocking, deletion,quarantine, or encryption.
· Thestrongest 2026 data security strategy combines encryption, key management,identity controls, data discovery, real-time DLP, and continuous monitoring.
Encryption remains one of the foundations of data security. It protects customer records, payment details, health information, credentials, intellectual property, and other confidential data by making the information unreadable without the correct key.
But encryption alone is no longer enough.
Sensitive data now moves continuously between SaaS applications, cloud storage, employee devices, browsers, AI assistants, APIs, and MCP-connected agents. An encrypted database does not stop an authorized employee from copying decrypted customer records into ChatGPT, uploading them to personal cloud storage, or sending them through Slack.
Modern data protection requires organizations to encrypt sensitive data and control what happens after that data is decrypted and used.
Data encryption transforms readable information, known as plaintext, into an unreadable format called ciphertext. A cryptographic algorithm and encryption key perform the transformation.
Only a user, application, or system with the correct key should be able to decrypt the ciphertext and restore the original information.
For example, an unencrypted customer record might contain:
Customer SSN: 123-45-6789
After encryption, it becomes an unreadable sequence of characters. If an attacker steals the encrypted record but cannot access the key, the information should remain unusable.
The two primary types of encryption are symmetric and asymmetric encryption. Modern security systems frequently use both because they solve different problems.
Symmetric encryption uses the same secret key to encrypt and decrypt information.
It is fast and efficient, making it suitable for encrypting:
The primary risk is key management. If the encryption key is exposed, an attacker may be able to decrypt everything protected by that key.
Organizations must securely generate, distribute, rotate, store, and revoke symmetric keys. Encryption becomes far less valuable when keys are stored beside the data they protect or are accessible to too many users and applications.
Asymmetric encryption uses a mathematically related pair of keys:
Information encrypted with the public key can only be decrypted with the corresponding private key. Asymmetric cryptography is commonly used for secure communications, digital signatures, identity verification, and exchanging symmetric encryption keys.
Because asymmetric encryption requires more computing resources, organizations often use it to establish trust and exchange keys, then use symmetric encryption for the actual data transfer.
Hashing is sometimes confused with encryption, but the two are not interchangeable.
Encryption is designed to be reversible with the correct key. Hashing creates a one-way representation of data and is commonly used for password verification and integrity checks.
A properly hashed password should not be recoverable from the hash. Encrypted information, by contrast, must be recoverable by an authorized party.
An effective encryption strategy must consider the different states in which sensitive data exists.
Data at rest includes information stored in:
Encryption at rest reduces the risk that stolen storage devices, database files, or backups will expose readable sensitive information.
However, encrypting a storage system does not automatically eliminate data exposure. When an authorized application or user accesses the system, the information is usually decrypted and becomes available for use.
Data in transit is information moving between systems, users, applications, or networks.
Transport Layer Security, commonly known as TLS, protects data traveling between browsers, APIs, cloud services, and other connected systems. It helps prevent interception and manipulation while the information is moving.
TLS protects the communication channel, but it does not control what the receiving application does with the data after delivery.
Data in use is information being accessed, processed, analyzed, copied, or modified.
This is where encryption alone frequently reaches its limits. Applications need access to readable data to process it. Employees may need to view customer records. AI assistants need to read prompts and contextual information to generate responses.
Once data is decrypted, it can potentially be:
Protecting data in use requires DLP, access controls, data classification, browser enforcement, endpoint monitoring, and activity auditing alongside encryption.
Encryption reduces the likelihood that stolen or intercepted data can be immediately exploited.
Organizations can use it to protect information such as:
Encryption is especially important for portable devices, cloud backups, databases, and other systems where the underlying storage could be compromised.
Security and privacy frameworks may require or strongly encourage encryption based on the type of information, system, and risk involved.
Encryption can support programs associated with:
However, encryption does not make an organization automatically compliant. Compliance also depends on access governance, retention, incident response, monitoring, risk assessment, key management, and evidence that controls are operating effectively.
When properly encrypted information is stolen without its encryption keys, the attacker may be unable to read or monetize it.
The word “properly” matters. Encryption may offer limited protection when:
Encryption reduces breach impact, but it cannot compensate for poor key management or uncontrolled data movement.
Organizations often treat encryption, tokenization, and redaction as interchangeable. Each technique serves a different purpose.
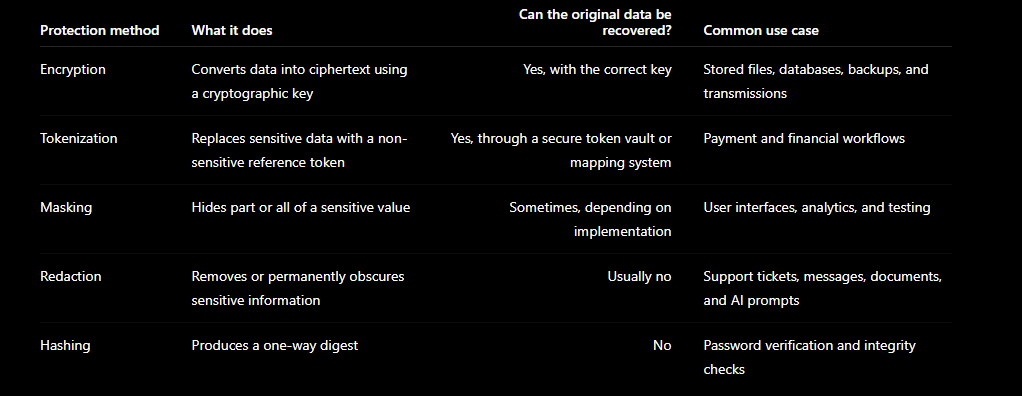
The appropriate method depends on whether the business still needs the original value and who should be permitted to retrieve it.
Encryption is powerful, but it is not a complete data protection program.
It cannot independently tell an organization:
Encryption protects data from unauthorized decryption. It does not determine whether an authorized user is handling decrypted information safely.
That is why encryption must be paired with Data Security Posture Management and Data Loss Prevention.
Encryption and DLP address complementary parts of the data security problem.
Encryption makes data unreadable without the correct key. DLP discovers and classifies sensitive information, monitors how it is being used, and enforces policies when risky activity occurs.
A modern DLP platform can help answer questions such as:
Encryption may be one possible DLP action, but it is not always the right one. Depending on the data, application, user, and destination, the appropriate response may be to redact, mask, block, quarantine, delete, encrypt, or simply audit the activity.
Traditional encryption programs were largely designed around databases, storage systems, laptops, and network connections.
The modern data estate is more fragmented. Sensitive information can move between dozens of SaaS applications and AI systems in seconds.
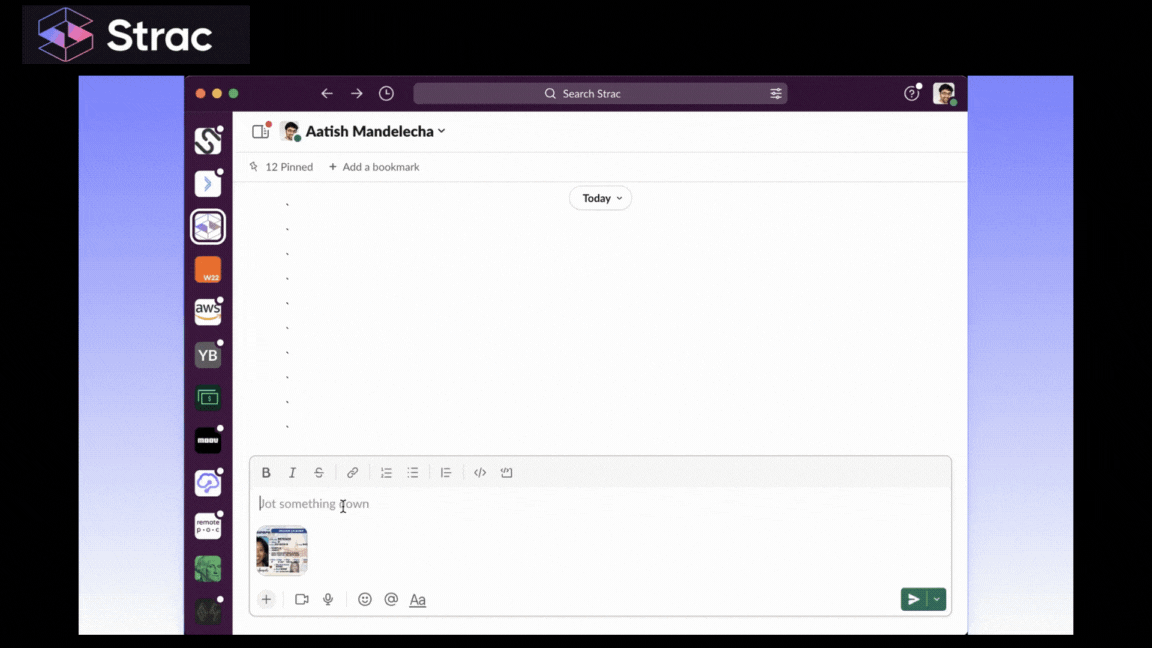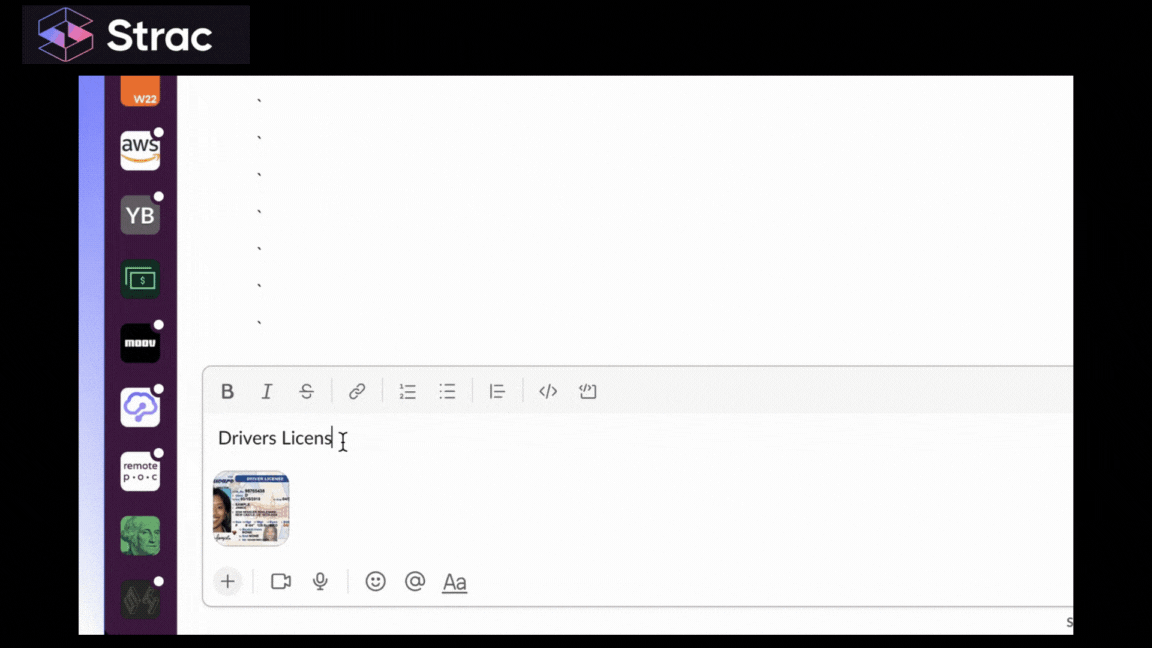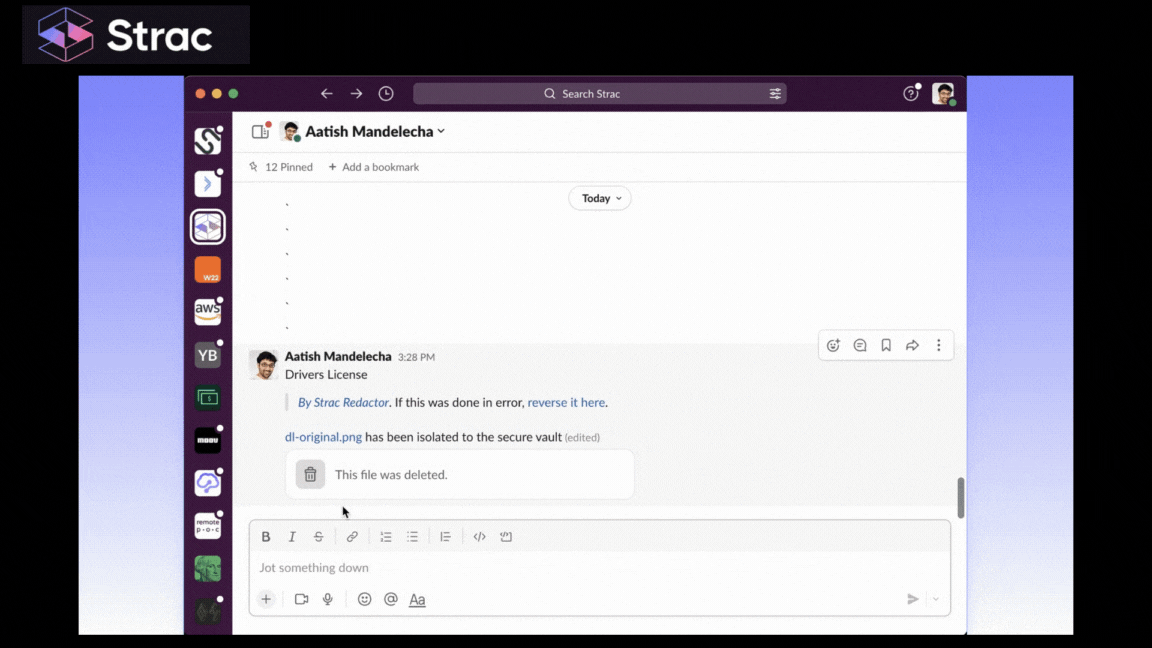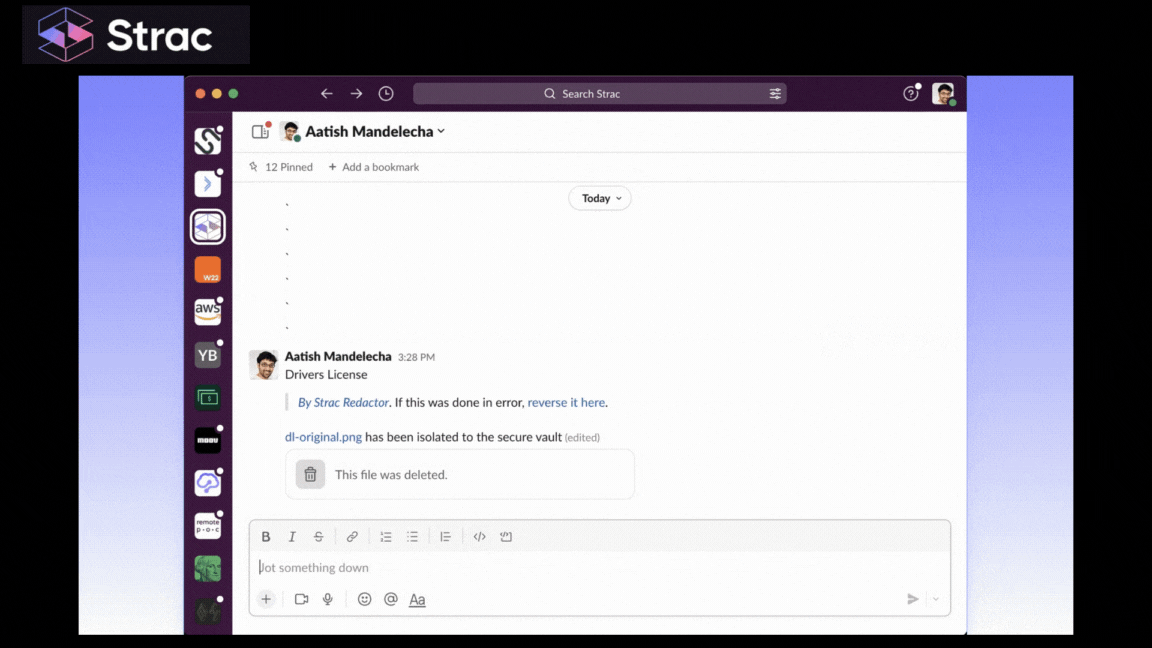
Customer and employee data may appear in Slack messages, Google Drive files, Salesforce records, Zendesk tickets, email threads, and uploaded attachments.
A SaaS provider may encrypt its infrastructure, but that does not mean sensitive data belongs in every message, ticket, or shared folder. Organizations still need visibility and policy enforcement inside the application.
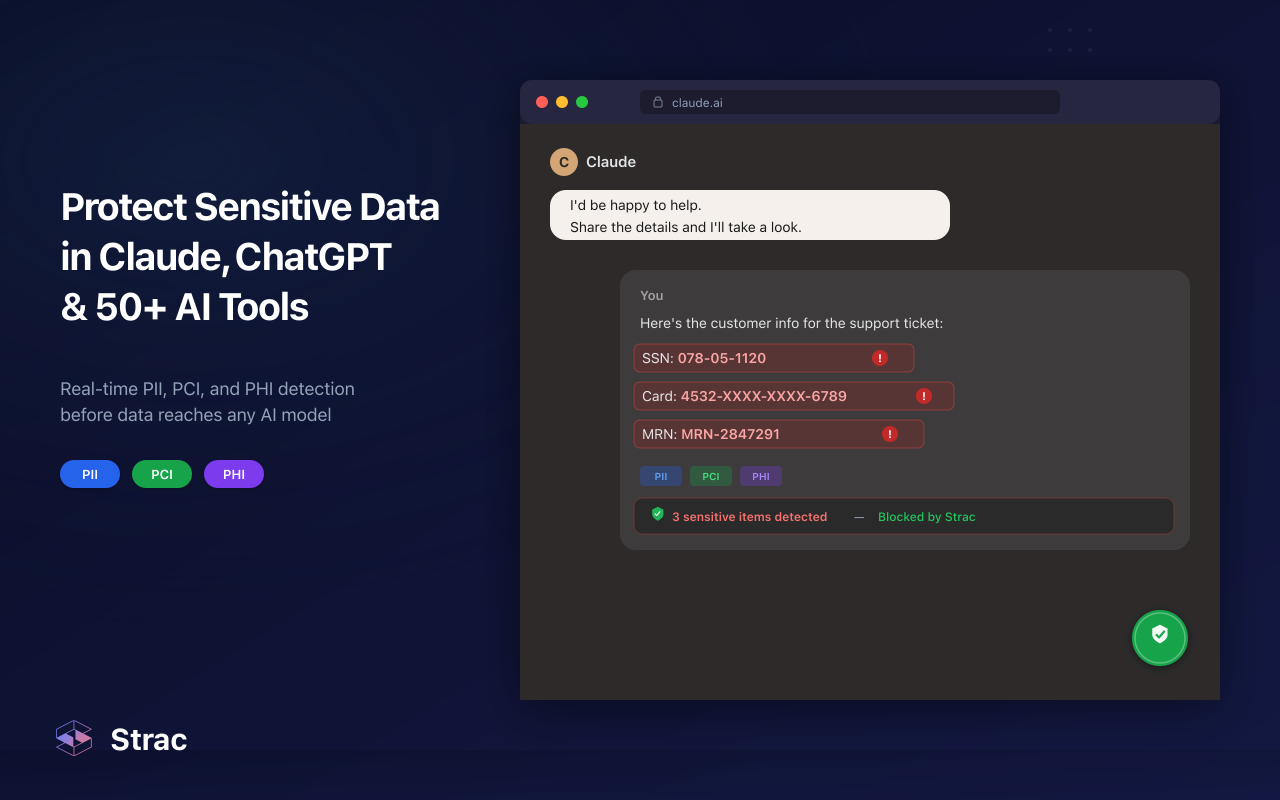
Employees may paste source code, customer records, medical information, financial data, or credentials into AI assistants.
The connection to the AI service may be encrypted with TLS, but the sensitive content still reaches the service. Transport encryption protects the journey; it does not decide whether the data should have been sent.
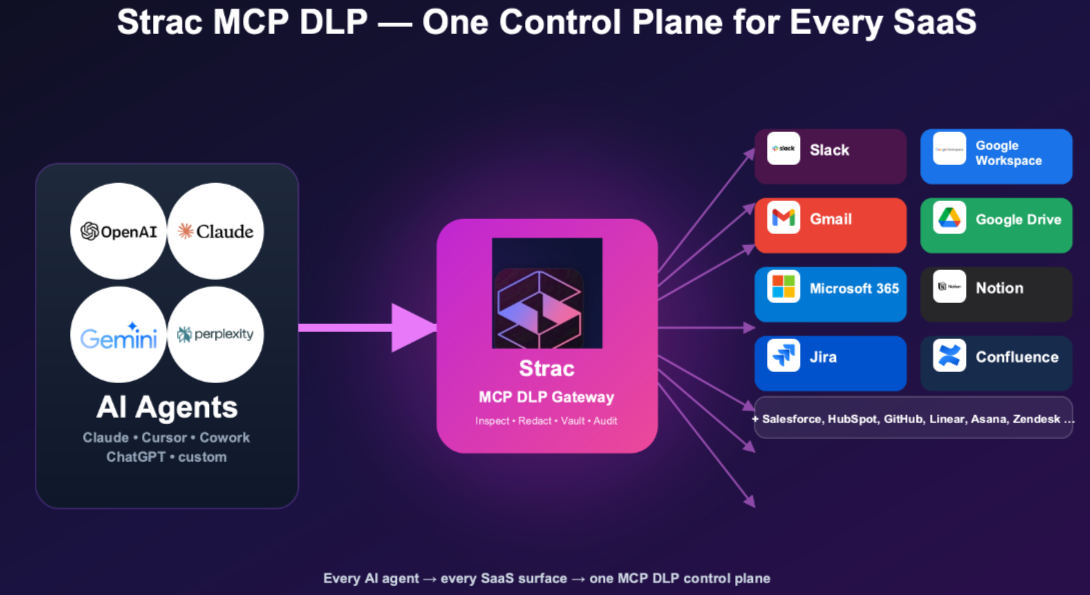
Model Context Protocol connections allow AI agents to retrieve information and perform actions across tools such as cloud storage, databases, ticketing platforms, and internal systems.
An encrypted MCP connection can protect data while it travels, but it cannot determine whether the agent requested excessive information, exposed sensitive data in its response, or sent information to an inappropriate destination.
MCP DLP adds a policy enforcement layer between AI agents and connected tools. It can inspect requests and responses, identify sensitive content, and apply actions before information reaches the model, tool, or end user.

Users can access encrypted SaaS platforms and then download, copy, paste, print, upload, or screenshot the decrypted information.
Browser and Endpoint DLP help control these actions based on the sensitive data involved, the application, the user, the device, and the destination.
Strac is not simply an encryption tool. It is a unified DSPM and DLP platform designed to discover, classify, and protect sensitive data across the places where businesses work in 2026.
Strac complements an organization’s existing encryption and identity controls by protecting sensitive information when it is stored, accessed, shared, or sent to AI systems.
Strac discovers sensitive data across SaaS applications, cloud platforms, GenAI tools, browsers, endpoints, and connected workflows.
This helps security teams identify sensitive information that may already be encrypted by the underlying platform but is stored in the wrong location, shared too broadly, or accessible to unnecessary users.
Instead of relying on separate discovery and enforcement products, Strac combines DSPM and DLP in one platform.
Strac provides detectors for PII, PHI, PCI data, financial information, credentials, secrets, and other confidential information.
Organizations can also create custom detectors for proprietary identifiers, internal classifications, customer-specific data, and other information unique to their business.
Strac uses content-aware detection, including machine learning and OCR, to inspect structured and unstructured content across:
This allows policies to evaluate the actual content instead of relying only on file names, keywords, or basic regular expressions.
Many legacy tools stop after generating an alert. Strac can act on the sensitive data it detects.
Depending on the channel and policy, Strac can:
For example, a company could allow a support representative to submit a ticket while automatically redacting the customer’s Social Security number from the message and its attachments.
Strac protects sensitive information across applications where employees collaborate, communicate, manage customers, and store files.
Its integrations help organizations extend detection and remediation into platforms such as Google Workspace, Microsoft 365, Slack, Salesforce, Zendesk, Intercom, and cloud data environments.
This provides application-level control that storage encryption alone cannot deliver.
Strac can inspect prompts, responses, and file uploads associated with generative AI tools.
Security teams can define different actions based on the information being shared. A policy might allow public marketing content, warn users before sharing internal information, and block credentials, source code, or regulated customer data.
Browser-level visibility can also help organizations identify Shadow AI usage, including unsanctioned AI tools that employees access without security approval.
Strac’s MCP DLP capabilities help secure data moving between AI agents, models, and MCP-connected tools.
Policies can inspect requests and responses for sensitive information and apply controls before exposure occurs. This becomes increasingly important as AI agents gain access to cloud drives, business applications, databases, and internal APIs.
Encryption protects the MCP connection. MCP DLP controls which data should be allowed to pass through it.
Endpoint DLP extends data protection to employee devices, where decrypted information is frequently copied, downloaded, printed, uploaded, or transferred.
Strac can enforce data-aware policies across channels such as browsers, email, cloud applications, removable media, printing, clipboard activity, and file transfers.
Endpoint Data Lineage also helps security teams understand where sensitive data originated, how it moved, and where it was sent. This context is essential for separating legitimate business activity from potential data exfiltration.
Strac provides centralized visibility into sensitive data findings, policy violations, remediation actions, and user activity.
This gives security and compliance teams a record of:
The result is more useful than an encryption status report alone because it shows how sensitive data is actually handled throughout the organization.
Organizations should treat encryption as one layer within a broader data security architecture.
Apply encryption to databases, storage systems, backups, endpoints, removable media, APIs, and network communications based on risk and regulatory requirements.
Keys should be protected through a dedicated key management system or hardware-backed security mechanism. Access to keys should be tightly restricted and logged.
Encryption keys should have defined lifecycles. Organizations need procedures for rotation, expiration, compromise, revocation, and recovery.
You cannot protect information you do not know exists. Continuous discovery helps identify regulated or confidential data across SaaS, cloud, AI, and endpoint environments.
Encryption does not help when too many authorized accounts can decrypt the data. Limit access according to job responsibilities and regularly review permissions.
Inspect data when employees or AI agents attempt to copy, upload, share, download, print, or transmit it. Policies should consider the data type, user, device, application, and destination.
Treat prompts, responses, retrieved context, tool calls, and agent actions as part of the sensitive data lifecycle. Do not assume that an encrypted connection makes an AI workflow safe.
Test encryption, key recovery, access restrictions, DLP policies, remediation actions, and incident response procedures. A control that has never been tested should not be assumed to work during a real incident.
Encryption strategies will continue evolving as cloud adoption, AI agents, and quantum computing reshape the threat landscape.
Organizations should begin understanding their exposure to future cryptographic risks, particularly for information that must remain confidential for many years. Cryptographic agility, which is the ability to replace algorithms and keys without rebuilding entire systems, will become increasingly important.
At the same time, the immediate challenge is not only stronger encryption. Businesses must control sensitive data after legitimate systems decrypt it. The future of data security therefore depends on combining modern cryptography with continuous discovery, identity governance, contextual DLP, AI security, and automated remediation.
Encryption is essential, but it is not a complete defense against modern data loss.
It can protect a stolen database, backup, device, or intercepted connection. It cannot independently stop an authorized user or AI agent from sharing decrypted information through SaaS, GenAI, MCP, browsers, or endpoints.
Strac helps close that gap by combining DSPM and DLP across the modern data estate. Organizations can discover sensitive information, understand how it moves, and automatically redact, mask, block, quarantine, delete, encrypt, or audit it based on context.
Encryption protects the data when it is unreadable. Strac helps protect it when people, applications, and AI systems are actually using it.
Check out Strac’s reviews on G2. Strac averages five stars.
Related reading:
No. Encryption protects data when attackers cannot access the decryption key. If credentials, encryption keys, or active user sessions are compromised, attackers may still access the readable data. Encryption must work alongside identity security, key management, DSPM, and DLP.
Because SaaS encryption protects the platform’s infrastructure, not every action users take inside it. Employees can still paste sensitive data into Slack, expose PHI in support tickets, overshare files, or download customer records. DLP controls how decrypted data is stored, shared, and moved.
Not necessarily. TLS encrypts the connection, but it does not determine whether the information should be sent. GenAI DLP inspects prompts, responses, and uploads so organizations can block or redact credentials, customer data, source code, and other confidential information.
Encryption protects data while it travels between an AI agent and an MCP-connected tool. It does not stop the agent from retrieving excessive data or exposing sensitive information in its response. MCP DLP inspects requests and responses and enforces policies before the data reaches the model, tool, or user.
It depends on the context. Encrypt data that authorized systems must recover later; redact information that users do not need to see; block transfers that should never occur. Strac applies context-aware actions such as encryption, redaction, masking, blocking, deletion, quarantine, or user coaching across SaaS, cloud, GenAI, MCP, browsers, and endpoints.